OpenPetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
- 287
- C
- MIT
- 2 mo ago
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
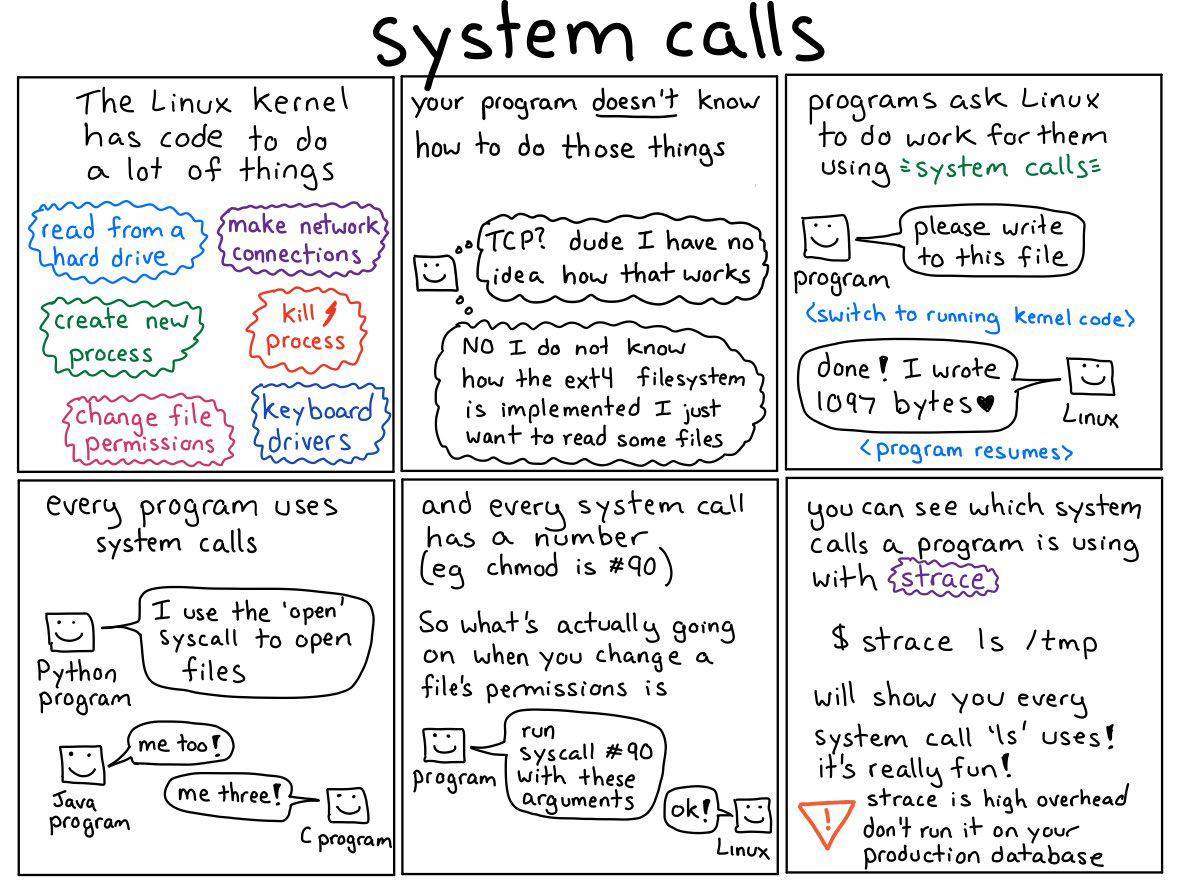
🐧 Assembly with Linux (Notes, Syscalls, Protection Rings) 🐧
💻 This repository provides solutions to most of the programming questions in the exercise given at the back of chapters for Bao Ji's Book (text book for course "Comp. Organization & Assembly Lang. EE213" at FAST). Sharing these, so they might help students in understanding the Assembly concepts.
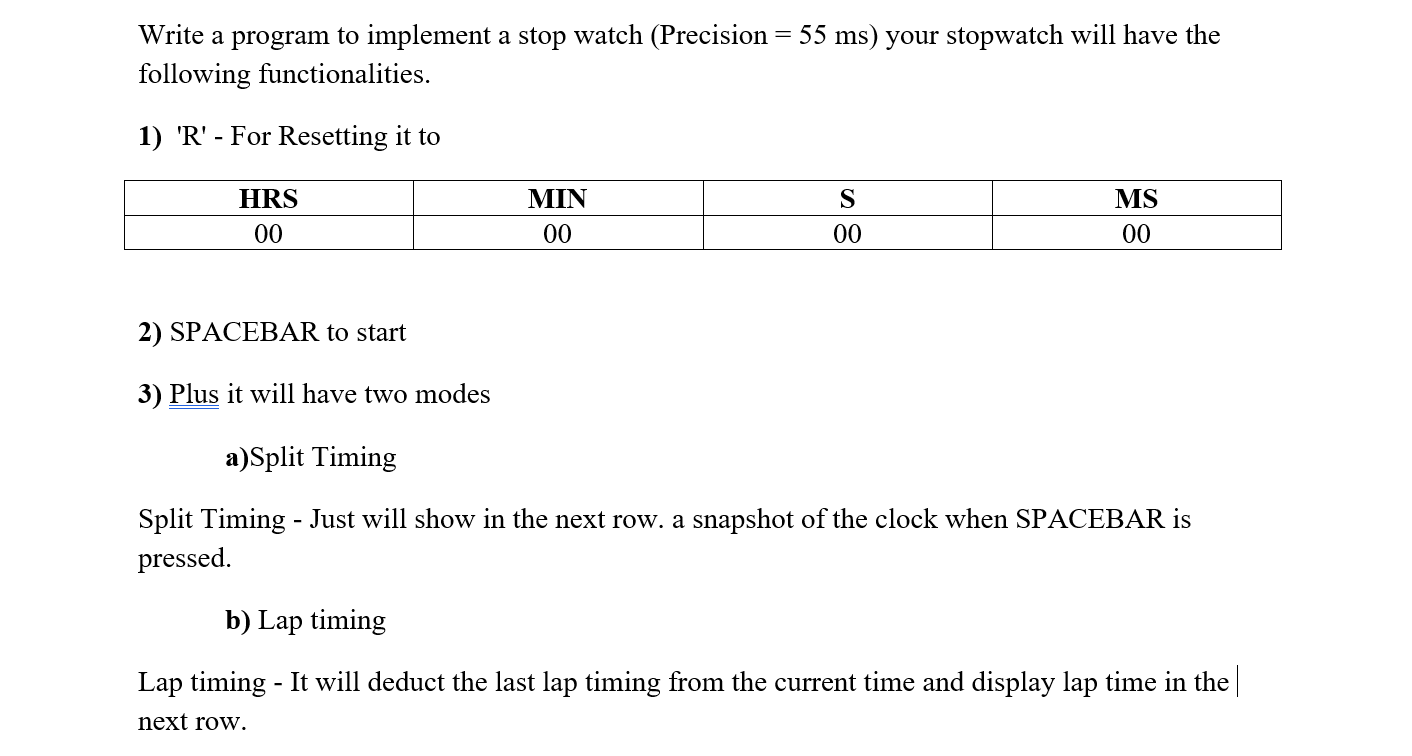
⏱️ A fully featured stop watch made in 8086 Assembly Language, having two modes: Split Timing and Lap Timing
Compiler for xlang, A C like high level programming language that emits Intel x86 assembly
🖥️ Interesting solved problems demonstrating the concepts of Bit Manipulation and Subroutines (Functions) in 8086 Assembly Language.
📌 Solved problems to help better understand the important concepts of Display Memory (Video Card Memory), String Manipulation, Software Interrupts and Hardware Interrupts in context of x86 Assembly Language (8086 Assembly)