slsa

Open repos and models their makers tagged slsa, most starred first. The same for everyone.

Run my own servicesRepo

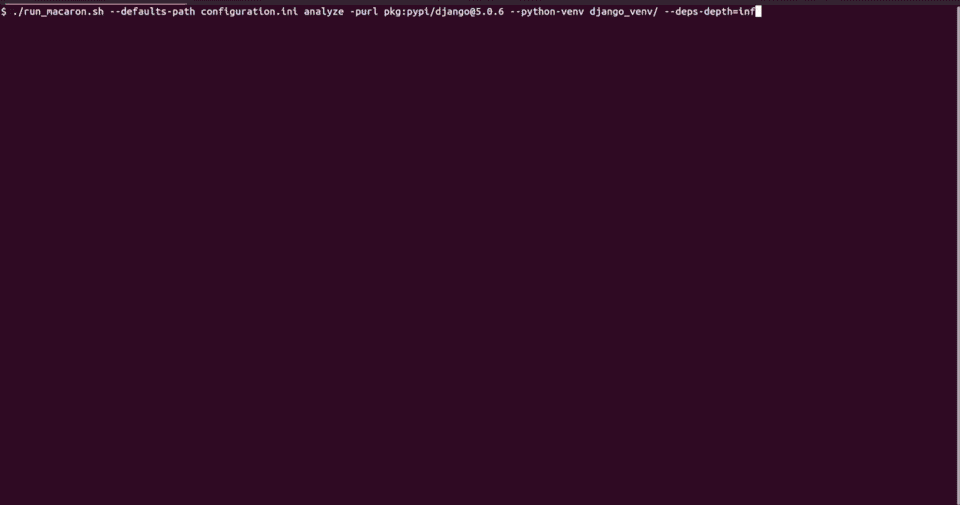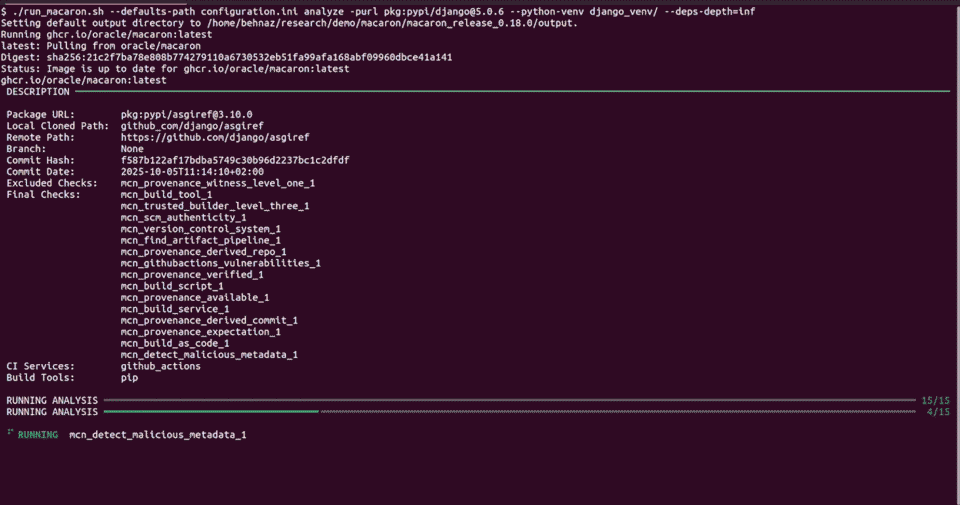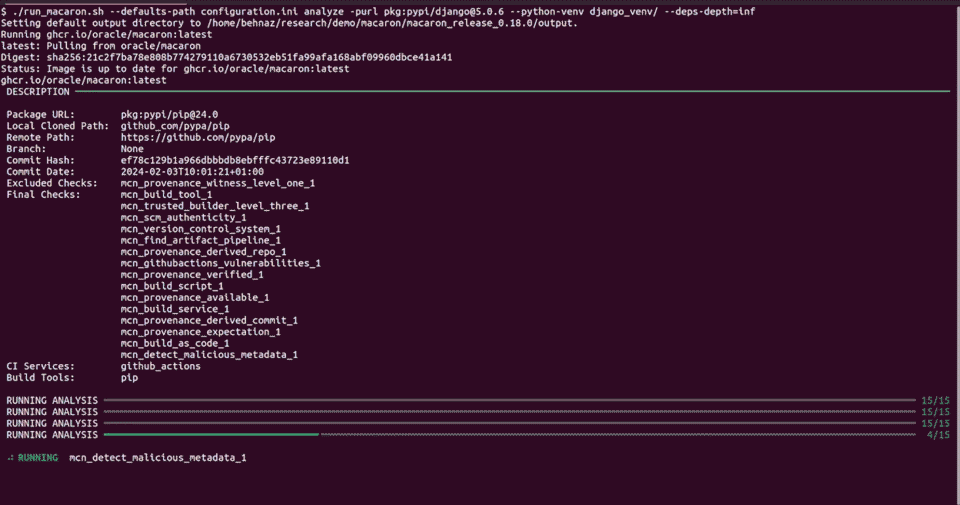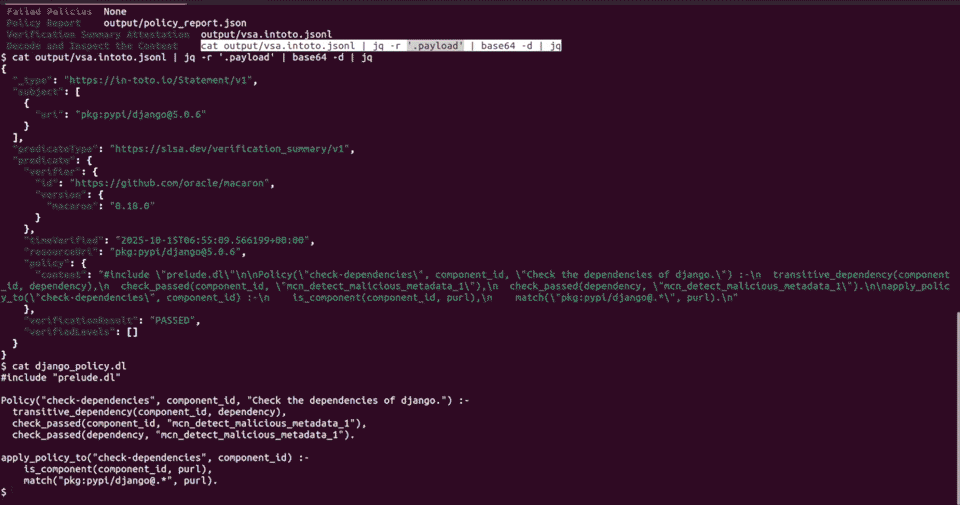
macaron

Macaron is an extensible supply-chain security analysis framework from Oracle Labs that supports a wide range of build systems and CI/CD services. It can be used to prevent supply chain attacks, detect malicious Python packages, or check conformance to frameworks, such as SLSA. Documentation:

  • 211
  • Python
  • UPL-1.0
  • 4 d ago
oracleTake it
Developer toolsRepo

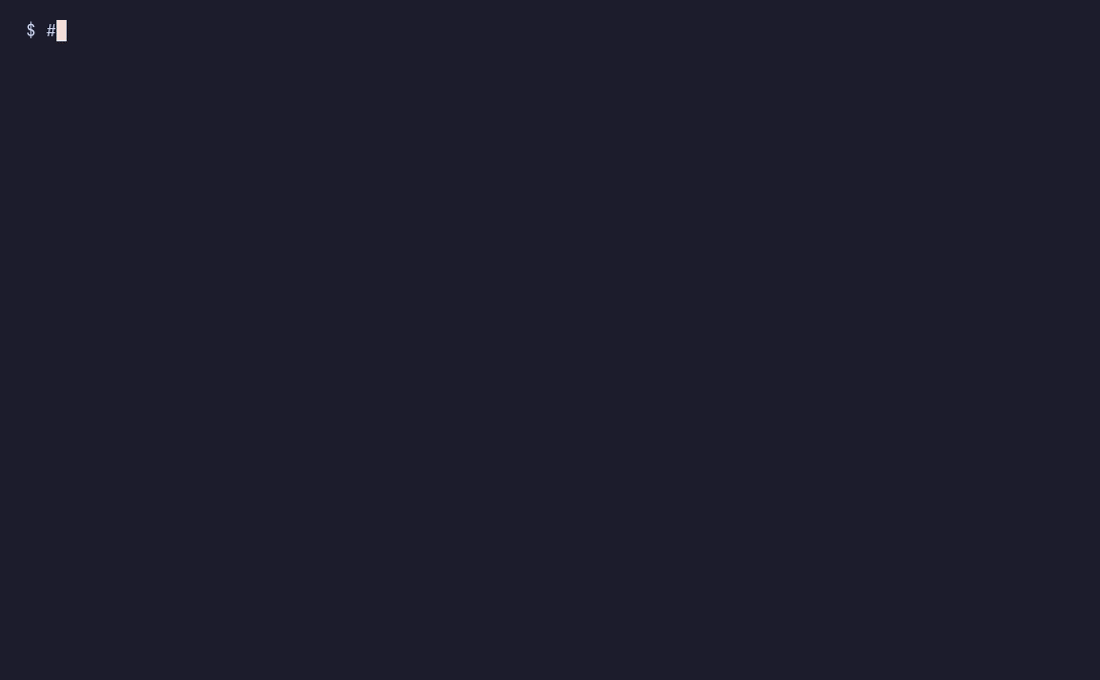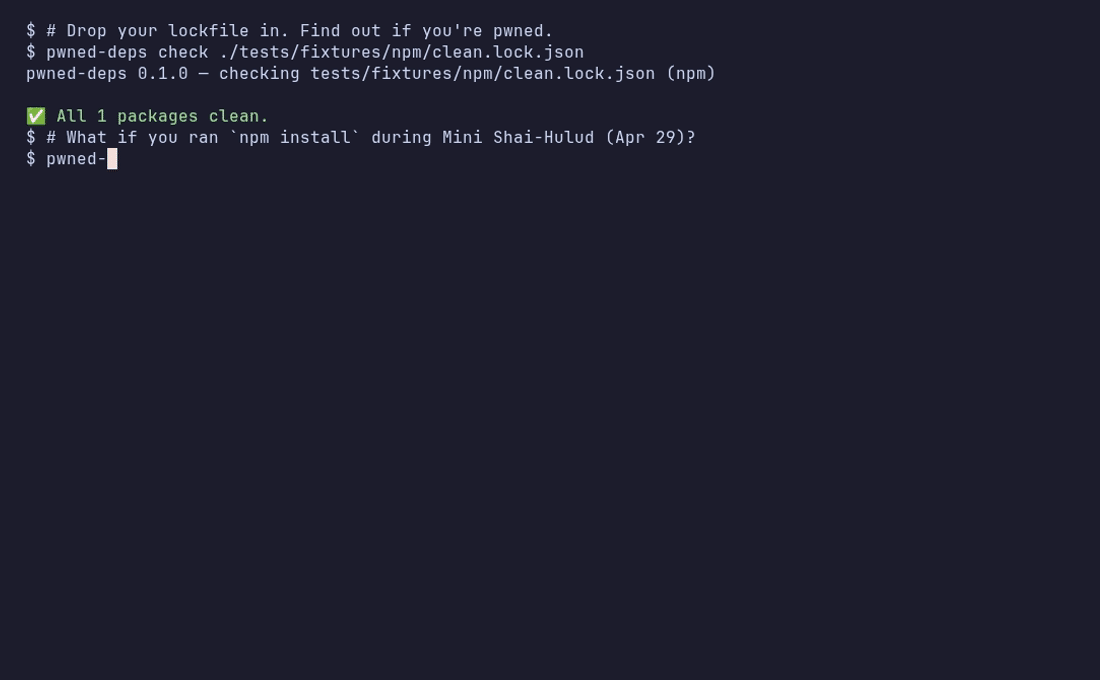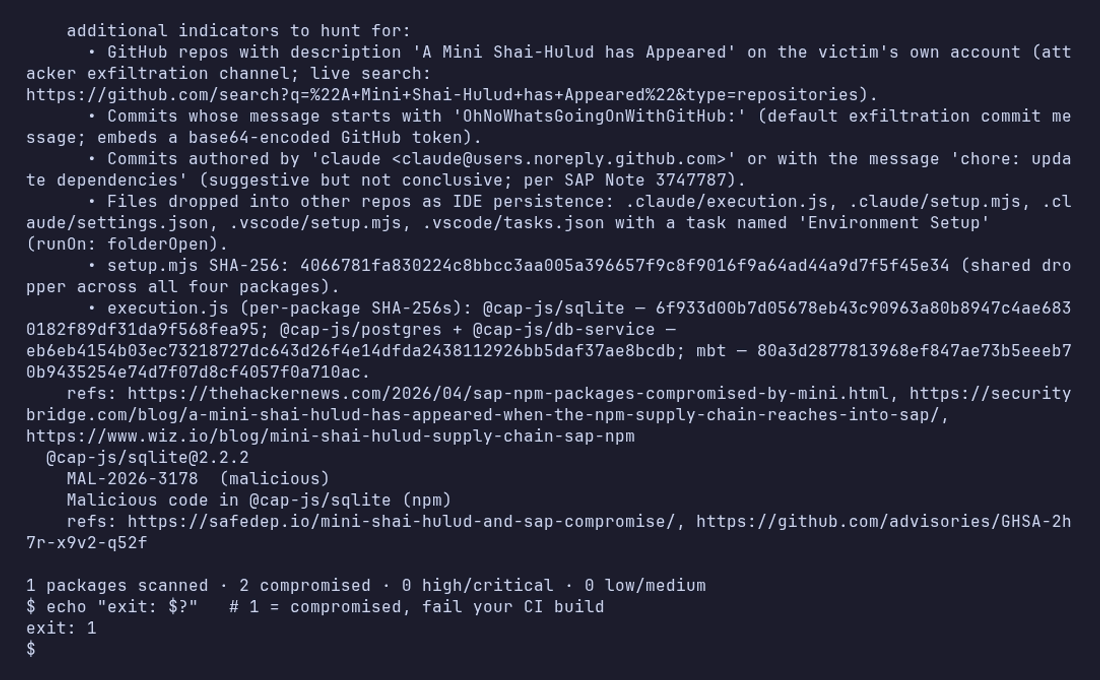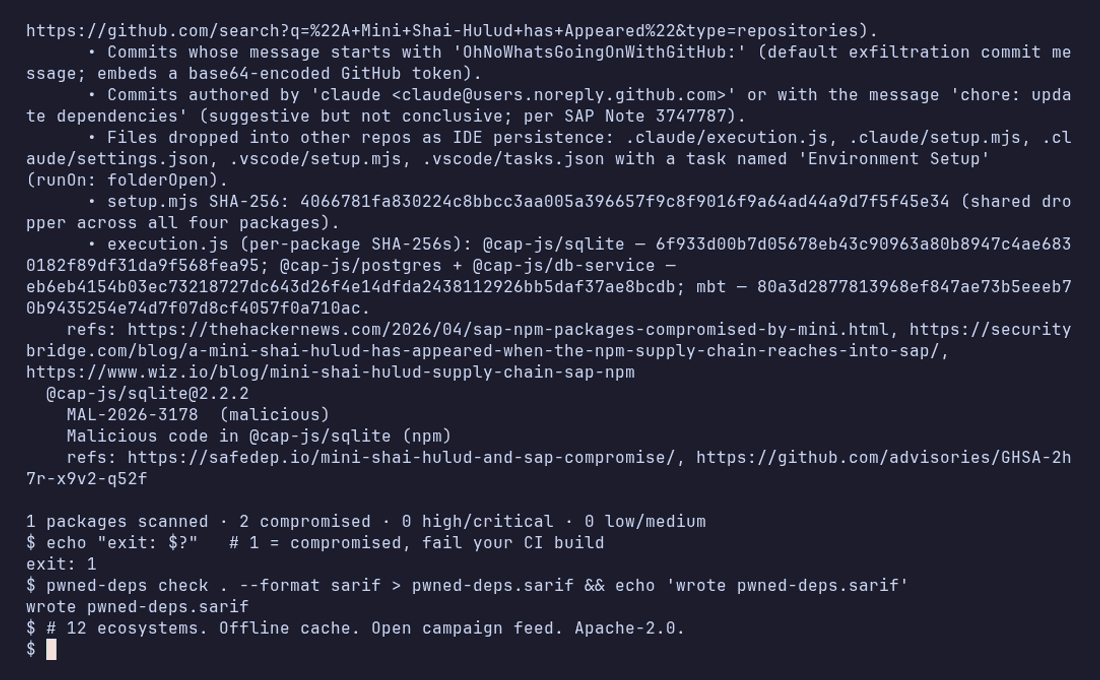
pwned-deps

Is your lockfile pwned? 5-second scan of npm/PyPI/Maven/Cargo/Go/RubyGems lockfiles for compromised packages — OSV + curated campaign feed, --min-age cooling-off gate, exit 4 when a scan is incomplete. SLSA L3, Sigstore-signed feed.

  • 164
  • Python
  • Apache-2.0
  • 4 d ago
mkbhardwas12Take it
Security and privacyRepo

bomdrift

SBOM diff with supply-chain risk signals — flags new CVEs, typosquats, and young maintainers on changed deps. Built after axios (Mar 2026), Shai-Hulud, and xz.

  • 7
  • Rust
  • Apache-2.0
  • 4 mo ago
MetbcyTake it
AI agentsRepo

mnemos

Self-hosted memory + evidence layer for AI agents (Claude Code, Codex, Hermes, ...) — embeddable Go library, MCP / HTTP / CLI, evidence-backed claims, bitemporal recall, axi-go execution kernel with JSONL audit + token budgets, cosign-signed releases with SLSA L3 provenance. No vendor cloud, no per-call billing.

  • 5
  • Go
  • MIT
  • 6 h ago
Search GitHub and Hugging Face for slsa

Get , open it once and sign in. Then come back here and press the button again.

slsa: open source repos and models on Take My Repo