pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
- 3.9k
- C++
- BSD-2-Clause
- 2 wk ago
Collection of codes focused on Linux rootkits
Repo MatheuZSecurity/Rootkit, read from GitHub 2 h ago. MatheuZSecurity has not joined Take My Repo.
MatheuZSecurity/Rootkit is a public repo on GitHub by MatheuZSecurity. Collection of codes focused on Linux rootkits. It declares the MIT license on GitHub. It is written mainly in C, has 229 stars and last changed on 2025-10-22. Nobody has reviewed it on Take My Repo yet, which says nothing about its quality. Read from GitHub on 2026-11-22.
[!Note] Some of these codes I created were taken from my server called Rootkit Researchers that I shared with people on my server, if you want to join feel free to be part of the community. Join Rootkit Community https://discord.gg/66N5ZQppU7
[!Important] This repository is for educational and research purposes only; We are not responsible for damages caused by use, which should only occur in controlled environments, such as VMs, with consent and in accordance with the law.
Feel free to make pull requests.
MatheuZSecurity/Rootkit is a public repo on GitHub by MatheuZSecurity. Collection of codes focused on Linux rootkits.
It declares the MIT license on GitHub.
Its maker tagged it for Linux. That is declared by the maker; Take My Repo has not tested it.
Open "Take it" on its page: Take My Repo writes an install plan for your machine and hands it to your AI agent (Claude Code, Codex or Cursor), which asks you before each step. Take My Repo has not tested it on any machine.
Its last change on GitHub was on 2025-10-22. Take My Repo does not judge from that whether it is maintained.
Nobody has reviewed it on Take My Repo yet, which says nothing about its quality.
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
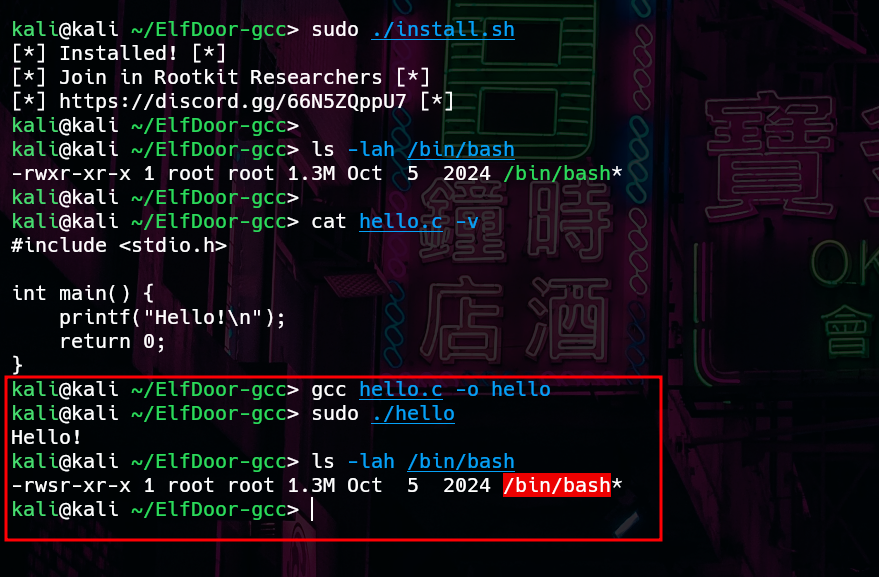
ElfDoor-gcc is an LD_PRELOAD that hijacks gcc to inject malicious code into binaries during linking, without touching the source code.