AutoGPT
AutoGPT is the vision of accessible AI for everyone, to use and to build on. Our mission is to provide the tools, so that you can focus on what matters.
- 188k
- Python
- 33 min ago
Agent Substrate: the core system
Repo agent-substrate/substrate, read from GitHub 1 min ago. agent-substrate has not joined Take My Repo.
agent-substrate/substrate is a public repo on GitHub by agent-substrate. Agent Substrate: the core system. It declares the Apache-2.0 license on GitHub. It is written mainly in Go, has 8,158 stars and last changed on 2026-11-22. Nobody has reviewed it on Take My Repo yet, which says nothing about its quality. Read from GitHub on 2026-11-22.
Zero-trust sandboxing for millions of agents on Kubernetes.
Quickstart · Security · Architecture · Contributing
Agent Substrate is a security-hardened, zero-trust runtime for sandboxed agents, engineered to safely run millions of agents and tools with 10x higher density than standard containers. Purpose-built for the era of autonomous agents, Substrate delivers fast resume operations in less than 500ms, with more than 500 activations per second. Agents get isolated compute, identity, networking, and storage. Sensitive credentials are kept out of reach from untrusted code. It supports multiple sandbox technologies, including microVMs and gVisor, while enabling a consistent lifecycle and management of all sandboxes.
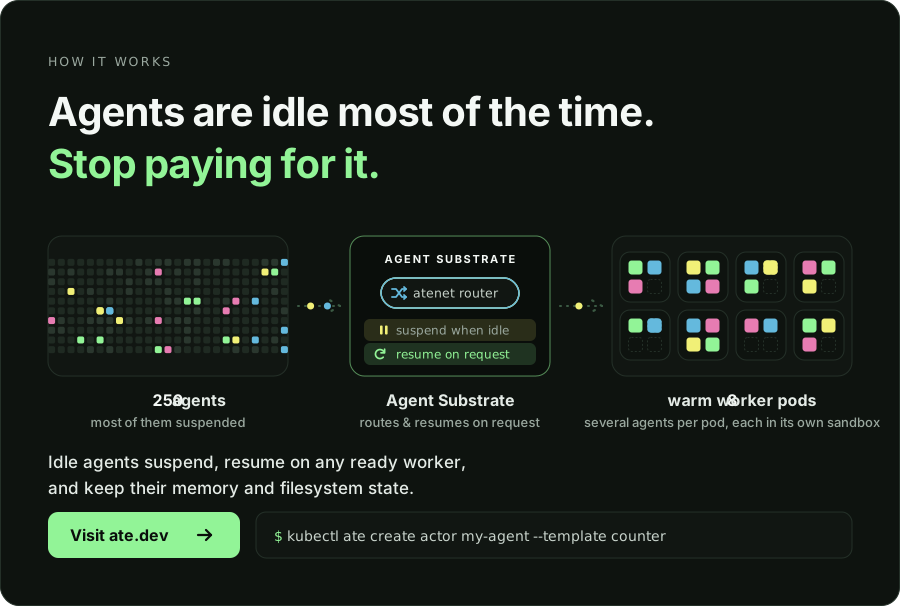
At its core, Agent Substrate maps a larger set of “actors” (stateful workloads such as agents) onto a smaller pool of ready “workers”. Because agents spend most of their lives waiting on models, tools, or humans, Substrate snapshots idle actors out of memory and restores them when a request arrives.
Substrate is a low-opinion runtime, not an agent SDK. The workloads it runs do not have to be AI agents, though autonomous, untrusted, mostly-idle agents are the target for its isolation and scheduling model. It runs on standard Kubernetes: Pods, autoscaling, NetworkPolicies. It adds agent-specific scheduling, snapshotting, identity, and network mediation. This allows agentic, inference, training, and reinforcement learning workloads to share one infrastructure plane.
Substrate treats every actor as untrusted and mutually hostile, so tenants can share physical nodes without sharing a security boundary. Every control operates within the cold-start and resume budget. See the Security Guide for the full list of security principles and threat model.
runsc) or Cloud Hypervisor microVM sandbox with segregated compute, network, and storage. Plain Linux containers are not supported.atenet-egress) injects credentials into approved outbound requests outside the sandbox, so a prompt-injected or compromised agent has nothing to exfiltrate.atenet-router), no lateral actor-to-actor or control-plane access, and outbound traffic restricted by the egress gateway.
Watch the Agent Substrate cluster multiplex ~250 stateful actors across just 8 physical pods.
This demo highlights the core developer experience and "Agentic Infrastructure" capabilities of Substrate:
To reproduce this demo in your own cluster, see the Counter Demo. For more walkthroughs, visit the agent-substrate YouTube channel.
Agent Substrate is framework and agent harness agnostic. Because it runs standard OCI container images inside gVisor or microVM sandboxes and enforces security outside the workload, it hosts agents built on any stack without SDK changes:
Agent Substrate has reached 1.0. We are committed to compatibility and stability of the public API, CLI, and configuration formats. We will continue to add new features, but we will not break existing APIs or configuration formats without a major version bump. See "Compatibility and schema evolution" in CONTRIBUTING.md for more details.
Currently we aim to support the latest stable release of Kubernetes, and the previous minor release.
For announcements, technical discussions, and community support, please join the ate-dev Google Group.
We host a weekly community meeting every Thursday from 10:00am - 11:00am PST.
We also have channels in the CNCF slack; request an invite here if you don't have access.
Please see CONTRIBUTING.md for guidelines on contributing to the project. We welcome contributions of all kinds, but the project is VERY young. Our immediate focus is on building out the core system and demos, so we may not be able to review or merge contributions that don't align with those goals in the near term.
To quickly set up the complete environment:
Make sure you have Go, kubectl, and docker installed and configured on your dev machine. We will automatically manage other dependencies via Go, including kind.
A Linux host that will run more than about a thousand sandboxes also needs a larger kernel neighbor table (net.ipv4.neigh.default.gc_thresh1/2/3 = 4096/16384/32768); hack/create-kind-cluster.sh warns when the host is at the default of 1024.
Run the following steps:
# create cluster and local registry
hack/create-kind-cluster.sh

# make ate-setup target the kind cluster; set this in every shell that runs
# ate-setup, including for the demo walkthroughs
export ATE_INSTALL_KIND=true

# install Substrate
go run ./cmd/ate-setup deploy ate-system --credential-provider='{"name":"k8s.io"}' \
  --ingress-allowed-spiffe-ids=spiffe://cluster.local/ns/ate-system/sa/atenet-client

# install counter demo
go run ./cmd/ate-setup deploy demo counter

# install kubectl-ate
go install ./cmd/kubectl-ate

# create a counter actor in the demo's atespace (--template names the
# actor template, resolved in the actor's atespace)
kubectl ate create actor my-counter-1 -a ate-demo-counter --template counter

# serve a local proxy on port 8000 that sends requests to the actor through the
# network router
kubectl ate proxy actor my-counter-1 -a ate-demo-counter
[!IMPORTANT]
{"name":"k8s.io"}deploys the bundled credential provider with an empty, default-deny namespace policy. Before an actor can have a credential injected, grant its atespace the namespaces whose Secrets it may read; see Enable it.
curl -X POST -i http://localhost:8000/
You can deploy or cleanup specific Agent Substrate components using
the installation script. See go run ./cmd/ate-setup for all options.
# Re-deploy only ate-apiserver of the ATE system
go run ./cmd/ate-setup deploy apiserver

# Delete everything (core system and all demos)
go run ./cmd/ate-setup delete all
kind resourcesIf you need to delete the local kind cluster and its registry (if it was created by hack/create-kind-cluster.sh):
./hack/delete-kind-cluster.sh
To deploy on Google Kubernetes Engine, follow the official GKE Installation Guide. It lists the prerequisites and gives the one-line installer command. The installer's source and detailed options are in substrate-gke.
We provide several sample applications demonstrating Agent Substrate's capabilities:
ActorTemplates running different binaries share one WorkerPool, even though the templates live in different atespaces.503.kubectl-ate.cmd/ateapi: The core control plane API server exposing gRPC endpoints to manage actor and worker lifecycles.cmd/atelet: A node-level DaemonSet that supervises physical worker pods, coordinates snapshotting, and manages state transfers.cmd/atecontroller: A Kubernetes controller that reconciles WorkerPool custom resources.cmd/ate-idp-server: Serves the OpenID discovery document and key set that relying parties use to verify actor JWTs.cmd/atenet: A combined networking controller providing Envoy routing and proxy sidecars.cmd/ateworker-gvisor: An interior-pod helper running inside sandboxed worker pods to execute runsc checkpoint and restore commands.cmd/ateworker-microvm: The microVM peer of ateworker-gvisor, running actors as cloud-hypervisor VMs.cmd/podcertcontroller: A "polyfill" that provides Pod Certificate signers that
will eventually ship in upstream Kubernetes (with different names).cmd/kubectl-ate: A CLI tool for managing Agent Substrate resources. See its README.cmd/benchmarking: Synthetic workloads used by the load tests, including glutton, which consumes RAM, disk, and file descriptors on demand.demos/: Sample applications demonstrating Agent Substrate capabilities.agent-substrate/substrate is a public repo on GitHub by agent-substrate. Agent Substrate: the core system.
It declares the Apache-2.0 license on GitHub.
Its maker has not tagged a system, so it is unknown here. Its README says what it needs.
Open "Take it" on its page: Take My Repo writes an install plan for your machine and hands it to your AI agent (Claude Code, Codex or Cursor), which asks you before each step. Take My Repo has not tested it on any machine.
Its last change on GitHub was on 2026-11-22. Take My Repo does not judge from that whether it is maintained.
Nobody has reviewed it on Take My Repo yet, which says nothing about its quality.
AutoGPT is the vision of accessible AI for everyone, to use and to build on. Our mission is to provide the tools, so that you can focus on what matters.
Run agents like Hermes, LangChain Deep Agents, and OpenClaw more securely inside NVIDIA OpenShell with managed inference
The agent harness performance optimization system. Skills, instincts, memory, security, and research-first development for Claude Code, Codex, Opencode, Cursor and beyond.
Reverse engineer anything with agents, from app behavior down to native binaries.
Langflow is a powerful tool for building and deploying AI-powered agents and workflows.
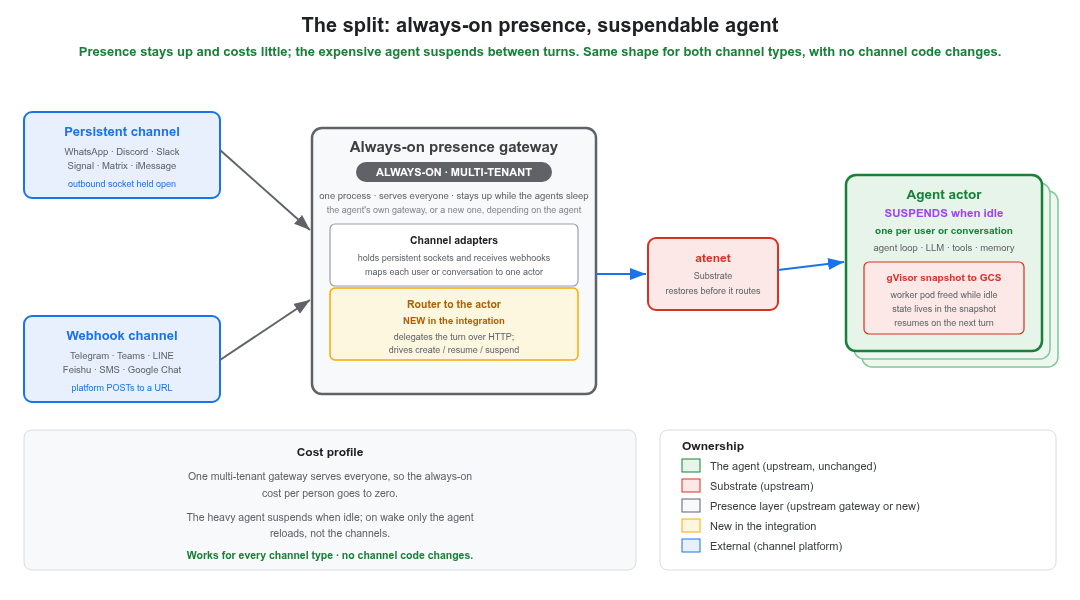
Run always-on messaging agents on Agent Substrate. A multi-tenant gateway holds the channel connections while each conversation runs as a suspendable actor, so presence stays warm and cognition suspends to reclaim compute. Reference implementation built on OpenClaw.