
google-dorking
Dorking: how to find what Google easily showing you (plus Shodan, Yandex, Tor, and more... )
- 122
- 8 mo ago
The maintainer has not written a description at the source.
Repo commit-issues/darkweb-exposure-toolkit, read from GitHub 1 min ago. commit-issues has not joined Take My Repo.
commit-issues/darkweb-exposure-toolkit is a public repo on GitHub by commit-issues. It declares the MIT license on GitHub. It is written mainly in Python, has 1 stars and last changed on 2026-10-05. Nobody has reviewed it on Take My Repo yet, which says nothing about its quality. Read from GitHub on 2026-11-22.

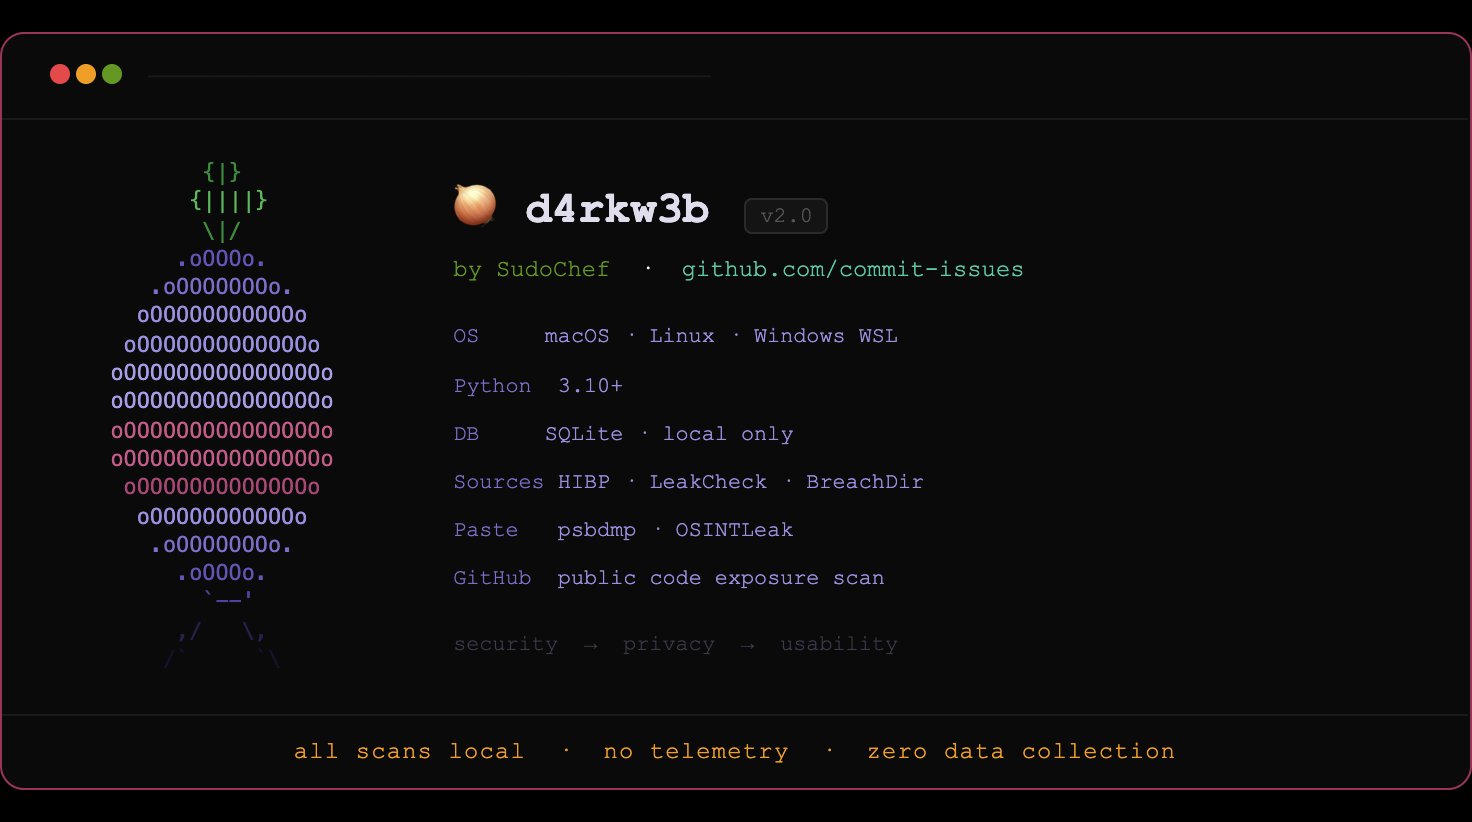
A privacy-first, terminal-based personal data exposure monitor.
Check if your information has been leaked, sold, or exposed — without leaving your terminal, without paying a subscription, and without handing your data to another company in the process.
When you use other sites to check if your data was breached:
d4rkw3b solves all three. Everything runs locally. Results stay on your device. Nothing phones home.
No passwords required. All checks use publicly indexed breach data — the same approach used by Google One, IntelX, and similar services.
| Target | Method | Stored in .env |
|---|---|---|
| Email addresses | HIBP breach lookup | ✅ Yes |
| Usernames | HIBP + GitHub public code scan | ✅ Yes |
| Phone numbers | HIBP breach lookup | ✅ Yes |
| Platform usernames | HIBP + paste sites (Discord, Steam, Reddit, Instagram + more) | Runtime prompt |
| Passwords | k-anonymity — only 5-char hash prefix transmitted, never your full password | Runtime prompt |
| API tokens & keys | Hash-based leak check (HasMySecretLeaked) + optional raw GitHub search | Runtime prompt |
| Layer | Approach |
|---|---|
| Breach checks | HIBP k-anonymity API — only a 5-char SHA-1 hash prefix is transmitted, never your full password |
| Paste site checks | Clearnet only — breach data surfaces on clearnet fast, no dark web access needed or used |
| Local cache | 24hr breach intelligence cache stored in SQLite on your machine — most searches never hit the network |
| Offline mode | Search local cache with zero network exposure after first run |
| Dark web crawling | Not included by design — public breach intelligence is sufficient and legally clean |
Security → Privacy/OPSEC → Usability. That is the order of priority in every decision this tool makes.
The password k-anonymity check uses SHA-1 hashing. This is not a security decision — it is a requirement of the HIBP k-anonymity API protocol. Only the first 5 characters of the hash are ever transmitted. Your full password never leaves your machine. usedforsecurity=False is set explicitly in the code to document this intent.
This tool is built entirely on free, public APIs. No hidden costs. No subscriptions required.
All sources included at time of development use free tiers only. If you need deeper intelligence, see the Premium Tools section below.
| Source | Checks | API Key Required |
|---|---|---|
| HaveIBeenPwned | Email, username, phone — breach history | Yes (free at haveibeenpwned.com/API/Key) |
| LeakCheck | Email, username, phone — 7B+ records | No (free tier) |
| BreachDirectory | Email, username — passwords and hashes | No (free) |
| Emailrep.io | Email — reputation, breach history, social profiles | Yes (free at emailrep.io/key) |
| OSINTLeak | Email, username — stealer logs, dark web forums | Yes (free starter at osintleak.com) |
| psbdmp.ws | Email, username — paste site dumps | No |
| Category | Platforms |
|---|---|
| 🎮 Gaming | Steam, PlayStation Network, Xbox, Roblox, Twitch |
| 💬 Social | Discord, Reddit, Twitter/X, Instagram, TikTok, Facebook, LinkedIn, Snapchat, YouTube, Telegram, Spotify |
| 👩💻 Developer | GitHub |
macOS / Linux:
git clone https://github.com/commit-issues/darkweb-exposure-toolkit.git
cd darkweb-exposure-toolkit
pip3 install -r requirements.txt --break-system-packages
cp .env.example .env
Windows (PowerShell):
git clone https://github.com/commit-issues/darkweb-exposure-toolkit.git
cd darkweb-exposure-toolkit
pip install -r requirements.txt
copy .env.example .env
Open .env in any text editor and fill in your values.
📖 New to this? See the full step-by-step guide: docs/setup.md
HIBP_API_KEY=your_key_here
GITHUB_TOKEN=your_token_here
EMAILS_TO_CHECK=you@example.com
USERNAMES_TO_CHECK=yourusername
PHONES_TO_CHECK=+12125551234
python3 src/run_all_checks.py
Force a cache refresh before scanning:
python3 src/run_all_checks.py --refresh
If you've configured a large number of identifiers (more than 20) and want to proceed anyway:
python3 src/run_all_checks.py --force
Cross-reference everything the tool has already found against your configured identifiers — entirely offline, no network calls, no new API keys.
python3 src/correlate.py
Sorts results into three files under data/correlation/:
| File | Contents |
|---|---|
confirmed.json |
Exact matches |
review.json |
Possible matches worth a manual look (e.g. plus-alias email variants) |
clean.json |
Identifiers with no matches found |
darkweb-exposure-toolkit/ │ ├── .env.example ← Copy to .env, fill in your keys ├── .gitignore ← Protects .env and data/ from commits ├── requirements.txt ├── setup.cfg ← Linter configuration ├── NOTICE ← Attribution — required to keep on forks │ ├── src/ │ ├── run_all_checks.py ← Main entry point │ ├── correlate.py ← Local correlation engine (offline) │ ├── tui.py ← Terminal UI, banner, pulse spinner │ ├── hibp_check.py ← HIBP breach + k-anonymity password check │ ├── github_search.py ← GitHub public code exposure scan │ ├── secret_leak_check.py ← Hash-based API key/token leak check │ ├── platform_check.py ← Platform username checks (Discord, Steam + more) │ ├── breach_scraper.py ← Multi-source breach intelligence scraper │ ├── scheduler.py ← 24hr cache refresh scheduler │ ├── validator.py ← Input validation and sanitization │ ├── notifier.py ← Console output formatter │ ├── db_utils.py ← Local SQLite operations │ ├── init_db.py ← Database setup │ └── verify.py ← Integrity verification │ └── data/ ← Local results DB (gitignored)
data/exposure.db.env file is in .gitignore — it will never be committeddata/exposure.db at any time to wipe all local resultsThese tools are used by law enforcement, private investigators, security researchers, and journalists for deeper investigations. They are not included in this tool — no paid services are ever called without your explicit configuration.
| Tool | Used By | Free Tier | API | Best For |
|---|---|---|---|---|
| IntelX (intelx.io) | Law enforcement, Bellingcat, journalists | 10 results/search | Paid | Dark web indexing, full breach records, historical WHOIS |
| OSINT Industries | 5,000+ law enforcement departments | No | Paid | Real-time social footprint across 1,500+ sources |
| DeHashed | Security researchers, pentesters | Basic only | Paid | Largest breach database — IP, email, username, address |
| Snusbase | Developers, researchers | No | Paid | Fast cleartext passwords, hashes, salts, IPs |
| LeakCheck Pro | OSINT researchers | Limited | Paid | 7B+ records with full credential detail |
| OSINTLeak Pro | Security teams, law enforcement | Free starter | Paid | Stealer logs, continuous monitoring, dark web forums |
Your Discord got compromised and you want to trace it: → Start here (free, local, private) → If you need full credential history: LeakCheck Pro or DeHashed
You're a journalist investigating a public figure: → IntelX for dark web indexing and historical WHOIS → OSINT Industries for social footprint across 1,500+ sources
You're a security researcher doing a full OSINT sweep: → DeHashed + Snusbase for deepest credential coverage
You're a PI or law enforcement: → OSINT Industries (used by 5,000+ departments worldwide) → IntelX for dark web and archived content
You just want to check your personal exposure for free: → This tool. That's what it's for.
| Guide | Link |
|---|---|
| Full setup guide (API keys, step by step) | docs/setup.md |
| GitHub account + SSH setup | secure-your-repo |
| Code audit standards | code-audit |
This tool is for personal security awareness only.
✅ Check your own accounts and credentials ✅ Educational use and learning ✅ Personal OPSEC and exposure monitoring ❌ Do not scan accounts you do not own ❌ Do not use for bulk or automated scanning of others
All source files pass the full audit stack:
black · flake8 · pylint 10/10 · mypy · bandit · pip-audit · detect-secrets · vulture · radon
Dependencies are pinned and CVE-free at time of release.
Original author: SudoCode by SudoChef (commit-issues)
Original repo: https://github.com/commit-issues/darkweb-exposure-toolkit
Created: April 2025
If you fork or build upon this work, you are required to retain the NOTICE file and original copyright notice in LICENSE per MIT License terms. Authorship is embedded in the source code, database, and signed git history.
MIT — see LICENSE.
Built by SudoCode
Security first. Privacy always.
commit-issues/darkweb-exposure-toolkit is a public repo on GitHub by commit-issues. Its maker has not written a description.
It declares the MIT license on GitHub.
Its maker tagged it for macOS, Windows and Linux, or as Docker or cross-platform. That is declared by the maker; Take My Repo has not tested it.
Open "Take it" on its page: Take My Repo writes an install plan for your machine and hands it to your AI agent (Claude Code, Codex or Cursor), which asks you before each step. Take My Repo has not tested it on any machine.
Its last change on GitHub was on 2026-10-05. GitHub counts 1 open issue and pull requests. Take My Repo does not judge from that whether it is maintained.
Dorking: how to find what Google easily showing you (plus Shodan, Yandex, Tor, and more... )
Nobody has reviewed it on Take My Repo yet, which says nothing about its quality.
Cyber Pantry — a Cyber Resource library of 325+ free cybersecurity resources, by SudoChef.
A clean nmap reference guide for CTF and professionals who don't want to keep googling nmap commands at 2AM. This will be the bookmark you actually use! . Part of the SudoChef's Pentesting Methodology Guide.
A simple but in-depth field guide for securing your GitHub presence, repositories, identity, and code.
Stop shipping AI slop. A simple code quality & security audit pipeline for every file, every time. Star it. You'll want it later.
Security Operations Dashboard - ETL pipeline analyzing 100+ incidents with interactive visualizations. Demonstrates Python, SQL, data visualization, and project management skills.