syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
- 9.9k
- Go
- Apache-2.0
- 4 d ago
Profile, templates, documentation and issue tracking for sbomify
Repo sbomify/.github, read from GitHub 48 min ago. sbomify has not joined Take My Repo.
sbomify/.github is a public repo on GitHub by sbomify. Profile, templates, documentation and issue tracking for sbomify. It declares the Apache-2.0 license on GitHub. It has 0 stars and last changed on 2025-07-24. Nobody has reviewed it on Take My Repo yet, which says nothing about its quality. Read from GitHub on 2026-11-21.
GitHub is limiting requests or did not answer. The facts on this page still come from the last successful read.
Open on GitHubsbomify/.github is a public repo on GitHub by sbomify. Profile, templates, documentation and issue tracking for sbomify.
It declares the Apache-2.0 license on GitHub.
Its maker has not tagged a system, so it is unknown here. Its README says what it needs.
Open "Take it" on its page: Take My Repo writes an install plan for your machine and hands it to your AI agent (Claude Code, Codex or Cursor), which asks you before each step. Take My Repo has not tested it on any machine.
Its last change on GitHub was on 2025-07-24. Take My Repo does not judge from that whether it is maintained.
Nobody has reviewed it on Take My Repo yet, which says nothing about its quality.
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
A suite of tools to automate software compliance checks.
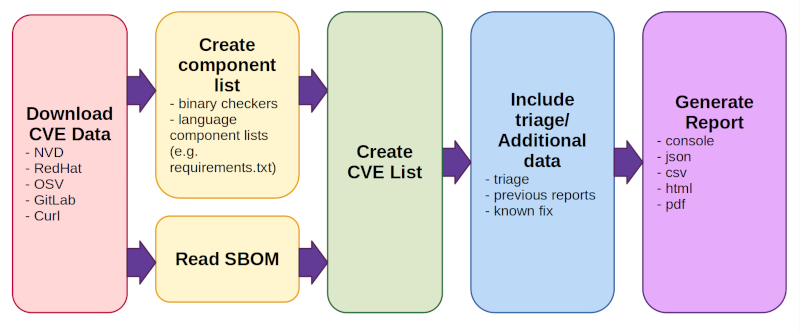
The CVE Binary Tool helps you determine if your system includes known vulnerabilities. You can scan binaries for over 350 common, vulnerable components (openssl, libpng, libxml2, expat and others), or if you know the components used, you can get a list of known vulnerabilities associated with an SBOM or a list of components and versions.
Dependency-Track is an intelligent Component Analysis platform that allows organizations to identify and reduce risk in the software supply chain.
LunaSec - Dependency Security Scanner that automatically notifies you about vulnerabilities like Log4Shell or node-ipc in your Pull Requests and Builds. Protect yourself in 30 seconds with the LunaTrace GitHub App: https://github.com/marketplace/lunatrace-by-lunasec/
A tool to automatically build a dependency graph and Software Bill of Materials (SBOM) for packages and arbitrary source code repositories.
SBOM generation, enrichment, and management for CI/CD. CycloneDX & SPDX, from lockfiles or containers.
A repository for testing various SBOM tools and benchmark them against each other.