
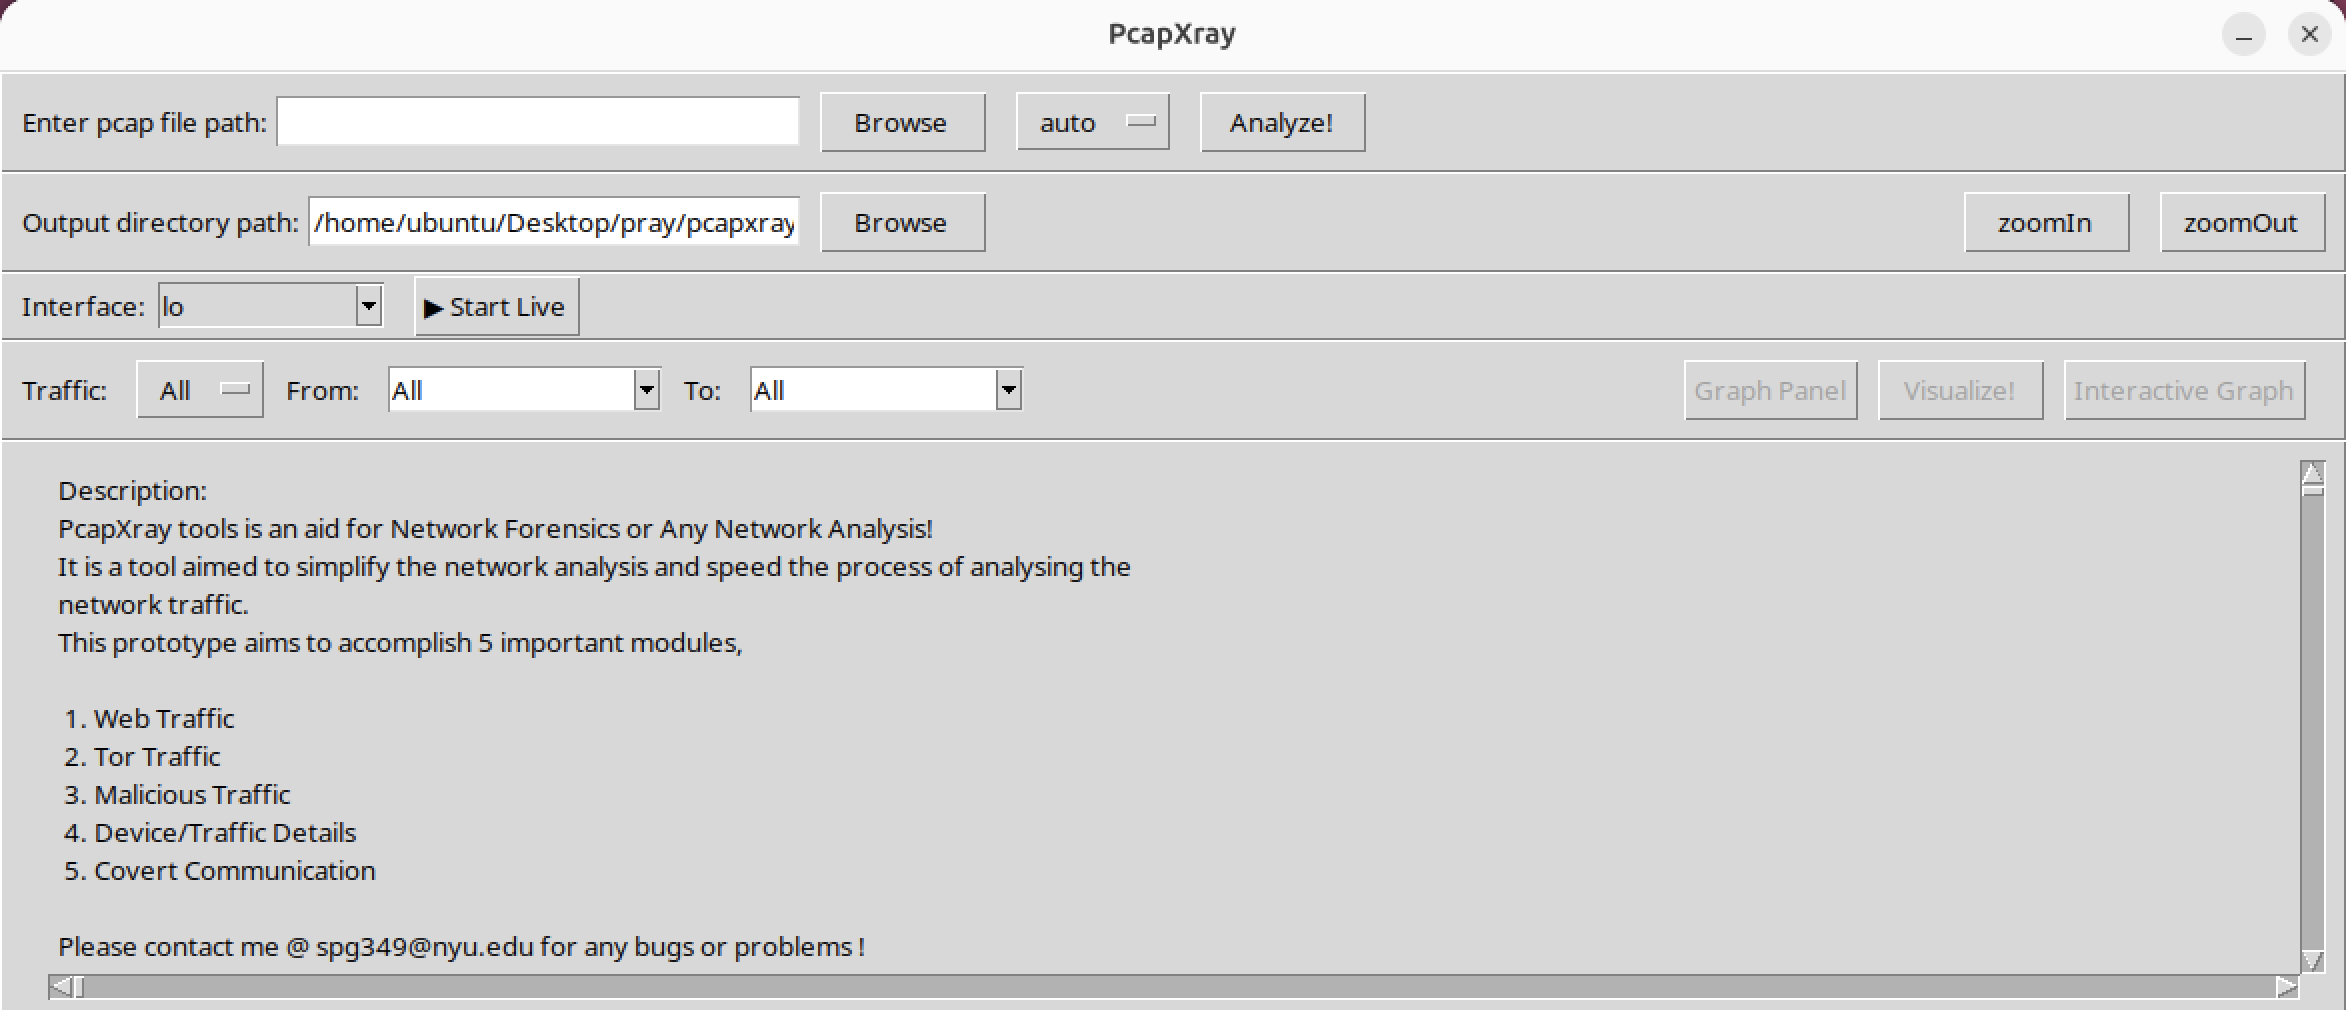
PcapXray
:snowflake: PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight important communication and file extraction
- 1.9k
- Python
- GPL-2.0
- 7 mo ago
An Anti Forensics Project - Concept: File Obfuscation
Repo srixivas/FileCrapper, read from GitHub 3 h ago. srixivas has not joined Take My Repo.
srixivas/FileCrapper is a public repo on GitHub by srixivas. An Anti Forensics Project - Concept: File Obfuscation. It declares the MIT license on GitHub. It has 0 stars and last changed on 2018-02-25. Nobody has reviewed it on Take My Repo yet, which says nothing about its quality. Read from GitHub on 2026-11-22.
srixivas/FileCrapper is a public repo on GitHub by srixivas. An Anti Forensics Project - Concept: File Obfuscation.
It declares the MIT license on GitHub.
Its maker has not tagged a system, so it is unknown here. Its README says what it needs.
Open "Take it" on its page: Take My Repo writes an install plan for your machine and hands it to your AI agent (Claude Code, Codex or Cursor), which asks you before each step. Take My Repo has not tested it on any machine.
Its last change on GitHub was on 2018-02-25. Take My Repo does not judge from that whether it is maintained.
Nobody has reviewed it on Take My Repo yet, which says nothing about its quality.
:snowflake: PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight important communication and file extraction
:pencil: urlRecon - Info Gathering or Recon tool for Urls -> Retrieves * Whois information of the domain * DNS Details of the domain * Server Fingerprint * IP geolocation of the server
:printer: :label: App development for Brother printer using Flutter :label: :printer:
:eyes::blue_book::pencil::thought_balloon::blue_book: Research, Study and Learning of Algorithms, ProblemSolving, ProgrammingLanguages
A Forensics Mini Project - File Recovery Tool that extracts Images and PDF from the memory dump image
:eyes::blue_book::pencil::thought_balloon::blue_book: Computer Security Nuggets -- > Ctf writeups + Explore, Research, Study, Fun and Learning Security


