Active-Directory-Exploitation-Cheat-Sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
- 6.8k
- MIT
- 6 mo ago
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
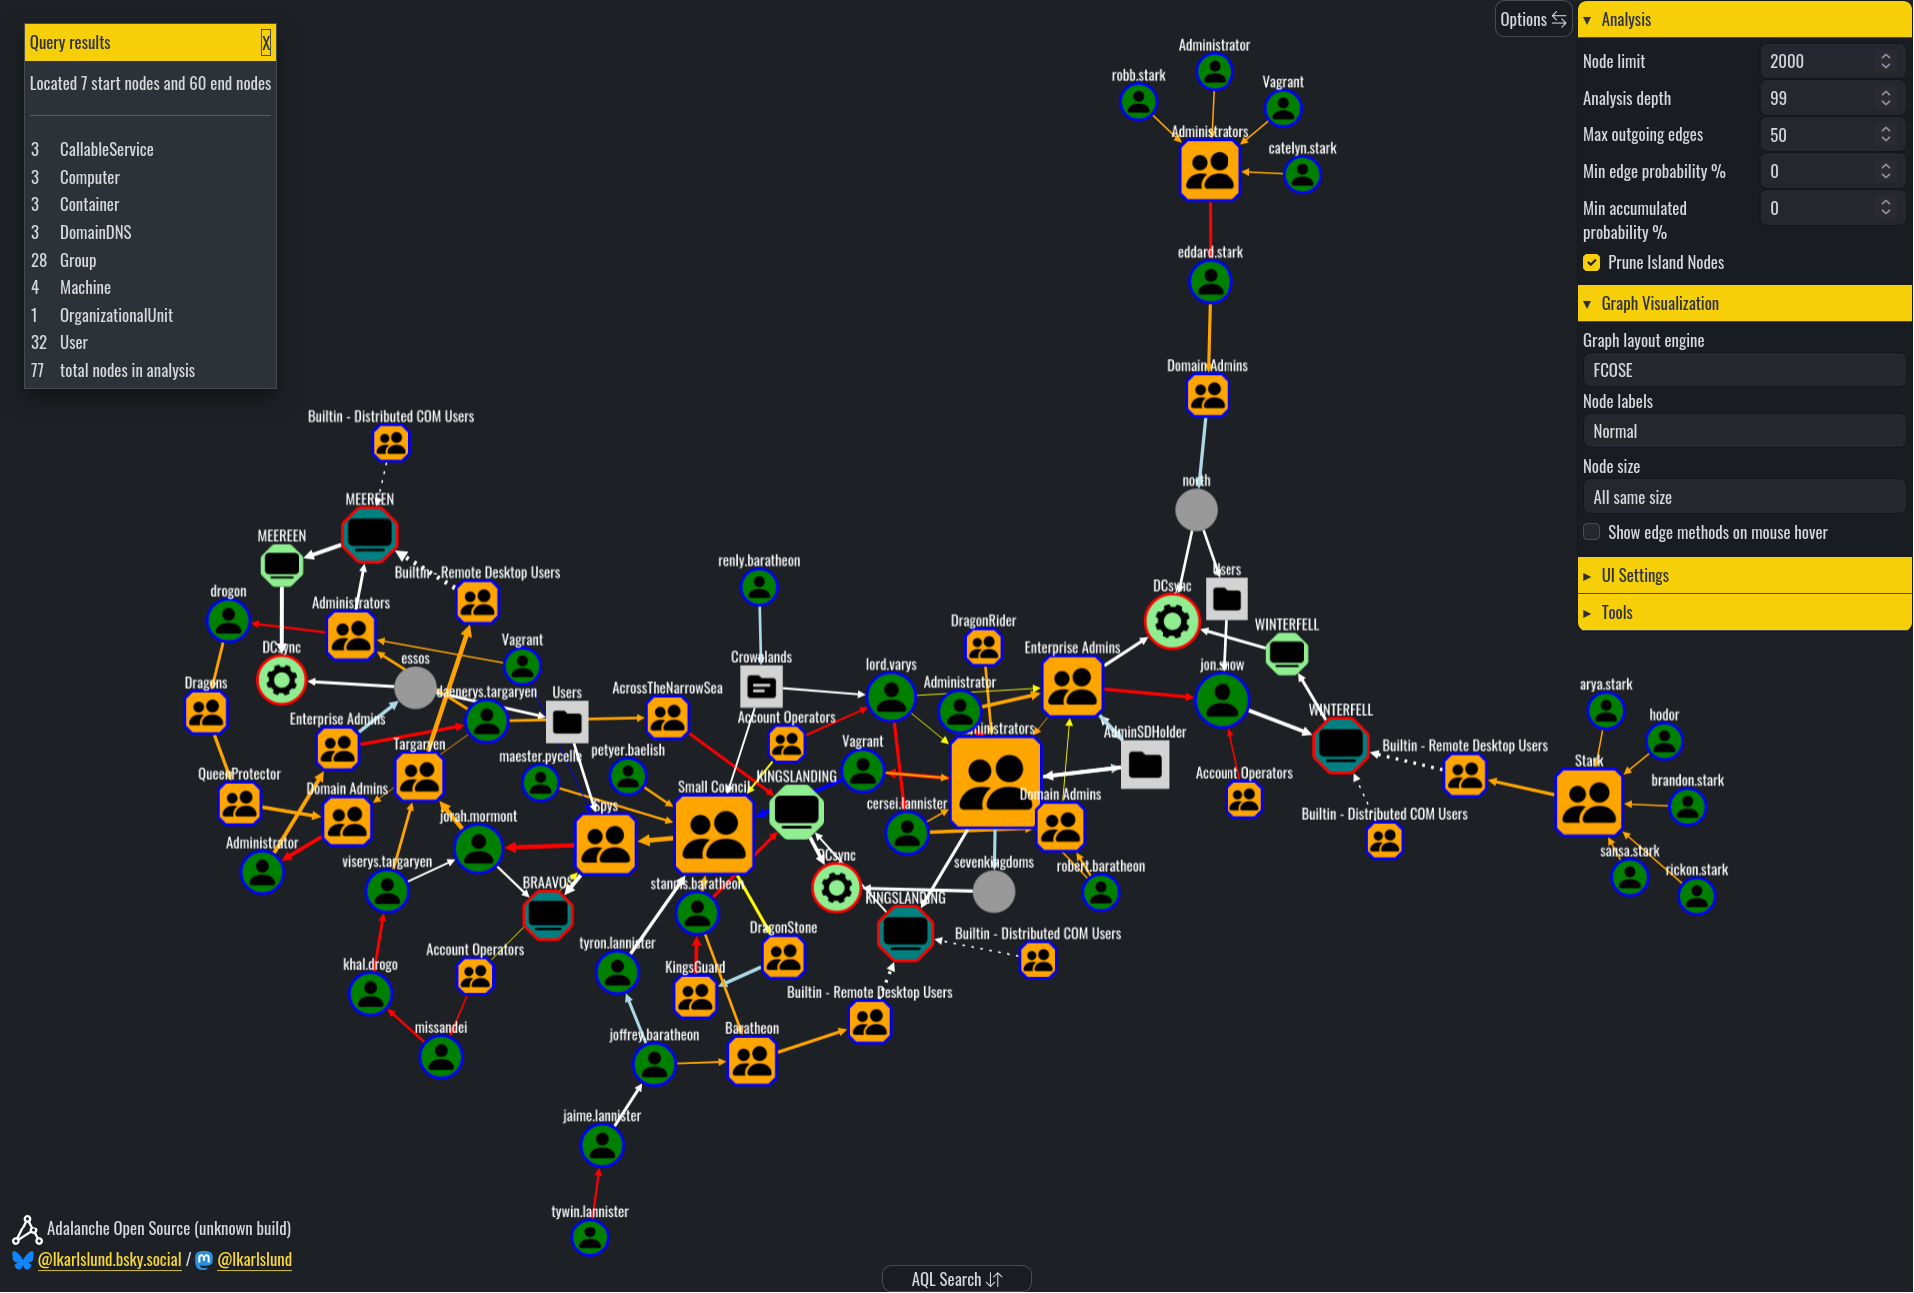
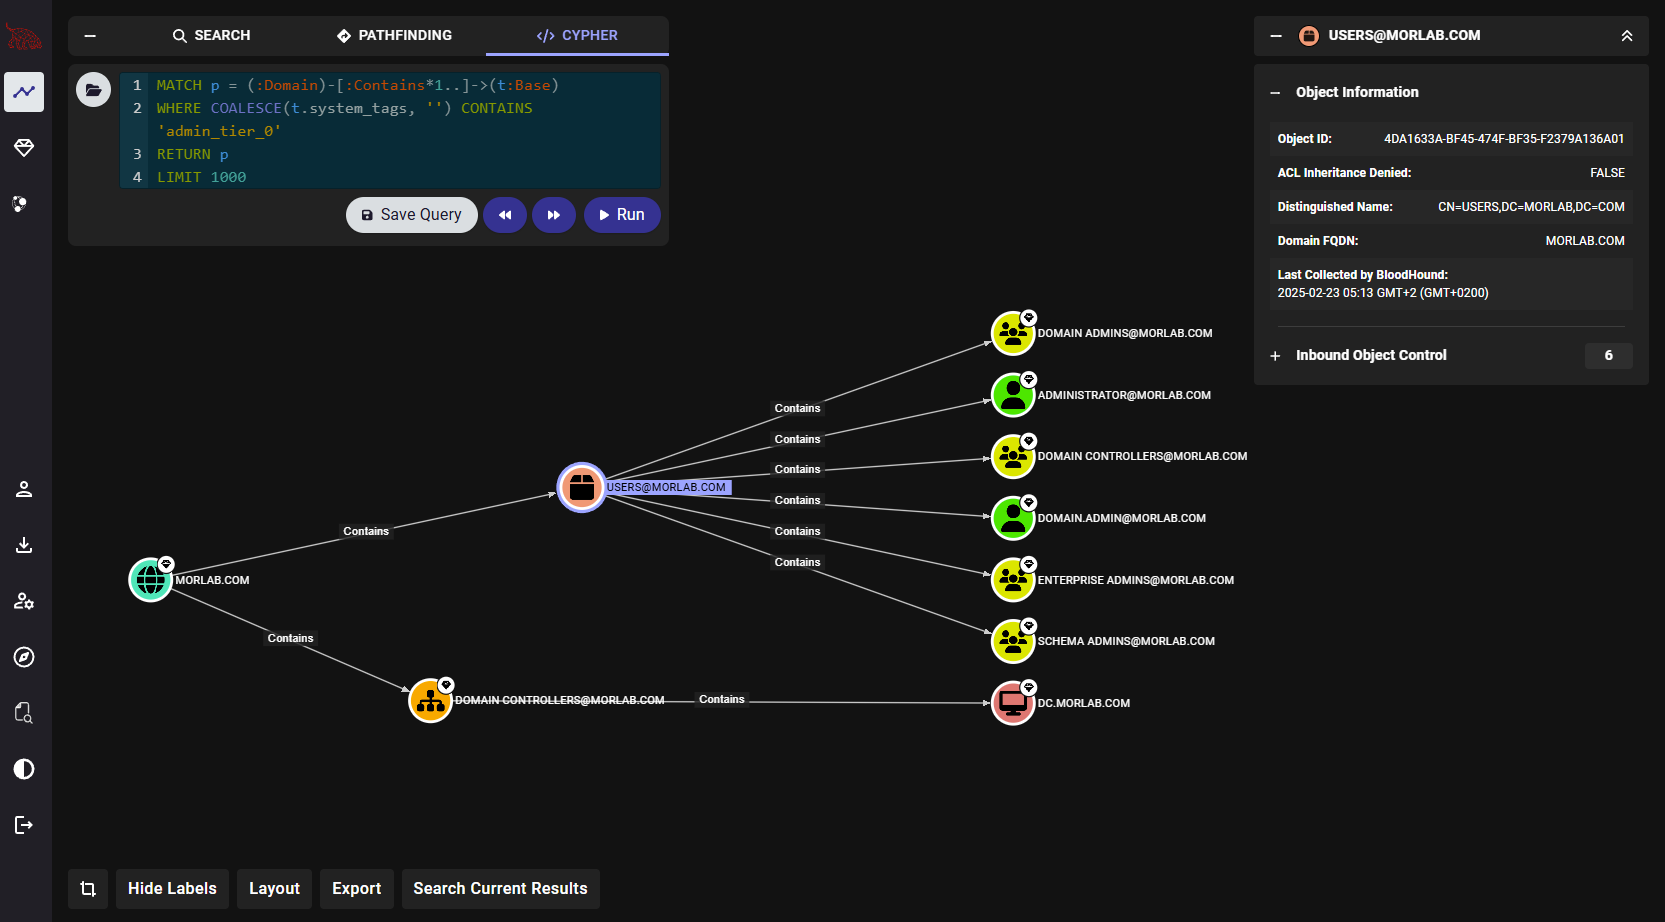
Attack Graph Visualizer and Explorer (Active Directory) ...Who's *really* Domain Admin?
Group Policy Eater is a PowerShell module that aims to gather information about Group Policies but also allows fixing issues that you may find in them.
A list of vulnerabilities or design flaws that Microsoft does not intend to fix. Since the number is growing, I decided to make a list. This list covers only vulnerabilities that came up in July 2021 (and SpoolSample ;-))
Pentesting and Bug Bounty Notes, Cheetsheets and Guide for Ethical Hacker, Whitehat Pentesters and CTF Players.
Windows Event Log tooling for PowerShell and .NET: typed queries, reporting, export, WEC, automation, and the PSEventViewer module.
This cheat sheet outlines common enumeration and attack methods for Windows Active Directory using PowerShell.
A lightweight tool to quickly extract valuable information from the Active Directory environment for both attacking and defending.
Hekatomb is a python script that connects to LDAP directory to retrieve all computers and users informations. Then it will download all DPAPI blob of all users from all computers and uses Domain backup keys to decrypt them.
Uses Sharphound, Bloodhound and Neo4j to produce an actionable list of attack paths for targeted remediation.
This module contains DSC resources for deployment and configuration of Active Directory Domain Services.
A flexible proxy for inspecting & transforming LDAP packets generated by any tool on the fly.
A Network Enumeration and Attack Toolset for Windows Active Directory Environments.
IdentityServer4 Ldap Extension (OpenLdap or ActiveDirectory)
PowerShell module to interact with Active Directory using ADSI and the System.DirectoryServices namespace (.NET Framework)
Enumerate AD through LDAP with a collection of helpfull scripts being bundled
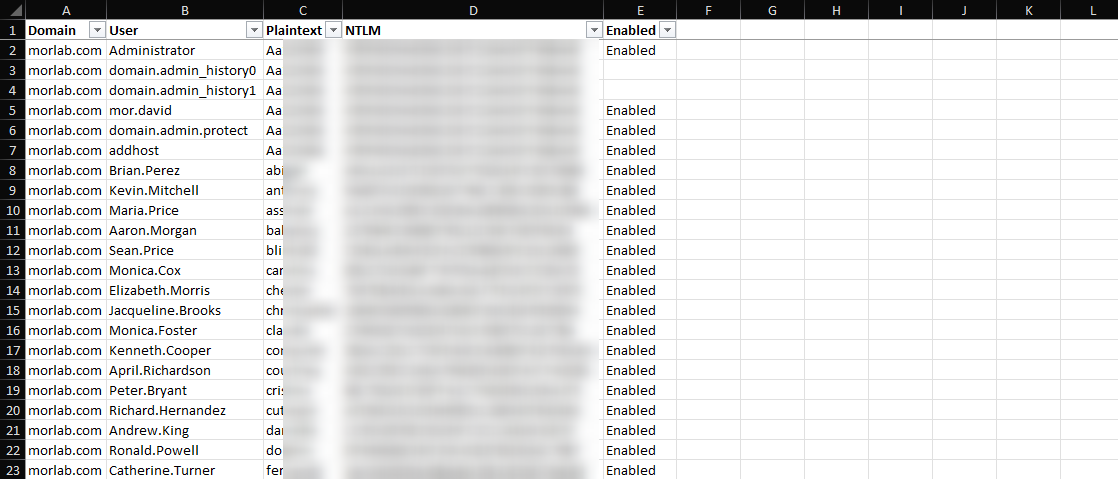
This script analyzes the DCSync output file from several tools (such as Mimikatz, Secretsdump and SharpKatz...)
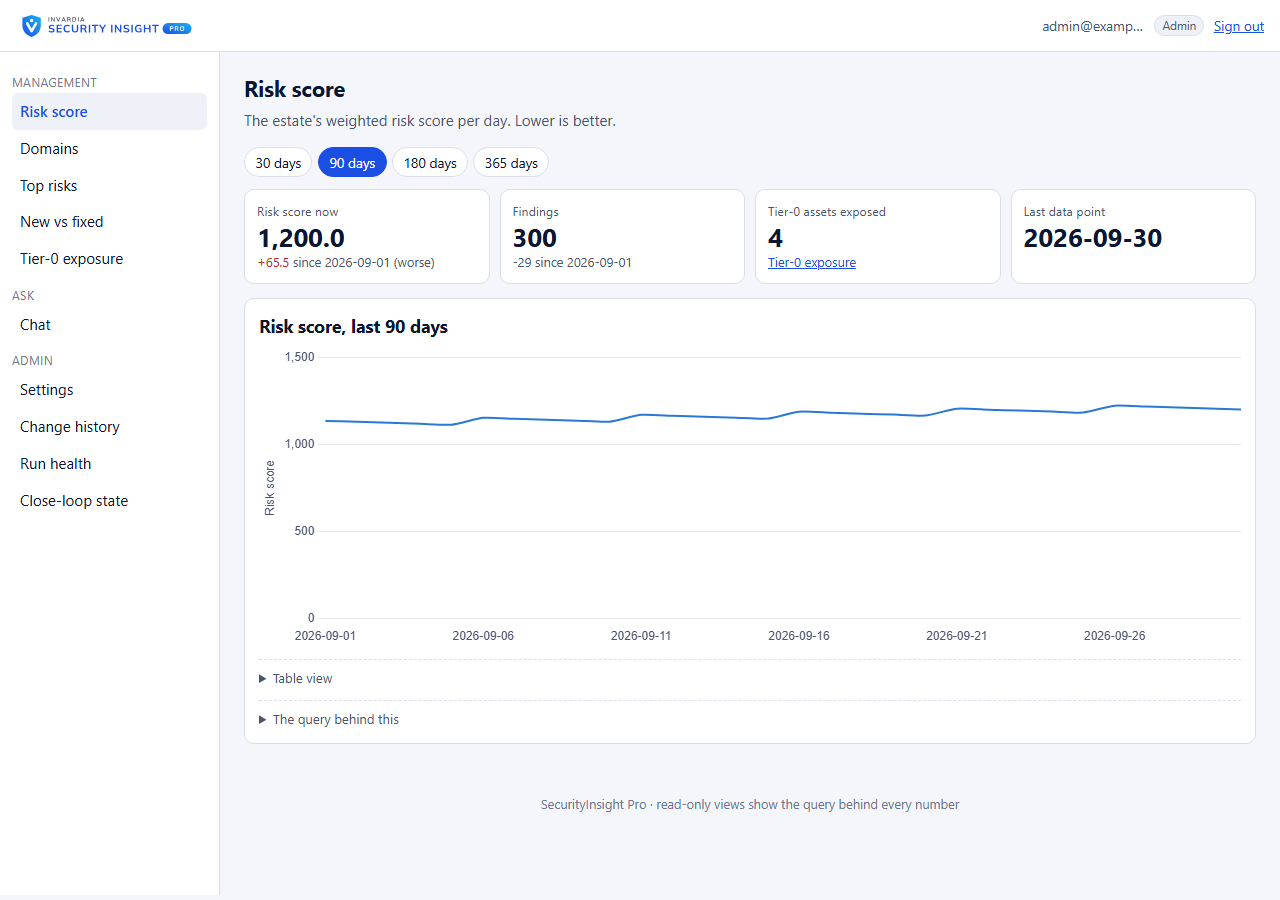
Rethink Secure Score: risk-based scoring across Defender XDR, Entra, AD, Azure, ExposureGraph, and Shodan — weighted by consequence, Tier 0–3 criticality, and risk factors. Fix what attackers reach for first. Asset profiling, ready-to-use reports, executive summary. Zero footprint, MVP-built, free.
A small Powershell script that disables all the Active Directory user accounts inactive for more than X days.