adversarial-robustness-toolbox
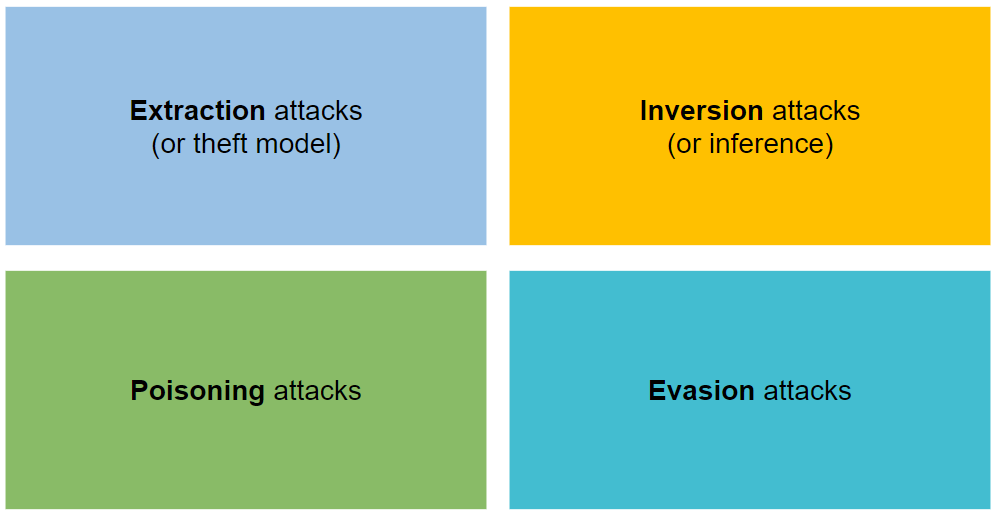
Adversarial Robustness Toolbox (ART) - Python Library for Machine Learning Security - Evasion, Poisoning, Extraction, Inference - Red and Blue Teams
- 6.3k
- Python
- MIT
- 8 d ago
Adversarial Robustness Toolbox (ART) - Python Library for Machine Learning Security - Evasion, Poisoning, Extraction, Inference - Red and Blue Teams
Fawkes, privacy preserving tool against facial recognition systems. More info at https://sandlab.cs.uchicago.edu/fawkes
TextAttack 🐙 is a Python framework for adversarial attacks, data augmentation, and model training in NLP https://textattack.readthedocs.io/en/master/
A curated list of useful resources that cover Offensive AI.
A curated list of adversarial attacks and defenses papers on graph-structured data.
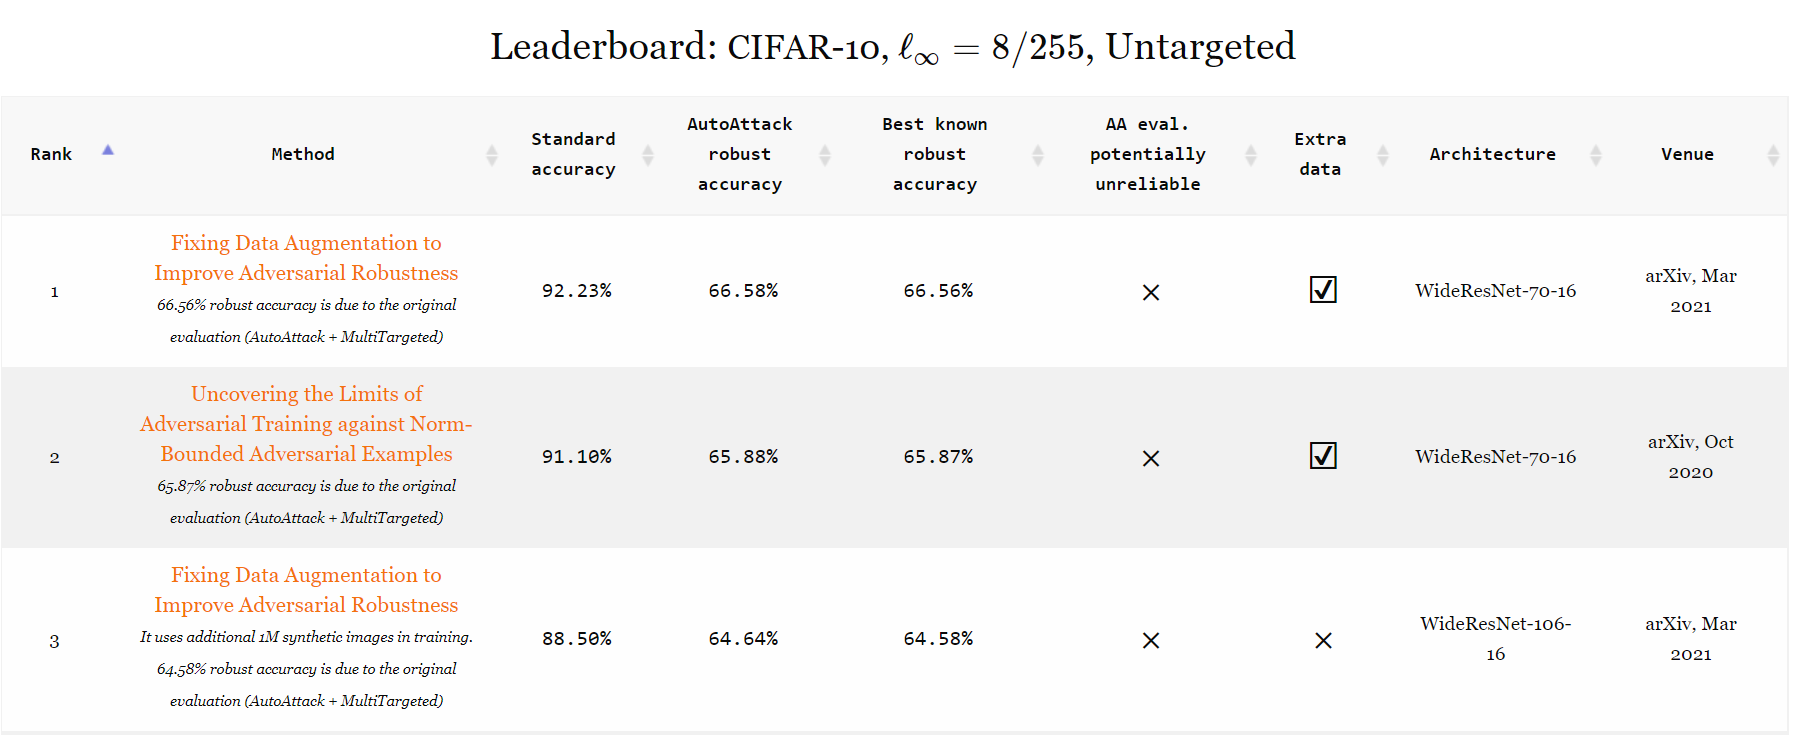
RobustBench: a standardized adversarial robustness benchmark [NeurIPS 2021 Benchmarks and Datasets Track]
Papers and resources related to the security and privacy of LLMs 🤖
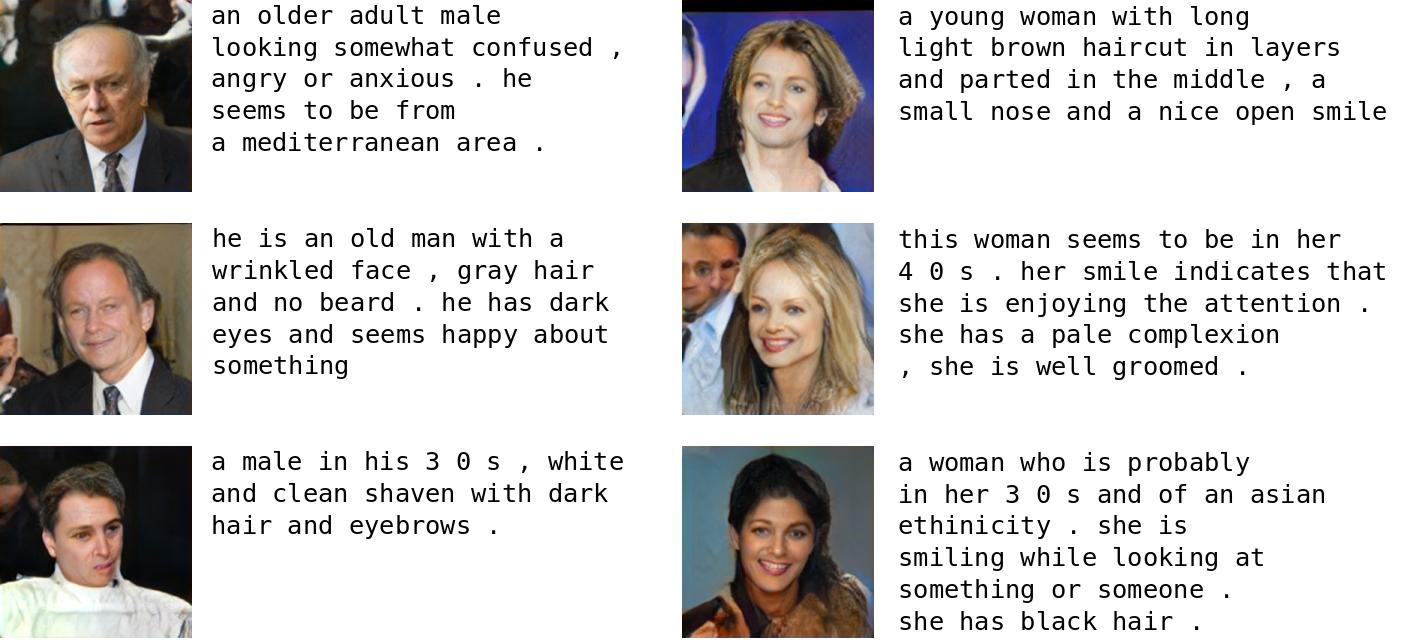
Unofficial PyTorch implementation of the paper titled "Progressive growing of GANs for improved Quality, Stability, and Variation"
A Python library for adversarial machine learning focusing on benchmarking adversarial robustness.
⚡ Vigil ⚡ Detect prompt injections, jailbreaks, and other potentially risky Large Language Model (LLM) inputs
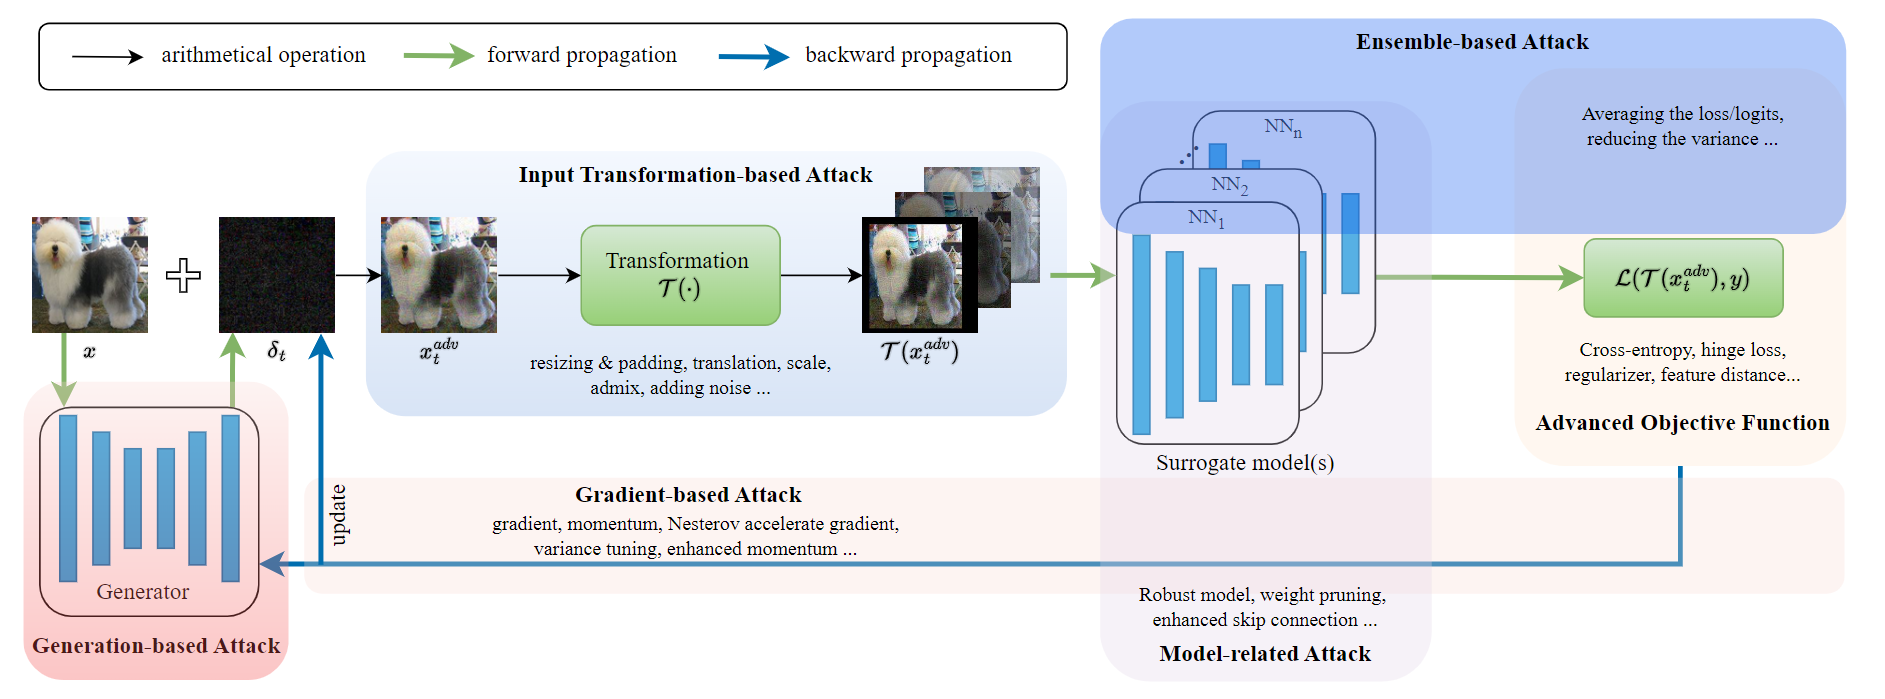
TransferAttack is a pytorch framework to boost the adversarial transferability for image classification.
A curated list of MLSecOps tools and resources for securing machine learning and AI systems - adversarial ML defense, LLM security, AI red teaming, model scanning, supply-chain protection, and MLOps pipeline security.
Security and Privacy Risk Simulator for Machine Learning (arXiv:2312.17667)
auto_LiRPA: An Automatic Linear Relaxation based Perturbation Analysis Library for Neural Networks and General Computational Graphs
💡 Adversarial attacks on explanations and how to defend them
Hack AI/ML applications — CTF challenges for model attacks, LLMs and AI Agent exploitation.
Create adversarial attacks against machine learning Windows malware detectors
A curated list of papers on adversarial machine learning (adversarial examples and defense methods).
A Python library for Secure and Explainable Machine Learning
This repository explores the variety of techniques and algorithms commonly used in deep learning and the implementation in MATLAB and PYTHON
Physical adversarial attack for fooling the Faster R-CNN object detector
MSG-GAN: Multi-Scale Gradients GAN (Architecture inspired from ProGAN but doesn't use layer-wise growing)
Adversarial Machine Learning (AML) Capture the Flag (CTF)
Ethicore Engine® is an AI safety, ethics, and compliance platform. This repo consists of the open-source components of Ethicore Engine™ - Guardian SDK; designed to protect your AI applications from prompt injection, jailbreaks, role hijacking, system-prompt extraction, and 100+ additional threat categories through a multi-layer analysis pipeline
A curated collection of adversarial attack and defense on recommender systems.
SHIELD: Fast, Practical Defense and Vaccination for Deep Learning using JPEG Compression
This repository includes code for the AutoML-based IDS and adversarial attack defense case studies presented in the paper "Enabling AutoML for Zero-Touch Network Security: Use-Case Driven Analysis" published in IEEE Transactions on Network and Service Management.
This repository serves as a comprehensive resource for integrating machine learning with security operations, offering innovative cybersecurity strategies. It features a mix of practical code examples, insightful research, and valuable resources tailored for advancing AI/ML cyber security practices.