K8tools
K8工具集(内网渗透/提权工具/远程溢出/漏洞利用/端口扫描/密码破解/免杀/Exploit/RCE/LPE/0day/Shellcode/Payload/BypassUAC/OverFlow/WebShell/PenTest/hacking(Struts2/Zimbra/Weblogic/Tomcat/Apache/Jboss/DotNetNuke/zabbix)
- 6.3k
- PowerShell
- MIT
- 1 d ago
K8工具集(内网渗透/提权工具/远程溢出/漏洞利用/端口扫描/密码破解/免杀/Exploit/RCE/LPE/0day/Shellcode/Payload/BypassUAC/OverFlow/WebShell/PenTest/hacking(Struts2/Zimbra/Weblogic/Tomcat/Apache/Jboss/DotNetNuke/zabbix)
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port scanning; Fuzz, HW, awesome BugBounty( ͡° ͜ʖ ͡°)...
Ladon大型内网渗透扫描器,PowerShell、Cobalt Strike插件、内存加载、无文件扫描。含端口扫描、服务识别、网络资产探测、密码审计、高危漏洞检测、漏洞利用、密码读取以及一键GetShell,支持批量A段/B段/C段以及跨网段扫描,支持URL、主机、域名列表扫描等。网络资产探测32种协议(ICMP\NBT\DNS\MAC\SMB\WMI\SSH\HTTP\HTTPS\Exchange\mssql\FTP\RDP)或方法快速获取目标网络存活主机IP、计算机名、工作组、共享资源、网卡地址、操作系统版本、网站、子域名、中间件、开放服务、路由器、交换机、数据库、打印机等,大量高危漏洞检测模块MS17010、Zimbra、Exchange
Ladon for Kali 全平台开源内网渗透扫描器,Windows/Linux/Mac/路由器内网渗透,使用它可轻松一键批量探测C段、B段、A段存活主机、高危漏洞检测MS17010、SmbGhost,远程执行SSH/Winrm,密码爆破SMB/SSH/FTP/Mysql/Mssql/Oracle/Winrm/HttpBasic/Redis,端口扫描服务识别PortScan指纹识别/HttpBanner/HttpTitle/TcpBanner/Weblogic/Oxid多网卡主机,端口扫描服务识别PortScan。
Ladon 911 for Cobalt Strike & Cracked Download,Large Network Penetration Scanner, vulnerability / exploit / detection / MS17010 / password/brute-force/psexec/atexec/sshexec/webshell/smbexec/netcat/osscan/netscan/struts2Poc/weblogicExp
A variant of the Largest Area Fit First (LAFF) algorithm + brute force algorithm
A simple multi-threaded distributed SSH brute-forcing tool written in Python
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative with native nerva/naabu pipeline integration.
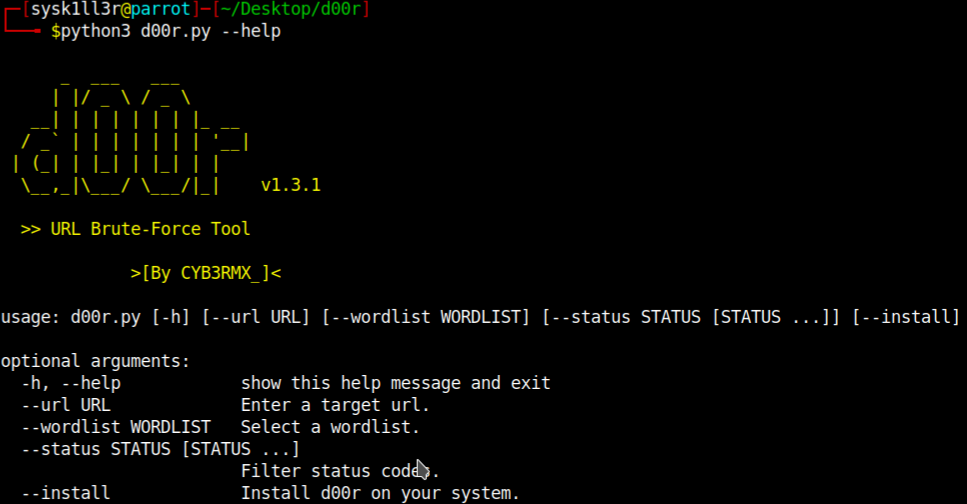
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
Relational database brute force and post exploitation tool for MySQL and MSSQL
🚀 This is a collection of hacking🔥 and pentesting 🧐 scripts to help with enumeration, OSINT, exploitation and post exploitation automated scripts to make hacking easier🌠. Have fun!😎
Some of the projects i made when starting to learn c#, winfroms and wpf
A tool to crack a wifi password using wordlist. The Wordlists contains over 100K commonly used passwords
[ igbf ]: Instagram Brute Forcer --easy-to-use --cross-platform --open-source --no-extl-lib-req
Mimicry is a dynamic deception tool that actively deceives an attacker during exploitation and post-exploitation.
Highly customizable low-interaction experimental honeypot that mimics specific hosts.
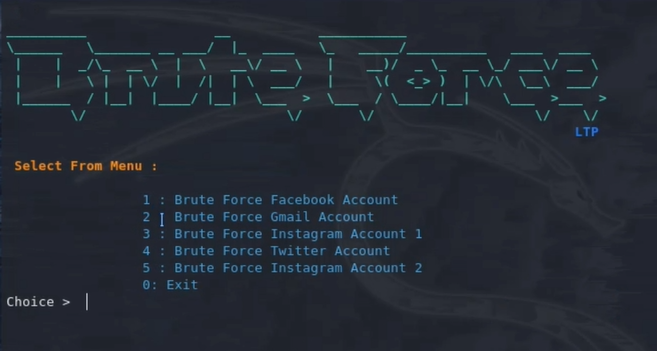
This is small python code based on educational purposes with new password list 2022 . It will check a correct password from a long wordlist. Facebook BruteForce. use the git : https://github.com/emhash/Pass-Tester
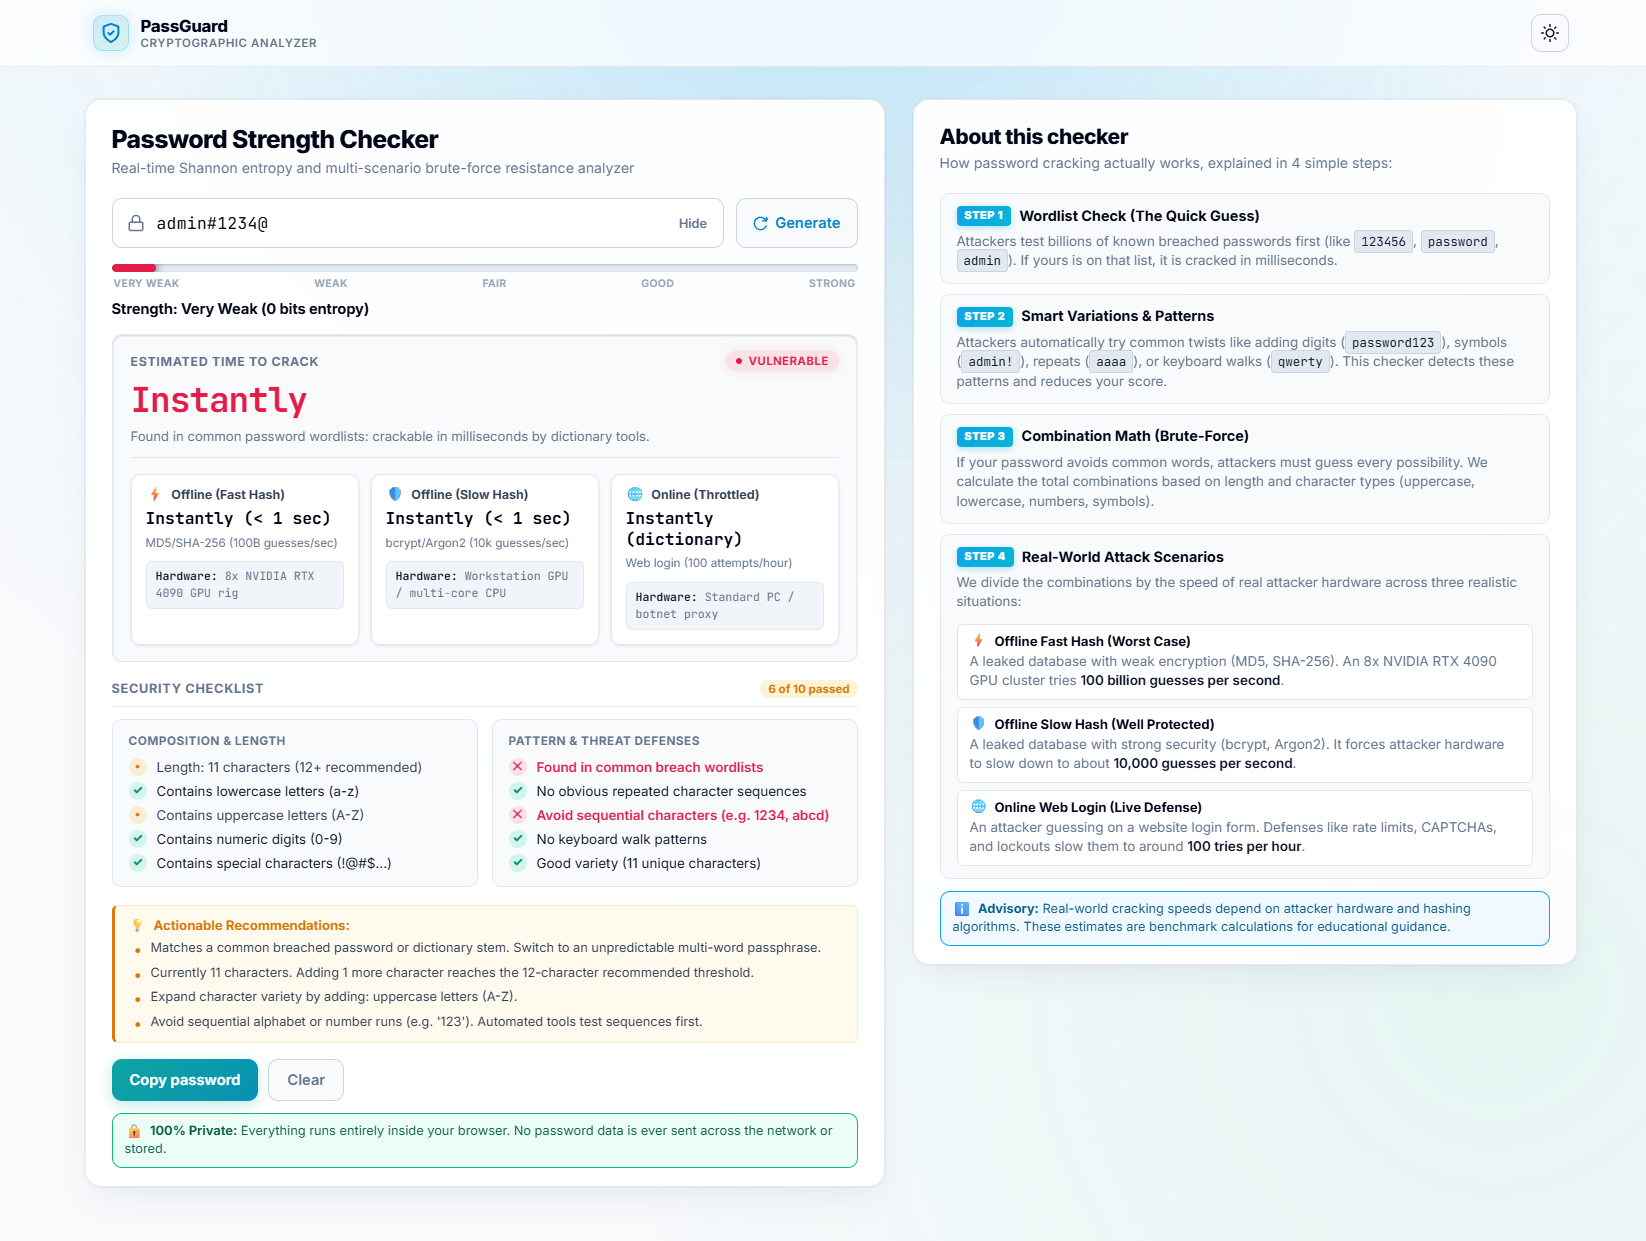
Real-time client-side password strength and entropy analyzer. Calculates Shannon entropy, detects repeated patterns and keyboard walks, and models brute-force cracking speeds across modern GPU clusters, hardened slow hashes, and throttled web logins. Includes a secure CSPRNG generator. 100% in-browser with zero dependencies.
Demos of some algorithms & data structures in C++ using dummy command line apps.
BruteforceLab2 is a self-contained, hands-on web security lab that demonstrates credential brute-force attacks and basic defenses. It includes a Flask login app, a CLI attacker simulator, optional in-memory rate limiting and lockout, automated tests and CI, and configuration knobs (rate window/max, enforce regex). Run locally to observe attacks, to