keycloak
Open Source Identity and Access Management For Modern Applications and Services
- 38k
- Java
- Apache-2.0
- 5 h ago
Open Source Identity and Access Management For Modern Applications and Services
Modern Confluence alternative designed for internal & external docs, built with Go + EmberJS
Container auto-configurations for Spring Boot based integration tests
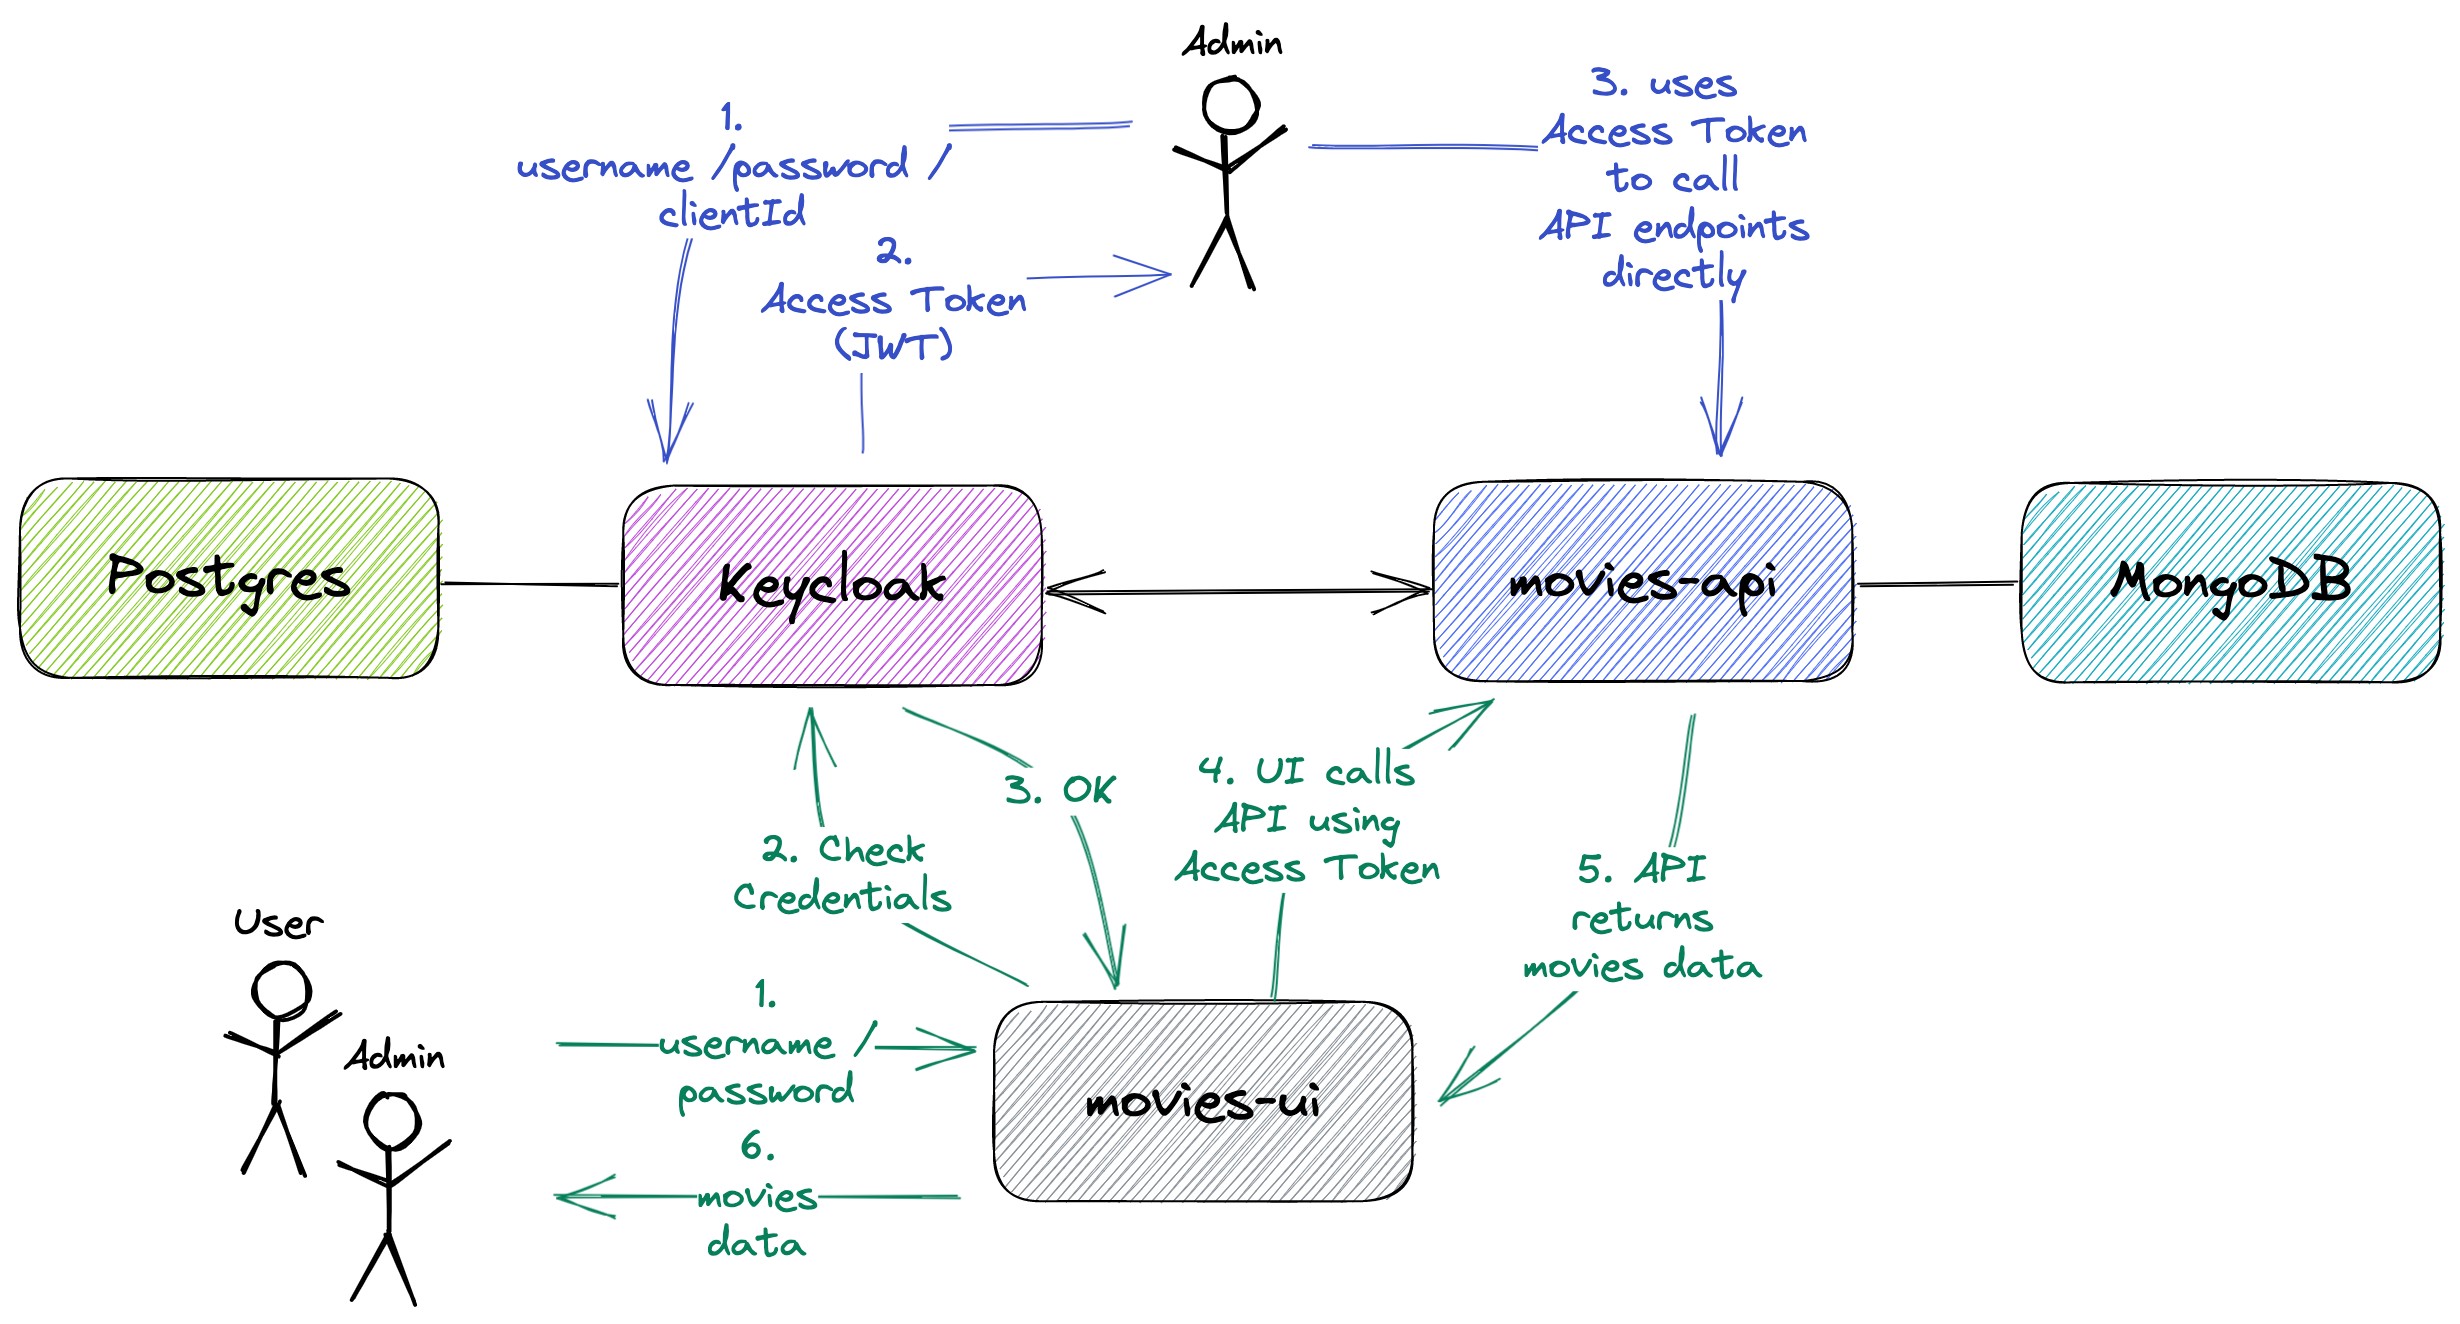
The goal of this project is to secure movies-app using Keycloak (with PKCE). movies-app consists of two applications: one is a Spring Boot Rest API called movies-api and another is a React application called movies-ui.
My Collection of Docker Compose Files. Use "make up" to test it.
Multi-service banking application built with Spring Boot, Eureka, Spring Cloud Gateway, Keycloak, and MySQL. Learning project — see the Arya Banking org for the event-driven platform.
YouTube Spring Boot Microservices Course Application
Keycloak-Clustered extends quay.io/keycloak/keycloak official Keycloak Docker image by adding JDBC_PING discovery protocol.
Keycloak client and admin provider for Nest.js applications with built-in User Managed Access (UMA) and ACL support.
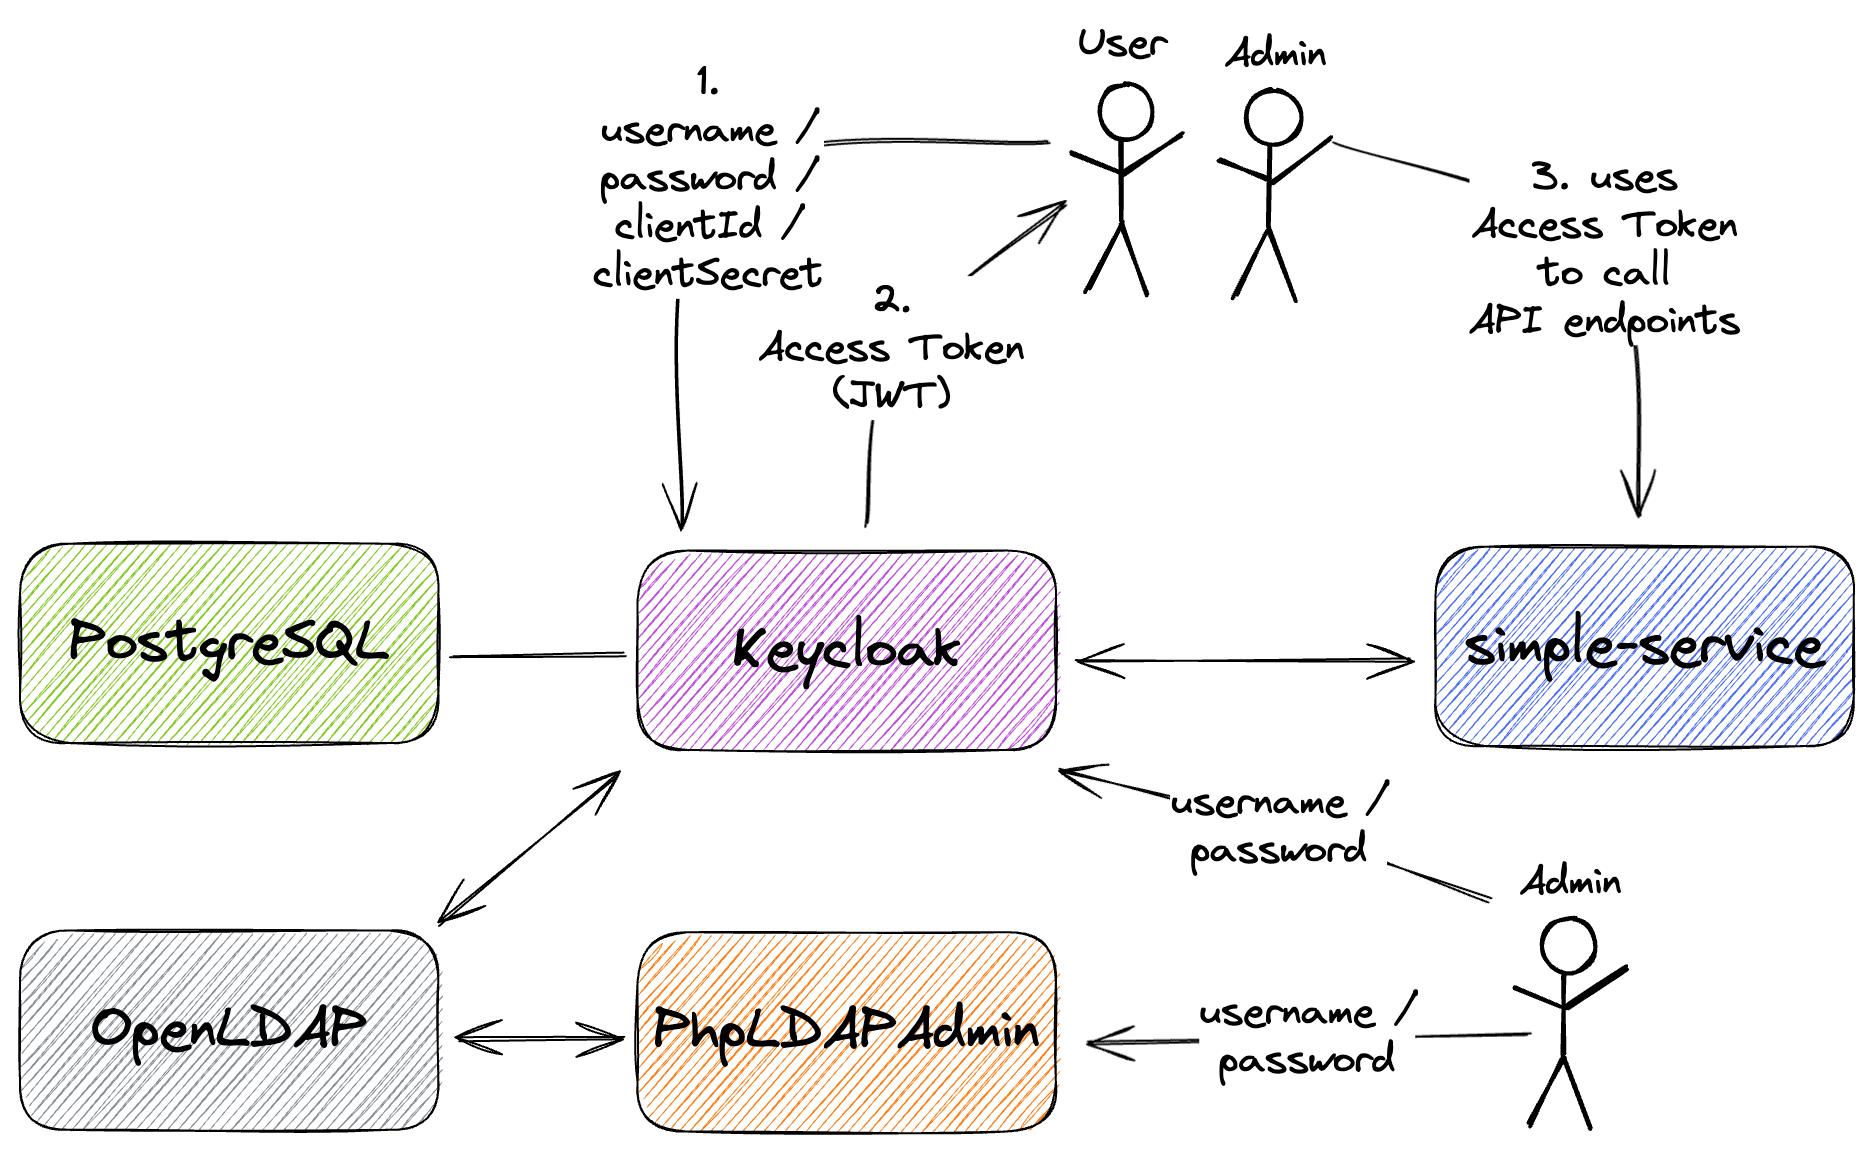
The goal of this project is to create a simple Spring Boot REST API, called simple-service, and secure it with Keycloak. Furthermore, the API users will be loaded into Keycloak from OpenLDAP server.
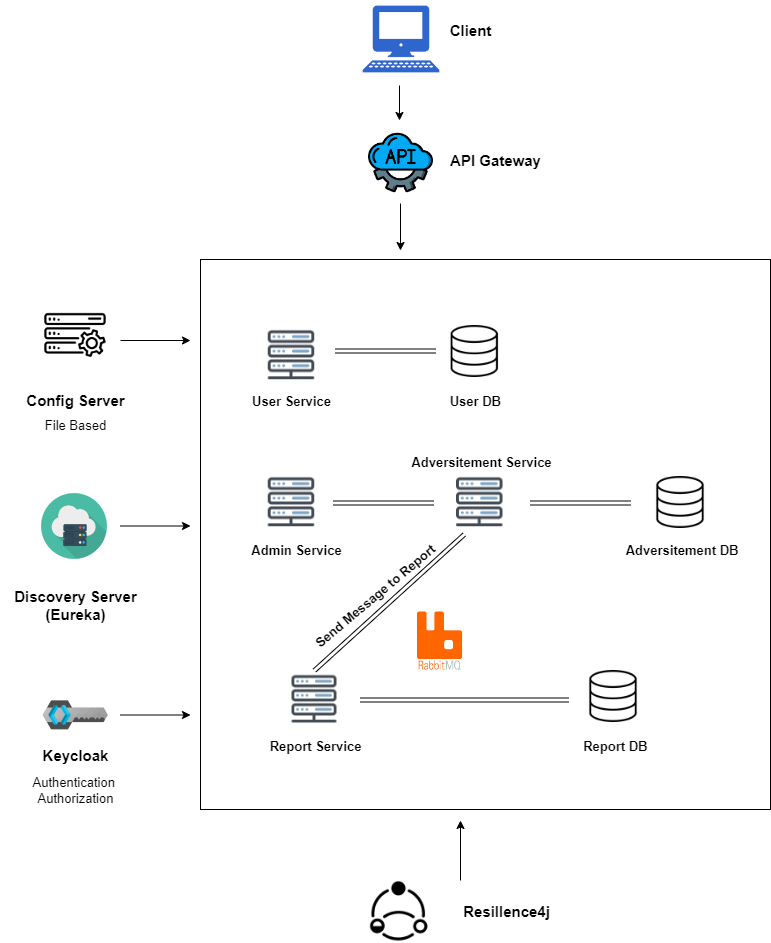
Spring Boot Microservice Example(Eureka Server, Config Server, API Gateway, Services , RabbitMq, Keycloak)
A Java library to test REST endpoints secured by Keycloak via OpenID connect.
デジタル庁のガバメントAI「源内(GENAI)」を完全ローカル(ローカルLLM/OpenAI互換)で動かす非公式プロジェクト。SAML認証(Keycloak)・RAG(Qdrant)・文字起こし(Whisper)・画像生成(SD)・チーム単位ナレッジをローカル完結。
Keycloak with Let's Encrypt Using Docker Compose
Sample keycloak project using react-oidc-context
Demo illustrating the usage of Spring Security in microservices built on top of Spring Boot and Spring Cloud
It is responsible for establishing a connection to provided Keycloak Server, reconciling realms, and clients according to the created CRs
An open-source Identity and Access Management (IAM) / Single-Sign-On (SSO) platform with web UI supporting OAuth 2.0, OIDC, SAML, CAS, LDAP, WebAuthn, TOTP and MFA
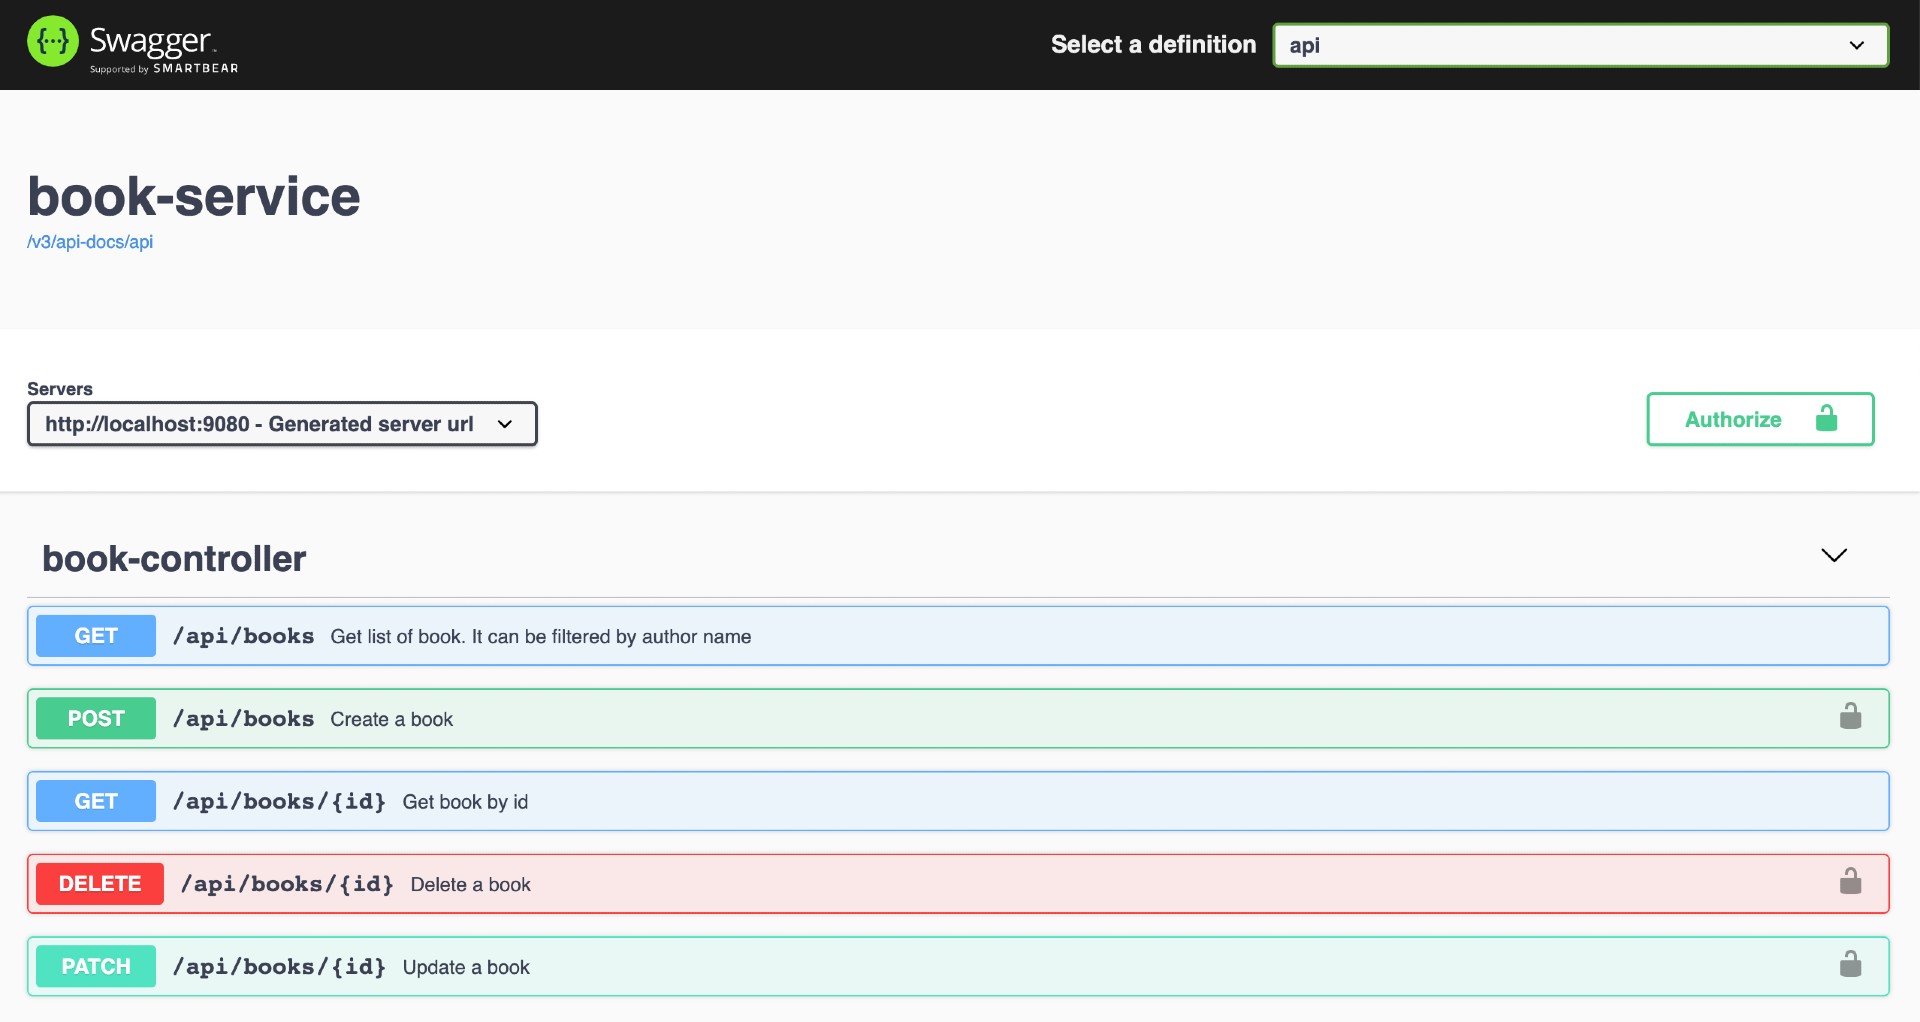
The goals of this project are to: 1) Create a Spring Boot application that manages books, called book-service; 2) Use Keycloak as OpenID Connect provider; 3) Test using Testcontainers; 4) Explore the utilities and annotations that Spring Boot provides for testing applications.
Two applications in different branches illustrates how to create asynchronous microservices with Vert.x, Consul and MongoDB, and how to secure them with Vert.x OAuth2 module and Keycloak
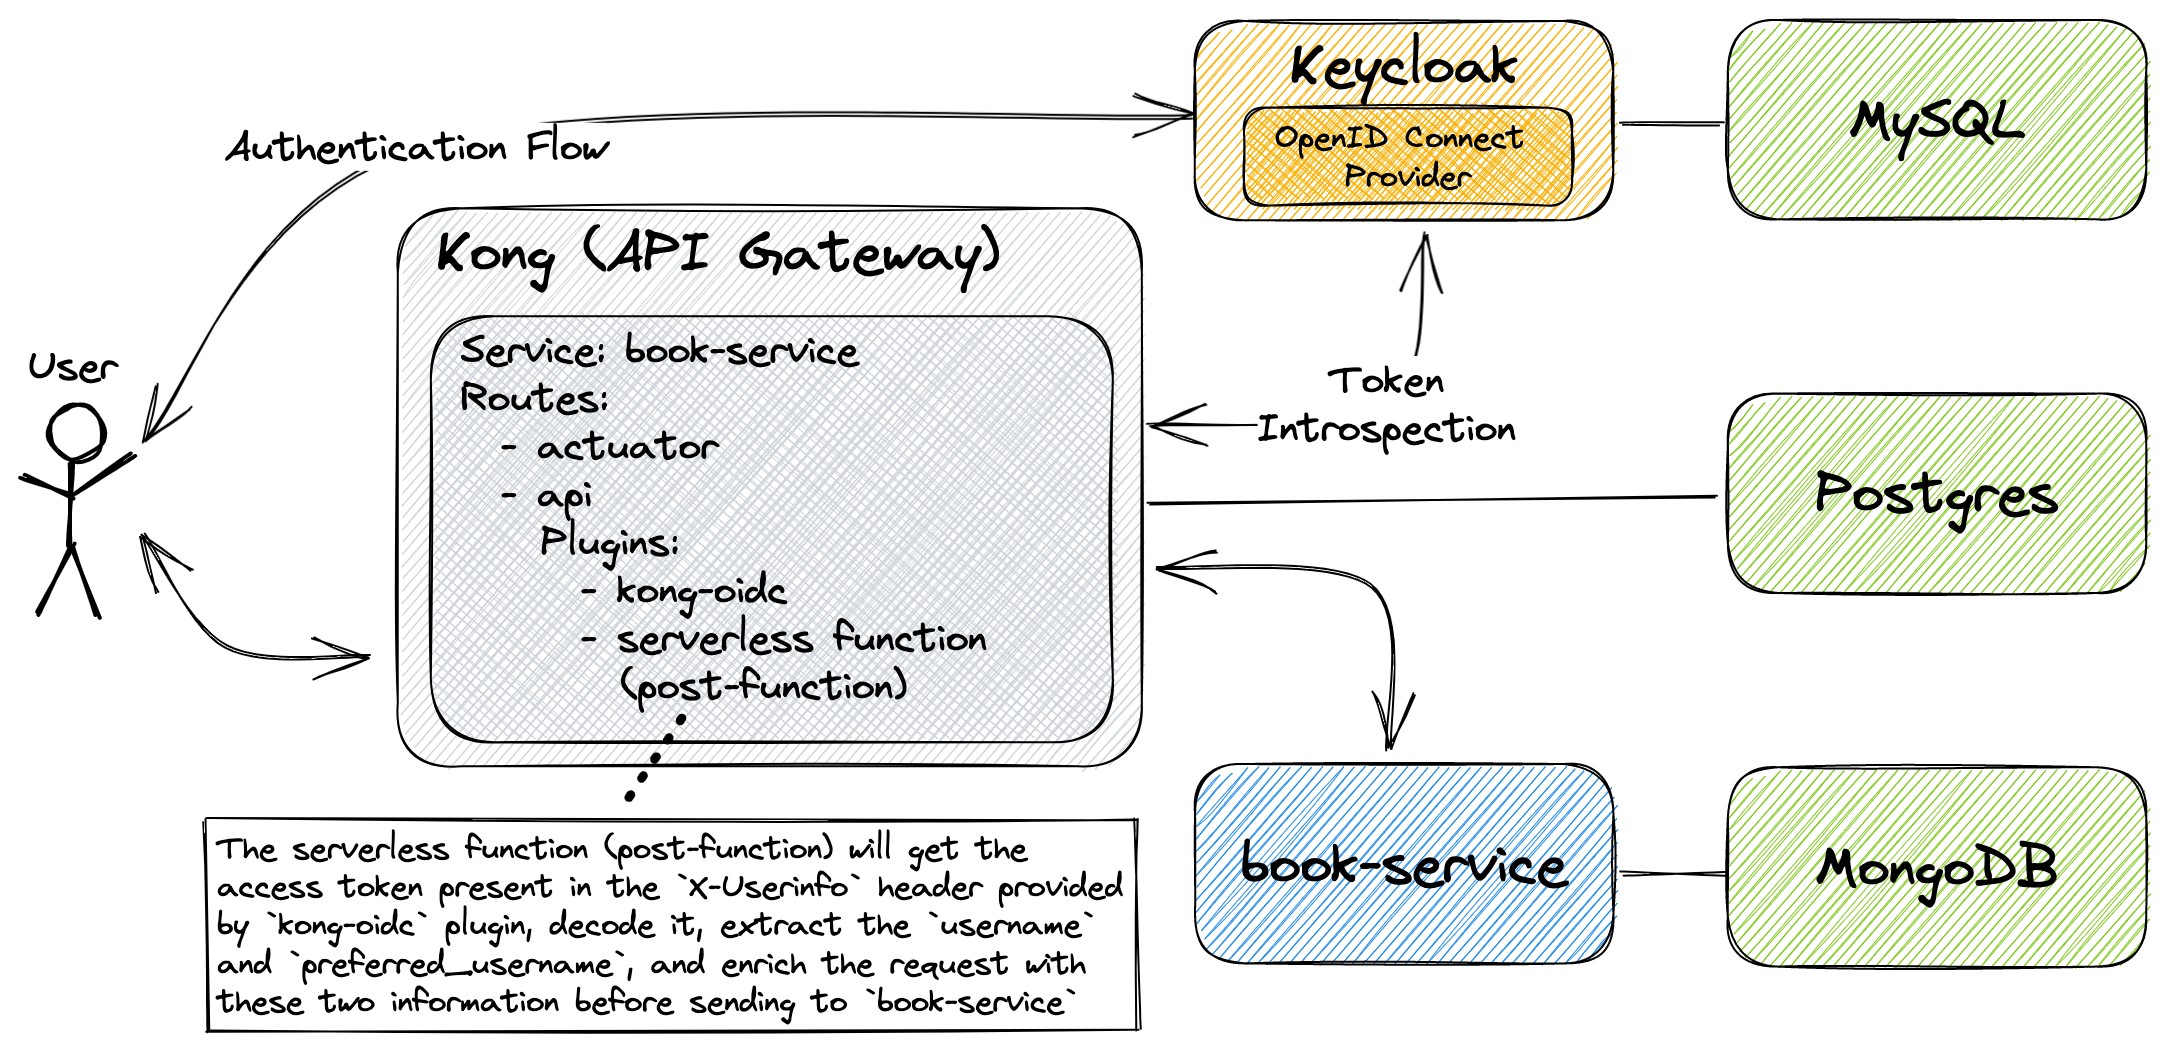
Goal: create a Spring Boot app called book-service accessible only through the Kong API gateway. In Kong, the kong-oidc plugin will be installed, enabling communication between Kong and Keycloak. This setup ensures that when Kong receives a request for book-service, it validates the request in conjunction with Keycloak to ensure its authenticity.
Self-hosted, open source GIS portal: web maps, PostGIS data layers, forms, an app builder with dashboards, an offline field PWA, OGC APIs, and a QGIS plugin. PostGIS + MapLibre + Keycloak on Docker Compose.
Simple and Fast (3K simultaneous users, 5K RPS) OpenId-Connect authorization server with Keycloak compatible API written in GO. The possibility to increase application clients number and authentication/authorization speed without any modification due to the API compatibility
Java library for developing reactive programming(reactor-core) backend systems in microservices
Keycloak's Site Reliability Engineers Special Interest Group (Keycloak SRE SIG): To improve the lives of people running and operating Keycloak
Basic brute-force script targeting the standard Keycloak Admin/User Console browser login flow.