iamlive
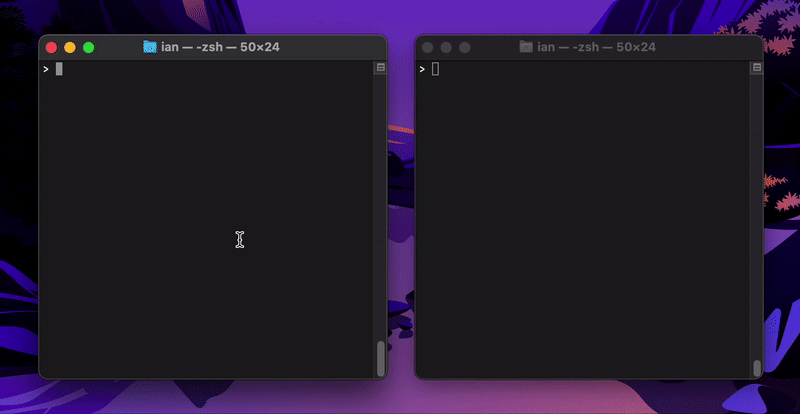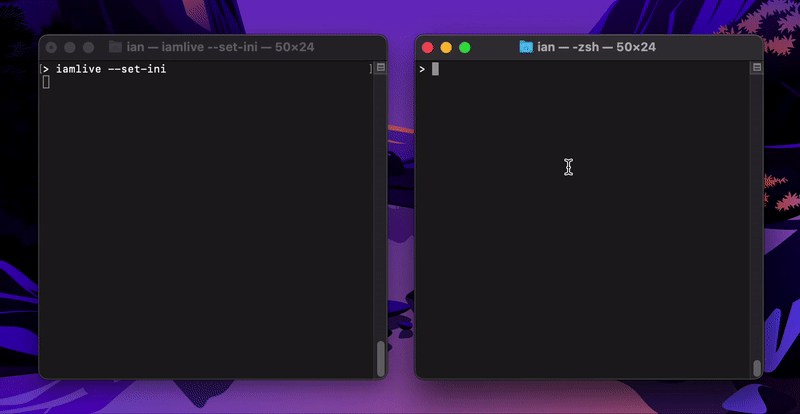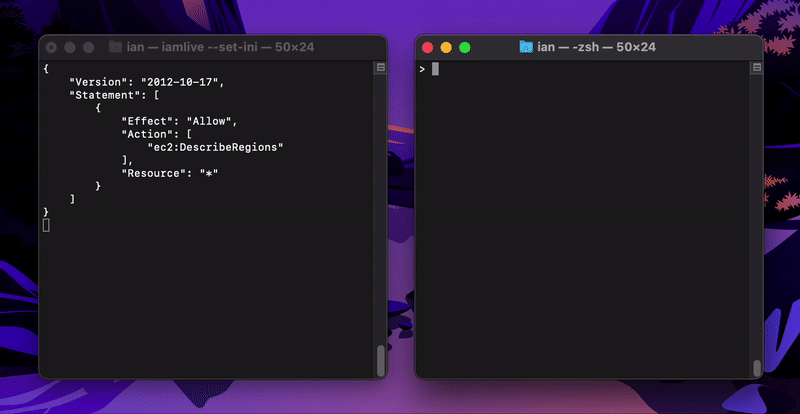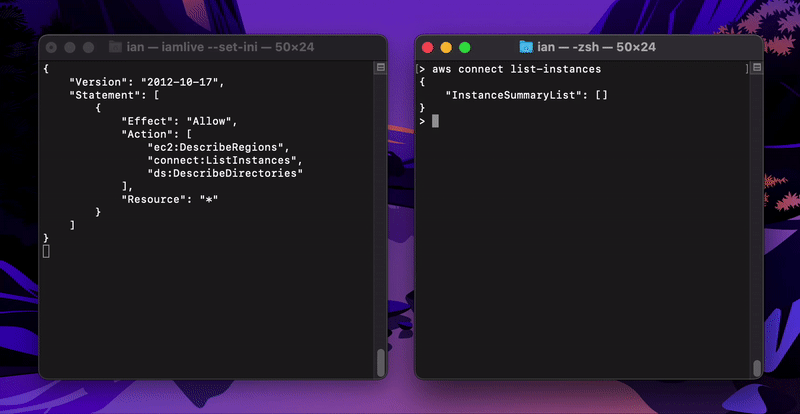
Generate an IAM policy from AWS, Azure, or Google Cloud (GCP) calls using client-side monitoring (CSM) or embedded proxy
- 3.4k
- Go
- MIT
- 7 mo ago
Generate an IAM policy from AWS, Azure, or Google Cloud (GCP) calls using client-side monitoring (CSM) or embedded proxy
Purpose-bound authorization reference: RBAC + ABAC + ReBAC, row/field controls, fidelity gates, lifecycle governance, and a tested 100K synthetic-data path.
Verify what AI coding agents can actually read, write, execute and reach using synthetic canaries.
Cloud governance reports from native services in a clear and readable digest
Web4: an open standard for verifiable AI presence — LCT identity, T3/V3 trust tensors, MRH context, ATP/ADP. Rust + Python SDKs on crates.io/PyPI. AGPL-3.0-or-later.
Python CLI for detecting cloud storage misconfigurations. AWS S3 real API scanning with boto3. Azure Blob and GCP Storage on roadmap.
Hestia — universal Web4 presence for humans and AI. Local-first cryptographic identity, encrypted vault, delegation authority, witnessed trust record, and device constellation. Cross-platform app + AI plugin + CLI. EUDI-compatible credential issuance. AGPL-3.0.
Mission-bounded authorization mesh for humans, workloads, and AI agents — deterministic policy enforcement across RBAC, ABAC, ReBAC, OAuth, Kubernetes, and agentic tool calls.
Evidence-backed minimum-security profiles for container images: the capabilities and read-only-filesystem config each image actually needs, with drop-test proof
An MCP platform for agent work, built in public, and the method used to build it: every agent session runs in its own sandbox, every change passes a gate that counts scenarios and kills mutants, every fact is checked against published literature.
Ship the customer-facing agent you shelved. Missura binds each agent run to one customer entity — same vendor SDK, read-only, minutes, no vendor credentials in the agent.
Expiring, renewal-bound authority leases for autonomous AI agents. Least-privilege access that dies unless trusted supervision renews it.
POSIX filesystem permission and IAM privilege auditor scanning for unauthorized SUID/SGID binaries, world-writable paths, insecure /etc/sudoers rules, and over-permissive cloud IAM policies.
Agent MCP tool permission least-privilege auditor with blast radius scoring, privilege escalation chain detection, and capability matrix verification.
Inspektor Gadget advisor gadgets: derive minimal capabilities, read-only rootfs + writable paths, and device grants from live eBPF observation
Web4 Community Hub — single-binary Rust daemon that turns a community into a sovereign Web4 society: signed law, witnessed ledger, sealed member channels. Standalone mirror of web4/hub; development happens in dp-web4/web4.
WebMCP challenge demo for explainable least-privilege SaaS access reviews.
Least-privilege OAuth scopes per provider for common AI agent tasks (Gmail, Drive, Slack, GitHub, Microsoft Graph), with review triggers and token pitfalls.
Azure RBAC defined in Terraform and then actually tested: each identity signs in and attempts what it should be refused, with drift detection and privilege-escalation analysis that avoid the false positives that make such tools unreadable.
Agentic ops copilot on Microsoft Foundry: a prompt agent that queries and repairs Azure infrastructure through an MCP tool server, with approval-gated write actions.