nmap


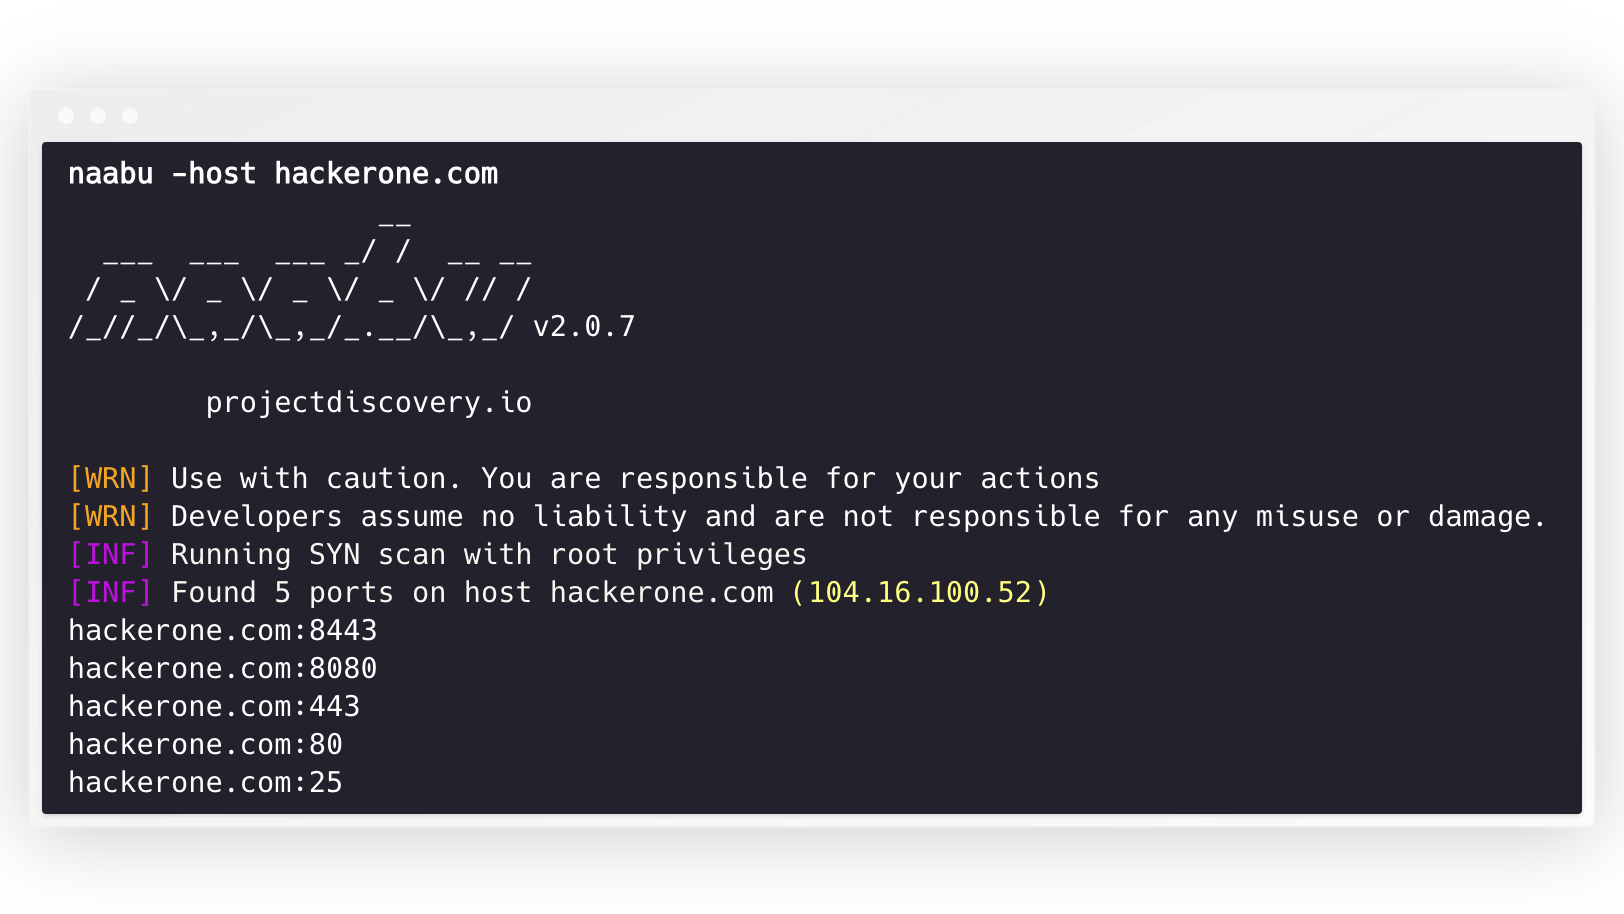
naabu
A fast port scanner written in go with a focus on reliability and simplicity. Designed to be used in combination with other tools for attack surface discovery in bug bounties and pentests
- 6.4k
- Go
- MIT
- 1 d ago


htrace.sh
My simple Swiss Army knife for http/https troubleshooting and profiling.
- 3.9k
- Shell
- GPL-3.0
- 24 mo ago


Reconnoitre
A security tool for multithreaded information gathering and service enumeration whilst building directory structures to store results, along with writing out recommendations for further testing.
- 2.2k
- Python
- GPL-3.0
- 4 y ago

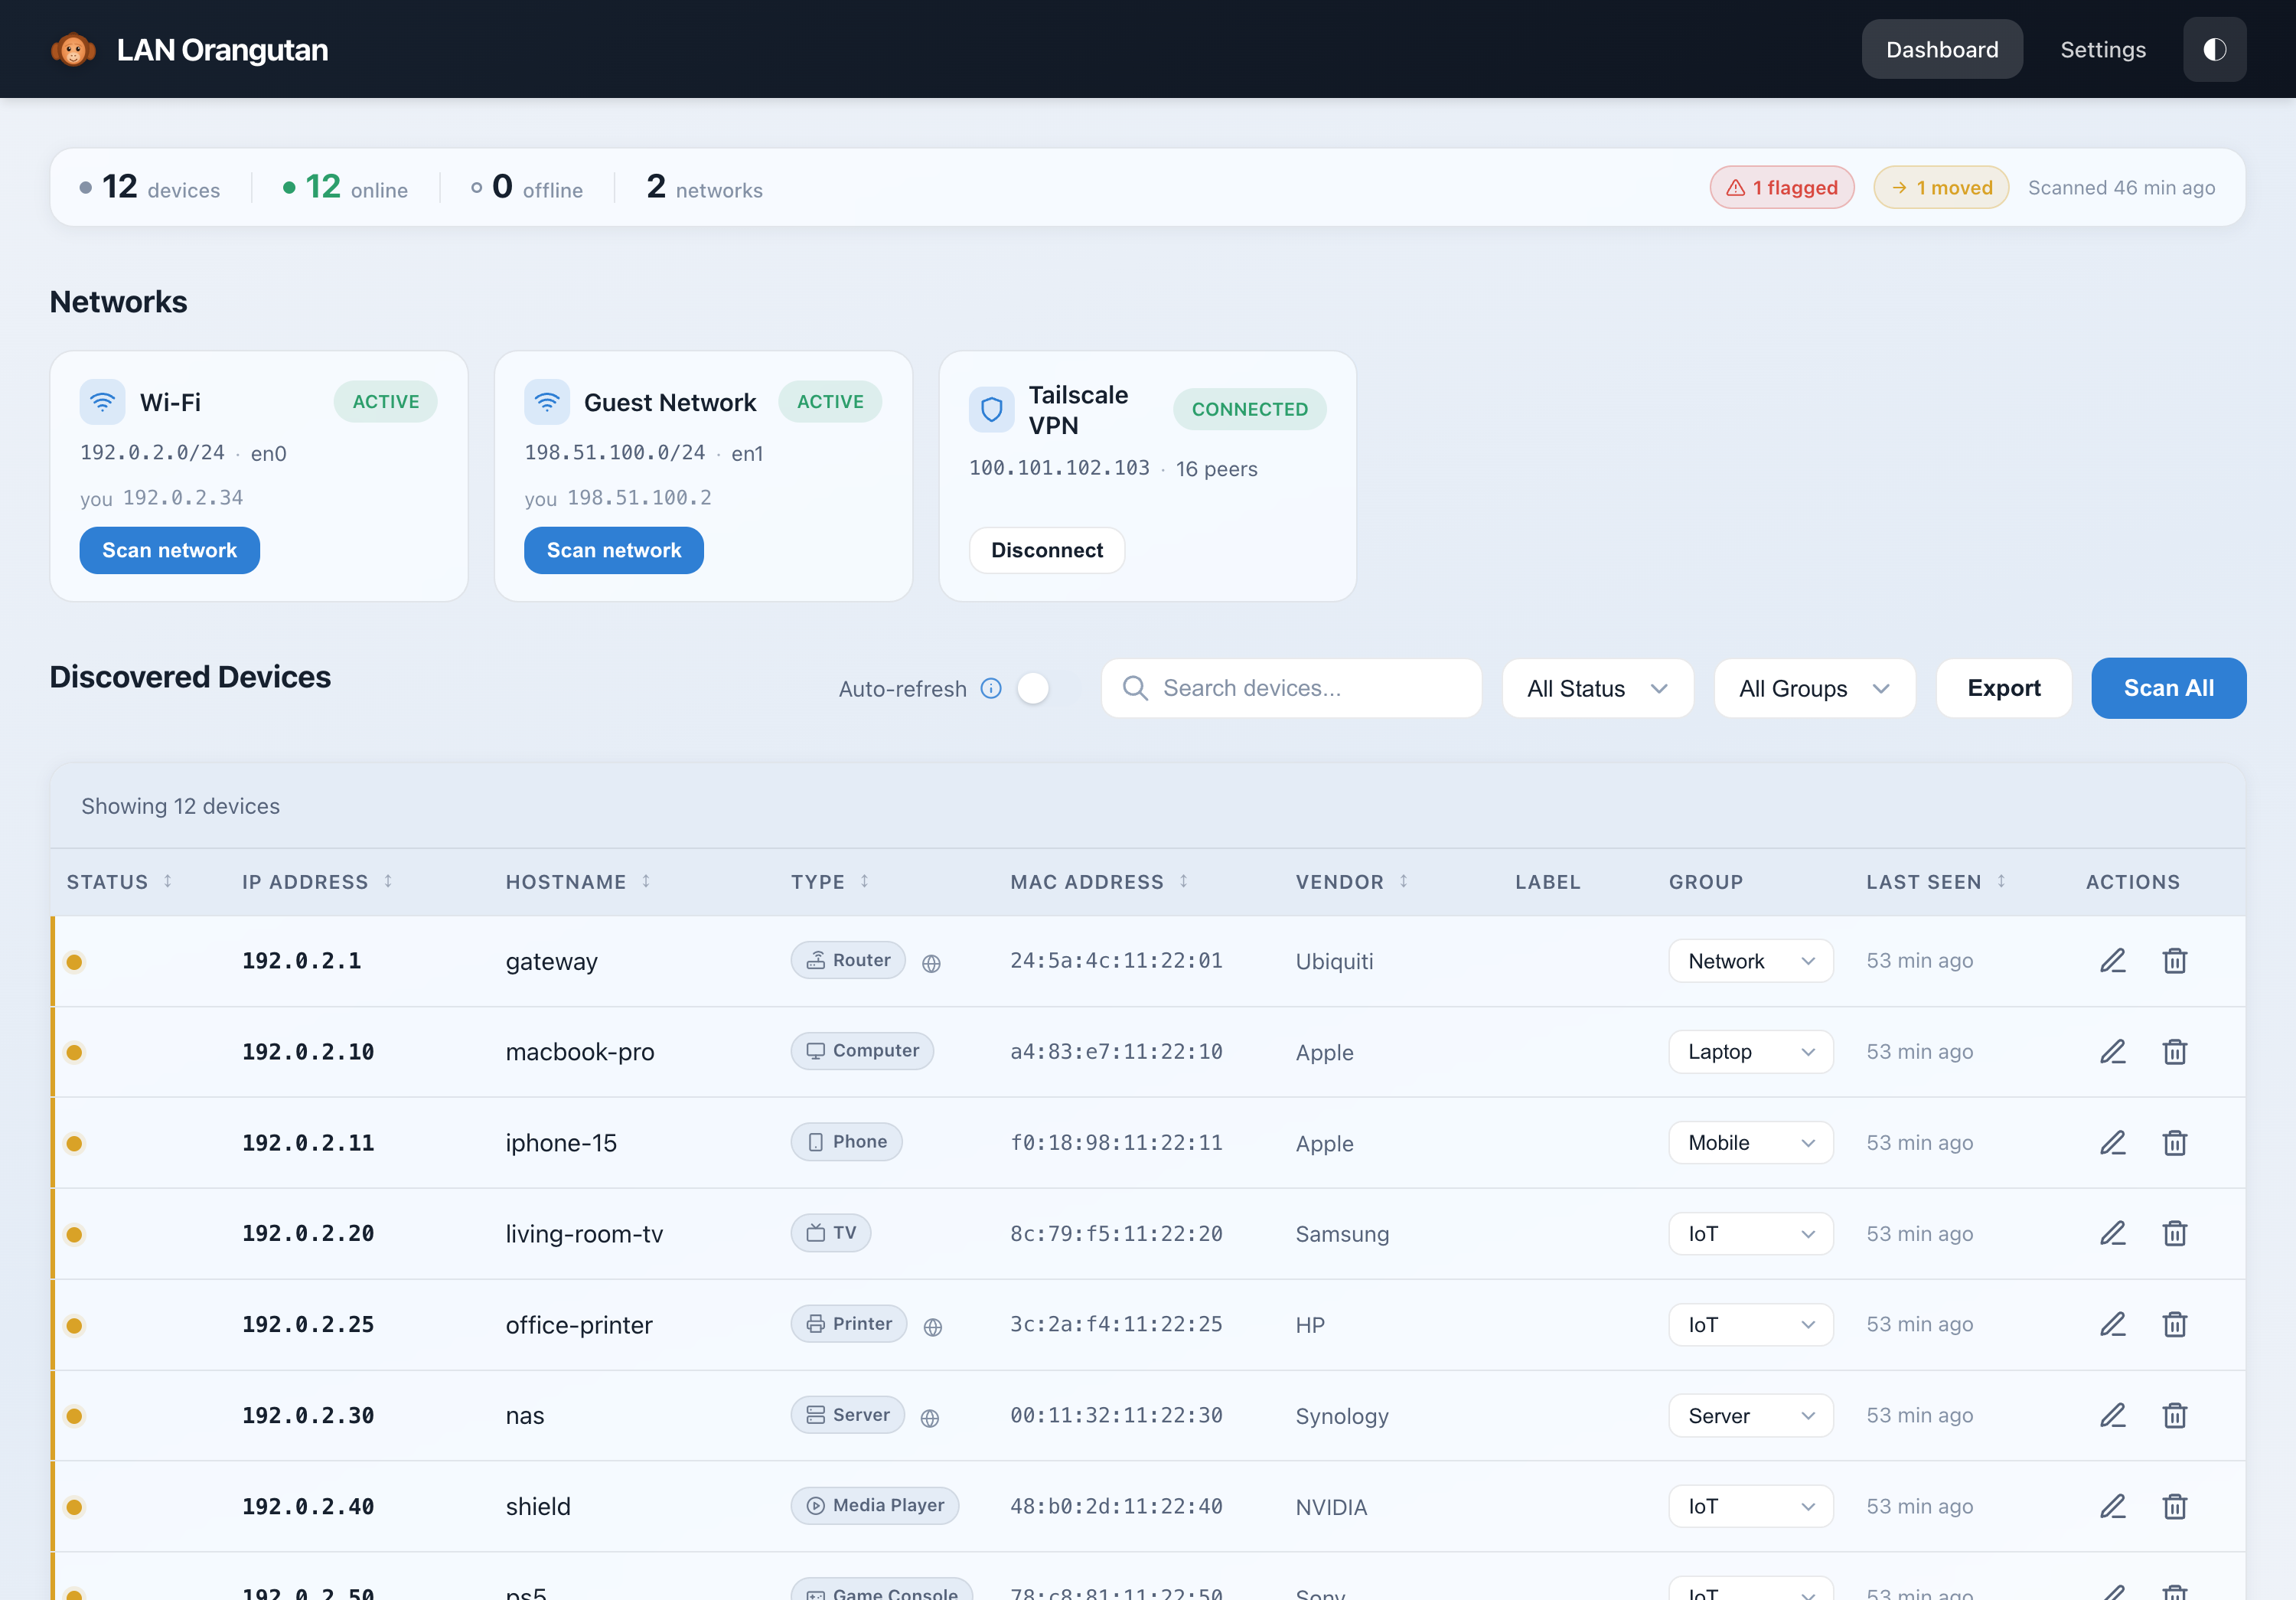
LAN-Orangutan
LAN-Orangutan is a self-hosted network discovery tool. Find every device on your LAN, label and group them, snapshot your network and compare it later, and get flagged when something unexpected shows up. Single binary, no setup, Tailscale built in. Built by 291 Group.
- 1.2k
- Go
- MIT
- 5 h ago


Hacking-Tools
This Repository is a collection of different ethical hacking tools and malware's for penetration testing and research purpose written in python, ruby, rust, c++, go and c.
- 1.1k
- C
- 3 mo ago

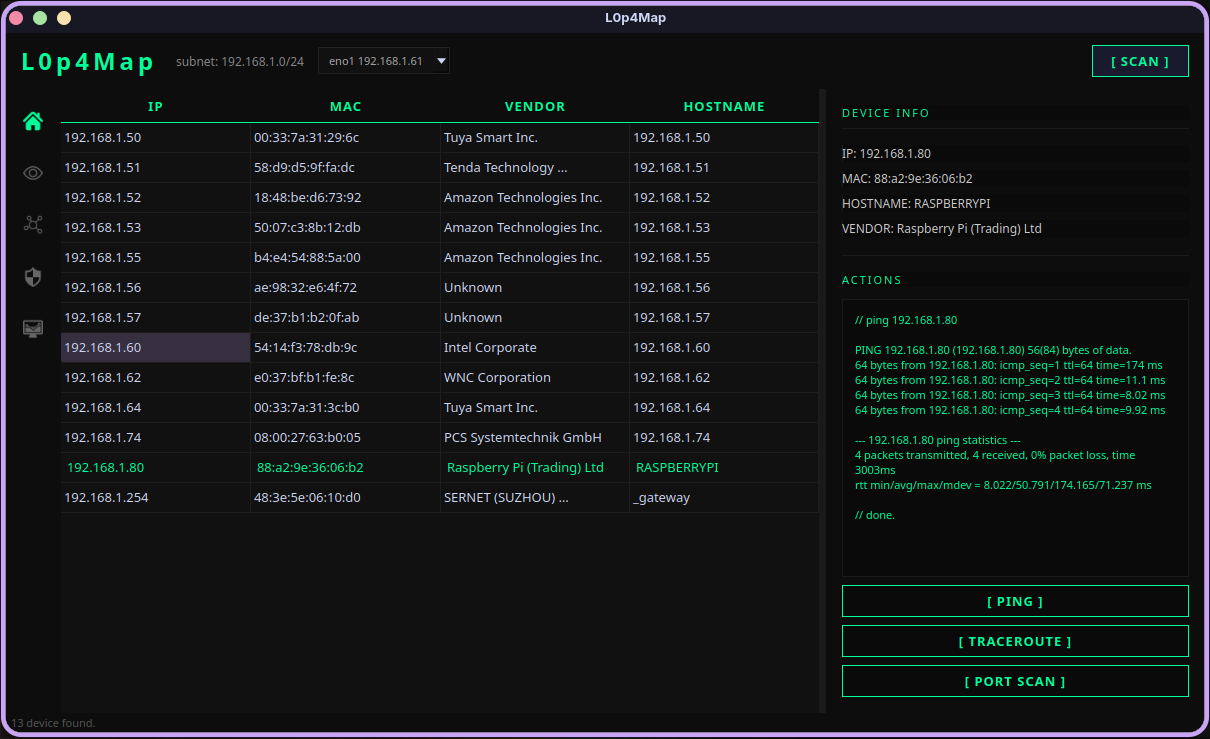
L0p4Map
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time interactive network topology engine. Works on both local networks and custom IPs/websites.
- 1k
- Python
- GPL-3.0
- 4 mo ago


nmap-formatter
A tool that allows you to convert NMAP results to html, csv, json, markdown, graphviz (dot), sqlite, excel and d2-lang. Simply put it's nmap converter.
- 746
- Go
- MIT
- 4 d ago


HellRaiser
Vulnerability scanner using Nmap for scanning and correlating found CPEs with CVEs.
- 587
- Ruby
- 4 y ago



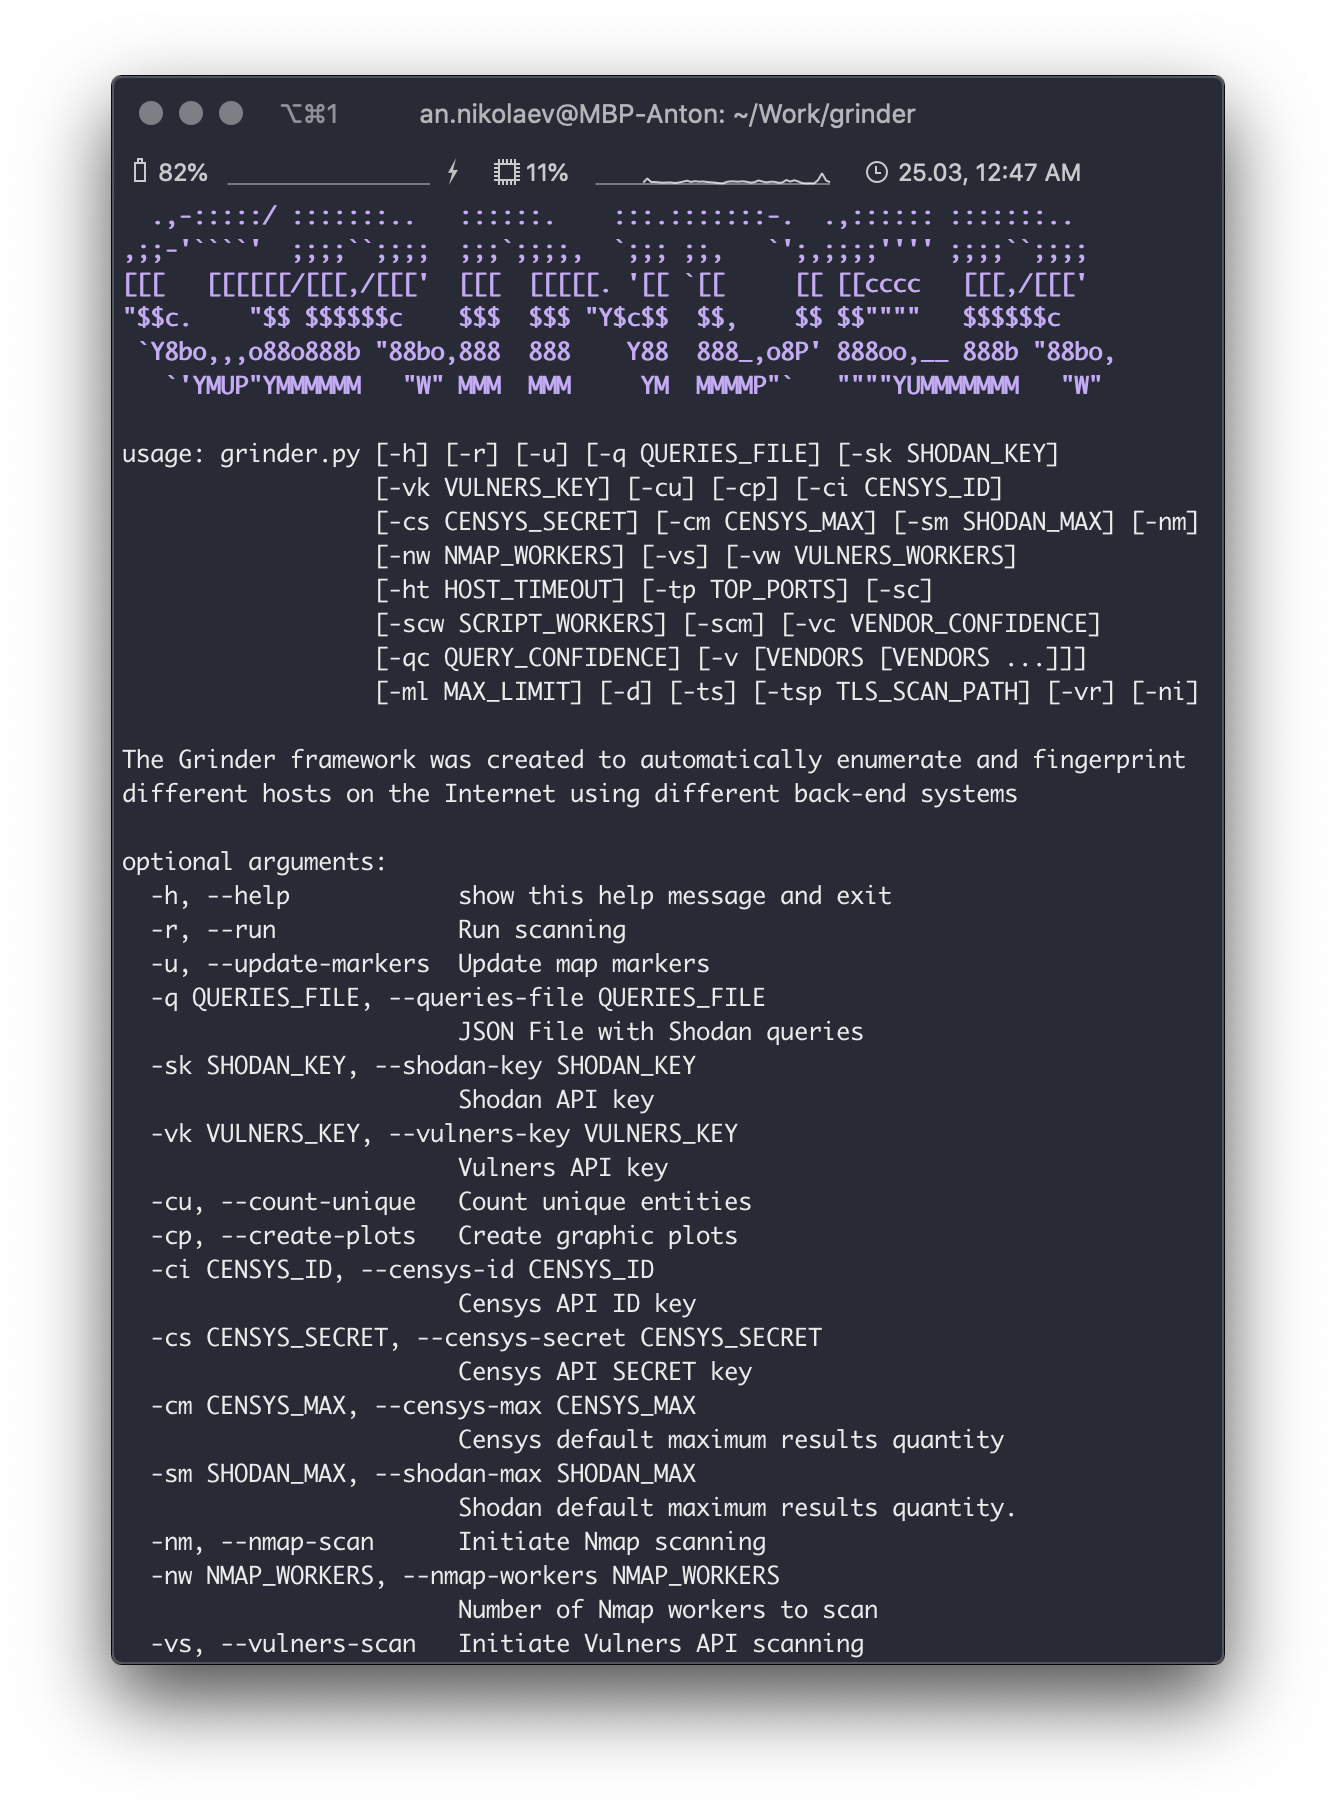
grinder
:mag_right: Python framework to automatically discover and enumerate hosts from different back-end systems (Shodan, Censys)
- 298
- Python
- GPL-2.0
- 5 y ago

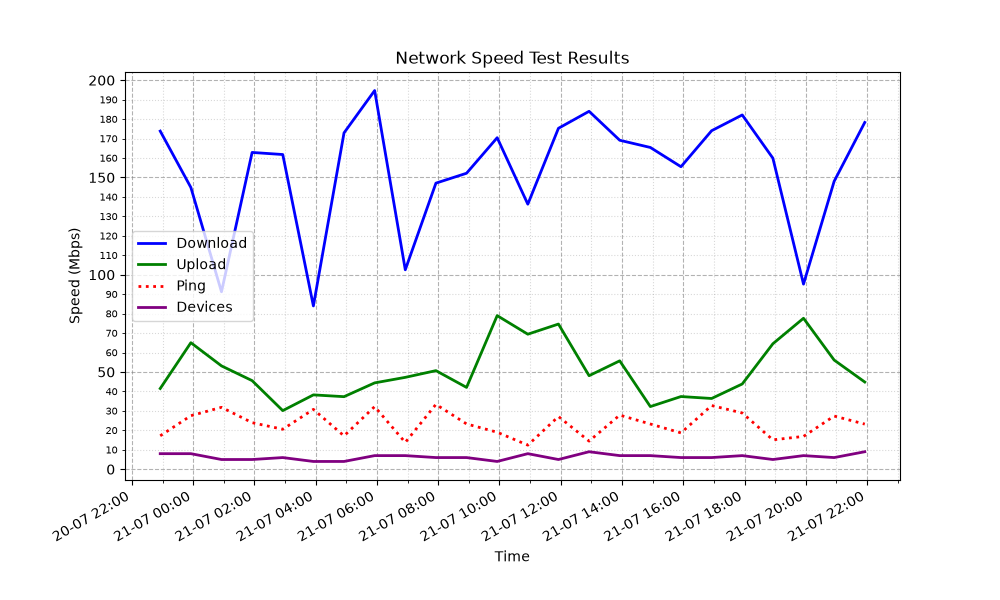
netmon
Self-hosted network monitor - hourly speed tests, LAN device counts via ARP scan, and sarcastic AI-generated reports delivered to Telegram or Discord.
- 288
- Python
- MIT
- 6 wk ago

vedetta
Home Assistant app: a local network scanner that finds, recognizes and explains every device on your LAN (name, brand, model, presence, latency). No cloud, no accounts.
- 109
- Python
- MIT
- 2 h ago


penetration-testing-roadmap
🎯 A structured 60-week penetration testing curriculum with 500+ free TryHackMe labs, OWASP Top 10 deep dives, tool mastery guides, and certification roadmaps. Three learning paths from zero to professional pentester. 2026 Edition; includes AI/LLM, Cloud & API security.
- 92
- 9 d ago

NmapScanningTool
A secure, production-ready Python CLI wrapper for Nmap that makes powerful scans easy and repeatable. Includes 12 built-in profiles (SYN, aggressive, OS detection, vulnerability/NSE checks), interactive and non-interactive modes, strict input validation, Docker support, CI, and script-friendly flags for automation.
- 30
- Python
- MIT
- 8 d ago
eidolon
Network scanner that maps infrastructure into a Neo4j graph and executes natural-language security operations via AI agents.
- 20
- Python
- MIT
- 10 mo ago

BLX
Gerador de comandos de pentest: escolha a ferramenta, responda às perguntas do wizard e receba comandos prontos para copiar ou baixar como script .sh. Nmap, SQLMap, Metasploit, Mimikatz, BloodHound e mais — 24 ferramentas, 100% offline, em um único binário (Linux, macOS, Windows e Android).
- 2
- Go
- MIT
- 3 mo ago

