npm-security

why-claude-code-leaked
Why Claude Code leaked: a deep dive into npm packaging failures, source map exposure, and modern supply chain security risks.
- 16
- JavaScript
- MIT
- 8 mo ago

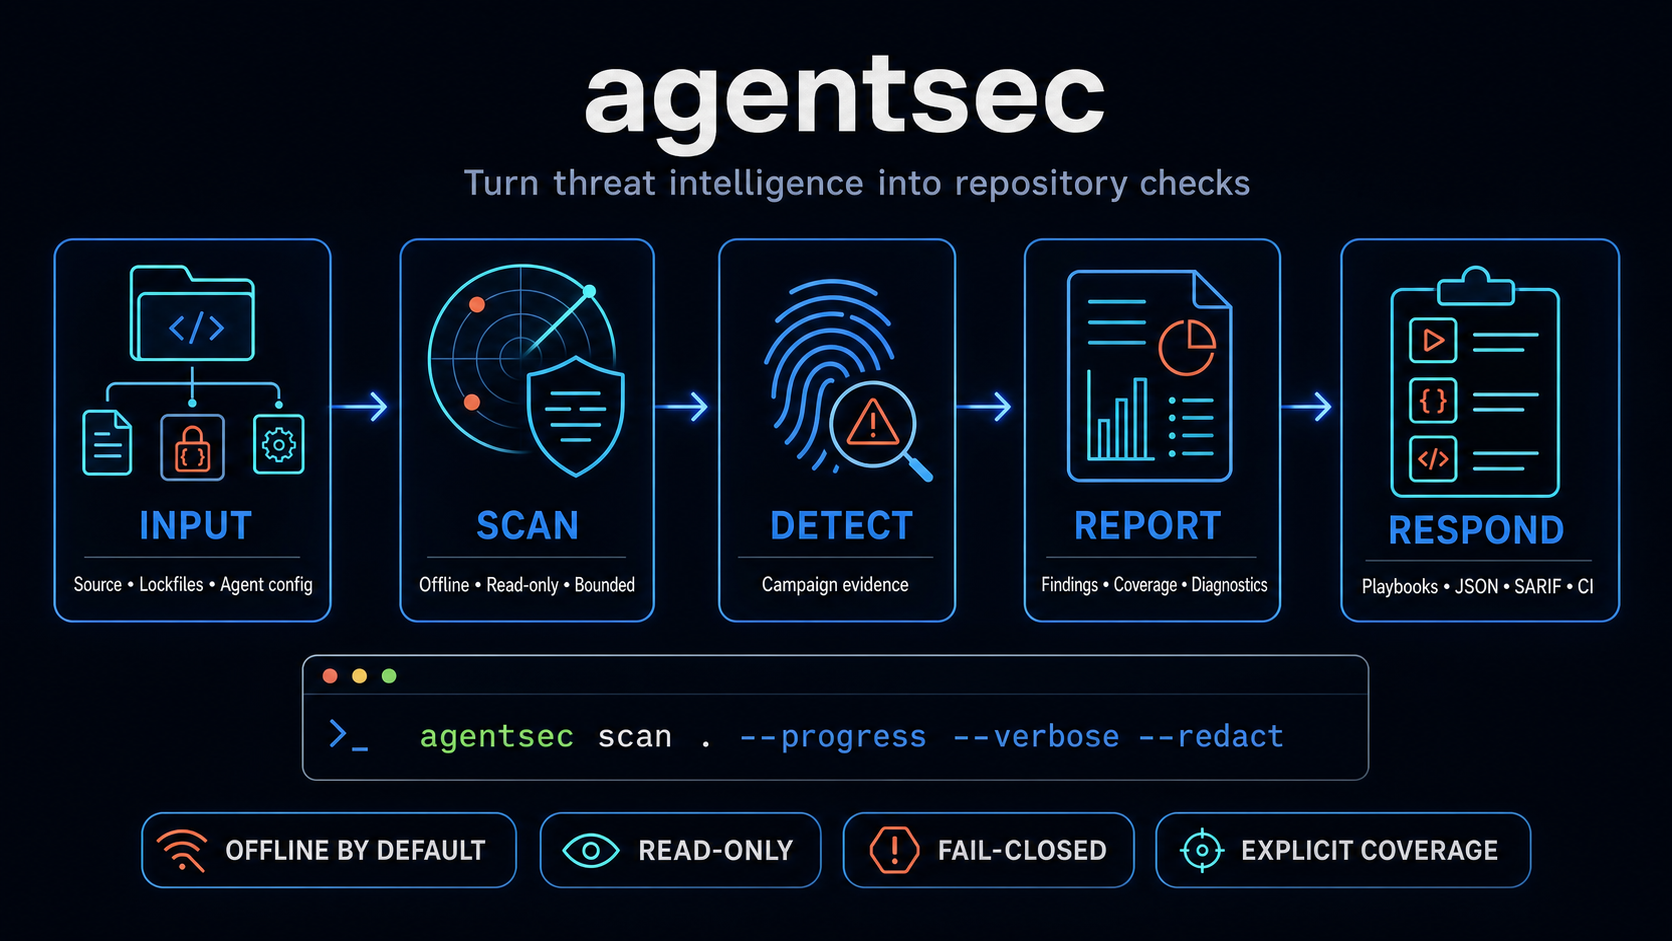
agentsec-triage
Offline, read-only repository triage for documented software supply-chain and coding-agent attacks, with explicit coverage and fail-closed results
- 9
- Python
- 2 wk ago

supply-chain-mcp-server
90-tool MCP server for software supply chain security — OSV, GHSA, NVD, EPSS, CISA KEV, npm, PyPI, crates.io, RubyGems, NuGet, Packagist, Go, deps.dev, Scorecard, Rekor, ClearlyDefined, Repology, typosquatting detection
- 3
- TypeScript
- MIT
- 2 mo ago

tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
- 2
- Shell
- MIT
- 6 d ago

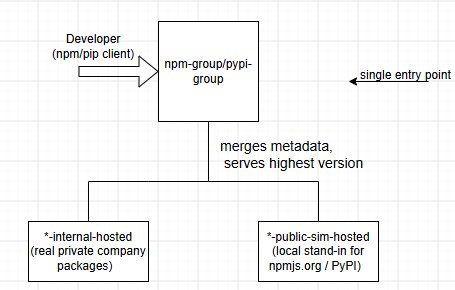
supply-chain-dependency-confusion
Local, fully self-contained demo of a dependency confusion attack using Nexus Repository OSS — showing how group repositories merge public and internal package sources by version, and two layers of defense (client-side scope routing + server-side Routing Rules) that close the gap.
- 0
- Shell
- MIT
- 5 wk ago
