cve-mcp-server
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan, VirusTotal, and more.
- 1.8k
- Python
- Apache-2.0
- 7 wk ago
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan, VirusTotal, and more.
A free and open vulnerabilities database and the packages they impact. And the tools to aggregate and correlate these vulnerabilities. Sponsored by NLnet https://nlnet.nl/project/vulnerabilitydatabase/ for https://www.aboutcode.org/ Chat at https://gitter.im/aboutcode-org/vulnerablecode Docs at https://vulnerablecode.readthedocs.org/
A free, public vulnerability feed: CVE, GHSA, OSV, CISA KEV and EPSS merged into one entry per vulnerability. RSS, JSON API and MCP. Docs and issues only.
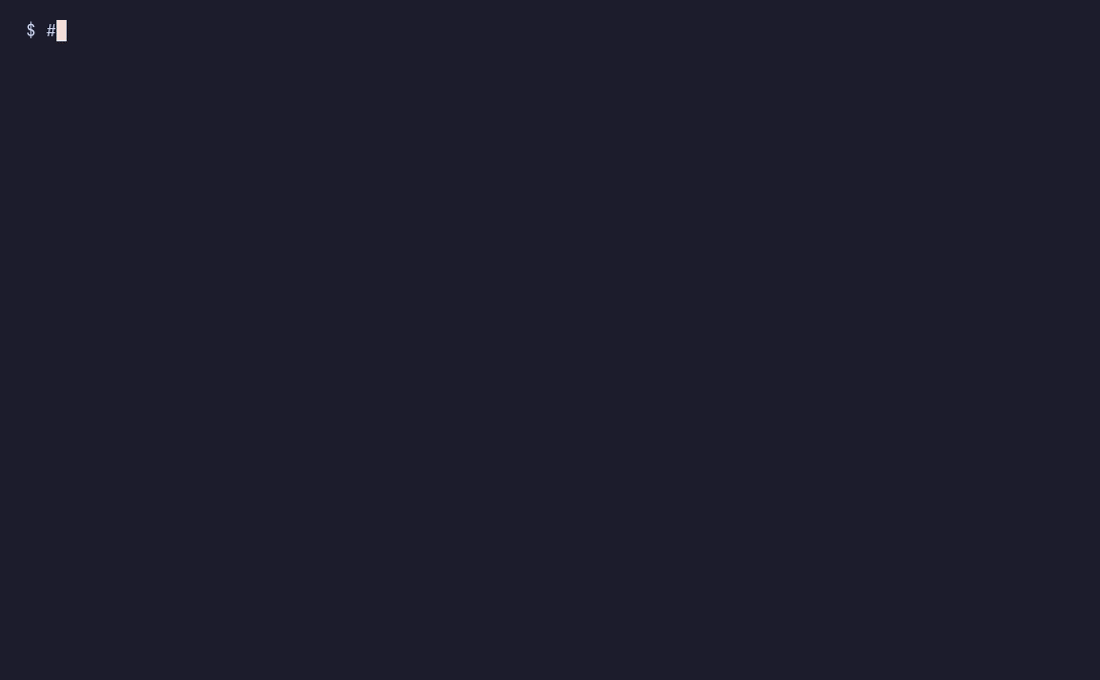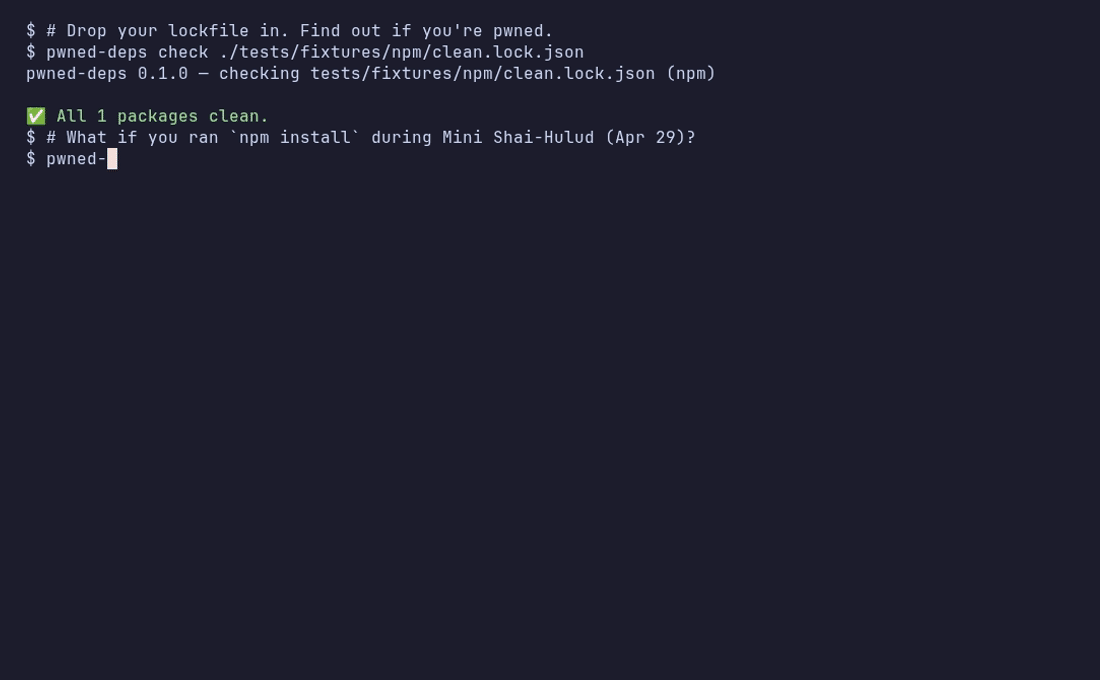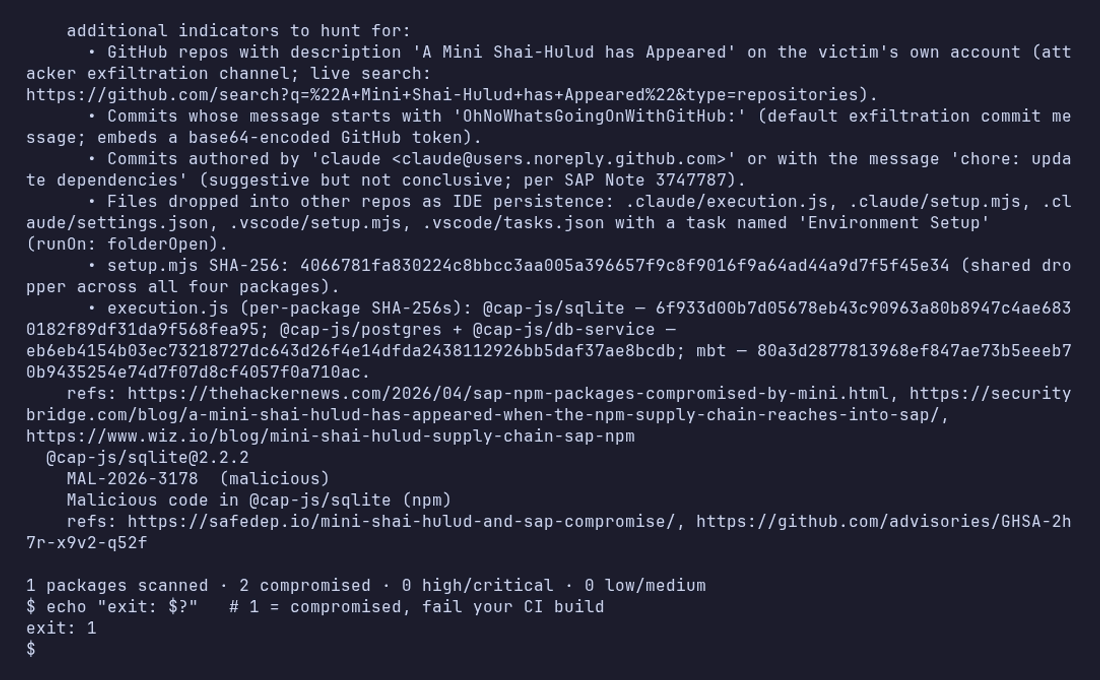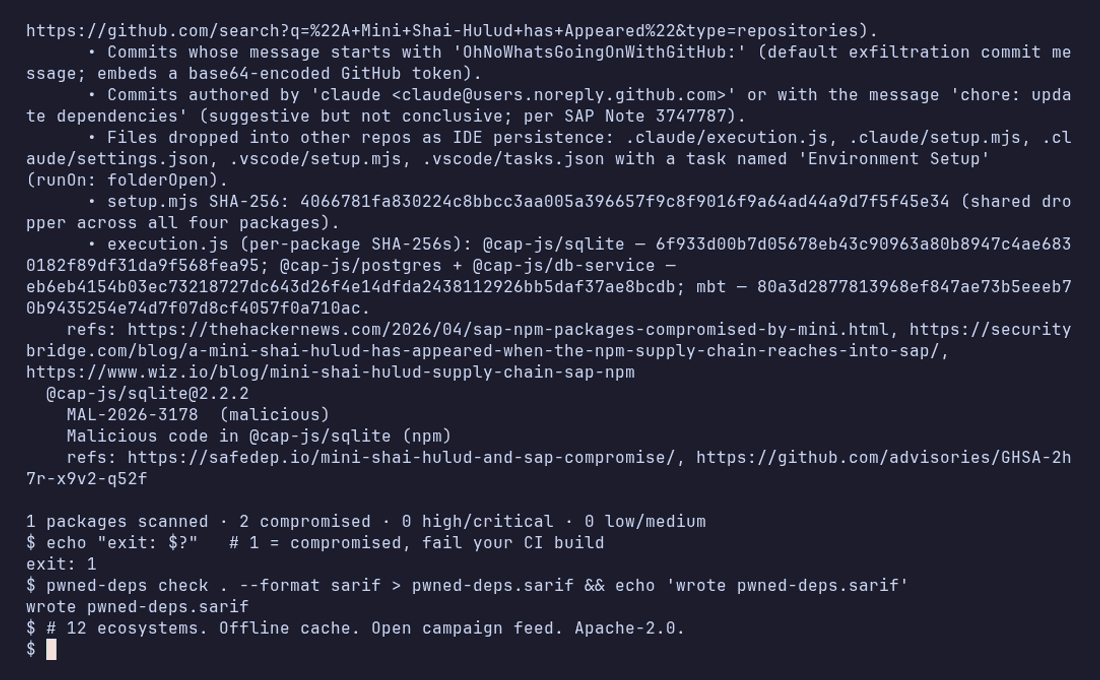
Is your lockfile pwned? 5-second scan of npm/PyPI/Maven/Cargo/Go/RubyGems lockfiles for compromised packages — OSV + curated campaign feed, --min-age cooling-off gate, exit 4 when a scan is incomplete. SLSA L3, Sigstore-signed feed.
Security intelligence API and MCP server: CVE, KEV, EPSS, package, domain and IP lookups, and monitoring
Security advisories your scanner can't see yet: published by maintainers, not yet reviewed into GitHub's database or OSV. Live tracker, open OSV feed, and a CI watcher for GitLab, GitHub, Gitea and Forgejo.
23-tool MCP server for CVE & vulnerability intelligence. NVD, EPSS, CISA KEV, GitHub Advisory, OSV — unified in one server. Risk scoring, bulk triage, exploit search. 2 dependencies, runs with npx.
Agent Reliability Analyzer extension for VS Code and Cursor: find agent reliability issues
CA9 is a local evidence engine for Python AppSec triage. It sits after scanners and before engineers waste time, proving which findings matter.
Educational dependency scanner built in pure Go—parse go.mod and go.sum, inspect direct and indirect modules, query OSV for vulnerabilities, and summarize licenses.
SBOM diff with supply-chain risk signals — flags new CVEs, typosquats, and young maintainers on changed deps. Built after axios (Mar 2026), Shai-Hulud, and xz.
Which of your products does this CVE reach? SBOM dependency graph with CISA KEV, EPSS and OpenVEX. Single static Go binary. Continuation of Minefield.
Lightweight, dependency-free shell script that scans 12 ecosystems (npm, PyPI, Go, Rust, Maven/Gradle, NuGet, RubyGems, Composer, Pub, Hex, Swift, GitHub Actions) for vulnerable dependencies using OSV & GHSA feeds — or your own JSON / CSV / PURL / SBOM / SARIF / Trivy sources
Supply-chain security for npm and PyPI: scans install scripts and native binaries (Ghidra decompilation, YARA, AI classification), checks OSV malware advisories, and gates PRs with a GitHub Action.
🧰 Free tools for writing security reports: find a CWE, look up CVEs and GHSAs, score CVSS 3.1/4.0, check EPSS and KEV, build version ranges, get PURLs and find a CNA
90-tool MCP server for software supply chain security — OSV, GHSA, NVD, EPSS, CISA KEV, npm, PyPI, crates.io, RubyGems, NuGet, Packagist, Go, deps.dev, Scorecard, Rekor, ClearlyDefined, Repology, typosquatting detection
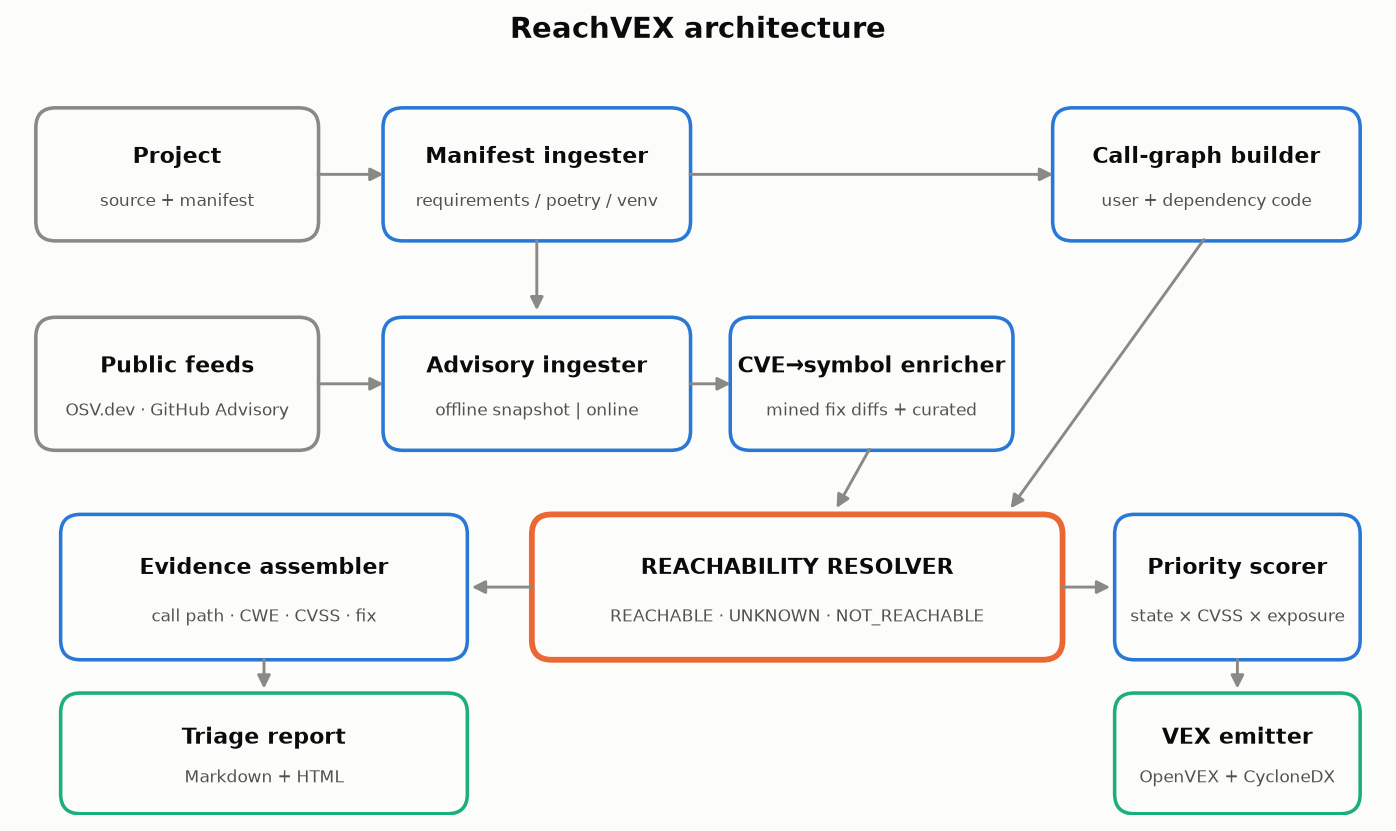
Reachability-based CVE triage engine: proves whether your code reaches each vulnerable dependency function and emits OpenVEX / CycloneDX VEX evidence
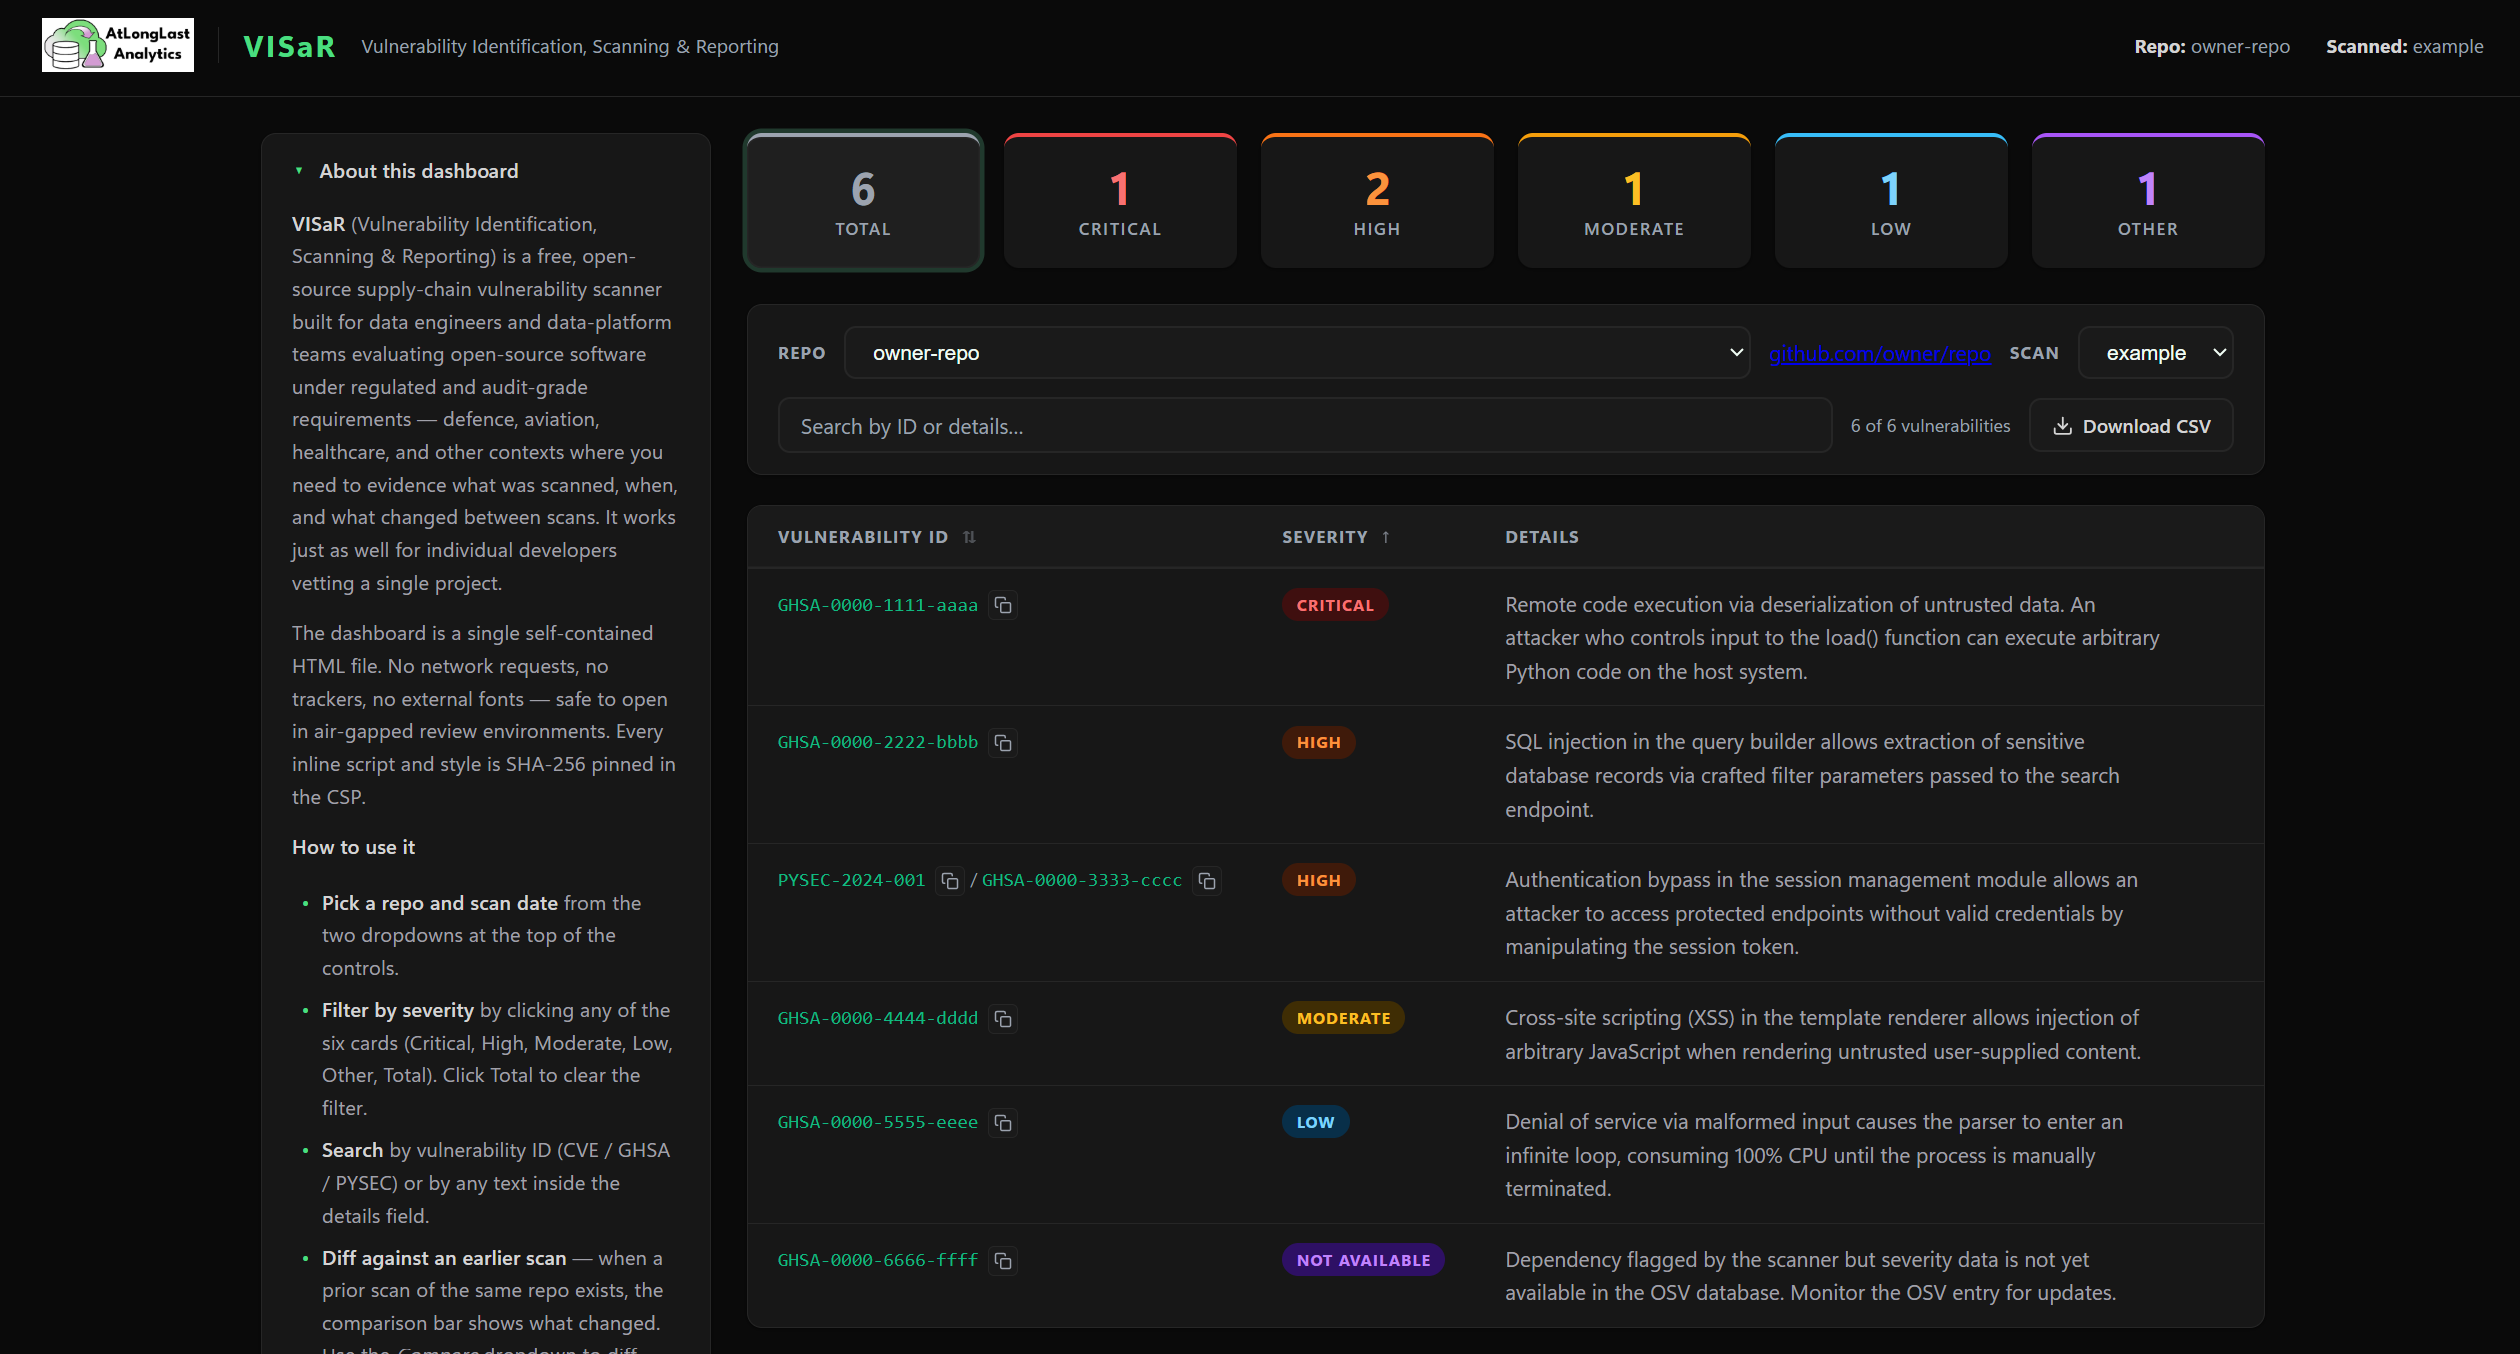
Free, open-source vulnerability scanning and reporting for GitHub repositories. Powered by OSSF Scorecard and OSV.
GitHub Action: find dependencies affected by security advisories in limbo, published but not yet in the databases scanners read
Air-gapped vulnerability patch analyzer matching OS package inventories and dependency lockfiles against offline OSV and NVD CVE advisories with CVSS risk prioritization and SARIF v2.1.0 export.
Security-first GitHub discovery, evolution tracking, and local static analysis in Rust. Features explainable triage, transactional outbox, SBOM, and native GUI/CLI.
SCA scan engine (Trivy + OSV) for the ai-dial-ci scheduled scan workflow
A Claude skill that patches your computer against this week's security advisories and supply-chain attacks, plus a standalone OSV checker for Python.
Shared OSV Scanner Workflow for GitHub Actions
Command-line vulnerability triage: scan your project's dependencies, rank CVEs by real-world exploitation (CISA KEV + FIRST EPSS), and get exact upgrade recommendations. Powered by NVD + OSV.dev.