TracePcap
Open-source, self-hosted PCAP analyzer for network forensics: device discovery, network maps, Suricata and nDPI threat detection, change monitoring, and local-LLM incident stories. Runs fully offline.
- 57
- Java
- MIT
- 1 h ago
Open-source, self-hosted PCAP analyzer for network forensics: device discovery, network maps, Suricata and nDPI threat detection, change monitoring, and local-LLM incident stories. Runs fully offline.
SIP & RTP capture, analysis, and security tool. One binary, one dependency (libpcap), built in Rust.
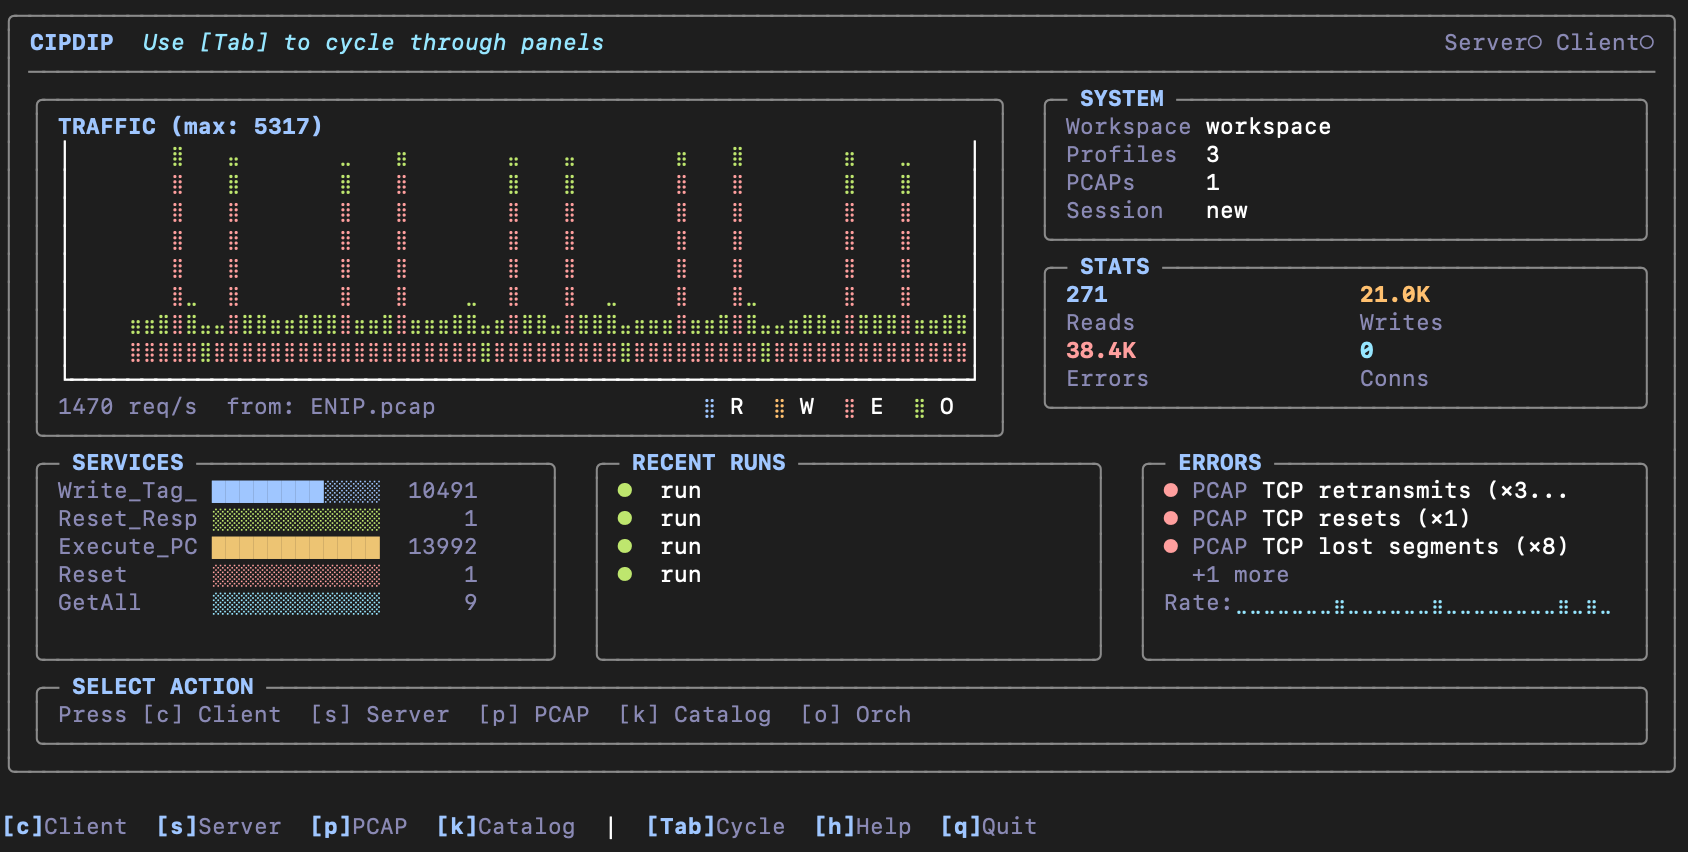
Protocol-aware CIP/EtherNet-IP deep packet inspection test harness for evaluating industrial firewall DPI engines
Desktop wardrive evidence analysis platform with local vault, parsers, and report exports.
🧭 Advanced PowerShell tool for gaming network quality analysis. Analyzes PCAP or live traffic to measure jitter, burst, spike with S+/S/A/B/C scoring. Supports Fortnite, Valorant, CS2, Warzone, LoL. Features: interactive menu, HTML reports, trend comparison, bufferbloat test, QUIC analysis.