pcapng

ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64\arm64 and loong64.
- 16k
- C
- Apache-2.0
- 2 d ago

hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
- 2.5k
- C
- MIT
- 3 d ago


awesome-malware-traffic-analysis-scientific-research
Awesome Malware Traffic Analysis Scientific Research
- 4
- TeX
- CC0-1.0
- 5 d ago

awesome-raw-packet-level-malware-detection-scientific-research
Awesome Raw Packet level Malware Detection Scientific Research
- 1
- TeX
- CC0-1.0
- 4 d ago
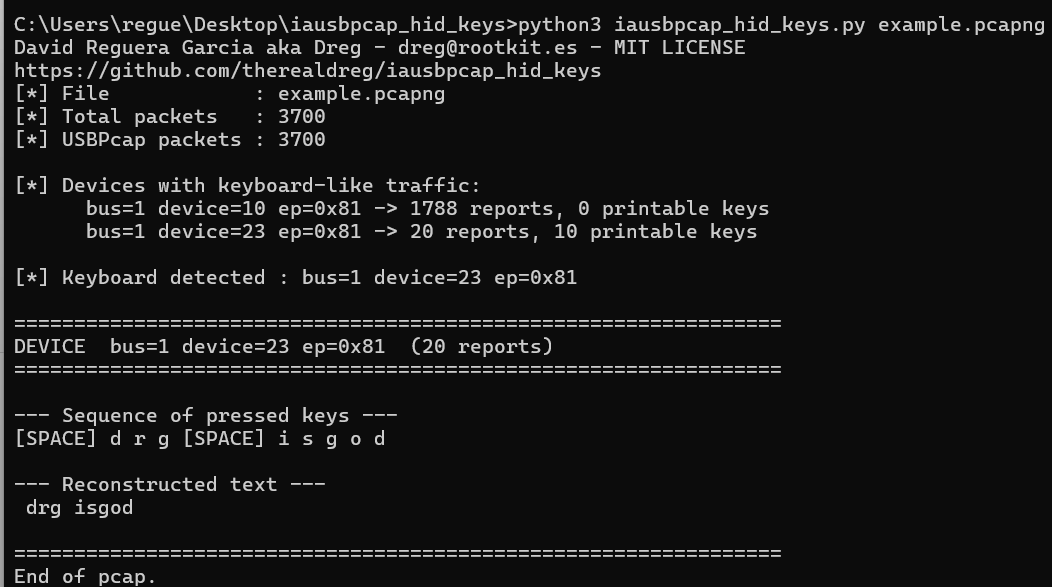
iausbpcap_hid_keys
Extract HID keyboard keystrokes from a USBPcap capture. Pure Python 3, zero dependencies, parses the pcap/pcapng and USBPcap headers directly.
- 1
- Python
- MIT
- 5 mo ago

