smart-contract-vulndb
🍋 An open dataset containing smart contract audit issues from various sources.
- 244
- JavaScript
- 3 y ago
🍋 An open dataset containing smart contract audit issues from various sources.
18 Claude Code skill files for smart contract security — built from 2,749 Immunefi reports, 681 DeFiHack reproductions, and real hunt experience
This repo contains anti-hack checklists, which will help projects to build and develop secure DeFi applications. If you find anything missing or want to update existing resources, you can create a pull request and contribute to the project.
Unified knowledge base of Soroban common vulnerabilities and best practices
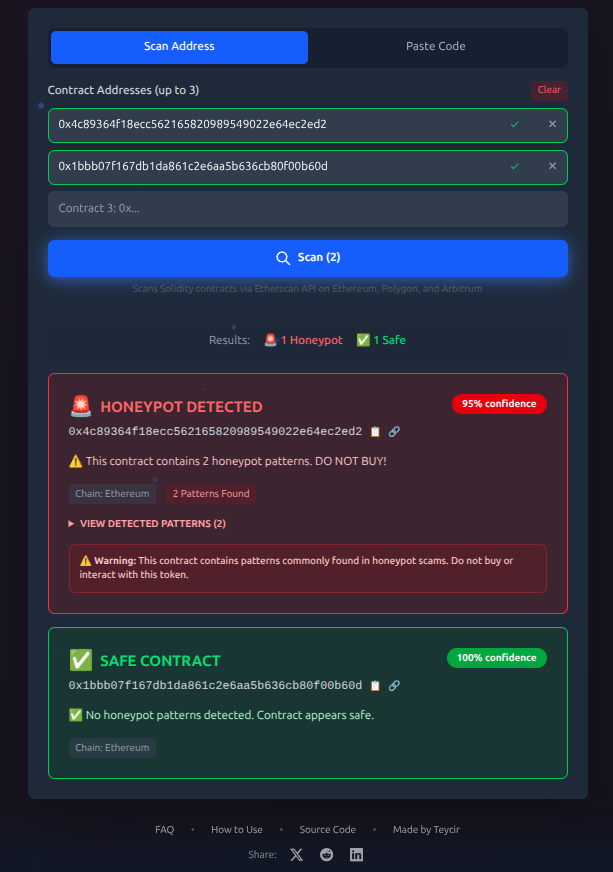
Free honeypot token scanner for Ethereum, Polygon & Arbitrum. Detect scam tokens before you buy. Instant analysis of smart contracts using 13 specialized patterns. No API keys, no limits, 100% free. Built with Next.js 16 & Cloudflare Workers.
AI agent safety layer for crypto transactions - blocks honeypots, blacklists, and rug pulls before they happen
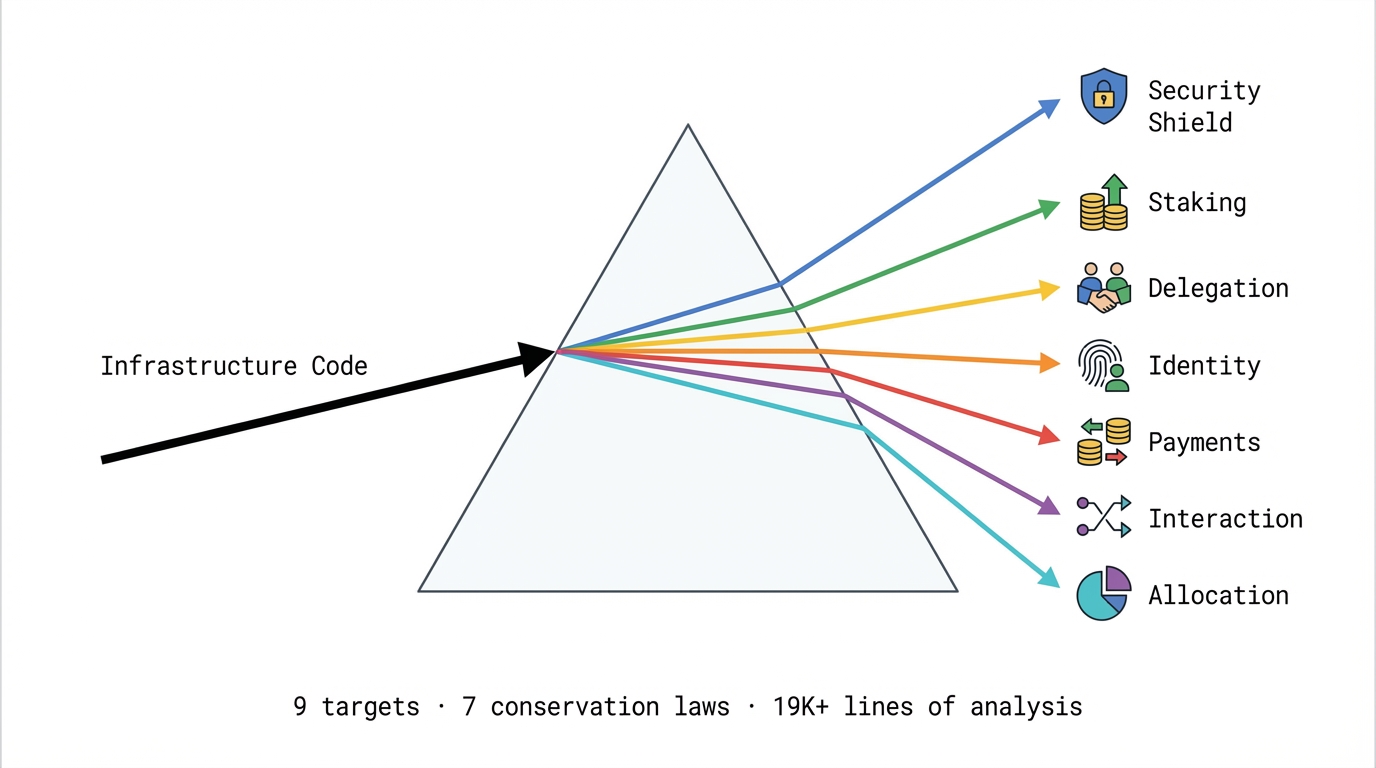
Structural trust analysis for infrastructure code. 9 targets, 7 conservation laws, 19K+ lines of analysis. Synthesis Hackathon 2026.
Math proofs, checked by a computer, that 15 top Ethereum tokens (WBTC, LINK, DAI, UNI, SHIB, PEPE...) do what they promise. Proved in Lean 4 on the exact deployed bytecode, for every input and caller.
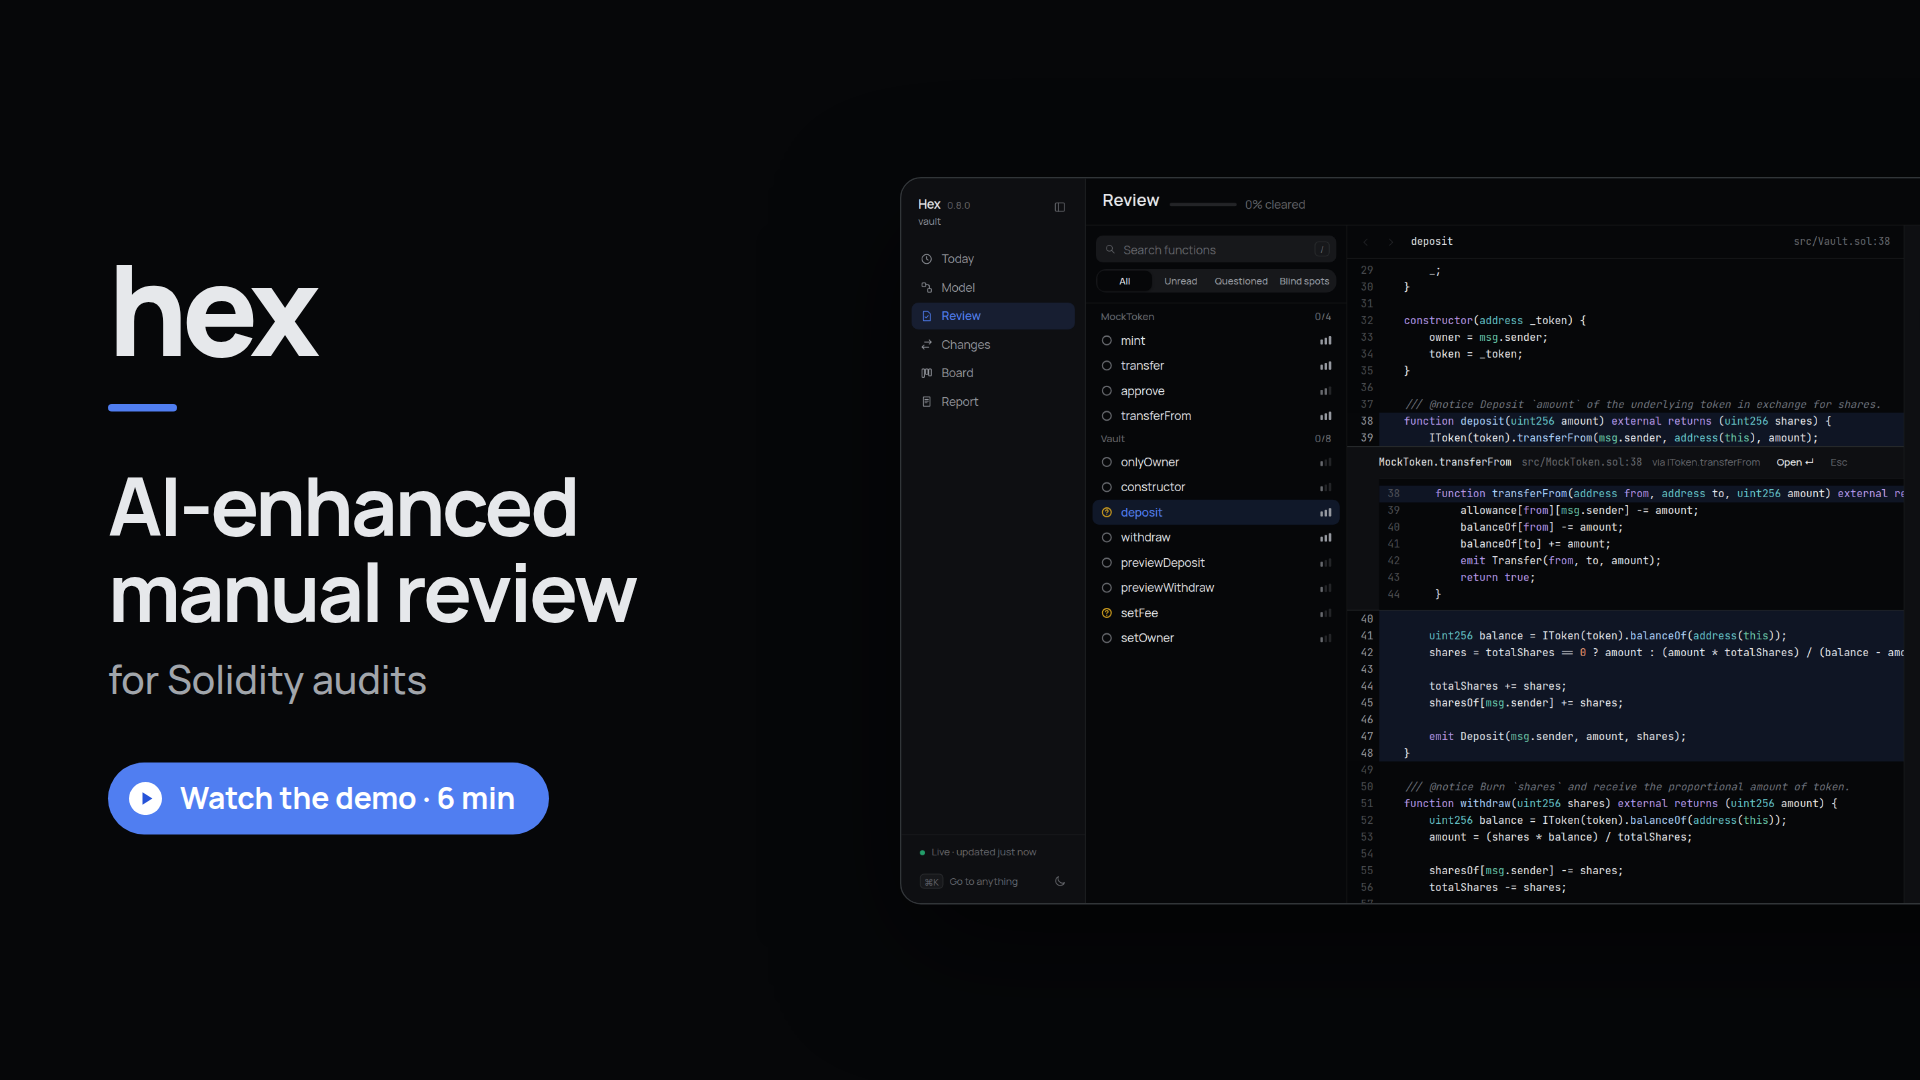
A toolkit for Solidity smart contract auditors. SolAudit combines CLI analysis tools, Claude Code skills, and a local dashboard to take you from "I just received the code" to "here are my validated findings" — faster and with better coverage.
High-performance Rust tool for detecting security vulnerabilities in smart contracts. Ethereum mainnet support with YAML-based pattern templates, CI/CD integration, and SARIF output for GitHub Security tab.
Non-custodial agent wallet toolkit plus a gated Solidity workflow: EVM and Bitcoin CLI (init, send, swap, deploy) and a contract walk (spec, threat model, audit, deploy) with an in-process EVM sandbox. solc 0.8.36, no Foundry, no node, no funds. Local keys, JSON envelope, /skills add.
Solidity risk scan: a first pass before an audit. Reads .sol files and lists, with file:line:column, state changes with no access check, ignored low-level call results, external calls before state writes, tx.origin checks, delegatecall, selfdestruct, block-value randomness and loops over state arrays. A heuristic, not an audit.