DependencyCheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
- 7.8k
- Java
- Apache-2.0
- 3 d ago
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
Dependency-Track is an intelligent Component Analysis platform that allows organizations to identify and reduce risk in the software supply chain.
:mag: ScanCode detects licenses, copyrights, dependencies by "scanning code" ... to discover and inventory open source and third-party packages used in your code. Sponsored by NLnet, the Google Summer of Code, Azure credits, nexB and other generous sponsors!
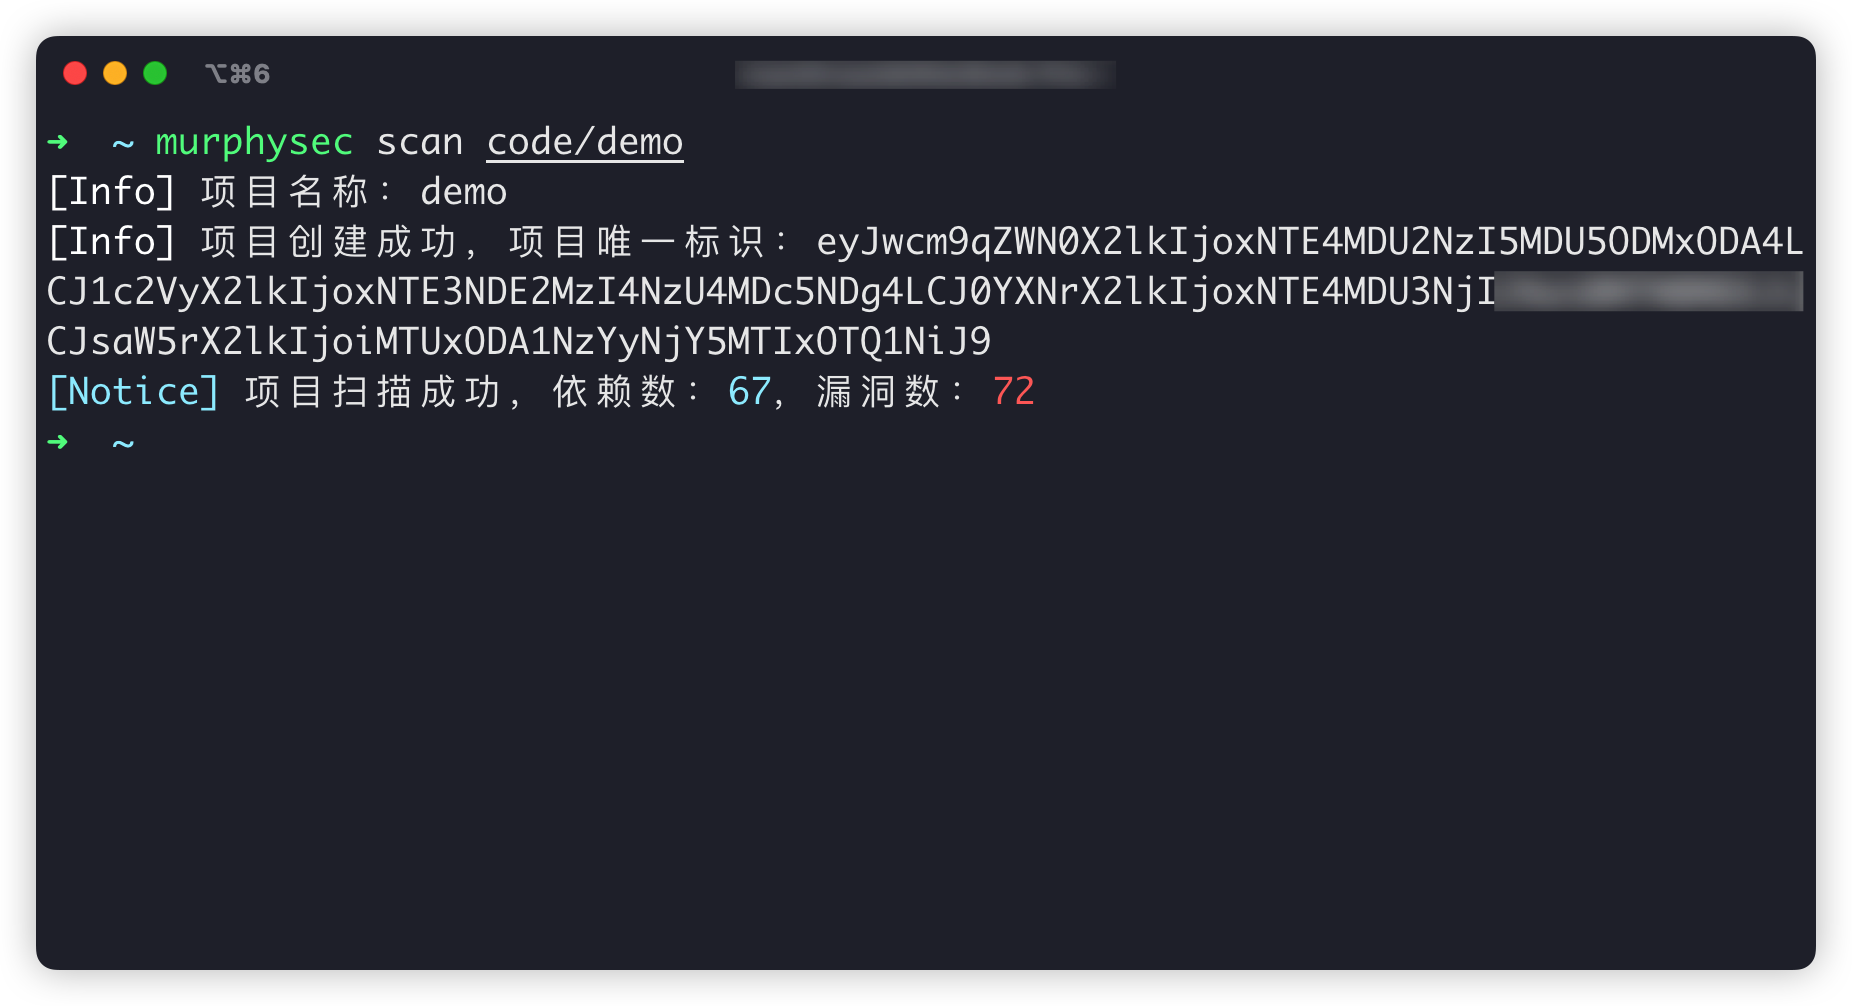
An open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。
OpenSCA is an open source software supply chain security solution that supports the detection of open source dependencies, vulnerabilities and license compliance with a widely noticed accuracy by the community.
ScanCode.io is a server to script and automate software composition analysis with pipelines. This project is sponsored by the European Commission, NLnet NGI0, the Google Summer of Code, nexB and others generous sponsors!