guarddog
:snake: :mag: GuardDog is a CLI tool to Identify malicious PyPI and npm packages
- 1.3k
- Python
- Apache-2.0
- 6 d ago
:snake: :mag: GuardDog is a CLI tool to Identify malicious PyPI and npm packages
OpenSCA is an open source software supply chain security solution that supports the detection of open source dependencies, vulnerabilities and license compliance with a widely noticed accuracy by the community.
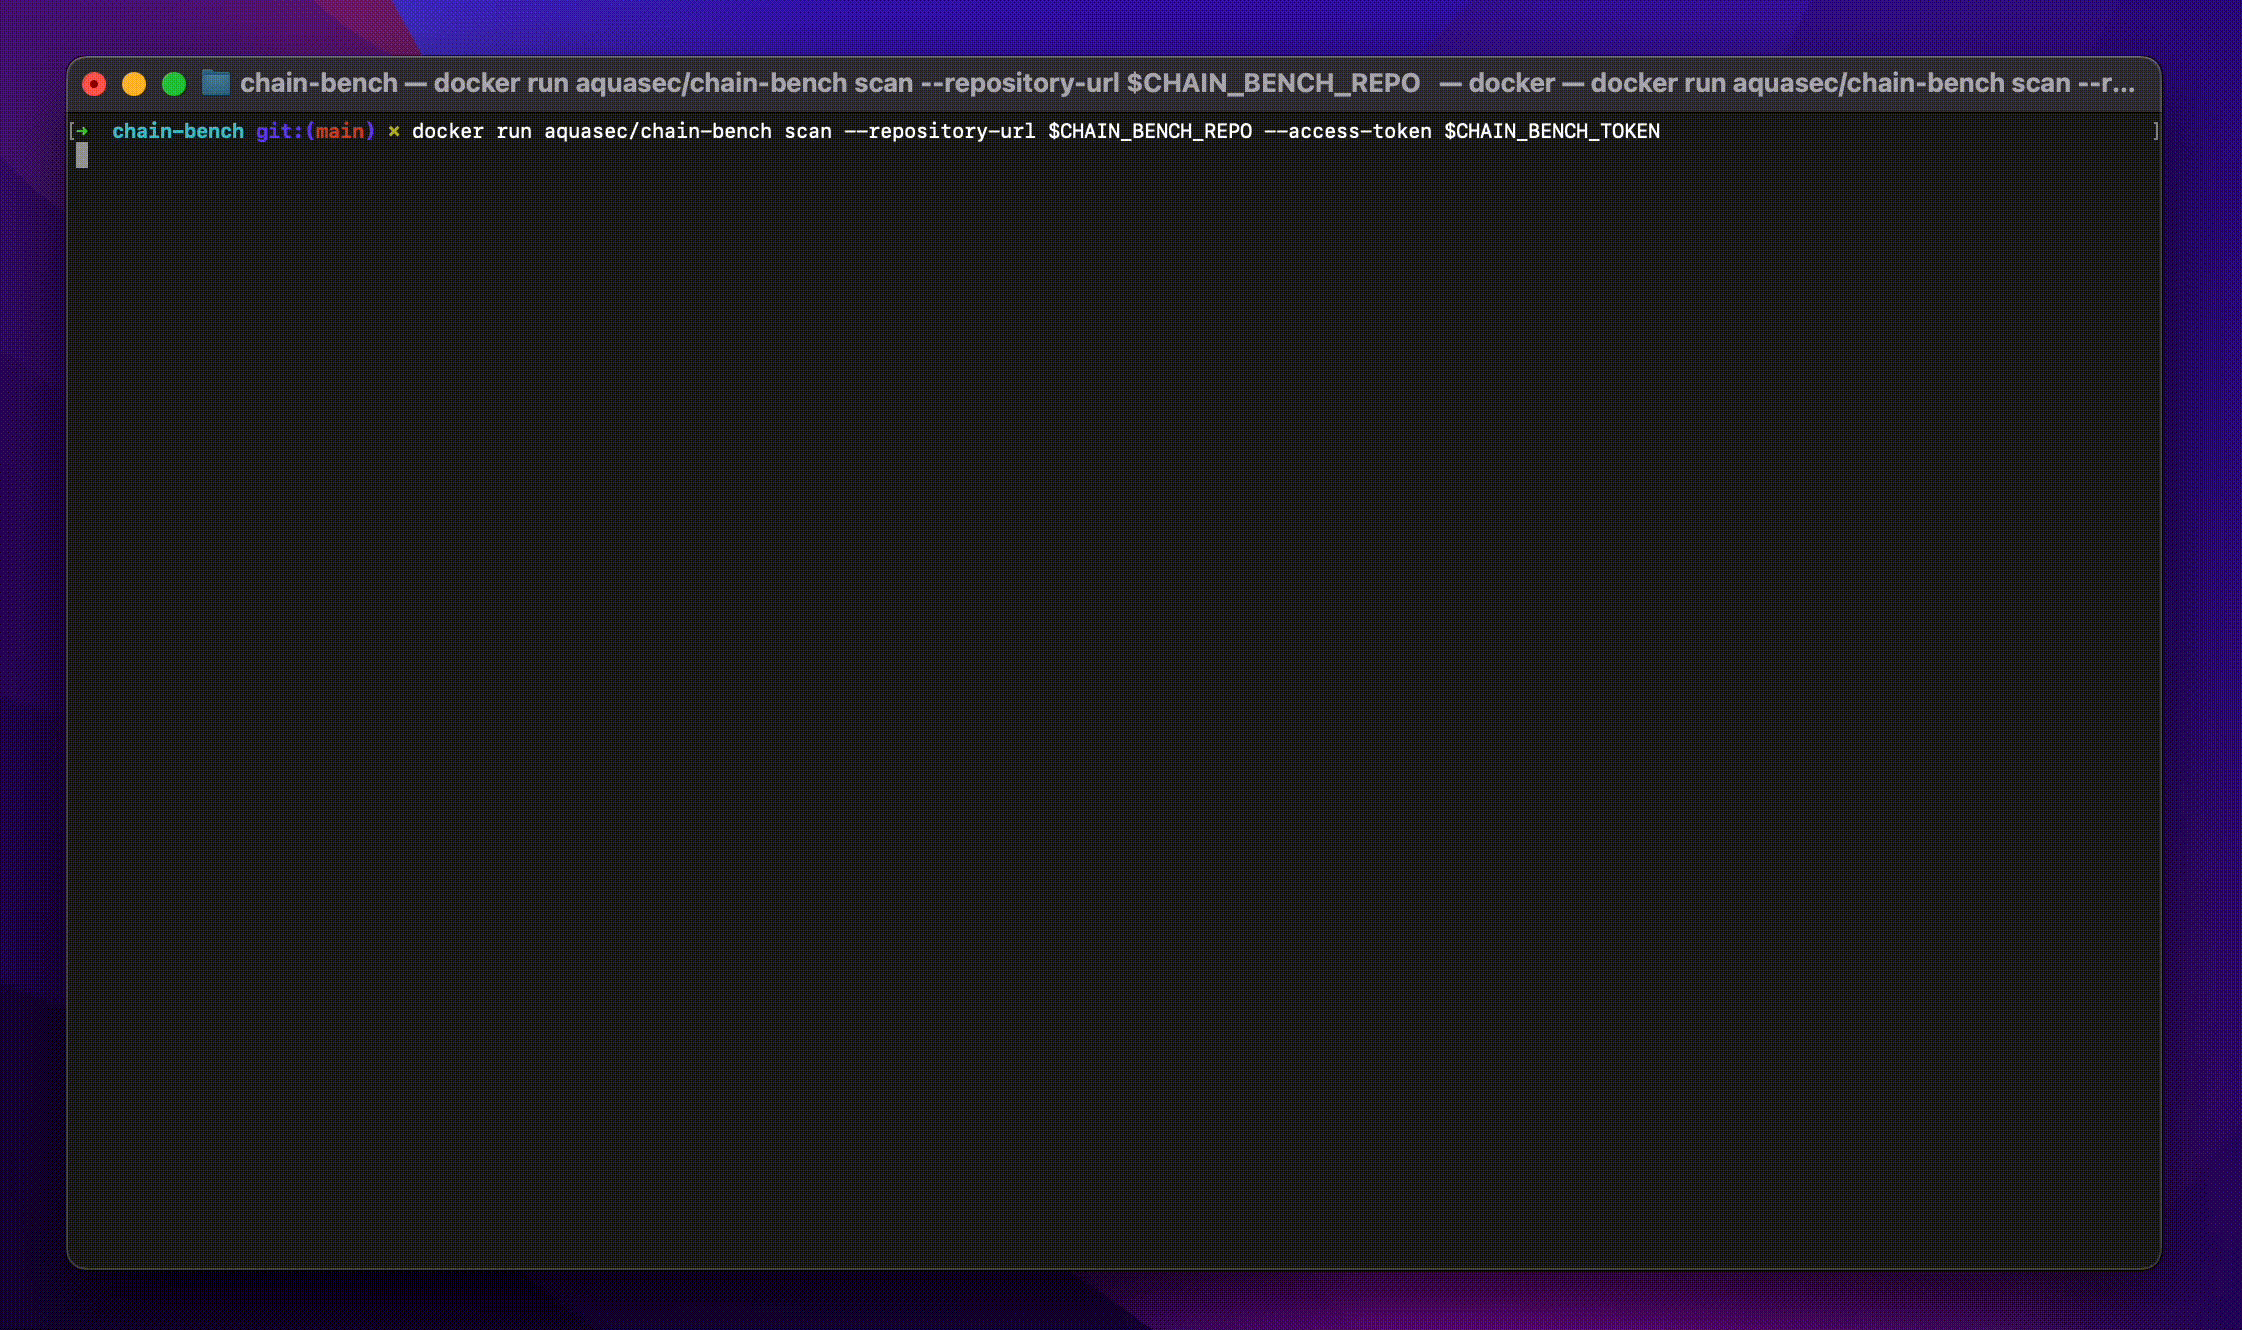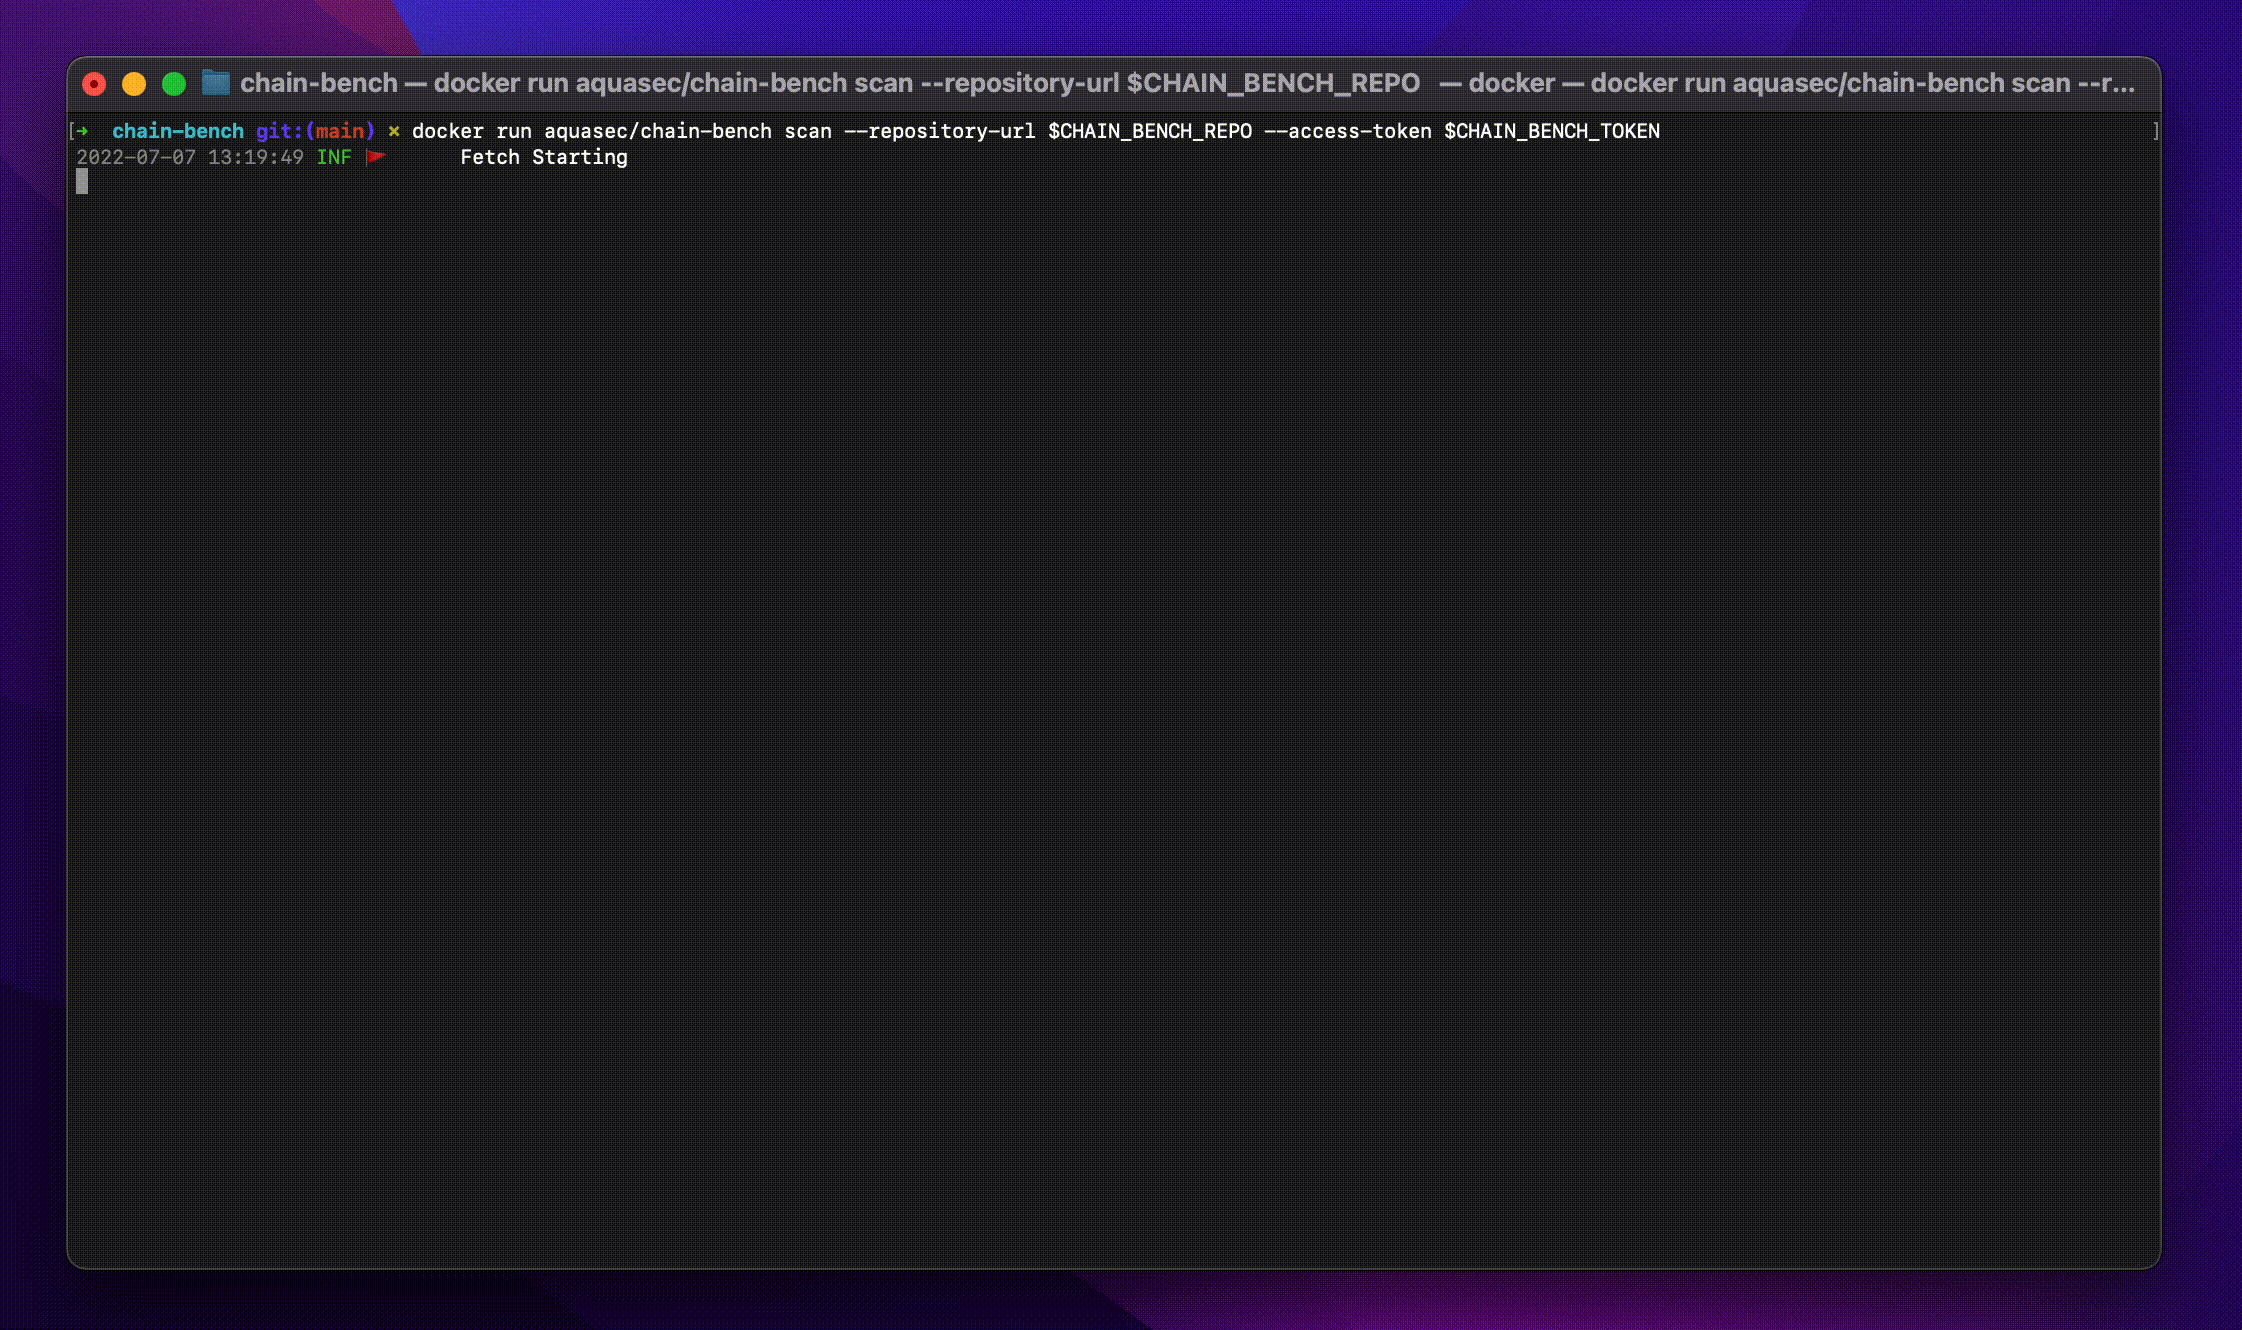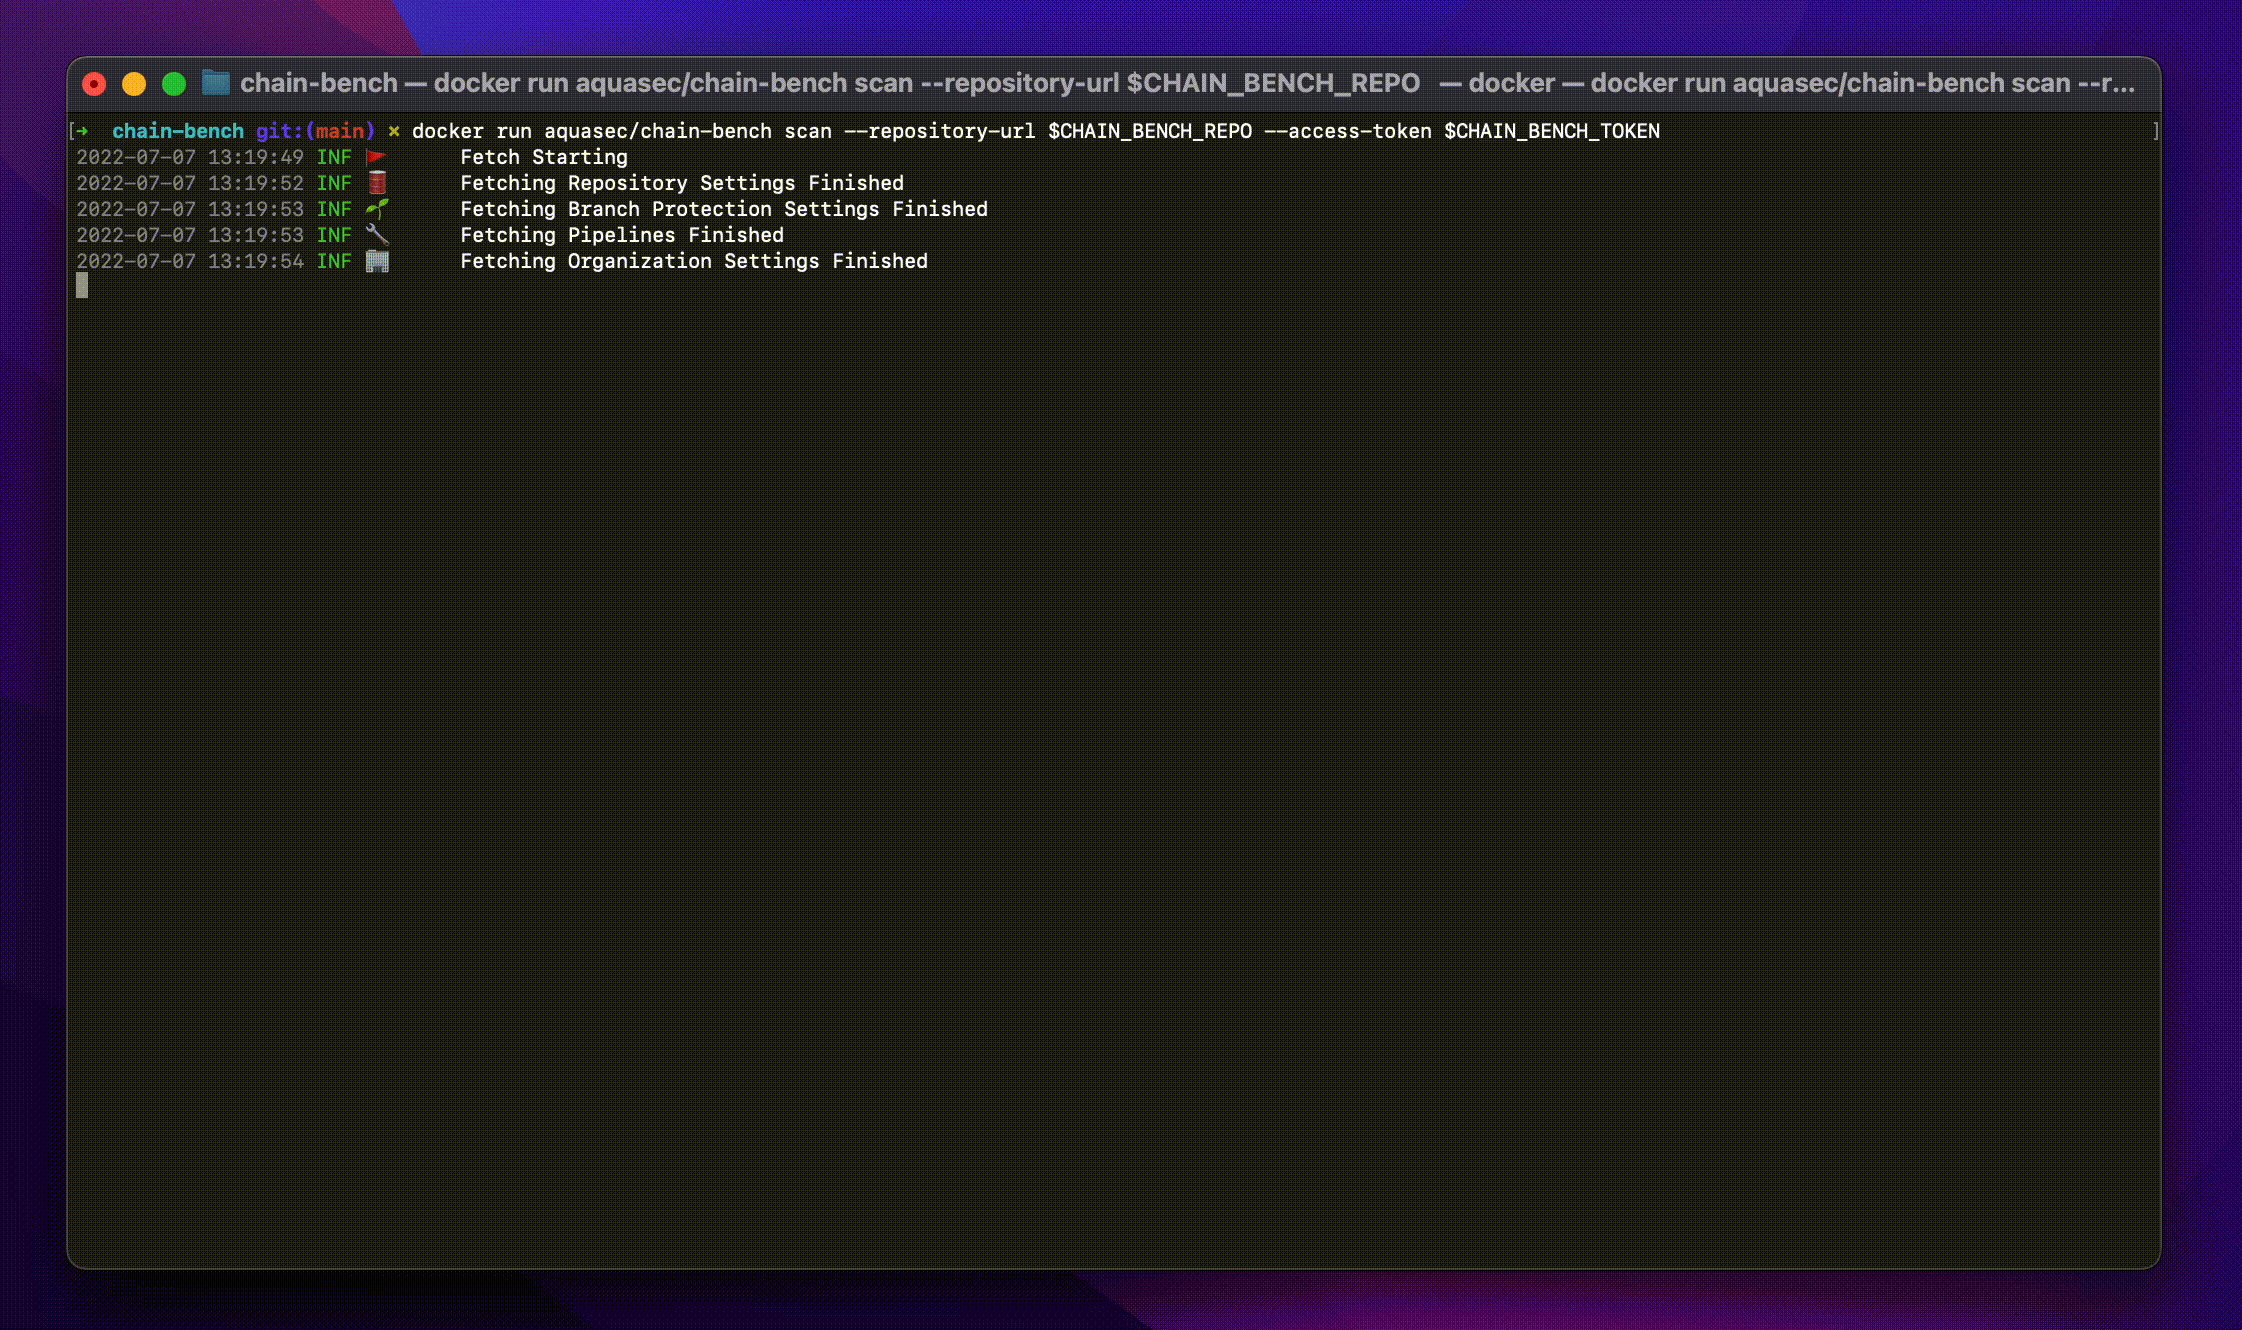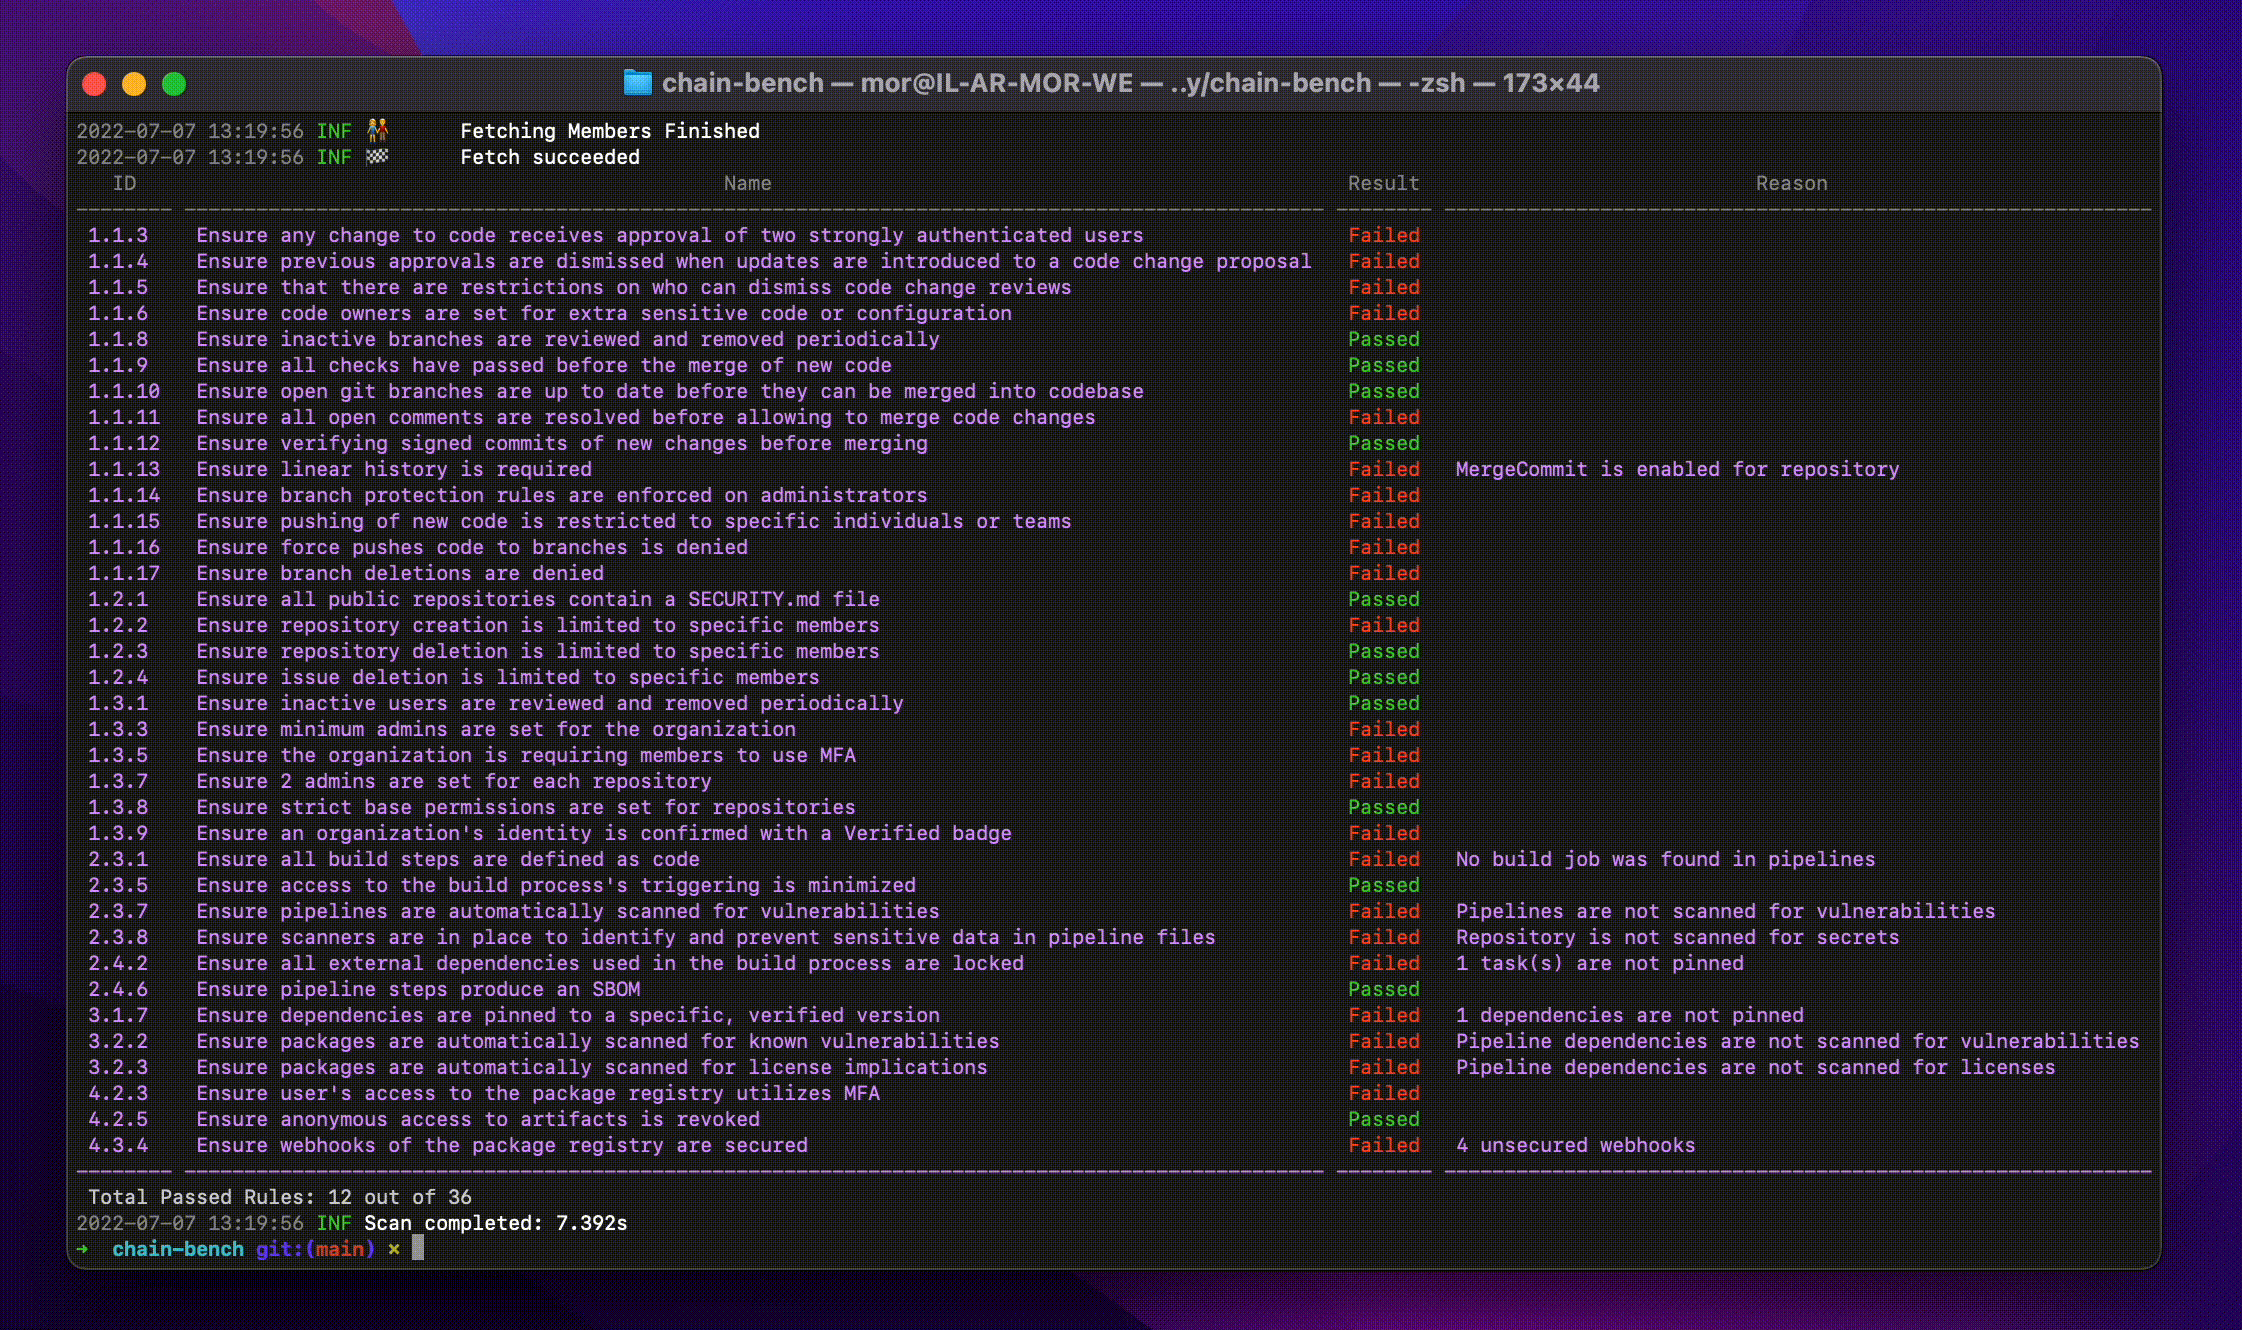
An open-source tool for auditing your software supply chain stack for security compliance based on a new CIS Software Supply Chain benchmark.
Supply Chain Firewall (SCFW) is a tool for preventing the installation of malicious npm and PyPI packages :fire:
Semantic SBOM/CBOM/AI-BOM diff, quality scoring, and compliance validation for CycloneDX/SPDX — component, license, and vulnerability change analysis, cryptographic inventory grading, PQC readiness (CNSA 2.0, NIST IR 8547), and regulatory gates for NTIA, FDA, EU CRA, BSI TR-03183, EUCC, SSDF, EO 14028, and the EU AI Act.
A compilation of resources in the software supply chain security domain, with emphasis on open source
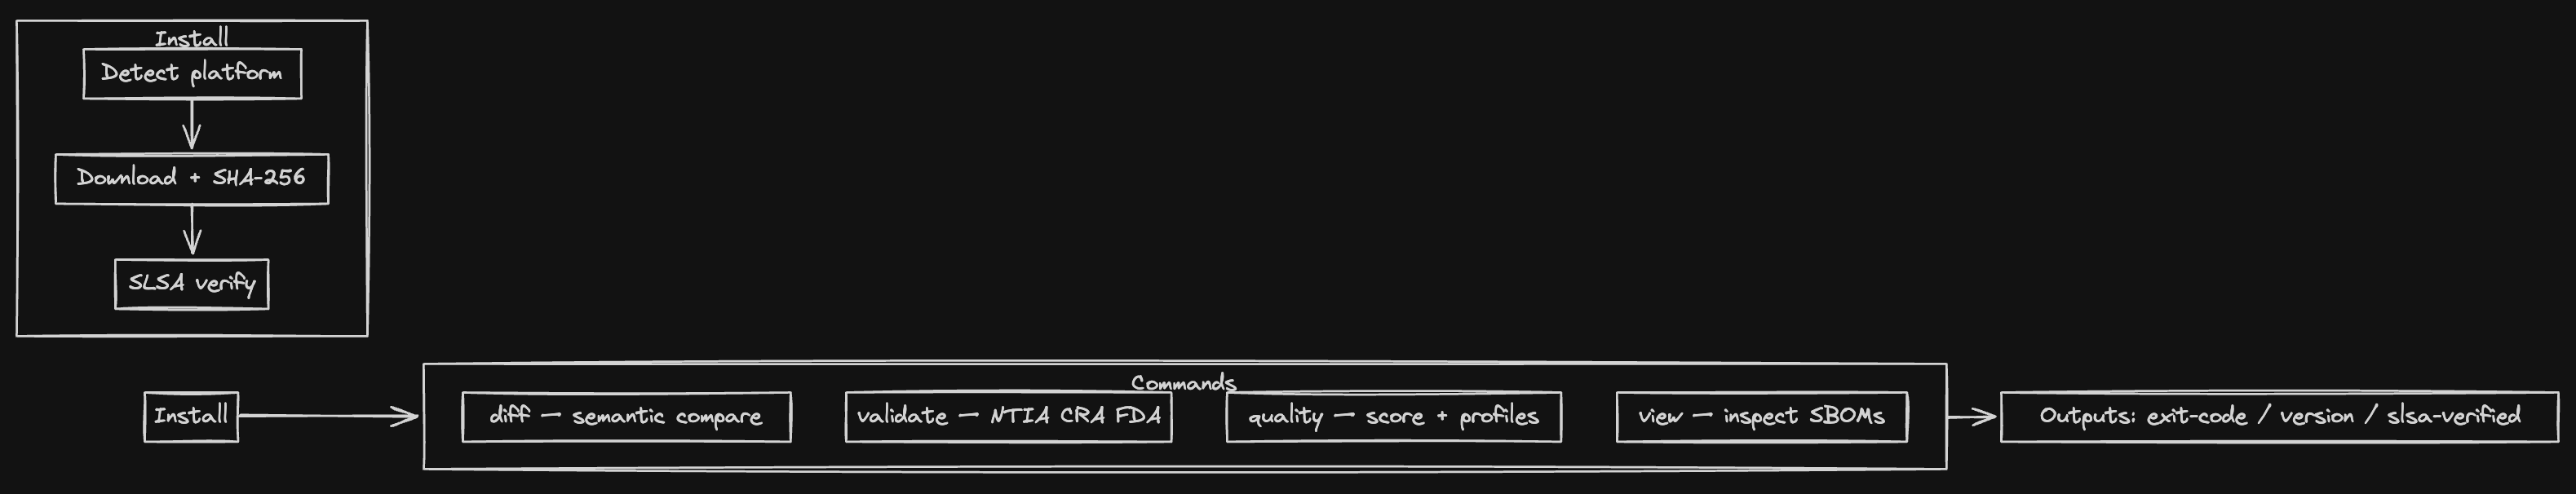
GitHub Action for installing and running sbom-tools — semantic SBOM diff, validation, and quality scoring
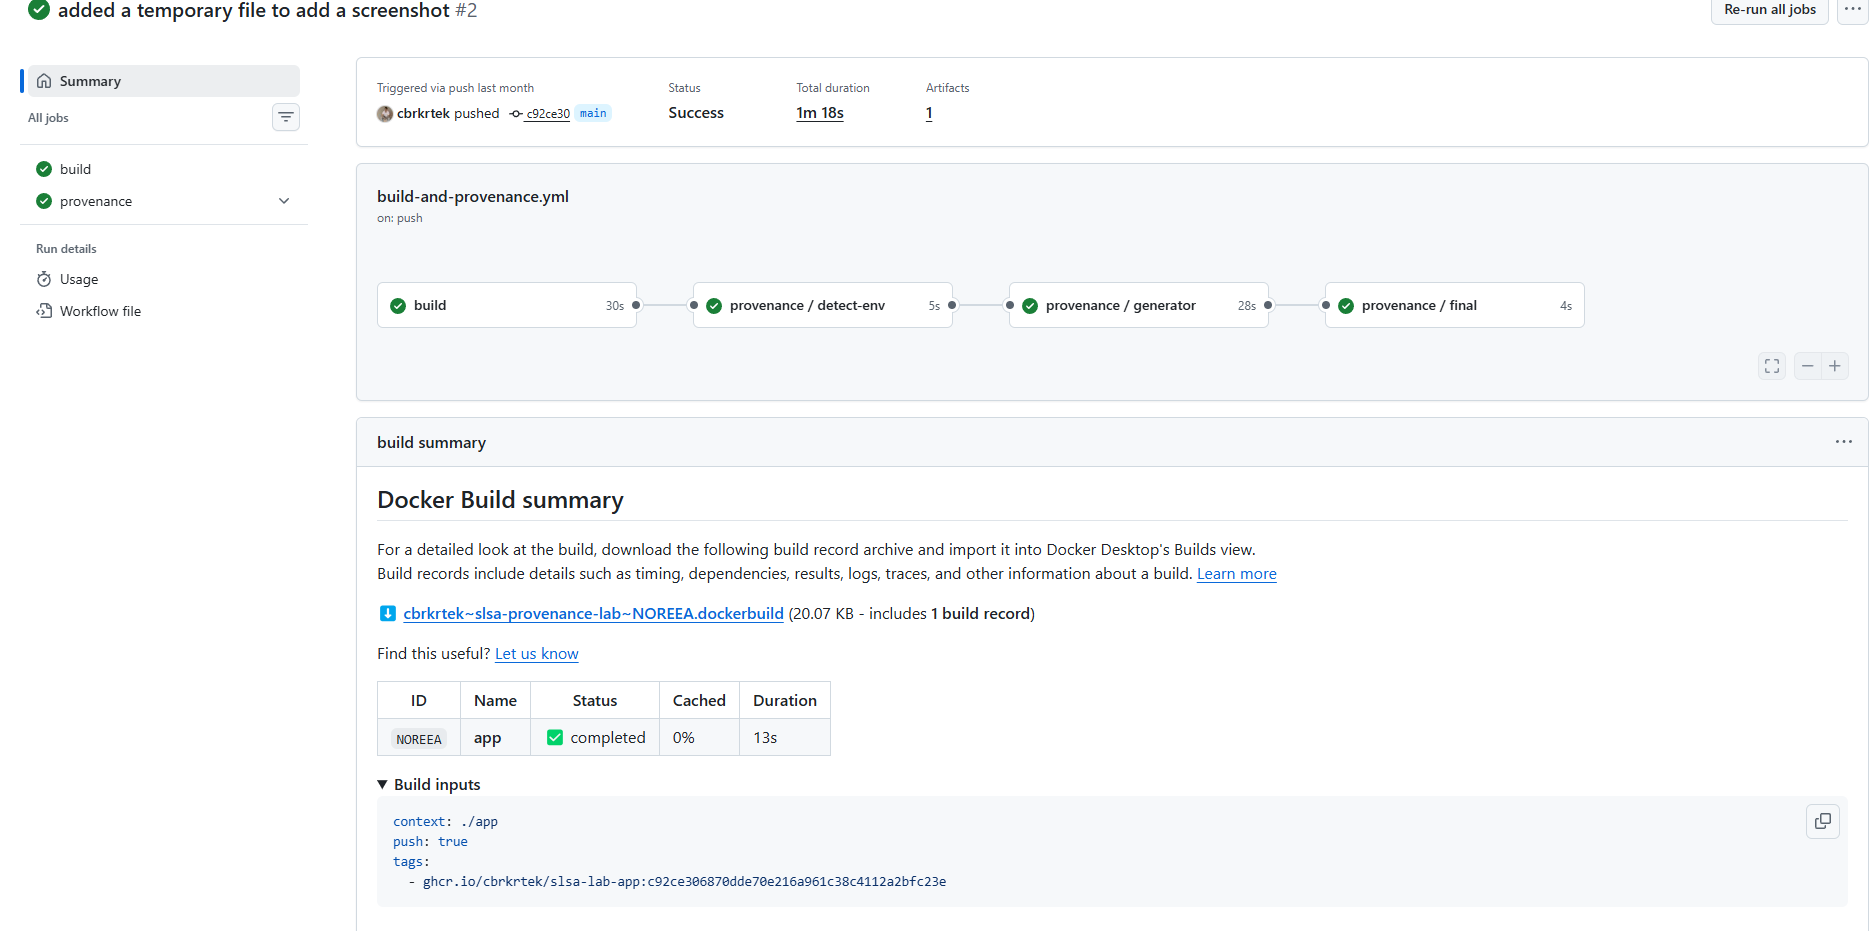
Cryptographic proof of how an artifact was built, not just that it wasn't tampered with. Hands-on lab comparing Cosign signing vs SLSA Level 3 provenance using GitHub Actions, slsa-github-generator and slsa-verifier - including a forged-provenance attack demo.