Malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata alerts.
- 2.6k
- Python
- 1 d ago
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata alerts.
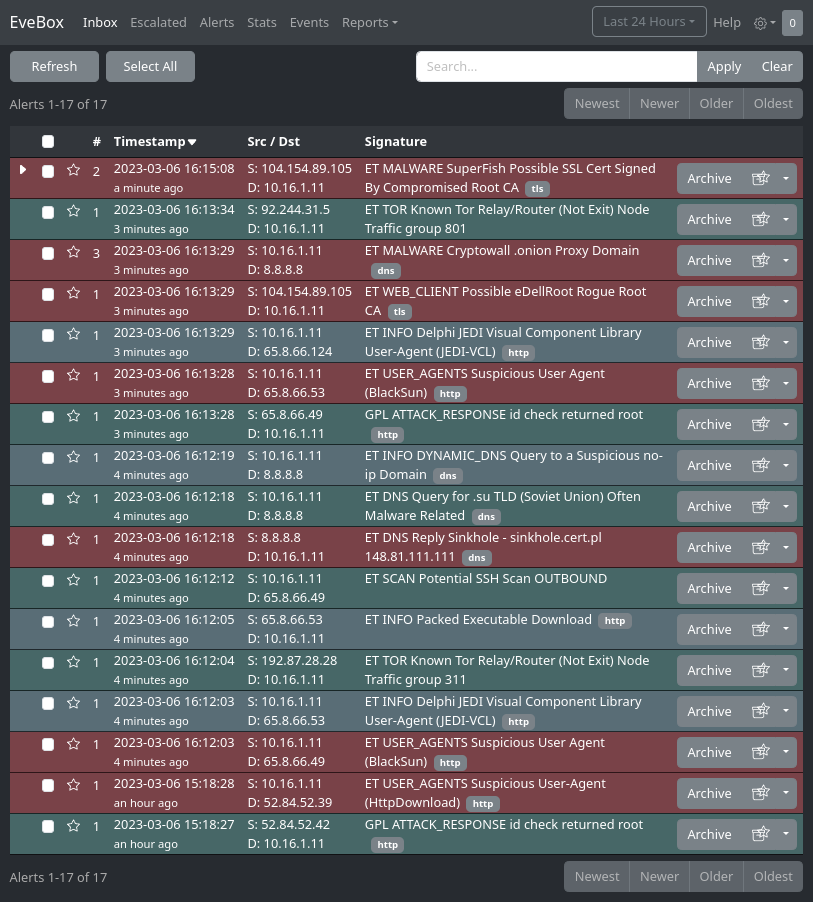
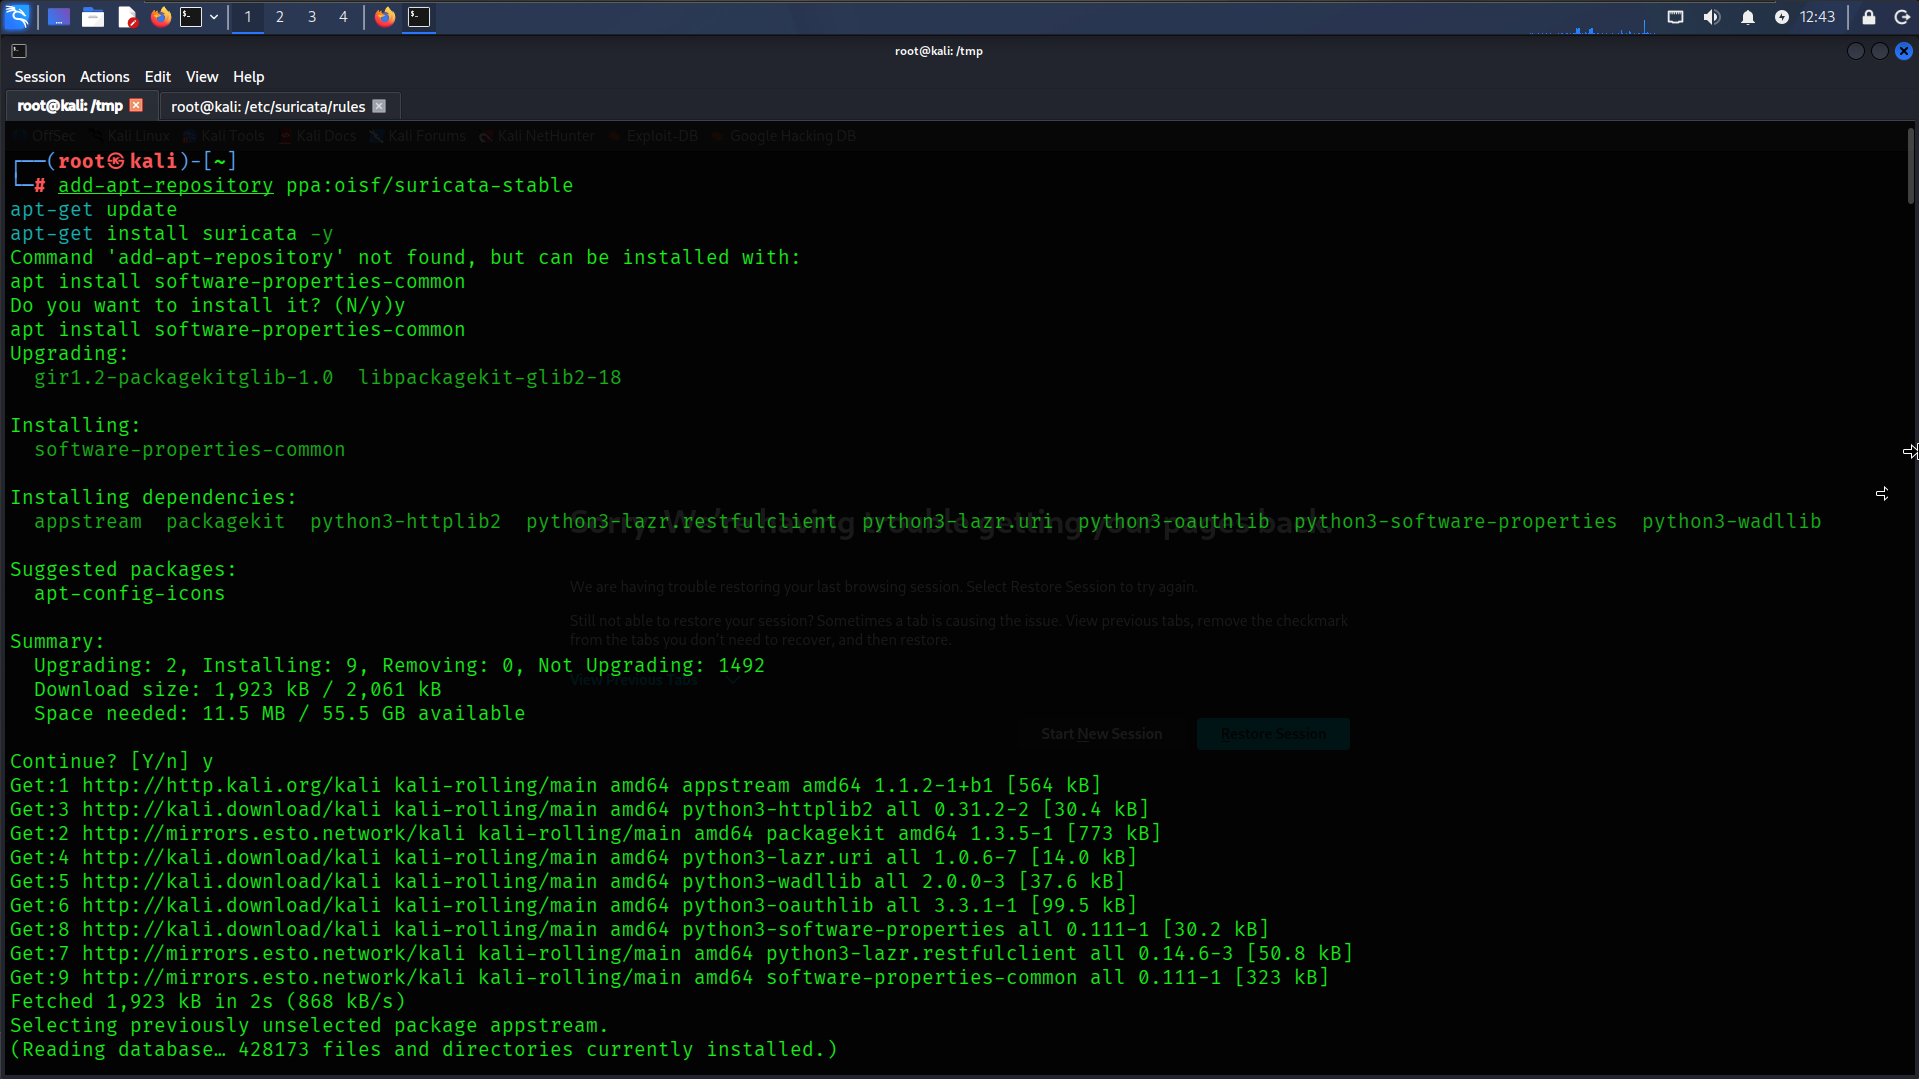
Suricata is a network Intrusion Detection System, Intrusion Prevention System and Network Security Monitoring engine developed by the OISF and the Suricata community.
Curated sources of indicators of compromise, detection signatures and IOC tools.
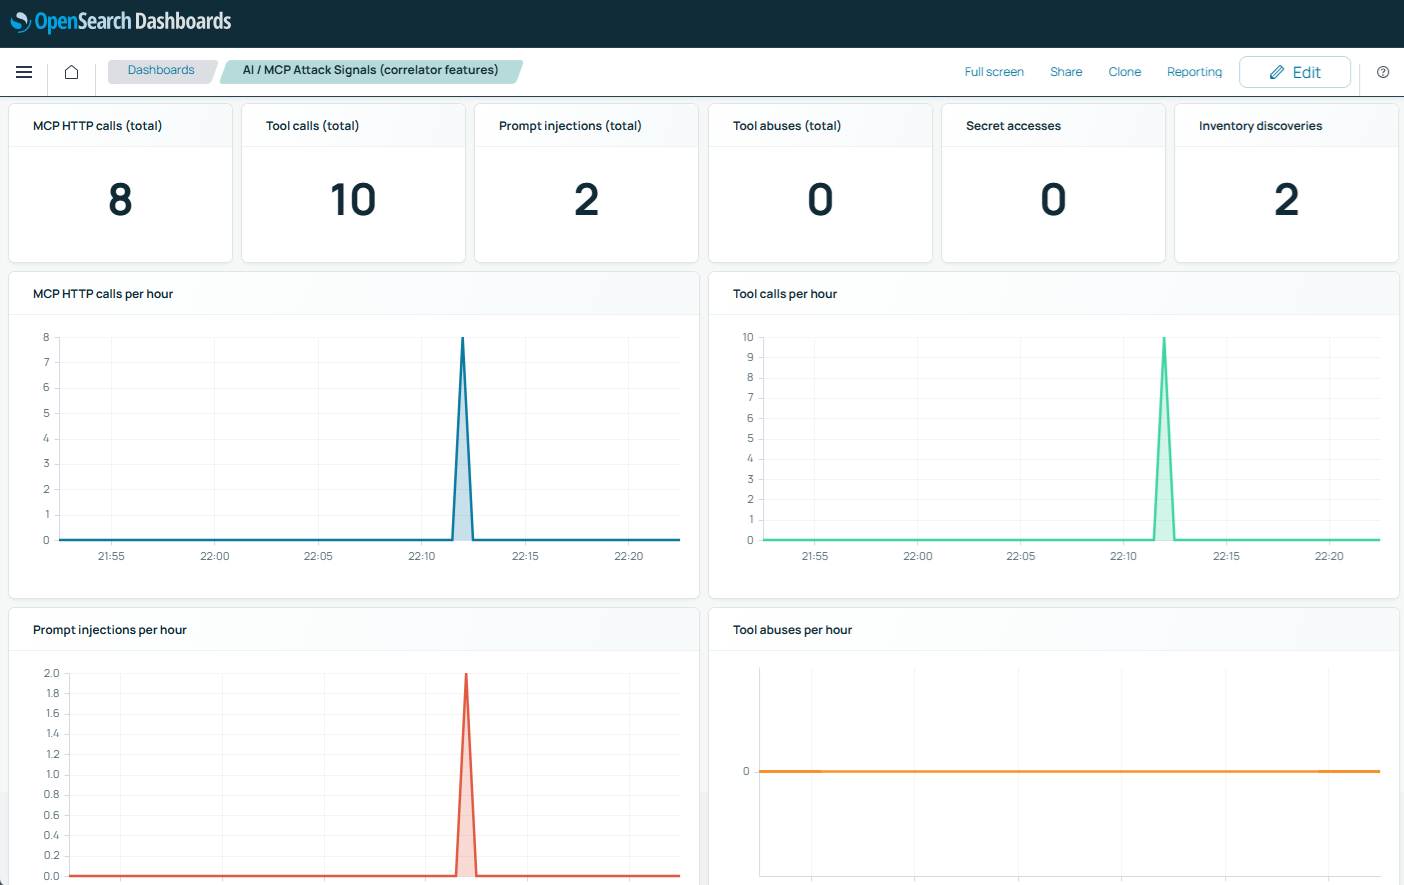
Collector/Correlator, Embedded log-based WAF, AI Patterns Classifier
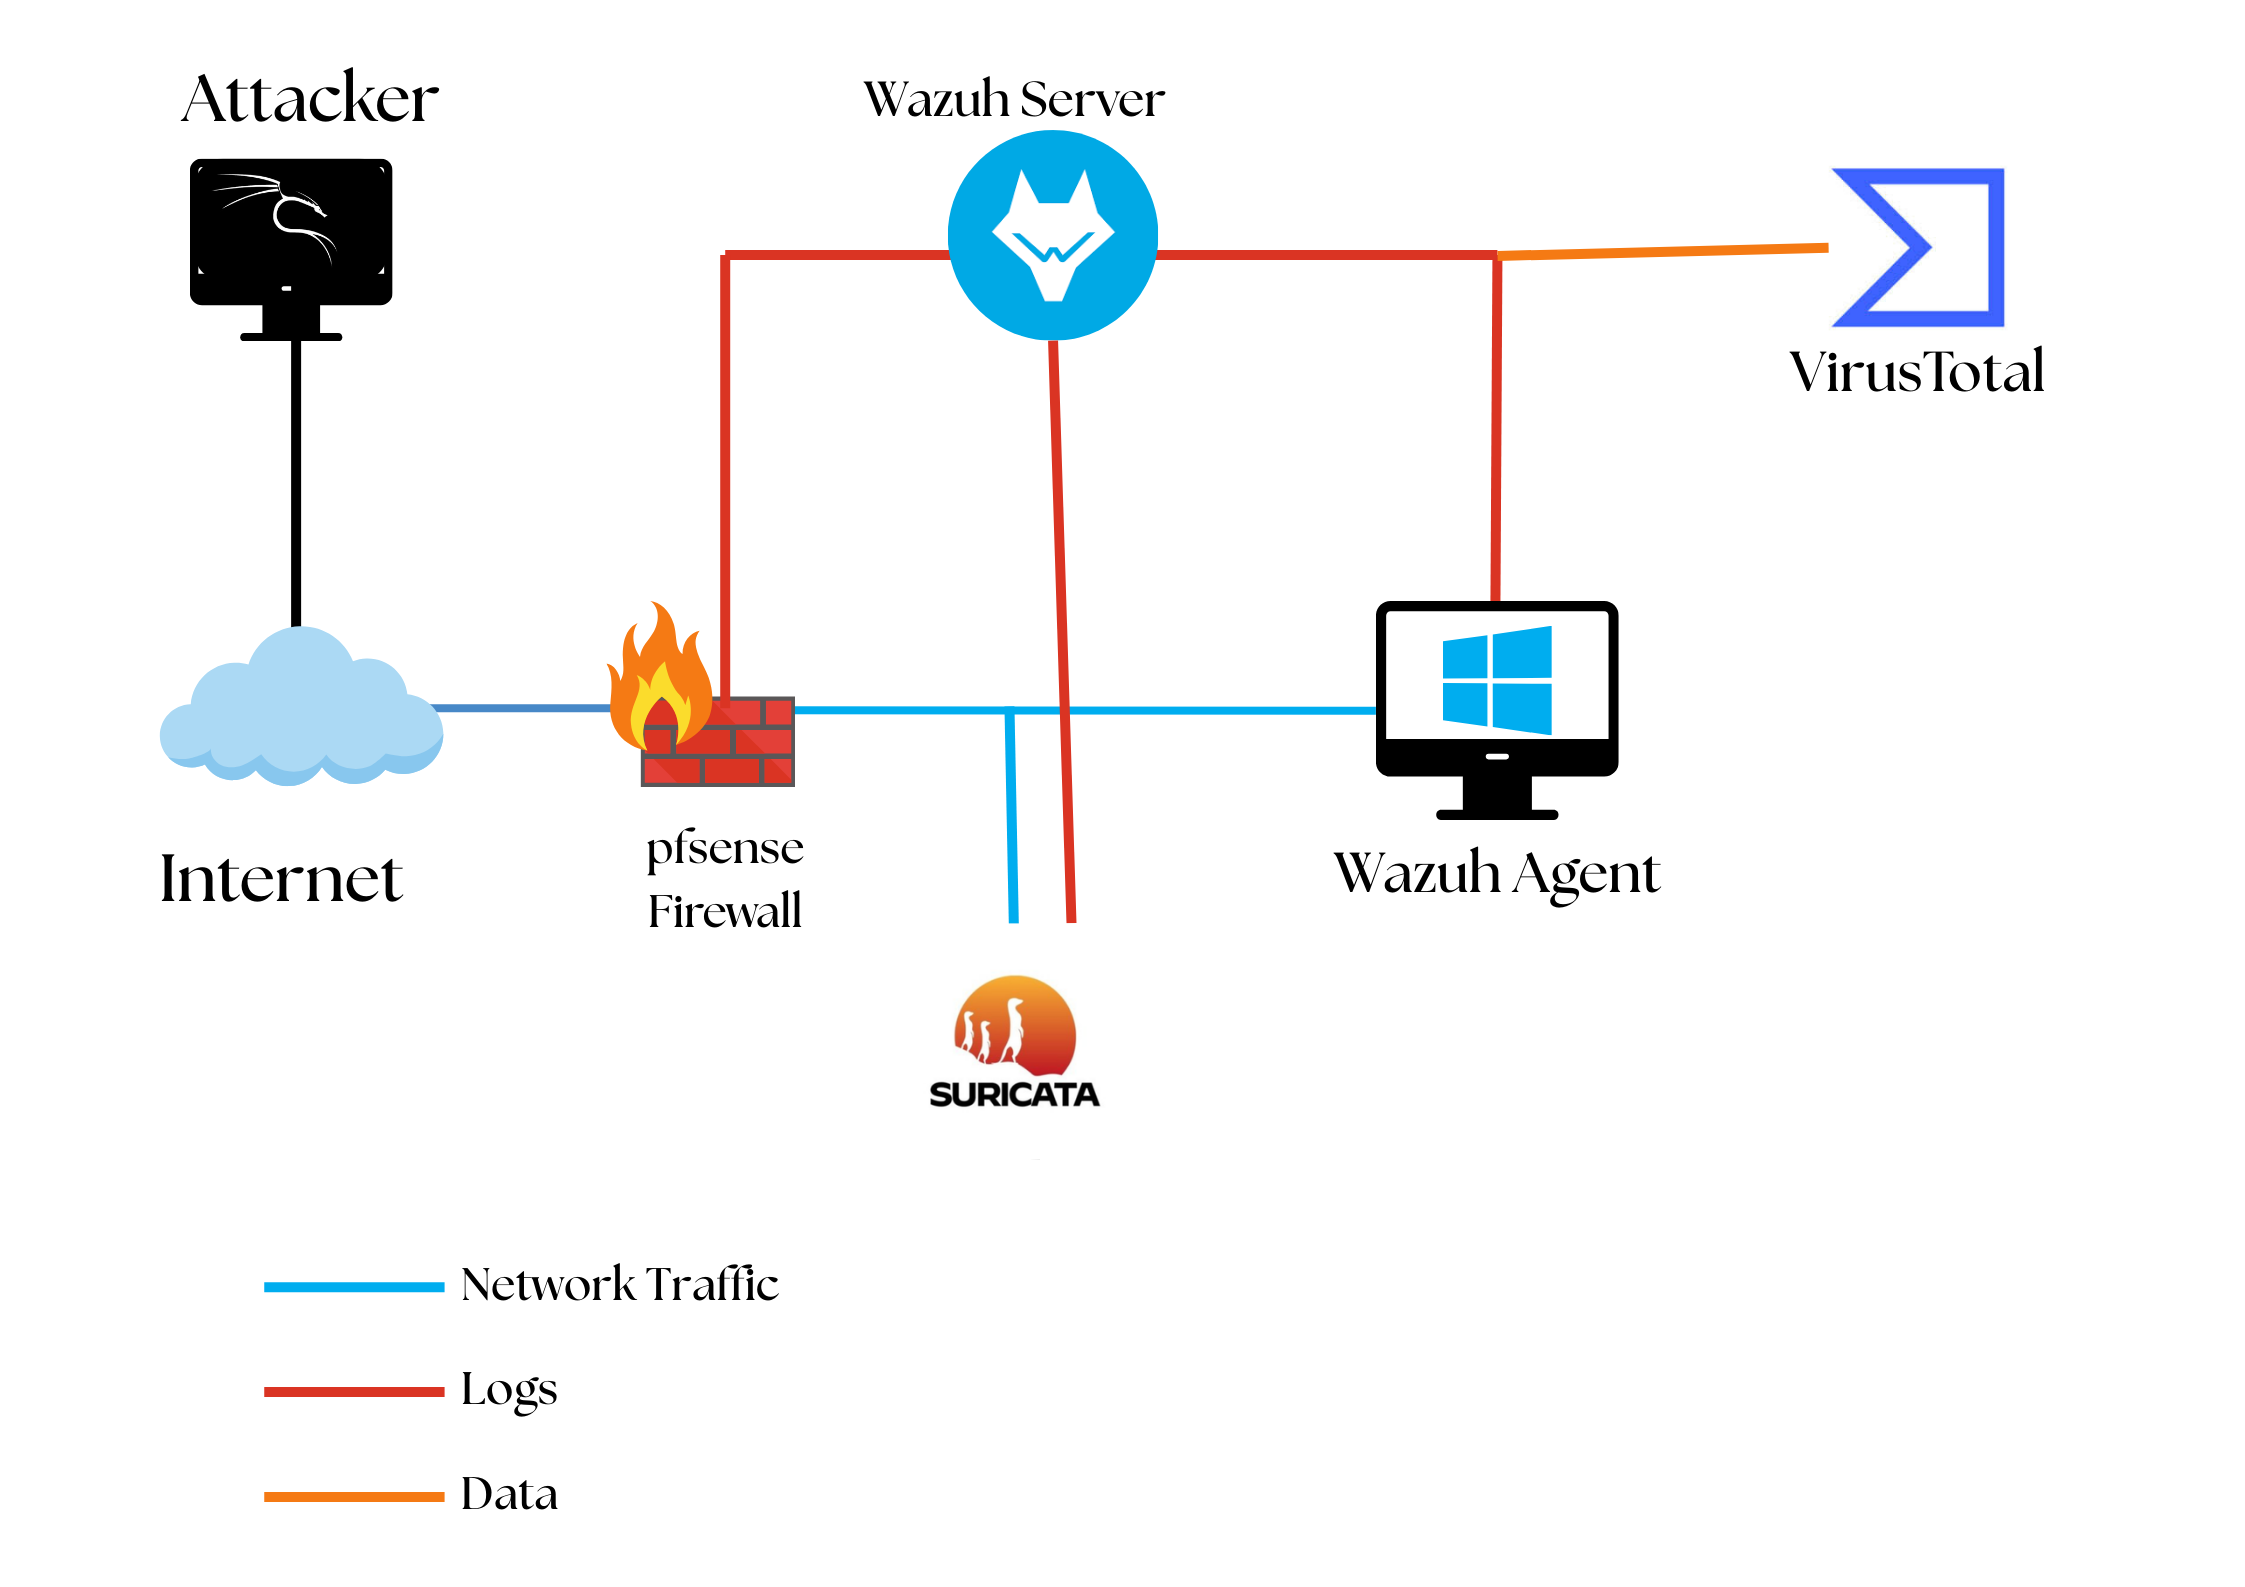
A SOC home lab built with Wazuh SIEM/XDR, pfSense, Suricata IDS/IPS, VirusTotal and Sysmon. Demonstrating log collection, threat detection, and attack simulation.
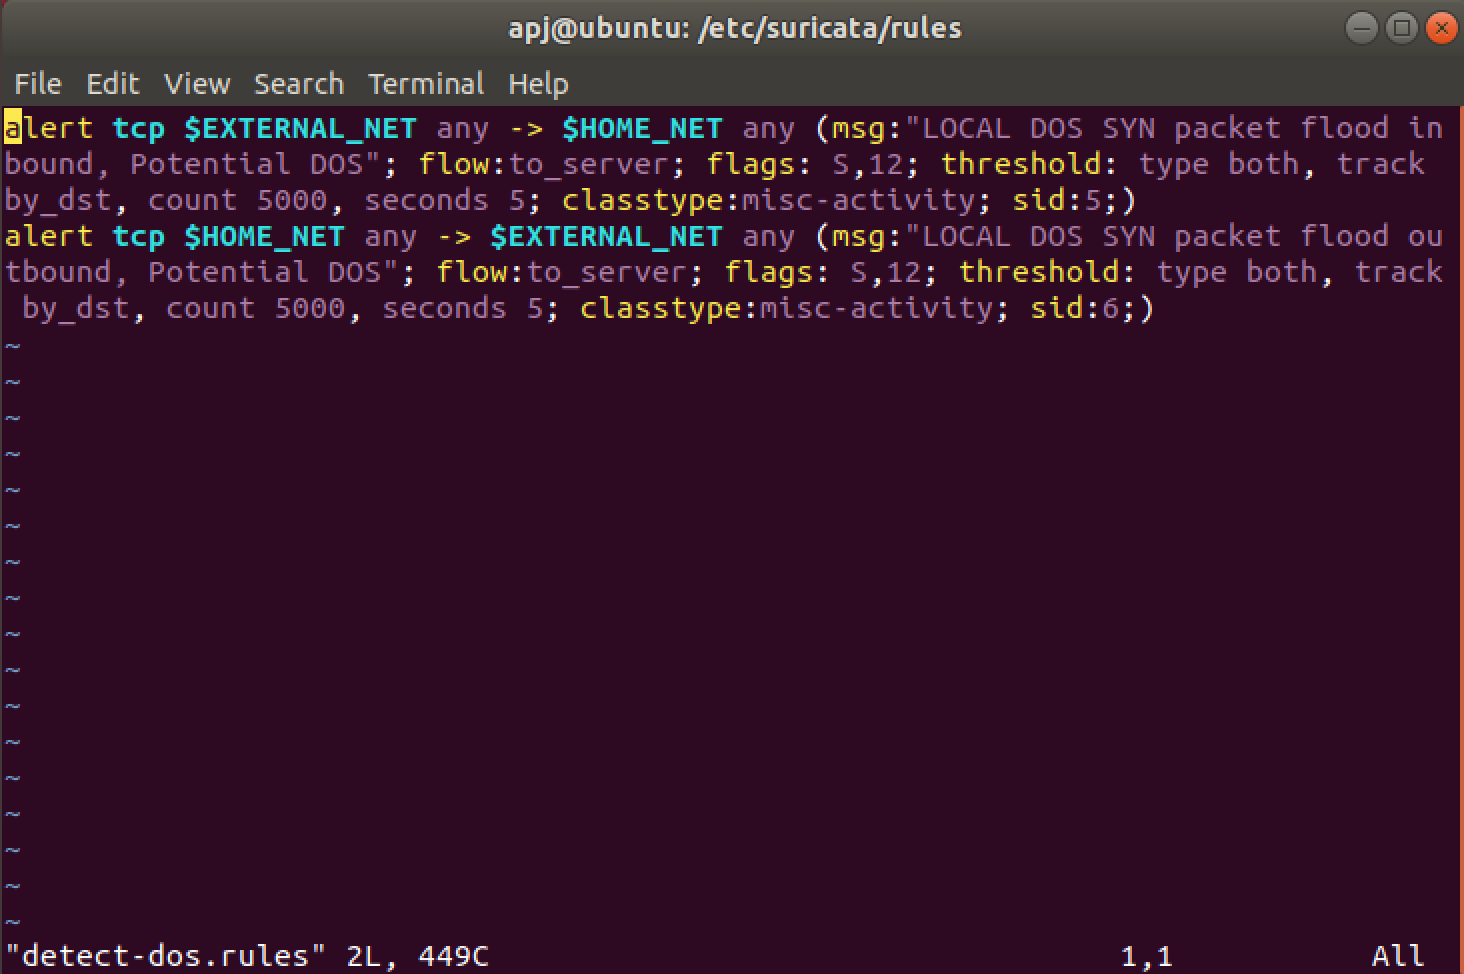
Configuring the Suricata IDS to detect DoS attacks by adding custom rule file.
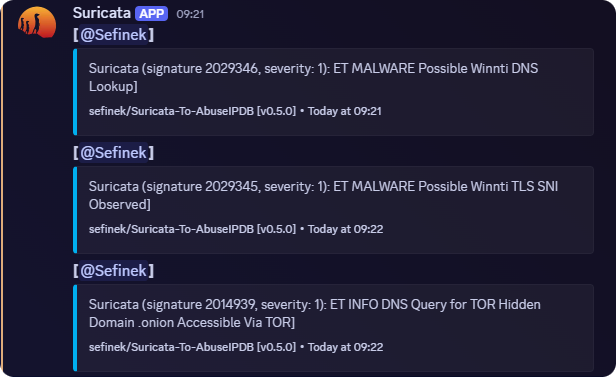
Integration tool that analyzes Suricata logs in real time and reports malicious IP addresses to AbuseIPDB.
Wazuh, Suricata, IDS, Threat Detection: Integrating Suricata with Wazuh to detect network reconnaissance activity and centralize security monitoring.