sysmon


sentinel-attack
Tools to rapidly deploy a threat hunting capability on Azure Sentinel that leverages Sysmon and MITRE ATT&CK
- 1.1k
- MIT
- 24 mo ago

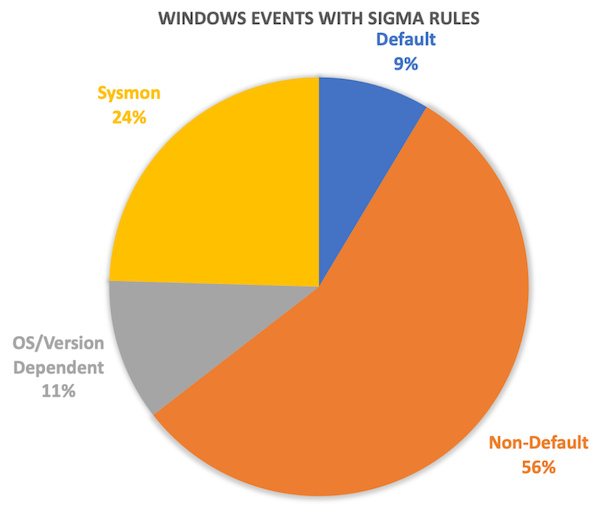
EnableWindowsLogSettings
Documentation and scripts to properly enable Windows event logs.
- 734
- Batchfile
- GPL-3.0
- 14 mo ago

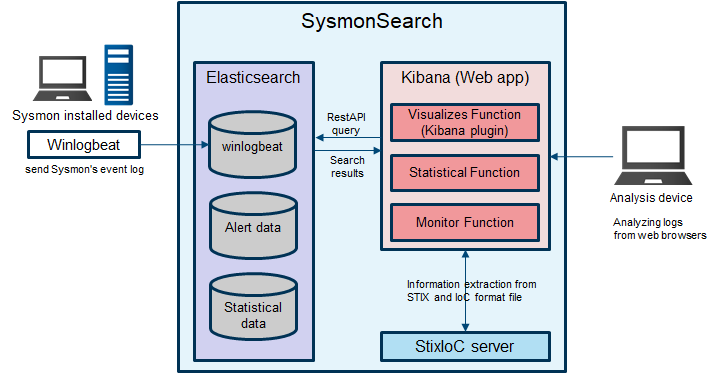

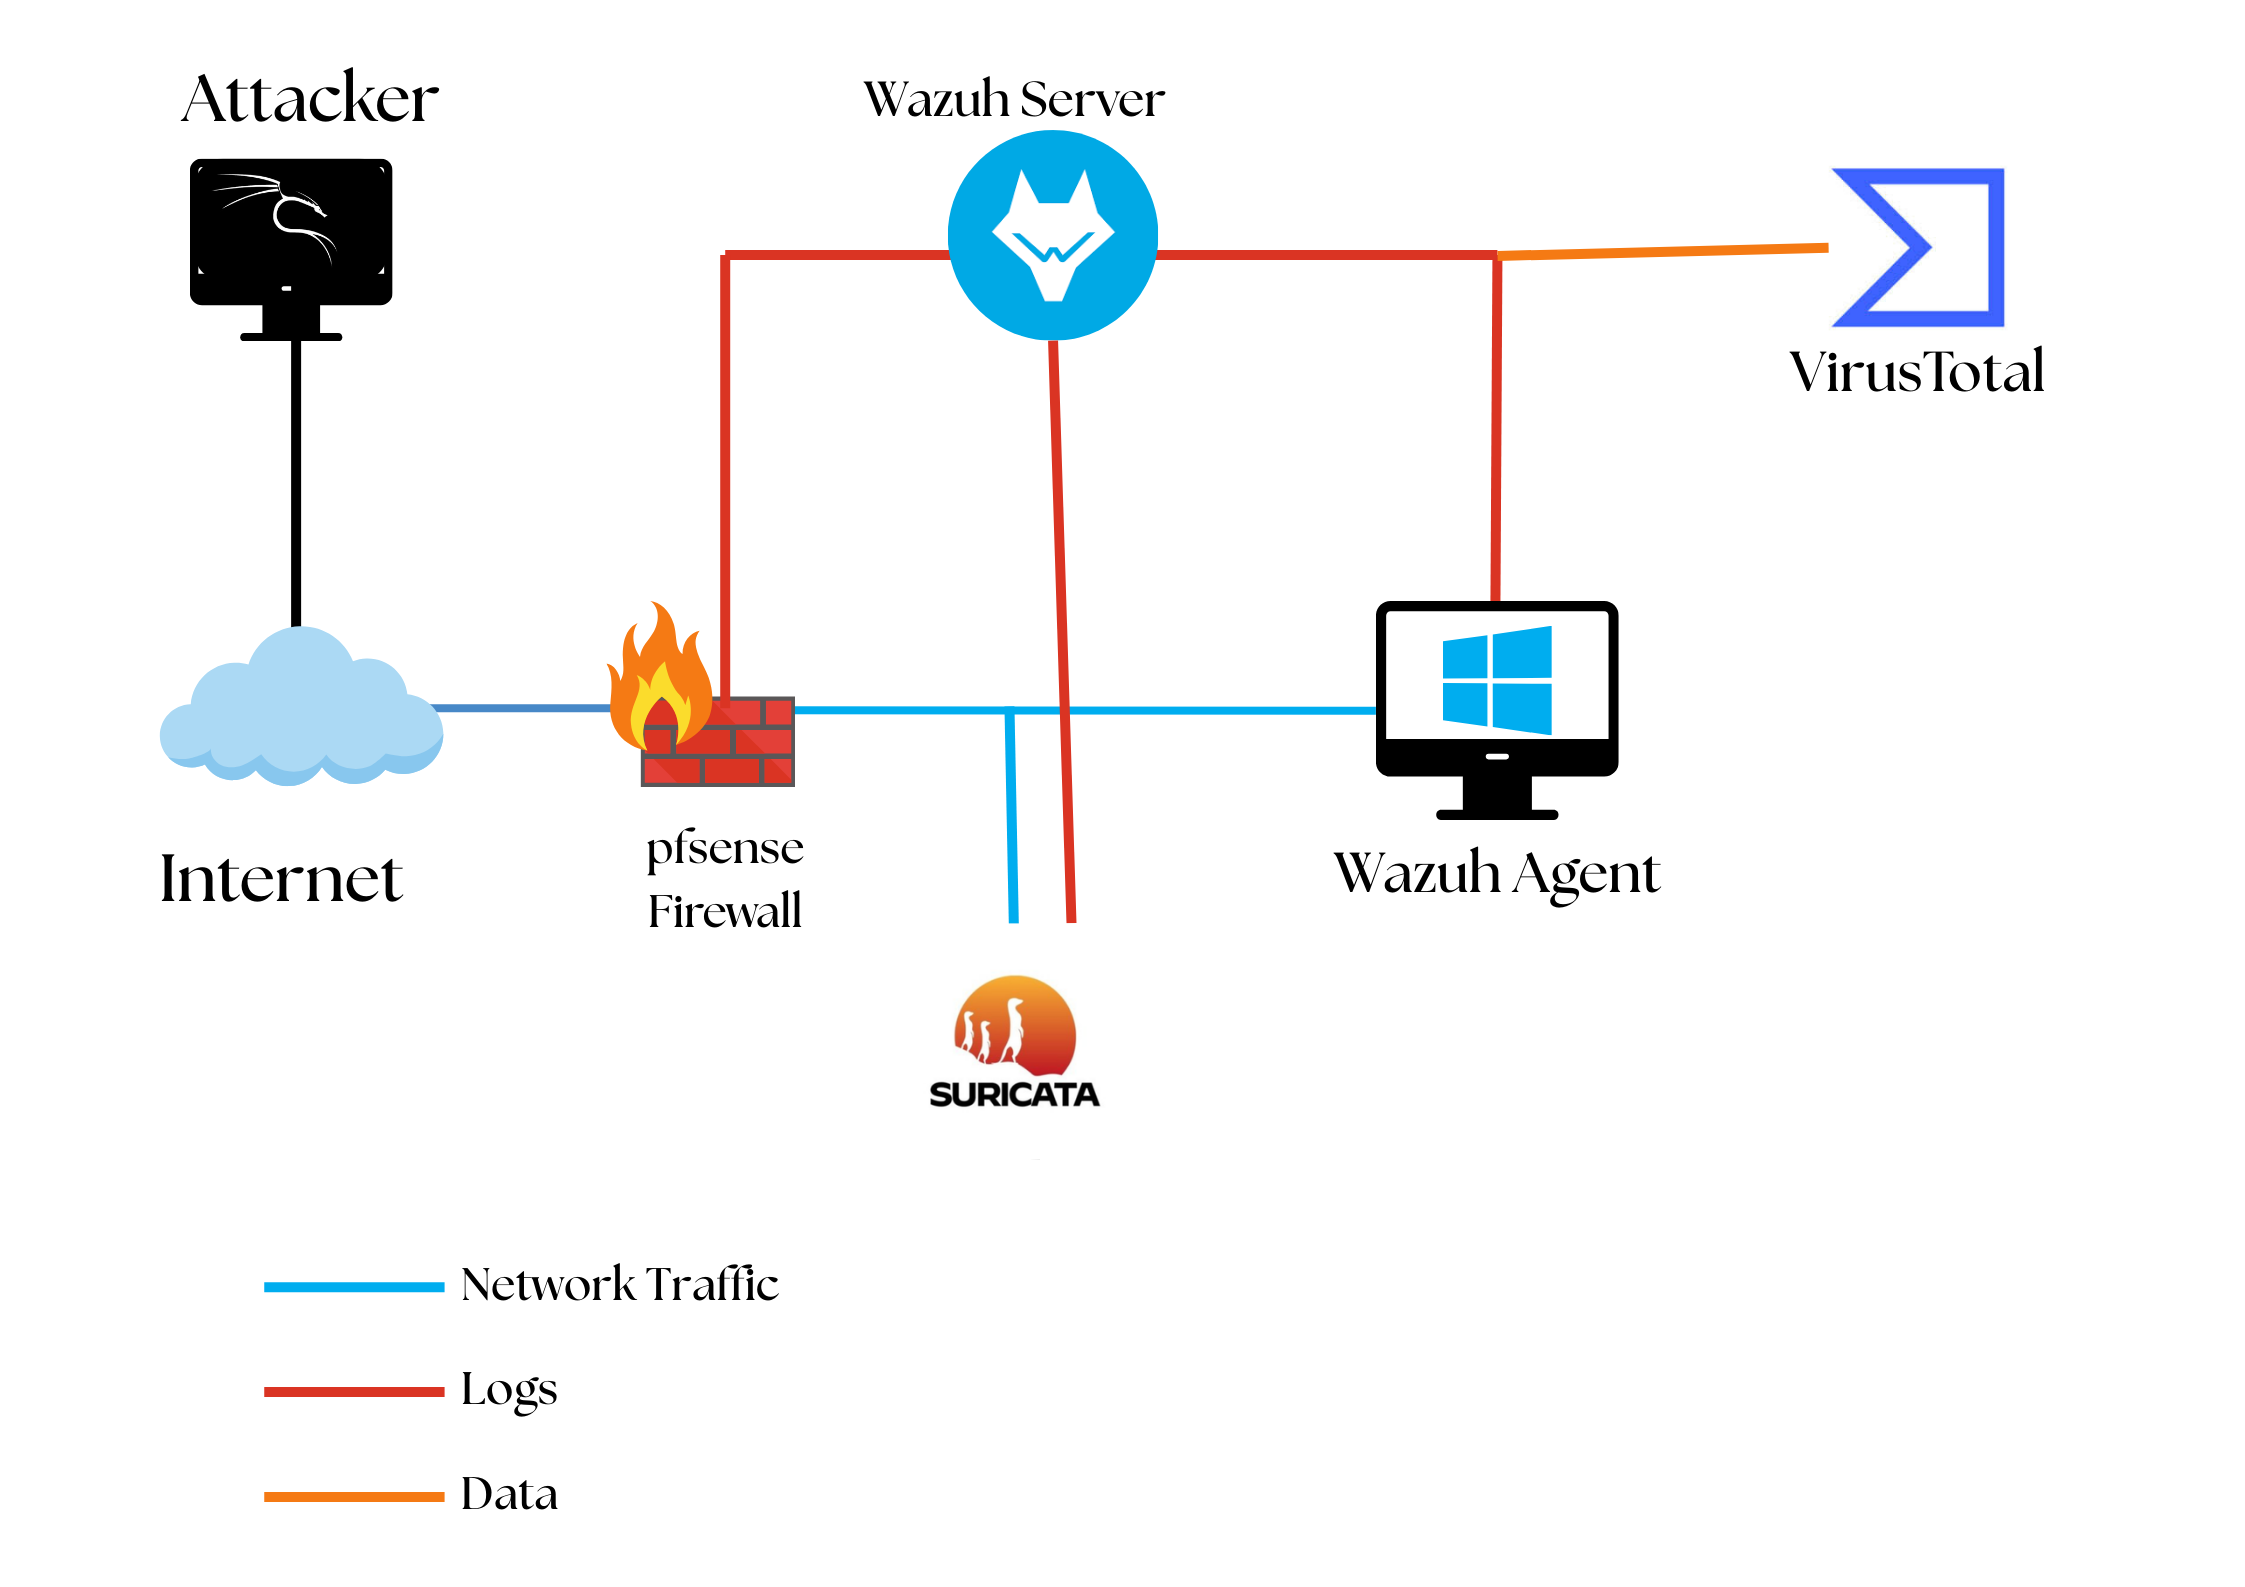
Wazuh-SOC-Lab
A SOC home lab built with Wazuh SIEM/XDR, pfSense, Suricata IDS/IPS, VirusTotal and Sysmon. Demonstrating log collection, threat detection, and attack simulation.
- 58
- 14 mo ago


living-off-the-land-lolbins-mcp-server
Living off the Land LOLBins MCP Server — 59 composite tools for LOL binary intelligence across 10 catalogs (GTFOBins, LOLBAS, LOOBins, LOLDrivers, LOLRMM, LOLESXi, LOTP, LOLC2, LOFLCAB, WADComs)
- 2
- TypeScript
- MIT
- 6 wk ago

wazuh-detection-lab
Free Wazuh SIEM home lab: attack simulation, detection rules and investigation reports.
- 0
- Shell
- MIT
- 7 d ago
