hayabusa
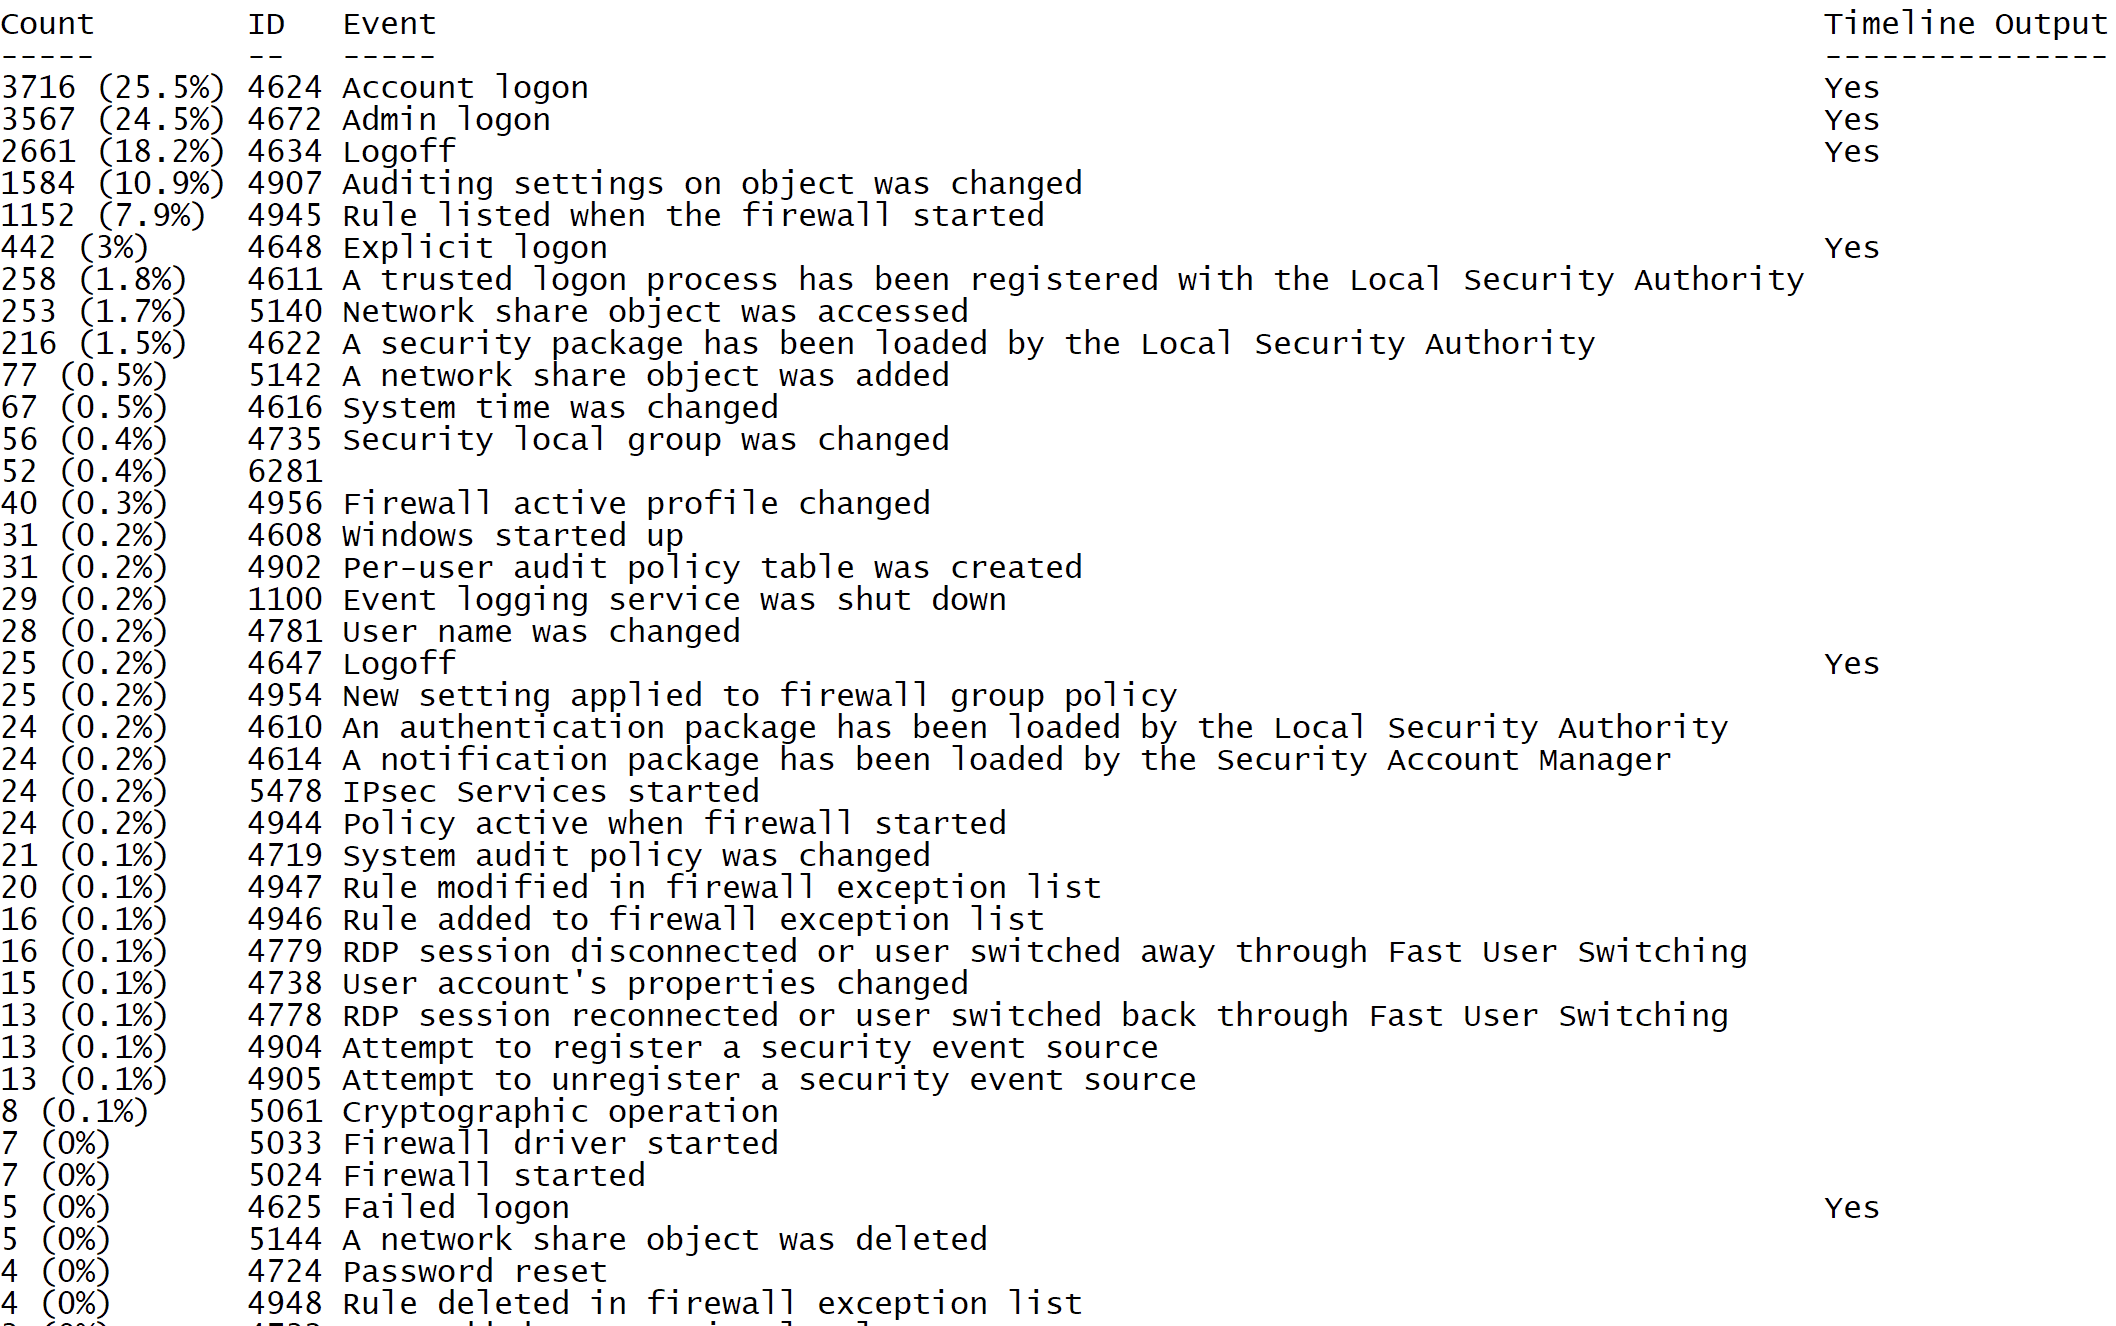
Hayabusa (隼) is a sigma-based threat hunting and fast forensics timeline generator for Windows event logs.
- 3.5k
- Rust
- AGPL-3.0
- 12 d ago
Hayabusa (隼) is a sigma-based threat hunting and fast forensics timeline generator for Windows event logs.
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
WELA (Windows Event Log Analyzer): The Swiss Army knife for Windows Event Logs! ゑ羅(ウェラ)
Suzaku (朱雀) is a sigma-based threat hunting and fast forensics timeline generator for cloud logs.
Easy-to-use Threat modeling-as-a-Code (TaaC) solution following DevSecOps principles. Simple CI/CD integration as well as console usage. Sugar-Free and Secure: no any external dependencies except for chart plotting are used
Prowler Studio an AI workflow that ensures Claude Code follows Prowler's guardrails to deliver consistent, tested, and PR-ready threat detection checks, remediations and update compliance frameworks.