authelia
The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.
- 30k
- Go
- Apache-2.0
- 1 d ago
The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.
🧑🚀 Authentication and authorization infrastructure for SaaS and AI apps, built on OIDC and OAuth 2.1 with multi-tenancy, SSO, and RBAC.
The tiniest OpenID Certified™ authorization and authentication server you have ever seen.
🧰 A zero trust swiss army knife for working with X509, OAuth, JWT, OATH OTP, etc.
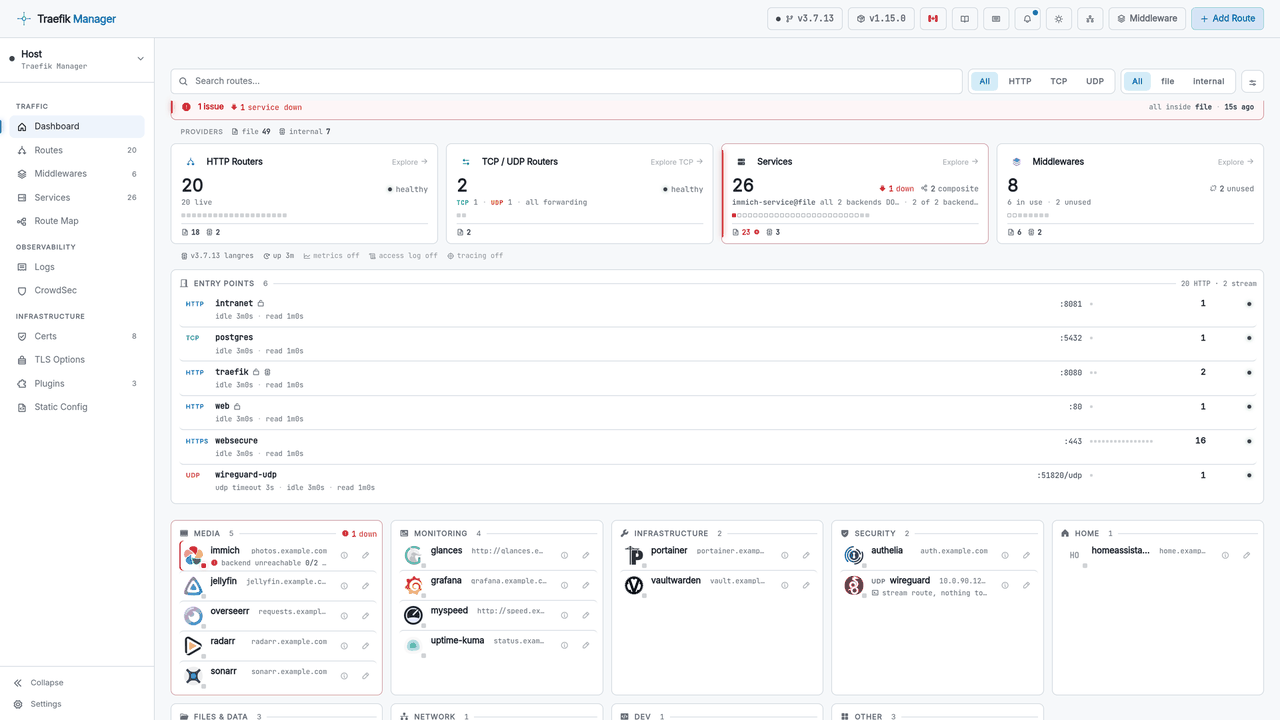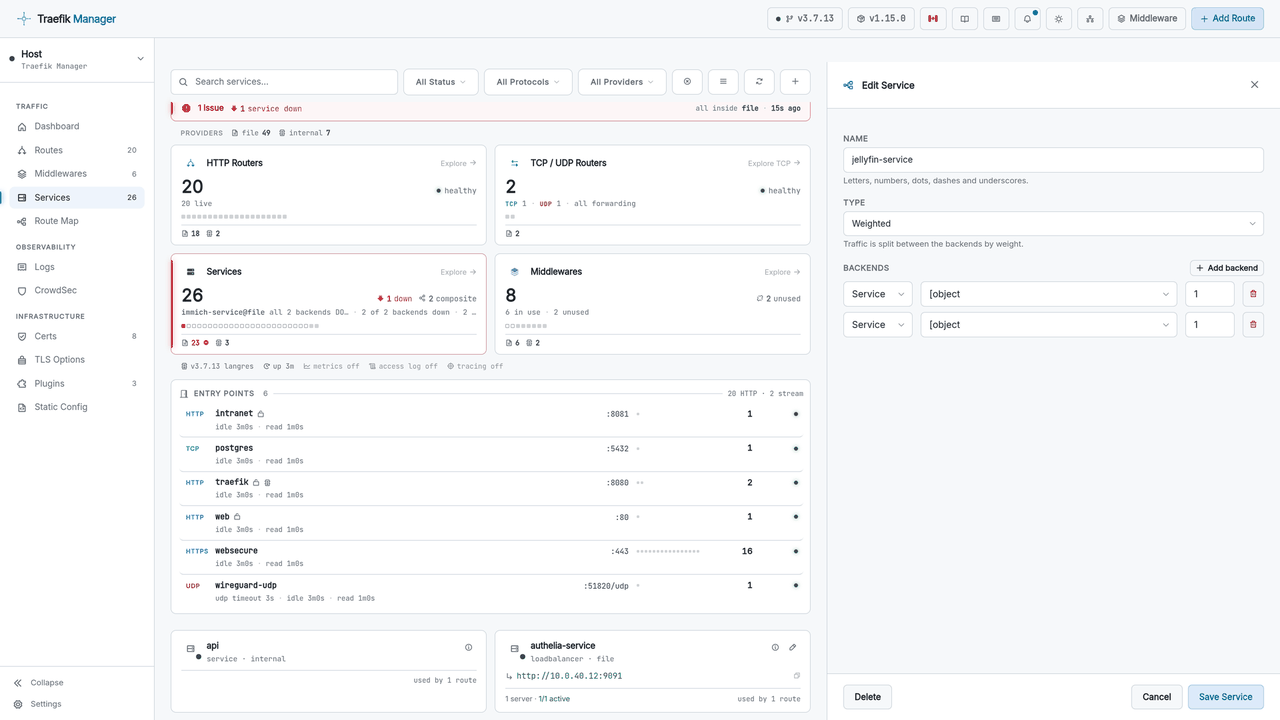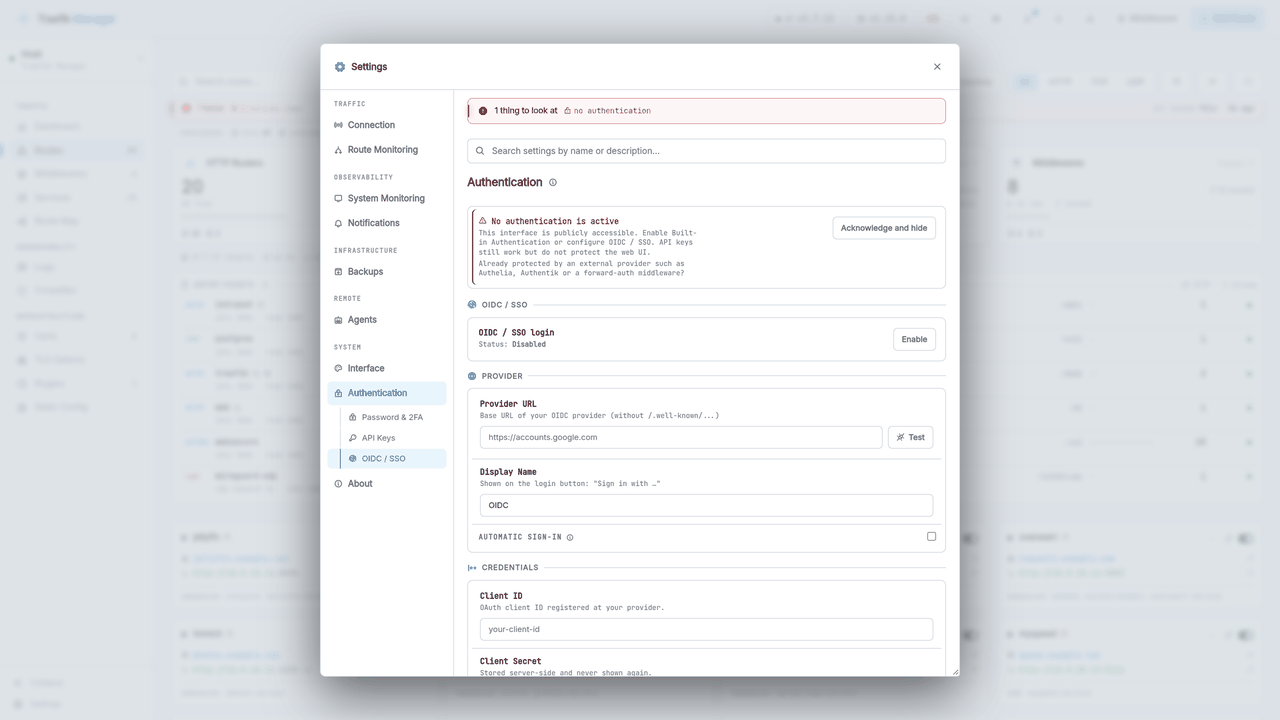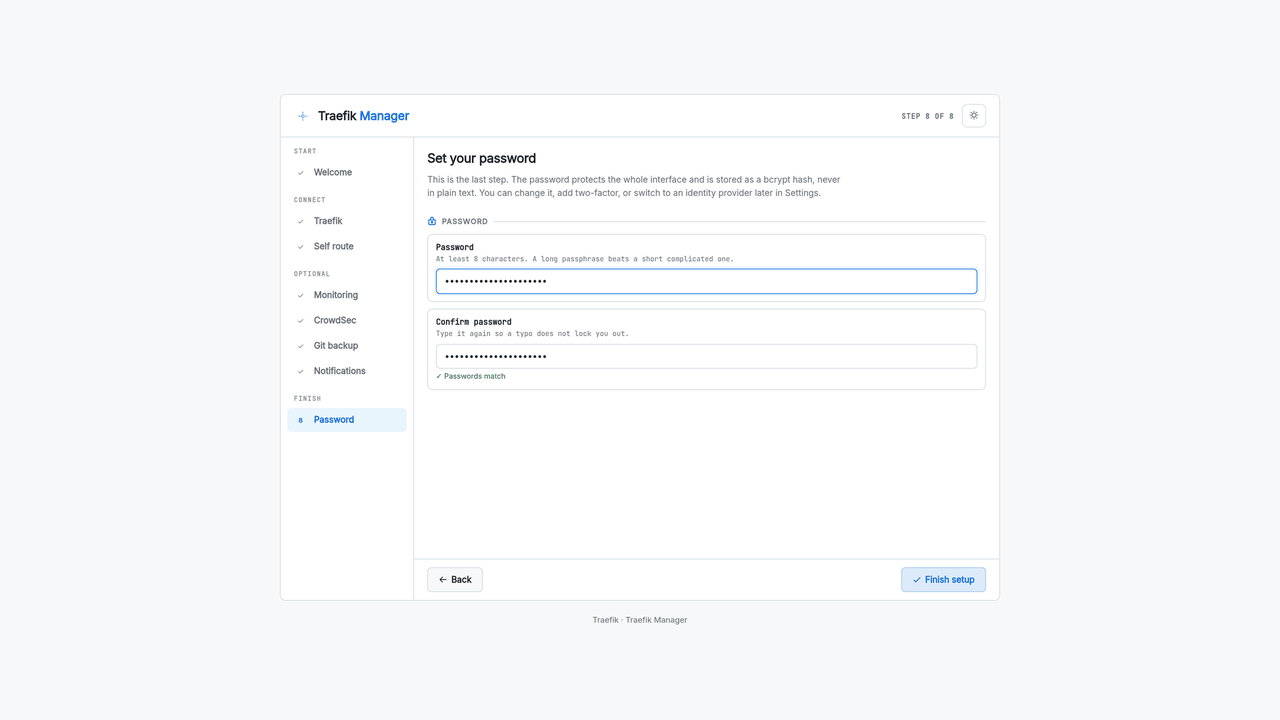
A clean, self-hosted web UI for managing your Traefik reverse proxy.
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
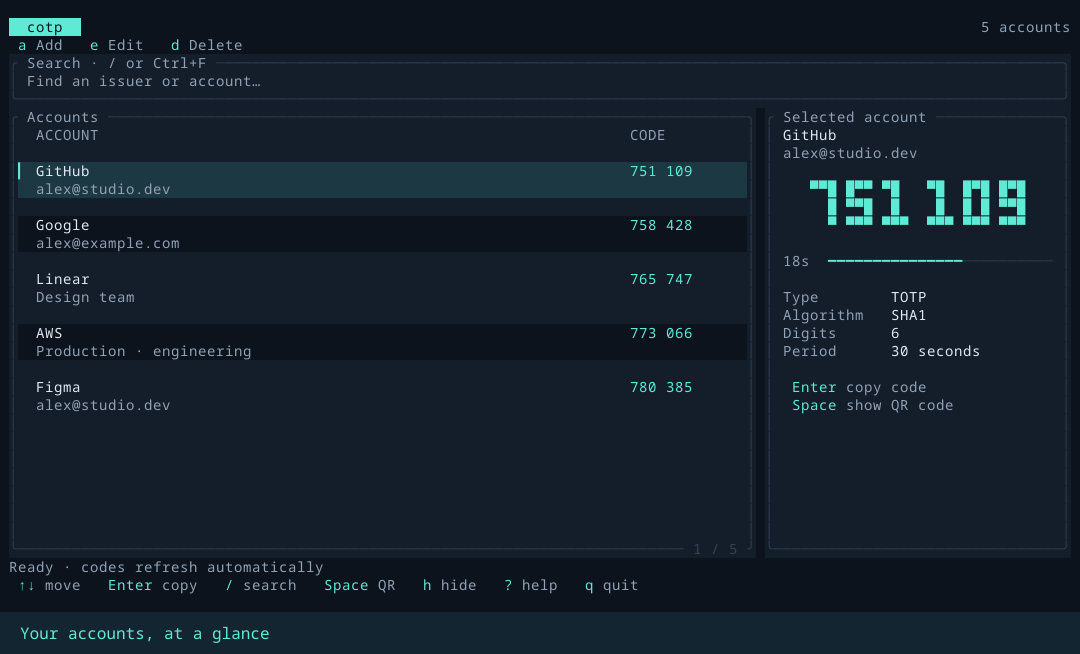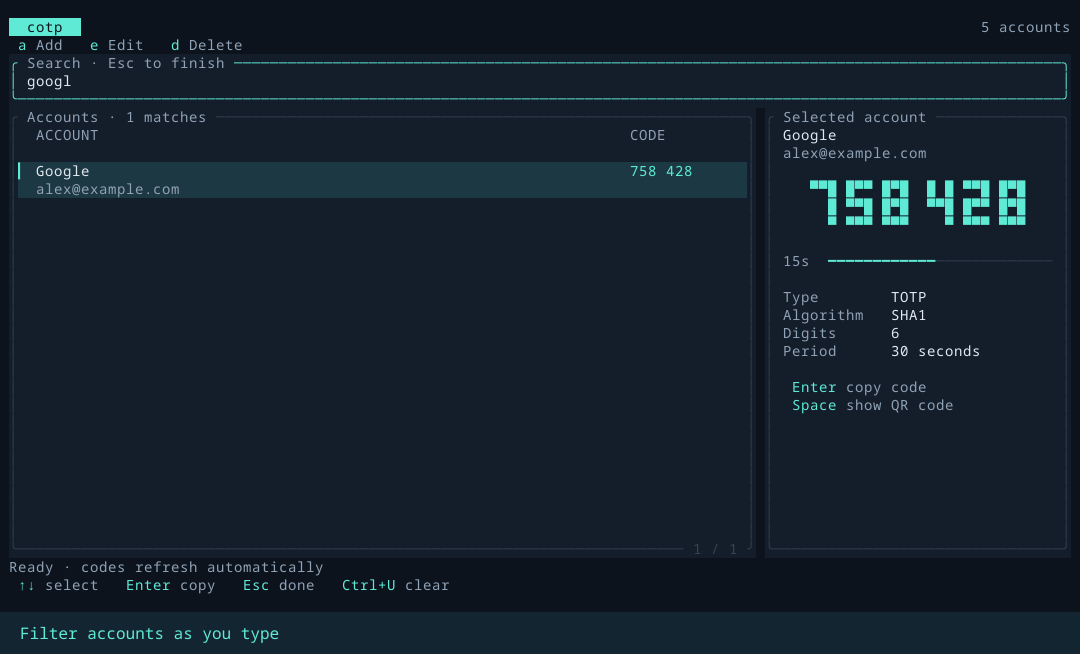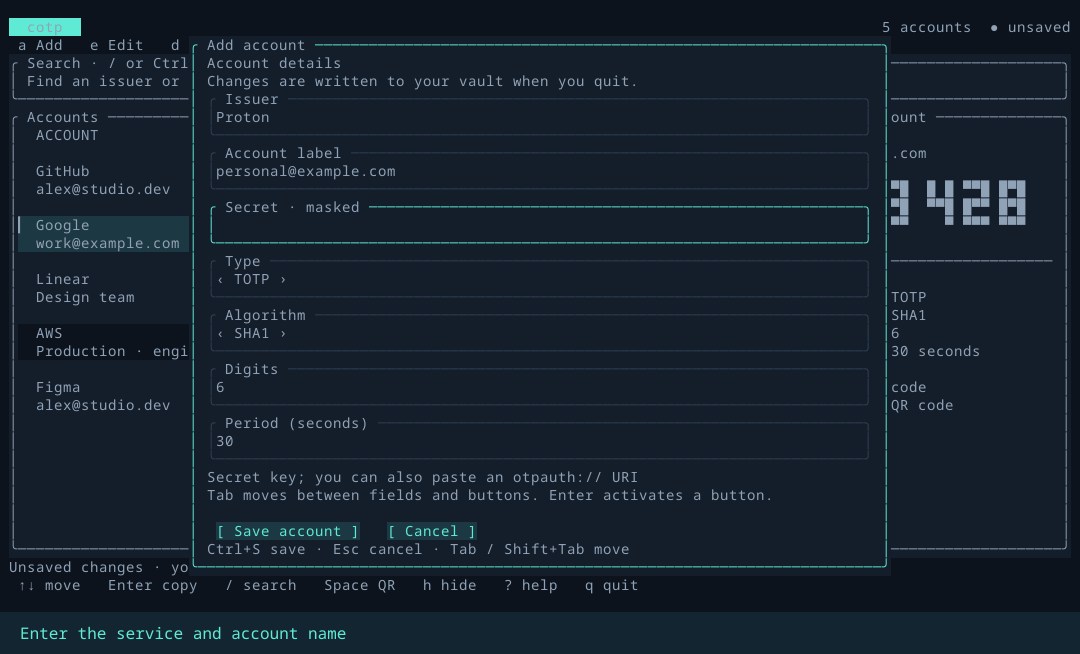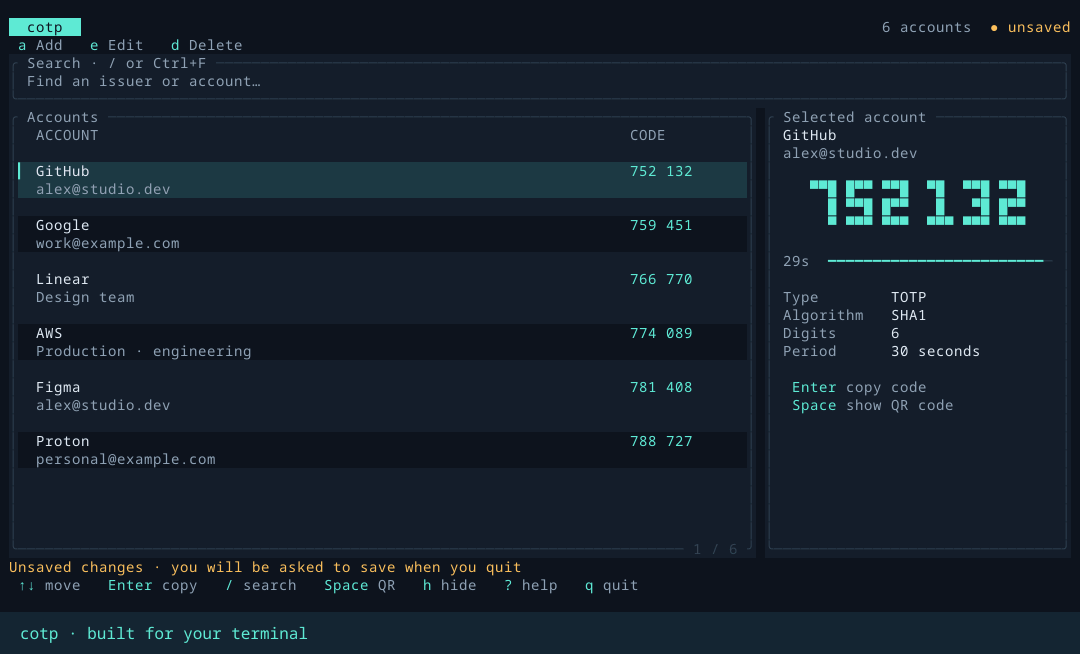
Encrypted, command-line TOTP/HOTP authenticator app with import functionality.
A Django app that handles MFA, it supports TOTP, U2F, FIDO2 U2F (Webauthn), Email Token and Trusted Devices
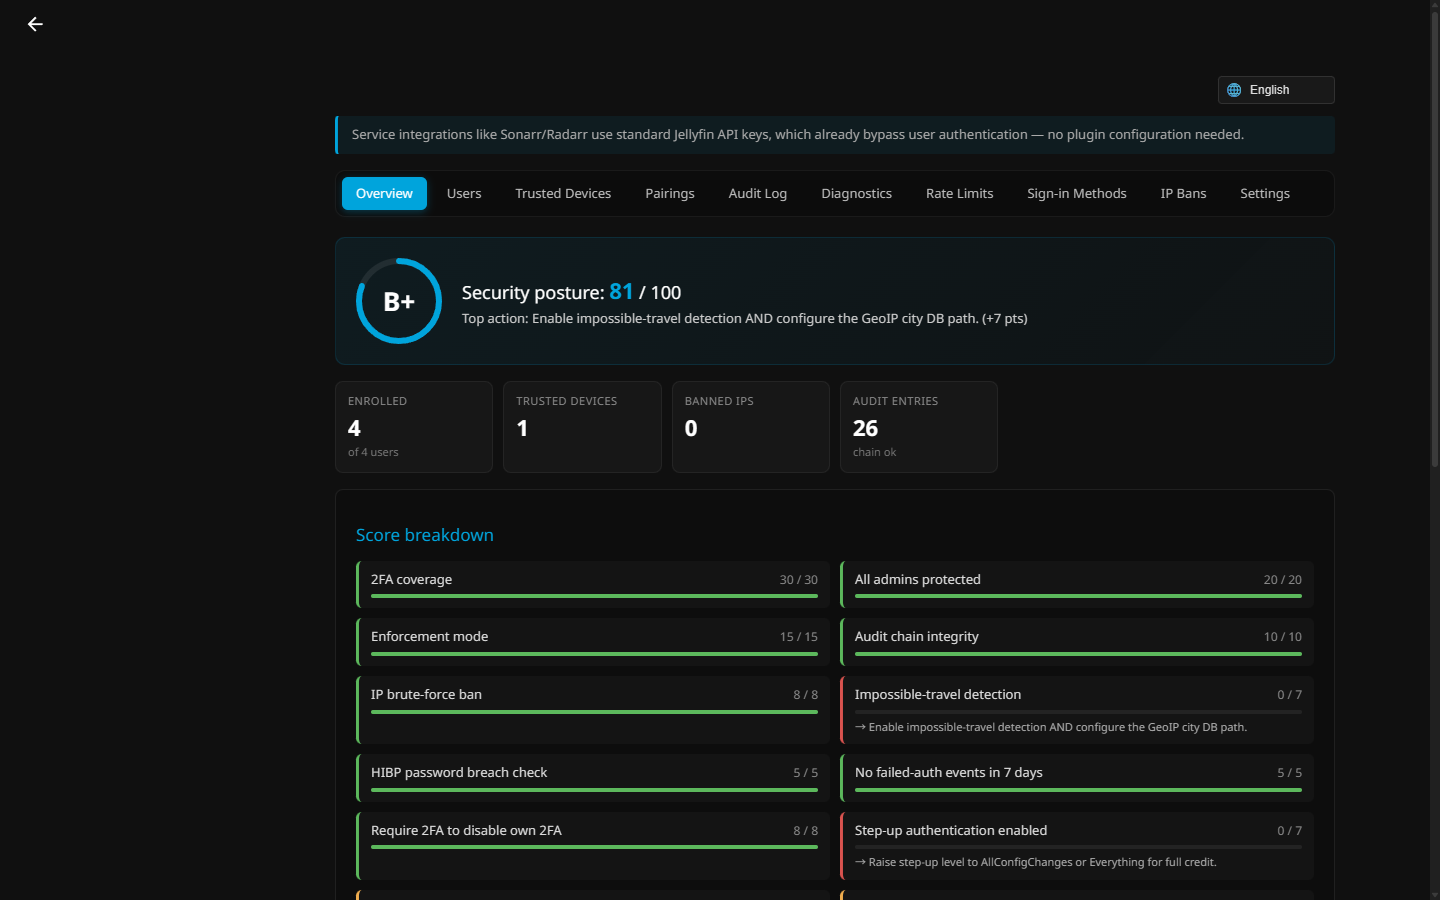
A Jellyfin plugin that adds native two-factor authentication (TOTP, email OTP) with trusted device tokens, TV device pairing, LAN bypass, and API key bypass. Server-side enforcement — works with all clients including web, mobile, TV, and service integrations like Sonarr/Radarr.
AnyPass: A Compose Multiplatform app for your all-in-one password manager
One Time Password (TOTP and HOTP) library for Clojure. TOTP/HOTP is widely used for Two Factor / Multi Factor Authentication.
A comprehensive Node.js package that simplifies the implementation of One-Time Password (OTP).
Keepassxc Talroora organizes credential records and manages encrypted password databases.
A native Mac password manager for Vaultwarden and Bitwarden — Swift/SwiftUI, AutoFill with passkeys and one-time codes, Touch ID, command palette, SSH agent.
Lightweight, thread-safe Java/Kotlin TOTP (time-based one-time passwords) and HOTP generator and validator for multi-factor authentication valid for both prover and verifier based on shared secret
Produces secure keys and passwords. SSH, PGP, OTP, TOR, X509, OTP, SLIP10
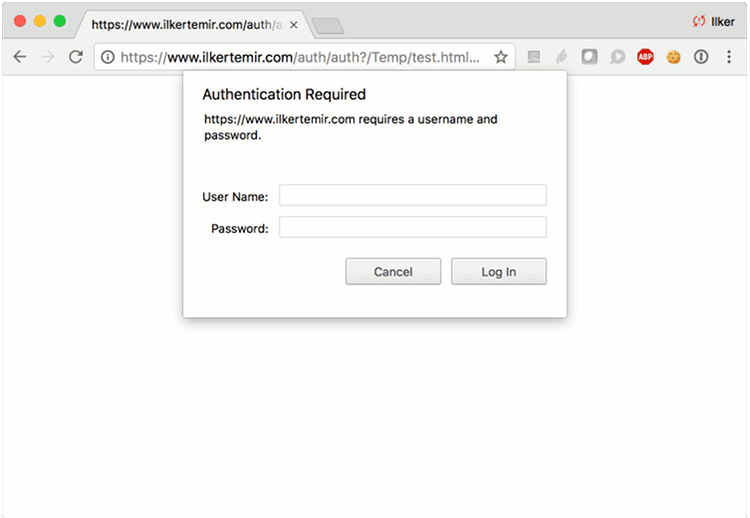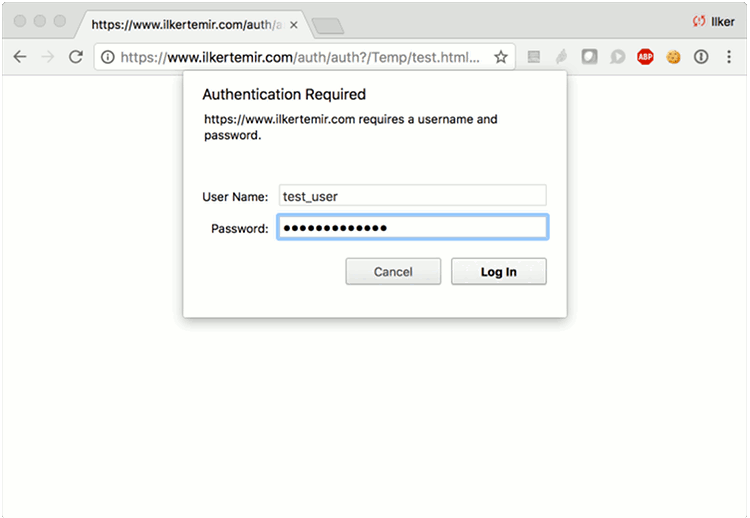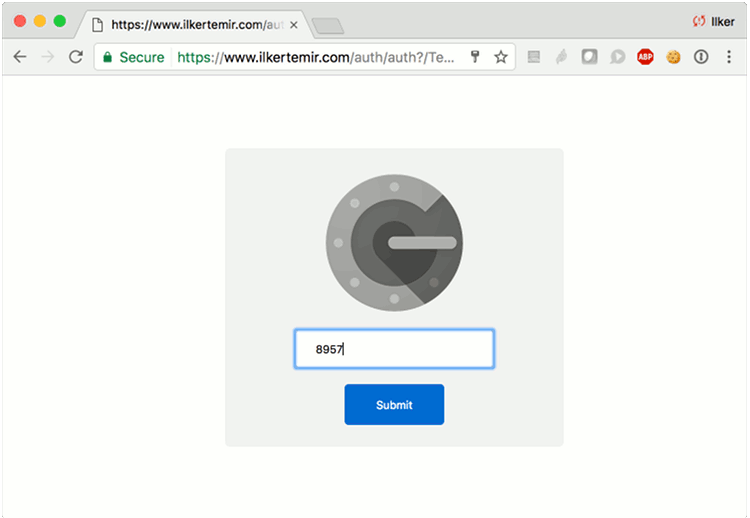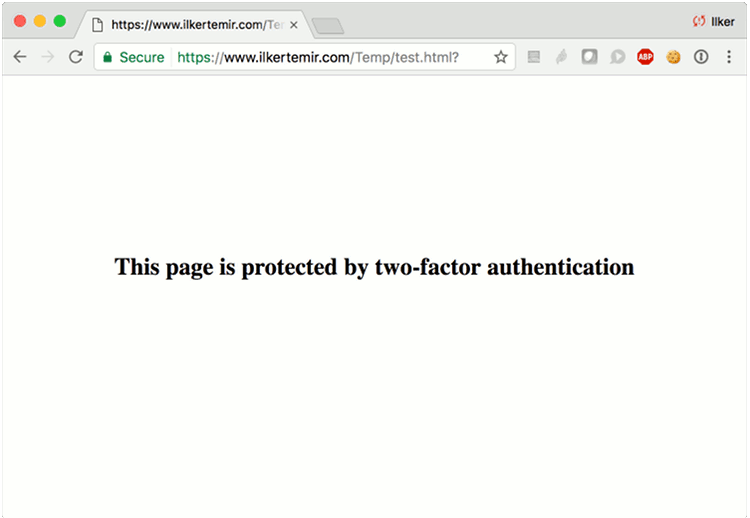
This article will teach you how to secure a Node.js API by implementing two-factor authentication (2FA) system using tokens generated by Google Authenticator or Authy. The one-time passcode (OTP) can be delivered via different methods like SMS but we will use Google Authenticator or Authy to reduce the complexity of the project.
Time-Based One-Time Password (TOTP) and HMAC-Based One-Time Password (HOTP) library for Go.
Apache two-factor (2FA) authentication with Google Authenticator based on Time-based One-Time Password (TOTP) or HMAC-based one-time password (HOTP) Algorithms.
OpenConnect Menu Bar - Connect/Disconnect/Status - for MacOS (supports Duo push/sms/phone, or Yubikey, Google Authenticator, Duo, or any TOTP) and SAML