bettercap
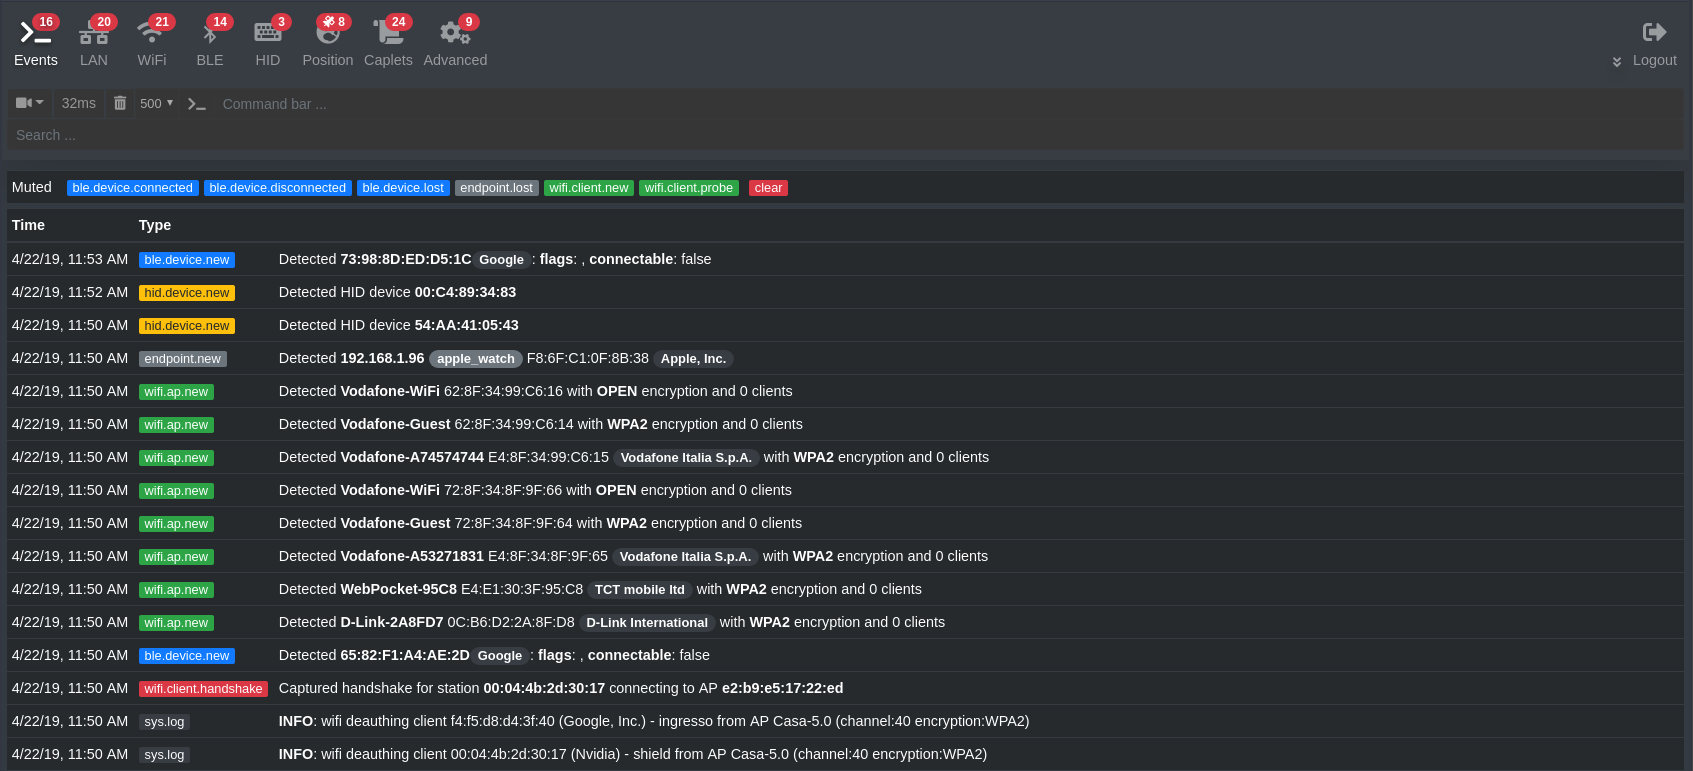
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
- 20k
- Go
- 24 h ago
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
A POSIX-compliant, fully automated WPA PSK PMKID and handshake capture script aimed at penetration testing
Open, hands-on study notes on wireless security & Wi-Fi penetration testing (802.11, WEP/WPA/WPA2/WPA3, aircrack-ng). CC BY 4.0.
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
ESP32-based Wi-Fi security and analysis tool built using Espressif ESP-IDF framework. Supports wireless frame sniffing, access point scanning, and WPA2 4-way handshake capture in promiscuous mode for wireless monitoring, protocol analysis, and cybersecurity research purposes.
Wi-Fi QR Code generator supporting WPA2 and WPA3 for Android devices implemented in HTML/CSS/JavaScript.