openwifi
open-source IEEE 802.11 WiFi baseband FPGA (chip) design: driver, software
- 4.9k
- C
- AGPL-3.0
- 6 d ago
open-source IEEE 802.11 WiFi baseband FPGA (chip) design: driver, software
Exploring possibilities of ESP32 platform to attack on nearby Wi-Fi networks.
Open, hands-on study notes on wireless security & Wi-Fi penetration testing (802.11, WEP/WPA/WPA2/WPA3, aircrack-ng). CC BY 4.0.
Sythesizable, modular Verilog implementation of 802.11 OFDM decoder.
Scans all nearby wifi networks and the devices connected to each network for Indoor positioning
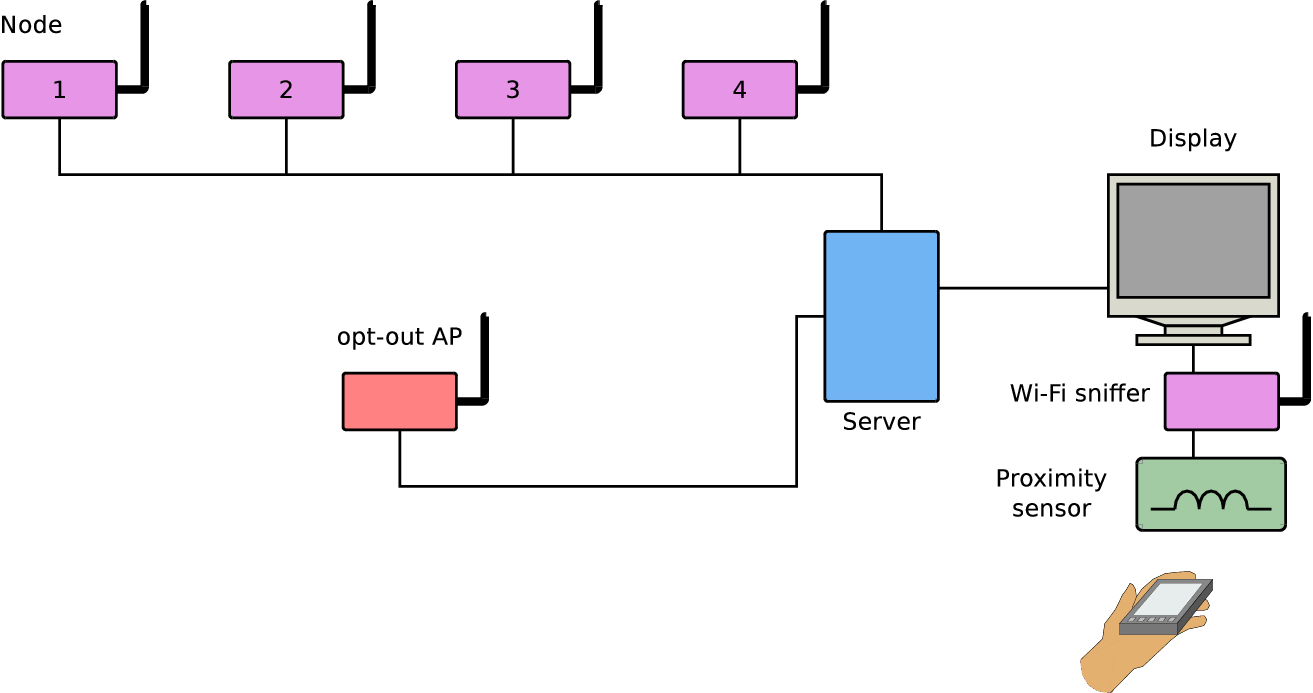
A Multitool For Tracking And Locating Nearby Devices Via Their RF Activities.
Arduino code for your ESP8266. Deauthenticate all clients from all access points
Raw 802.11 frame injection on ESP-IDF v5+/v6+ via a one-command objcopy --weaken-symbol patch. Enables Authentication (SAE Commit), Deauth, Reassoc, Disassoc, and Control frames (RTS/CTS/ACK) through esp_wifi_80211_tx()
NRSuite a wireless security testing toolkit for Android with no root required. Uses a $3 ESP32 over USB to add Wi-Fi packet capture, WPA2/PMKID handshake grabbing, BLE HID keyboard injection, USB mass storage, and BadUSB payloads to any Android phone through Termux.
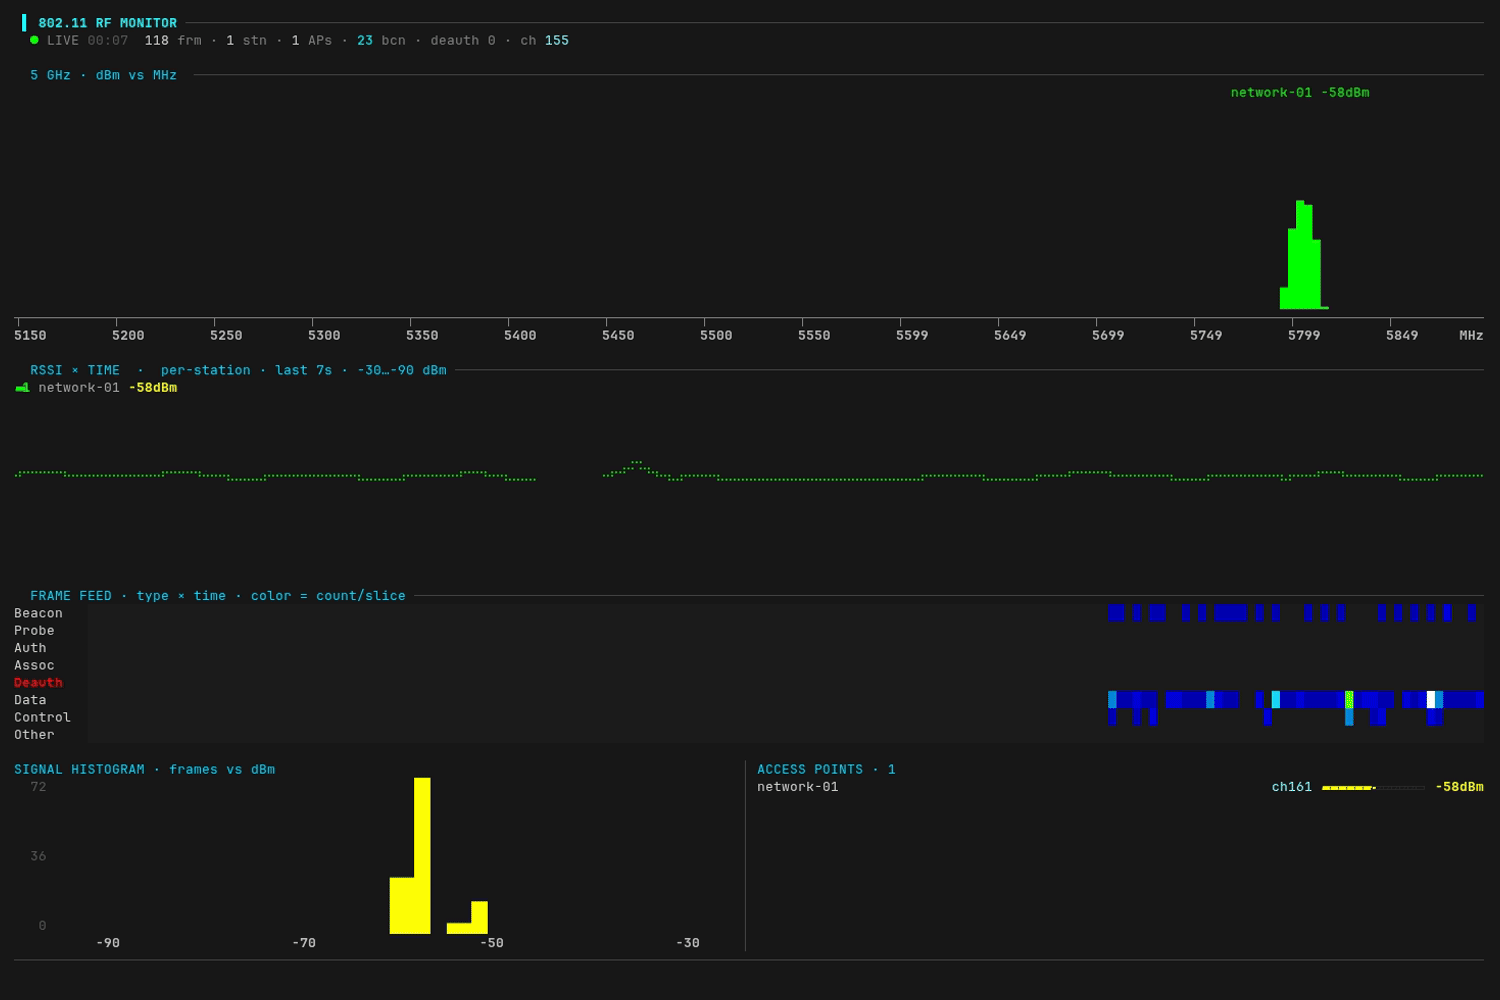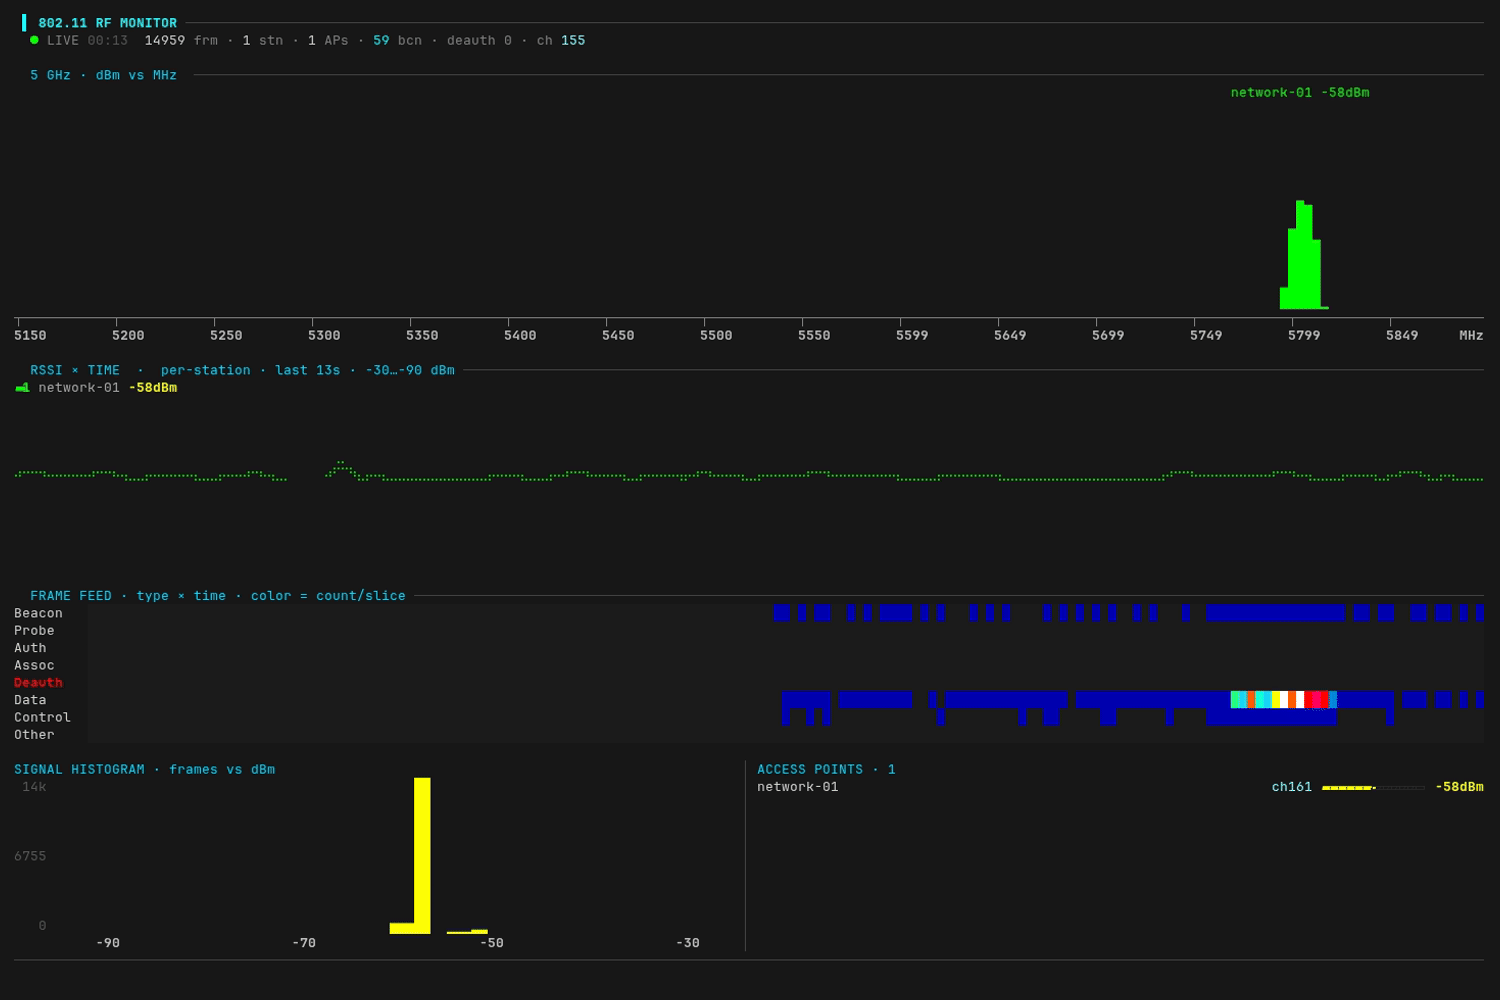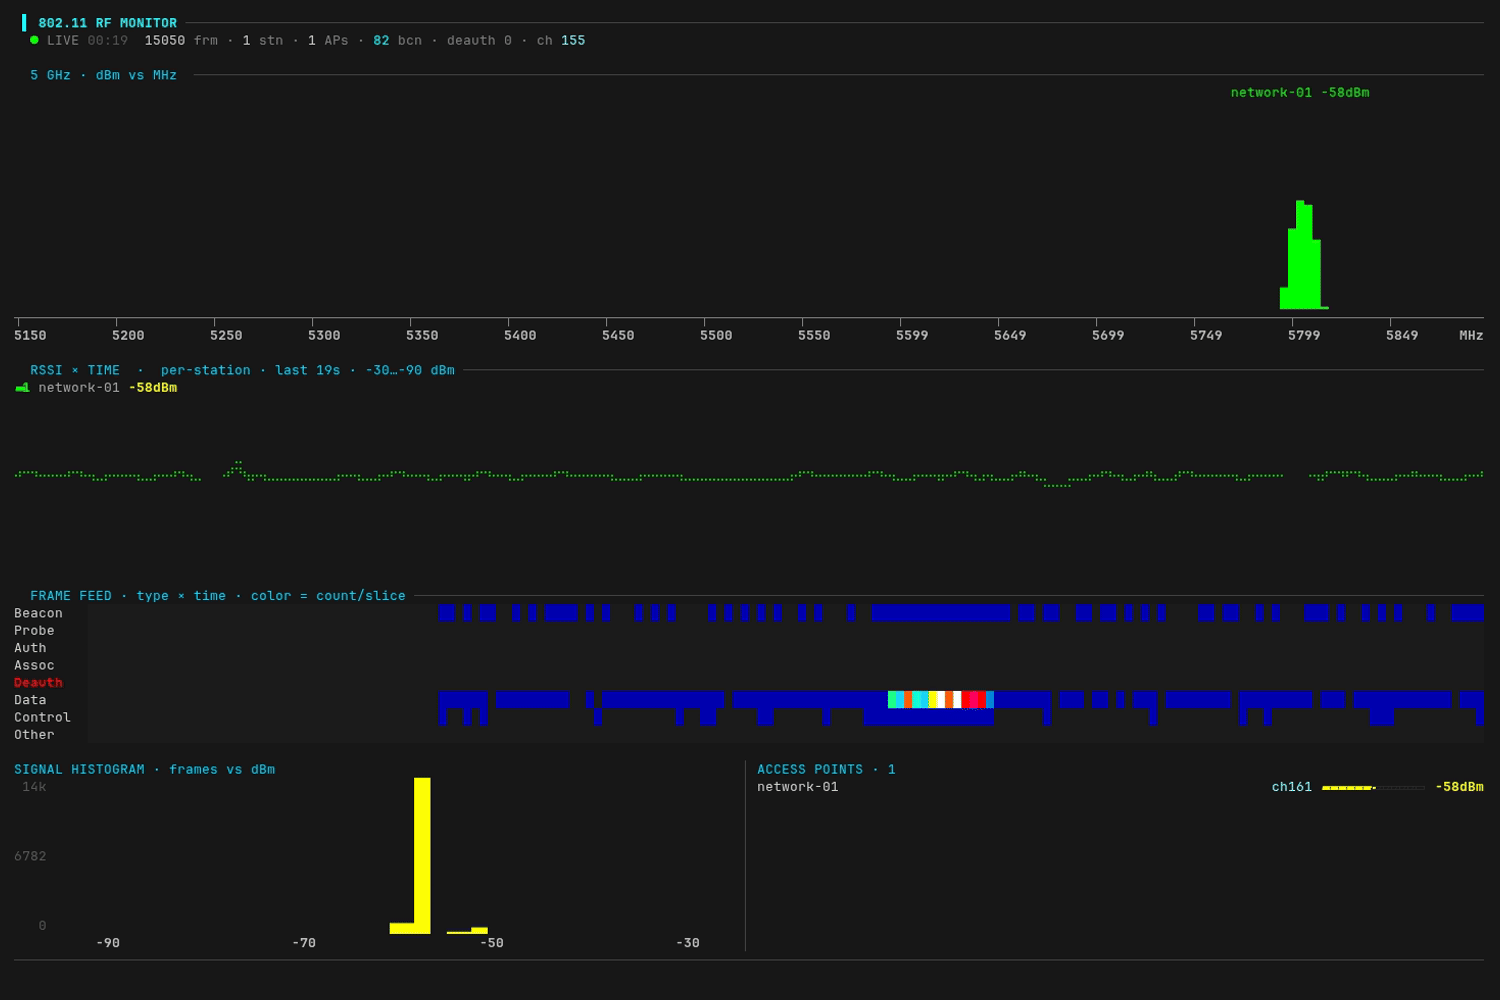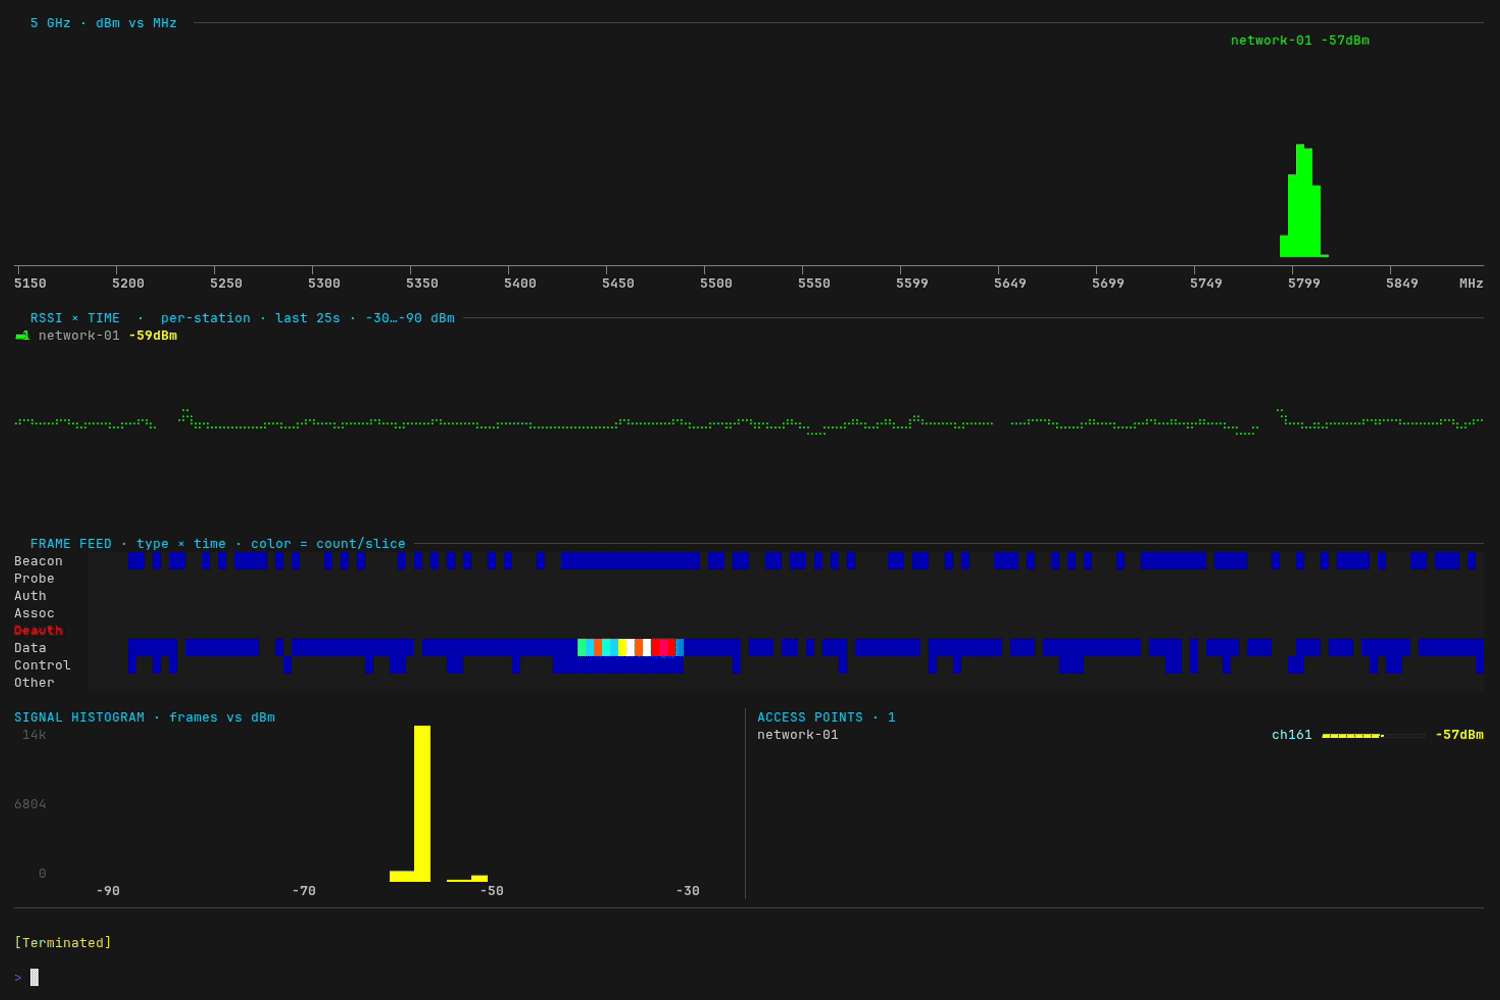
htop for the airwaves — a live 802.11 (Wi-Fi) RF dashboard in your terminal
Simplest DIY low power, low cost, standalone or web connected IOT sensors network framework using ESP32 or ESP8266 (no third party service required).
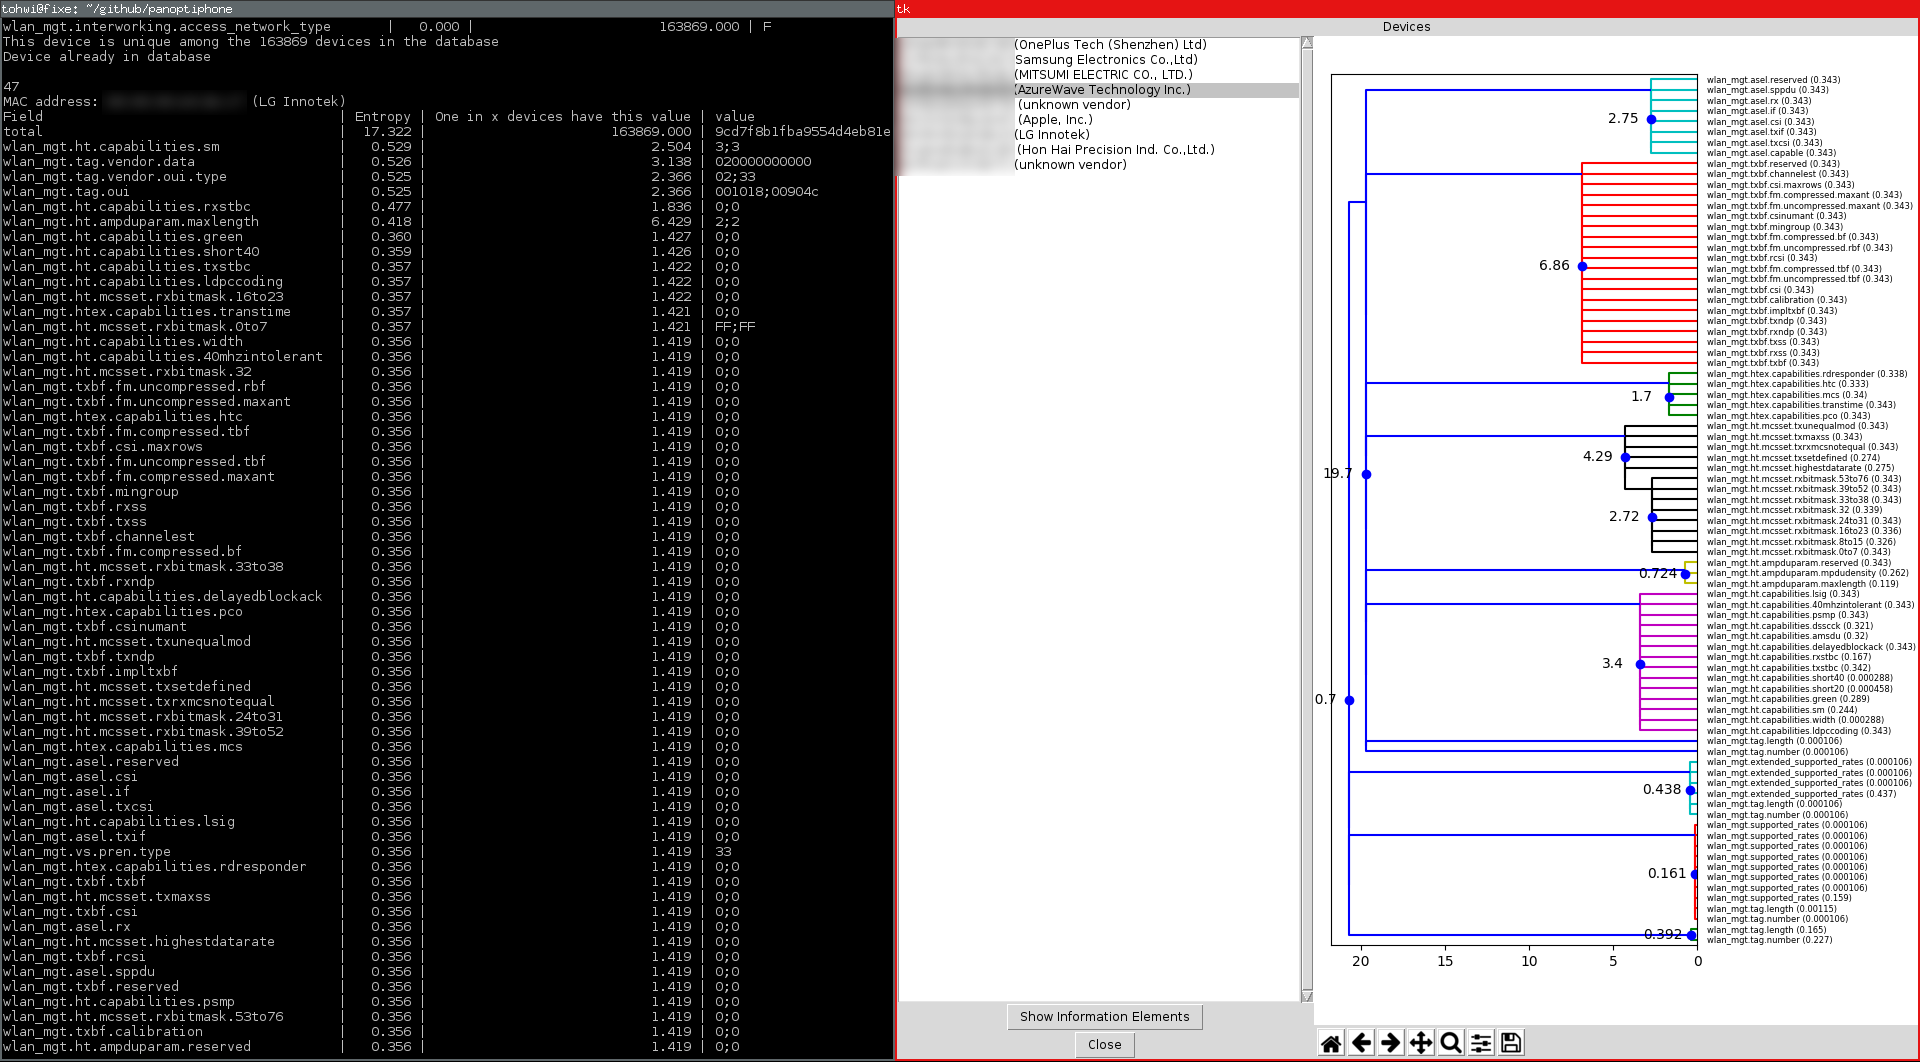
Estimates the uniqueness of a device based on the content of its emitted Wi-Fi frames, even if the MAC address is randomized
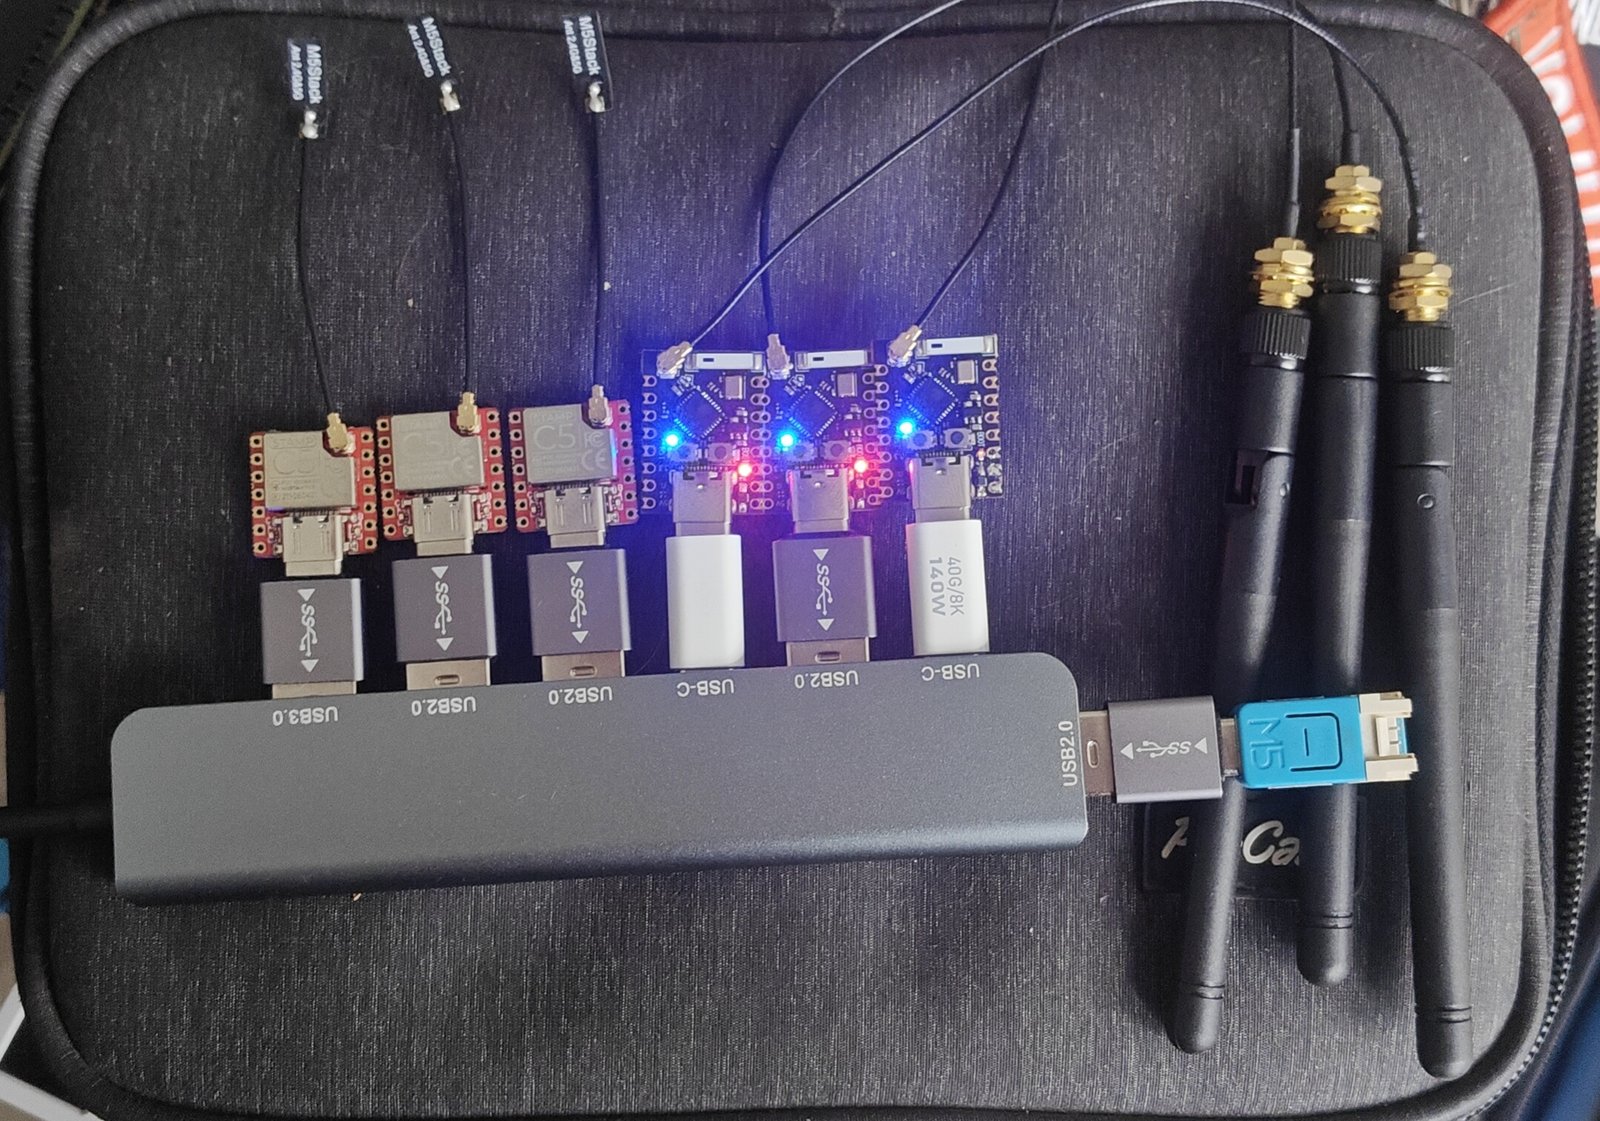
DIY parallel 2.4 GHz WiFi capture array (Hak5 WiFi Coconut style) from spare ESP32-C3/C5 boards: one channel per node, merged live into Wireshark. Passive, stdlib Python.
ESP32 firmware for the NRSuite security research toolkit. Wi-Fi/BLE attack and capture modules (deauth, beacon spam, captive portal, BLE HID, BadUSB) over USB serial.
ESP32-based Wi-Fi security and analysis tool built using Espressif ESP-IDF framework. Supports wireless frame sniffing, access point scanning, and WPA2 4-way handshake capture in promiscuous mode for wireless monitoring, protocol analysis, and cybersecurity research purposes.
Garuda is a wireless intrusion detection system (WIDS) , supports 802.11 wireless lan. it's designed for detecting war drivers, rouge AP, DoS attacks and even MAC spoofing, including rule-based detection module, statistics module, enummeration module.