pangolin
Modern networking and security platform providing secure access and connectivity to apps, infrastructure, and AI workloads. Connect and protect your users.
- 24k
- TypeScript
- 2 h ago
Modern networking and security platform providing secure access and connectivity to apps, infrastructure, and AI workloads. Connect and protect your users.
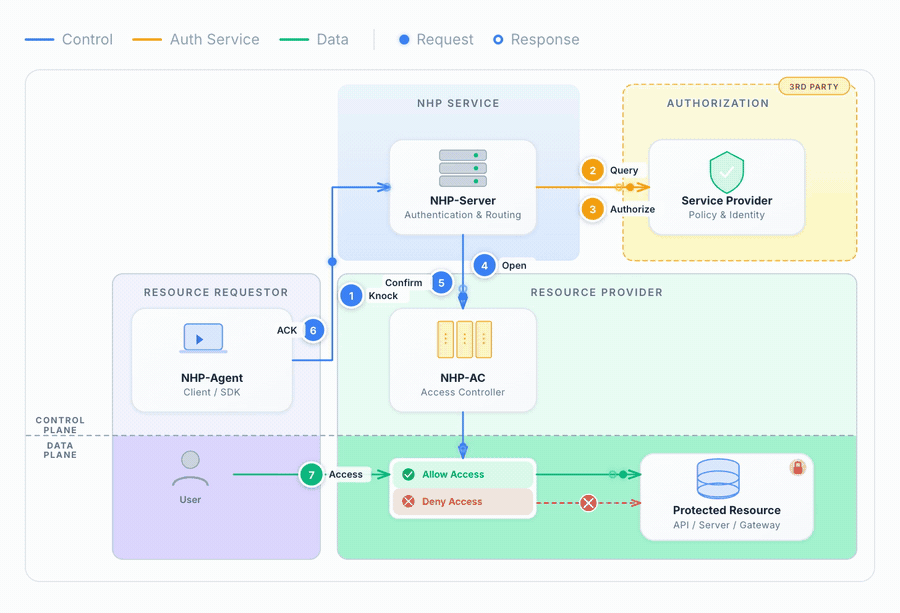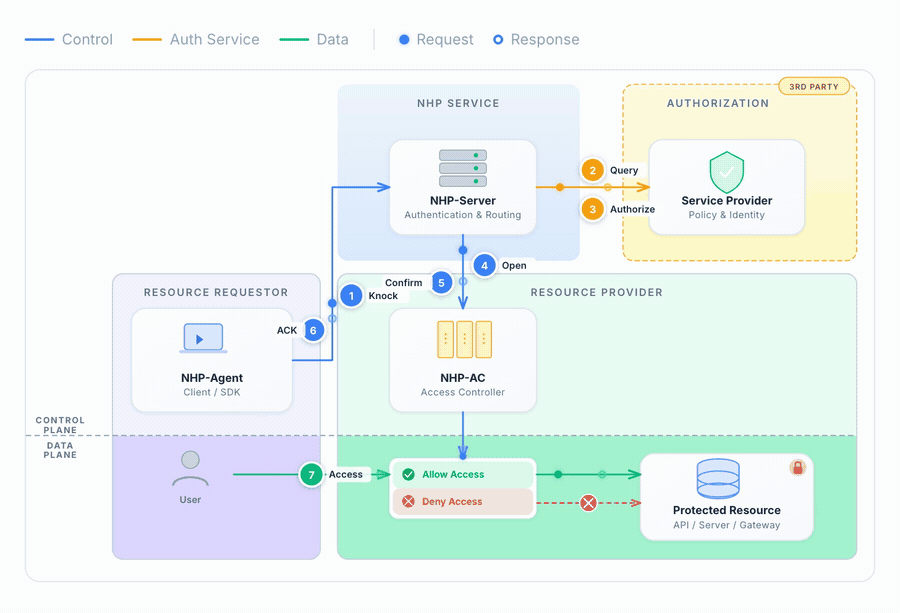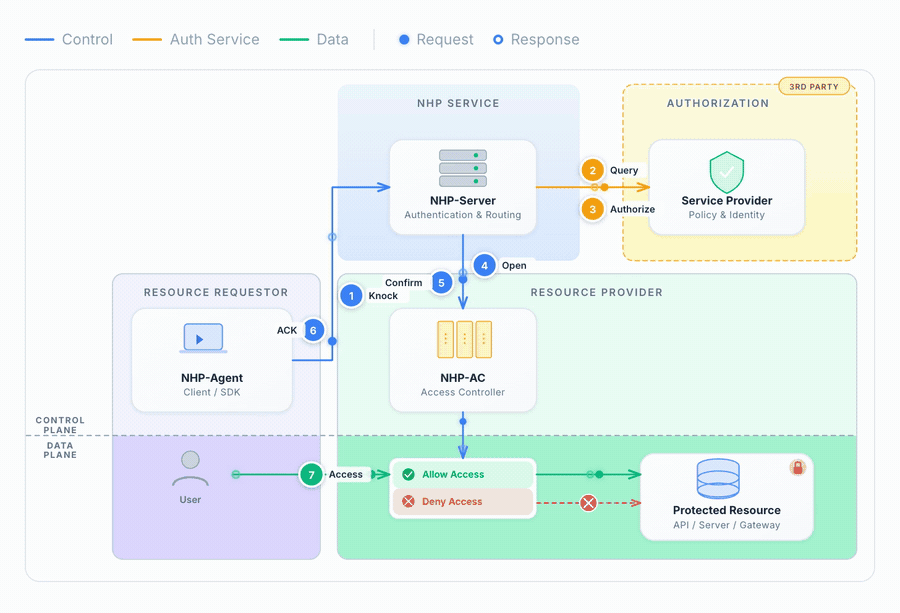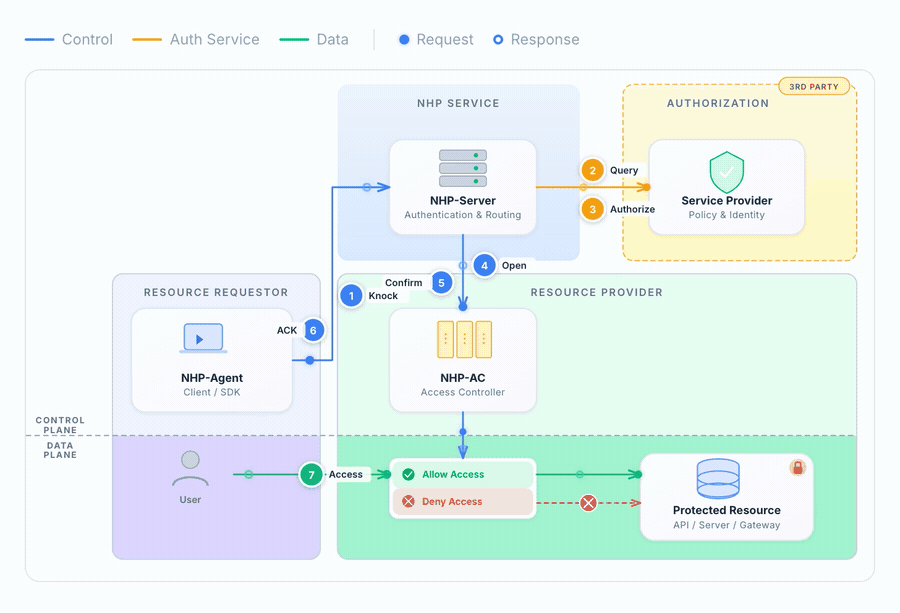
Make your infrastructure invisible to attackers. OpenNHP implements the Network-infrastructure Hiding Protocol (NHP): authenticate before connection, cryptographically. IETF draft.
Netmaker makes networks with WireGuard. Netmaker automates fast, secure, and distributed virtual networks.
immudb - immutable database based on zero trust, SQL/Key-Value/Document model, tamperproof, data change history
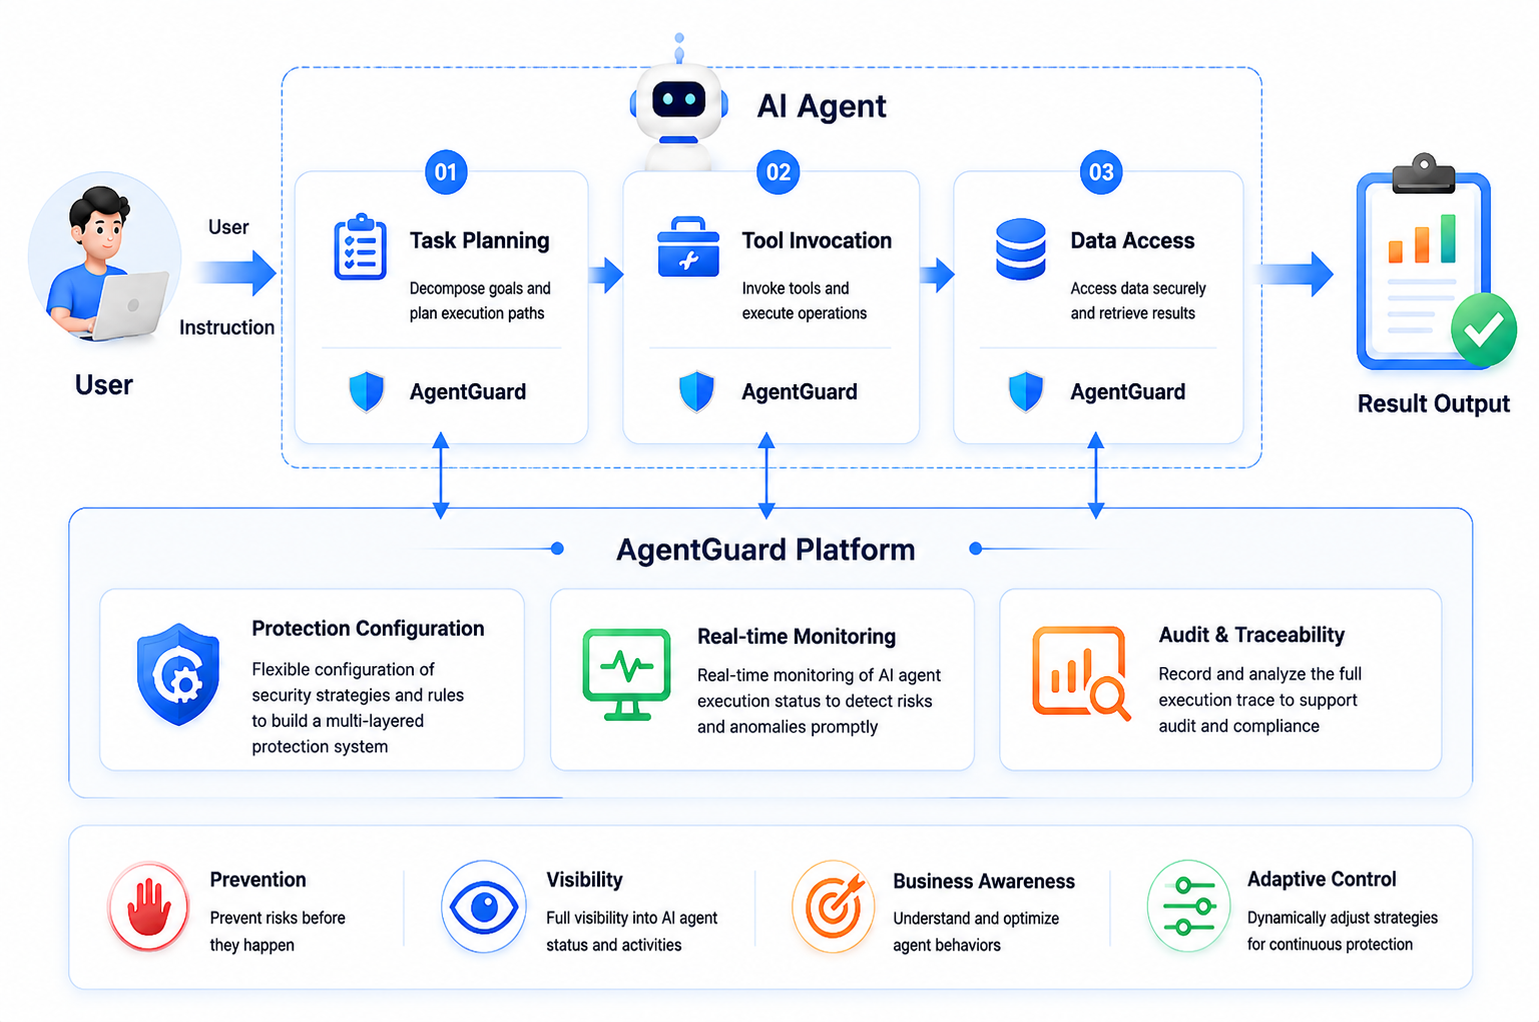
AI Agent Governance Toolkit — Policy enforcement, zero-trust identity, execution sandboxing, and reliability engineering for autonomous AI agents. Covers 10/10 OWASP Agentic Top 10.
A simple, secure, easy-to-use bastion and session auditing system. Supports RDP, SSH, VNC, Telnet, HTTP, records and replays sessions for auditing and compliance.
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
The parent project for OpenZiti. Here you will find the executables for a fully zero-trust, programmable network @OpenZiti
A next-gen FOSS self-hosted unified zero trust secure access platform that can operate as a remote access VPN, a ZTNA platform, API/AI/MCP gateway, a PaaS, an ngrok-alternative and a homelab infrastructure.
💚🇺🇸🗽Secure browser infrastructure for regulated enterprises, AI and agentic microtasks
Ready-to-run Docker Compose stacks for 120+ self-hosted apps, each with a Tailscale sidecar and automatic HTTPS
LunaSec - Dependency Security Scanner that automatically notifies you about vulnerabilities like Log4Shell or node-ipc in your Pull Requests and Builds. Protect yourself in 30 seconds with the LunaTrace GitHub App: https://github.com/marketplace/lunatrace-by-lunasec/
Learn cloud security by building it! An open-source homelab teaching Zero Trust, DevSecOps, IaC, and cloud architecture from the ground up.
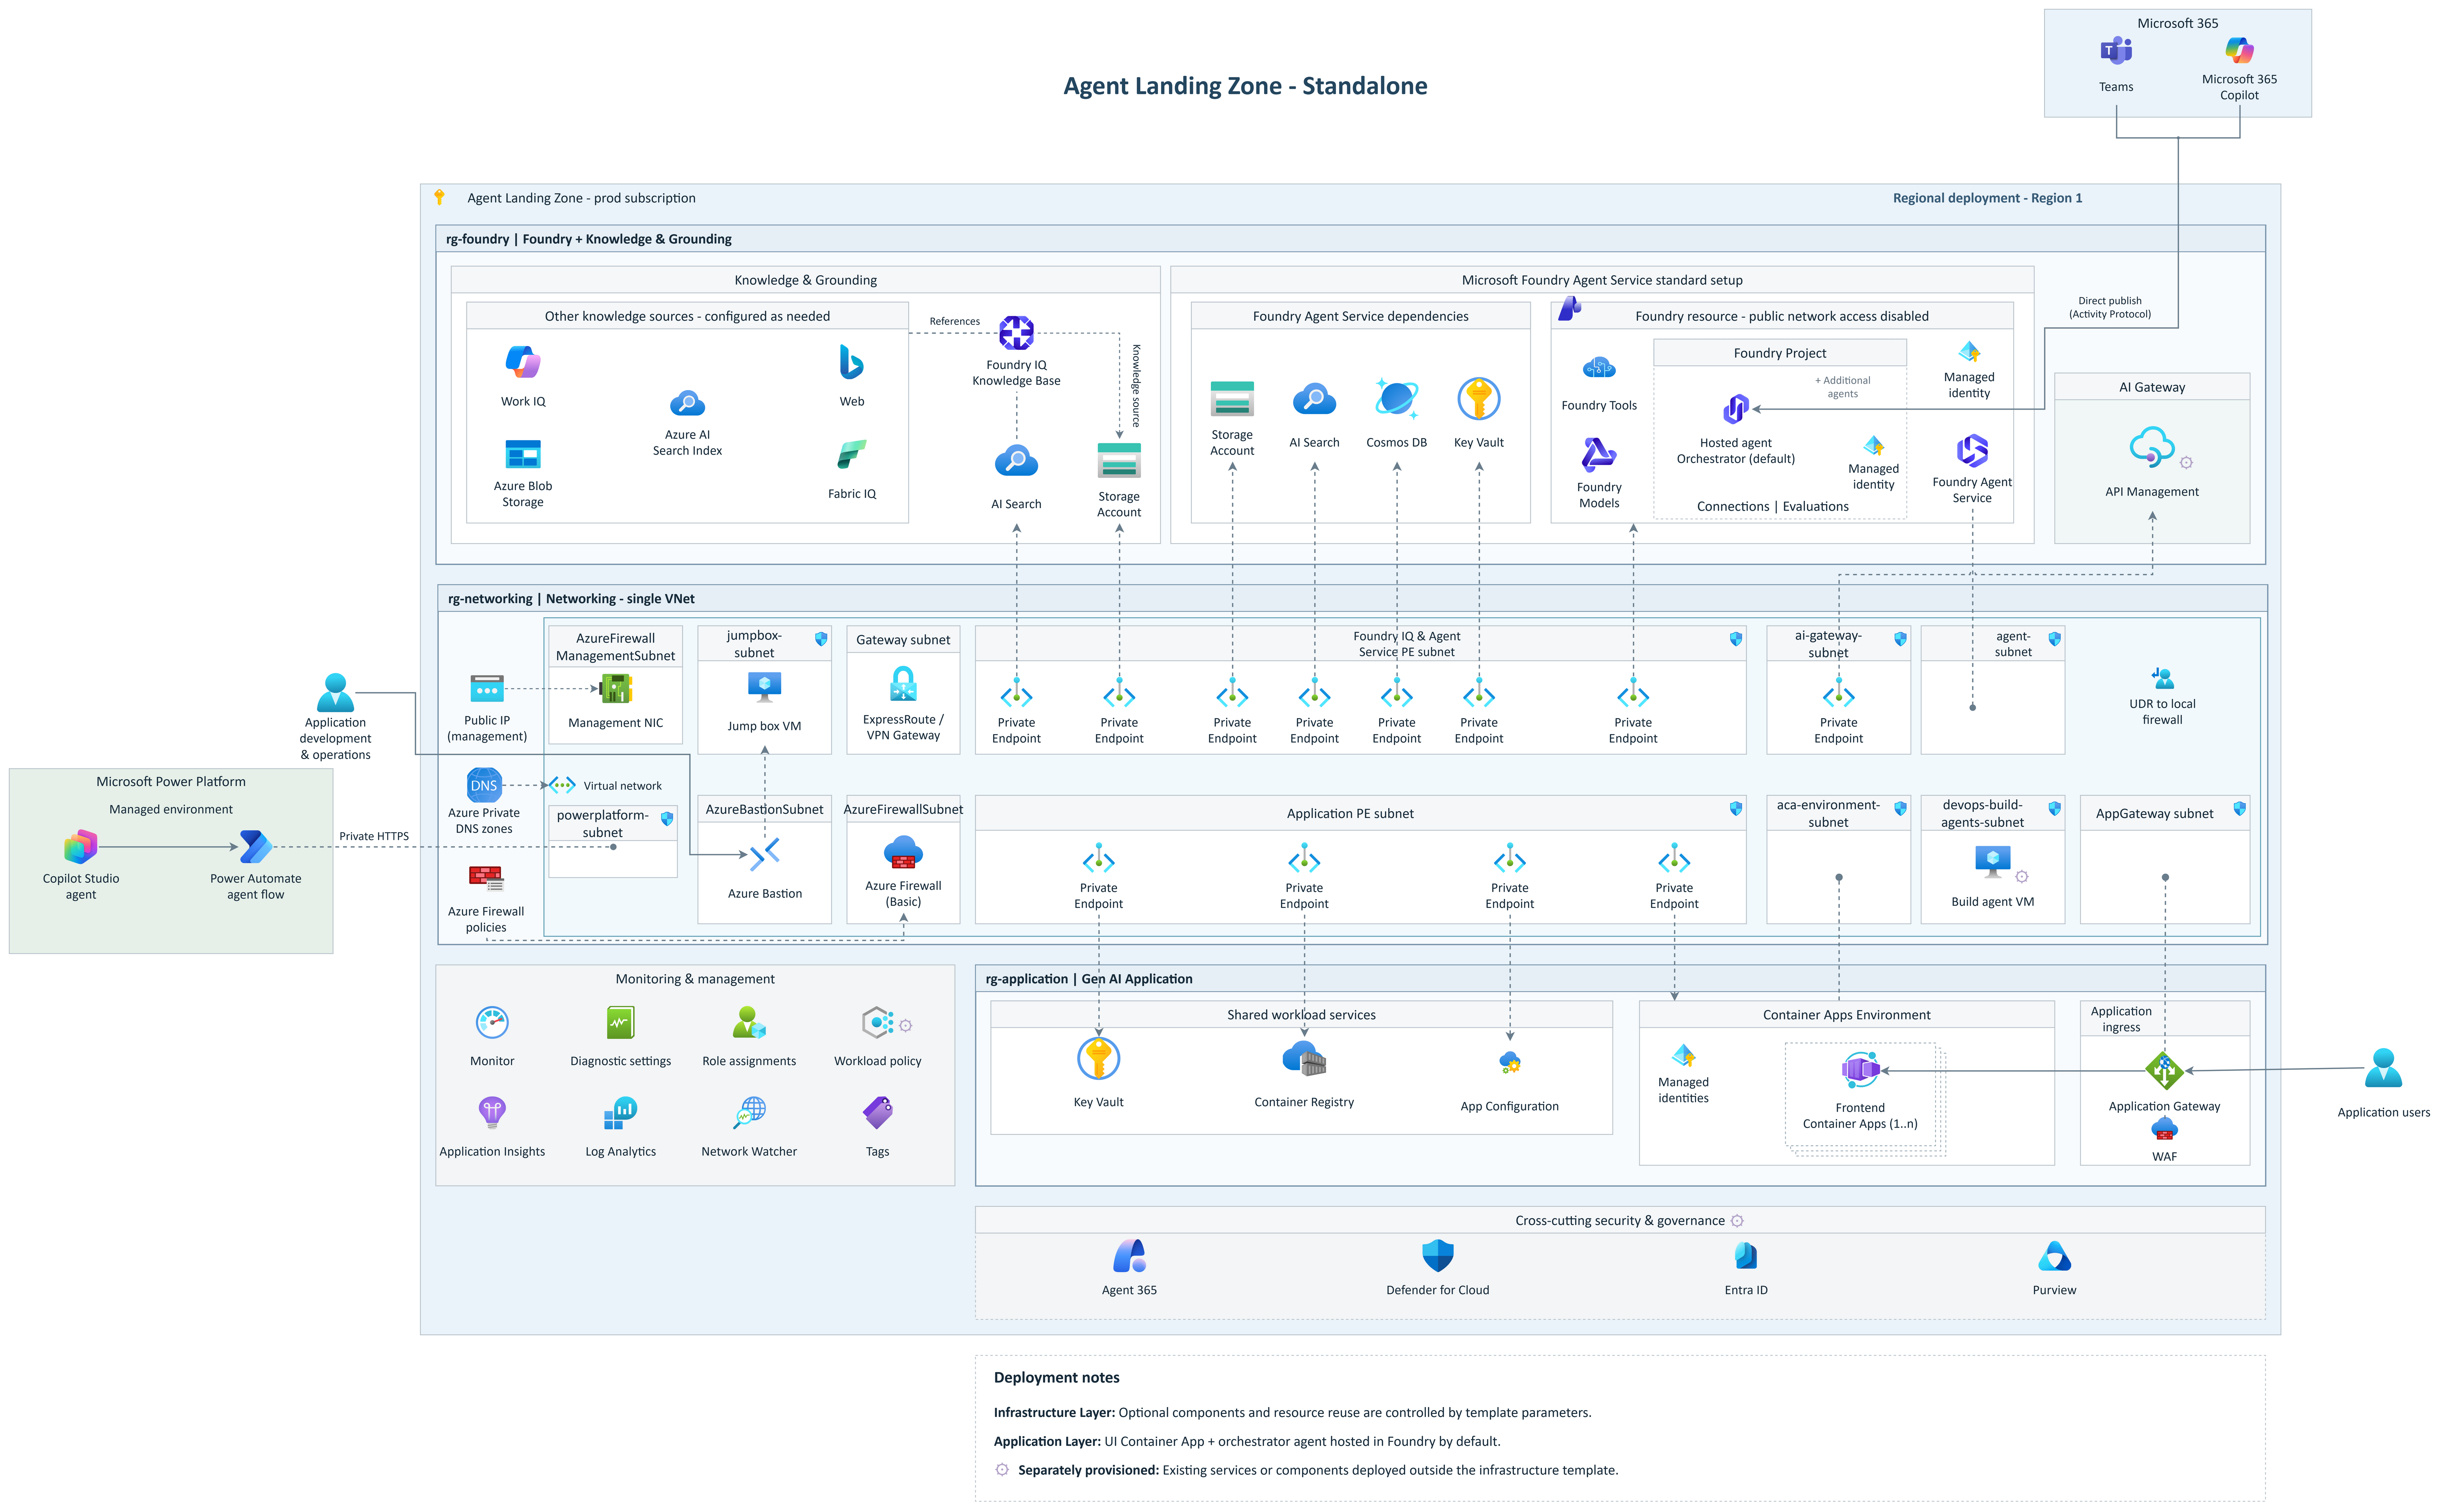
Enterprise-grade landing zone for AI agent applications on Azure. Deploy the secure infrastructure, the agent app, or both — built on Microsoft Foundry and Microsoft Agent Framework, with Zero-Trust networking, observability and IaC.
Open-Source Network Management, Monitoring, ITOM, Observability, and Security Analytics
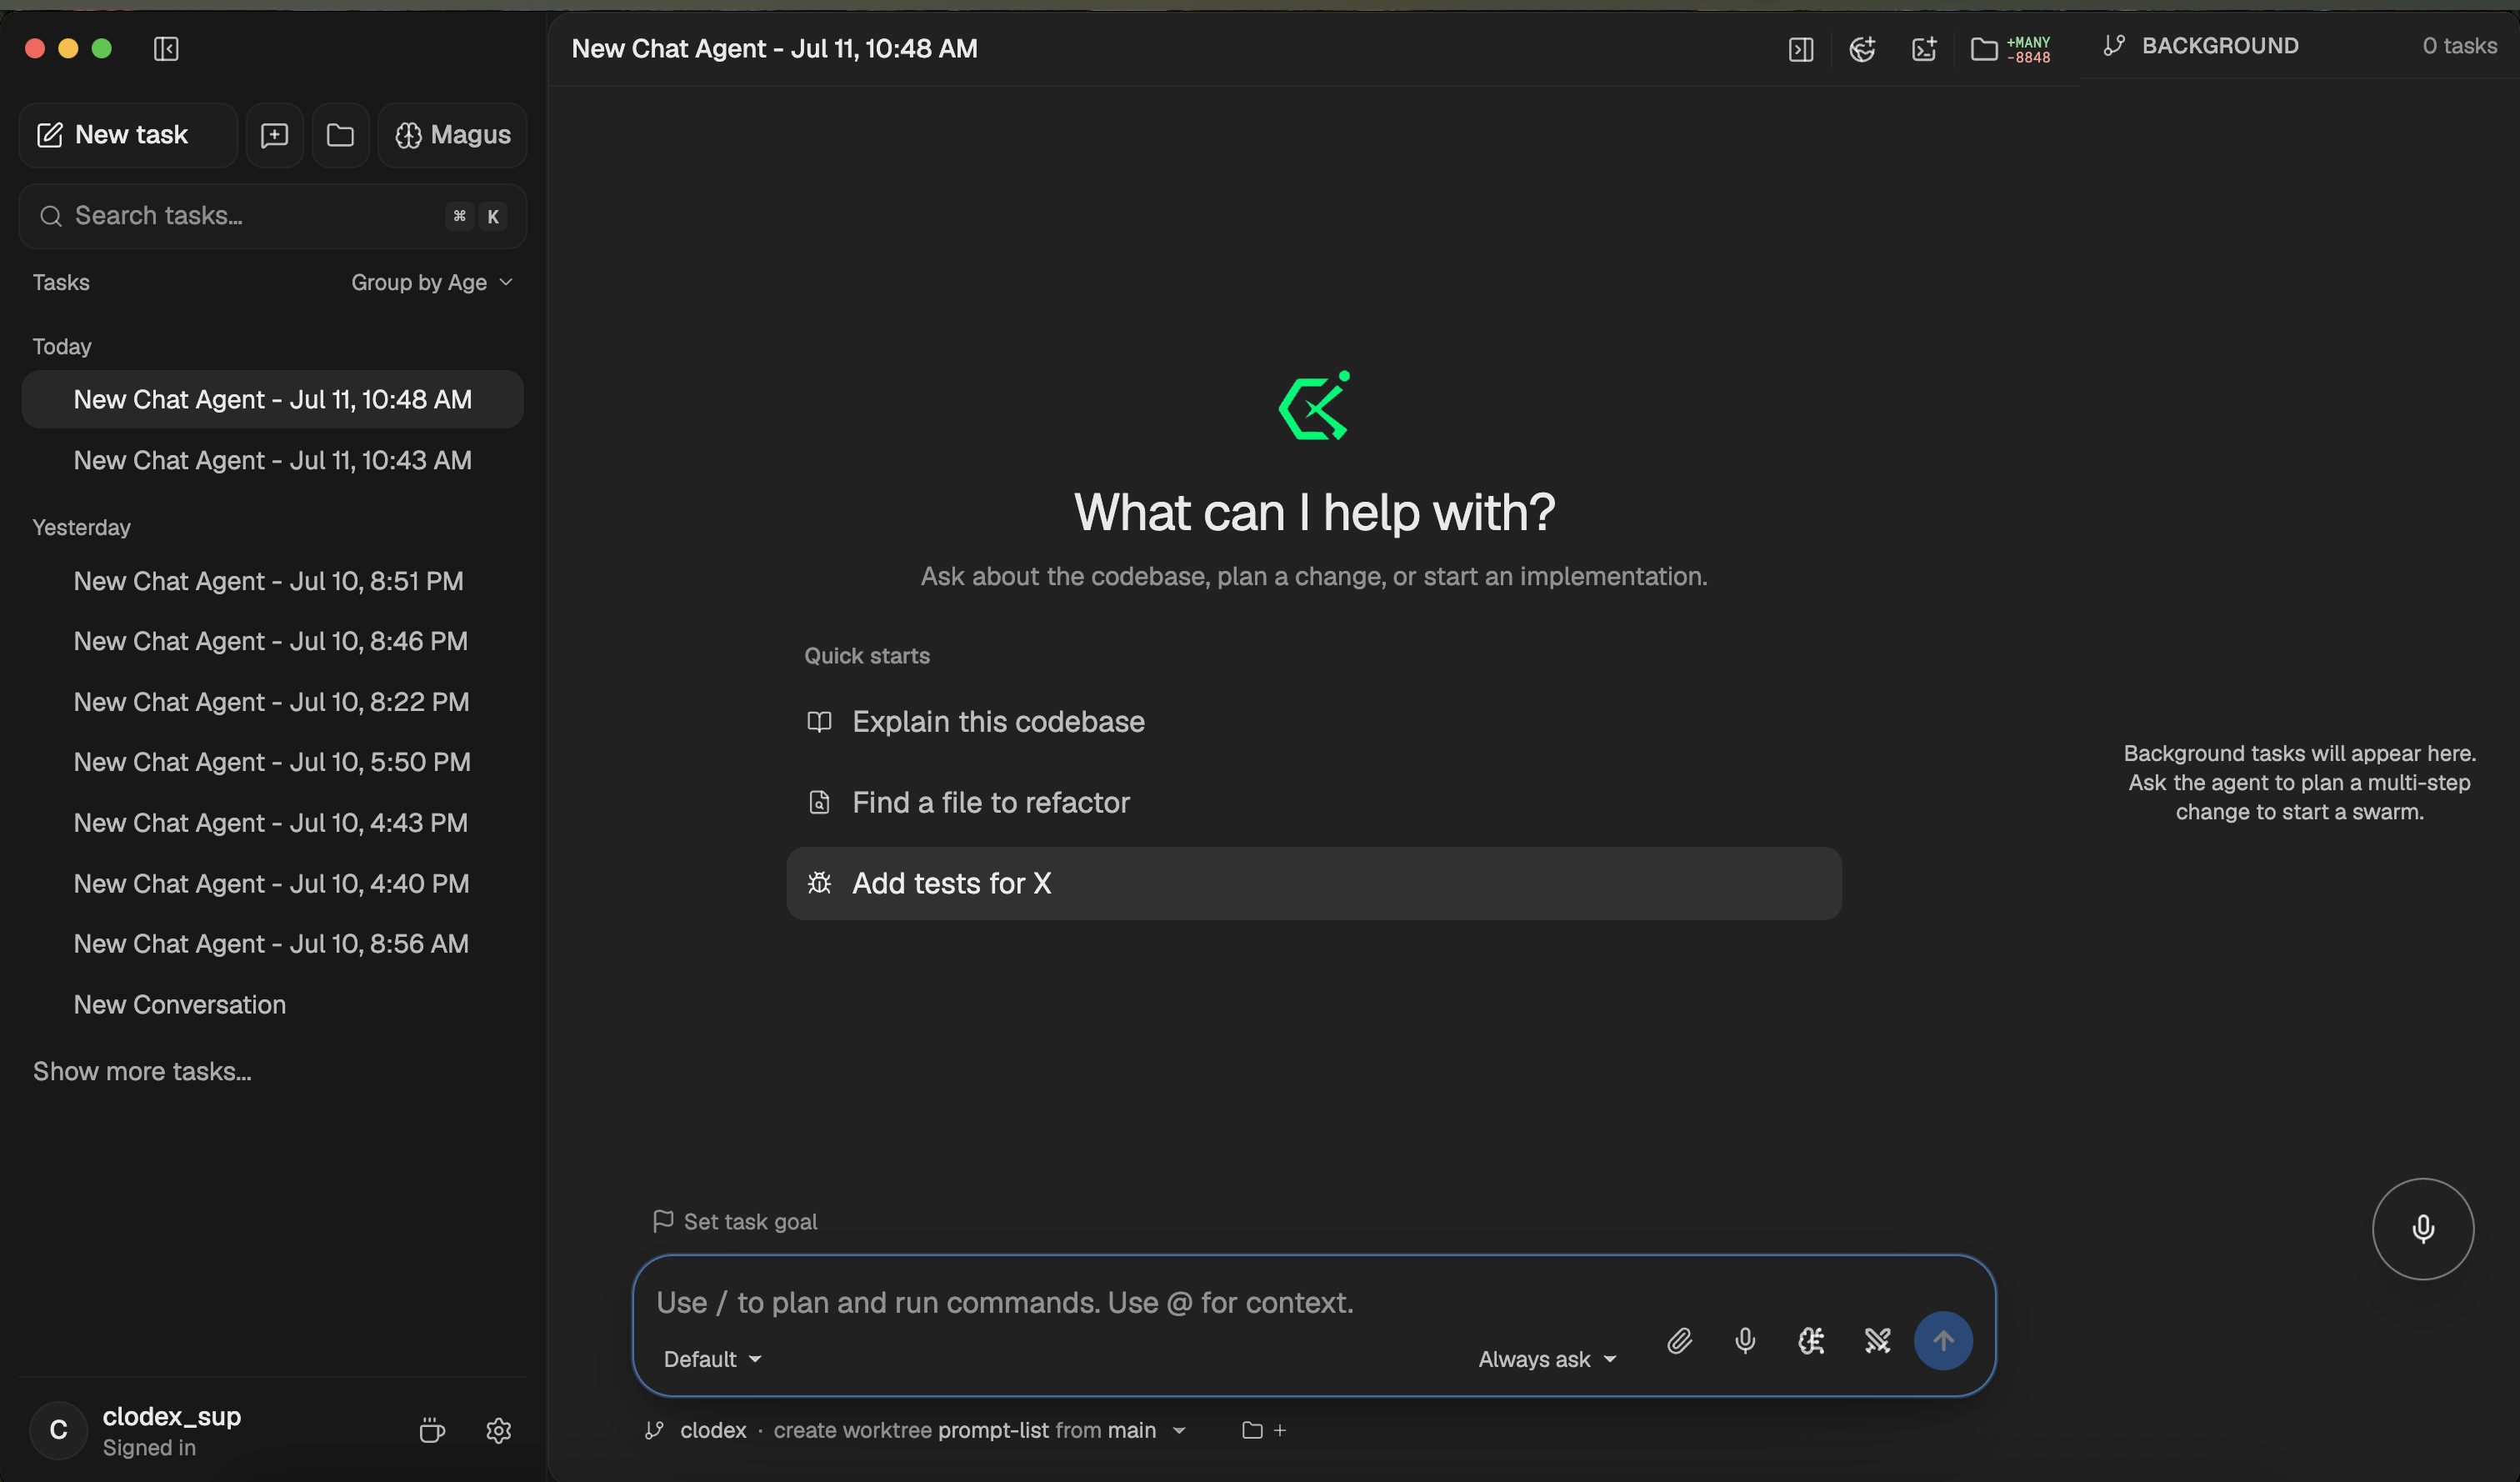
Local-first, zero-trust agentic IDE for verifiable autonomous software development.
A source-grounded course and architectural reference for engineers designing systems that must survive real traffic, partial failure, security review, and changing requirements, spanning enterprise system design, distributed systems, AI systems, cybersecurity, reliability, cloud, HPC, edge, and mission-critical infrastructure.
Run AI agents in a sandbox that restricts what they can execute, read, write, and reach on the network. Box combines OS isolation with default-deny Dogwood policies and credential injection that keeps secrets outside the agent. Written in Rust. Supports macOS on Apple silicon and Linux.
Apeireth — a digital companion that grows with you. Pure Safe Rust AGI cognitive microkernel: memory that fades like a person's, human approval before every side effect, honest boundaries. 31-member workspace (30 crates + 1 bench).
Easy auditing & sandboxing for your JavaScript dependencies 🪱
BeyondCorp-inspired HTTPS/SSO Access Proxy. Secure internal services outside your VPN/perimeter network during a zero-trust transition.
Open-source platform for multi-agent AI orchestration, real-world asset tokenization, workflow automation. Includes OAuth 2.1 MCP agent management, a 44-field RWA schema, Stripe, designed to integrate with AetherNet QUAS & KVS sovereign, post quantum, architecture agnostic omni-substrate, semantic memory, & institutional settlement system.
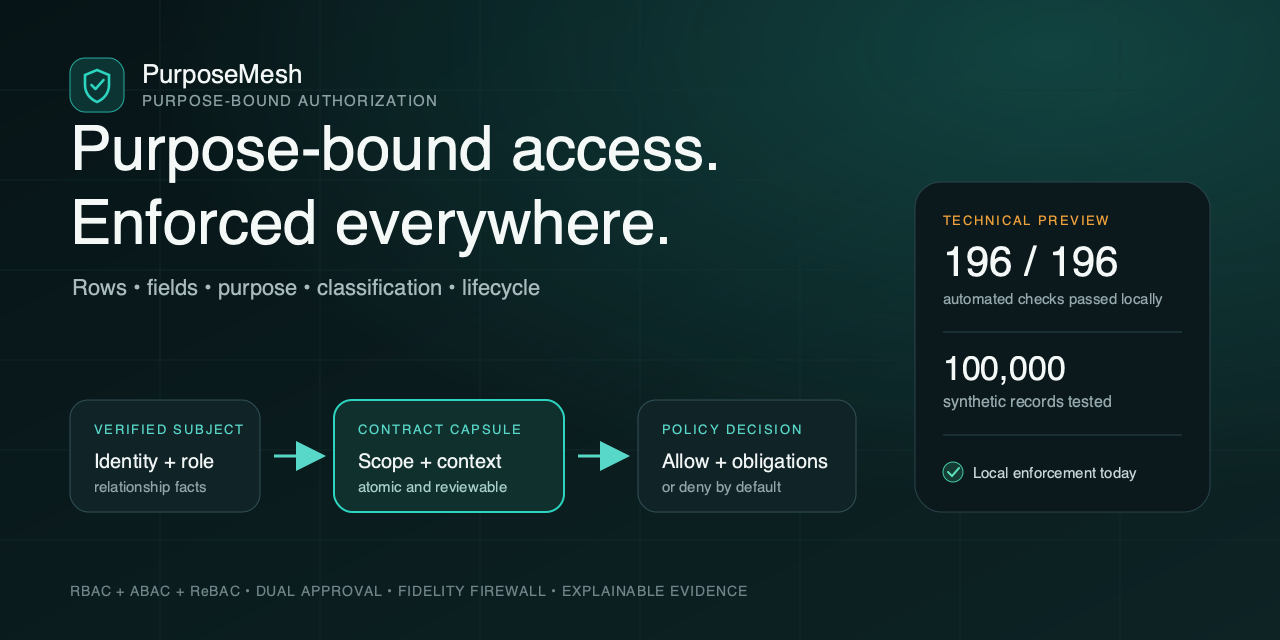
Purpose-bound authorization reference: RBAC + ABAC + ReBAC, row/field controls, fidelity gates, lifecycle governance, and a tested 100K synthetic-data path.
Your private network, wherever you work. Peer-to-peer first, end-to-end encrypted access to your own LANs — no port forwarding, no public URLs. | 无论你在哪里办公,你的私有网络都如影随形。以点对点优先,端到端加密访问你自己的局域网——不用端口转发,也没有公开网址。
🔑 Team Access Sharing - a self-hosted solution with single sign-on for secure, easy shared access to servers, databases, and applications.
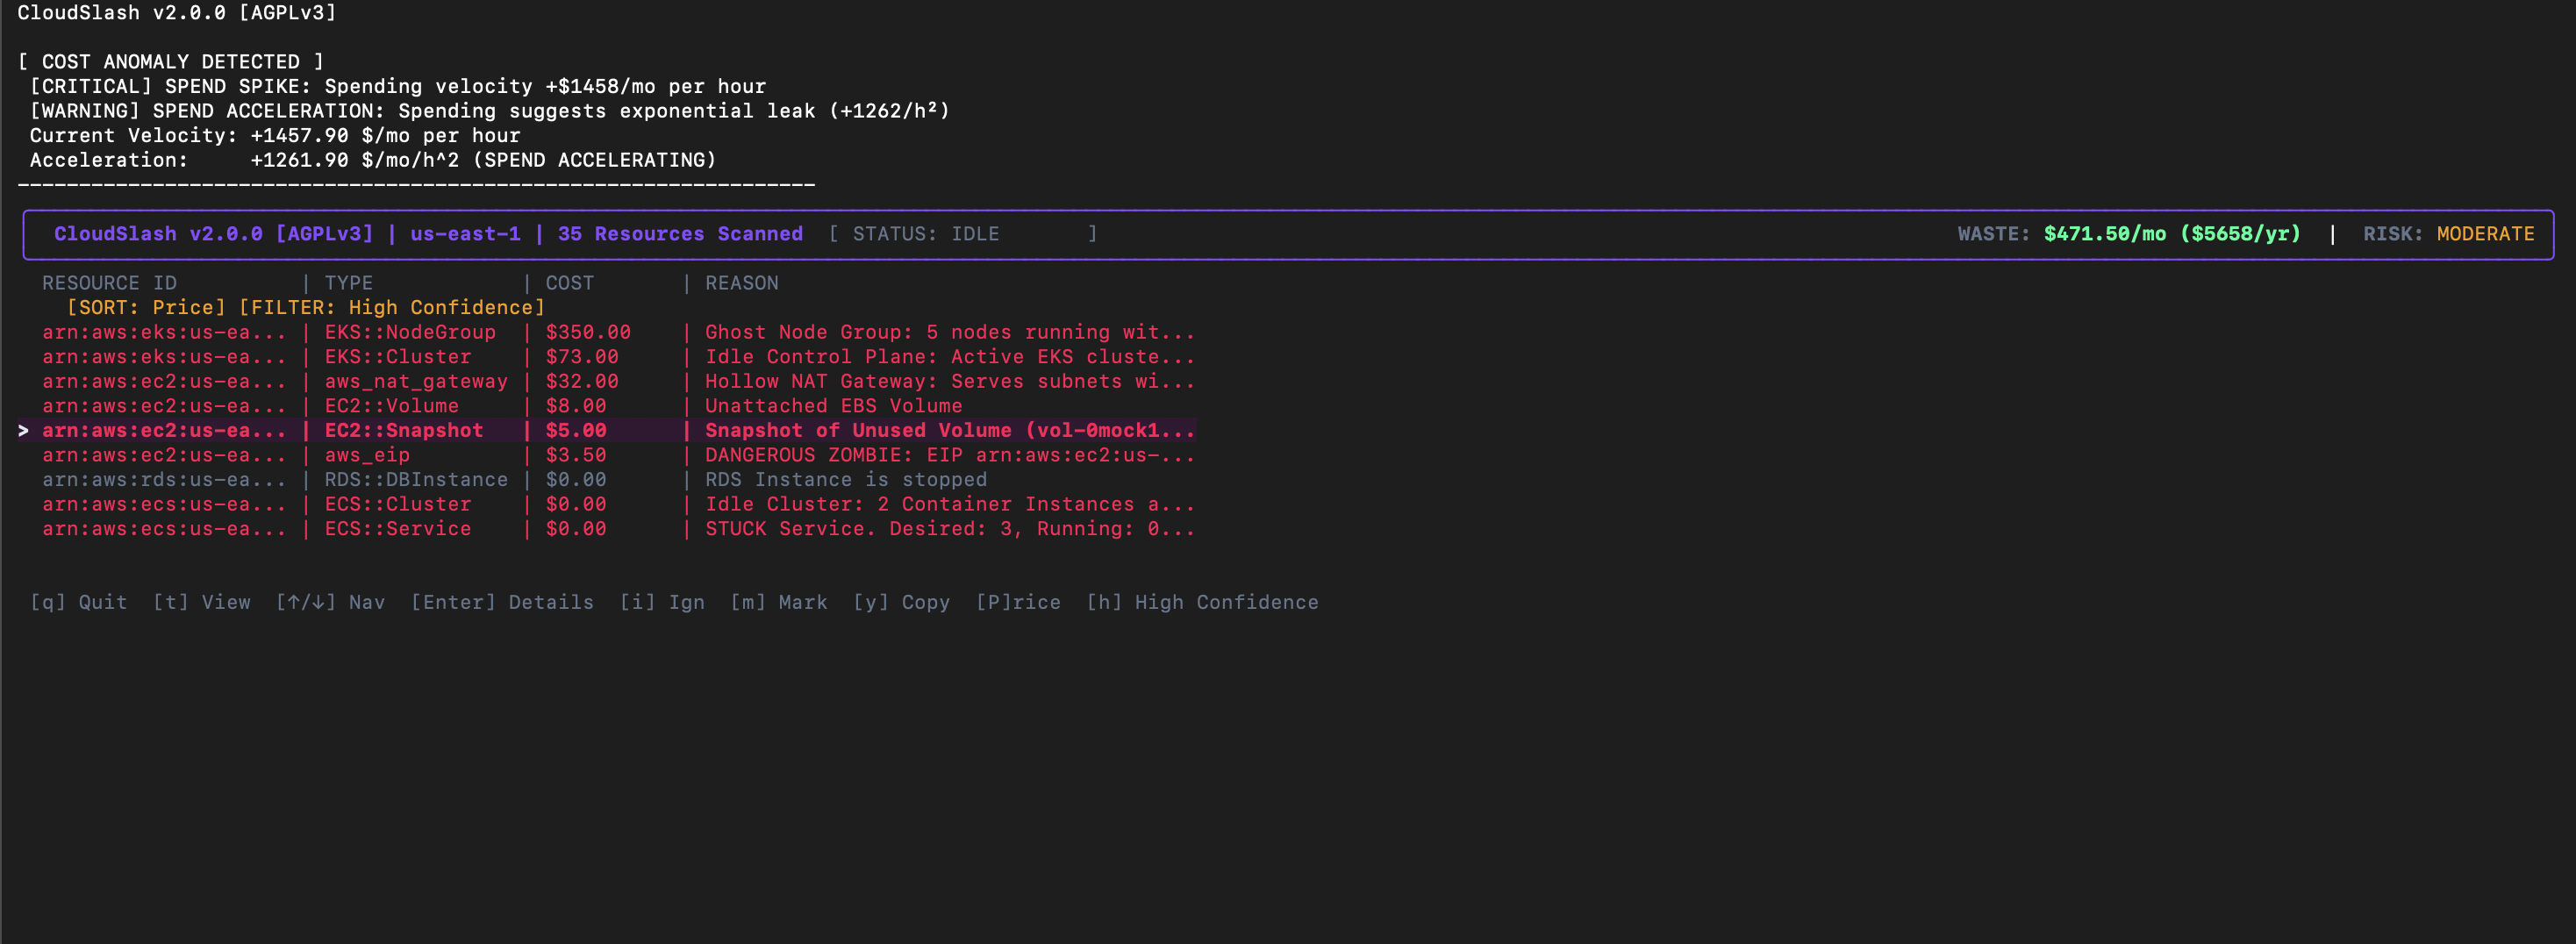
System-agnostic visibility, governance, and waste remediation. Read-only plugin discovery, a universal resource graph, and signed remediation plans. Use it from any AI agent over MCP: https://cloudslash.dev
Zero-GPU-idle gateway for running ComfyUI on ephemeral Google Colab VMs with Zero-Trust Access
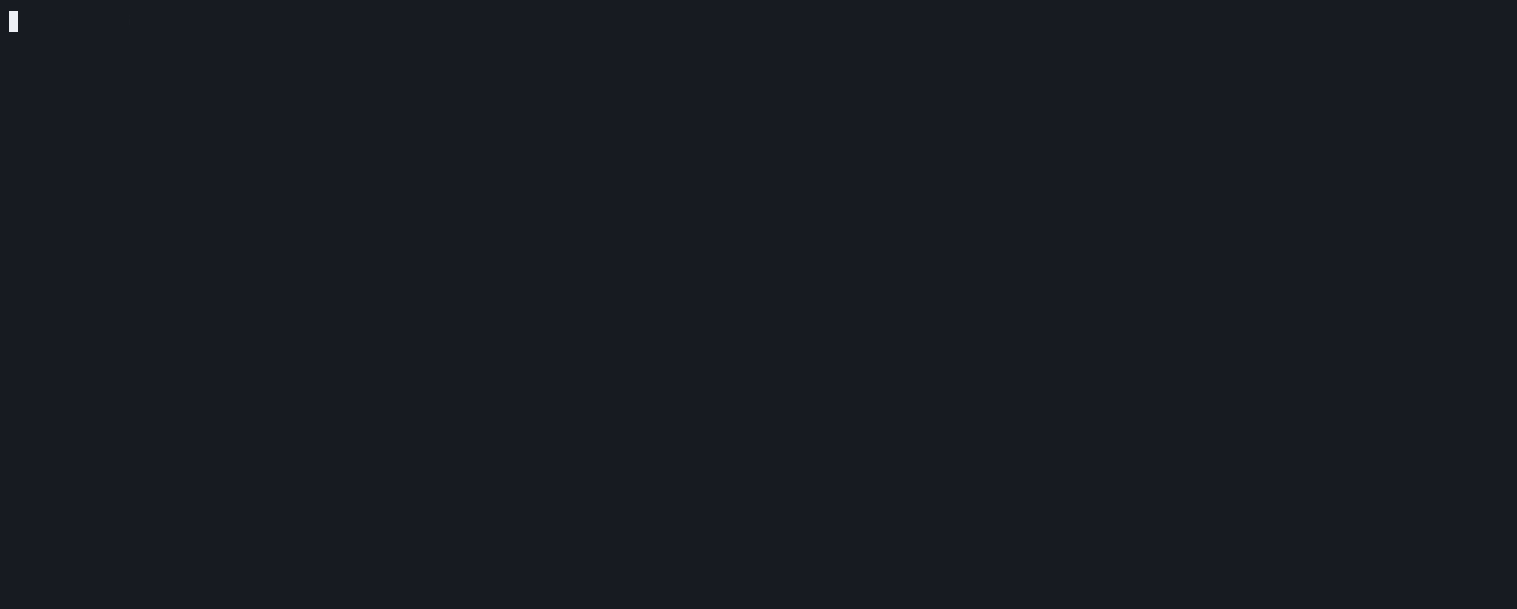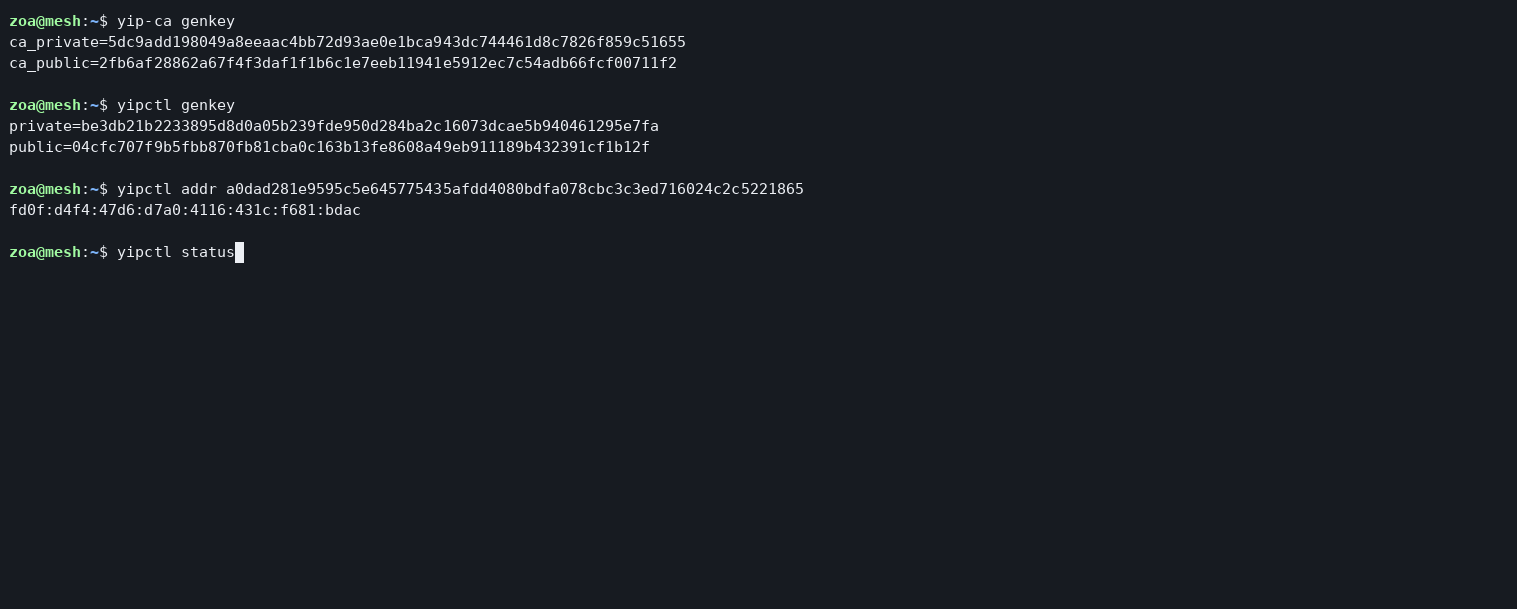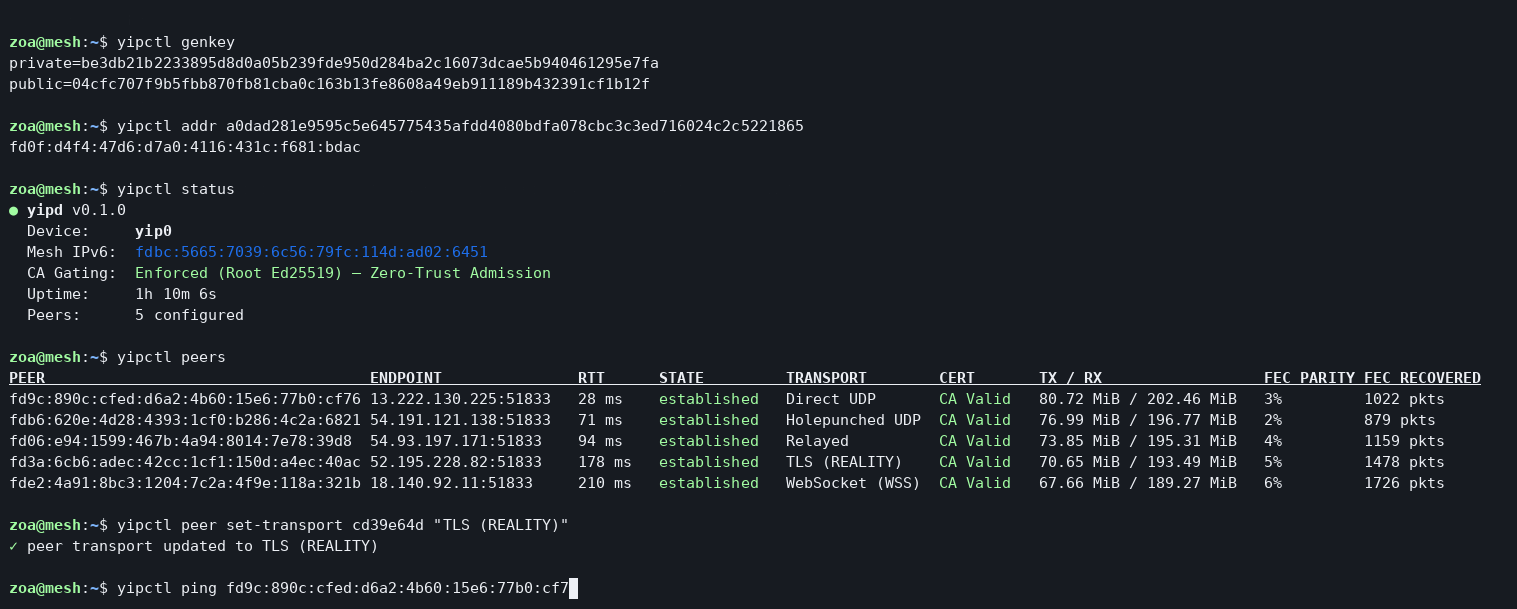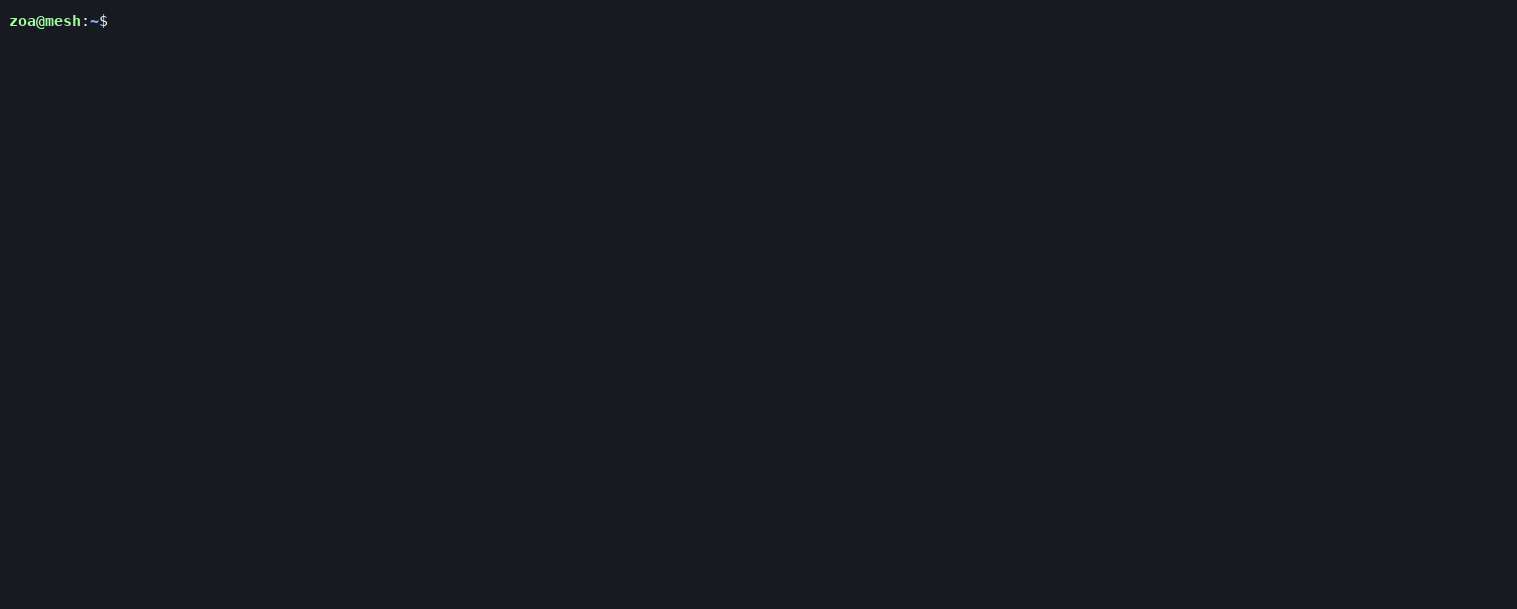
🦊 Low-latency P2P mesh VPN in Rust. Reed–Solomon FEC loss immunity, Post-Quantum, 40 Gbps AF_XDP, multi-core scaling, NAT traversal, decentralized CA, self-certifying routing, DAITA, and anti-DPI TLS mimicry.
Zero trust LLM gateway. OpenAI-compatible proxy with semantic routing and load balancing across OpenAI, Anthropic, Ollama, vLLM, and any compatible backend. Identity-based access, virtual API keys, and end-to-end encryption via OpenZiti