ImHex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
- 56k
- C++
- GPL-2.0
- 1 d ago
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
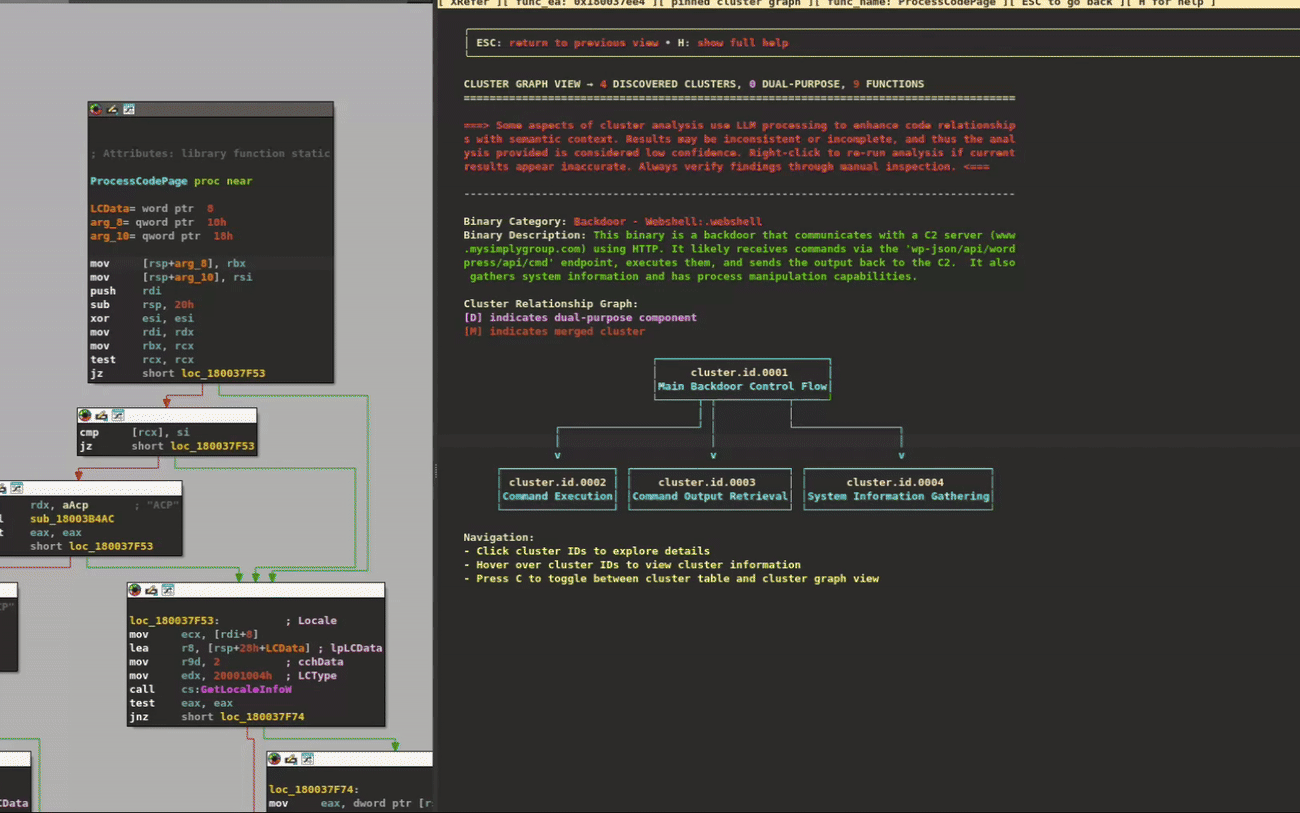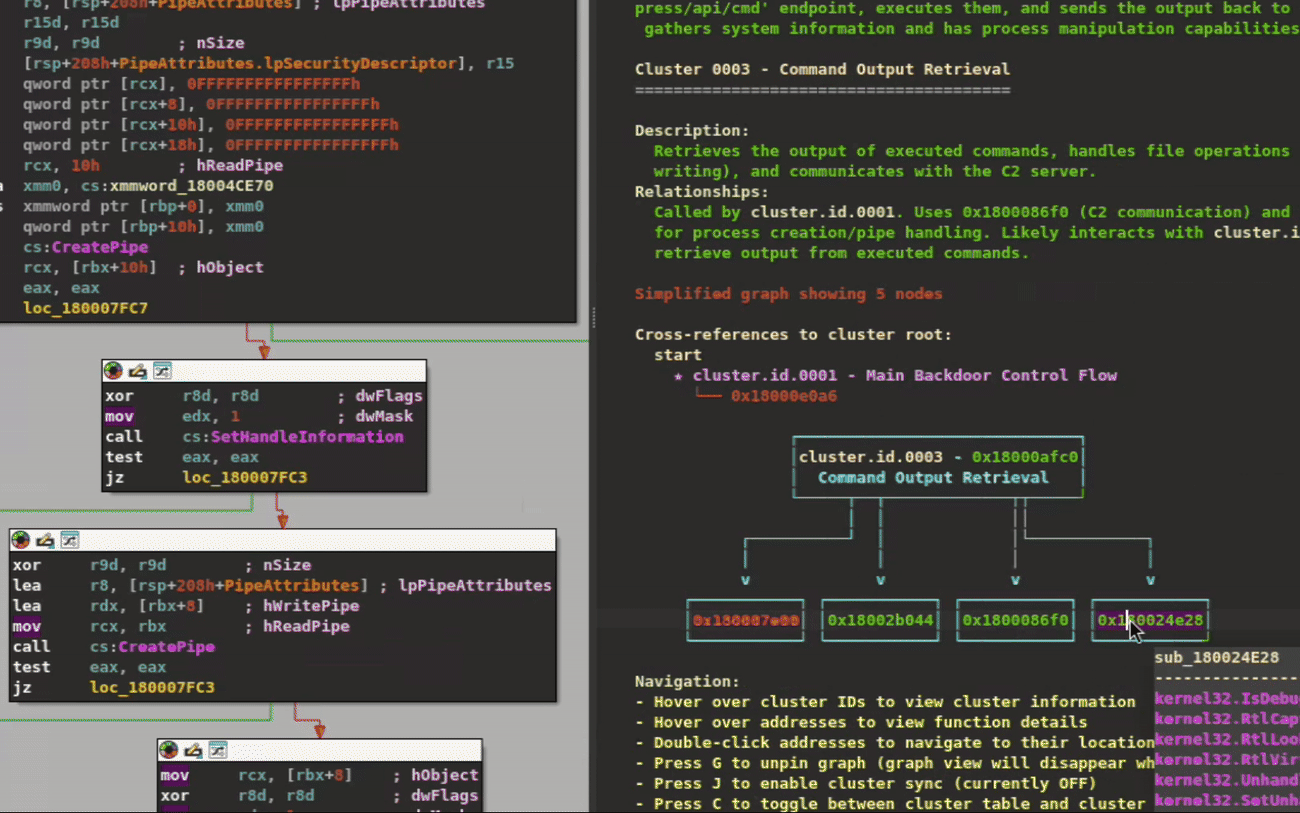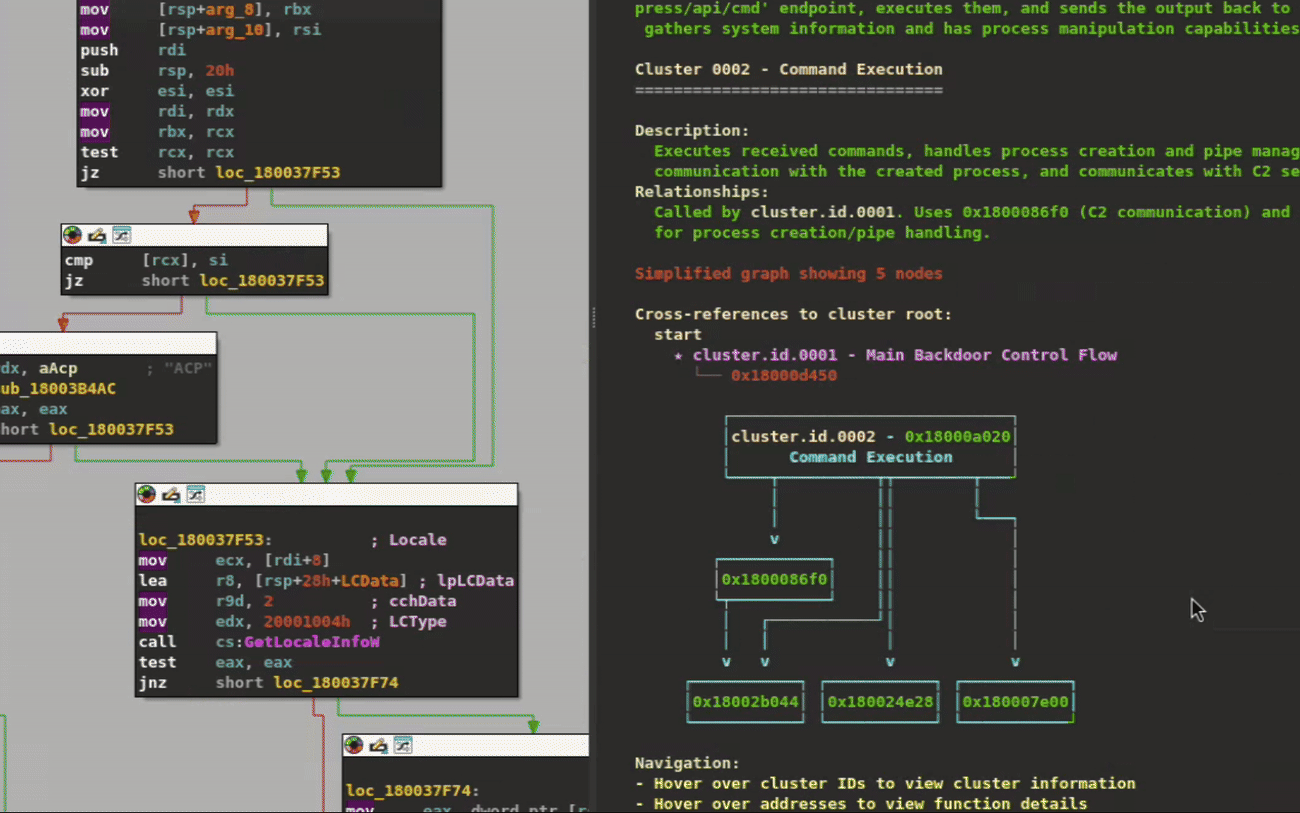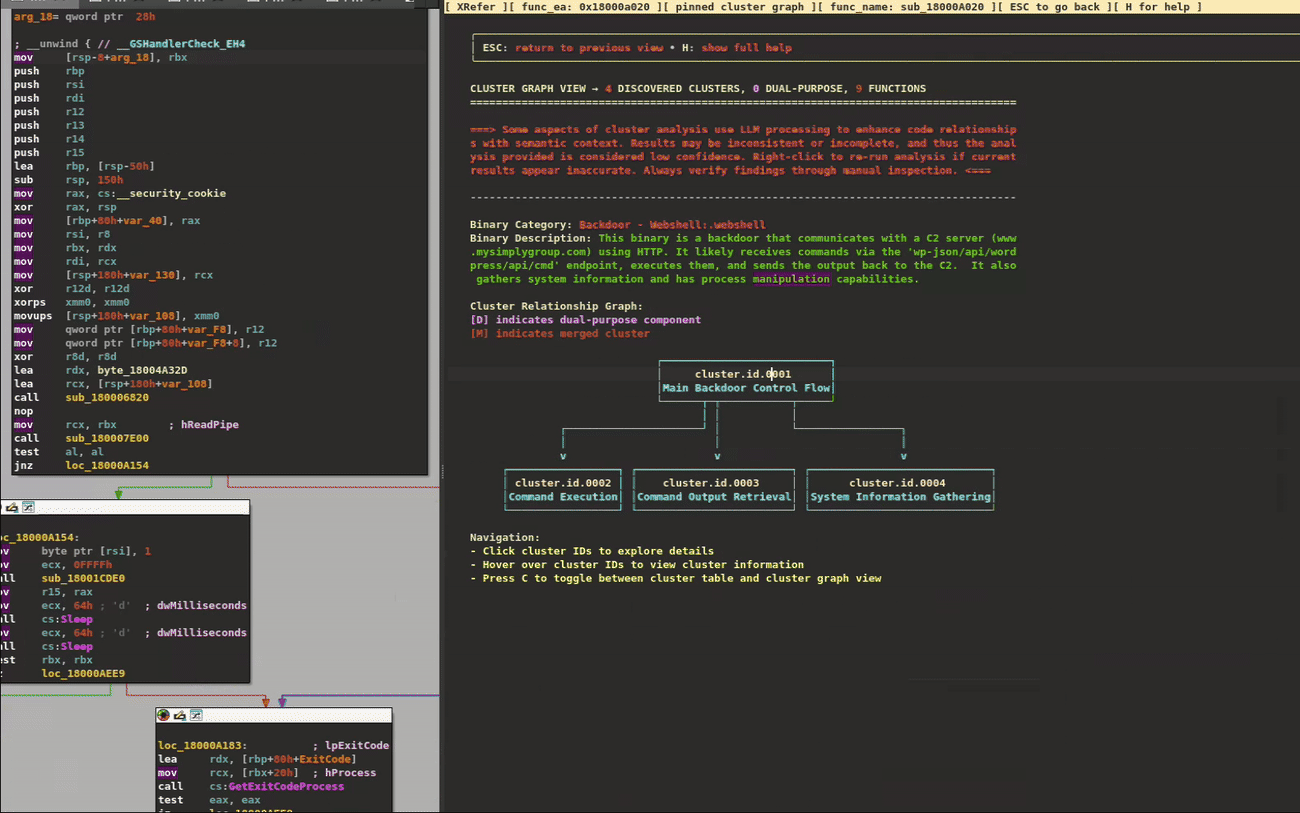
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
Program for determining types of files for Windows, Linux and MacOS.
The Ultimate Open-Source Security Arsenal for Hackers, Enterprises, and AI Agents——面向极客、企业与 AI 智能体的全域开源网络安全工具矩阵
The FLARE team's open-source tool to identify capabilities in executable files.
Ghidra MCP Server — 200+ MCP tools for AI-powered reverse engineering. GUI plugin + headless server, lazy tool loading, convention enforcement, batch operations, Ghidra Server integration, and Docker deployment.
Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification or just emulate code.
Curated tools, case studies and papers for reverse engineering websites, games, apps, binaries, firmware and protocols. Source-reviewed, English and Chinese.
BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
Stop your AI from making things up — it proposes, deterministic tools decide, every claim checked against ground truth with evidence. Grounded facts and context survive resets. Reverse engineering is the proving ground. MCP server + CLI.
DyninstAPI: Tools for binary instrumentation, analysis, and modification.
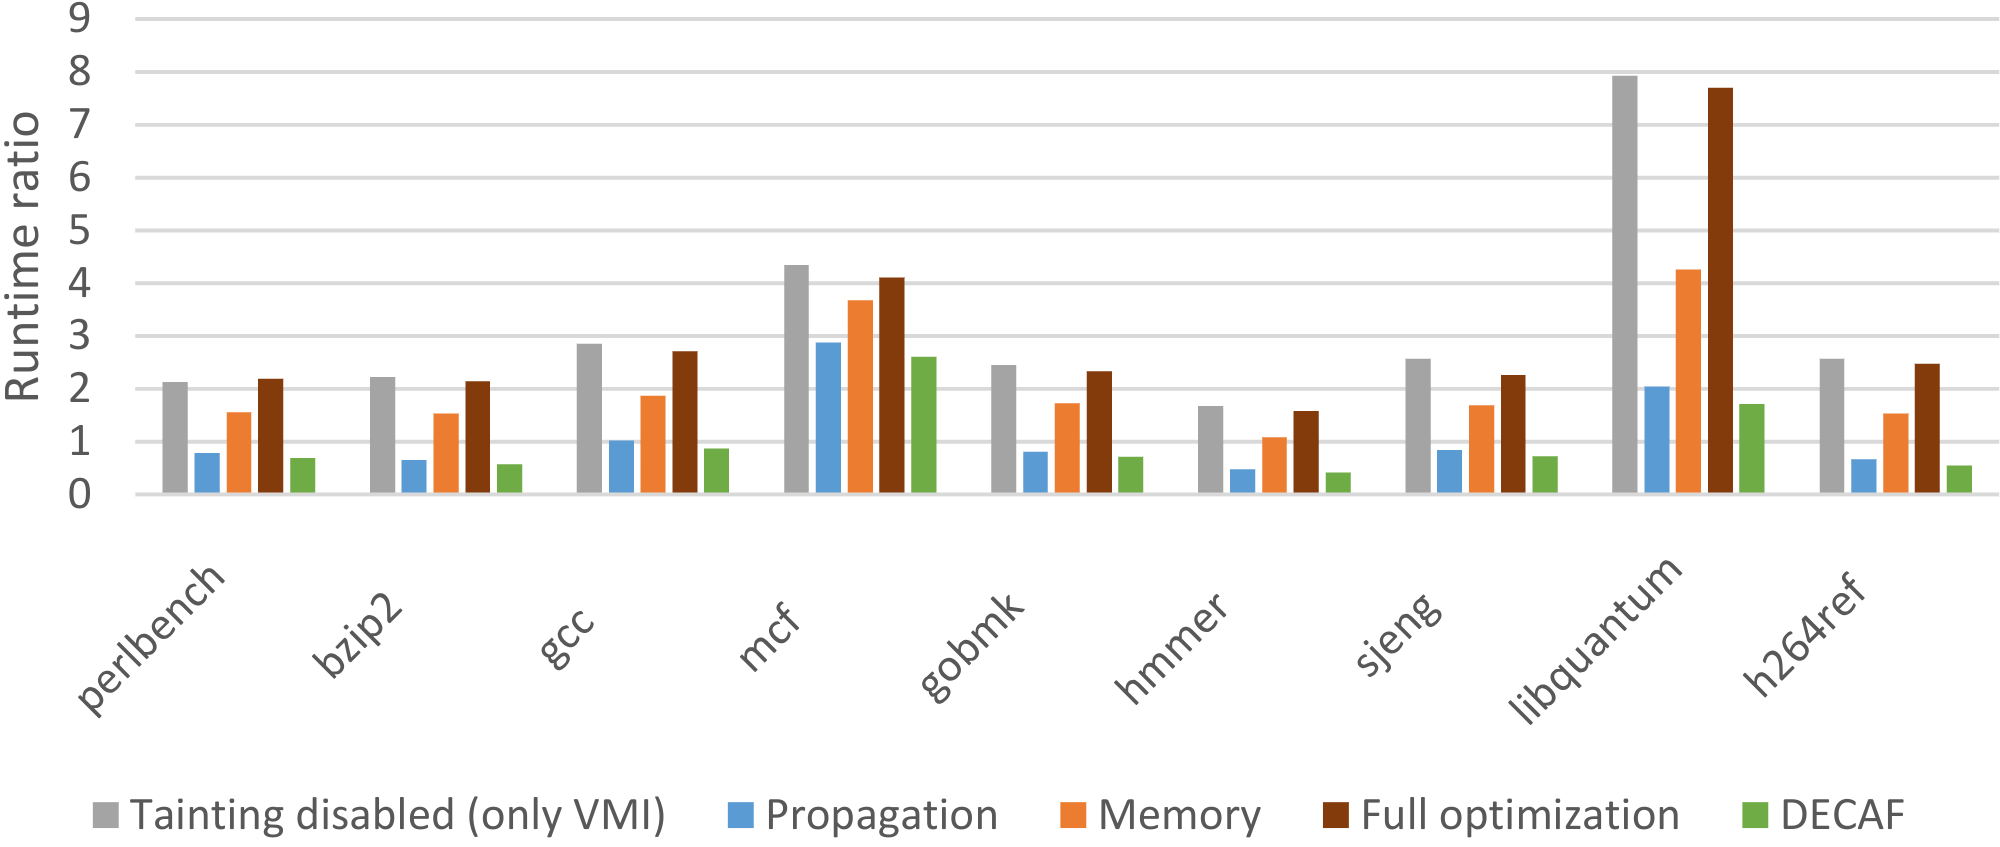
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope dynamic Android malware analysis platform. DroidScope is now an extension to DECAF.
Code and exercises for a workshop on z3 and angr