Triton
Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification or just emulate code.
- 4.4k
- C++
- Apache-2.0
- 9 d ago
Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification or just emulate code.
A PHP static analysis tool for finding errors and security vulnerabilities in PHP applications
The SpotBugs plugin for security audits of Java web applications and Android applications. (Also work with Kotlin, Groovy and Scala projects)
A Static Analysis Tool for Detecting Security Vulnerabilities in Python Web Applications
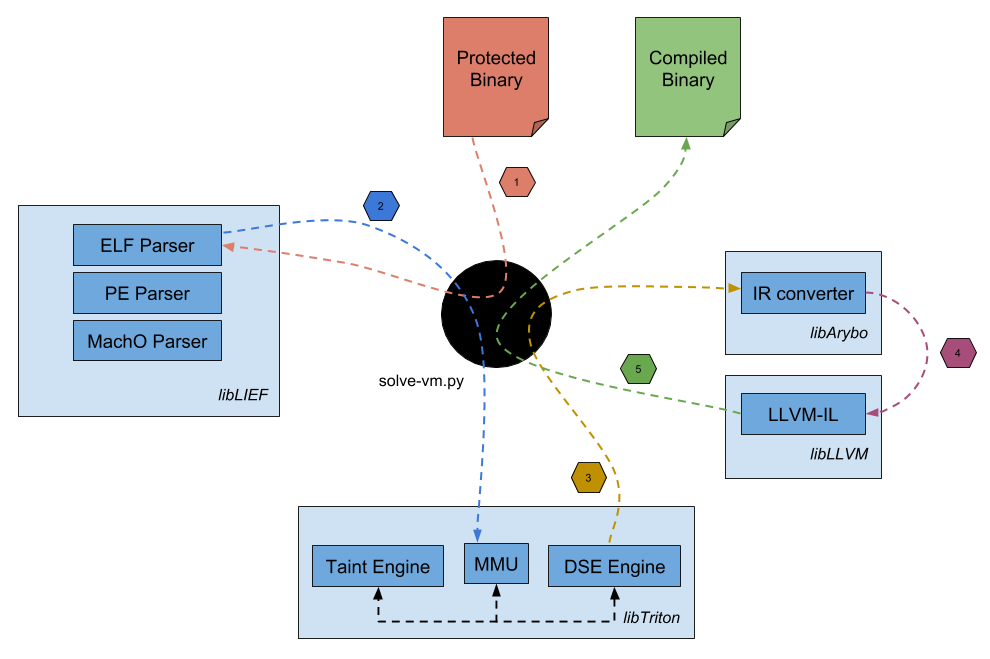
Playing with the Tigress software protection. Break some of its protections and solve their reverse engineering challenges. Automatic deobfuscation using symbolic execution, taint analysis and LLVM.
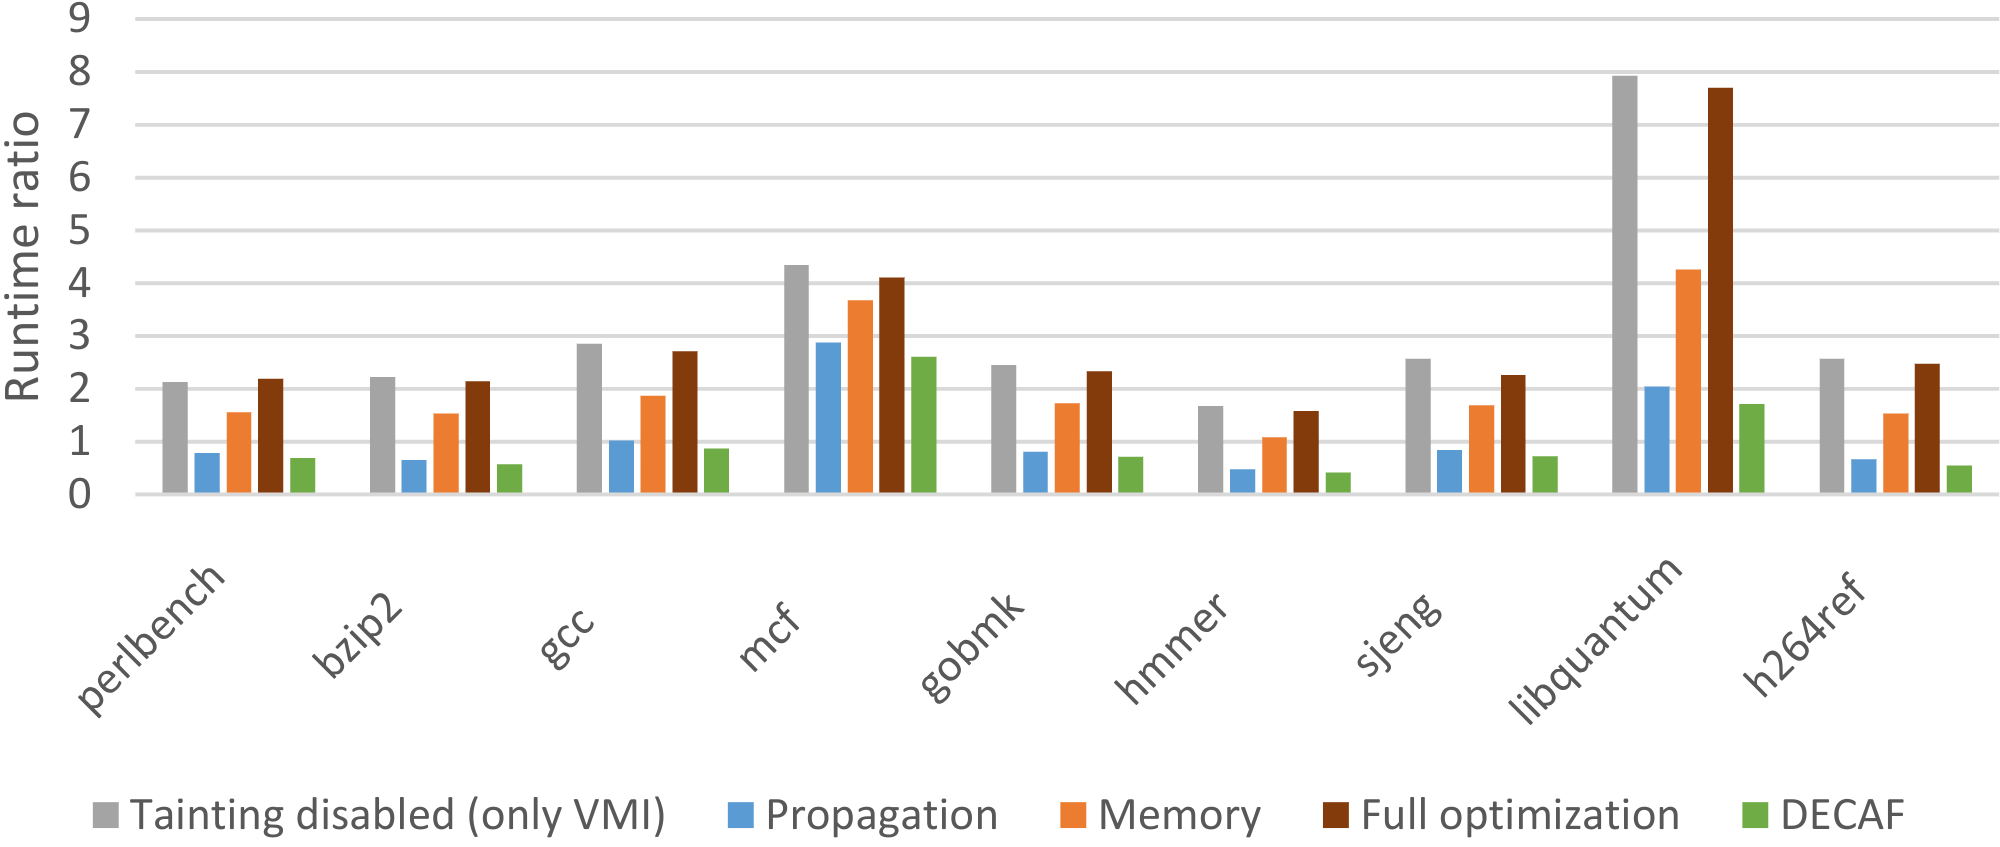
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope dynamic Android malware analysis platform. DroidScope is now an extension to DECAF.
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
Corax for Java: A general static analysis framework for java code checking.
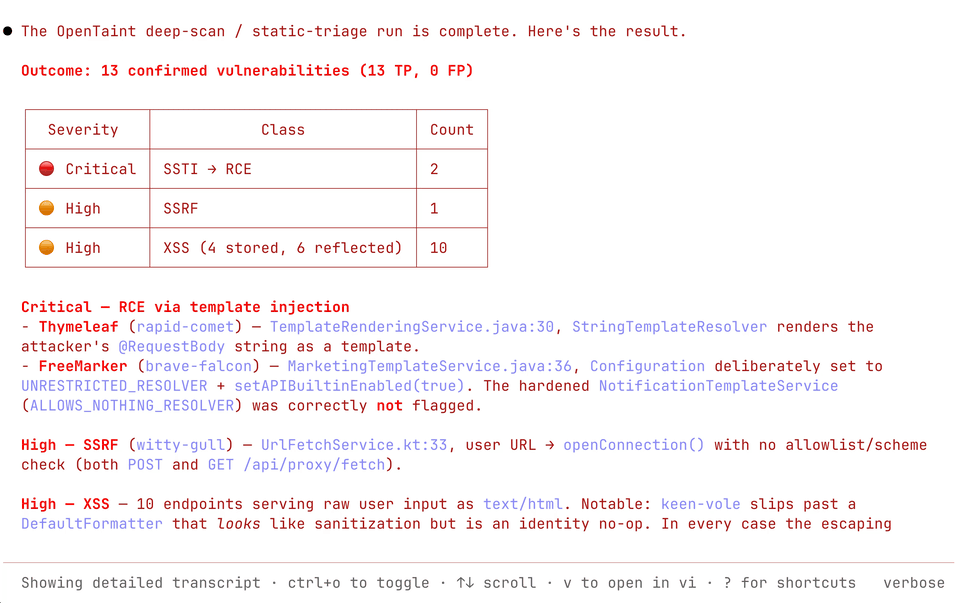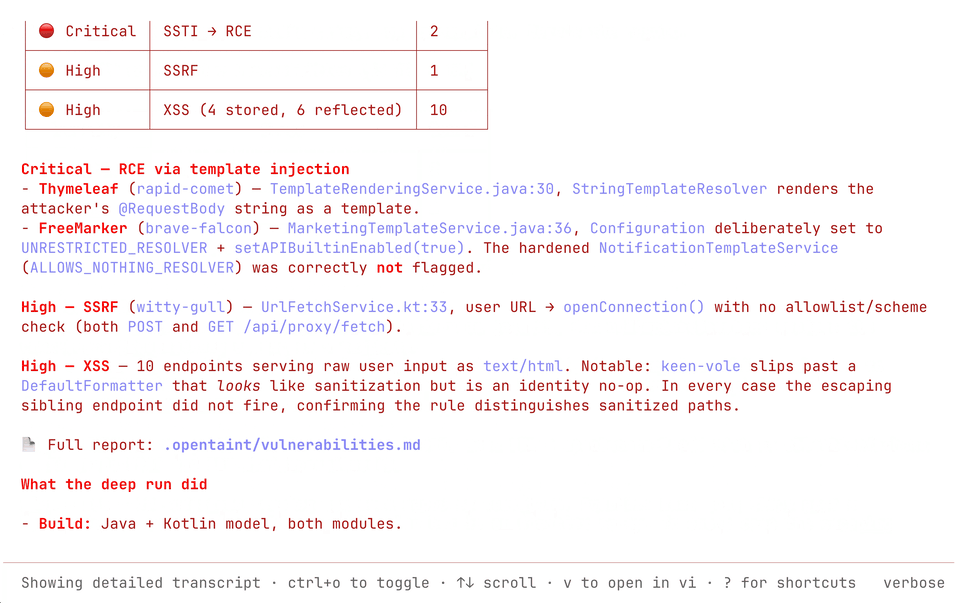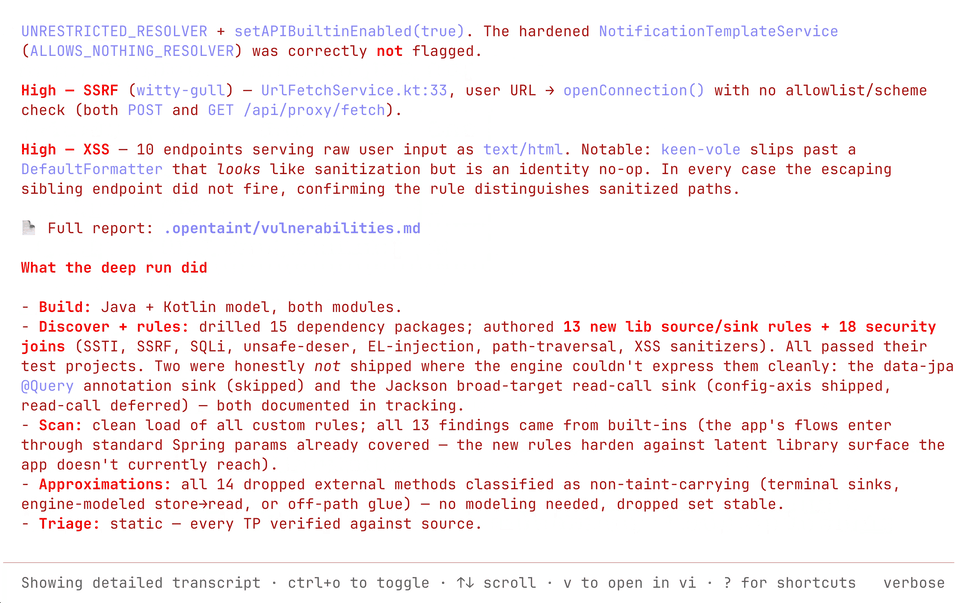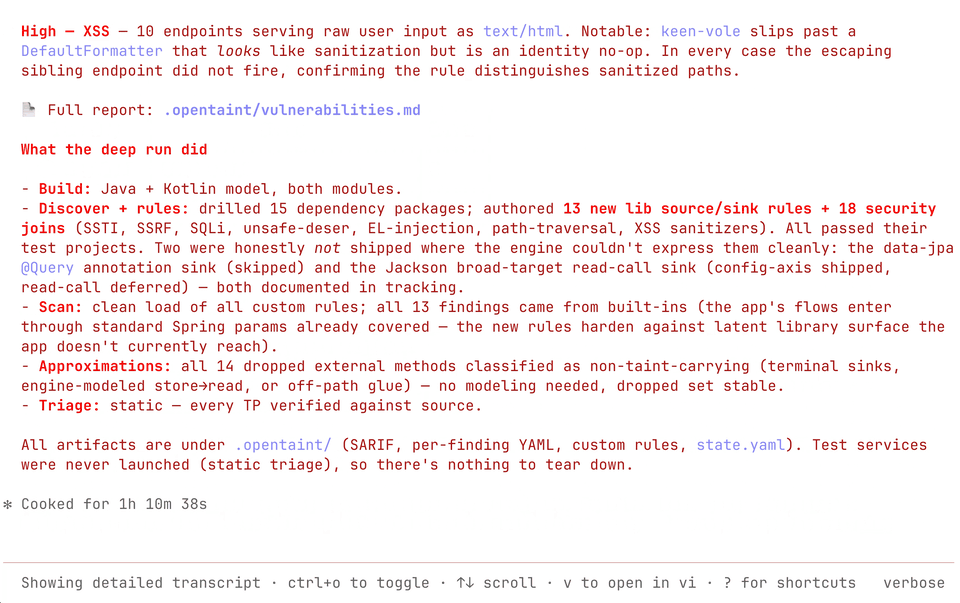
The open source taint analysis engine for the AI era. A formal dataflow analysis tool you can customize and self-host, built so AI agents drive your application security analysis without burning tokens on every scan. AI-ready open source alternative to Semgrep Pro and CodeQL.
🦡 codebadger is a containerized Model Context Protocol (MCP) server that gives AI agents and LLMs deep, queryable access to a codebase's structure and data flow through Joern Code Property Graphs (CPGs).
Static security scanner for LLM agents — prompt injection, MCP config auditing, taint analysis. 51 rules mapped to OWASP Agentic Top 10 (2026). Works with LangChain, CrewAI, AutoGen.
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
Local, evidence-based application security assessment engine with its own data flow (taint) engine for JavaScript, TypeScript, Python and Java, an evidence ledger and a Claude Code plugin
Static taint analysis for HarmonyOS/ArkTS with declarative assets, LLM-assisted API modeling, OCLFS, and evidence-driven postsolve.