bugbounty-tool


ppfuzz
A fast tool to scan client-side prototype pollution vulnerability written in Rust. 🦀
- 679
- Rust
- MIT
- 15 mo ago


missing-cve-nuclei-templates
Weekly updated list of missing CVEs in nuclei templates official repository. Mainly built for bug bounty, but useful for penetration tests and vulnerability assessments too.
- 454
- Shell
- MIT
- 5 d ago
PassDetective
PassDetective is a command-line tool that scans shell command history to detect mistakenly written passwords, API keys, and secrets. Using regular expressions, it helps prevent accidental exposure of sensitive information in your command history.
- 153
- Go
- Apache-2.0
- 5 d ago

gofingerprint
GoFingerprint is a Go tool for taking a list of target web servers and matching their HTTP responses against a user defined list of fingerprints.
- 209
- Go
- 3 y ago

bbr
An open source tool to aid in command line driven generation of bug bounty reports based on user provided templates.
- 217
- Go
- GPL-3.0
- 6 y ago

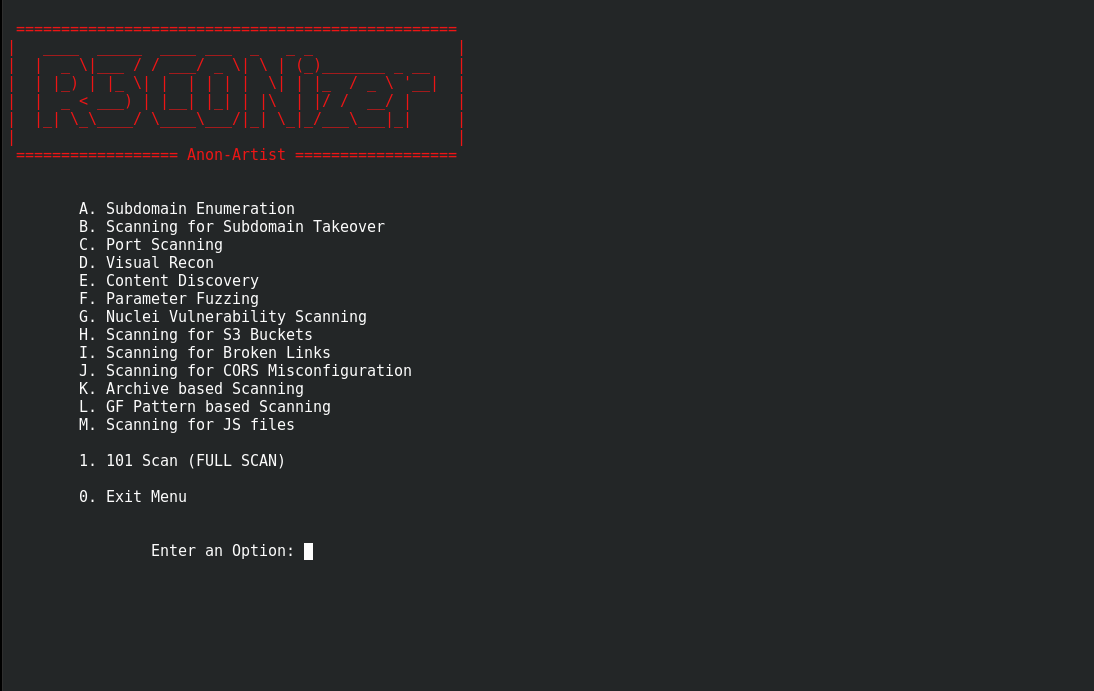
R3C0Nizer
R3C0Nizer is the first ever CLI based menu-driven web application B-Tier recon framework.
- 149
- Shell
- 6 y ago

AttackSurfaceManagement
Discover the attack surface and prioritize risks with our continuous Attack Surface Management (ASM) platform - Sn1per Professional #pentest #redteam #bugbounty
- 107
- Shell
- 5 y ago

ExternalAttacker-MCP
A modular external attack surface mapping tool integrating tools for automated reconnaissance and bug bounty workflows.
- 77
- Python
- 20 mo ago


Gui-Dorking
🕵️♂️ | Powerful tool for Google Dorking, Web Scraping, and Archive Searching. Designed for speed and efficiency with a Gui. Perfect for OSINT researchers
- 22
- Python
- MIT
- 22 mo ago


SnailHunter
SnailHunter is a fully automated bug bounty hunting platform that combines traditional security tools with AI-powered analysis.
- 20
- Python
- 7 mo ago


UUIDHunter
This Extension provides a Passive and Active Scan Check that detects V1 UUIDs and attempts to find other potentially valid ones.
- 6
- Java
- 4 y ago
Burp-wordlist-hub
WordlistHub is a Burp Suite extension that lets pentesters browse, search, download, cache, and use wordlist like SecLists and custom GitHub wordlists directly inside Burp. Select a wordlist and stream it straight into Intruder—no more switching to GitHub, downloading files, or copying and pasting payloads manually.
- 1
- Python
- 3 mo ago
