spiderfoot
SpiderFoot automates OSINT for threat intelligence and mapping your attack surface.
- 25k
- Python
- MIT
- 7 mo ago
SpiderFoot automates OSINT for threat intelligence and mapping your attack surface.
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port scanning; Fuzz, HW, awesome BugBounty( ͡° ͜ʖ ͡°)...
AI-powered bug bounty hunting toolkit that works with or without subscription.
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
Take a list of domains, crawl urls and scan for endpoints, secrets, api keys, file extensions, tokens and more
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering, reverse search, red team, trust & safety, AI.
Quickly discover exposed hosts on the internet using multiple search engines.
a recon tool that allows searching on URLs that are exposed via shortener services
Go CLI and Library for quickly mapping organization network ranges using ASN information.
OSINT Project. Collect information from a mail. Gather. Profile. Timeline.
Search Google/Bing/Ecosia/DuckDuckGo/Yandex/Yahoo for a search term (dork) with a default set of websites, bug bounty programs or custom collection.
⚡ Perform subdomain enumeration using the certificate transparency logs from Censys.
Internal penetration testing tool for Linux that can be used to enumerate OS information, domain information, shares, directories, and users through SMB.
GhostTrack 中文汉化版 | OSINT 追踪工具(IP/手机号/用户名)· 逻辑零改动纯汉化 · 原项目 HunxByts/GhostTrack
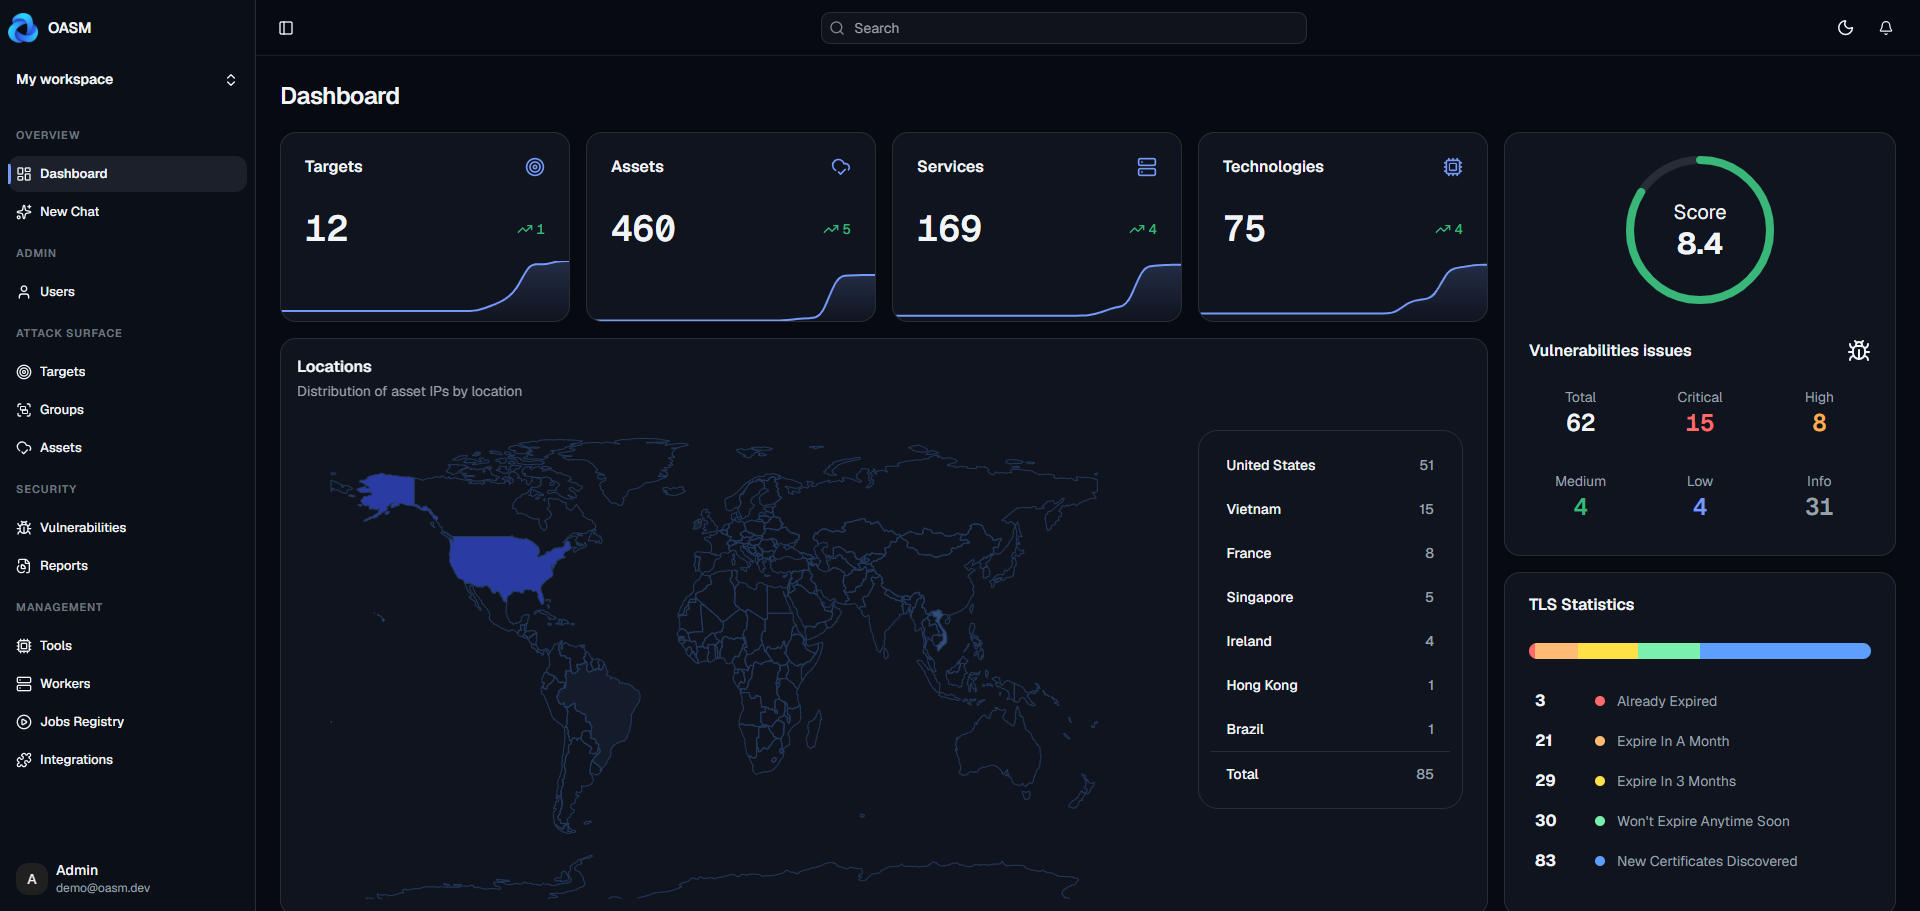
Open-source Attack Surface Management. Discover assets. Identify exposure. Own your security data.
Cross-platform username reconnaissance tool built for OSINT investigators, cyber threat analysts, red teamers, and CTF enthusiasts.
面向真实授权安全评估(SRC / 红队 / 代码审计)的 Agent 技能库:把顶尖安全研究员的方法论沉淀为可调度、可复用的 Skill 资产;v2 主分支适配 DeepSeek Harness,v1 分支保留 Claude Code / Codex 工作流。
This repository updates latest Bug Bounty medium writeups every 10 minutes, https://readmedium.com/Medium_URL, https://archive.ph/Medium_URL, https://freedium.cfd/Medium_URL
The agentic pentesting environment that lives on your machine. AI agent teams, visual workflows and your own tools, 100% local.
Self-hosted bug-bounty platform — verification-first recon & DAST, continuous monitoring. Your data stays on your machine.
A python script to extract information from a Microsoft Remote Desktop Web Access (RDWA) application
An automated GitHub Actions-based crawler that fetches and updates public scopes from popular bug bounty platforms (like Hackerone/Bugcrowd/Intigriti/etc) (updates every 10 minutes)
OWASP Amass Docker Compose for setting up a full instance of the infrastructure
Simultaneously execute various subdomain enumeration tools and aggregate results.