powershell-reverse-tcp
PowerShell scripts for communicating with a remote host.
- 300
- PowerShell
- MIT
- 3 mo ago
PowerShell scripts for communicating with a remote host.
My useful files for penetration tests, security assessments, bug bounty and other security related stuff
An open-source knowledge base of defensive countermeasures to protect AI/ML systems. Features interactive views and maps defenses to known threats from frameworks like MITRE ATLAS, MAESTRO, and OWASP.
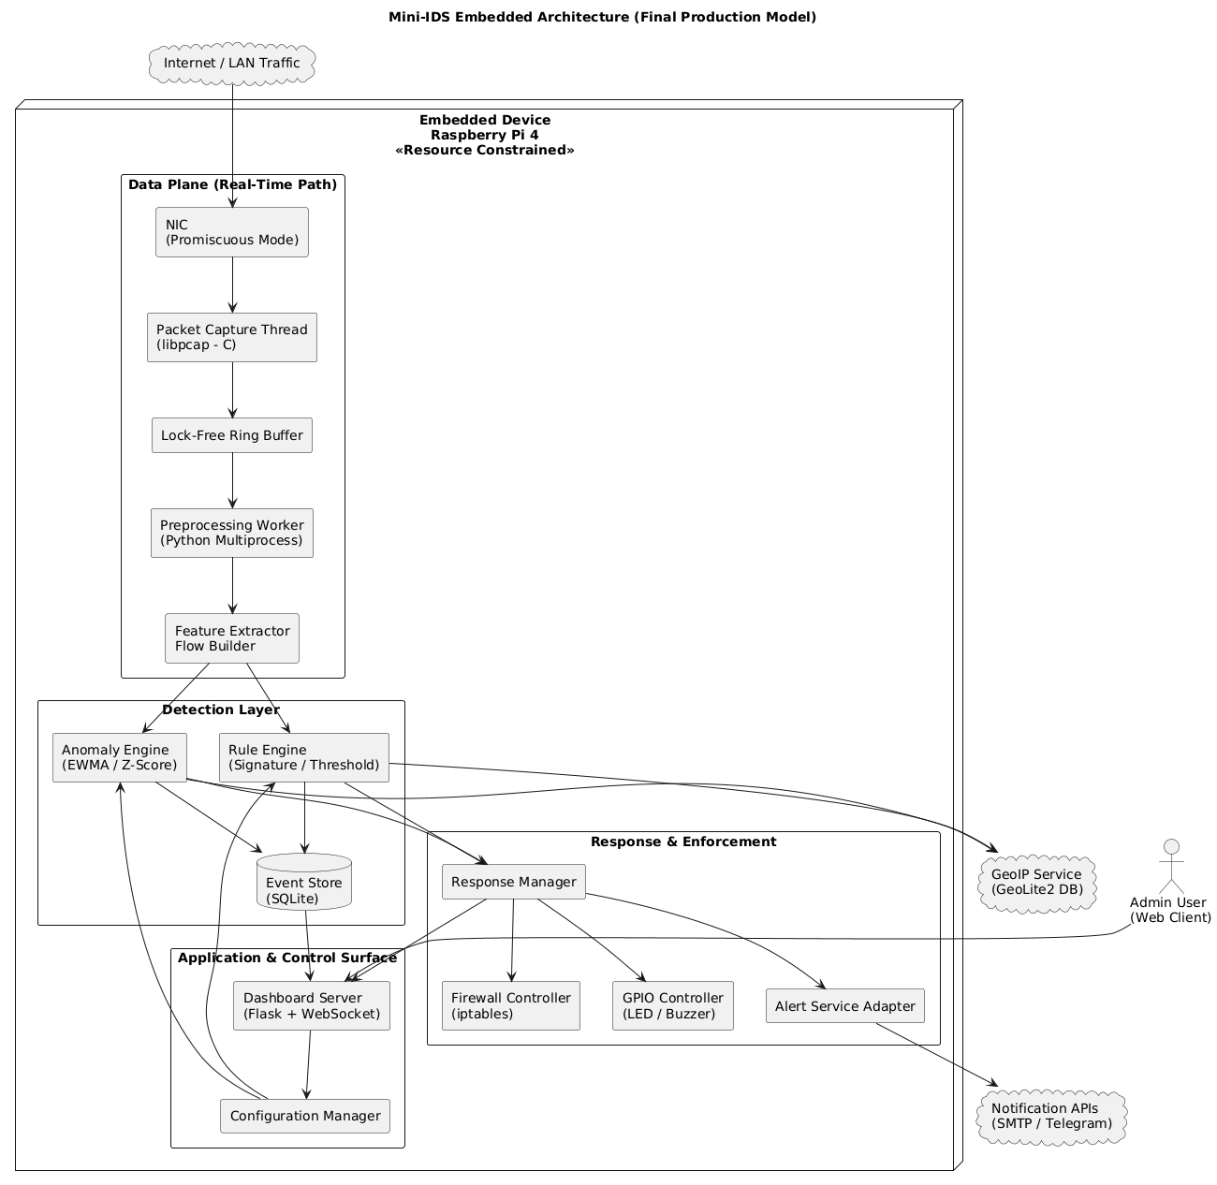
Behavioral Fingerprinting-Augmented Embedded IDS on Raspberry Pi 4 + ESP32. Detects zero-day attacks by learning per-device traffic profiles using Isolation Forest; no signatures needed. Features distributed MQTT nodes, real-time Flask dashboard, iptables auto-blocking, and GPIO alerts.
Highly customizable low-interaction experimental honeypot that mimics specific hosts.
CLI client (and Golang module) for deps.dev API. Free access to dependencies, licenses, advisories, and other critical health and security signals for open source package versions.
25 production-tested defensive security skills for Claude Code - WordPress, VPS, Cloudflare, Next.js hardening, AI agent guardrails, MCP security, prompt injection defense, OWASP LLM Top 10, LLM coding failure modes (slopsquatting, hallucinated APIs, sycophancy), incident response, GDPR/DACH compliance. MIT, battle-tested.
Educational security research notes documenting USB HID (BadUSB/Rubber Ducky) concepts from a defensive perspective. The repository preserves historical filenames while emphasizing detection, prevention, user awareness, and ethical lab use. No payloads, automation scripts, or actionable exploits are provided.
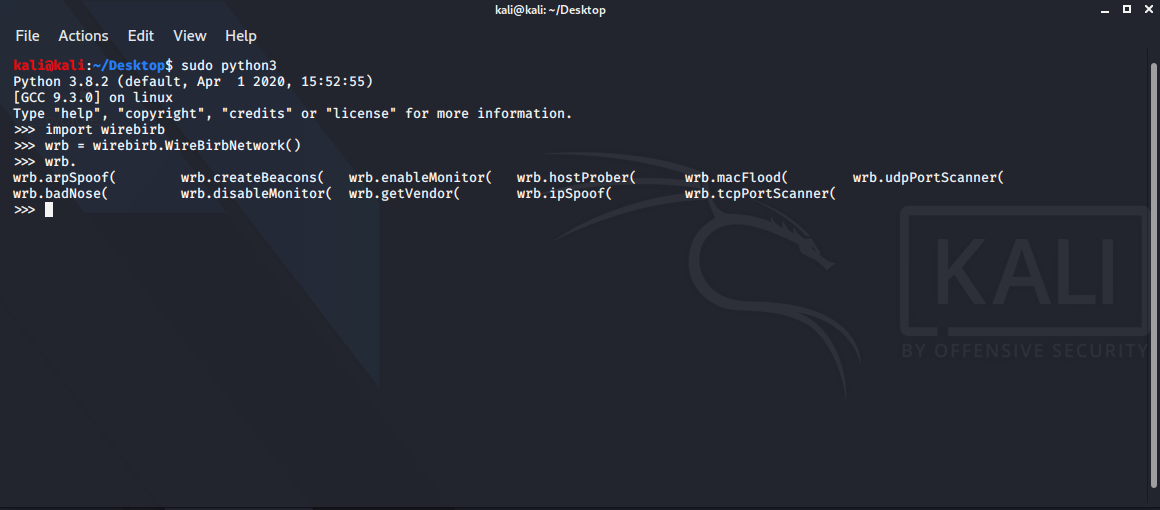
A scapy based module for programming offensive and defensive networking tools easier than before.
The future is Mythos-class agents that take vuln-to-exploits from days to hours, Linux defense is still stuck at human speed. Blacklight is the agentic counter-measure: a skills-native Managed Agent that directs OSS defensive primitives at the speed of the attack. GPL v2. (Opus 4.7 hackathon)
Static is a lightweight, dependency-free typosquatting reconnaissance tool written in pure Python. It generates common typo variations of a target domain and checks them using DNS and HTTP/HTTPS heuristics to identify potentially available domains and redirect behavior.
Image text to text model, used with gguf.
Image text to text model, used with mlx.
Easy-to-use, customizable, high-quality vulnerability management skills for AI agents.
Easy-to-use, customizable, high-quality threat modeling skills for AI agents.
Dork Factory is a cross-platform, interactive command-line tool designed to generate high-quality Google and Yandex dorks for Passive Recon & Discovery.
Prompt injection attack database for defensive AI security research with RAG-powered generation and testing integration
Easy-to-use, customizable, high-quality secure code review skills for AI agents.
Image text to text model, used with gguf.
Limsy is a small command-line tool designed to analyze HTTP rate-limiting behavior of web services and APIs.
CJChecker is a small command-line tool that checks web applications for basic Clickjacking protection by analyzing HTTP response headers.
Portable local AI assistant for offline infrastructure diagnostics using llama.cpp
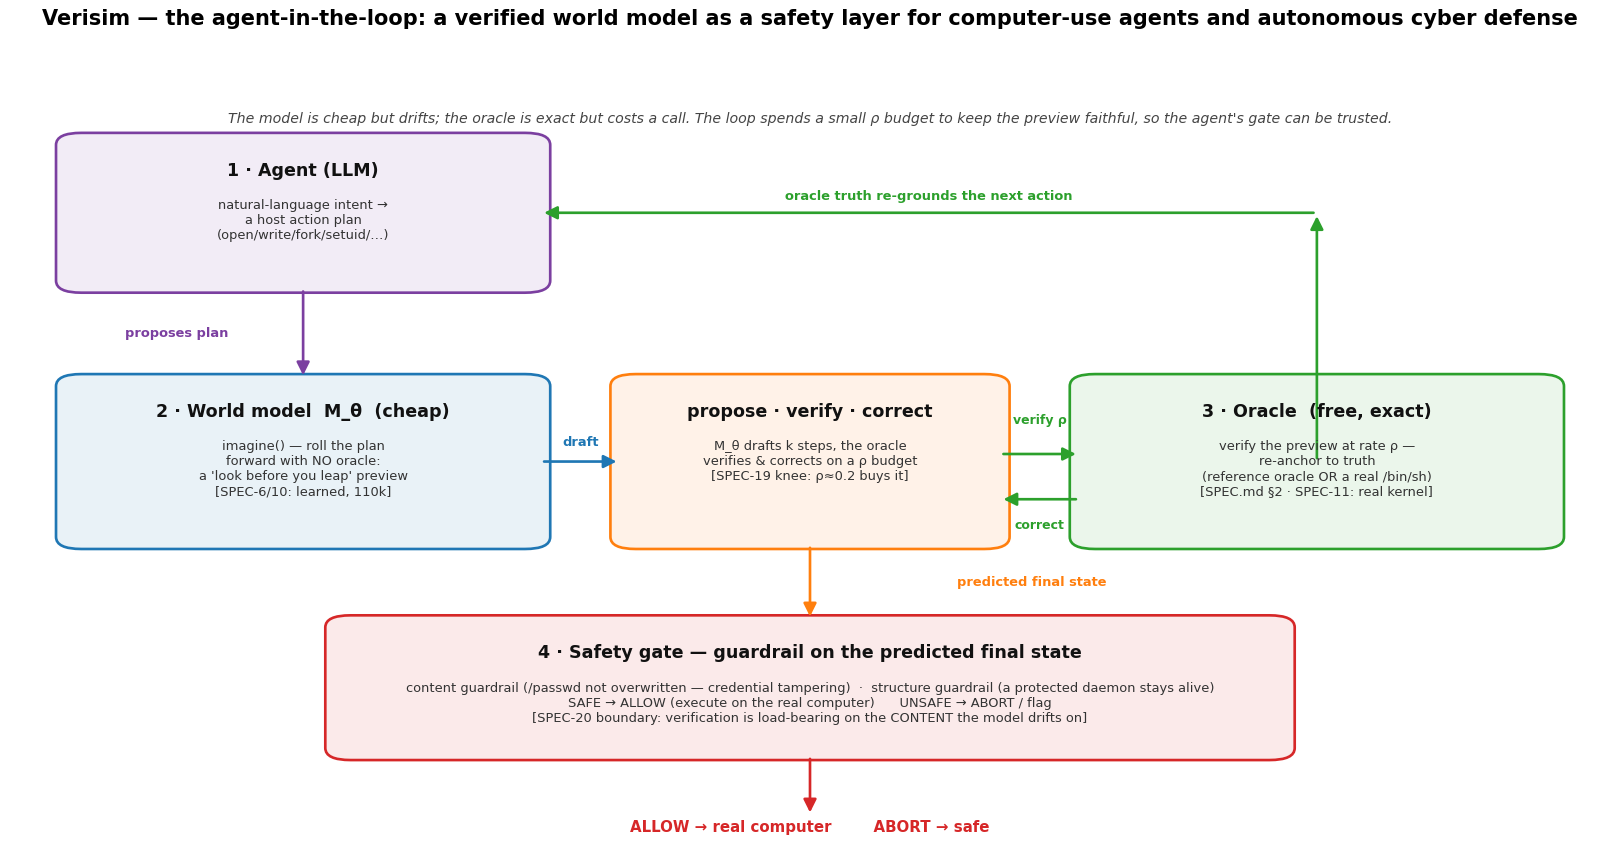
A coverage certifier for AI-agent guardrails: point it at a deployed PreToolUse hook or denylist and it returns the harm-realizing commands it lets through, proven against a real shell, with a certificate.
Thread-origin camouflage: a bounded, enumerable class of ntdll-origin thread-creation primitives on Windows 11 (HTH, RQPDI, static scanner)
Defensive Linux kernel security toolkit for vendor / Android arm64 — known-CVE detection, config hardening, LLM code audit & binary RE. 内核安全检测工具库:六类工具编排 + 一键装依赖 + ksec 三层检测