exploit-code

Open repos and models their makers tagged exploit-code, most starred first. The same for everyone.

DatabasesRepo

Exploit-Index

Exploit-Index : The Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and Threat Intelligence. Replacing manual searches for elite SOC teams, DevSecOps, and Bug Bounty Hunters.

  • 106
  • Python
  • MIT
  • 2 d ago
Websites and appsRepo

CVE-2026-0073-PoC-Exploit

CVE-2026-0073 – Android ADB Wireless Debugging Auth Bypass (CVSS 8.8) | Zero-click TLS type confusion to unauthenticated shell. 2 tools: Full Exploit (ADB shell, cmd exec, subnet scan, mDNS, stealth, SOCKS5) & SafeDetect (non-intrusive audit, CIDR, JSON/CSV/HTML). Red/Blue team toolkit. Ethical & Safety use only.

  • 17
  • Python
  • MIT
  • 22 h ago
tc4dyTake it
GitHubRepo

CVE-2026-87902-Toolkit

CVE-2026-87902 – WordPress Core LFI→RCE Toolkit (CVSS 9.2) - Red/Blue Team suite for WordPress 4.7–7.1.1. | 2 tools: Full Exploit (LFI, PEAR RCE, admin create, webshell, reverse shell, loot, mass scan, stealth) & SafeChecker (version detect, risk audit, JSON report). Use Ethically & Authorized Enviorement, Stay Legal <3

  • 16
  • Python
  • MIT
  • 6 wk ago
tc4dyTake it
GitHubRepo

CVE-2026-67279-86060-Toolkit

CVE-2026-67279 + CVE-2026-86060 – MikroTrick MikroTik RouterOS SSH Pre-Auth Takeover (CVSS 9.2) | Red/Blue Team suite. 2 tools: Full Exploit (rekey bypass, fd-2 policy swap, full-admin shell, plant, mass scan, SOCKS5/Tor, stealth) & SafeDetect (banner/version audit, IoC guidance, JSON/CSV/HTML). Use Ethically & Safety only.

  • 12
  • Python
  • MIT
  • 6 wk ago
tc4dyTake it
GitHubRepo

CVE-2026-121529-Toolkit

CVE-2026-121529 - FortiClient Local API Origin Validation Error (CVSS 9.6). Red/Blue Team suite with 2 tools: Full Exploit (RCE via CORS, browser payload server, interactive shell, mass scan, enum, chain mode, SOCKS5/Tor, stealth) and Safe Verifier (non-intrusive CORS audit, WAF detection, JSON/CSV reports). Use Ethically, Stay Legal.

  • 5
  • Python
  • MIT
  • 8 d ago
tc4dyTake it
GitHubRepo

CVE-2026-6875-PoC-Exploit

CVE-2026-6875 ServiceNow Pre-Auth RCE Framework | JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell, batch threading, WAF bypass, persistence, lateral movement, credential dump, fileless exec, clean tracks. CVSS 9.5 actively exploited. Authorized & Legal use only. Stay Legal.

  • 5
  • Python
  • MIT
  • 6 wk ago
tc4dyTake it
GitHubRepo

CVE-2026-82329-PoC-Exploit

CVE-2026-82329 – JFrog Artifactory Auth Bypass Toolkit (CVSS 9.8) | Red/Blue Team suite for self-hosted Artifactory 7.x (111-161). 2 tools: Full Exploit (JWTforge, admin token, user create, mass scan, stealth, interactive menu, resistence, WAF bypass etc.), SafeChecker (version detect, audit, JSON report). 🦾 Use Ethically, Stay Legal :V

  • 5
  • Python
  • MIT
  • 6 wk ago
tc4dyTake it
GitHubRepo

CVE-2026-85706-PoC-Toolkit

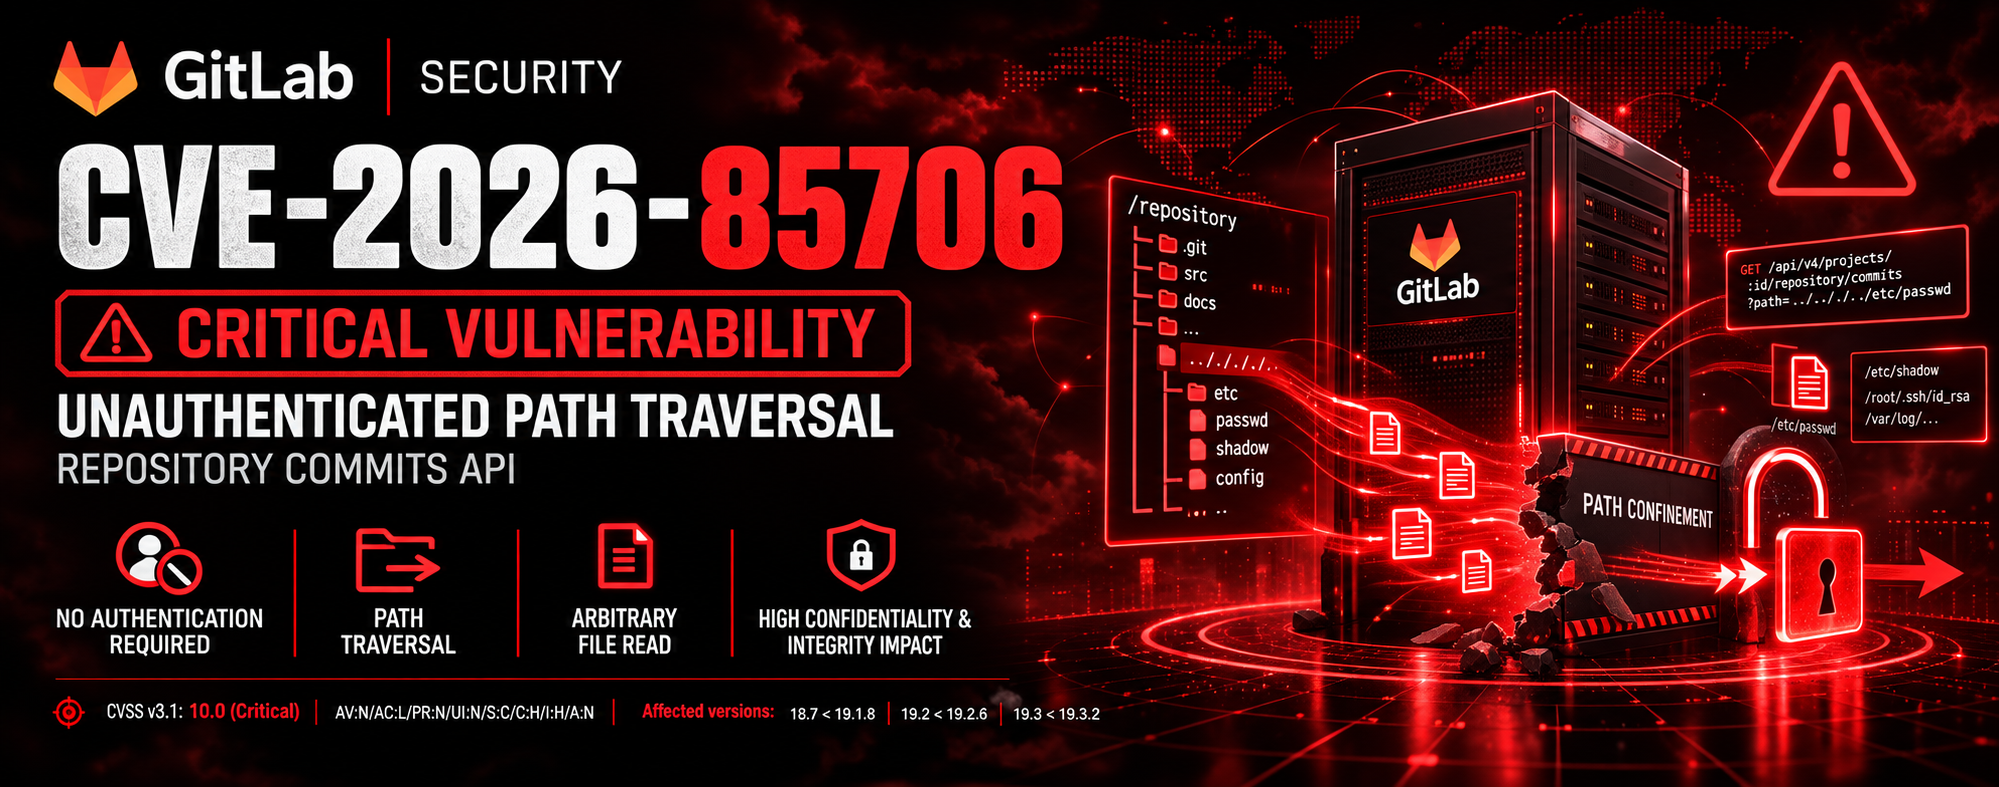
CVE-2026-85706 – GitLab Unauth File Read Toolkit (CVSS 10.0) | Red/Blue Team suite for self-managed GitLab CE/EE 18.7–19.3.1. 2 tools: Full Exploit (unauth file read, admin token, mass scan, loot, shell, stealth, SQLite/HTML/JSON output) etc., SafeChecker (version detect, audit, security headers, TLS check, MITRE). Only Use Ethically, Educ. <3

  • 2
  • Python
  • MIT
  • 6 wk ago
tc4dyTake it
Search GitHub and Hugging Face for exploit-code

Get , open it once and sign in. Then come back here and press the button again.

exploit-code: open source repos and models on Take My Repo