MalwareSourceCode
Collection of malware source code for a variety of platforms in an array of different programming languages.
- 19k
- Assembly
- 6 mo ago
Collection of malware source code for a variety of platforms in an array of different programming languages.
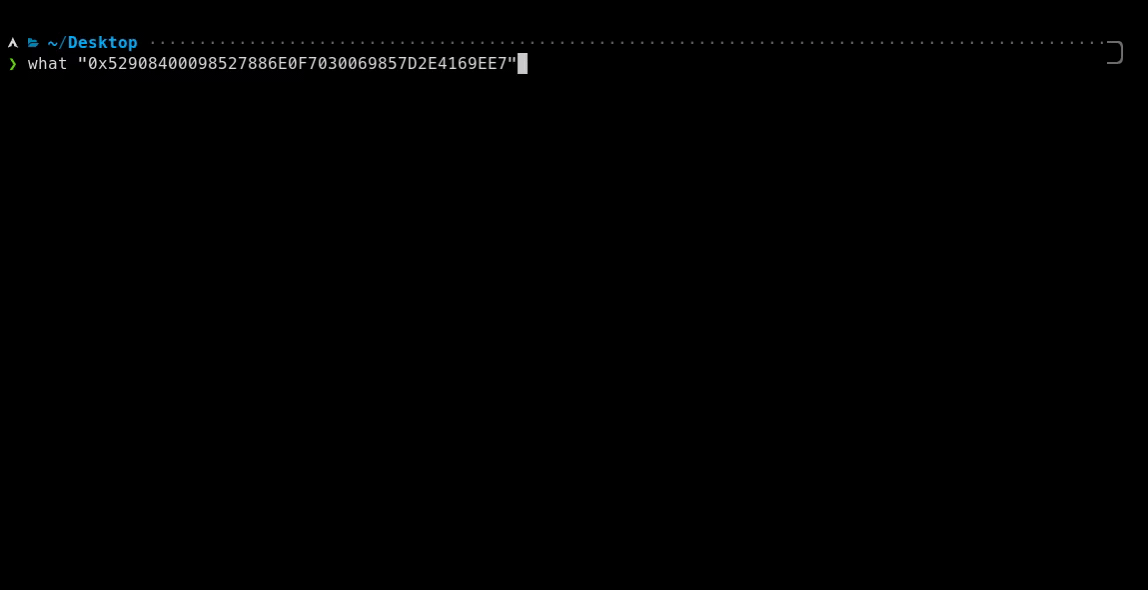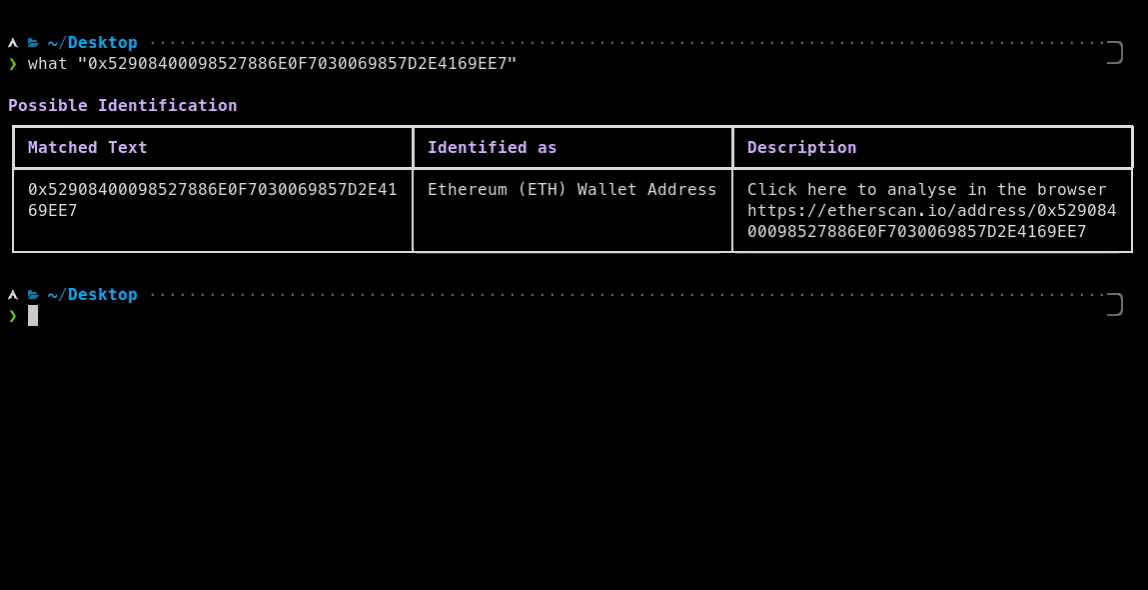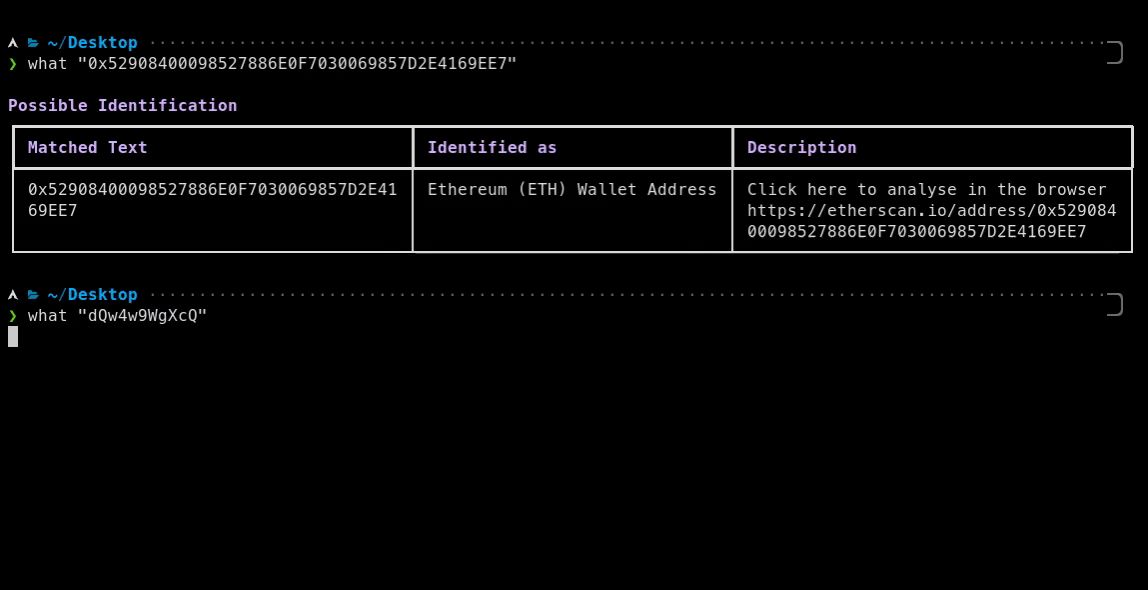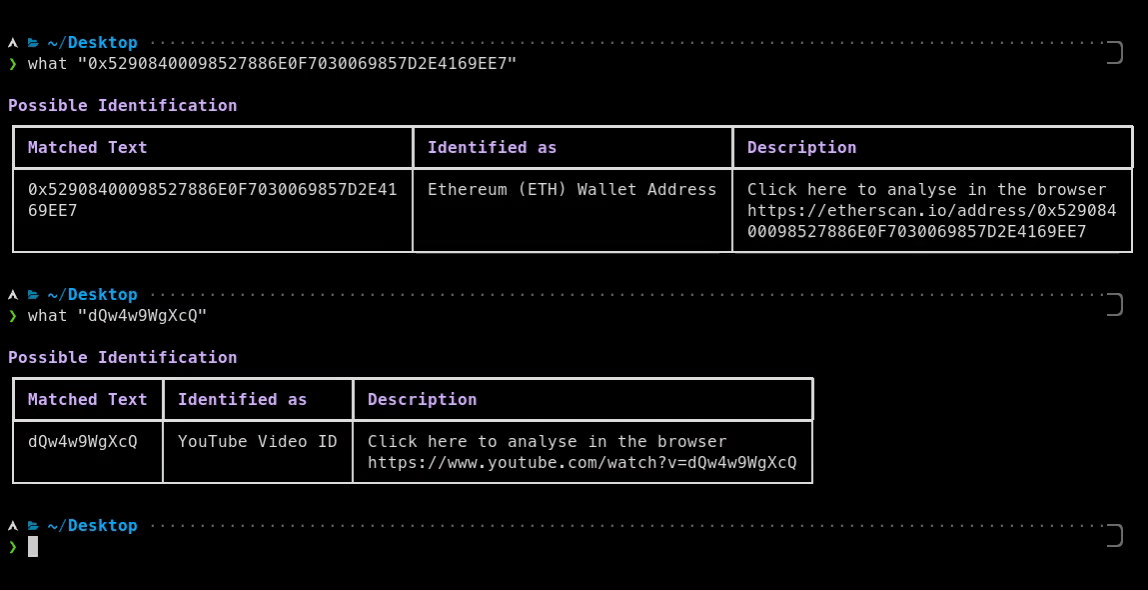
Program for determining types of files for Windows, Linux and MacOS.
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it is! 🧙♀️
x64dbg-MCP Server is a native MCP (Model Context Protocol) plugin for x64dbg that exposes the debugger's full functionality over HTTP. Connect any MCP-compatible AI assistant and control x64dbg programmatically: set breakpoints, step through code, read memory, dump registers, and more. Built with Zig — zero dependencies, single-binary output, cros
🚀🚀 This is a 🎇🔥 REAL WORLD🔥 🎇 Malware Collection I have Compiled & analysed by researchers🔥 to understand more about Malware threats😈, analysis and mitigation🧐.
Free educational courses in cybersecurity, reverse engineering, malware analysis, and programming designed to expand access, build practical skills, and support the next generation of cyber defenders.
"Pre-Owned" malware in ROM for AllWinner H616/H618 & RockChip RK3328 Android TV Boxes
Raw data from Threat Intelligence Reports with automatic reports collection and keyword search across thousands of reports
A Python Bytecode Disassembler helping reverse engineers in dissecting Python binaries by disassembling and analyzing the compiled python byte-code(.pyc) files across all python versions (including Python 3.10.*)
This repository contains analysis scripts, YARA rules, and additional IoCs related to our Telekom Security blog posts.
My projects to understand malware development and detection. Use responsibly. I'm not responsible if you cause unauthorised damage to anyone's system.
This will encrypt 🤐 your files using AES-256-CTR, then RSA-4096😵💫to secure the exchange with the server, or can use the Tor SOCKS5 Proxy😎 -- Functionality is based on Cryptolocker😈 ransomware. Be cool😉
A collection of techniques commonly used in malware to accomplish core tasks.
Parser for a custom executable formats from Hidden Bee and Rhadamanthys malware
Lookup file hashes, domain names and IP addresses using various vendors to assist with triaging potential threats.
Please do not try this at home. Gatherings of malware/ransomware etc. Written in Python and Bash