bettercap
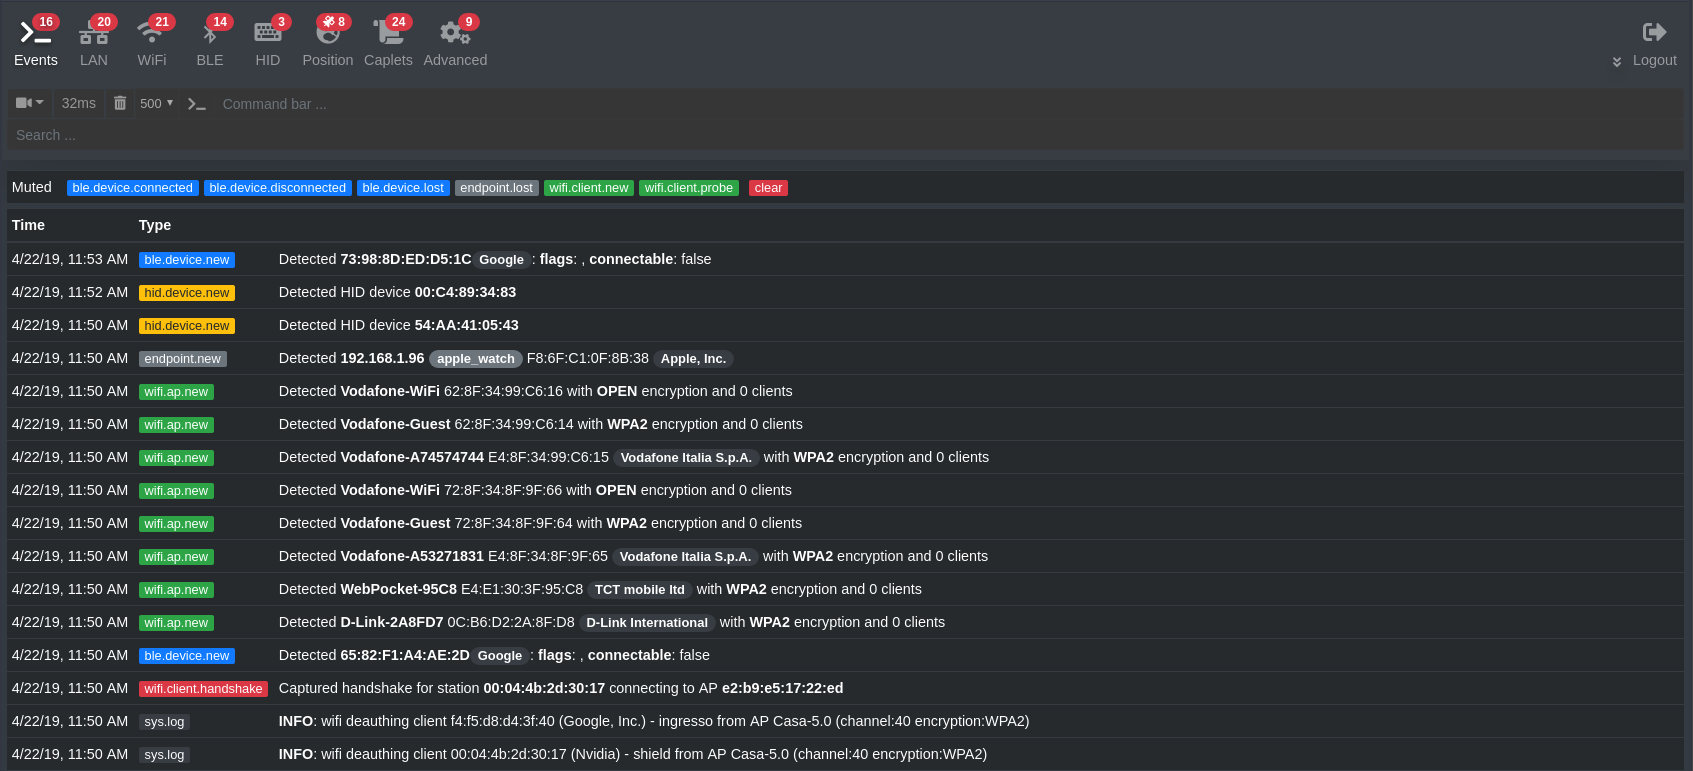
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
- 20k
- Go
- 1 d ago
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
Exploring possibilities of ESP32 platform to attack on nearby Wi-Fi networks.
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
WiFi handshake/PMKID capture firmware for ESP32 — LilyGo T-Embed CC1101, T-Display C5 & Waveshare ESP32-C5-LCD. Cloud cracking (wpa-sec/OnlineHashCrack/PwnCrack) via a hosted relay, a BLE phone console, and a browser USB flasher.