cariddi
Take a list of domains, crawl urls and scan for endpoints, secrets, api keys, file extensions, tokens and more
- 3.8k
- Go
- GPL-3.0
- 1 d ago
Take a list of domains, crawl urls and scan for endpoints, secrets, api keys, file extensions, tokens and more
Secrets Patterns DB: The largest open-source Database for detecting secrets, API keys, passwords, tokens, and more.
Open-source antivirus and firewall for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and skills at runtime.
LLM privacy gateway in Go — millisecond-latency PII and secret redaction. Used in production by PackyCode.
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
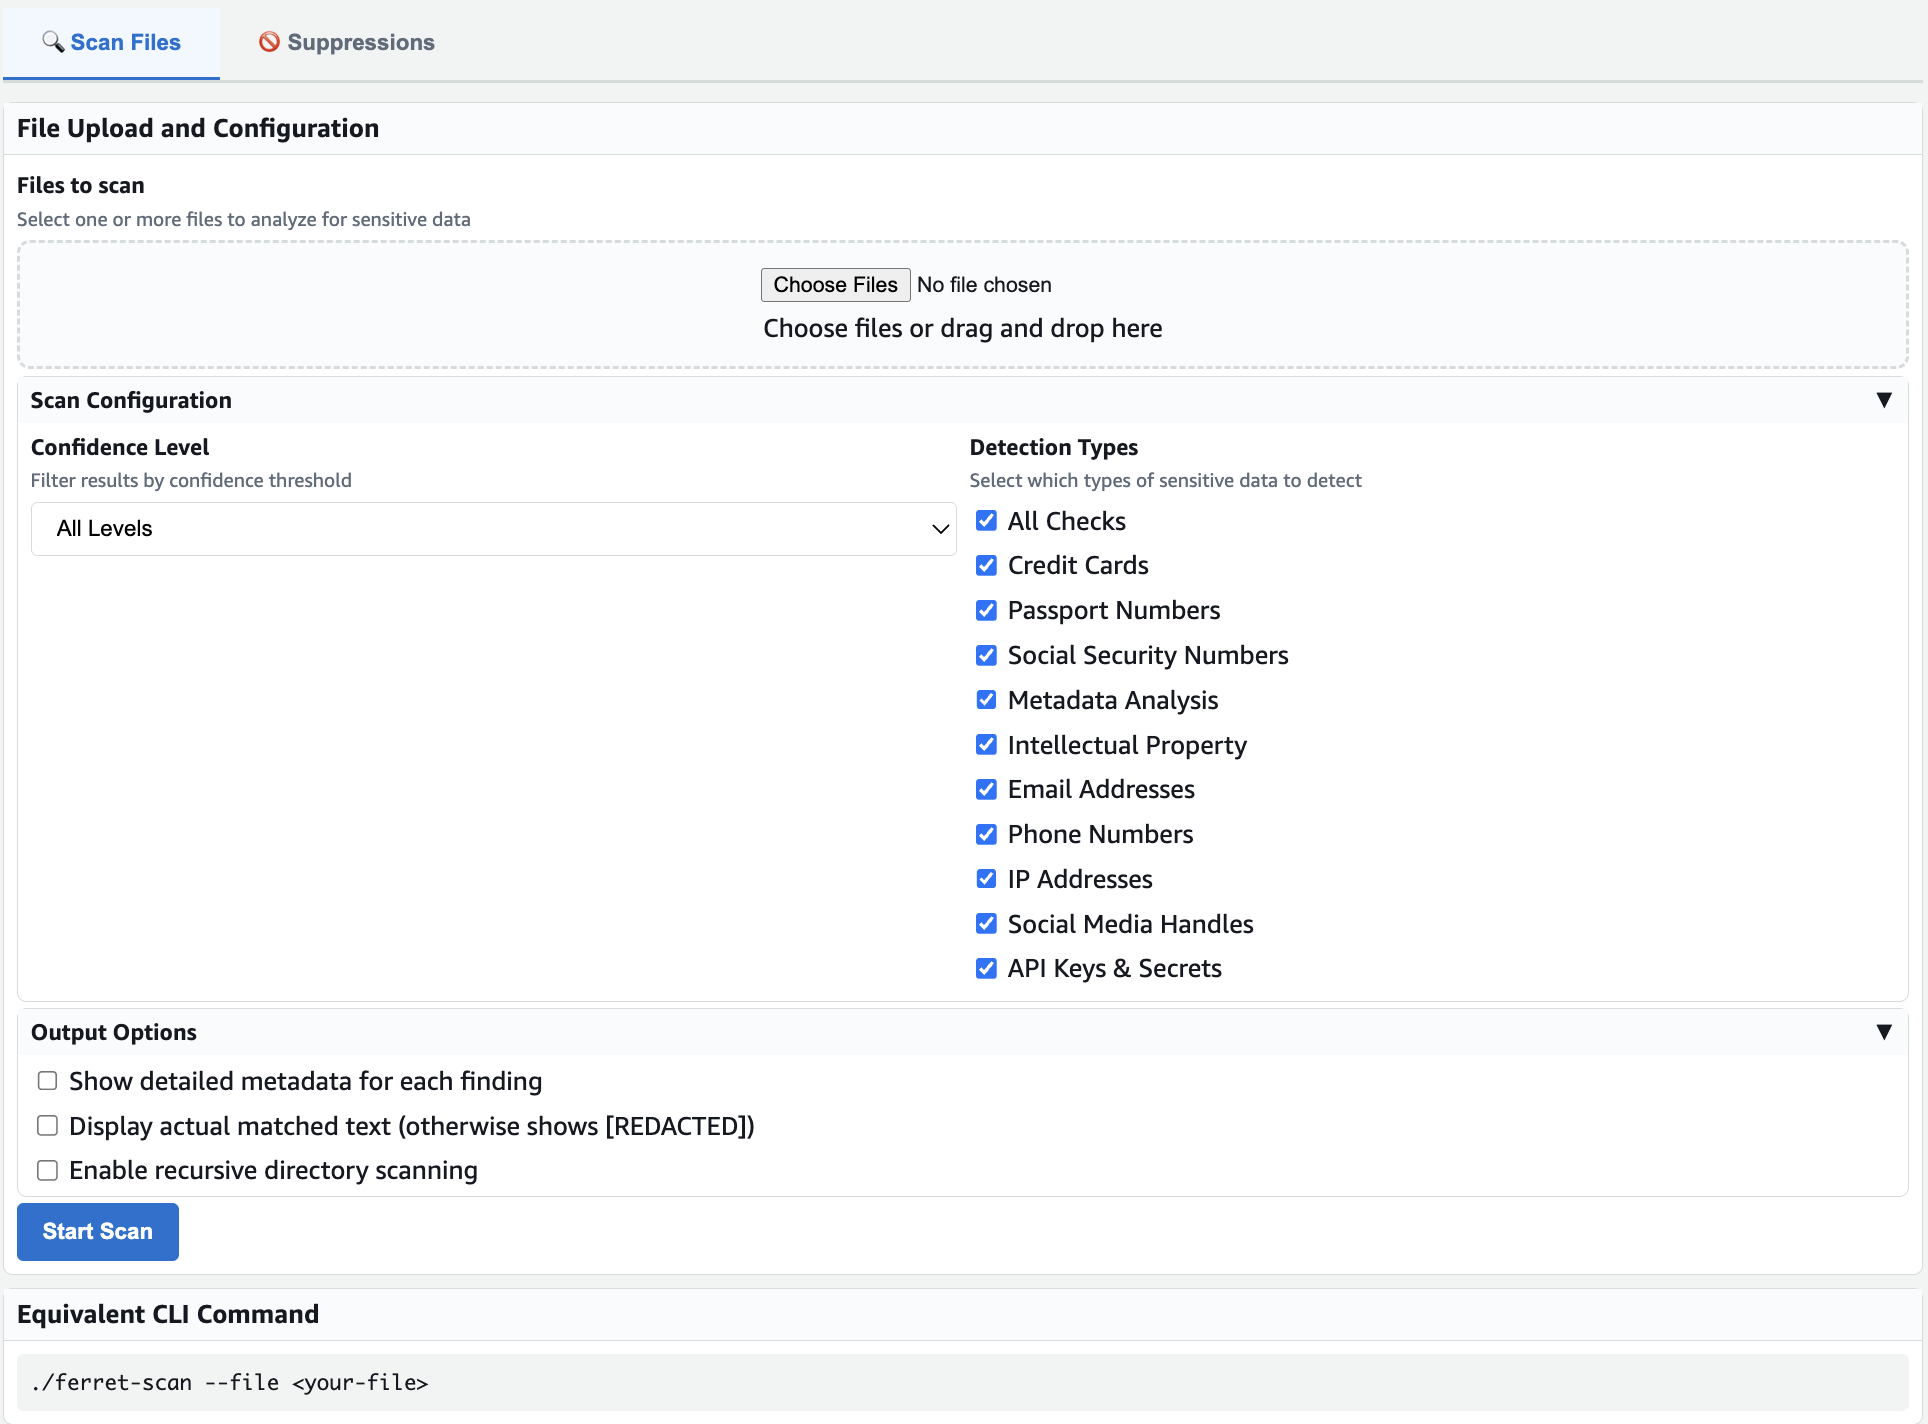
Find and redact sensitive data before it leaks — a fast, offline CLI and Go library that detects PII, secrets, and credentials in files and streams, scores them with context-aware confidence, and redacts them format-preserving. Nothing leaves your host.
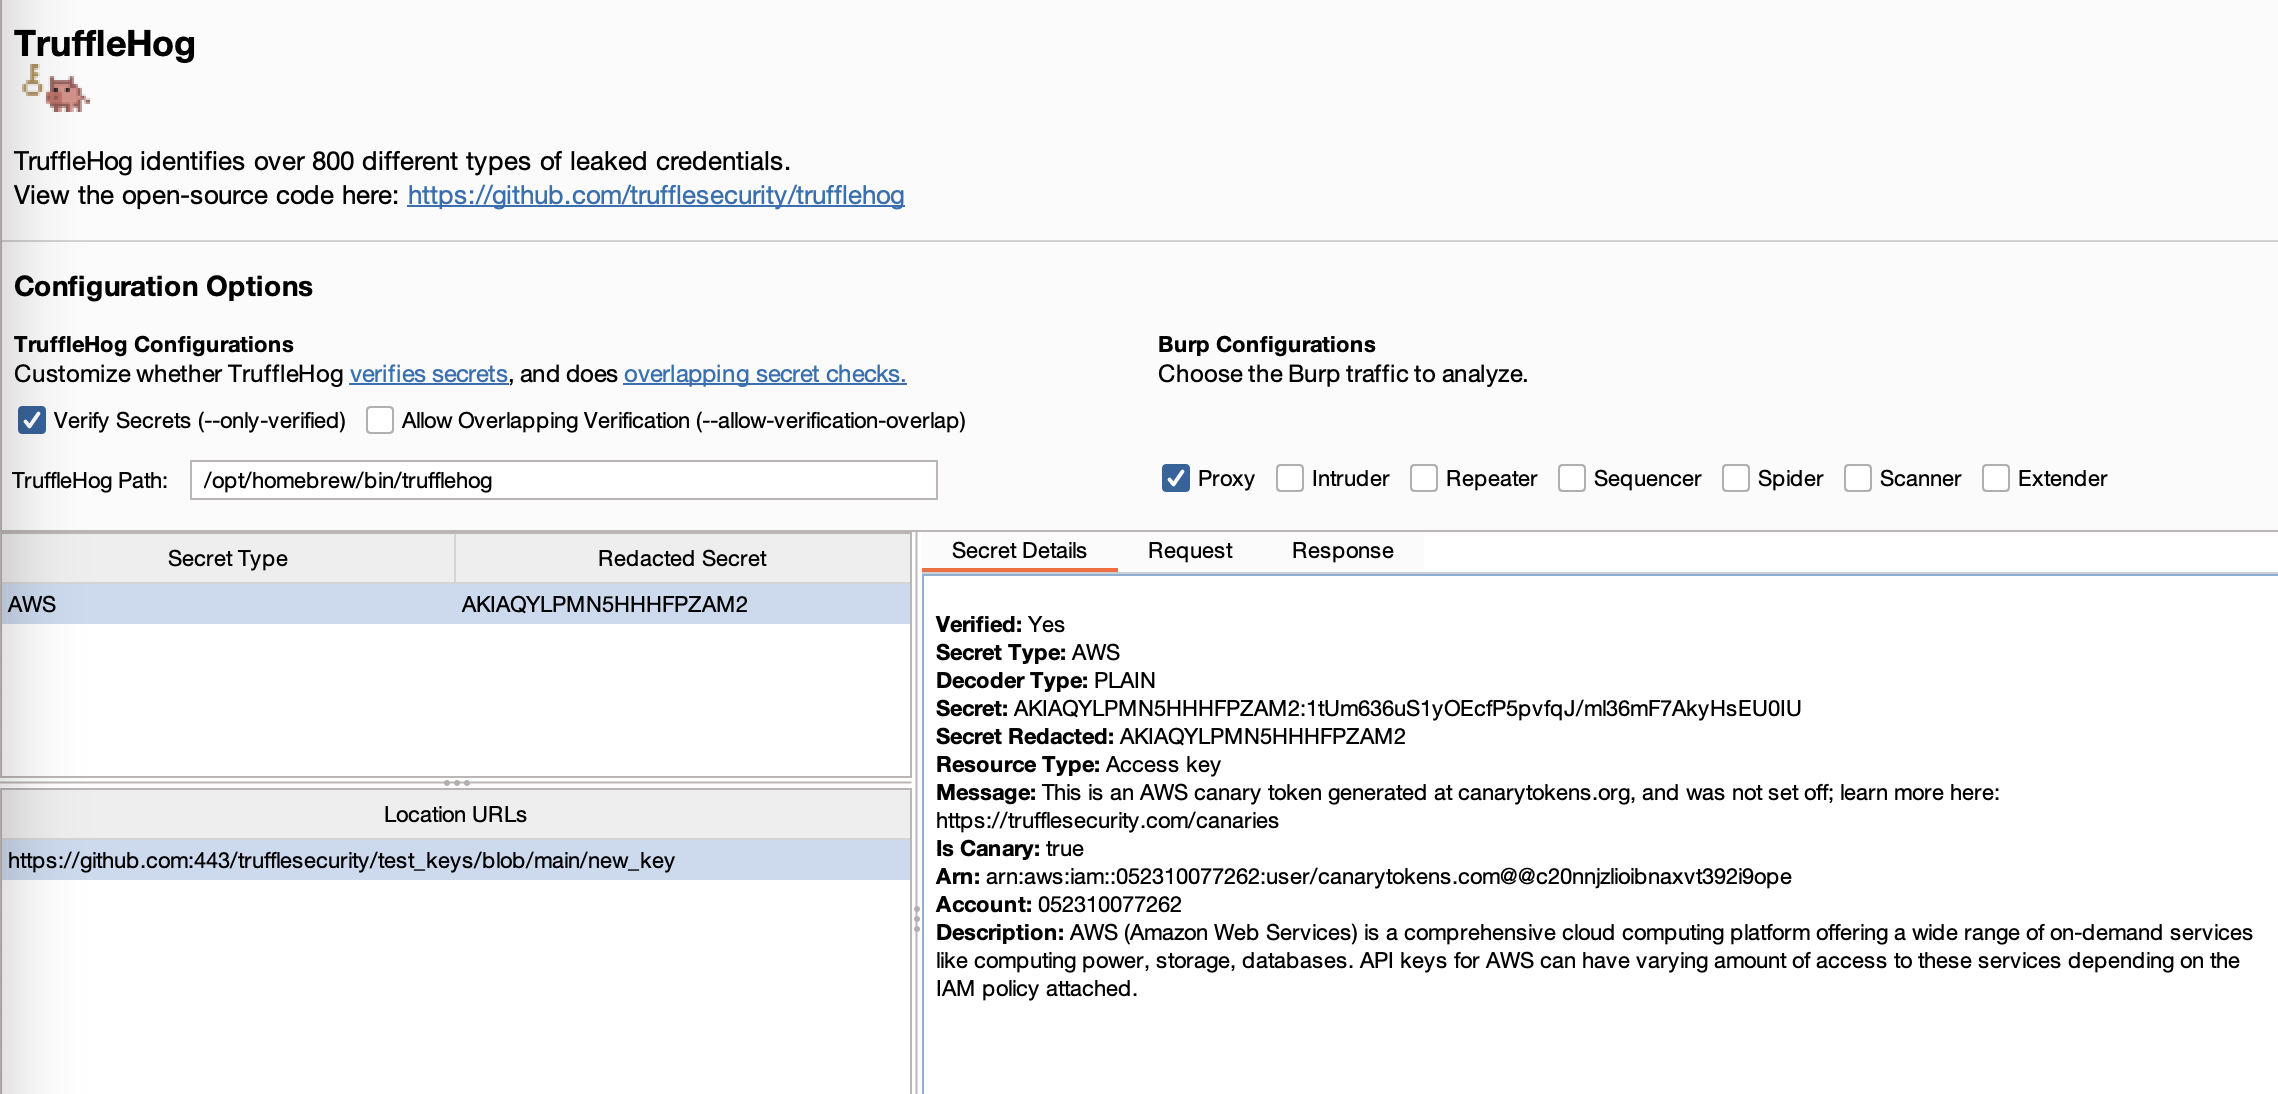
Official TruffleHog Burp Suite Extension. Scan Burp Suite traffic for 800+ different types of secrets (API keys, passwords, SSH keys, etc) using TruffleHog.
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security, vulnerability, insecure infrastructure as code, and potential legal issues with open source licenses.
🛡️ Claude Code plugin that blocks prompts containing secrets, API keys, and PII before they reach Claude.
An enterprise-grade, agentless, and open-source cloud security platform for AWS, GCP, and Azure that combines CSPM, DSPM, CIEM, ASM, and vulnerability management with deterministic YAML policies and natural language querying.
A tiny Go library to detect and redact API tokens, cloud credentials, and other secret material in arbitrary text.
Catch .env secrets leaking into git: a pre-commit hook and CLI that fails when an API key or any value of your env files is staged, tracked or anywhere in the history. Your real values, not patterns.
A Python-powered reconnaissance tool that hunts exposed secrets, leaked credentials, and sensitive endpoints in web applications.
Gateway engine for Claude Code, Codex and other AI clients, inside ThinkWatch Lite or on a Linux server: credential redaction, tool-call inspection, rule-based routing, per-request cost. Rust, MIT.
MCP server detecting leaked secrets/credentials (32+ provider rules). In the official MCP Registry: io.github.eltociear/secrets-audit-mcp. Pure stdlib, zero deps.
Deterministic content guardrails for LLM and agent applications. Prompt injection in the encoding, PII, secrets and your own rules, with published precision and recall and provenance on every decision.
Mask secrets & PII in logs, .env, JSON & HAR, in-browser
Runs in the browser on Hugging Face
Redact API keys, PII & faces in screenshots, in-browser
Runs in the browser on Hugging Face
Redact keys, names & faces in screen recordings
Runs in the browser on Hugging Face
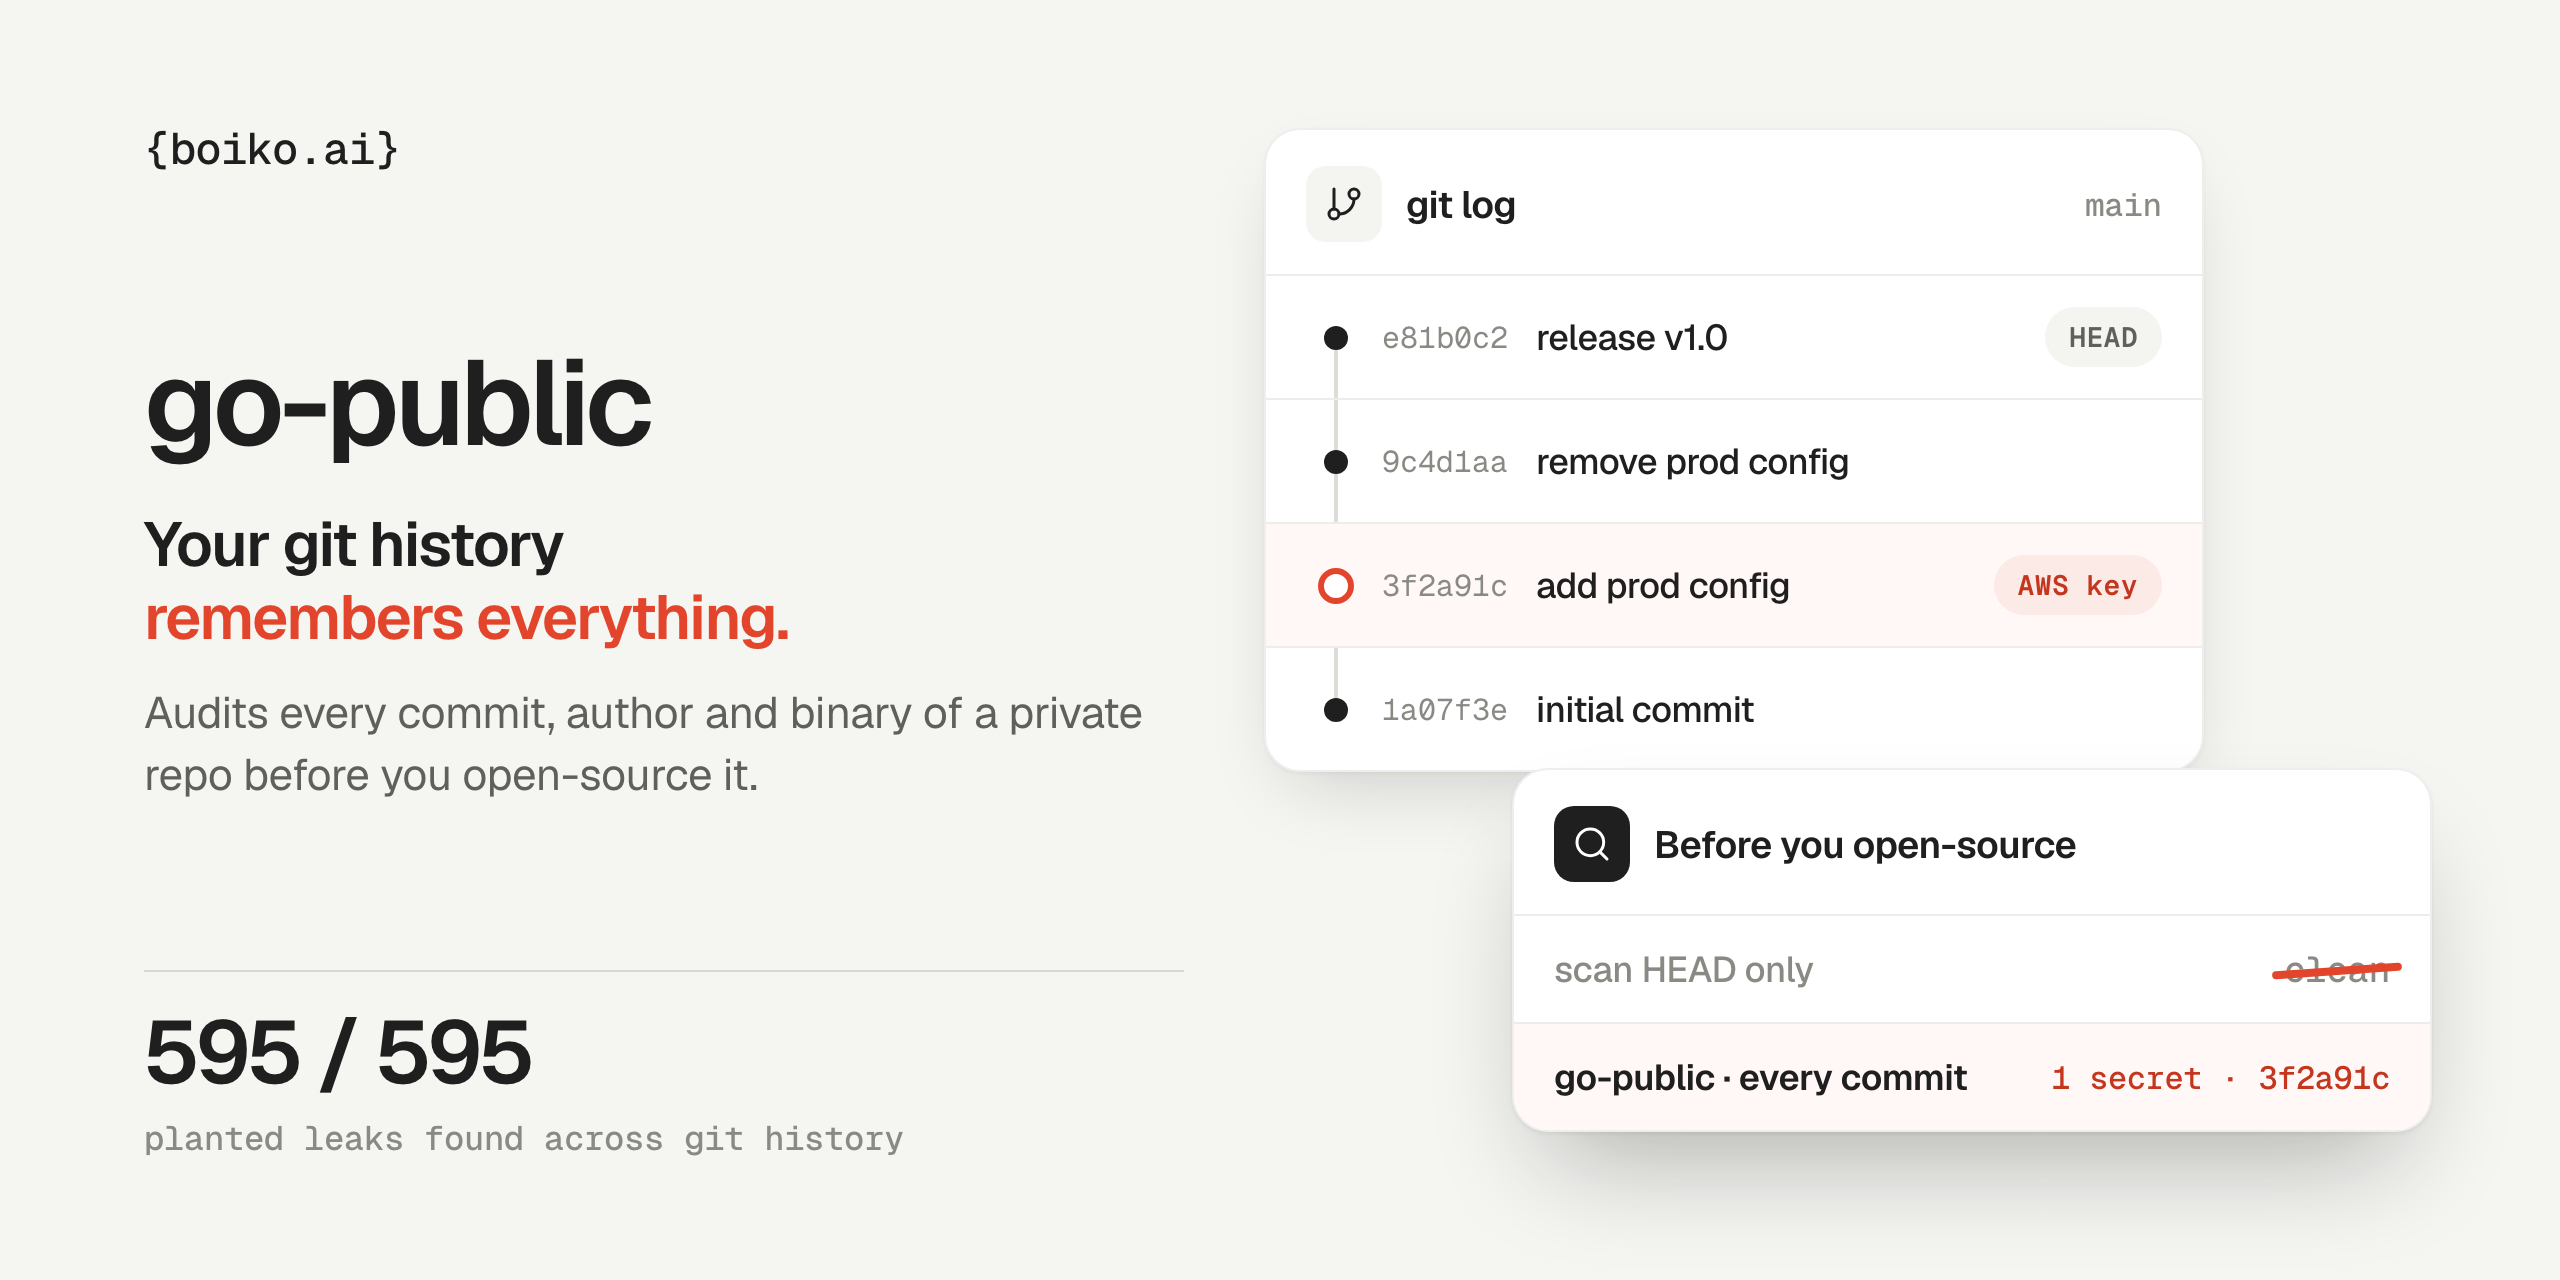
Audit a private git repo before you open-source it: scans every ref, commit, message, author and binary for secrets, personal data, organisation identifiers, local paths, file metadata and licence history, then writes a clean export and re-scans it. CLI and Claude Code plugin.
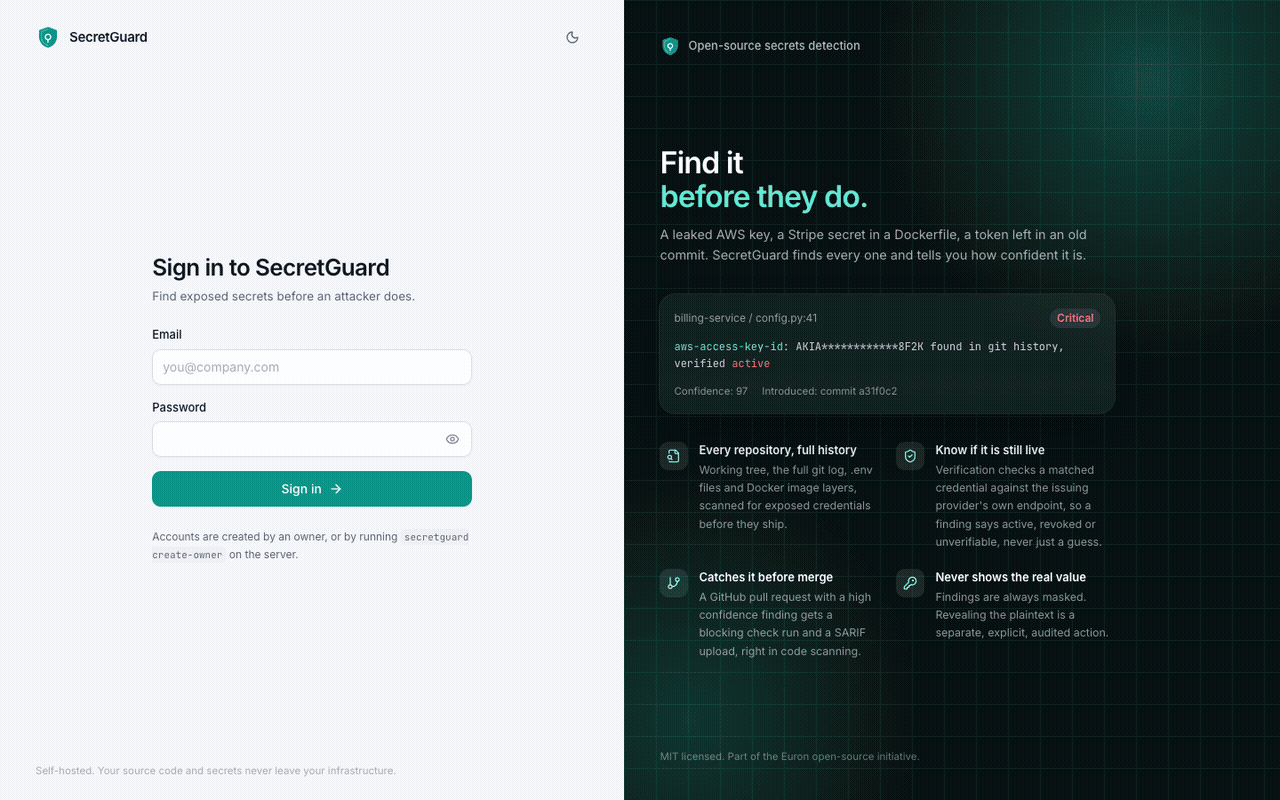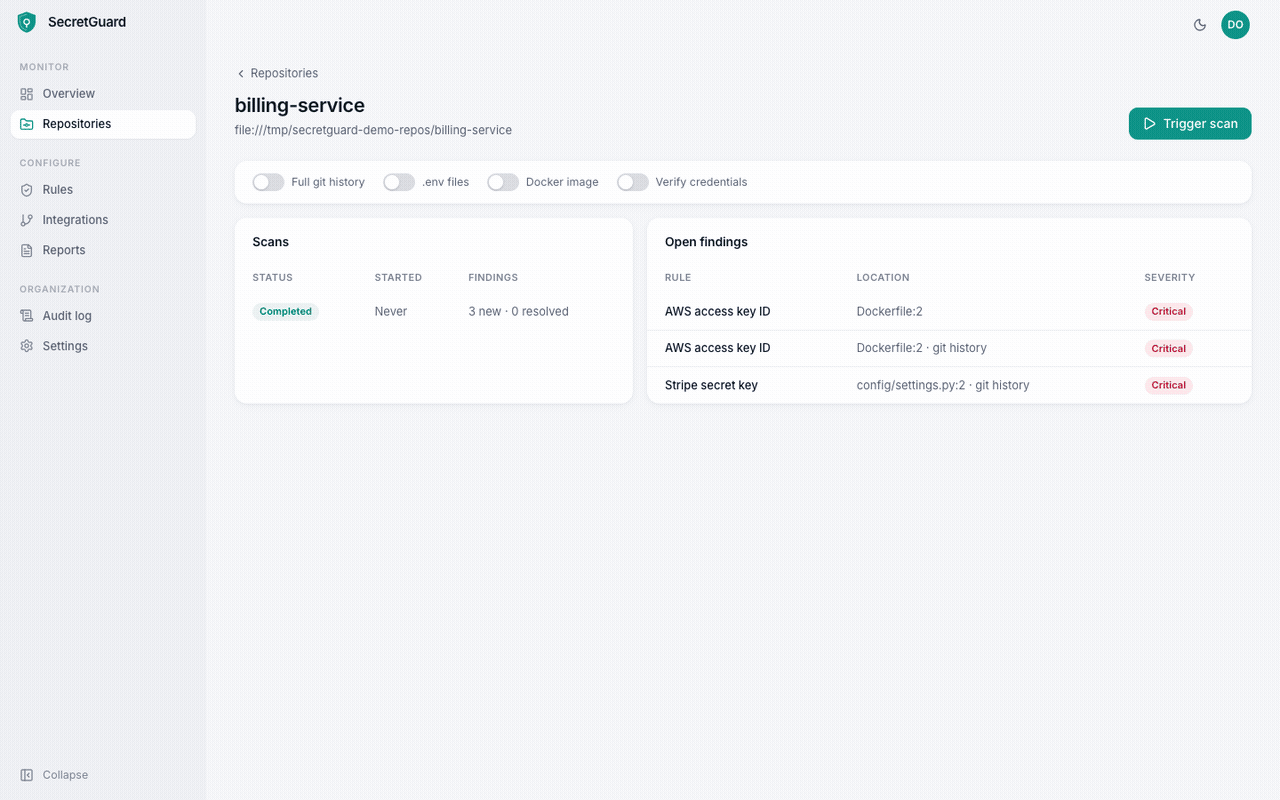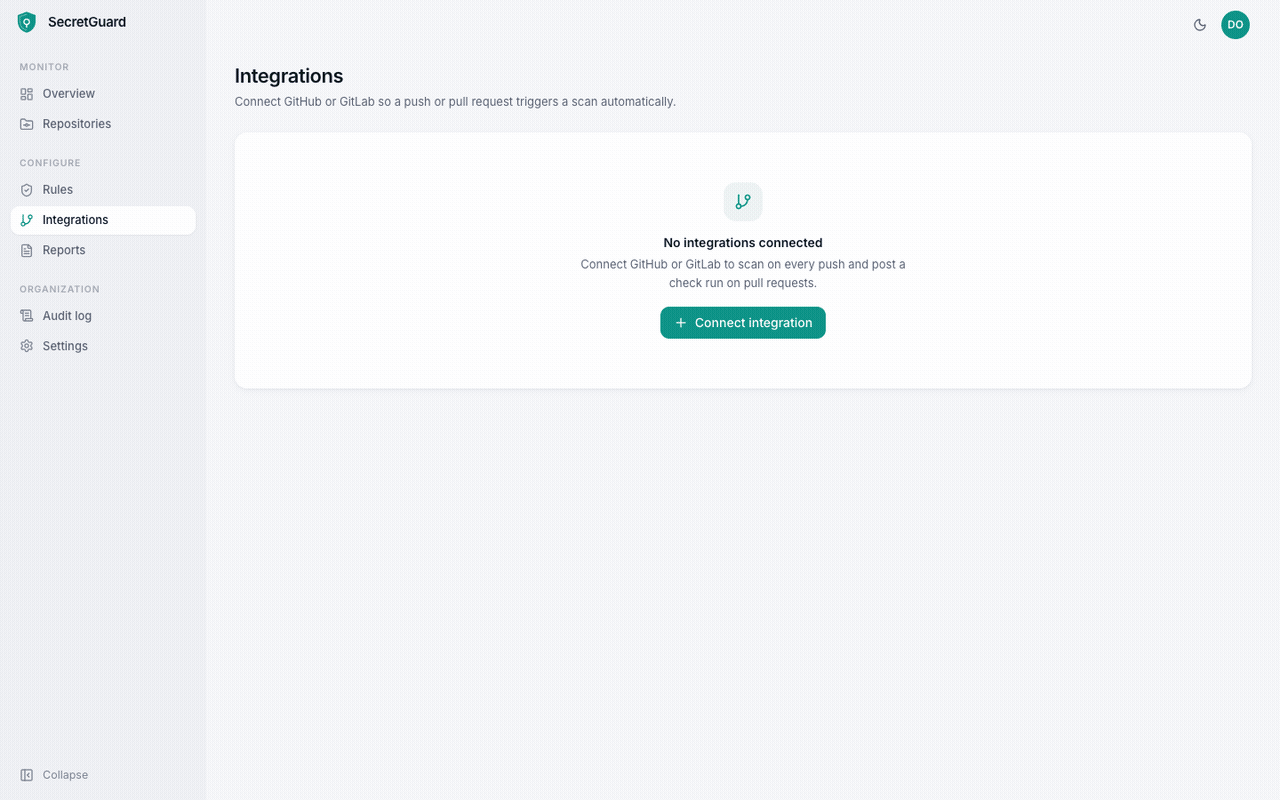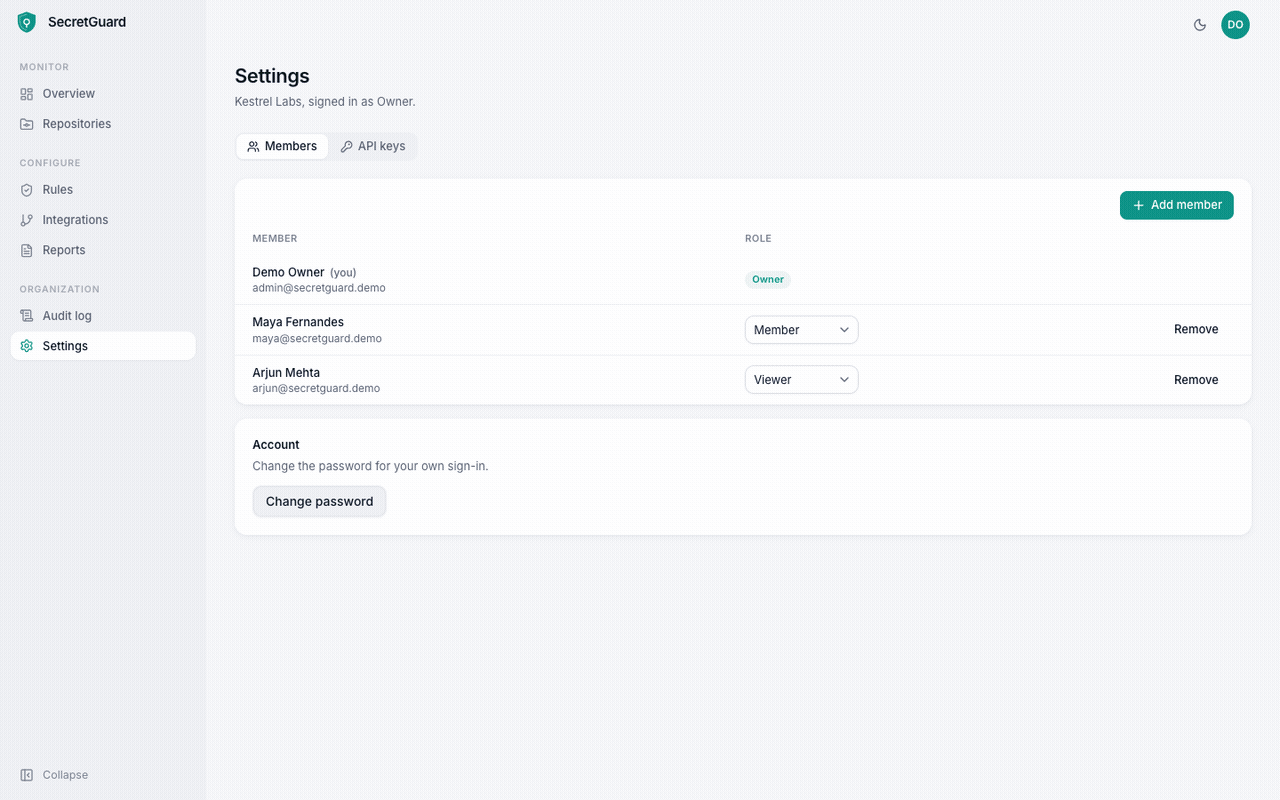
Self-hosted secrets detection: scan source, git history, env files and Docker images for exposed credentials before an attacker finds them
Claude Code hook that blocks secrets, passwords and API keys before your AI agent writes, commits or sends them. Known keys caught locally; unknown ones judged by Jev (TypeSafe), masked.