burpsuite


IntruderPayloads
A collection of Burpsuite Intruder payloads, BurpBounty payloads, fuzz lists, malicious file uploads and web pentesting methodologies and checklists.
- 4k
- BlitzBasic
- 5 y ago

Ethical-Hacking-Tools
Complete Listing and Usage of Tools used for Ethical Hacking
- 2.2k
- Apache-2.0
- 5 wk ago

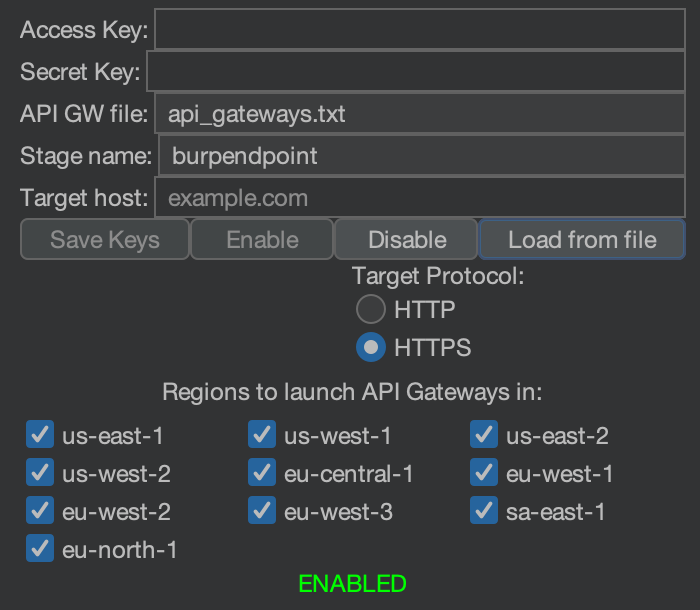
IPRotate_Burp_Extension
Extension for Burp Suite which uses AWS API Gateway to rotate your IP on every request.
- 897
- Python
- 9 mo ago


vulnrepo
VULNRΞPO - Free vulnerability report generator and repository, end-to-end encrypted! Templates of issues, CWE,CVE,MITRE ATT&CK,PCI DSS, import Nmap/Nessus/Burp/OpenVAS/Bugcrowd/Trivy, Jira export, TXT/JSON/MARKDOWN/HTML/DOCX, attachments, automatic changelog, stats, vulnerability management, bugbounty, local ai/llm, super fast pentest reporting!
- 587
- TypeScript
- Apache-2.0
- 8 h ago


burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application Security Testing (DAST).
- 533
- Python
- GPL-3.0
- 8 y ago


knary
A simple HTTP(S) and DNS Canary bot with Slack/Discord/MS Teams/Lark/Telegram & Pushover support
- 305
- Go
- GPL-3.0
- 3 wk ago

pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
- 229
- 2 y ago


Minesweeper
A Burpsuite plugin (BApp) to aid in the detection of scripts being loaded from over 23000 malicious cryptocurrency mining domains (cryptojacking).
- 204
- Python
- GPL-3.0
- 5 y ago

Proxer
A modern HTTP and HTTPS interception proxy with custom-made extensions support.
- 135
- TypeScript
- 5 mo ago

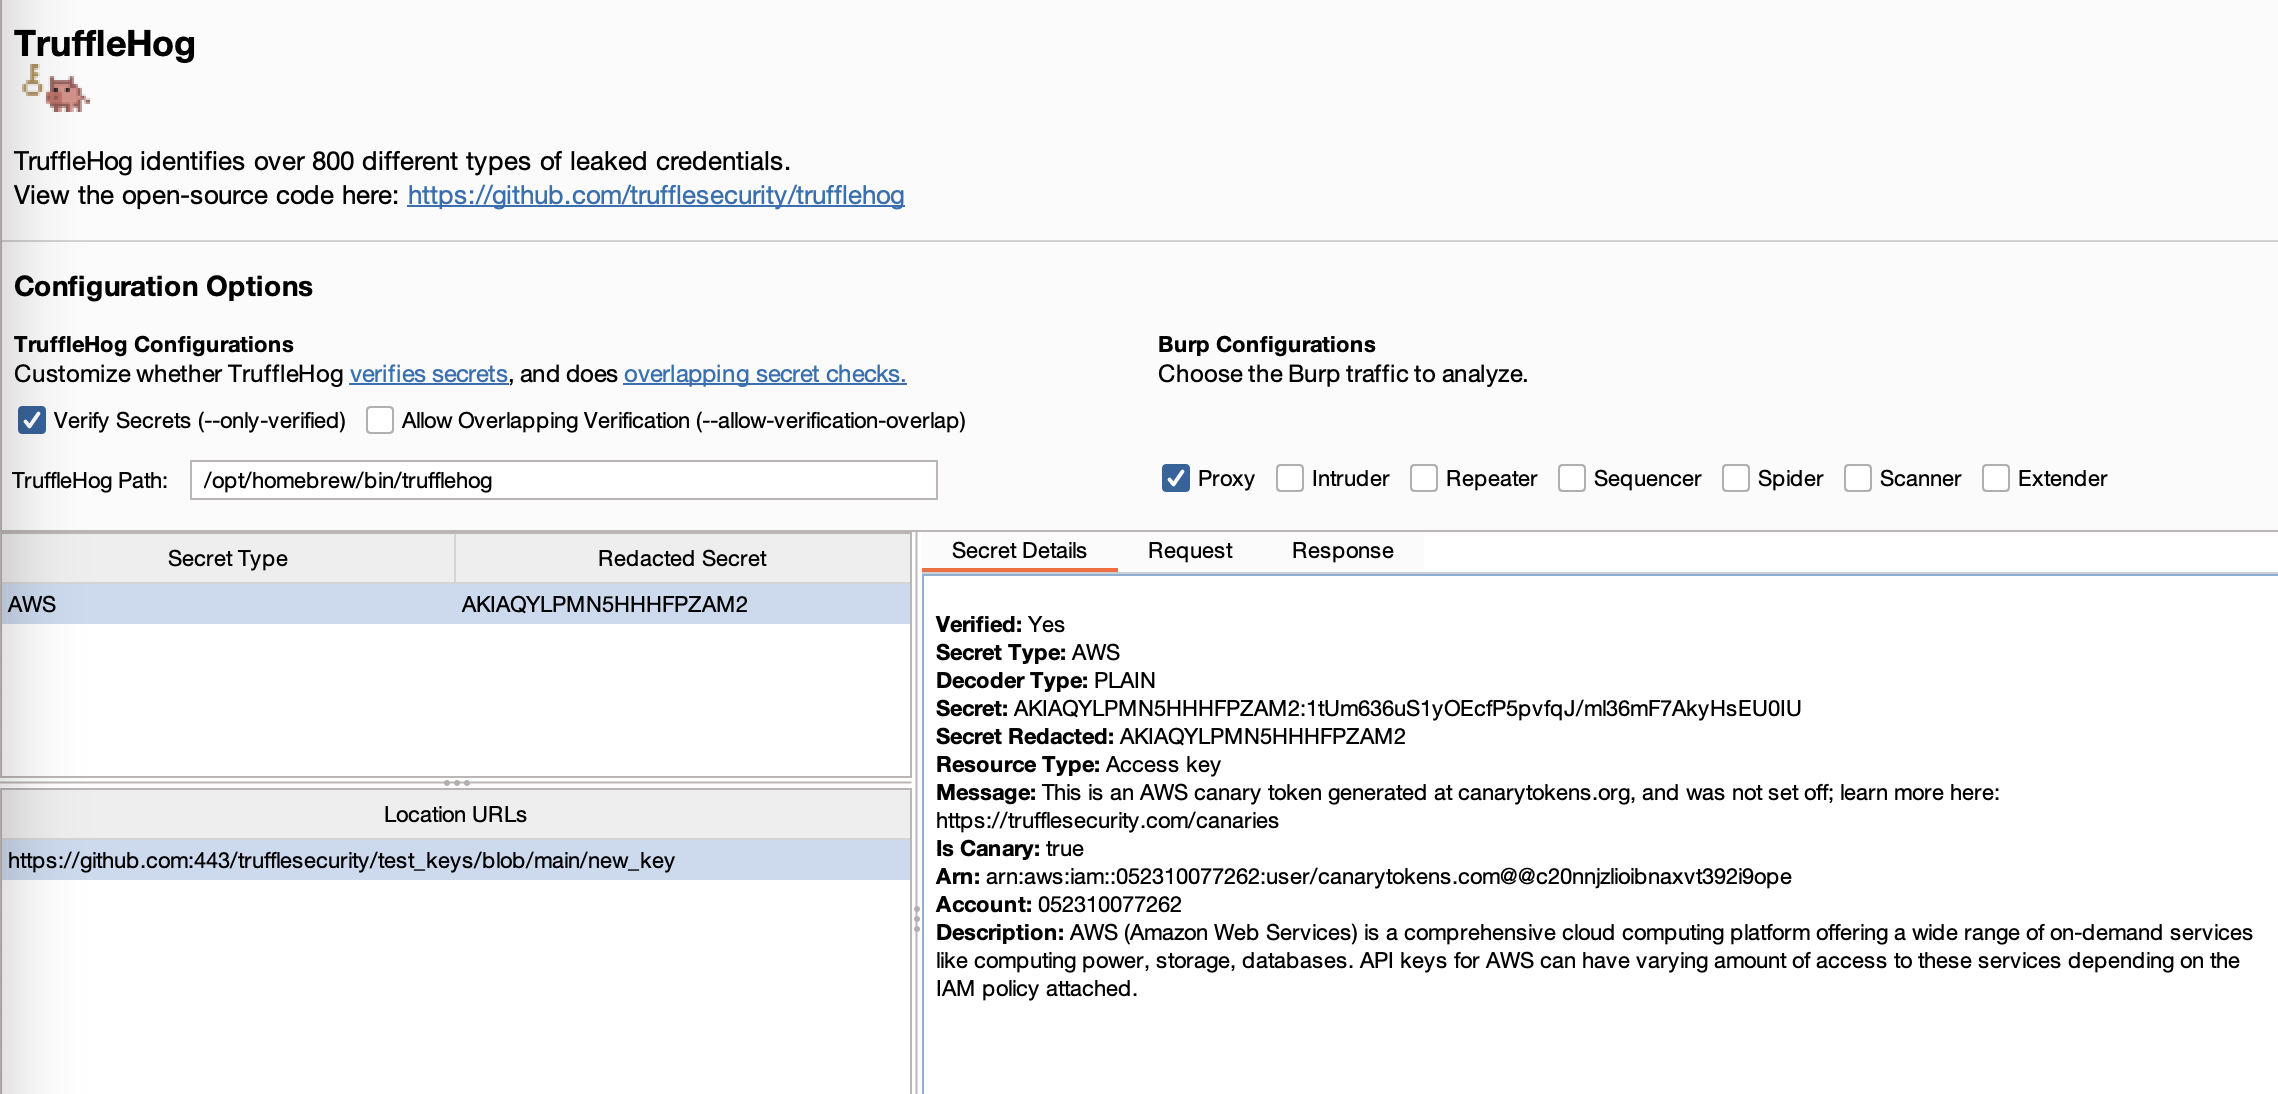
trufflehog-burp-suite-extension
Official TruffleHog Burp Suite Extension. Scan Burp Suite traffic for 800+ different types of secrets (API keys, passwords, SSH keys, etc) using TruffleHog.
- 103
- Python
- 21 mo ago

custom-bcheck-scan
This repository stores some of my custom BCheck Scan configurations. Its goal is to identify intriguing elements that warrant further manual testing.
- 103
- 3 y ago

RepeaterSearch
This extension adds a search bar to the Repeater tab that can be used to highlight all repeater tabs where the request and/or response matches a query via simple text matching or Regex.
- 79
- Java
- 3 y ago


Bookmarks
Reclaim control of your Burp Suite Repeater tabs with this powerful extension
- 69
- Kotlin
- MIT
- 5 mo ago


pivoting-tunneling-lab
Compromise a web application and delve deeper into the network to access hosts that you cannot directly reach from your attack host using different approaches.
- 28
- JavaScript
- 3 y ago

BurpSuiteAutoRepeaterNaming
This extension replaces the default repeater tab name with the URL path of the repeater request.
- 25
- Java
- 5 y ago
Android-SSL-Pinning-Bypass
Bypass Instagram / Meta SSL pinning on Android for HTTPS inspection - Frida (Tigon) + APK patcher (gadget, network-security-config, xapk/apkm merge). Latest tested Instagram v455.0.0.0.56 & v444.0.0.0.77 & v442.0.0.0.61
- 16
- Python
- 12 d ago

practical-ethical-hacking-course
Comprehensive notes from a hands-on course covering networking, Linux, Python, Metasploit, Burp Suite, Active Directory, and web application penetration testing.
- 16
- Python
- 2 y ago


DOM-XSS-in-innerHTML-sink-using-source-location.search-BurpSuite-Lab
DOM-based XSS flaw where location.search is injected into the page via innerHTML, letting us execute arbitrary JavaScript.
- 11
- MIT
- 12 mo ago

DOM-XSS-in-document.write-sink-using-source-location.search-BurpSuite-Lab
DOM-based XSS where location.search is written into the page via innerHTML, letting us inject HTML and trigger alert(1) using an SVG onload payload.
- 11
- MIT
- 12 mo ago
BurpSuite-Lab-SQL-injection-UNION-attack-retrieving-multiple-values-in-a-single-column
UNION-based SQLi PoC where we enumerate tables, extract usernames and passwords from the users table using string concatenation, and log in as the administrator to solve the lab.
- 11
- MIT
- 12 mo ago
Reflected-XSS-into-HTML-context-with-nothing-encoded
Simple reflected XSS vulnerability where unencoded HTML context allows direct JavaScript execution via a <script> payload.
- 11
- MIT
- 12 mo ago
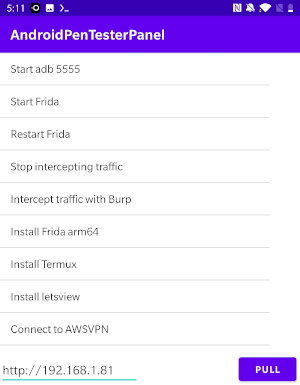
Android-Tester-Panel-App
It provides configurable shortcuts to help make the pre-qual/testing process more efficient.
- 11
- Java
- 4 y ago

DOM-XSS-in-jQuery-anchor-href-attribute-sink-using-location.search-source
DOM XSS in jQuery anchor href attribute sink using location.search source
- 10
- MIT
- 12 mo ago
BurpSuite-Lab-SQL-injection-UNION-attack-retrieving-data-from-other-tables
UNION-based SQLi to enumerate tables, dump usernames/passwords from the users table, and log in as the administrator.
- 10
- MIT
- 12 mo ago
Blind-SQL-injection-with-conditional-responses-BurpSuite-Lab
Blind SQL injection exploiting Welcome back responses to extract the administrator’s password using boolean conditions and substring-based brute-forcing.
- 10
- Python
- MIT
- 12 mo ago
BurpSuite-Lab-SQL-injection-UNION-attack-finding-a-column-containing-text
Finding which column accepts string data using a UNION-based SQL injection on the product category filter to display the lab’s provided value.
- 10
- MIT
- 12 mo ago
SQL-injection-attack-listing-the-database-contents-on-Oracle
A clean Oracle-based UNION SQLi walkthrough where I enumerate tables, extract user credentials, and log in as administrator to solve the lab.
- 10
- MIT
- 12 mo ago
SQL-injection-attack-listing-the-database-contents-on-non-Oracle-databases
UNION-based SQL injection used to enumerate database tables, extract credential columns, dump usernames and passwords, and log in as the administrator.
- 10
- MIT
- 12 mo ago
SQL-injection-attack-querying-the-database-type-and-version-on-MySQL-and-Microsoft
A simple UNION-based SQL injection exploiting the category filter to enumerate column count and extract the backend database version using @@version
- 10
- MIT
- 12 mo ago