security-research

Open repos and models their makers tagged security-research, most starred first. The same for everyone.

AI on my own machineRepo

artex-global

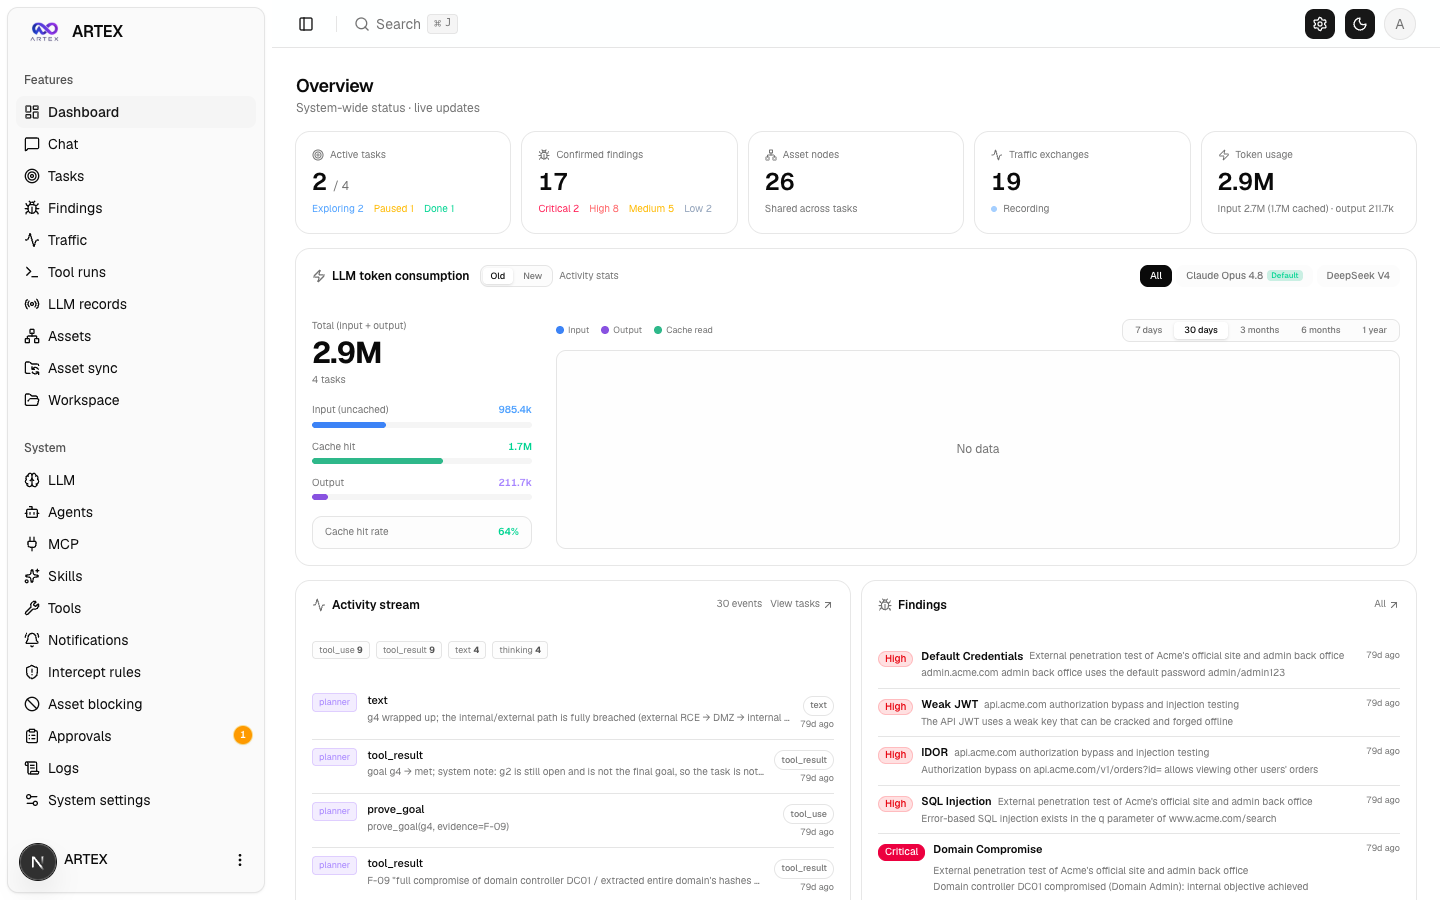
Global edition of ARTEX — an LLM multi-agent autonomous penetration-testing framework. English default, switchable to Korean/Chinese/Spanish/Japanese. For authorized, defensive and detection use only. (upstream: Autumn-27/ARTEX, AGPL-3.0)

  • 4k
  • Go
  • AGPL-3.0
  • 10 d ago
jiwoochrisTake it
Run my own servicesRepo

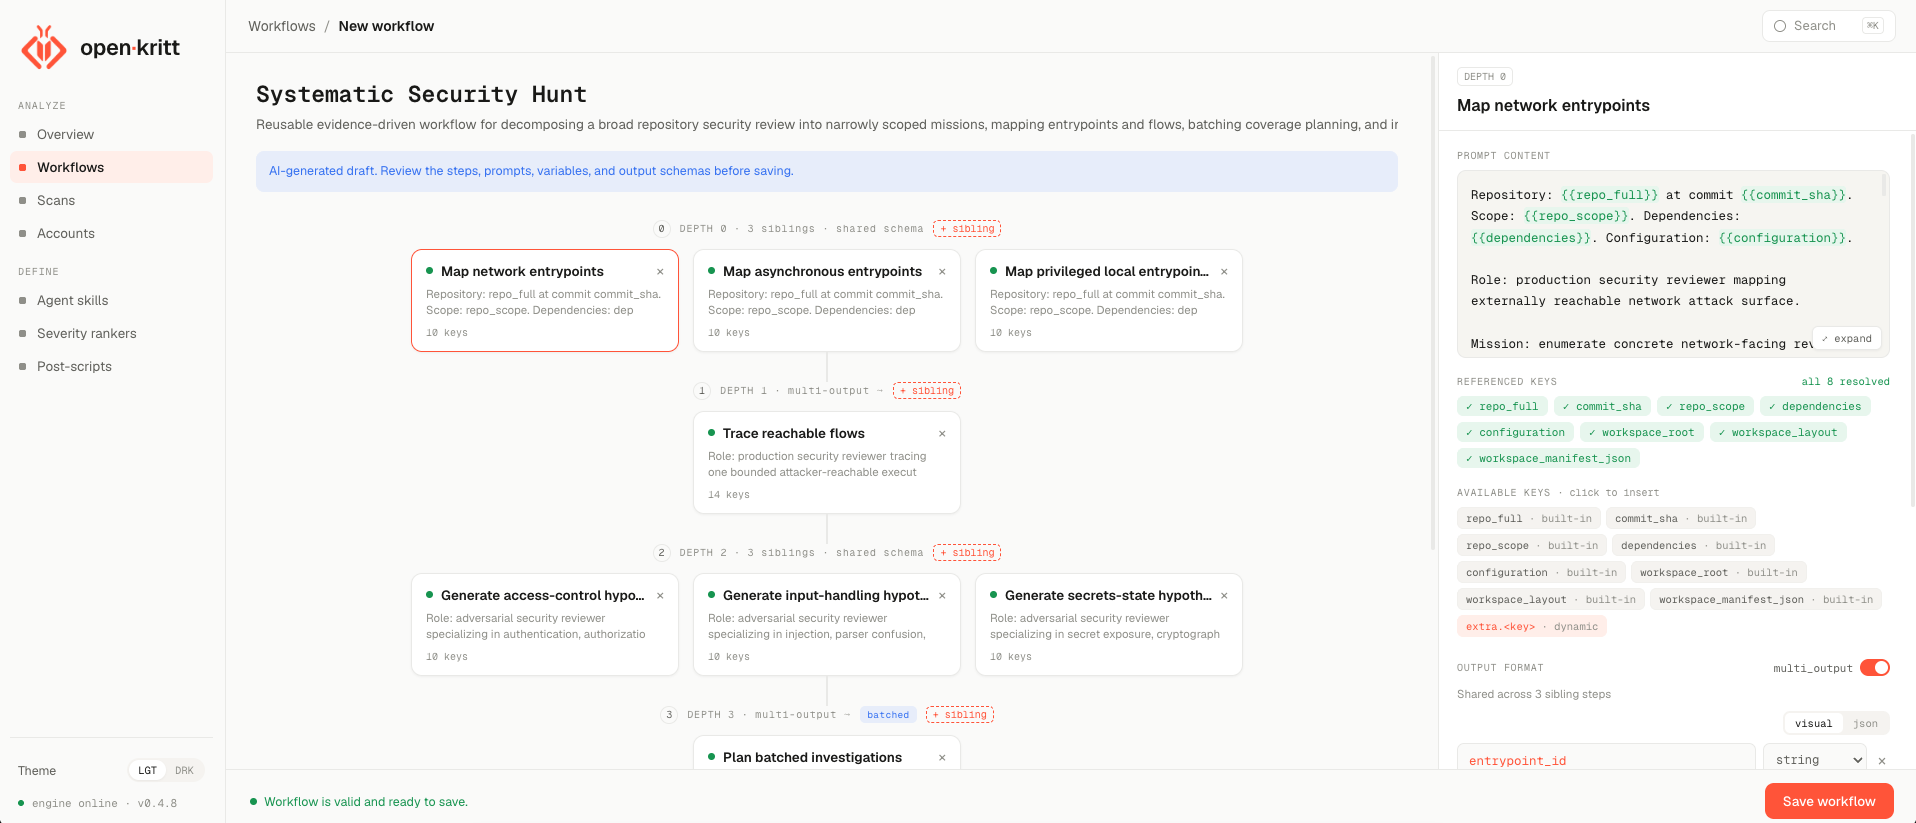
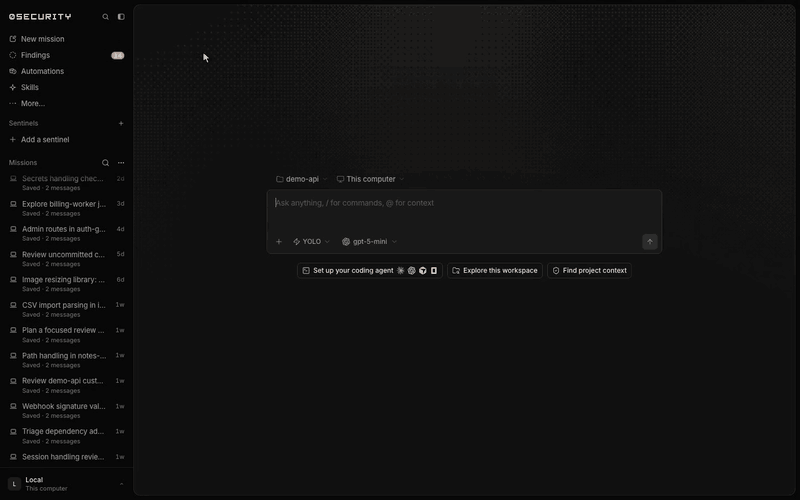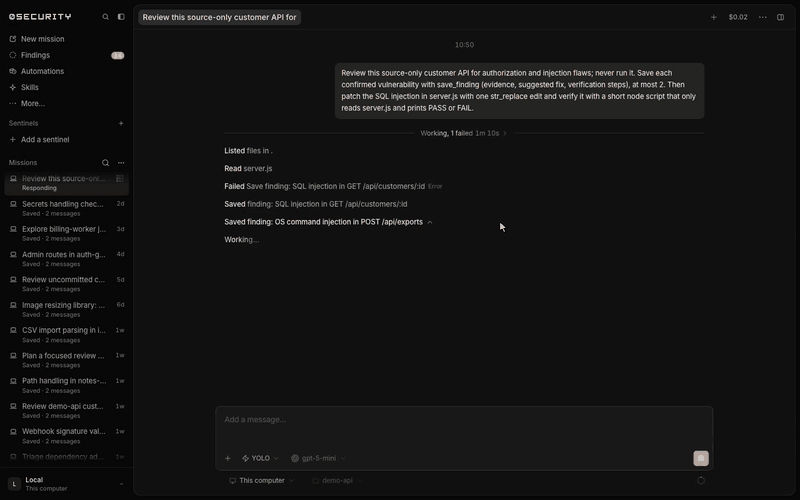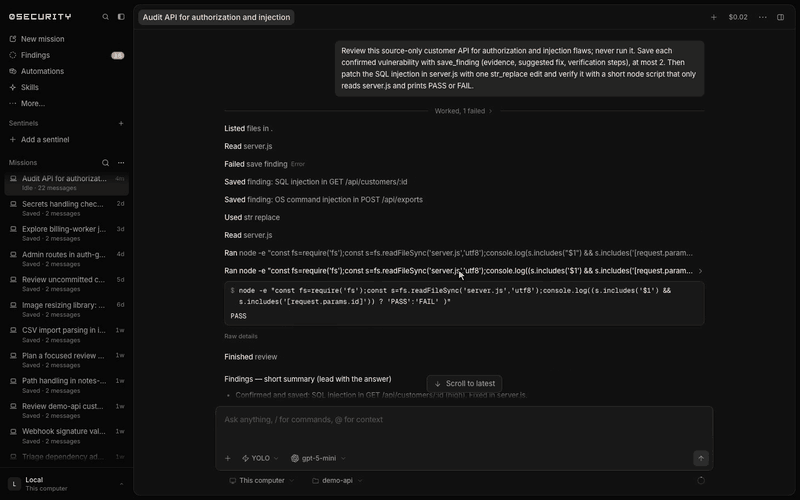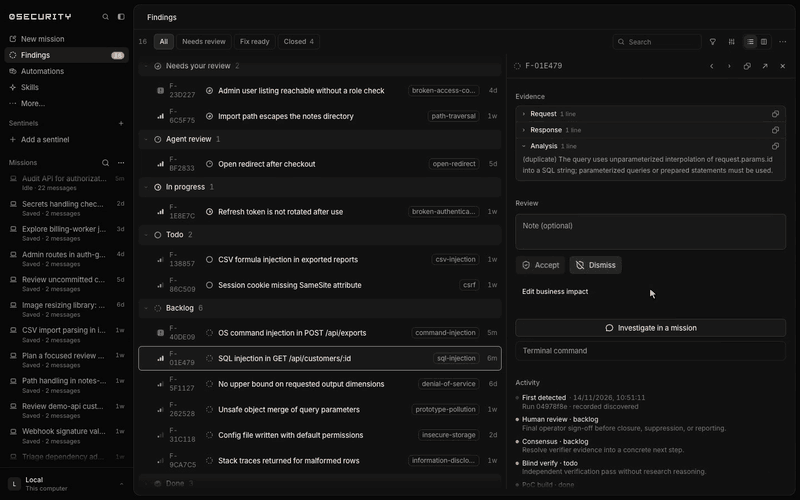
open-kritt

Open-source, self-hosted AI vulnerability research tool that orchestrates agents to find and validate security issues in code.

  • 2.4k
  • JavaScript
  • AGPL-3.0
  • 3 d ago
Kritt-aiTake it
Hardware and DIYRepo

NRSuite

NRSuite a wireless security testing toolkit for Android with no root required. Uses a $3 ESP32 over USB to add Wi-Fi packet capture, WPA2/PMKID handshake grabbing, BLE HID keyboard injection, USB mass storage, and BadUSB payloads to any Android phone through Termux.

  • 65
  • C++
  • MIT
  • 6 wk ago
7wp81xTake it
Hardware and DIYRepo

Flipper-EvilRelay

ISO-DEP (ISO 14443-4) NFC relay for the Flipper Zero. Read a real contactless card on a phone/Evil-Cardputer, relay APDUs over Wi-Fi to an ESP32-C3 bridge, and emulate the card to the reader with the Flipper. Ported from Evil-M5Project.

  • 45
  • Kotlin
  • GPL-3.0
  • 5 wk ago
7h30th3r0n3Take it
GitHubRepo

GhostBLE

GhostBLE is a BLE privacy scanner for the M5Stack Cardputer. It discovers nearby devices, analyzes their privacy posture, and visualizes BLE activity with the interactive mascot Nibbles.

  • 42
  • C++
  • MIT
  • 3 wk ago
SmonSETake it
GitHubRepo

Skullr

SKULLR is a fully automated wrapper around FFUF designed to enhance web content discovery. It includes automatic installation, protocol detection, wordlist management, false-positive checks, structured reporting, and subdomain discovery—all in one command.

  • 3
  • Shell
  • MIT
  • 7 mo ago
URDev4everTake it
Security and privacyRepo

jwtelescope

🔭 JWTelescope is an advanced CLI tool for decoding, inspecting, and performing security analysis on JSON Web Tokens (JWTs). It is designed for bug bounty hunters, pentesters, and developers who want fast insight into JWT structure, claims, and common misconfigurations.

  • 3
  • Python
  • MIT
  • 8 mo ago
URDev4everTake it
Search GitHub and Hugging Face for security-research

Get , open it once and sign in. Then come back here and press the button again.