syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
- 9.9k
- Go
- Apache-2.0
- 3 d ago
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
:mag: ScanCode detects licenses, copyrights, dependencies by "scanning code" ... to discover and inventory open source and third-party packages used in your code. Sponsored by NLnet, the Google Summer of Code, Azure credits, nexB and other generous sponsors!
OpenSCA is an open source software supply chain security solution that supports the detection of open source dependencies, vulnerabilities and license compliance with a widely noticed accuracy by the community.
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate in your CI/CD pipeline with automatic submission to Dependency Track server
Ruby gem & CLI to detect a project's open source license (SPDX) from LICENSE files, package manifests, and READMEs
🎁 snapshot every package on your machine to one file, restore it on a new one
Various data formats for the SPDX License List including RDFa, HTML, Text, and JSON
CycloneDX CLI tool for SBOM analysis, merging, diffs and format conversions.
Semantic SBOM/CBOM/AI-BOM diff, quality scoring, and compliance validation for CycloneDX/SPDX — component, license, and vulnerability change analysis, cryptographic inventory grading, PQC readiness (CNSA 2.0, NIST IR 8547), and regulatory gates for NTIA, FDA, EU CRA, BSI TR-03183, EUCC, SSDF, EO 14028, and the EU AI Act.
A Python library to parse, validate and create SPDX documents.
ScanCode.io is a server to script and automate software composition analysis with pipelines. This project is sponsored by the European Commission, NLnet NGI0, the Google Summer of Code, nexB and others generous sponsors!
licensechecker (lc) a command line application which scans directories and identifies what software license things are under producing reports as either SPDX, CSV, JSON, XLSX or CLI Tabular output. Dual-licensed under MIT or the UNLICENSE.
Utility that provides an API platform for validating, querying and managing BOM data
A standard API specification for exchanging supply chain artifacts and intelligence
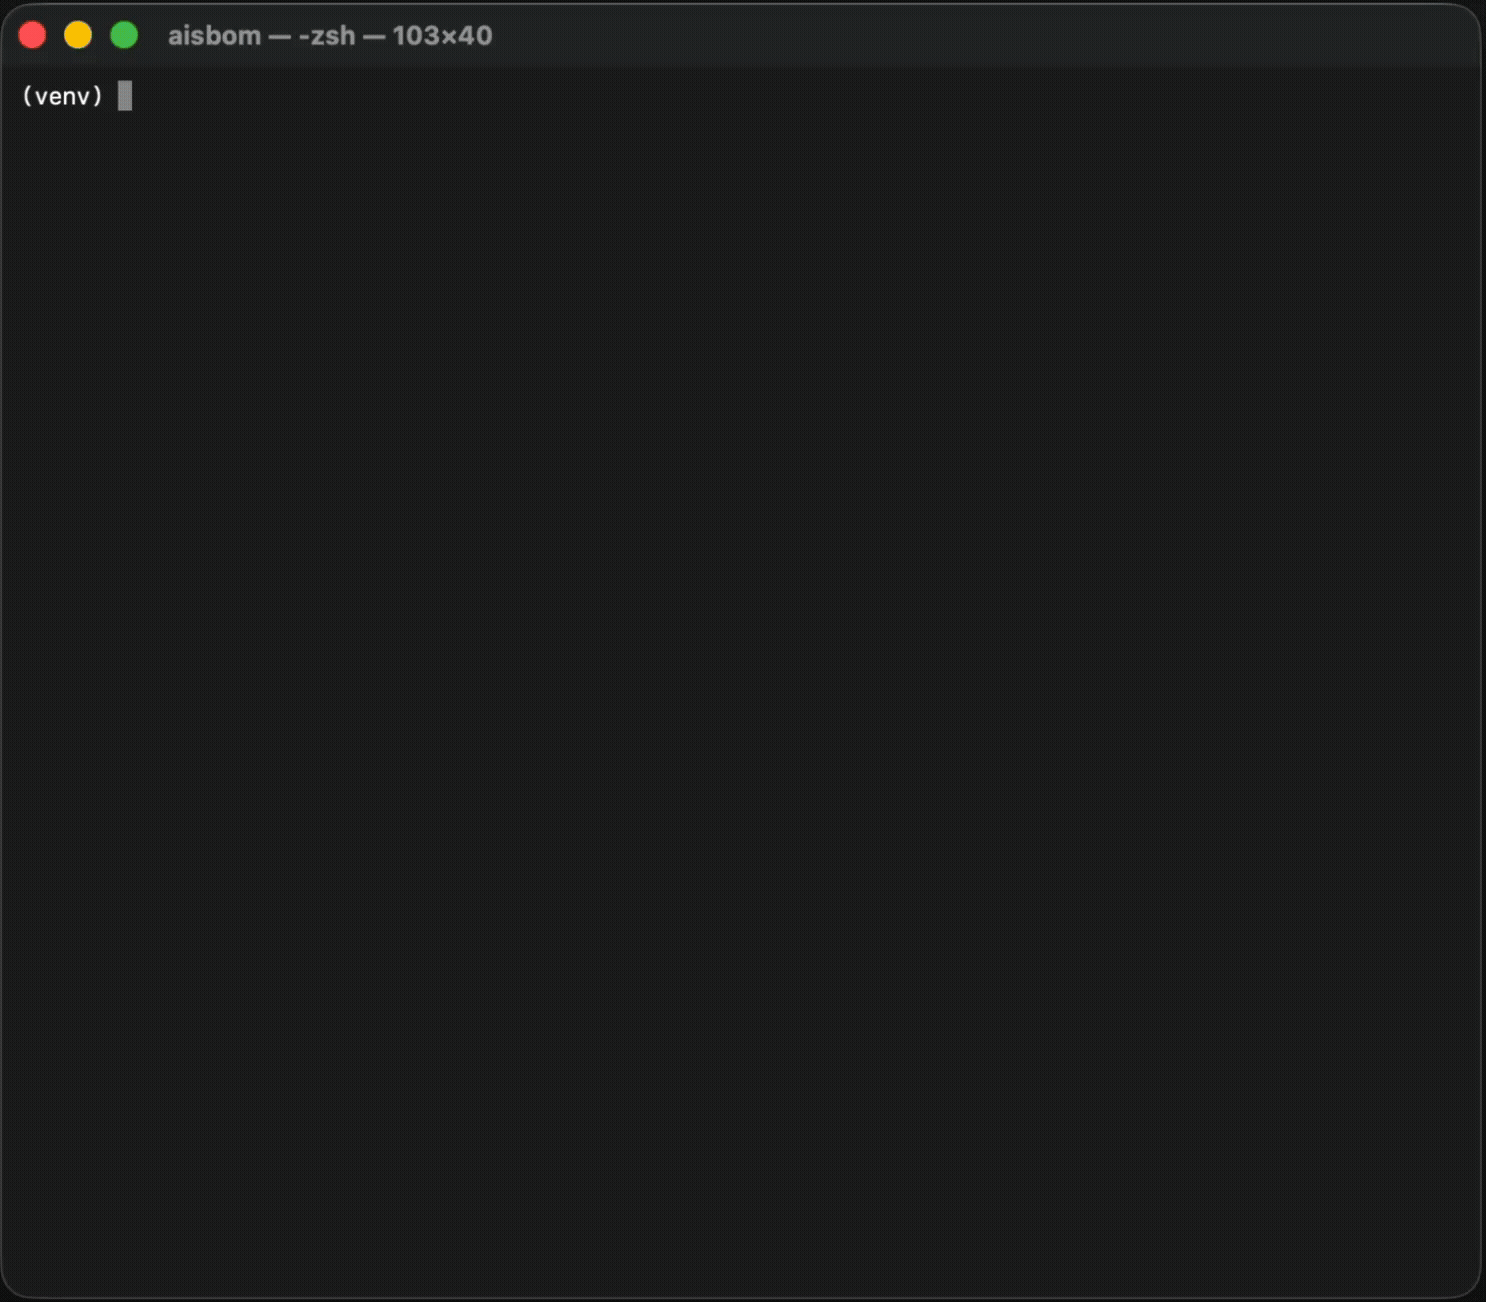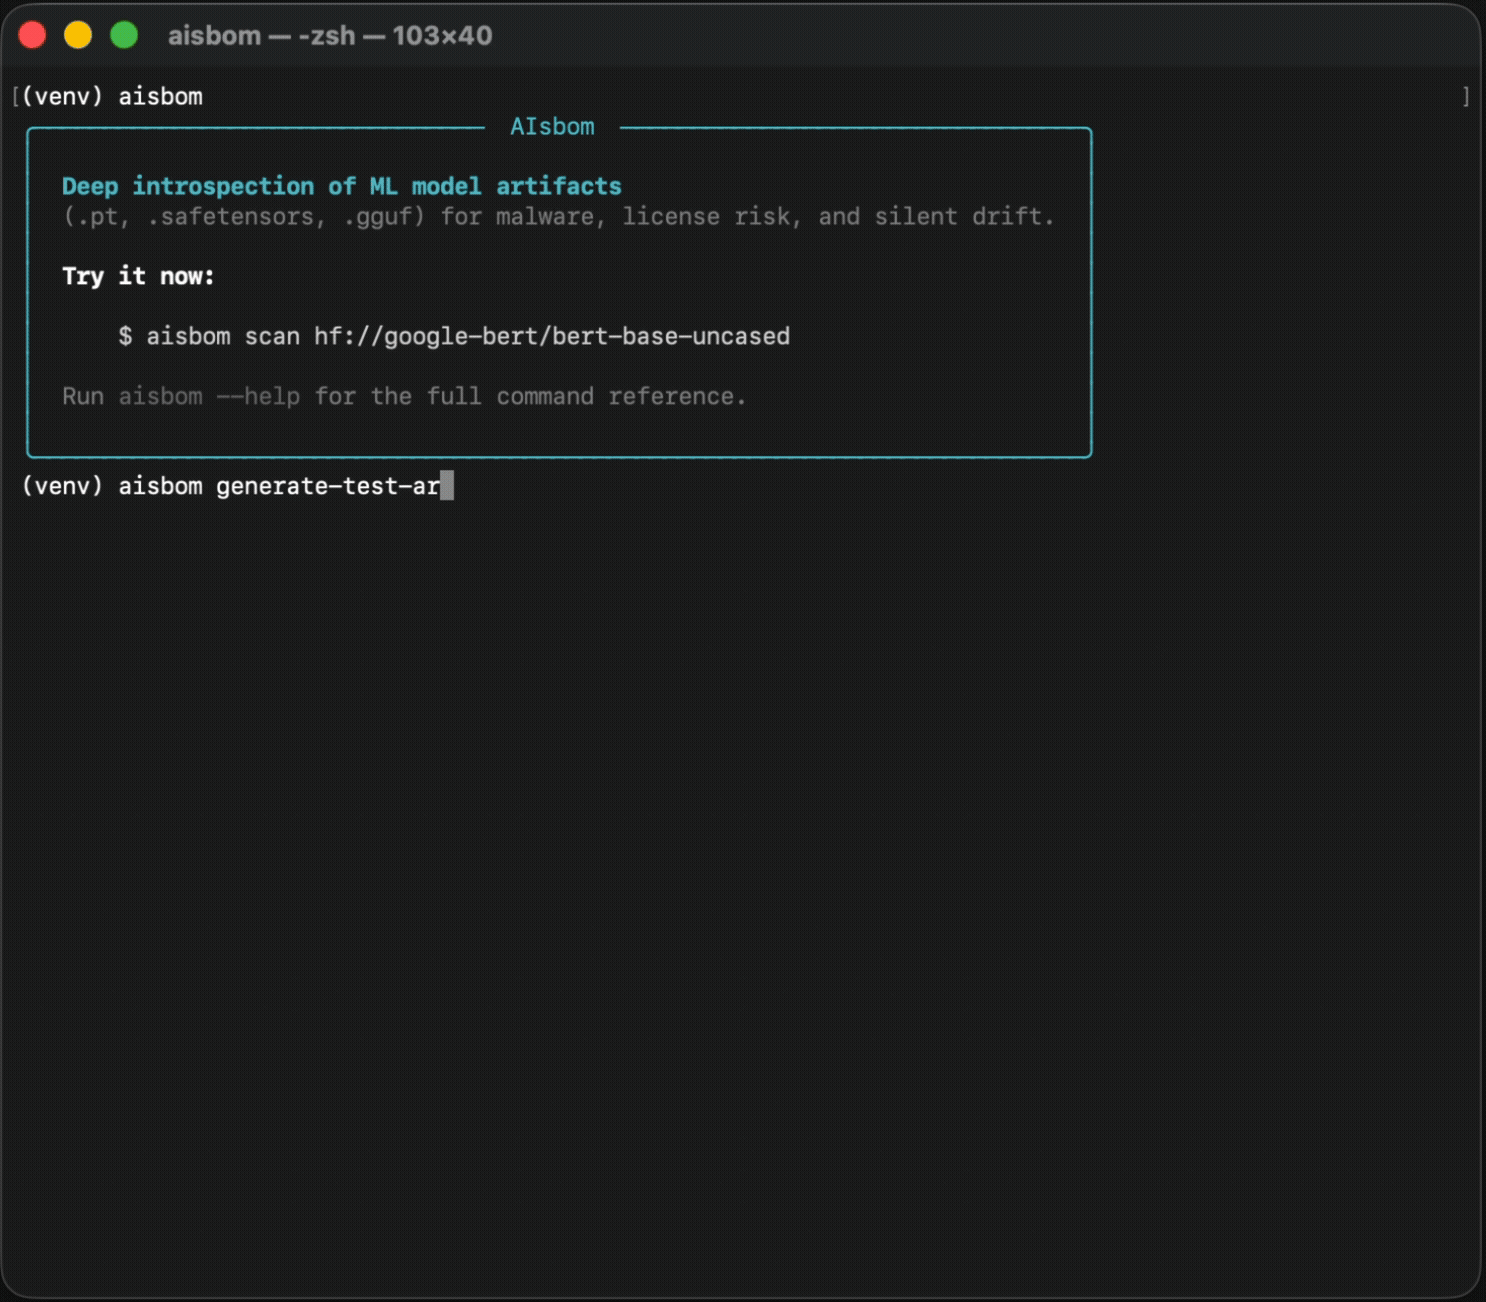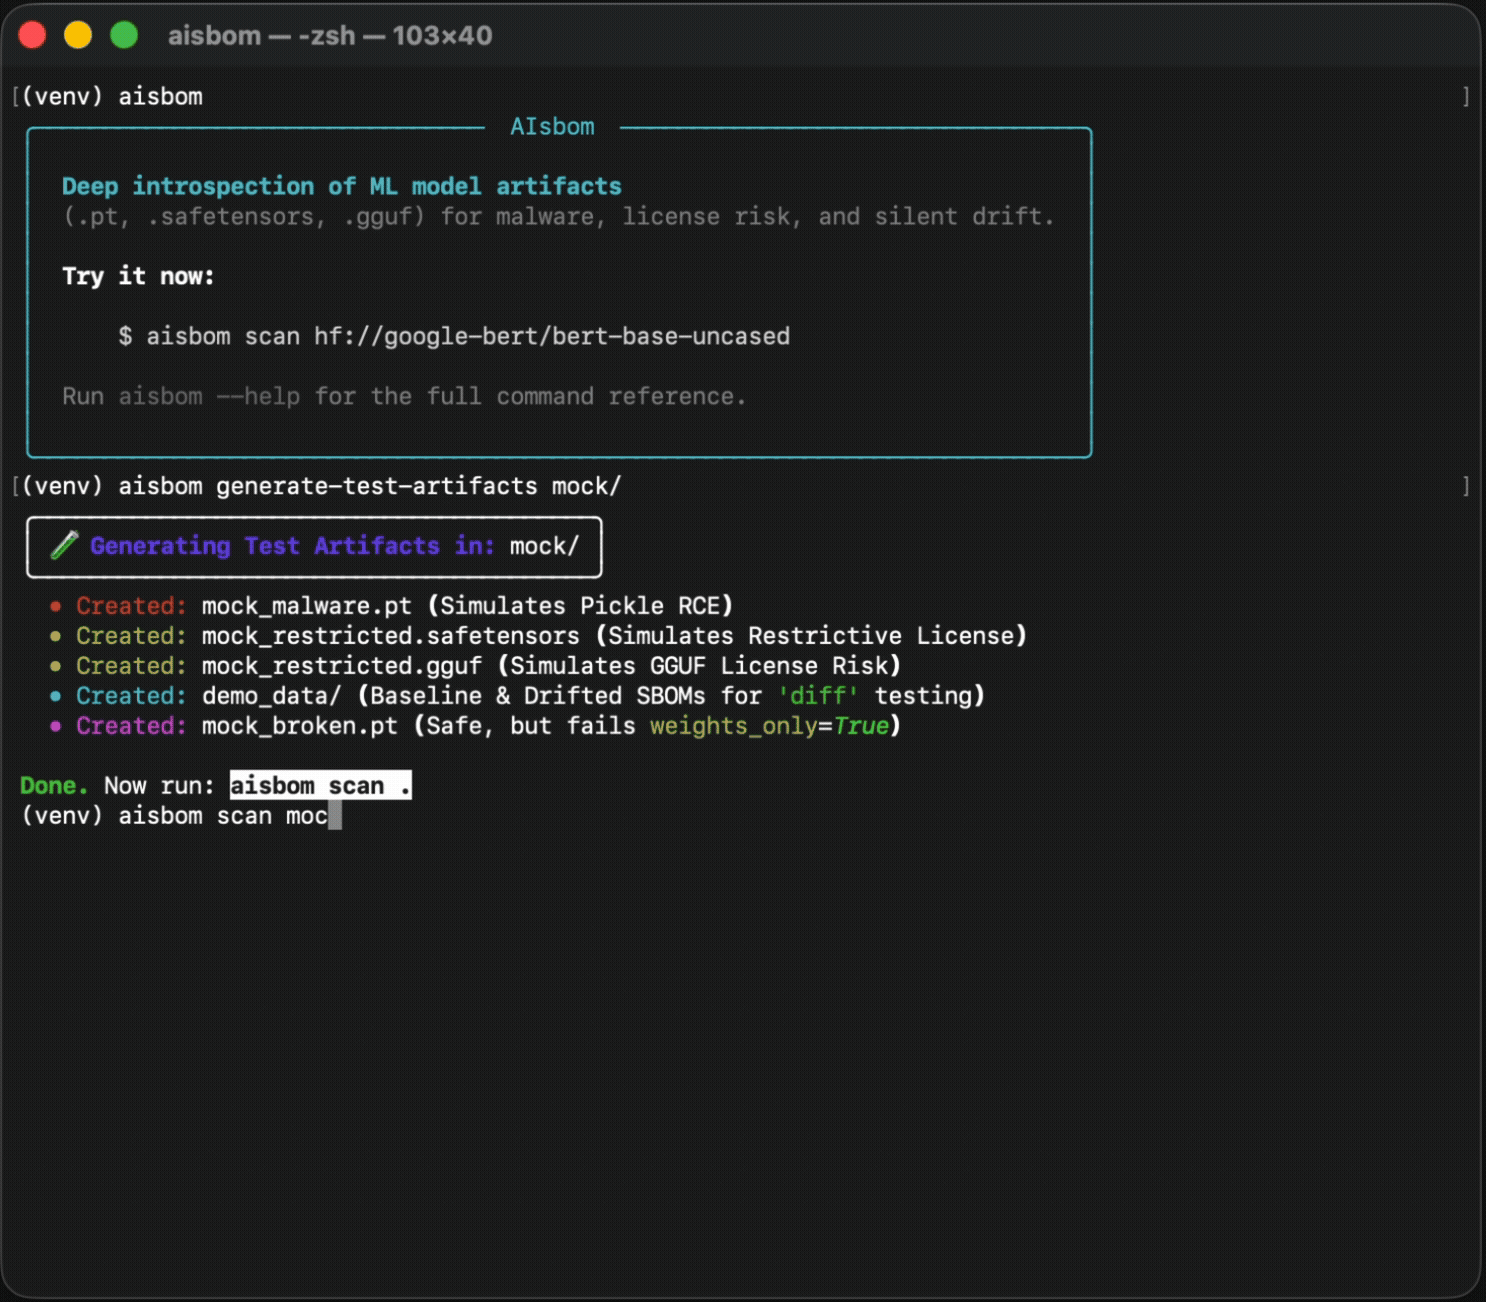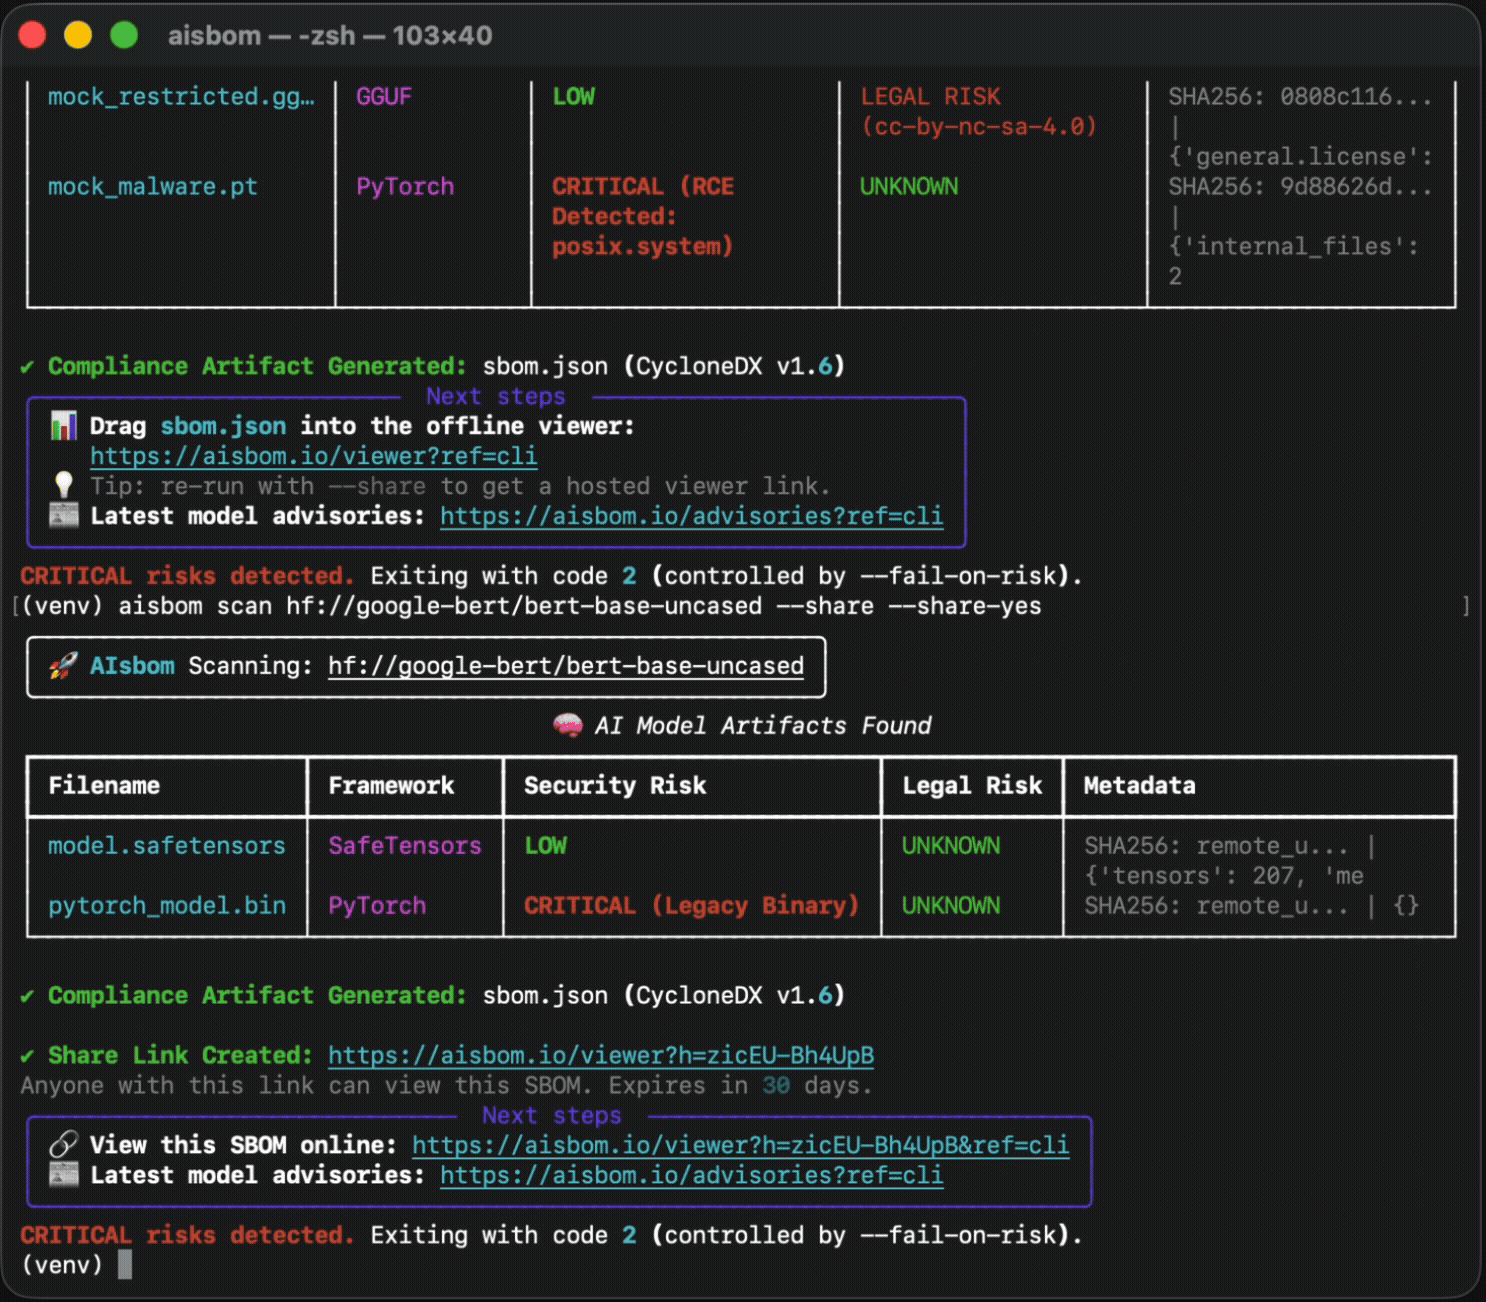
Static security scanner for ML model files — detects pickle bombs, Keras Lambda RCE and GGUF template injection, and generates CycloneDX / SPDX AI-BOMs (AIBOM) as EU AI Act, CRA and FDA §524B evidence.
Utility library to parse, normalize and compare License expressions for Python using a boolean logic engine. For expressions using SPDX or any other license id scheme.
Curated catalog of free, commercially usable game assets, libraries and tools. Each licence recorded from its source with the date it was read. Links only, nothing rehosted. JSON/CSV dataset and feeds.
Open-source GitHub automation bot for licensing, community standards, security, documentation, PR & issue management, and repository maintenance. One GitHub App, multiple capabilities.
Chrome/Firefox browser extension to compare text against spdx license list
Run ORT in your GitHub action workflow to do licensing, security and best practices checks and generate reports/SBOMs
A tool to match license text with SPDX license list using a an algorithm with finds close matches. It follows SPDX Matching guidelines to keep the substantial text as well as ignore the replaceable text for matching purposes.
Fast cross-ecosystem dependency license compatibility checker + Claude Code review skill
SBOM diff with supply-chain risk signals — flags new CVEs, typosquats, and young maintainers on changed deps. Built after axios (Mar 2026), Shai-Hulud, and xz.
Which of your products does this CVE reach? SBOM dependency graph with CISA KEV, EPSS and OpenVEX. Single static Go binary. Continuation of Minefield.
📓 A python CLI tool to extract a software bill of materials and license info from a vcpkg manifest.