Triton
Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification or just emulate code.
- 4.4k
- C++
- Apache-2.0
- 11 d ago
Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification or just emulate code.
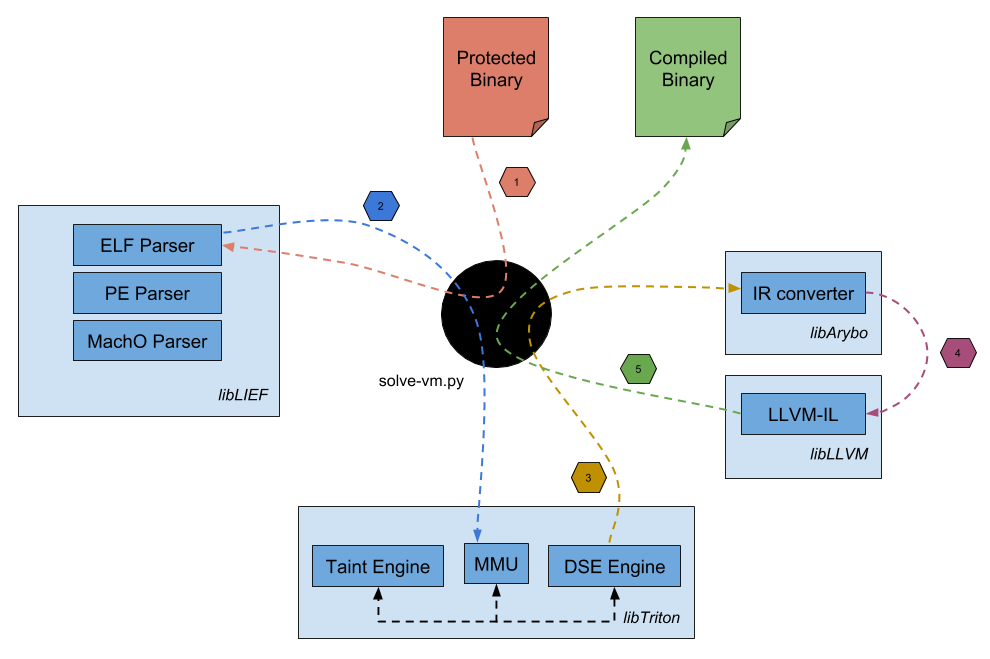
Playing with the Tigress software protection. Break some of its protections and solve their reverse engineering challenges. Automatic deobfuscation using symbolic execution, taint analysis and LLVM.
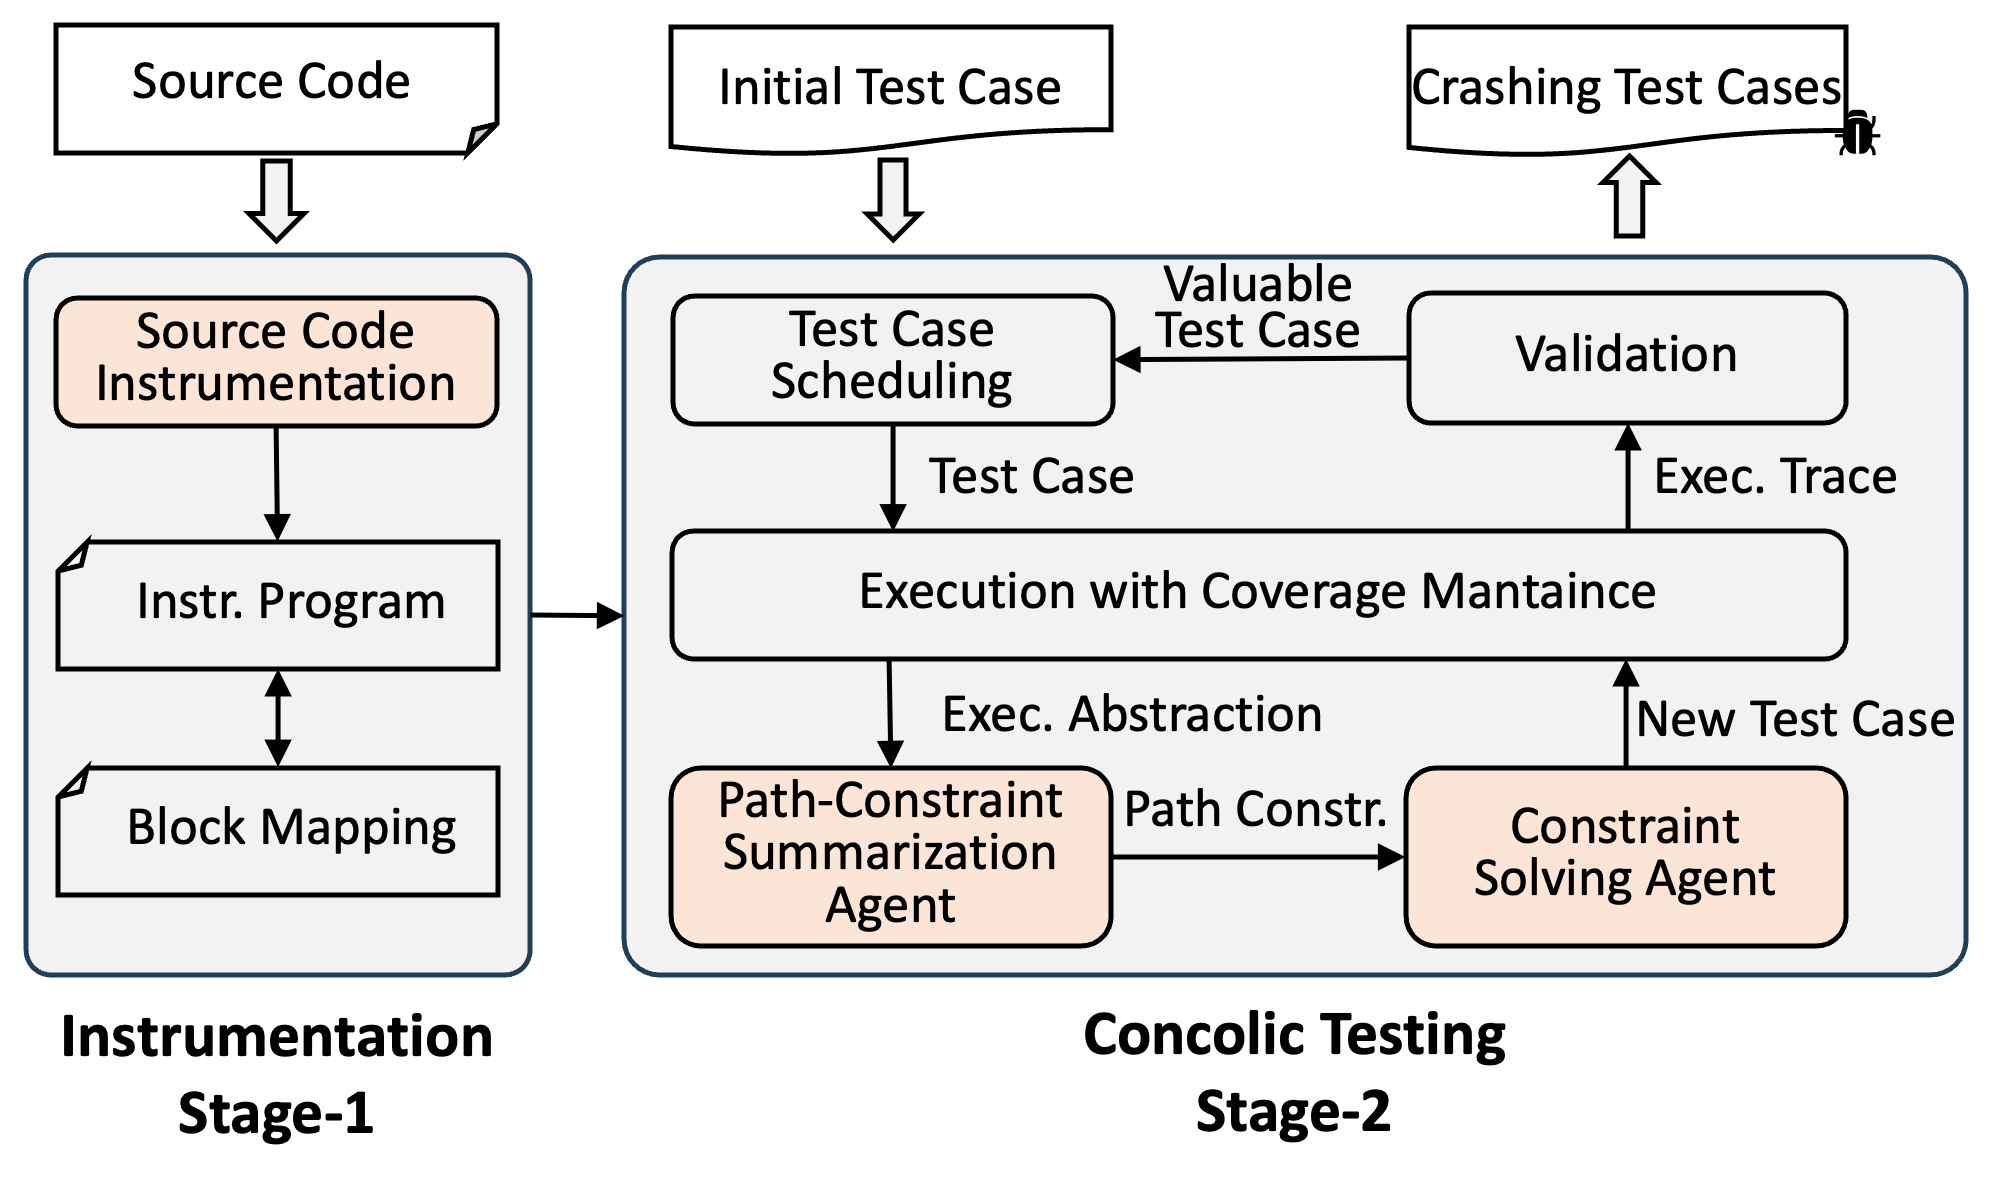
ConcoLLMic: the first language- and theory-agonistic concolic execution engine via LLM agents
OSS-Sydr-Fuzz - OSS-Fuzz fork for hybrid fuzzing (fuzzer+DSE) open source software.
Automated unit test generation and precise code analysis for Java
A structured binary exploitation curriculum covering stack, heap, mitigations, ROP, and automated exploitation.
The sound, open SAST for modern apps: code, dependencies, secrets, infrastructure and AI, in one tool
IRSentry is a C++ CLI for static analysis of LLVM IR. It leverages Path-Guided Symbolic Execution with Function Summaries and a Symbolic Memory model, backed by the Z3 SMT solver, to detect vulnerabilities and generate concrete inputs. Language-agnostic, with an FTXUI interface and Doxygen docs.