vex

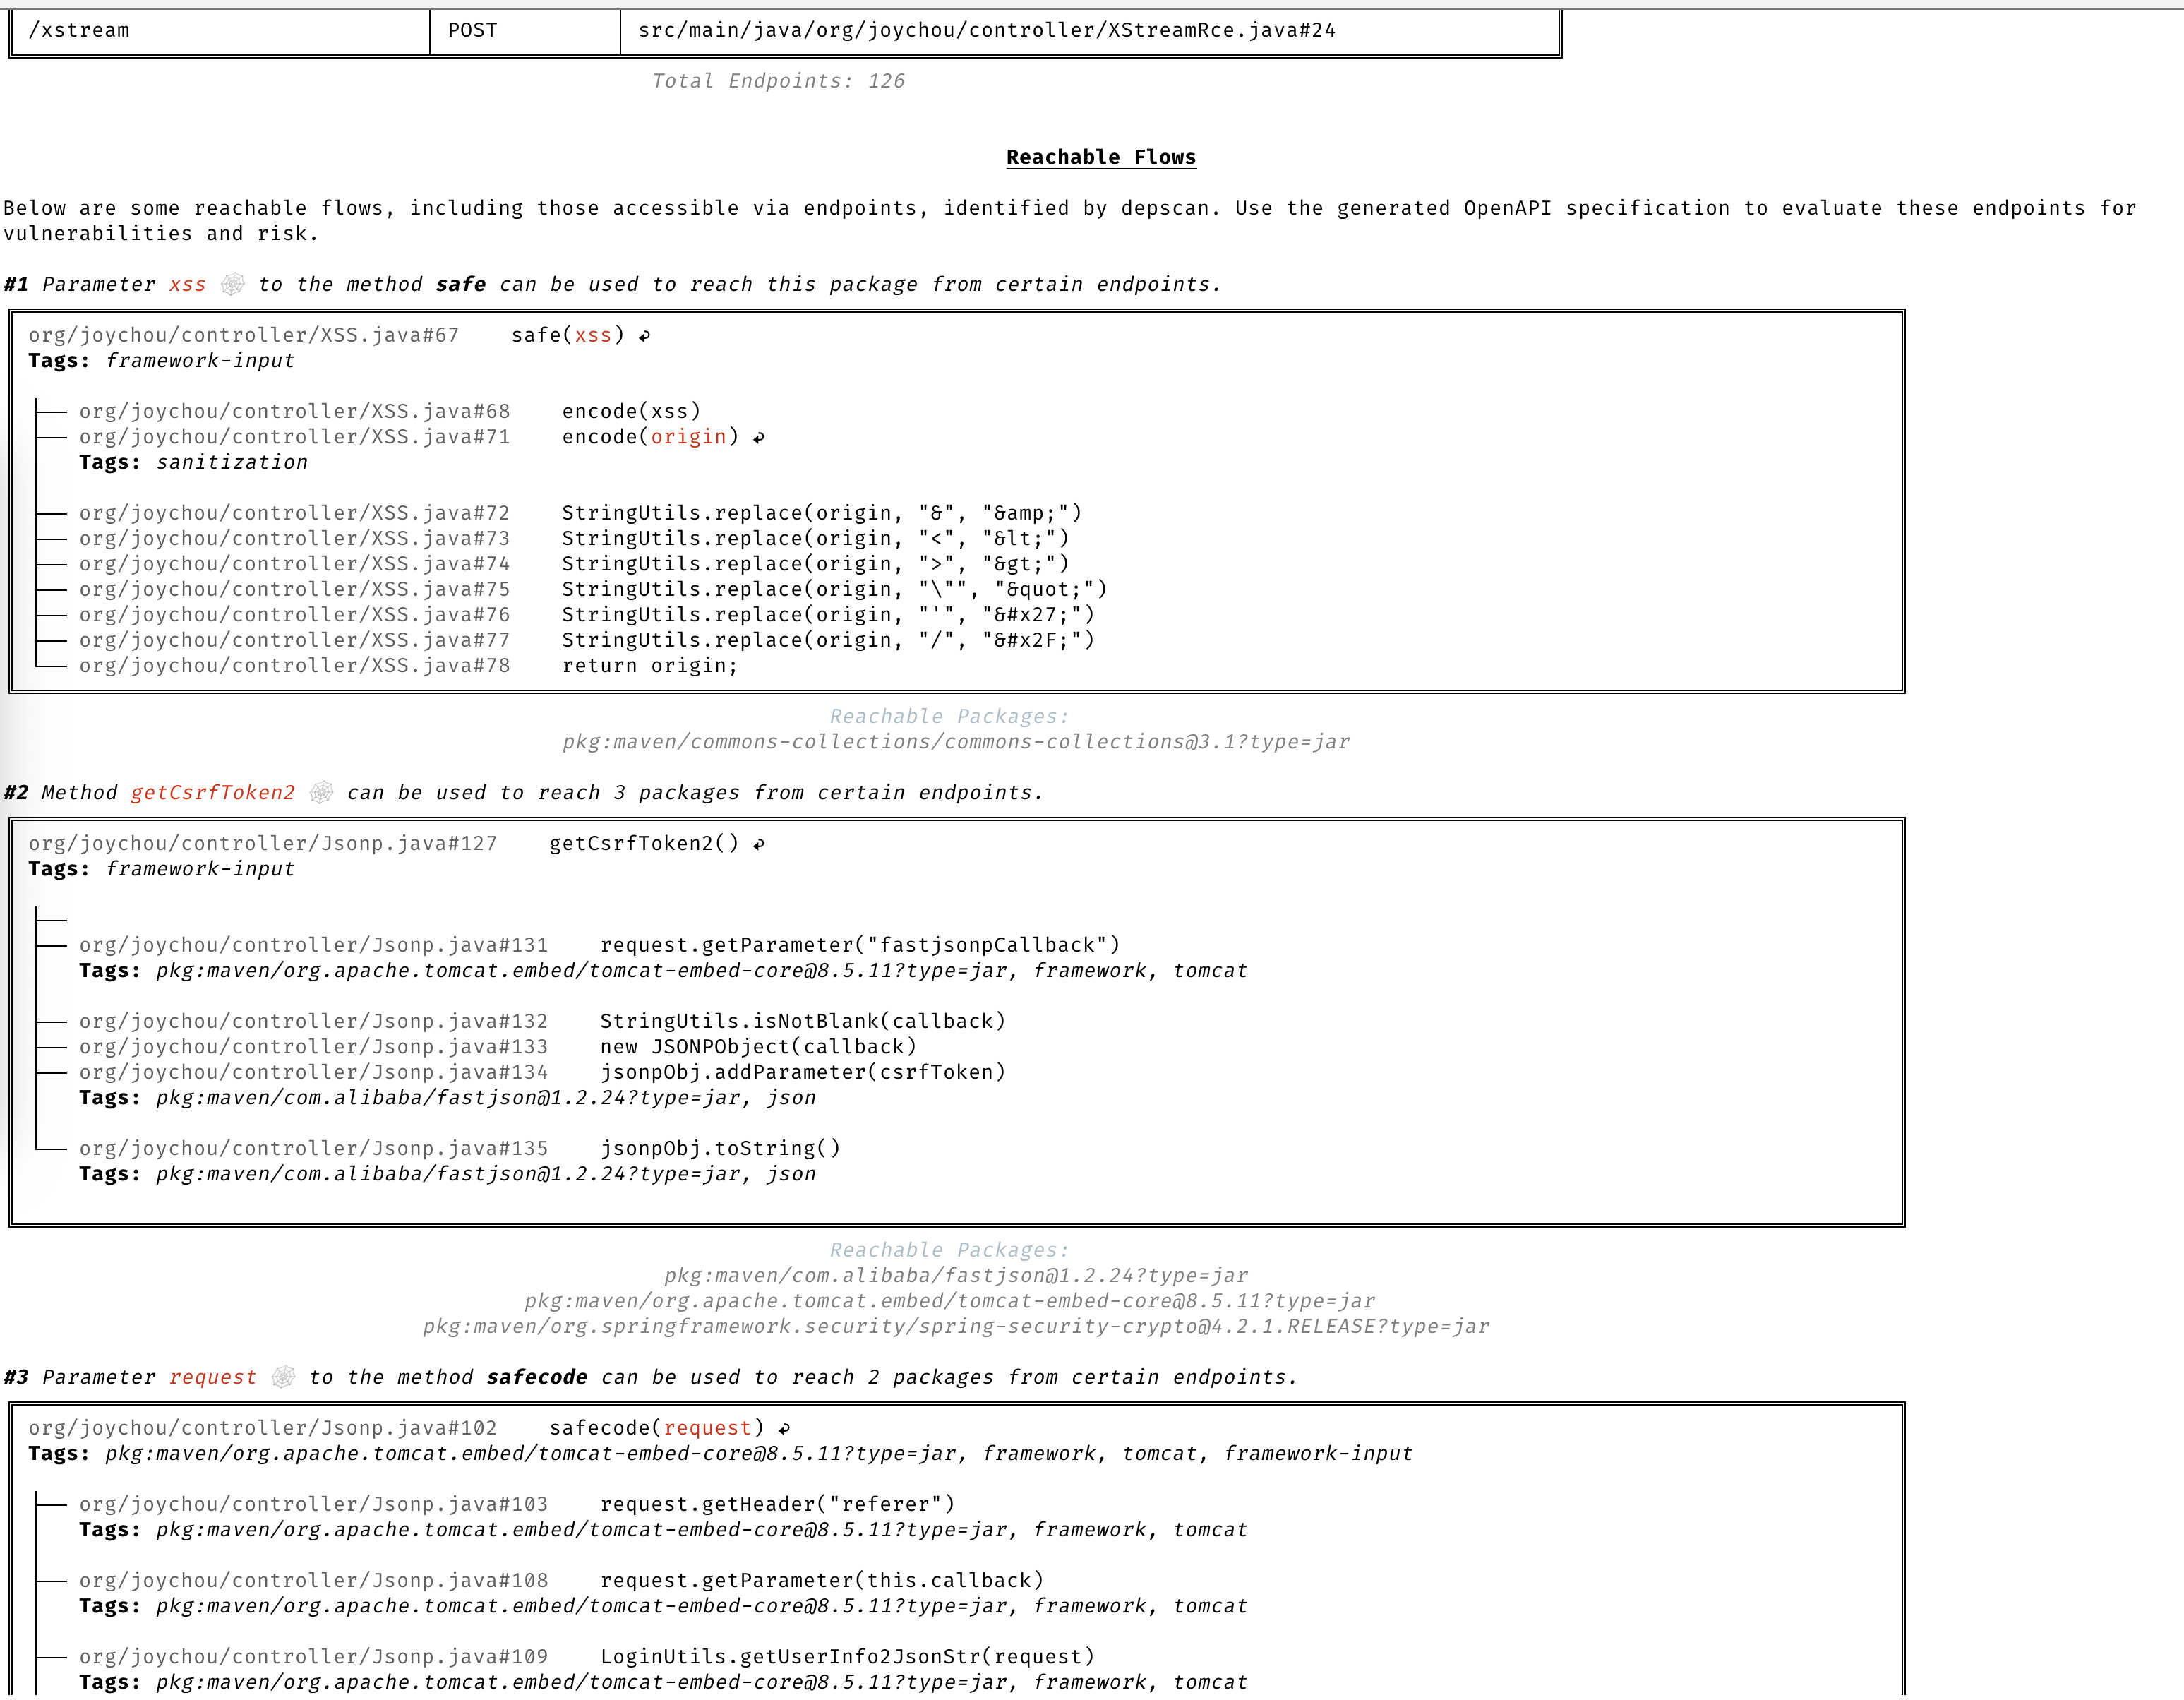
dep-scan
OWASP dep-scan is a next-generation security and risk audit tool based on known vulnerabilities, advisories, and license limitations for project dependencies. Both local repositories and container images are supported as the input, and the tool is ideal for integration.
- 1.5k
- Python
- MIT
- 1 d ago

cyclonedx-cli
CycloneDX CLI tool for SBOM analysis, merging, diffs and format conversions.
- 563
- C#
- Apache-2.0
- 5 wk ago

sbom-tools
Semantic SBOM/CBOM/AI-BOM diff, quality scoring, and compliance validation for CycloneDX/SPDX — component, license, and vulnerability change analysis, cryptographic inventory grading, PQC readiness (CNSA 2.0, NIST IR 8547), and regulatory gates for NTIA, FDA, EU CRA, BSI TR-03183, EUCC, SSDF, EO 14028, and the EU AI Act.
- 268
- Rust
- MIT
- 4 d ago


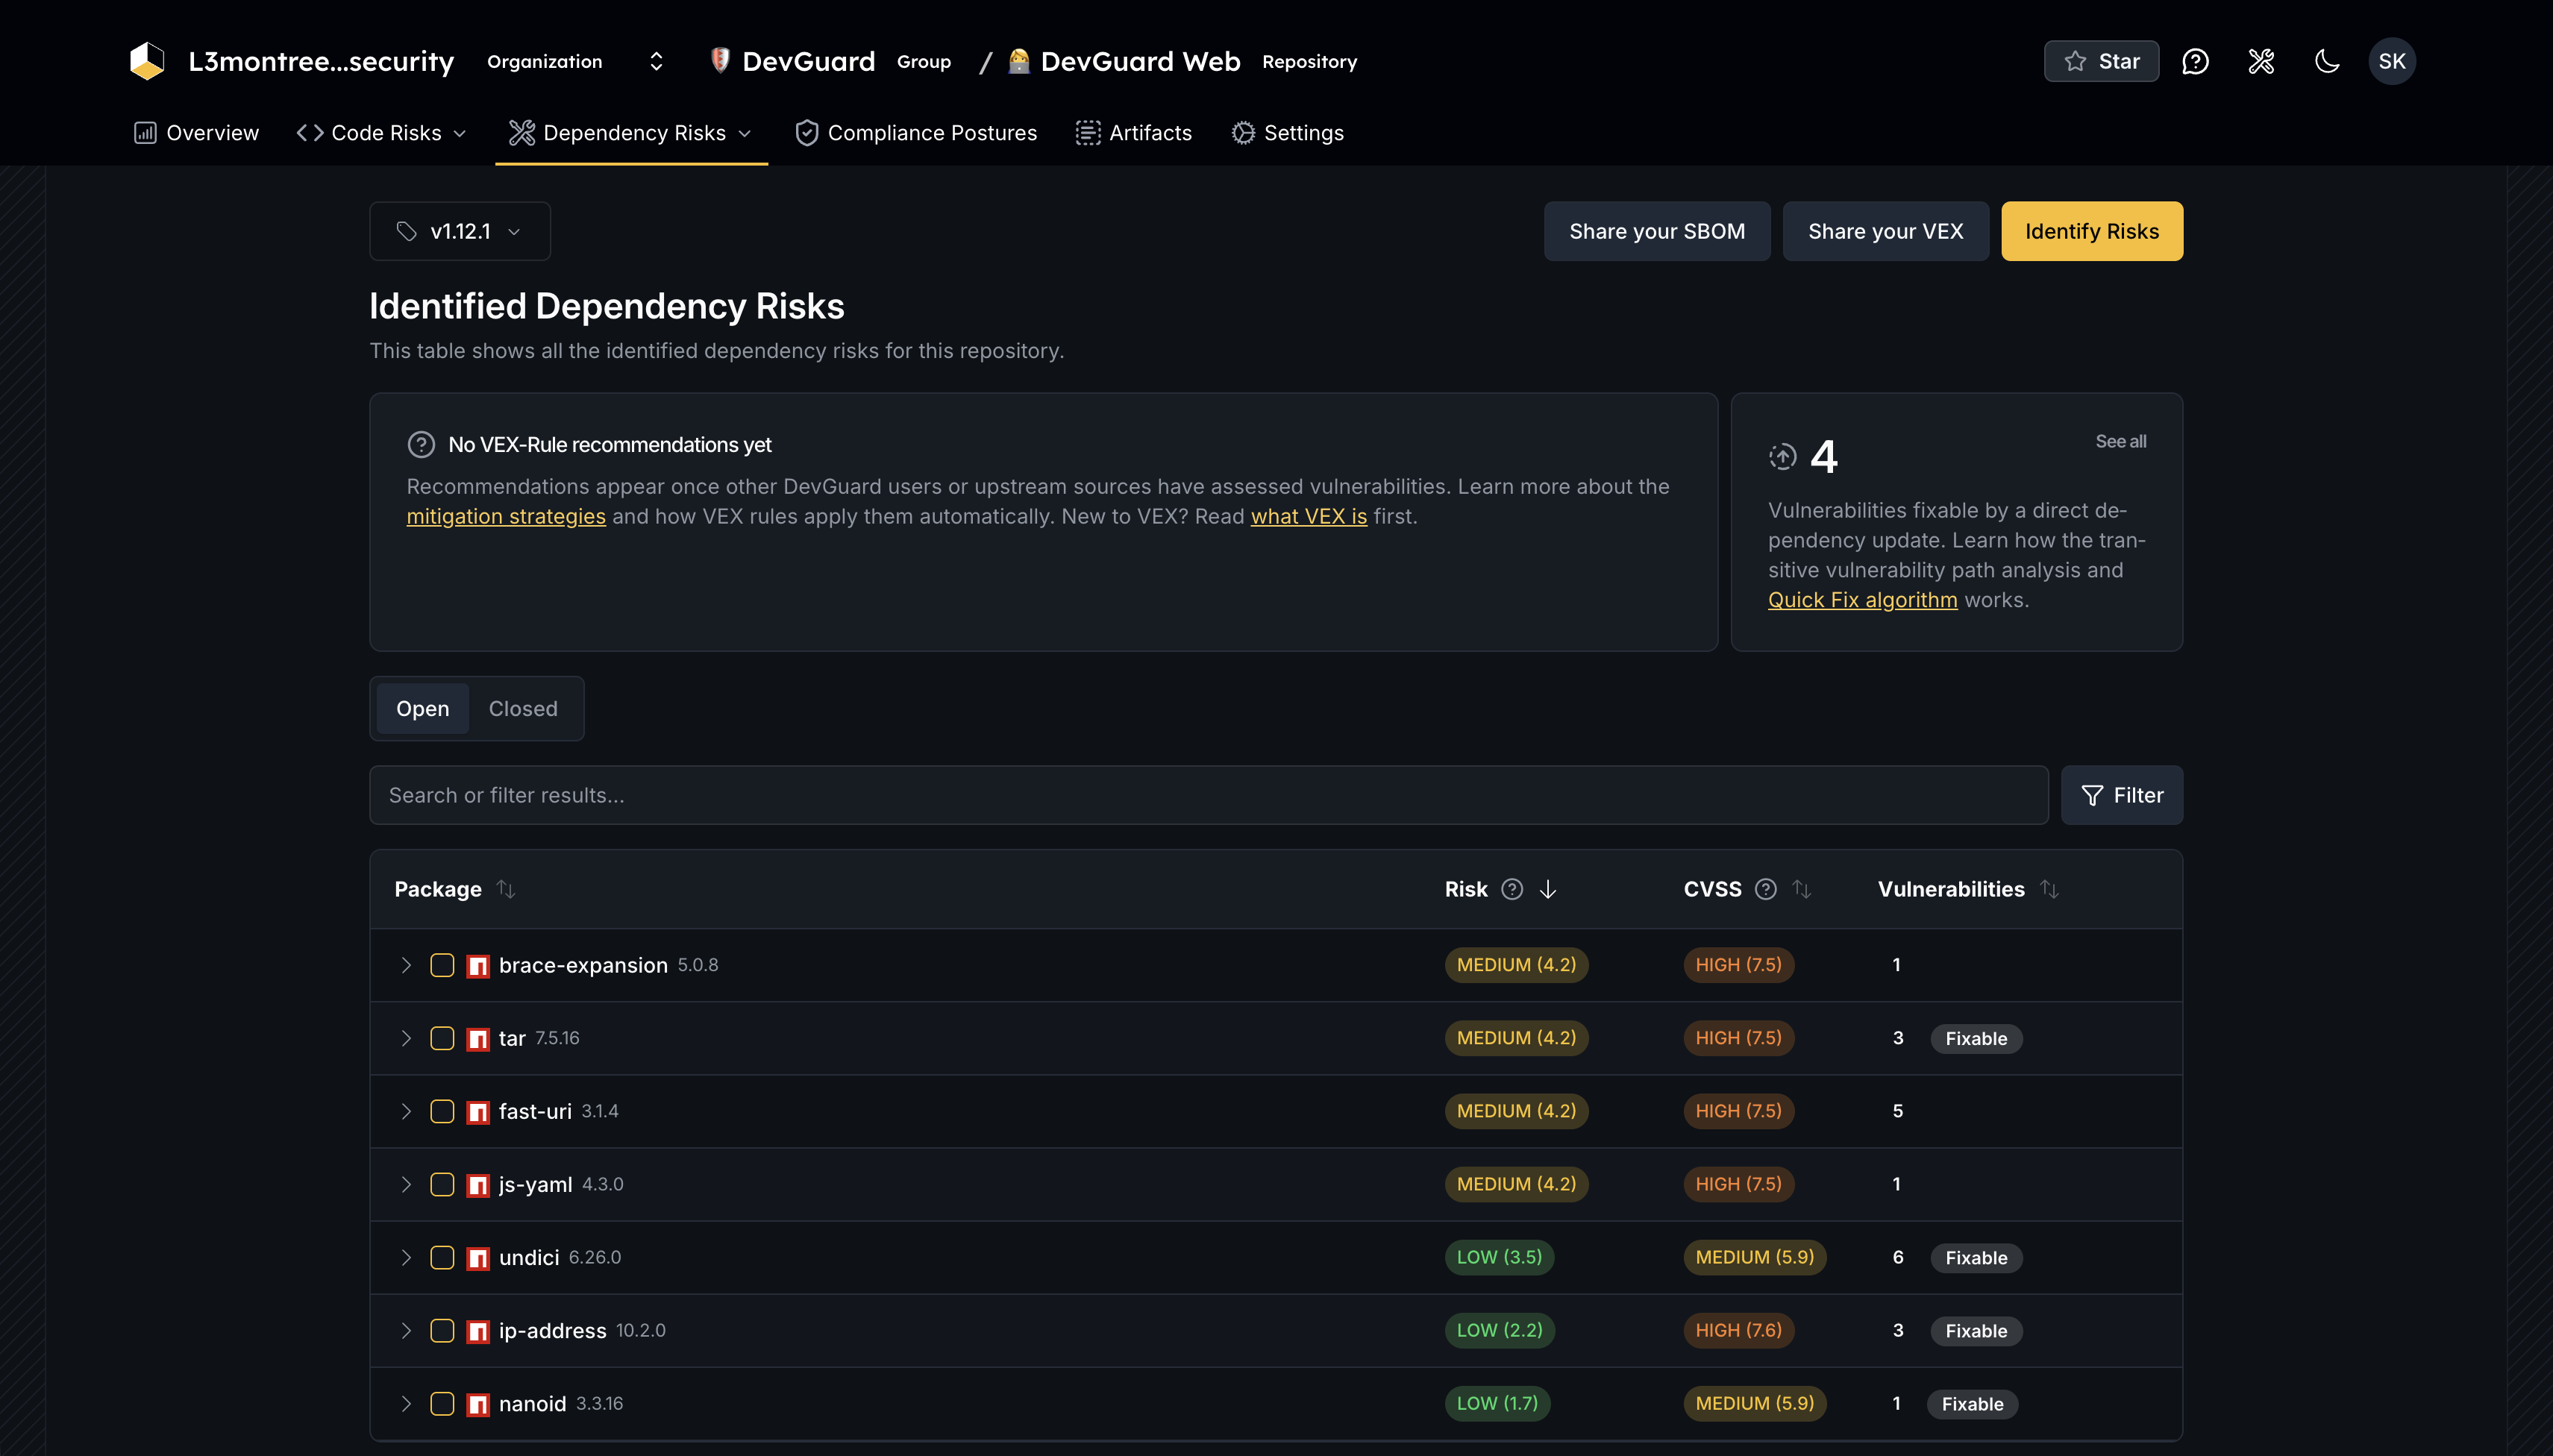
devguard
DevGuard Backend — Open-source software supply chain security: SBOM, CVE and VEX management, scanner integration, SLSA Dependency Ingestion Platform, Dependency Firewall and attestation-based compliance as code. An OWASP Incubator Project & OpenSSF General Member.
- 220
- Go
- 1 d ago

sbom-utility
Utility that provides an API platform for validating, querying and managing BOM data
- 171
- Go
- Apache-2.0
- 2 wk ago

nixos-vex
OpenVEX feed and NixOS module to manage NixOS CVEs, evaluated against your system's configuration.
- 35
- Python
- MIT
- 6 d ago

vulnlog
Record vulnerability analysis once in YAML. Generate suppression files, impact reports, and OpenVEX documents for your scanners, team, and customers.
- 22
- Kotlin
- Apache-2.0
- 2 d ago


AVL
Advanced function library, written in VEX language for SideFX Houdini. Now in development
- 17
- Apache-2.0
- 6 y ago

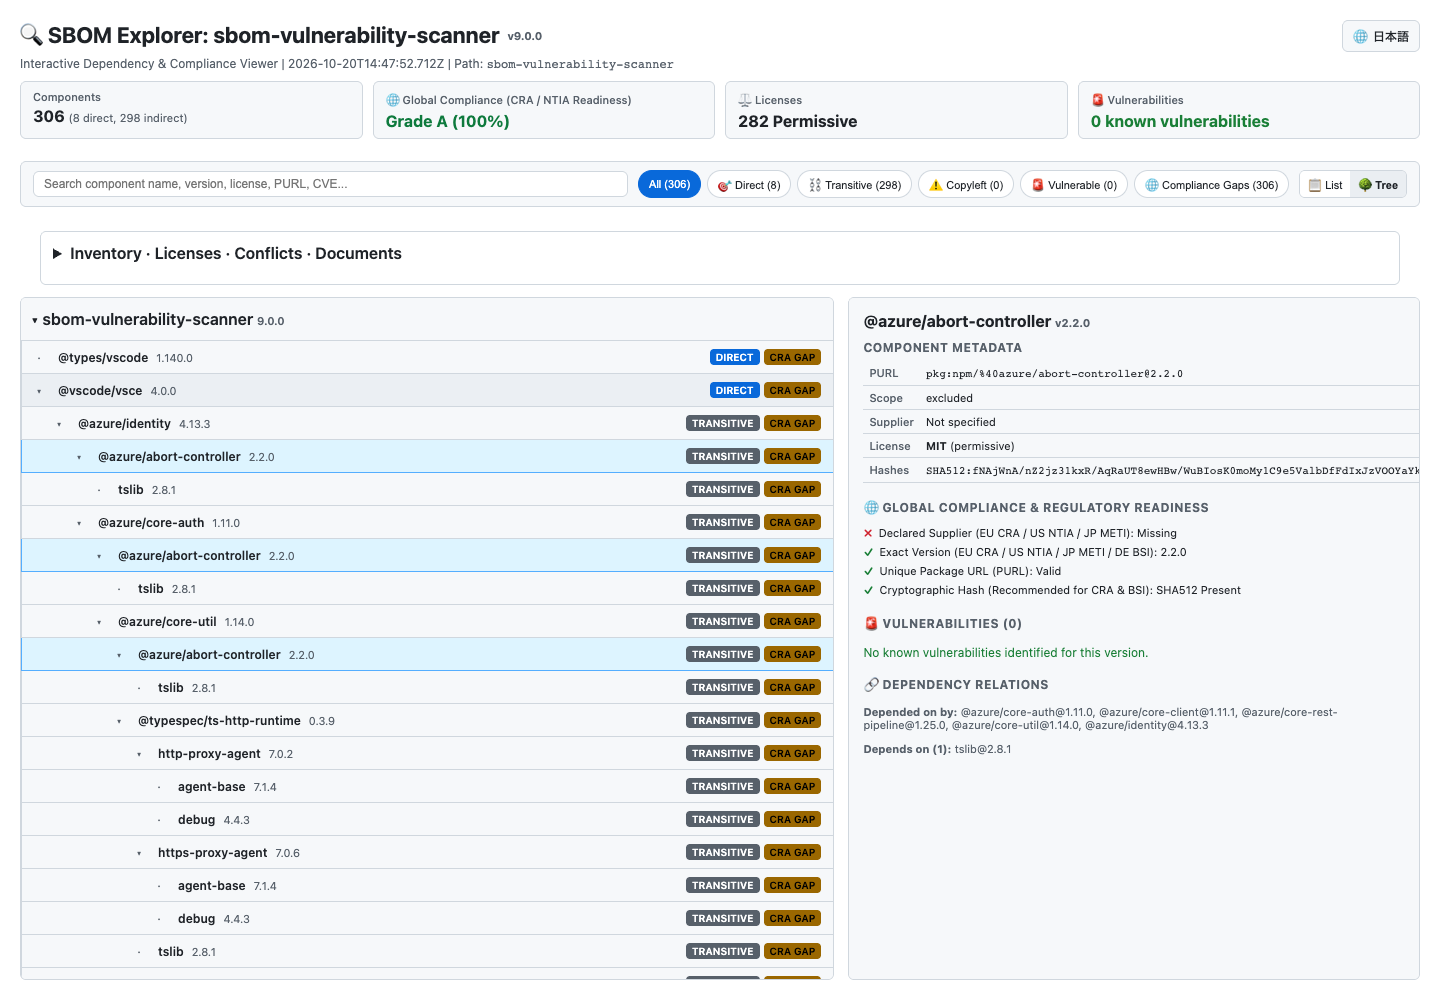
sbom-vulnerability-scanner
CycloneDX & SPDX SBOM generator, vulnerability scanner, EPSS exploit predictor, VEX engine, and compliance auditor for VS Code.
- 3
- JavaScript
- Apache-2.0
- 5 d ago

bomdrift
SBOM diff with supply-chain risk signals — flags new CVEs, typosquats, and young maintainers on changed deps. Built after axios (Mar 2026), Shai-Hulud, and xz.
- 7
- Rust
- Apache-2.0
- 4 mo ago


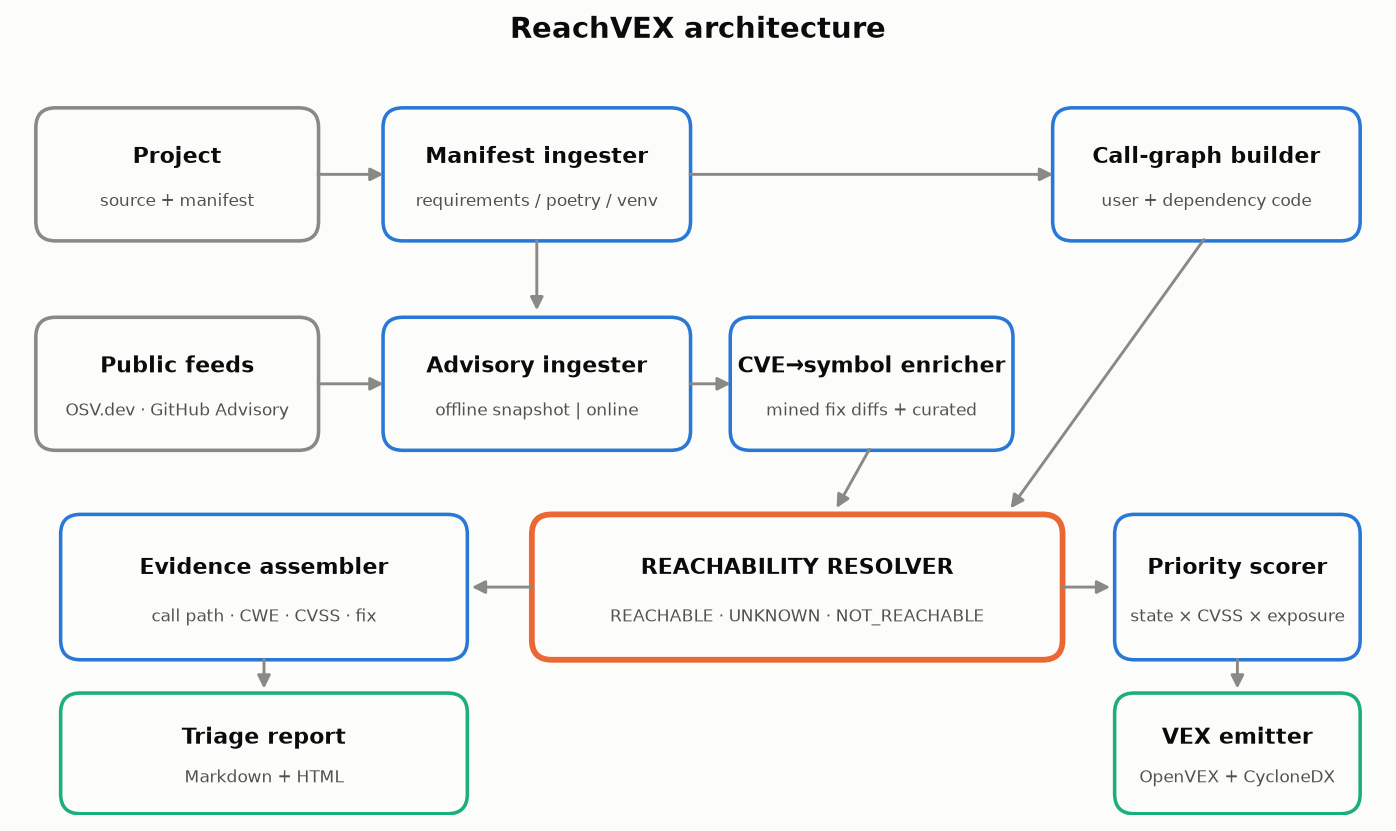
reachvex
Reachability-based CVE triage engine: proves whether your code reaches each vulnerable dependency function and emits OpenVEX / CycloneDX VEX evidence
- 2
- Python
- MIT
- 7 wk ago


web-security-hub
Open-source web security verification workspace: OWASP-aligned dynamic scanning, local static analysis, evidence-based OpenVEX drafts and an MCP server.
- 2
- TypeScript
- Apache-2.0
- 5 d ago
jvex
Java library for generating, consuming, and operating on OpenVEX documents
- 2
- Java
- Apache-2.0
- 3 y ago

