PayloadsAllTheThings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
- 83k
- Python
- MIT
- 3 wk ago
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
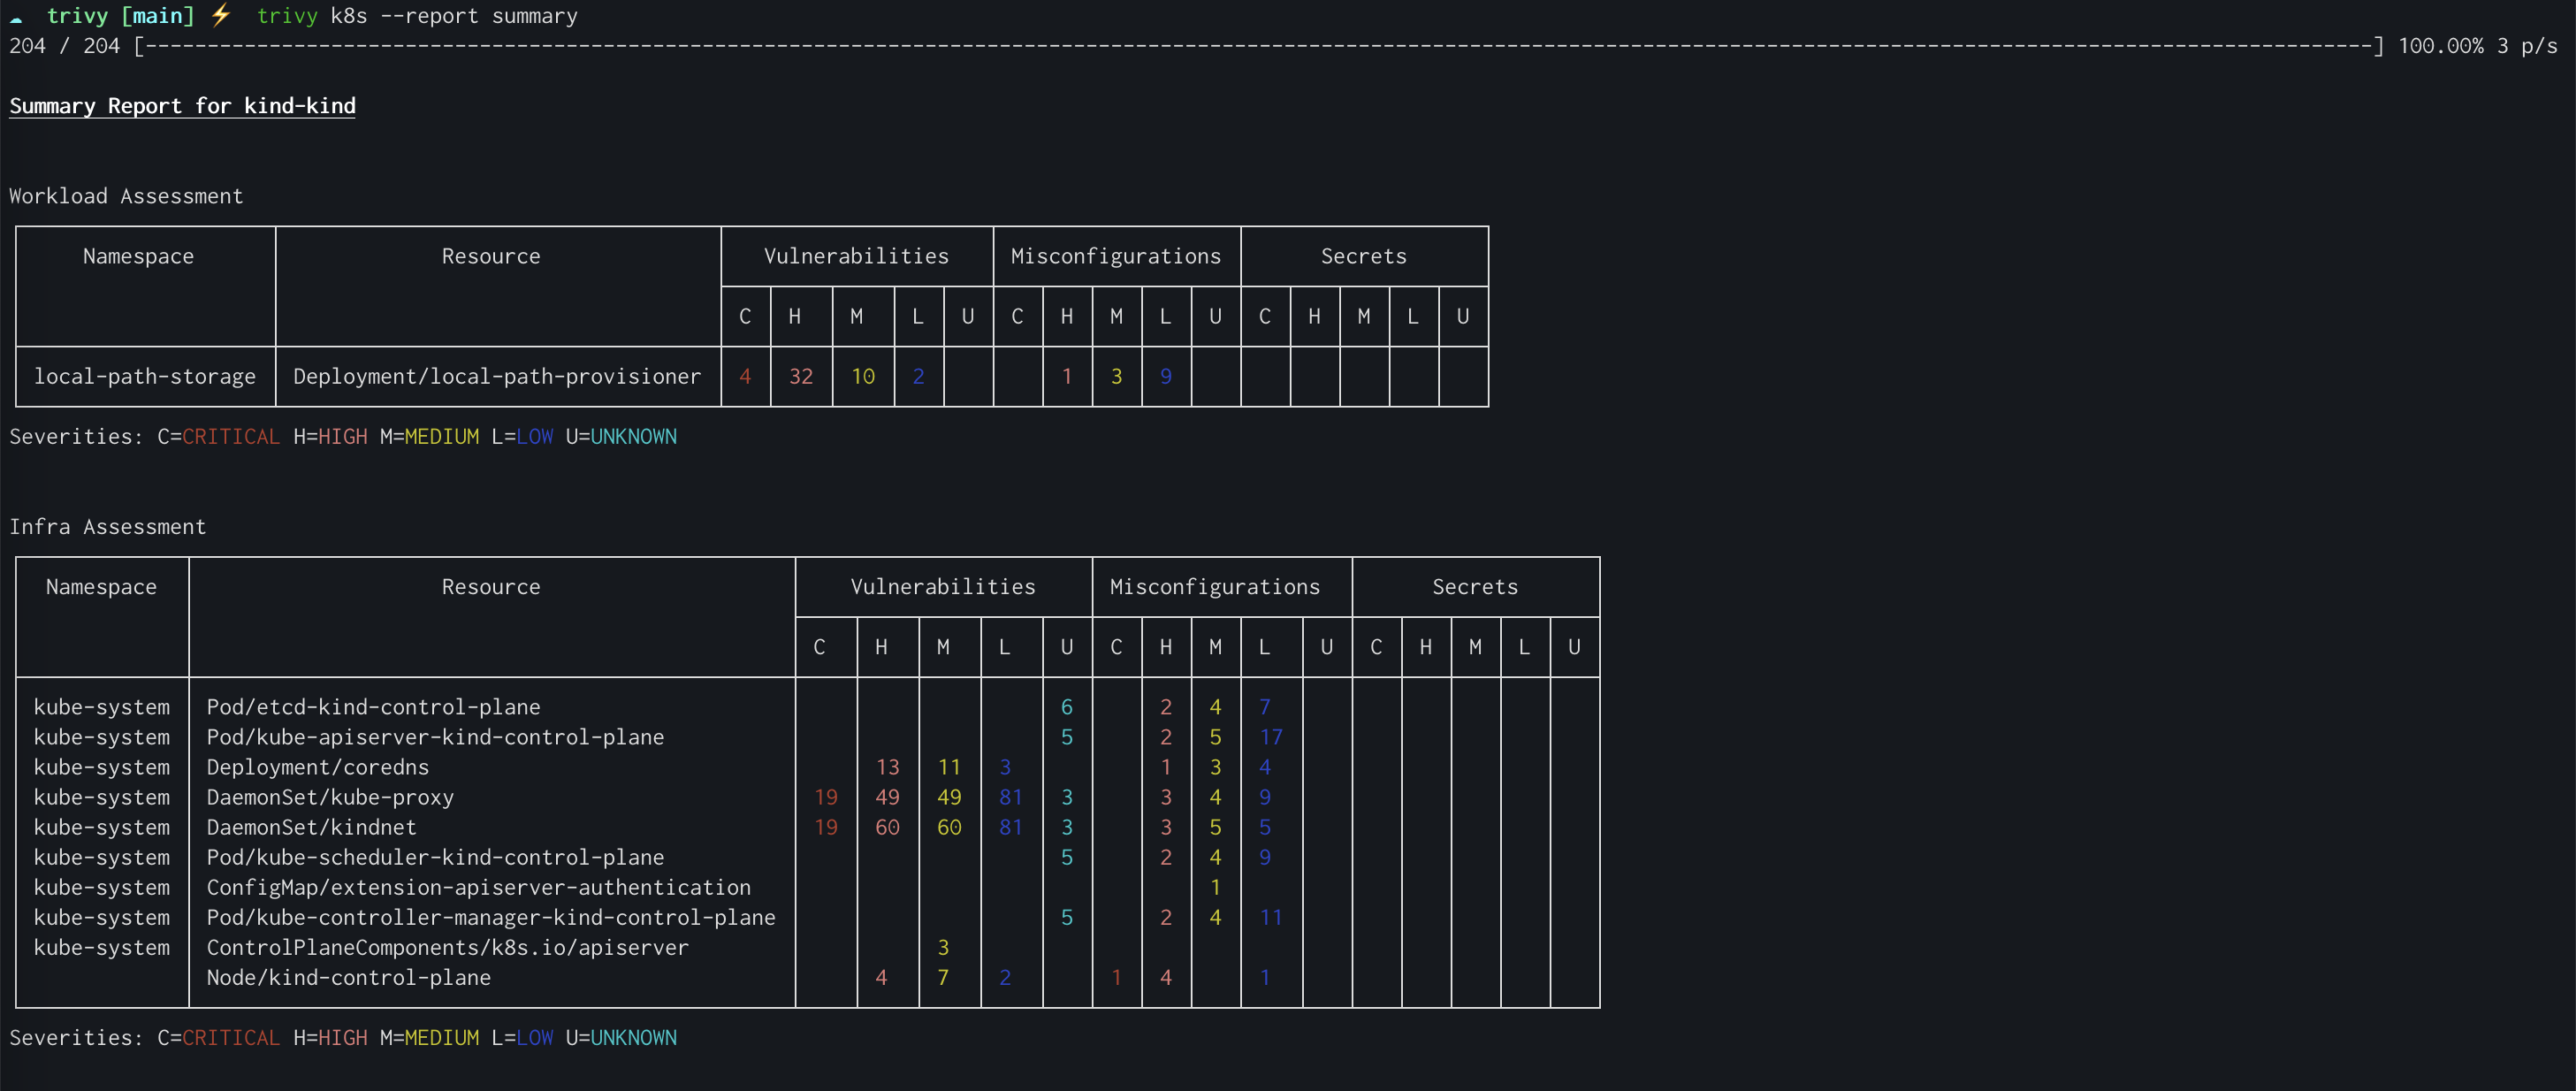
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
This repository is maintained by Omar Santos (@santosomar) and includes thousands of resources related to ethical hacking, bug bounties, digital forensics and incident response (DFIR), AI security, vulnerability research, exploit development, reverse engineering, and more. 🔥 Also check: https://hackertraining.org
SafeLine is a self-hosted WAF(Web Application Firewall) / reverse proxy to protect your web apps from attacks and exploits.
Source code for Hacker101.com - a free online web and mobile security class.
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
Collection of methodology and test case for various web vulnerabilities.
A phone number can reveal whether a device is active, in standby or offline (and more). This PoC demonstrates how delivery receipts + RTT timing leak sensitive device-activity patterns. (WhatsApp / Signal)
Penetration tests guide based on OWASP including test cases, resources and examples.
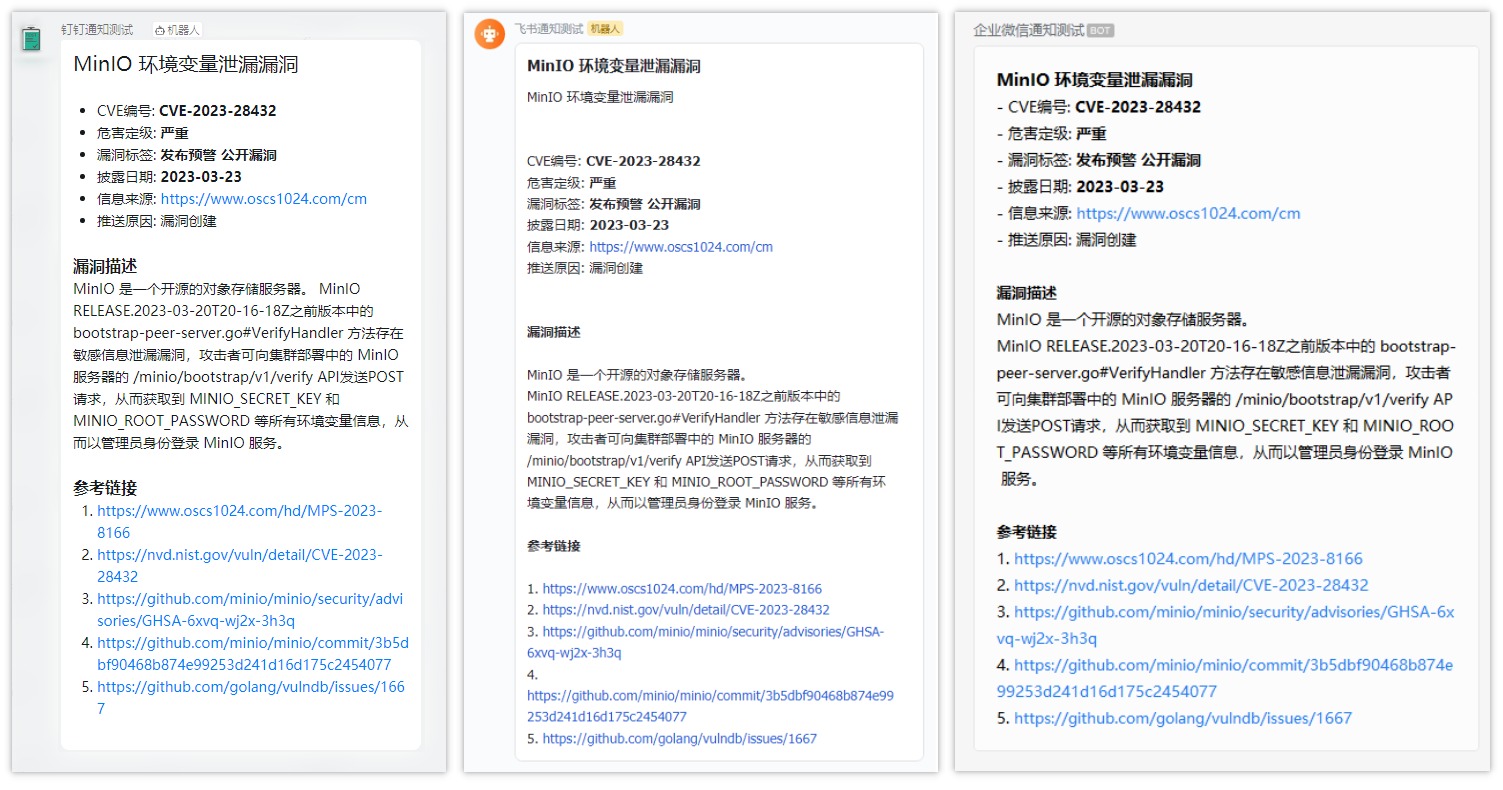
一个高价值漏洞采集与推送服务 | Collect valueable vulnerabilities and push them to various services
Appshark is a static taint analysis platform to scan vulnerabilities in an Android app.
Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.
Process Herpaderping proof of concept, tool, and technical deep dive. Process Herpaderping bypasses security products by obscuring the intentions of a process.
A laboratory for learning secure web and mobile development in a practical manner.
Vulnerability (CVE) scanner for Nix/NixOS [maintainer=@henrirosten]
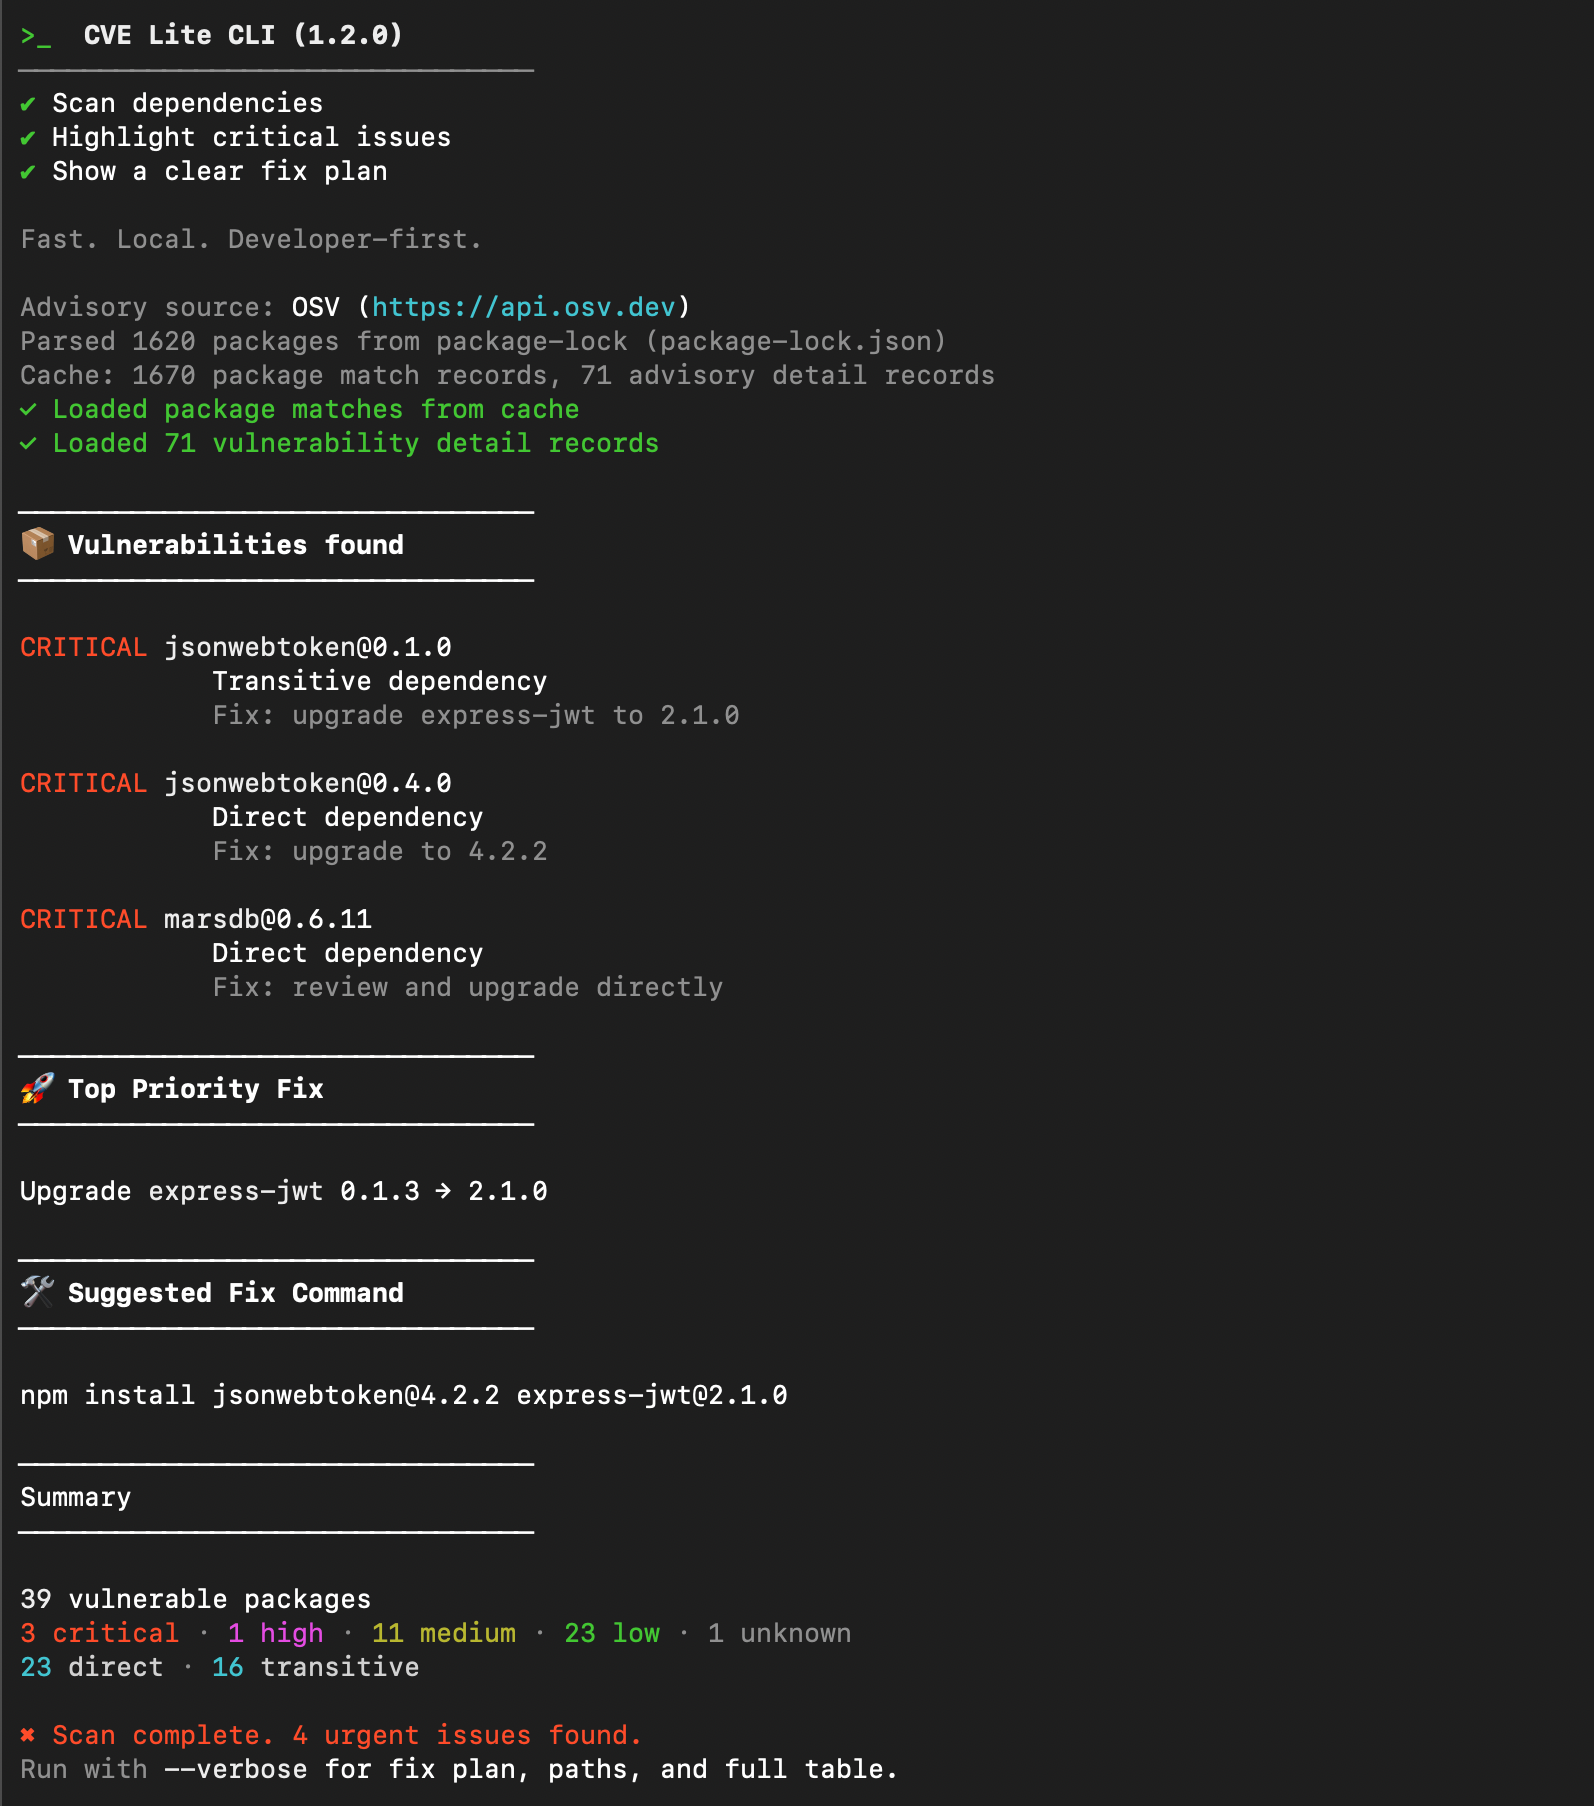
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix, JSON output, and practical remediation guidance.
Claude Code skill for OWASP security best practices (2025-2026). Includes Top 10:2025, ASVS 5.0, Agentic AI security, and 20+ language-specific security quirks.
✨ Purpose only! The dangers of Bluetooth Low Energy(BLE)implementations: Unveiling zero day vulnerabilities and security flaws in modern Bluetooth LE stacks.
Finds security holes in your Python projects from PyCharm and GitHub
Greenbone Security Assistant - The web frontend for the Greenbone Community Edition
Corax for Java: A general static analysis framework for java code checking.
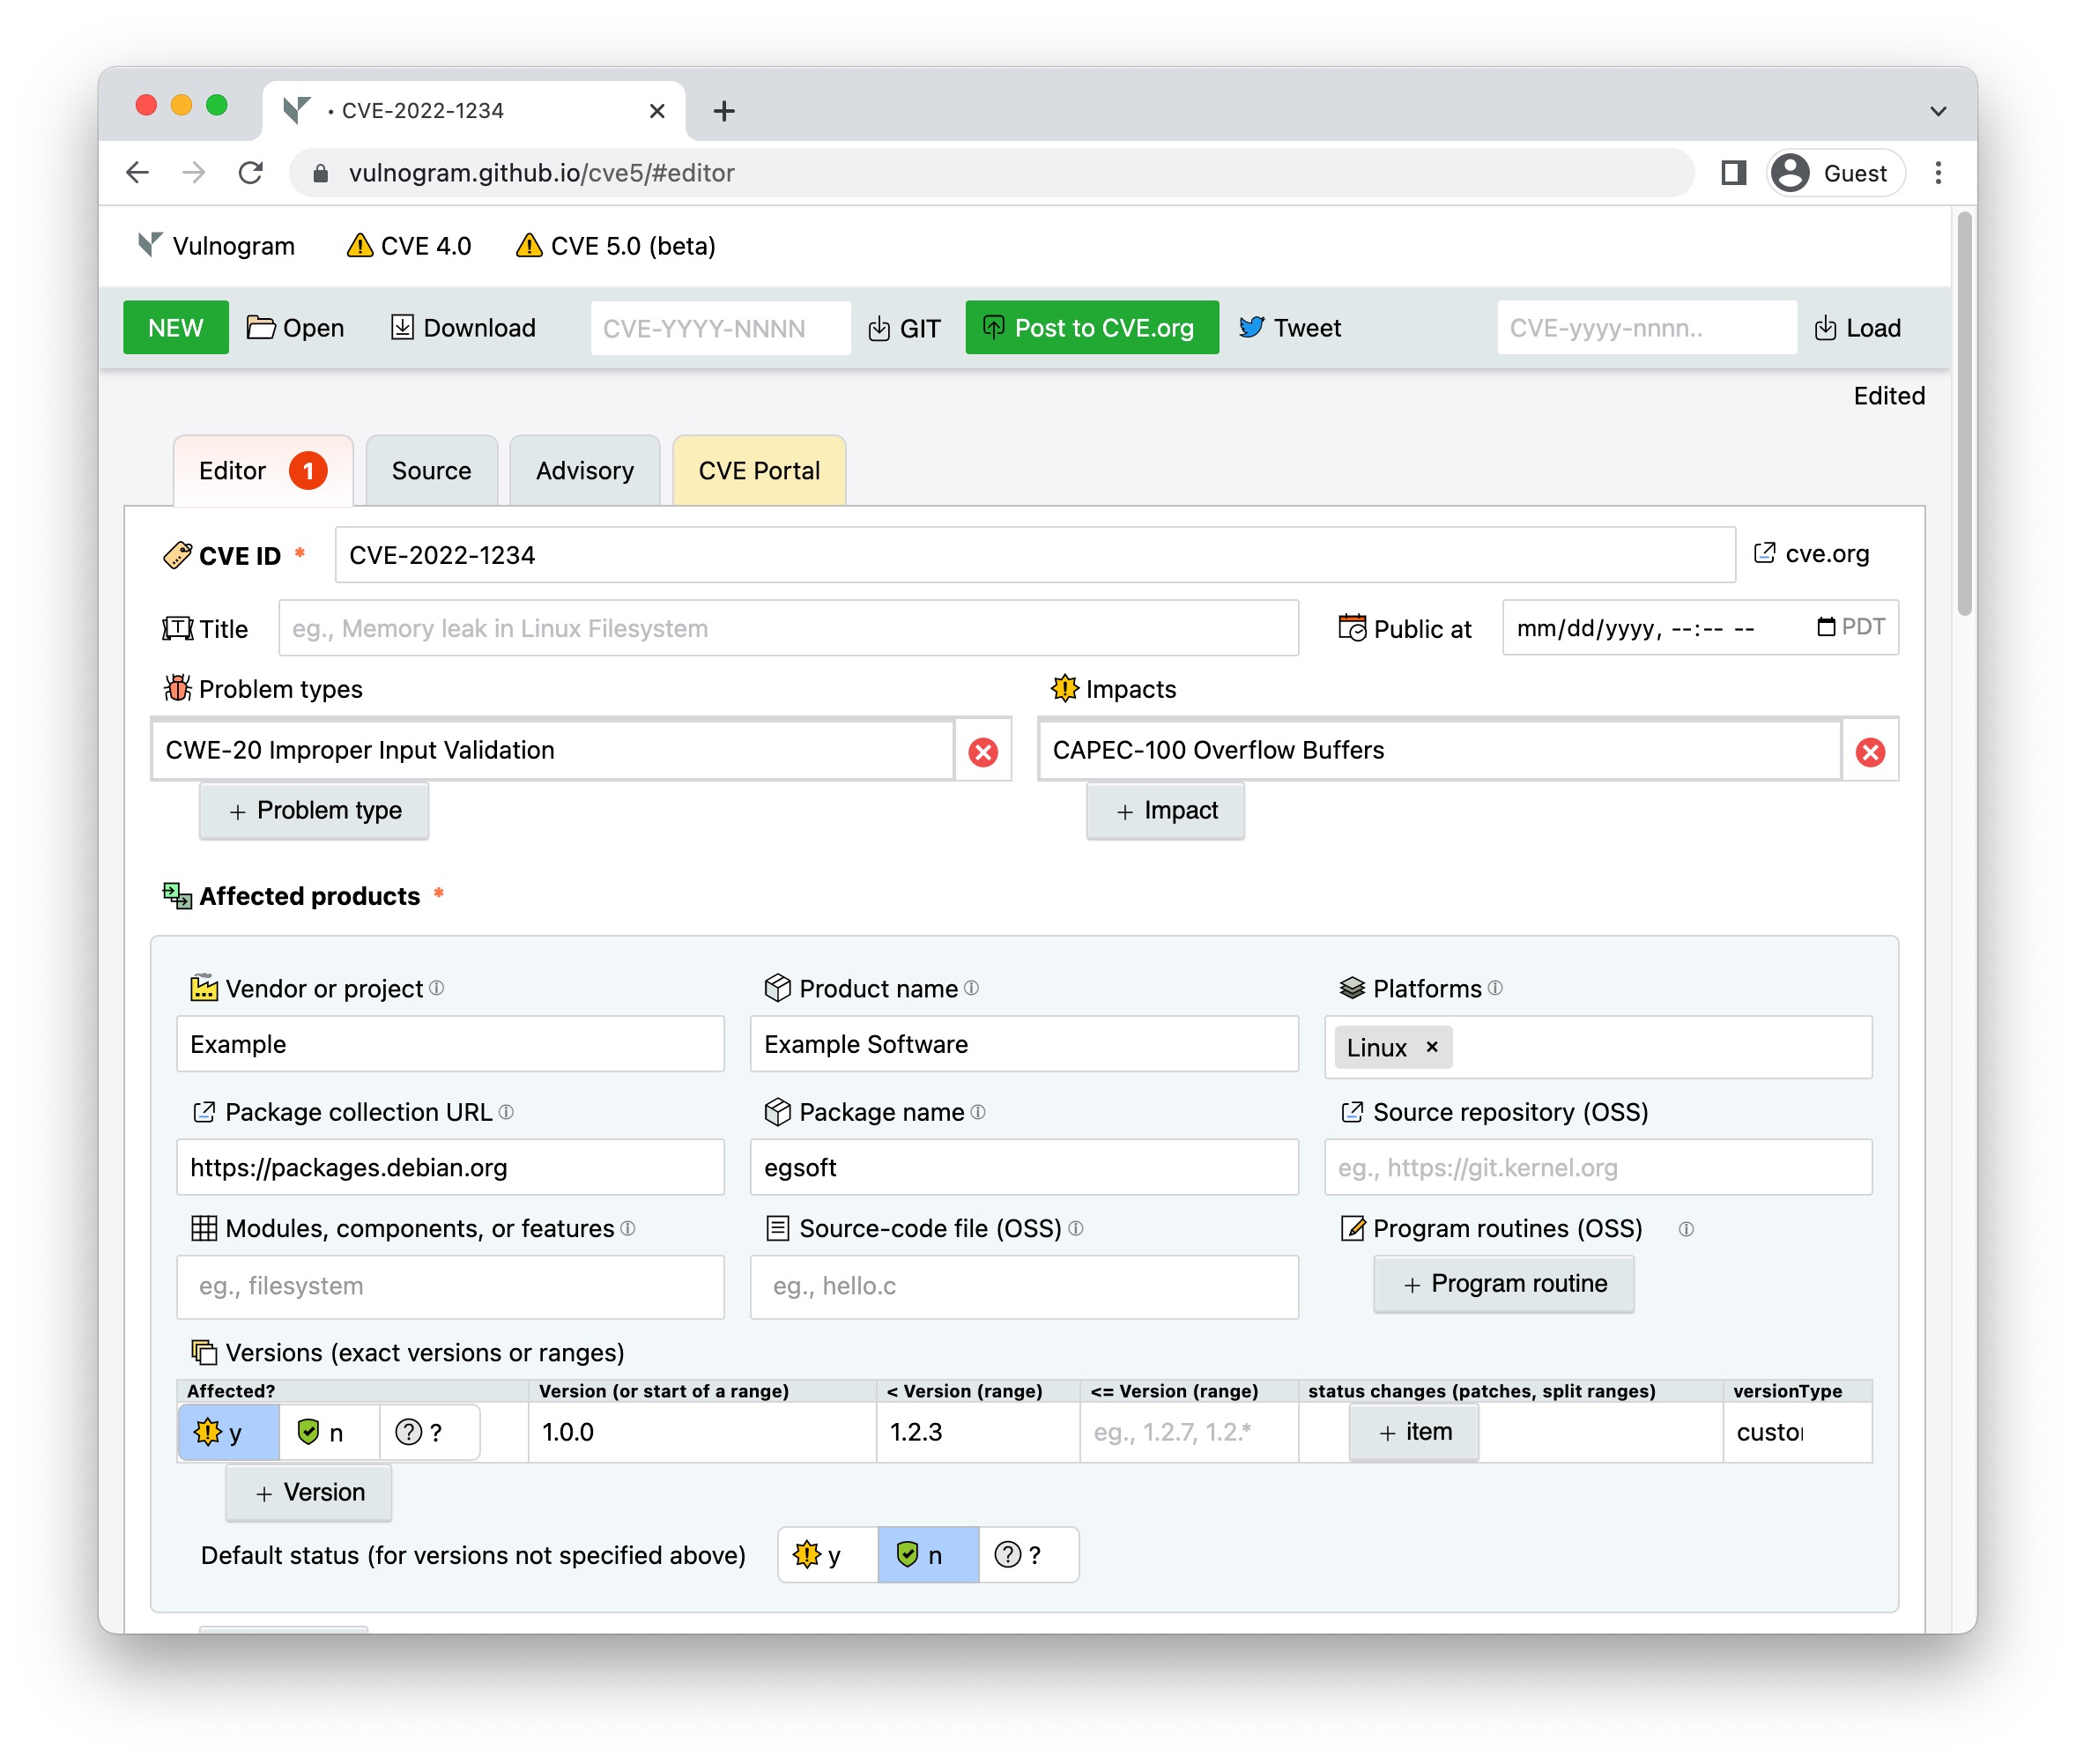
Vulnogram is the tool for reserving, managing, and publishing CVEs. Get started at vulnogram.org or deploy Docker edition for full enterprise features.
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to elevate vendor security standards and advance the field.
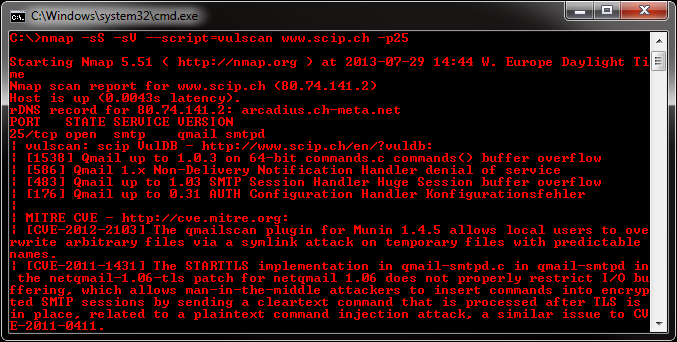
Nmap script that scans for probable vulnerabilities based on services discovered in open ports.
Docker labs + defensive scanner for fastjson remote-class-load RCE. fastjson 1.2.66-1.2.83: @JSONType resource probe (CVE-2026-16723). fastjson2 2.0.57: attacker @type reaches loadClass with autoType DISABLED via polymorphic types (@JSONType(seeAlso) / Jackson @JsonSubTypes). Marker-only payloads; safeMode + JDK17 controls.
Text classification model, used with transformers.
Text classification model, used with transformers.