exploit-kit

Open repos and models their makers tagged exploit-kit, most starred first. The same for everyone.

Websites and appsRepo

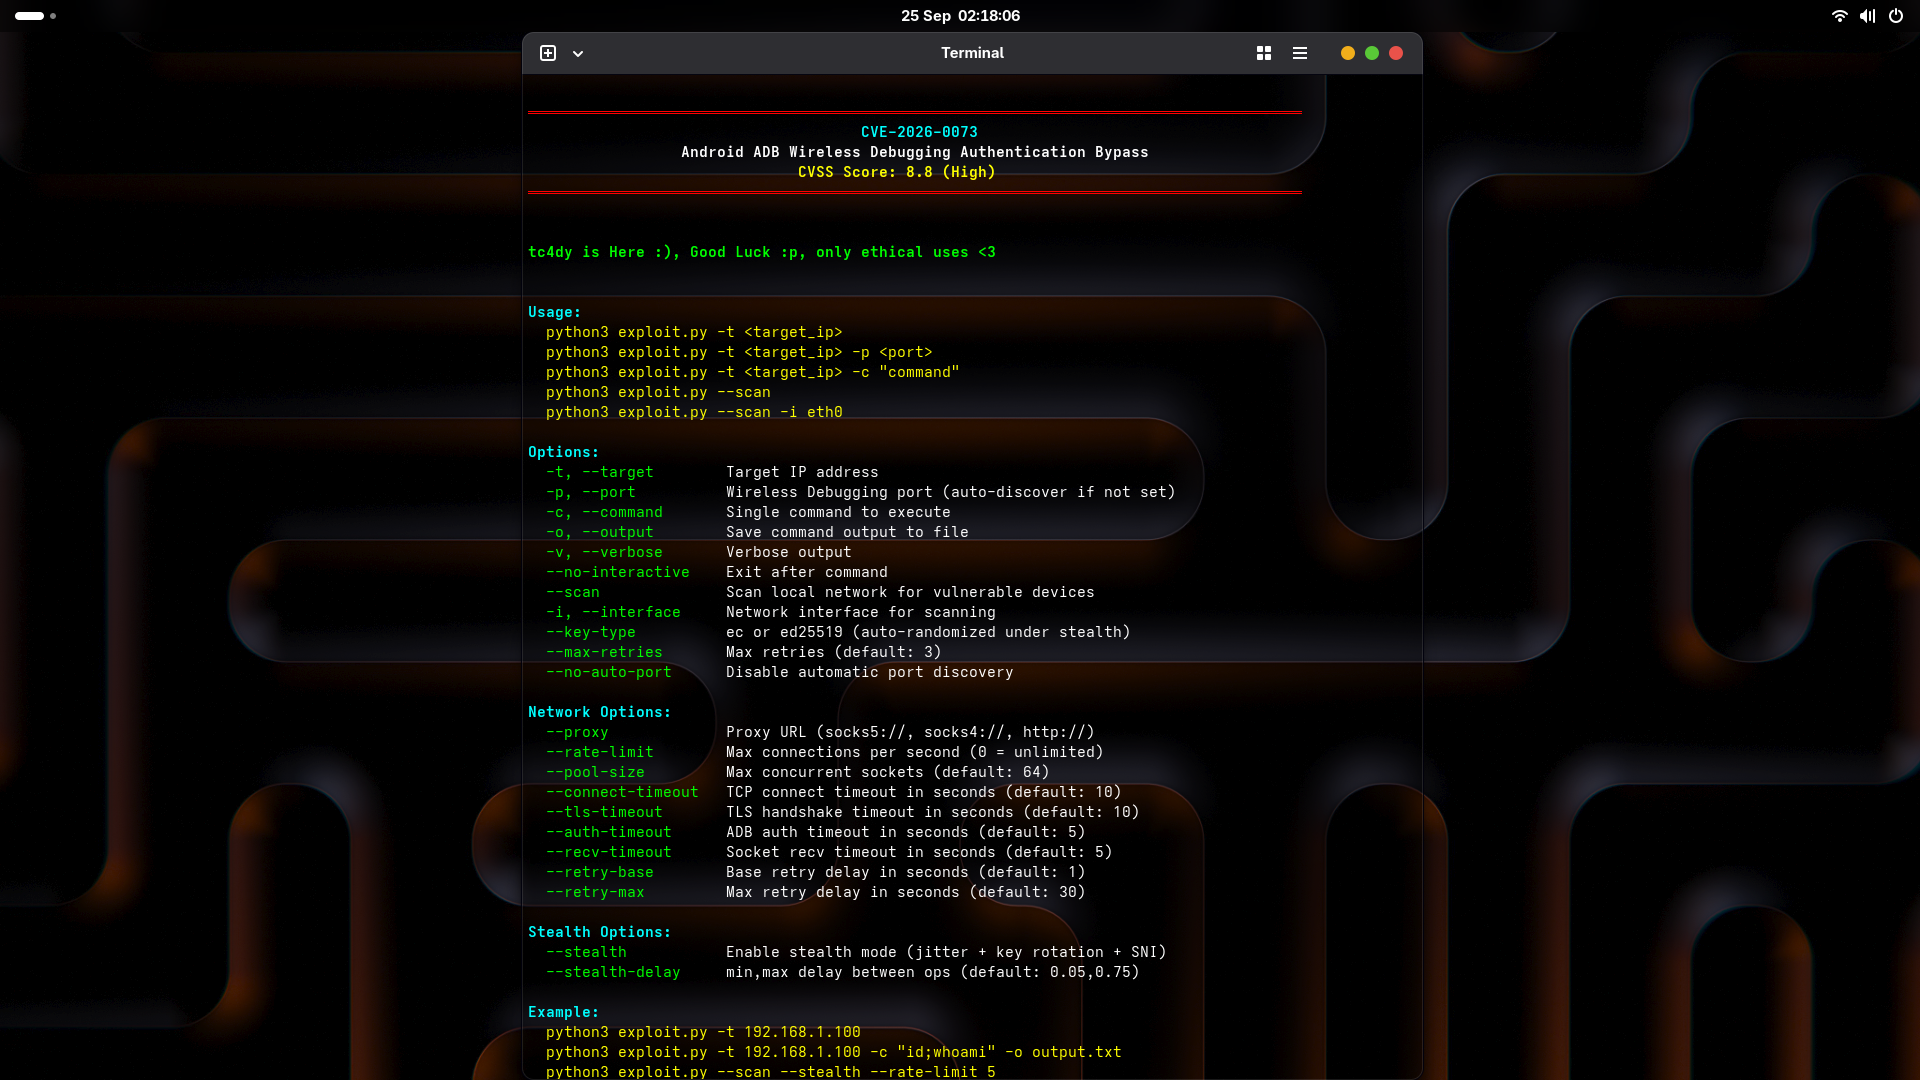
CVE-2026-0073-PoC-Exploit

CVE-2026-0073 – Android ADB Wireless Debugging Auth Bypass (CVSS 8.8) | Zero-click TLS type confusion to unauthenticated shell. 2 tools: Full Exploit (ADB shell, cmd exec, subnet scan, mDNS, stealth, SOCKS5) & SafeDetect (non-intrusive audit, CIDR, JSON/CSV/HTML). Red/Blue team toolkit. Ethical & Safety use only.

  • 17
  • Python
  • MIT
  • 22 h ago
tc4dyTake it
GitHubRepo

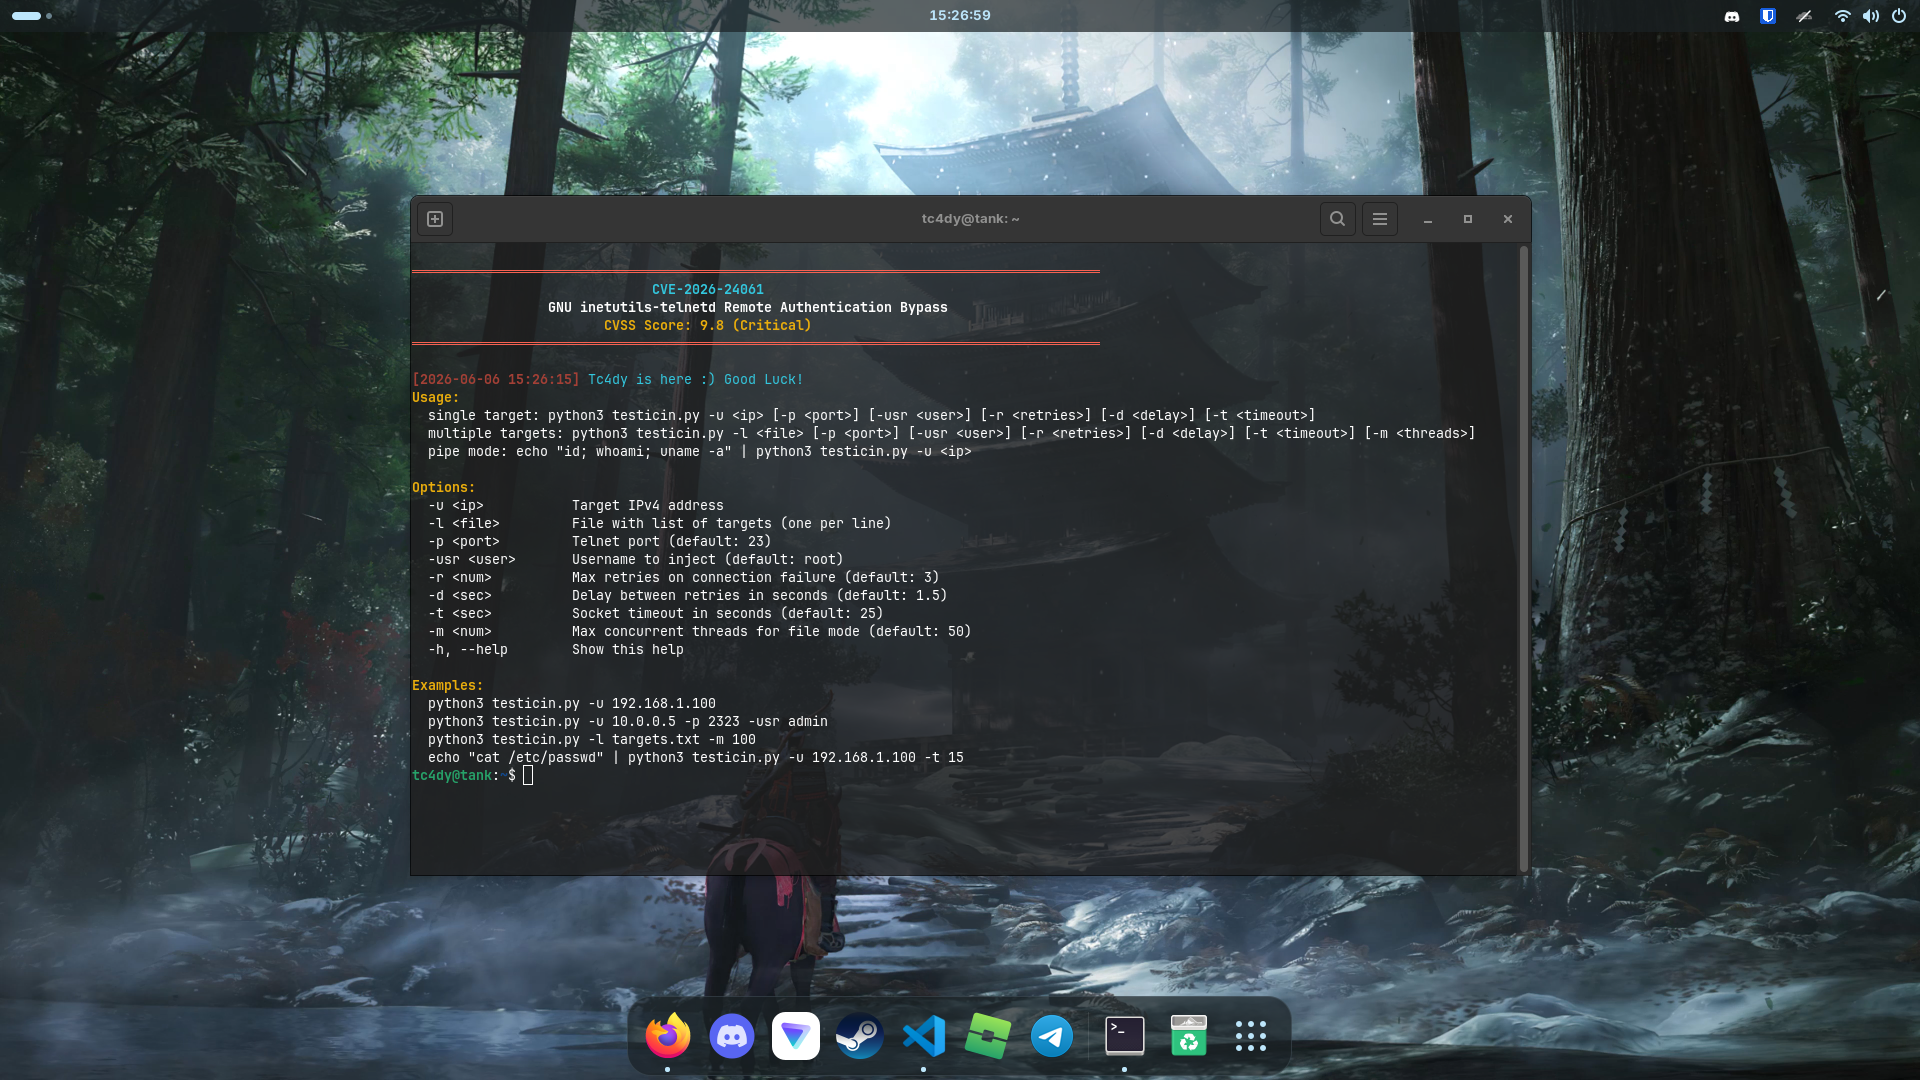
CVE-2026-24061-PoC-Exploit

CVE-2026-24061 - GNU inetutils-telnetd Auth Bypass Exploit - Full Control with CRLF injection via NEW_ENVIRON leads to auth bypass & instant root shell. Single/Mass exploitation, multi-threading, custom port/user, pipe mode, session keep-alive, colored output, retries, timeout support. Python & Bash versions. Critical CVSS 9.8.

  • 9
  • Shell
  • GPL-3.0
  • 5 d ago
tc4dyTake it
GitHubRepo

CVE-2026-106173-PoC-Exploit

CVE-2026-106173 – FortiSIEM phQueryMaster RCE (CVSS 9.8) | Red/Blue Team suite for unpatched FortiSIEM 7.5.0. 2 tools: Full Exploit (multi-primitive RCE, reverse shell, persistence, creds, readback, mass scan, Tor), Blue Team Checker (exposure detection, HTTP/2 fingerprint, reporting, audit). Only Use Ethically, Stay Legal <3

  • 6
  • Python
  • MIT
  • 4 wk ago
tc4dyTake it
GitHubRepo

CVE-2026-82329-PoC-Exploit

CVE-2026-82329 – JFrog Artifactory Auth Bypass Toolkit (CVSS 9.8) | Red/Blue Team suite for self-hosted Artifactory 7.x (111-161). 2 tools: Full Exploit (JWTforge, admin token, user create, mass scan, stealth, interactive menu, resistence, WAF bypass etc.), SafeChecker (version detect, audit, JSON report). 🦾 Use Ethically, Stay Legal :V

  • 5
  • Python
  • MIT
  • 6 wk ago
tc4dyTake it
Search GitHub and Hugging Face for exploit-kit

Get , open it once and sign in. Then come back here and press the button again.

exploit-kit: open source repos and models on Take My Repo