SafeLine
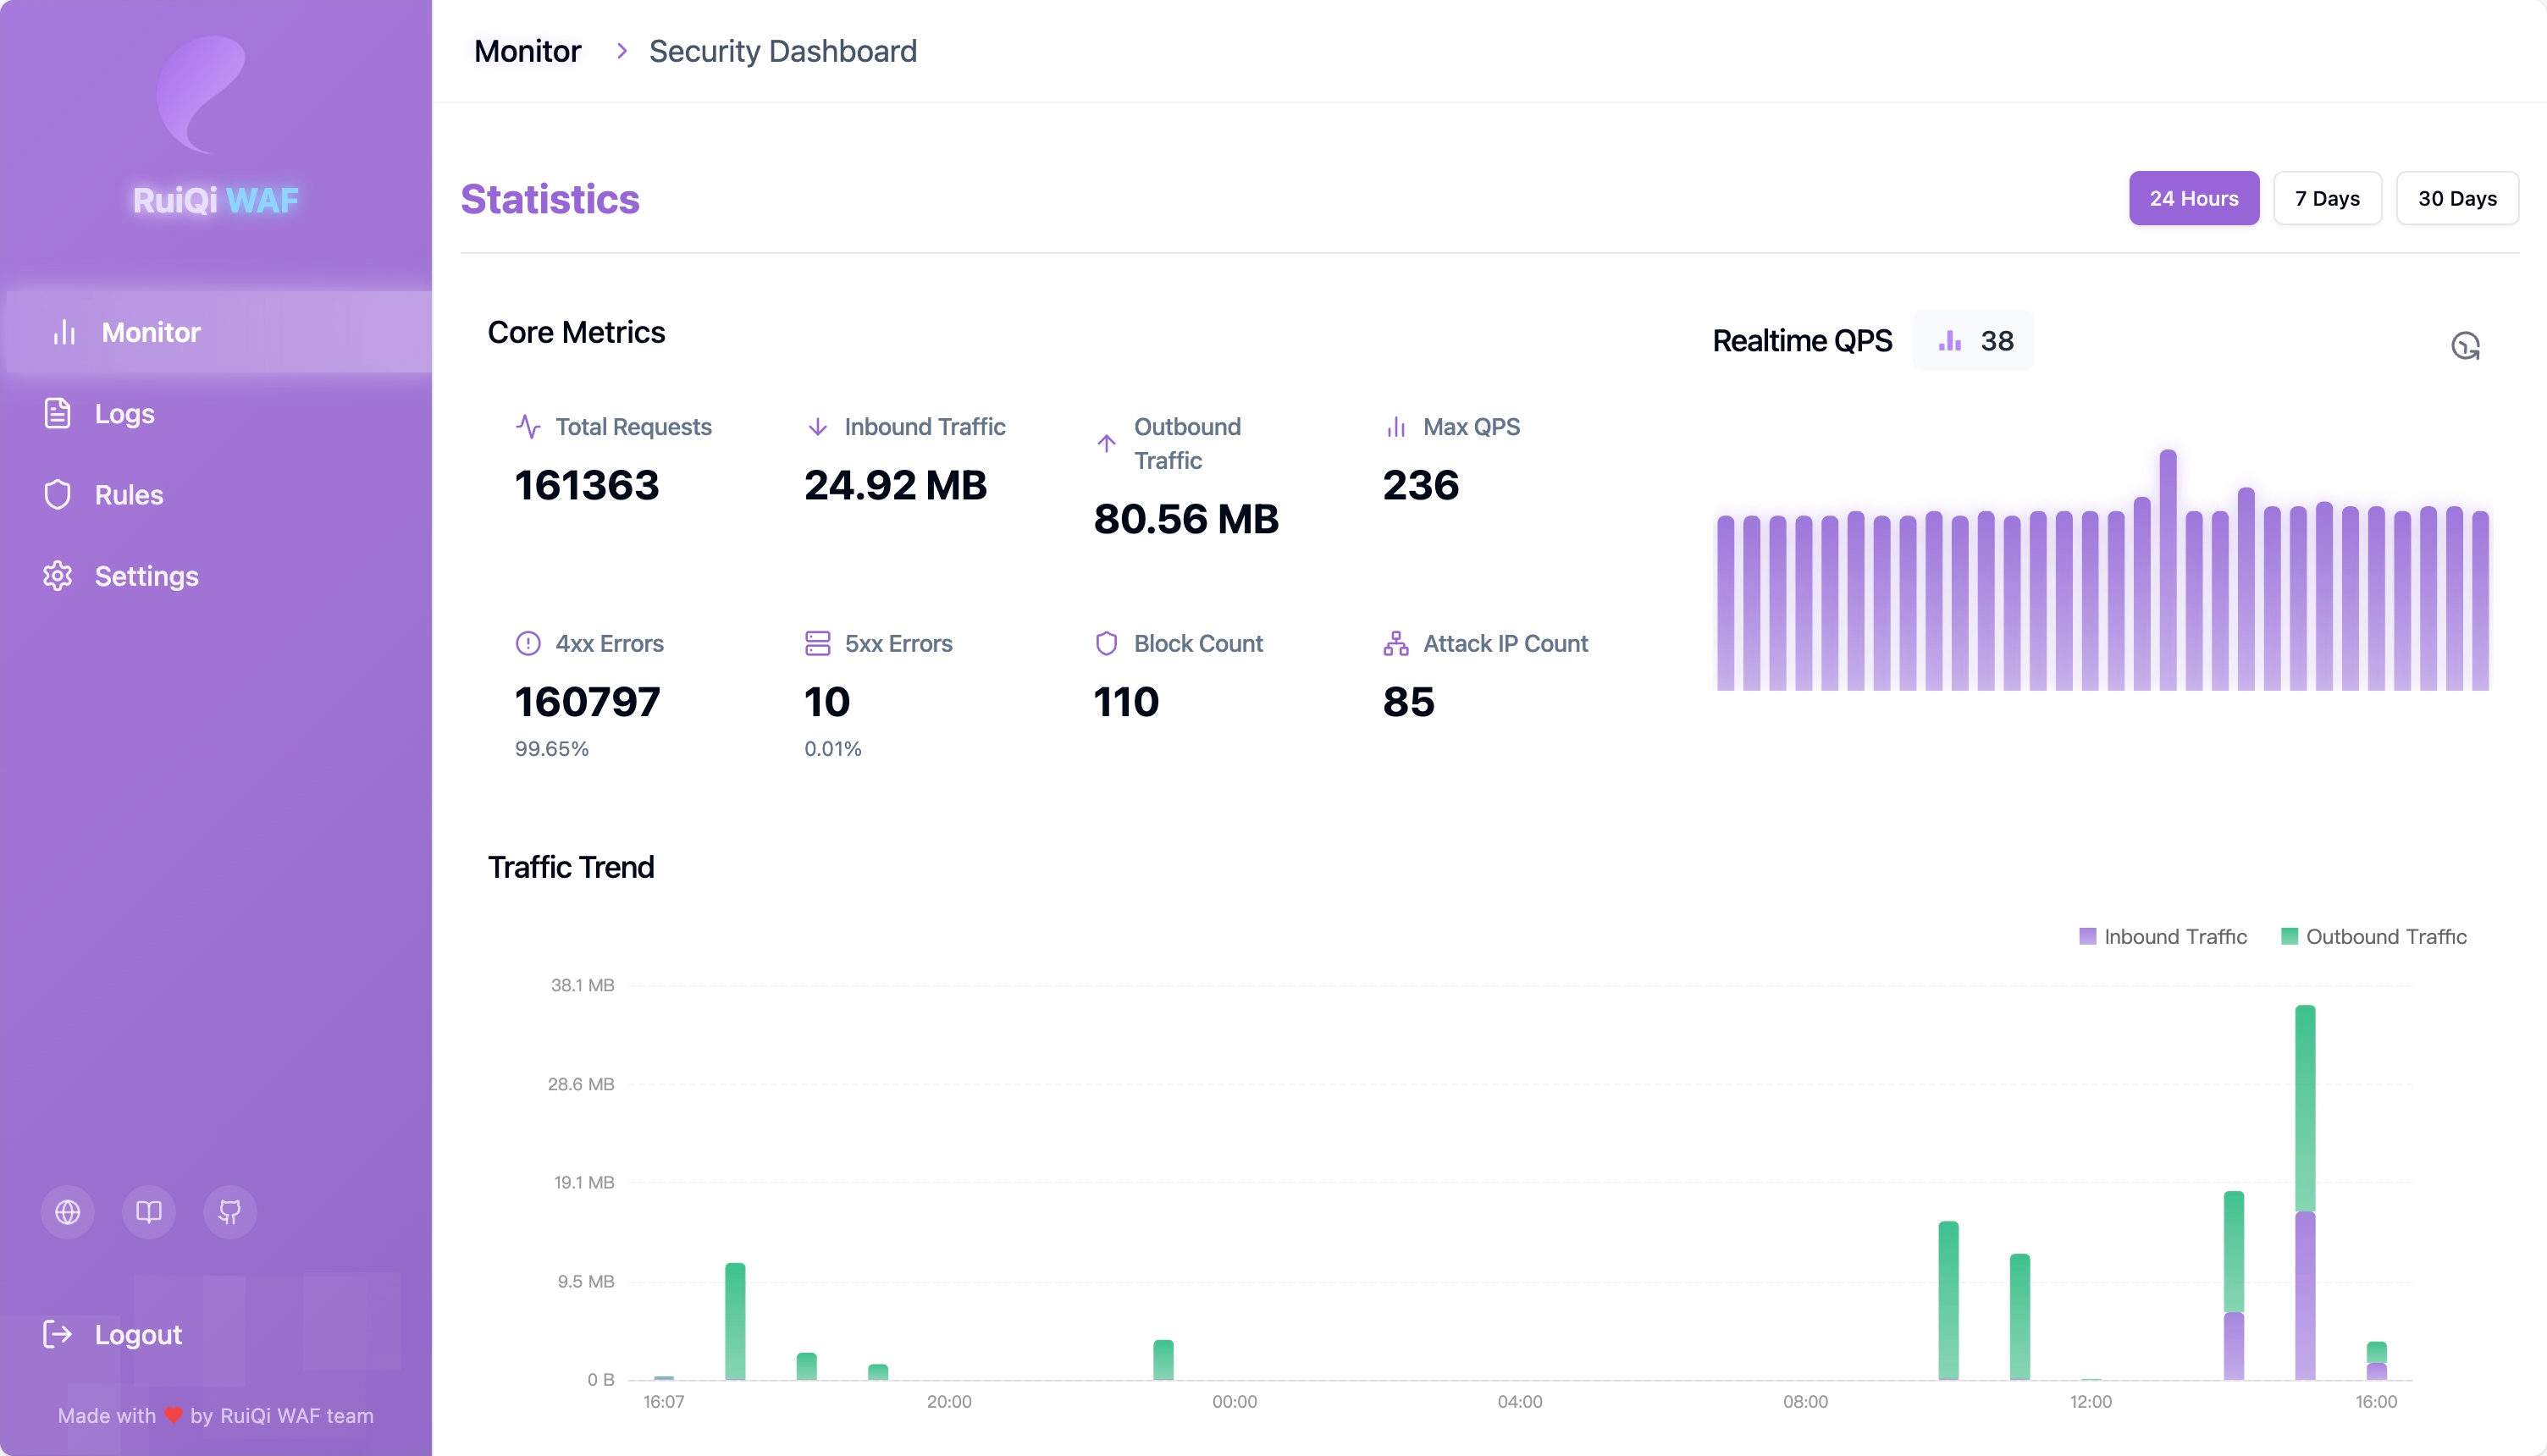
SafeLine is a self-hosted WAF(Web Application Firewall) / reverse proxy to protect your web apps from attacks and exploits.
- 23k
- Go
- GPL-3.0
- 9 d ago
SafeLine is a self-hosted WAF(Web Application Firewall) / reverse proxy to protect your web apps from attacks and exploits.
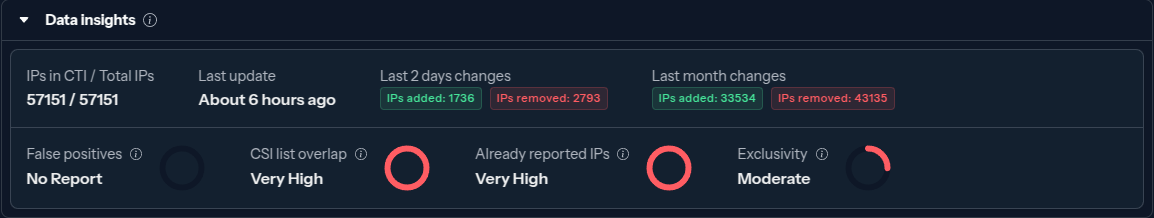
Open-source IDS/IPS, WAF and bot detection for Linux, Windows, Docker and Kubernetes, with a crowdsourced blocklist of malicious IPs.
My simple Swiss Army knife for http/https troubleshooting and profiling.
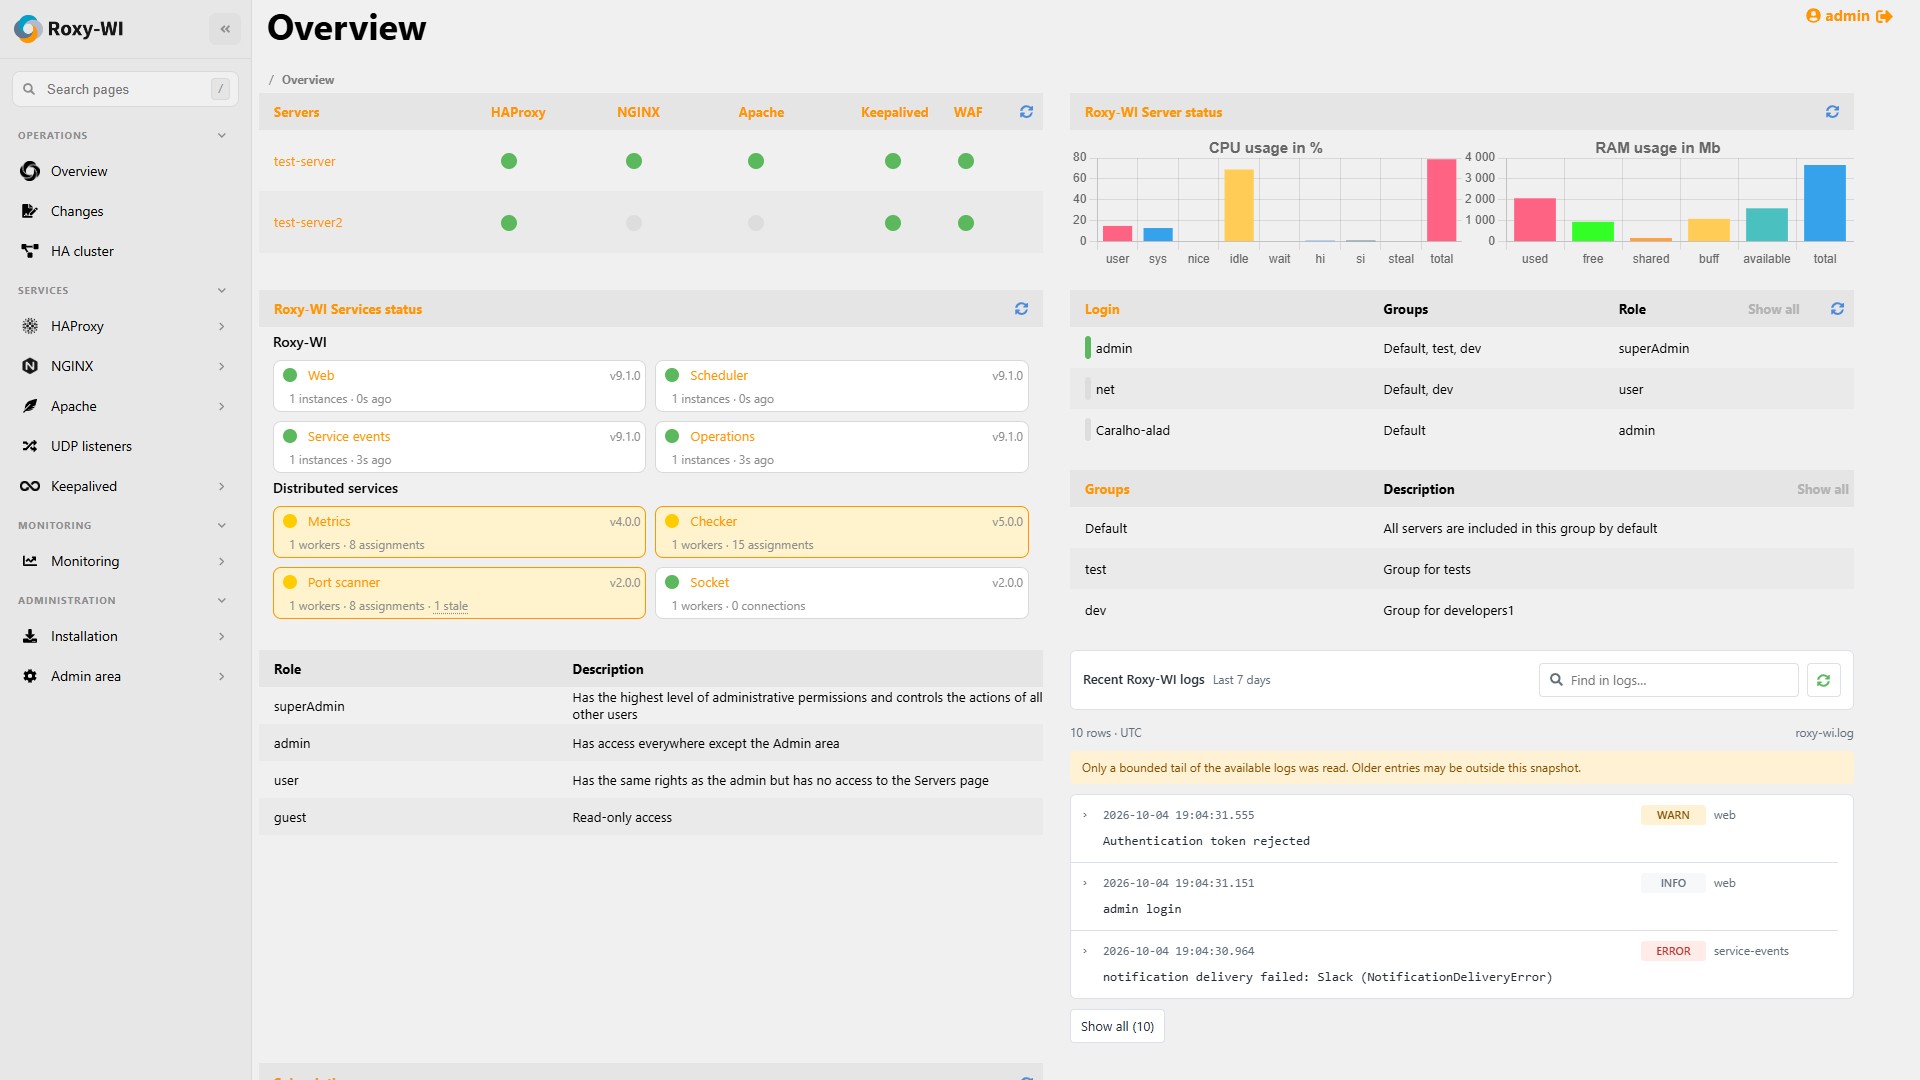
Web interface for managing Haproxy, Nginx, Apache and Keepalived servers
Modified source engine (2017) developed by valve and leaked in 2020. Not for commercial purporses
Industry-leading free, high-performance, AI and semantic technology Web Application Firewall and API Security Gateway (WAAP) - UUSEC WAF.
A collection of bash shell scripts for automating various tasks with Amazon Web Services using the AWS CLI and jq.
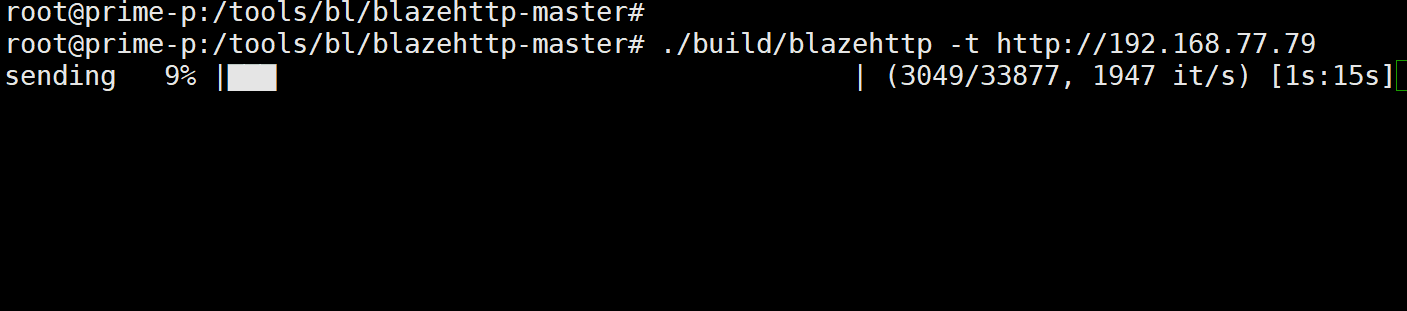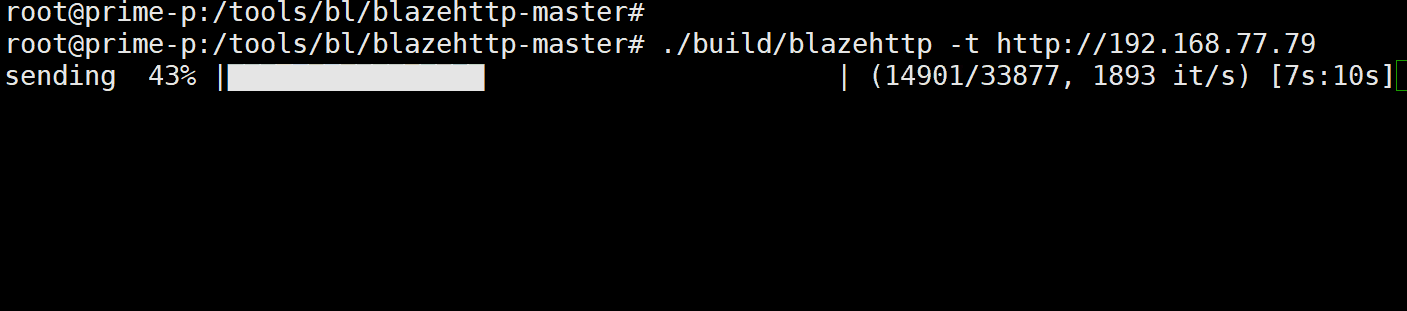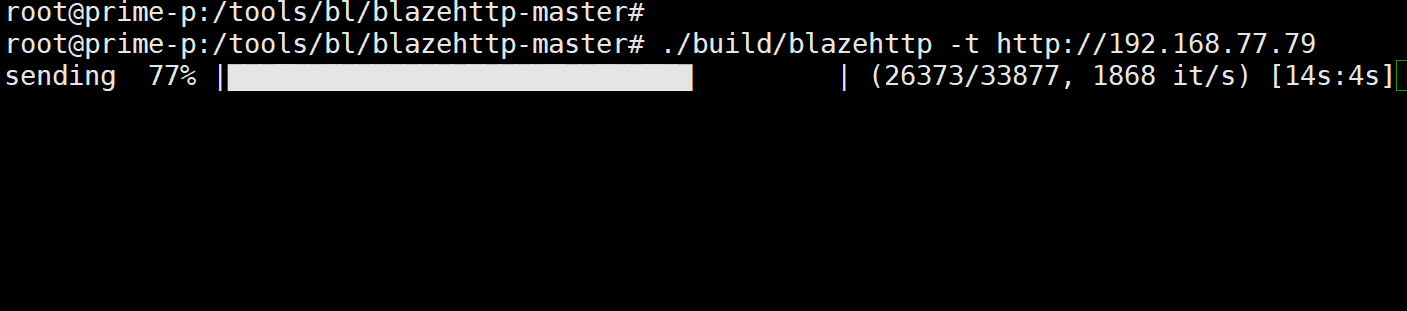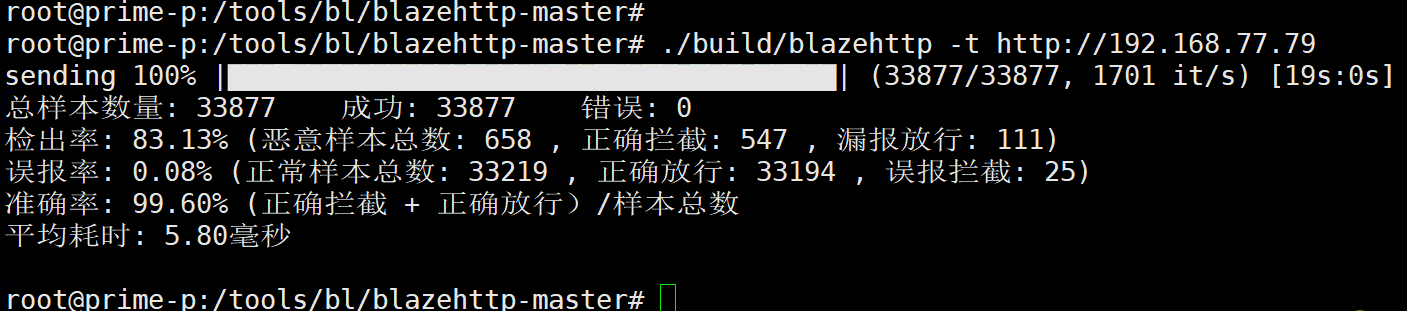
BlazeHTTP 是一款简单易用的 WAF 防护效果测试工具。BlazeHTTP stands as a user-friendly WAF protection efficacy evaluation tool.
Caddy WAF (Regex Rules, IP and DNS filtering, Rate Limiting, GeoIP, Tor, Anomaly Detection)
🔥 A curated list of awesome links related to application security related to the environments with NGINX or Kubernetes Ingres Controller (based on NGINX)
Compile NGINX from source with custom modules and patches on Debian and Ubuntu
Self-hosted gateway with a web UI: reverse proxy, automatic HTTPS, DDNS, NAT traversal, WAF and fail2ban-style bans in one binary.
Automated OWASP CRS and Bad Bot Detection for Nginx, Apache, Traefik and HaProxy
Next-Gen Distributed Reverse Proxy & Edge Security Gateway for OpenResty / Nginx
Check Risk WAF is an all-in-one Web Application Firewall with Anti-Bot and Anti-DDoS protection at L3, L4, and L7. Available on-premises or as SaaS, it protects web apps against OWASP Top 10 attacks, CWE vulnerabilities, botnets, and DoS/DDoS. Free and unlimited for everyone, forever for personal, non-commercial use.
Cloudflare WAF (Web Application Firewall) rules with a script for automatic updates. Block unwanted and malicious requests to improve the security of your origin server. The solution also supports integration with SniffCat and AbuseIPDB.
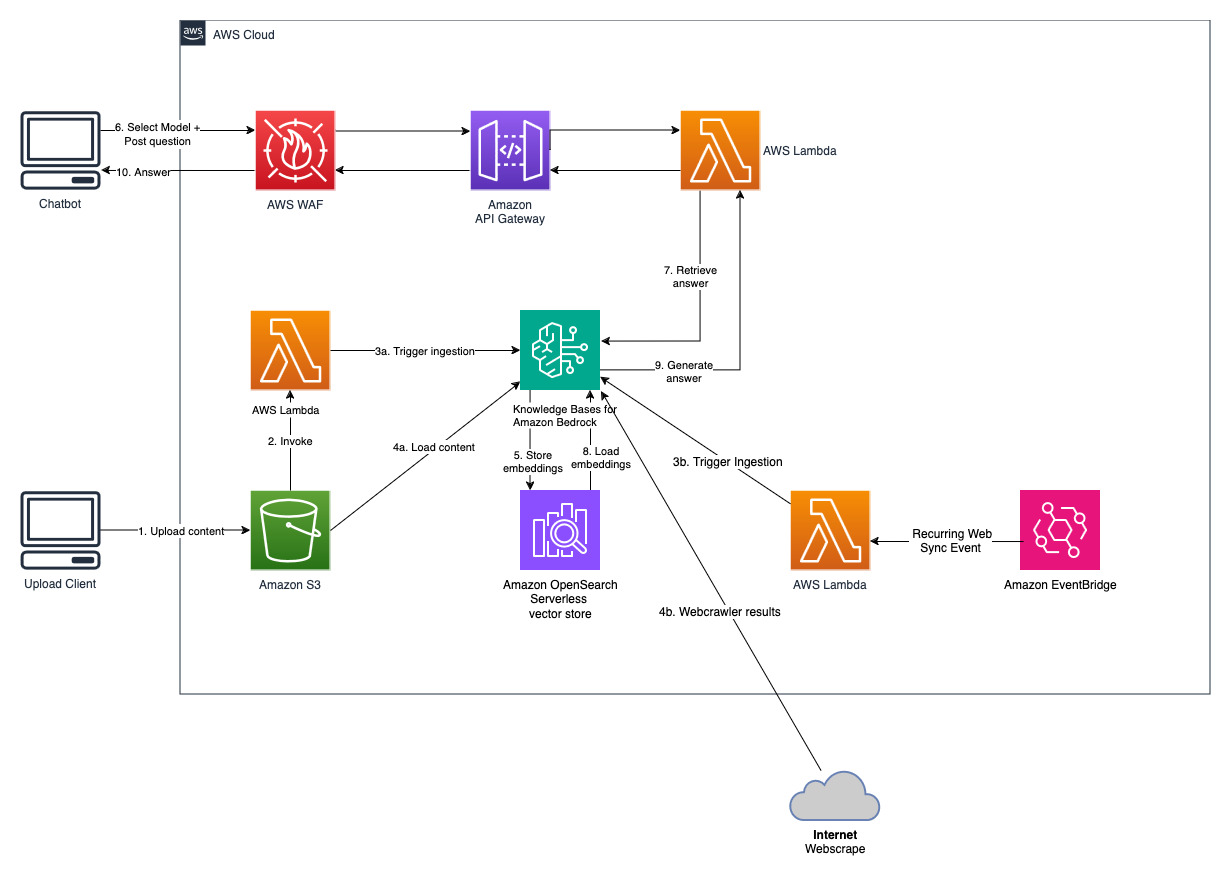
Fully managed RAG solution implemented using Knowledge Bases for Amazon Bedrock
A modern web application firewall (WAF) management system built on top of HAProxy and OWASP Coraza WAF with the Coraza SPOA integration. This system provides a comprehensive backend API for managing HAProxy configurations, Coraza WAF rules, and traffic inspection.
Lua implementation of the T1K protocol for Chaitin/SafeLine WAF
Apply design thinking to build and ship your software securely and at scale with GitHub
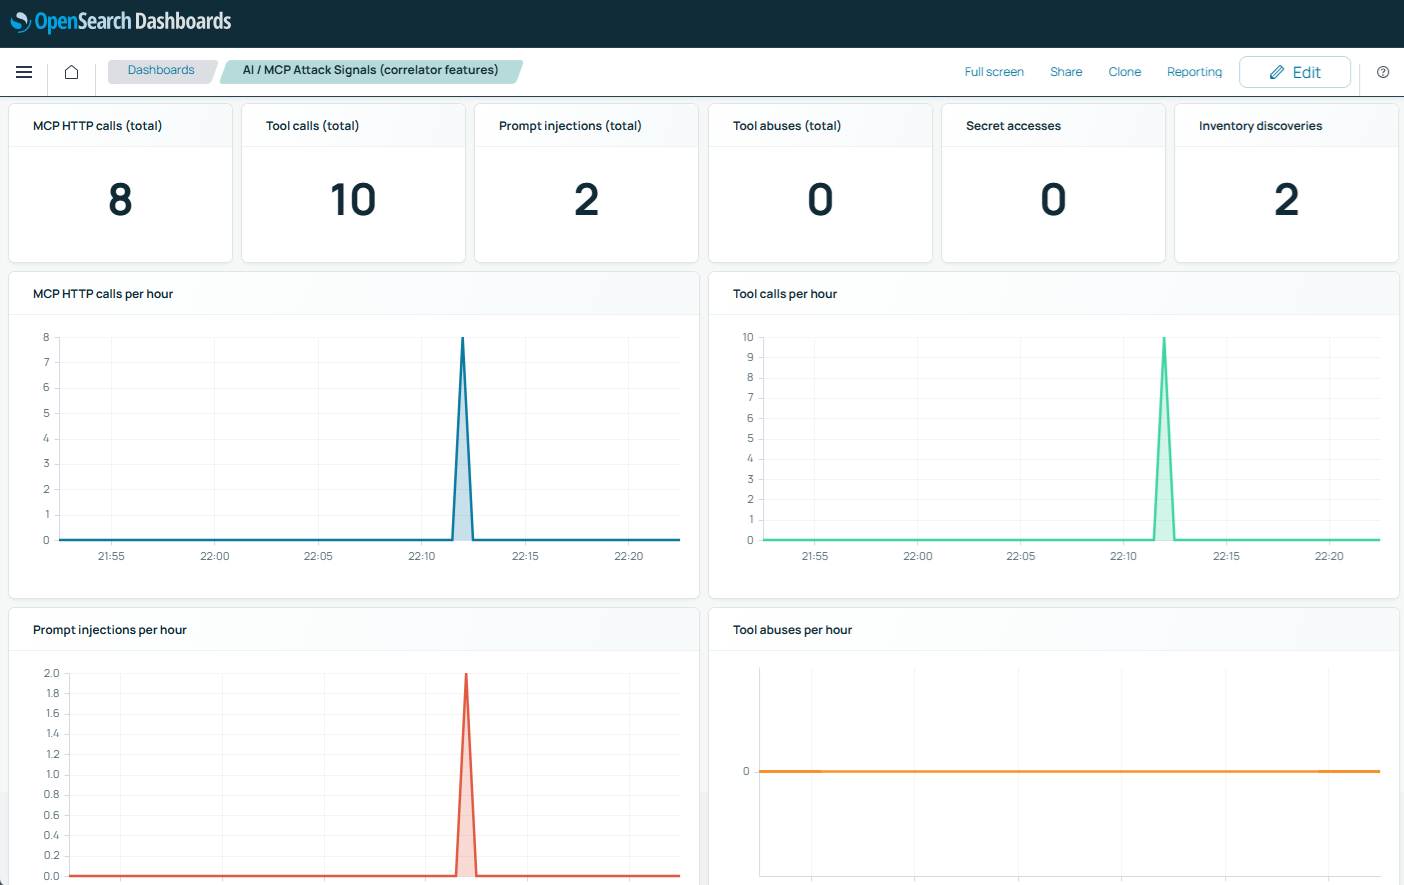
Collector/Correlator, Embedded log-based WAF, AI Patterns Classifier
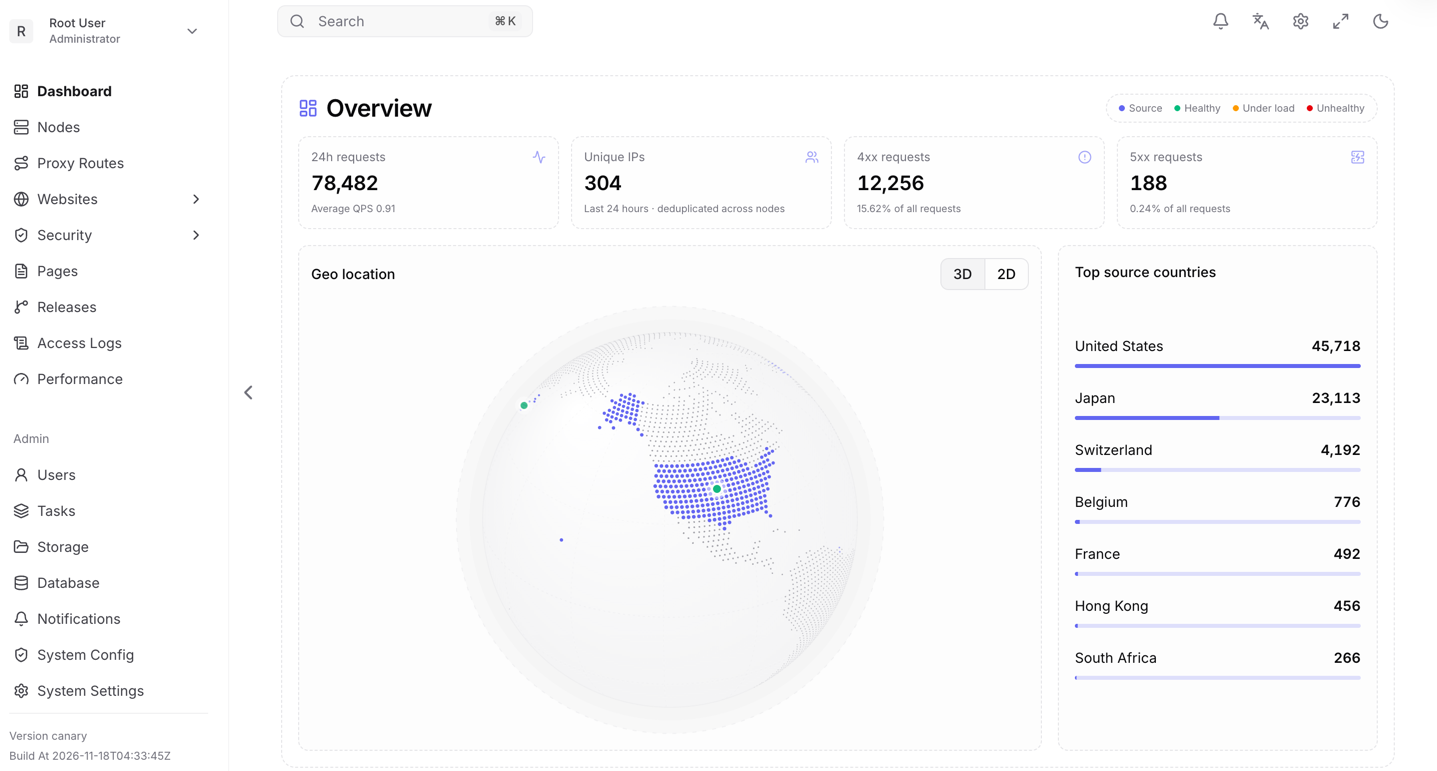
Distributed, centrally-controlled Web Application Firewall built on pingap & Cloudflare Pingora. Semantic attack detection, Cloudflare-style rules, CC & Bot defense, automatic TLS, embedded i18n dashboard.
Detect antibot protection from 30+ providers — Cloudflare, Akamai, DataDome, PerimeterX, and more.
Mimicry is a dynamic deception tool that actively deceives an attacker during exploitation and post-exploitation.
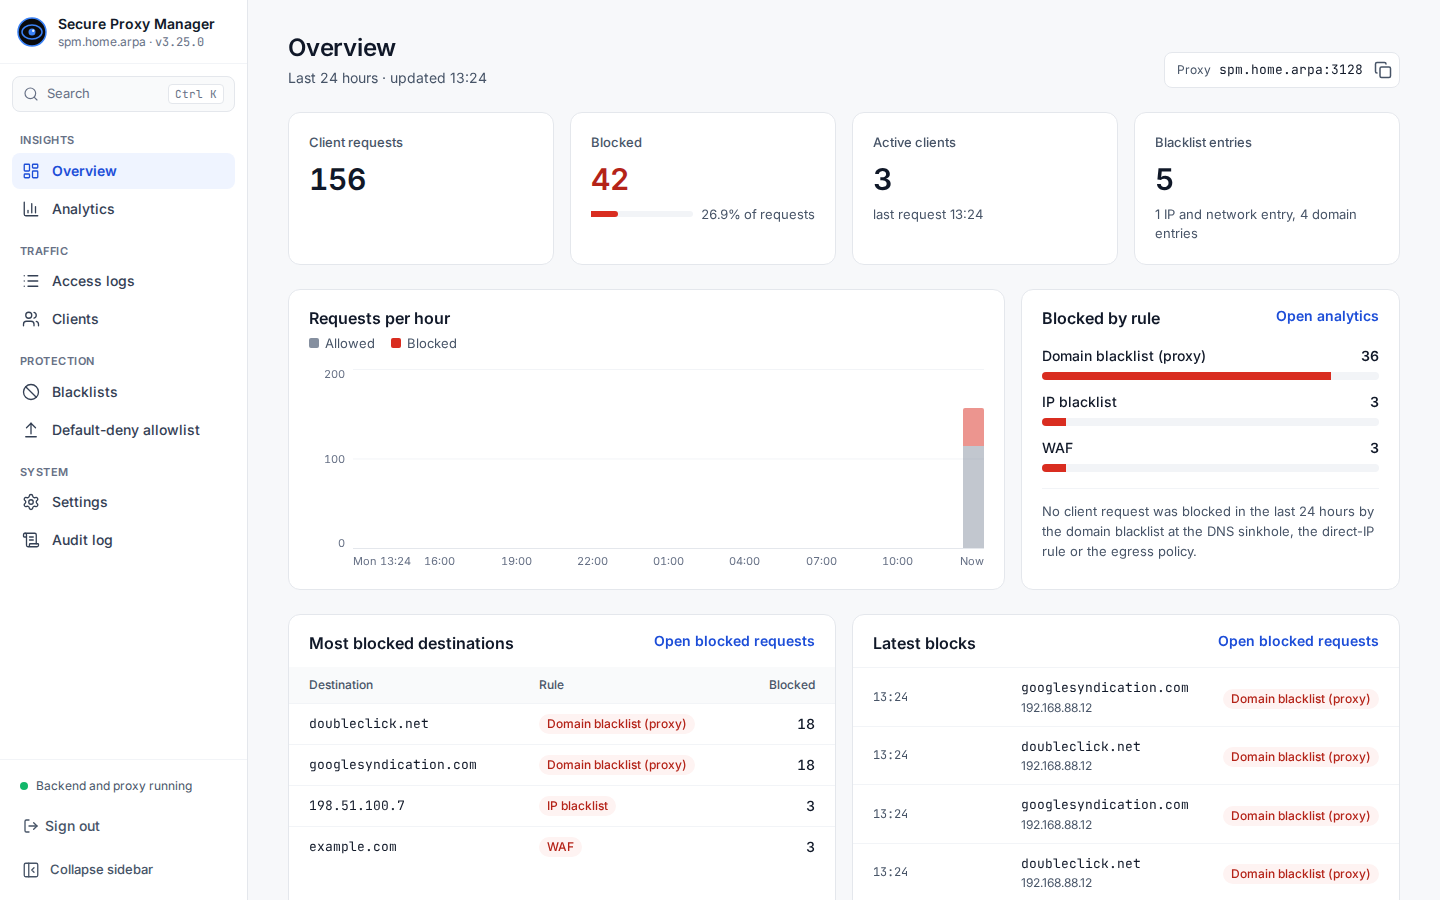
Secure proxy solution with filtering, real-time monitoring and a modern web UI.
These are automated updated IP address blacklist/whitelist you can use to fetch and parse and put in your firewall, waf, null-routing, sinkhole or what ever you choose. The blacklists are not necessary threat actors, it's just lists i like to have ready and handy.