wazuh
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints and cloud workloads.
- 18k
- C++
- 1 d ago
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints and cloud workloads.
Production-grade MCP server for Wazuh SIEM — 55 security tools for alert triage, threat hunting, vulnerability management, compliance (PCI DSS, GDPR, HIPAA, NIST CSF, ISO 27001) and active response. Connect Claude or any LLM to your SOC. OAuth 2.1, RBAC, multi-cluster, air-gap ready.
SOAR Automation with Shuffle, Wazuh & TheHive | This project integrates Shuffle SOAR, Wazuh SIEM, and TheHive to automate security incident response. It enriches alerts using VirusTotal & AbuseIPDB, creates incidents in TheHive, and sends real-time Discord notifications.
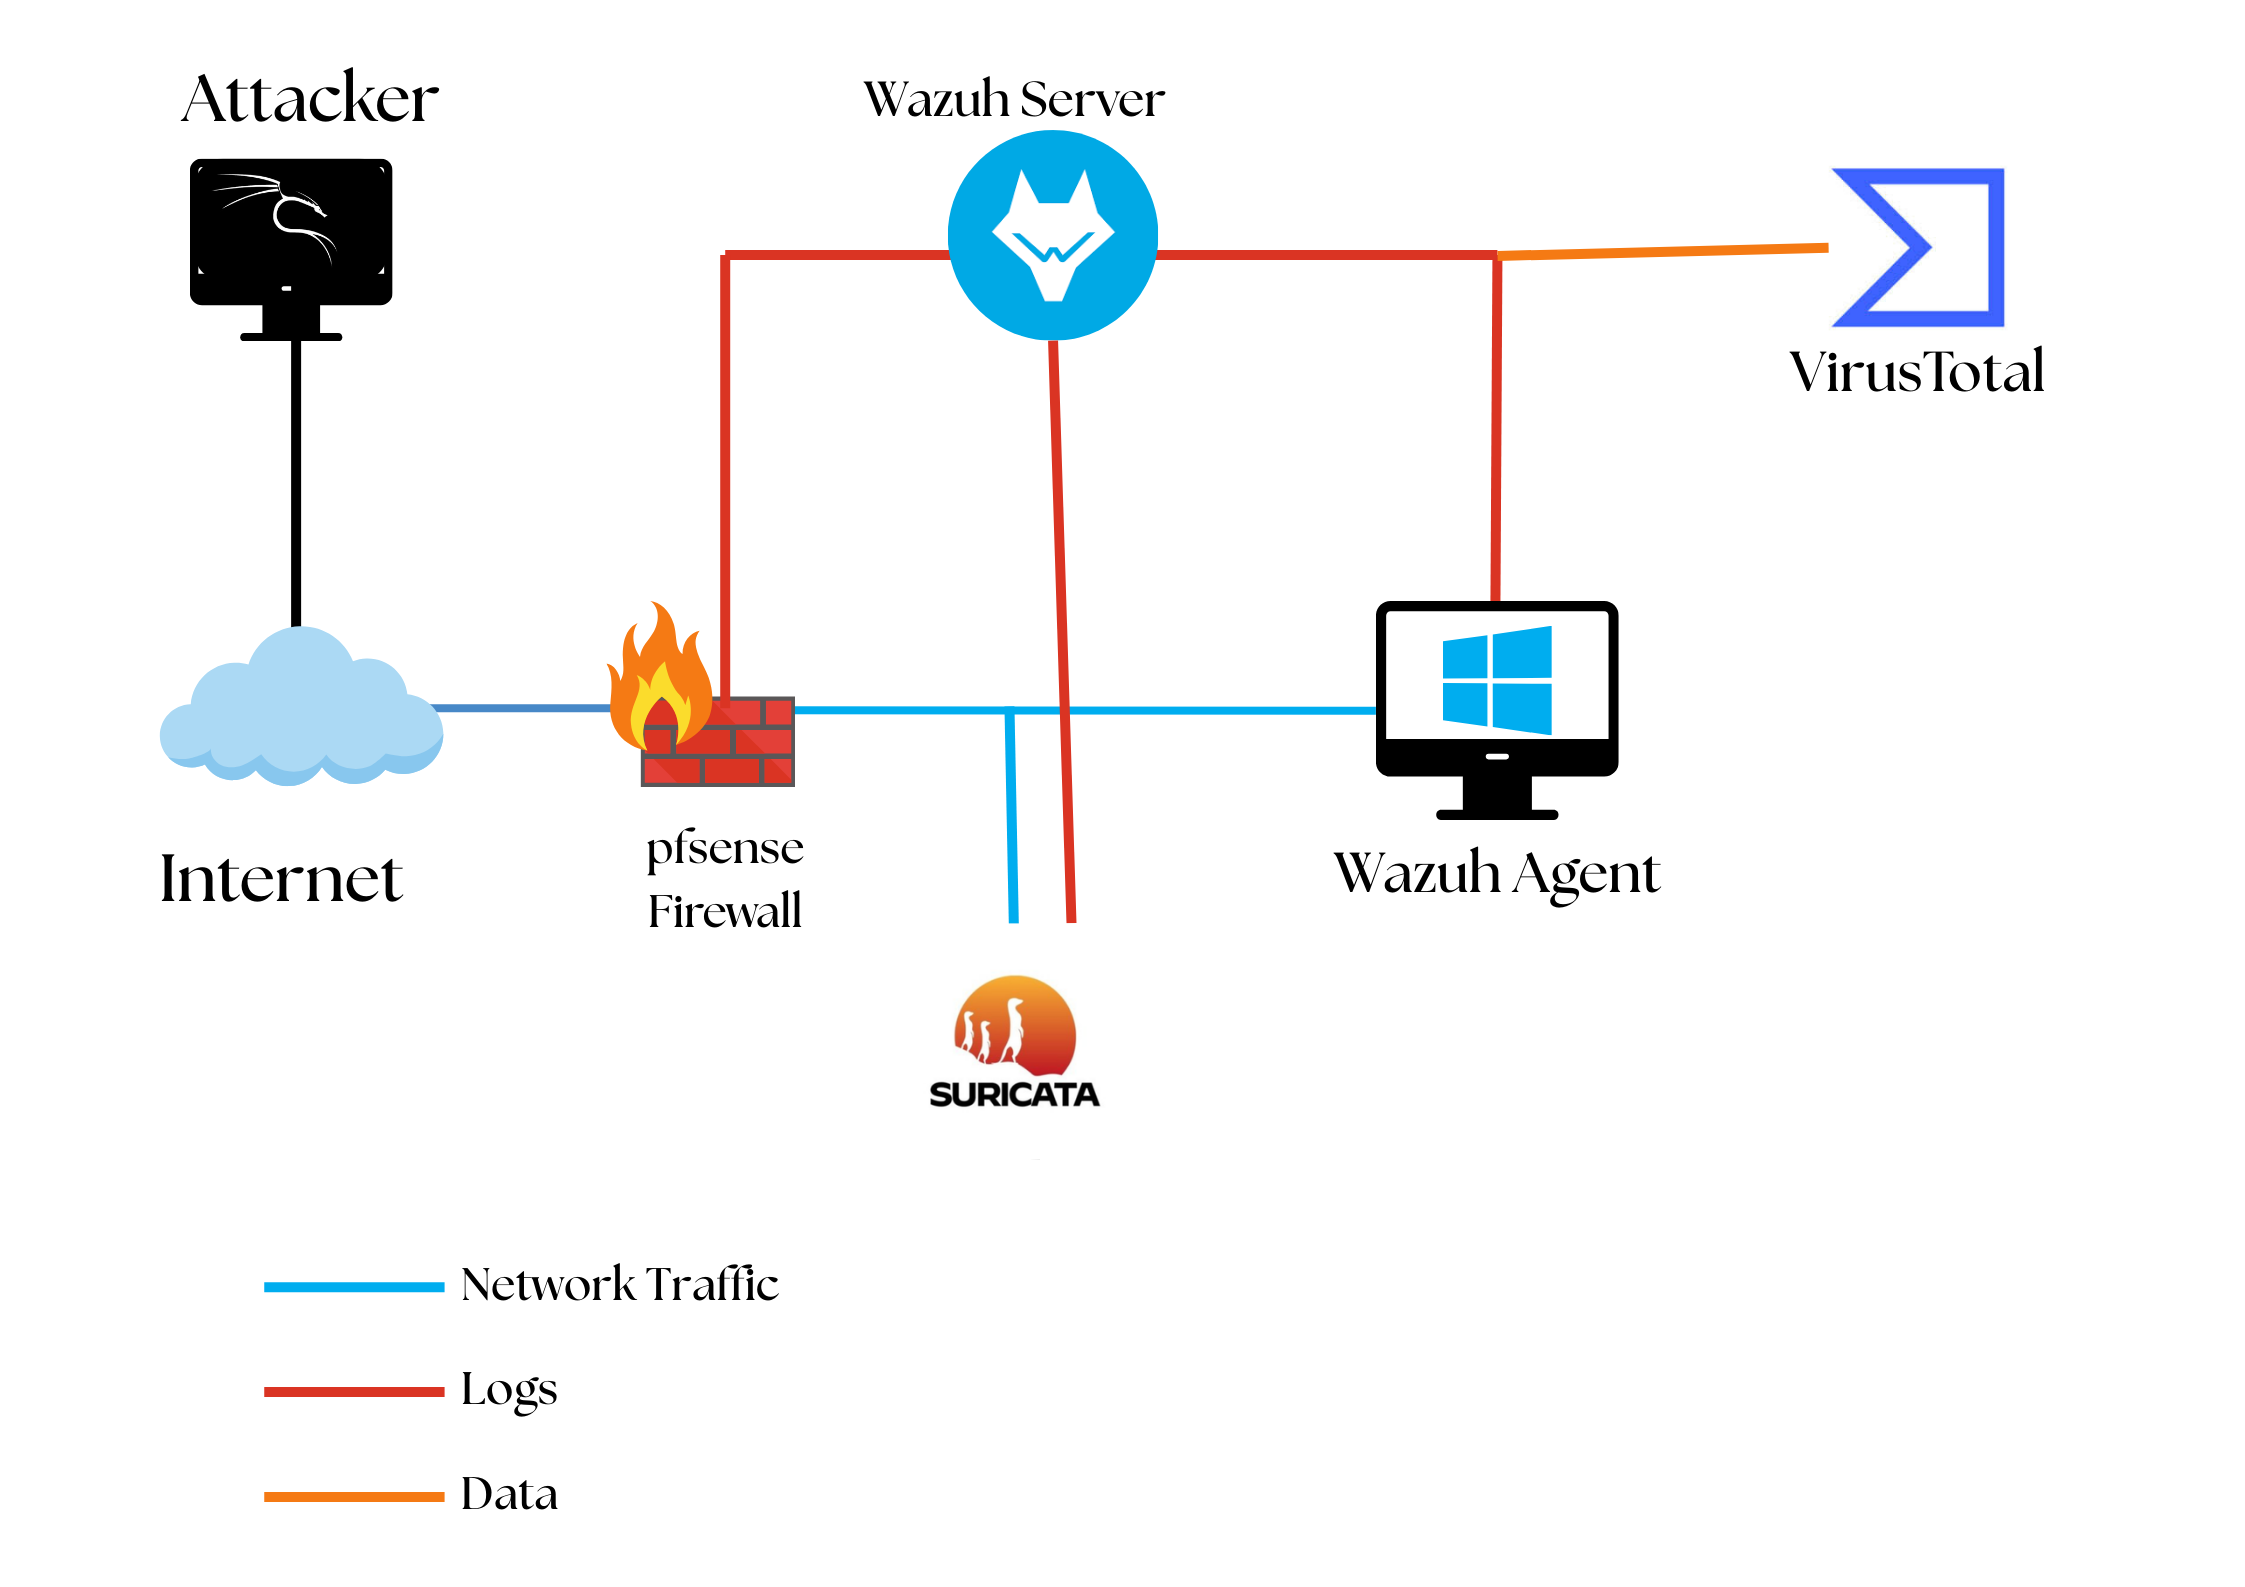
A SOC home lab built with Wazuh SIEM/XDR, pfSense, Suricata IDS/IPS, VirusTotal and Sysmon. Demonstrating log collection, threat detection, and attack simulation.
Agentic SOC for Wazuh built on Strands Agents: a 13-agent swarm with 37 Wazuh-verified skills triages, investigates and plans response through the Wazuh MCP Server. Policy-gated autonomy, approvals, RBAC, audit, tracing and evals in one Docker stack. Bedrock, Anthropic, NVIDIA NIM, vLLM, LiteLLM or air-gapped Ollama.
RuleVis is a powerful analysis tool that transforms your Wazuh ruleset into a dynamic, interactive force-directed graph. It helps you visualize the complex relationships between rules, identify critical dependencies, discover structural issues, and analyze the distribution of your rule IDs.
A Purple Team lab simulating Active Directory attacks (Kerberoasting, BloodHound, lateral movement) and implementing defensive hardening (gMSA, tiering, LLMNR/NetBIOS disabling) with Wazuh SIEM detection rules mapped to MITRE ATT&CK.
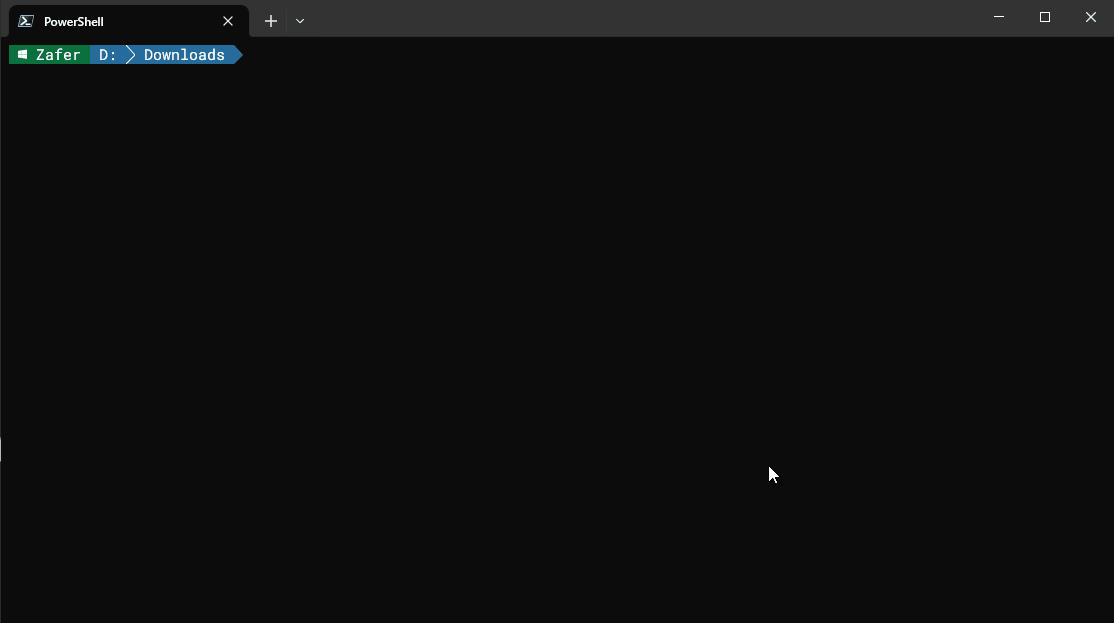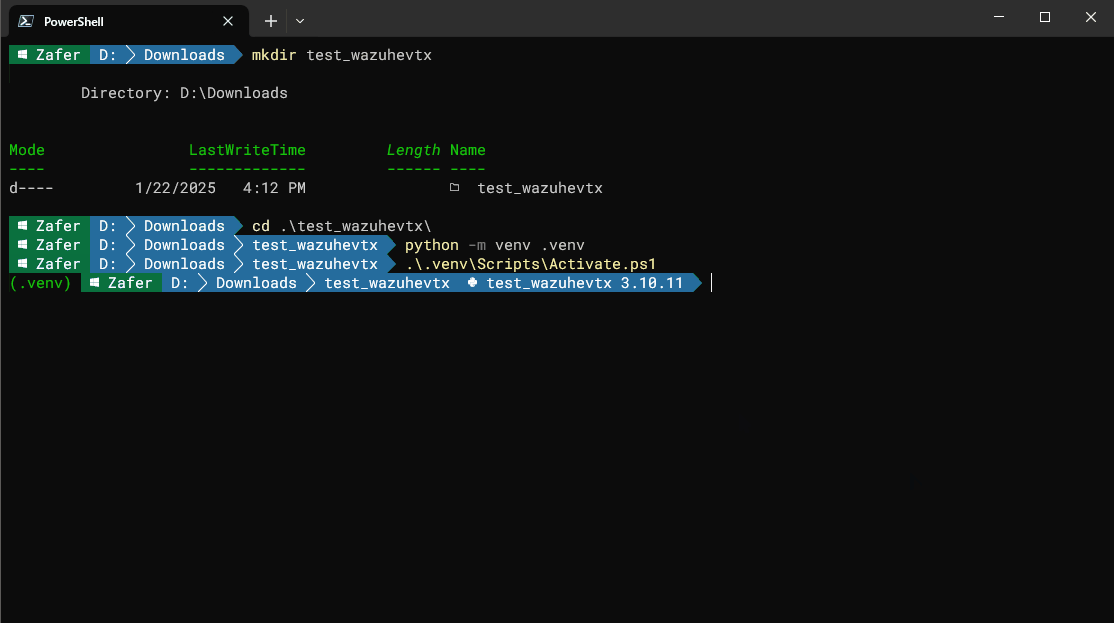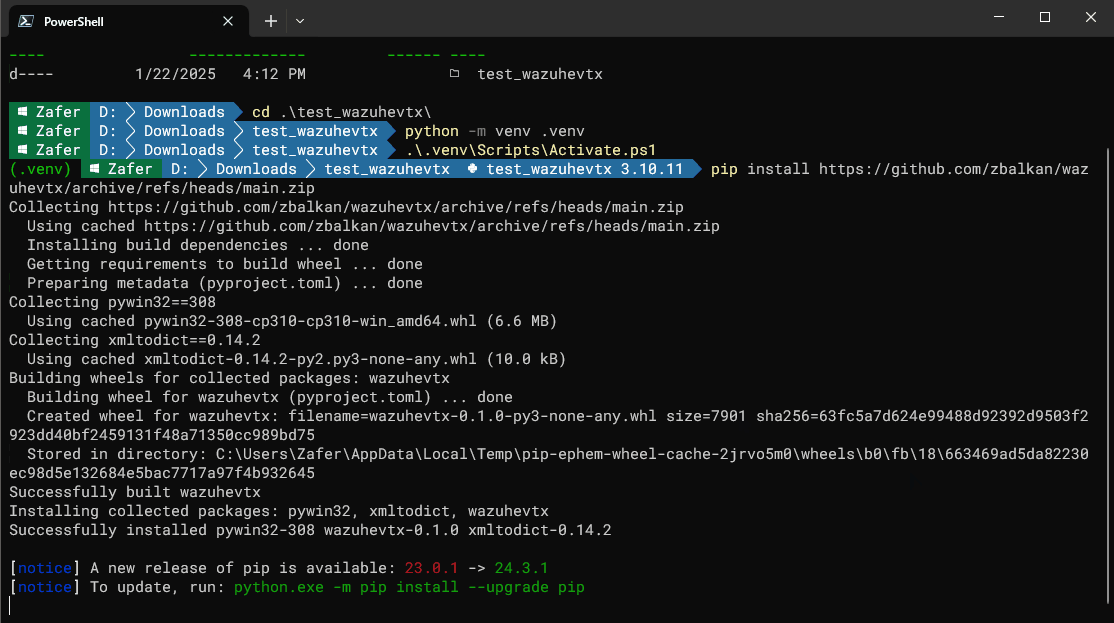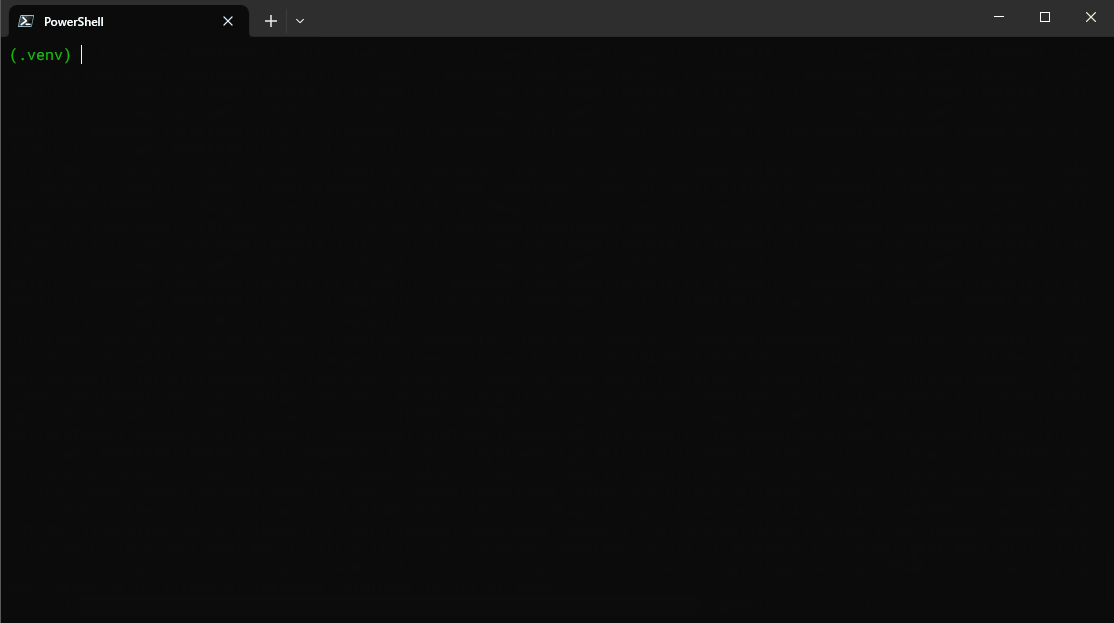
A Python tool that parses EVTX files and converts them into JSON formatted logs mimicking Wazuh agent behavior in version 4.x. wazuhevtx is designed as a helper for wazuh-logtest tool.
A helper for Wazuh Security Configuration Assessment (SCA) to create a custom SCA based on loosening.
Docker Container Setup with Wazuh for Vulnerability Scanning DVWA Container
The project utilizes of a wazuh-manager installed on WSL or a Linux machine, allowing testing custom rules locally before moving to production.
A comprehensive Blue Team lab project for detecting and responding to insider threat breaches using Wazuh, Splunk, and ELK.
A tool to help detection engineers generate Wazuh rule tests either derived from INI test files from Wazuh repository, Windows Event Log (EVTX) files, or Wazuh rule files. The test format uses Python's unittest. It is designed to accompany wazuh-devenv project.
This project focuses on optimizing the Wazuh Indexer for a single-node setup by tuning shard counts, replica settings, index lifecycle policies (ISM), and increasing heap memory usage to avoid cluster overload and log ingestion issues.
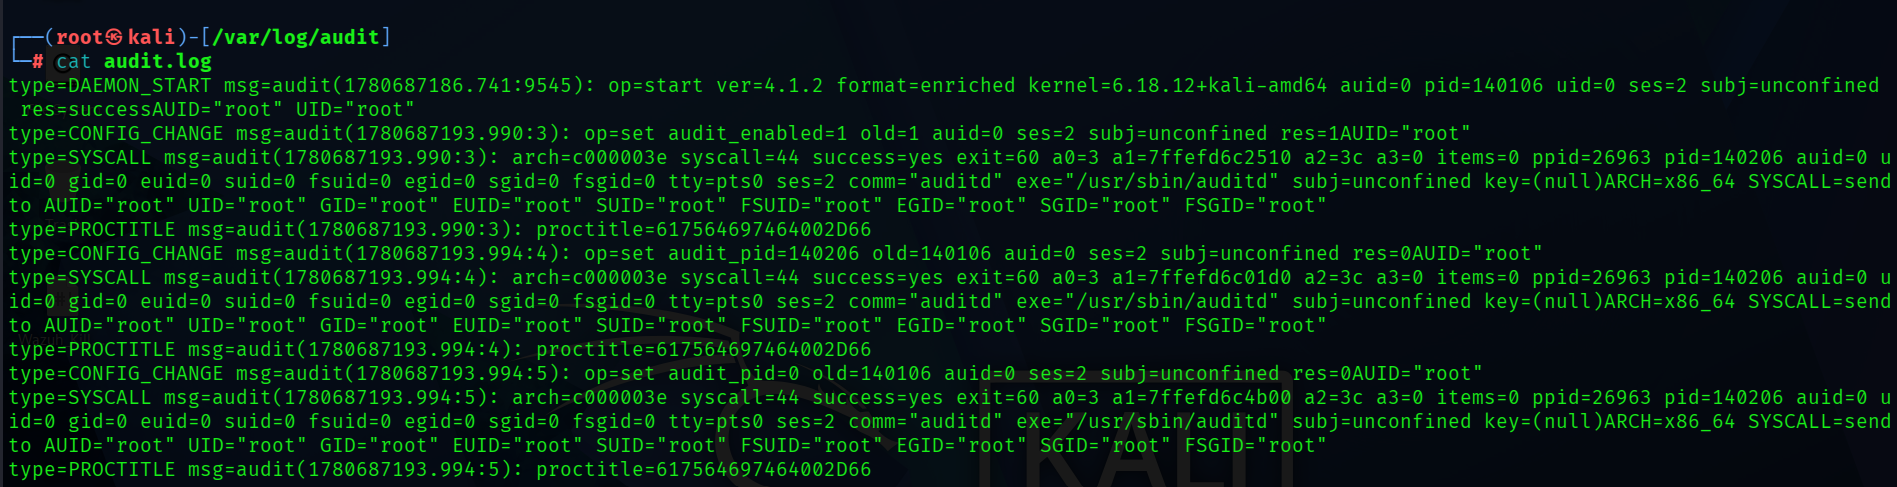
Wazuh, Auditd, Threat Hunting | Detecting privileged command execution and endpoint activity through centralized log monitoring.
Wazuh integration to send alerts to Keep (open-source alert management and AIOps platform)
Wazuh, Suricata, IDS, Threat Detection: Integrating Suricata with Wazuh to detect network reconnaissance activity and centralize security monitoring.
To deploy Wazuh, Kolide Fleet launcher, OSquery, Winlogbeat, Rsyslog agents for Windows and Linux.
Repository for configuration files, scripts, and other information on the Watchtower Stack
Wazuh SCA Linux hardening policy for Copy Fail (CVE-2026-31431)
This project contains custom LKRG (Linux Kernel Runtime Guard) decoders and rules for Wazuh