wazuh
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints and cloud workloads.
- 18k
- C++
- 4 h ago
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints and cloud workloads.
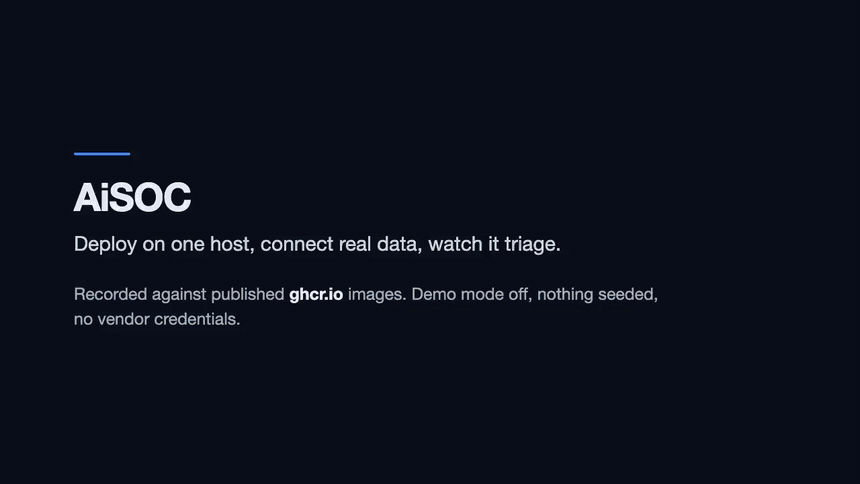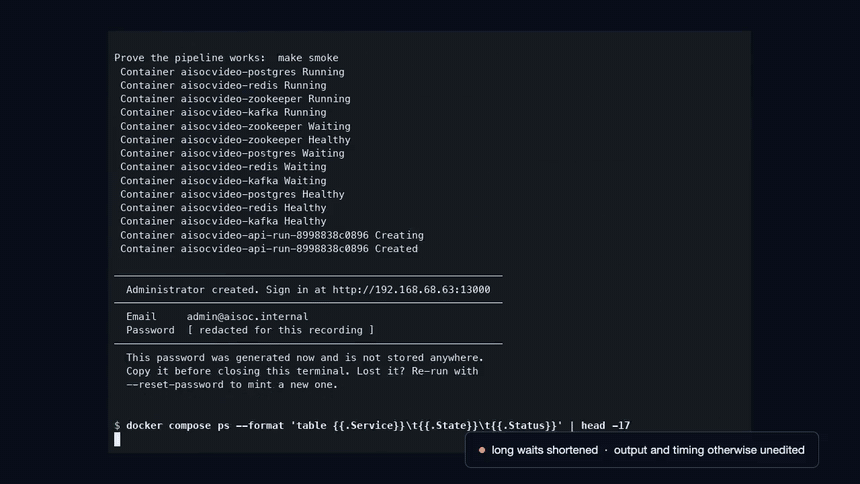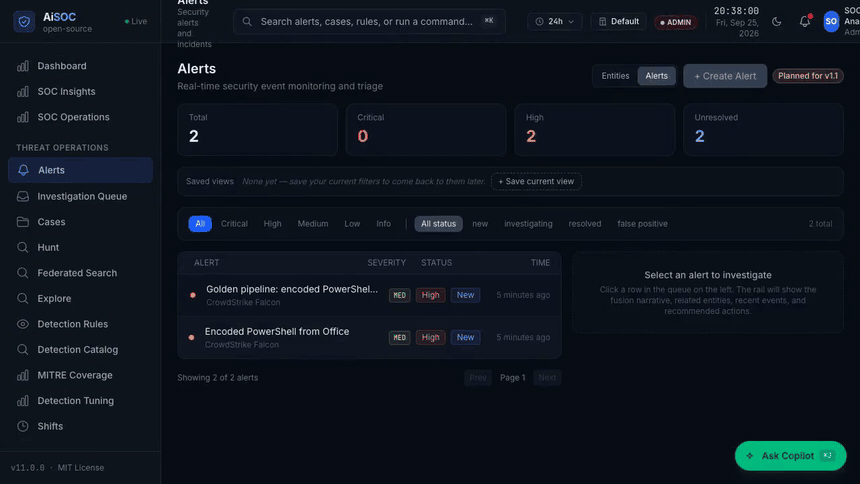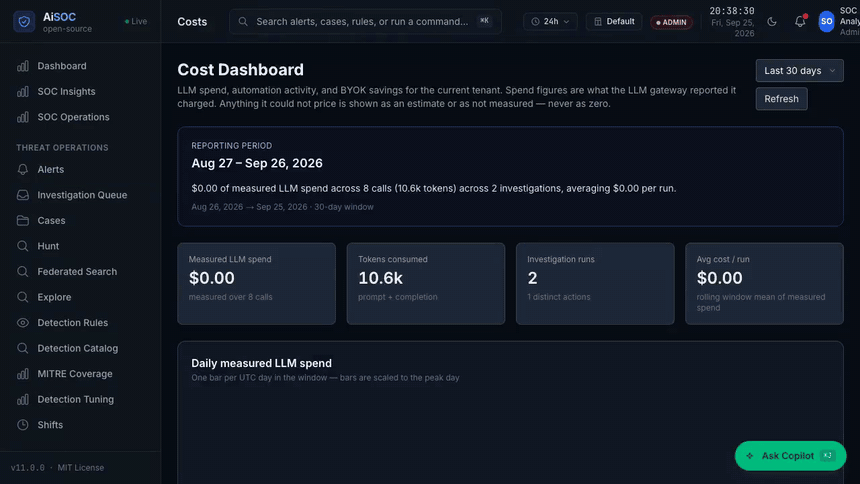
Open-source AI Security Operations Center: alert fusion, LLM-agent triage, MITRE ATT&CK investigation, and a replayable decision ledger for every agent step. Self-hostable, runs with no API keys, MIT licensed. Ships an MCP server for Claude, Cursor and Continue.
🐳 Elastic Stack (ELK) v9+ on Docker with Compose. Pre-configured out of the box to enable Logging, Metrics, APM, Alerting, ML, and SIEM features. Up with a Single Command.
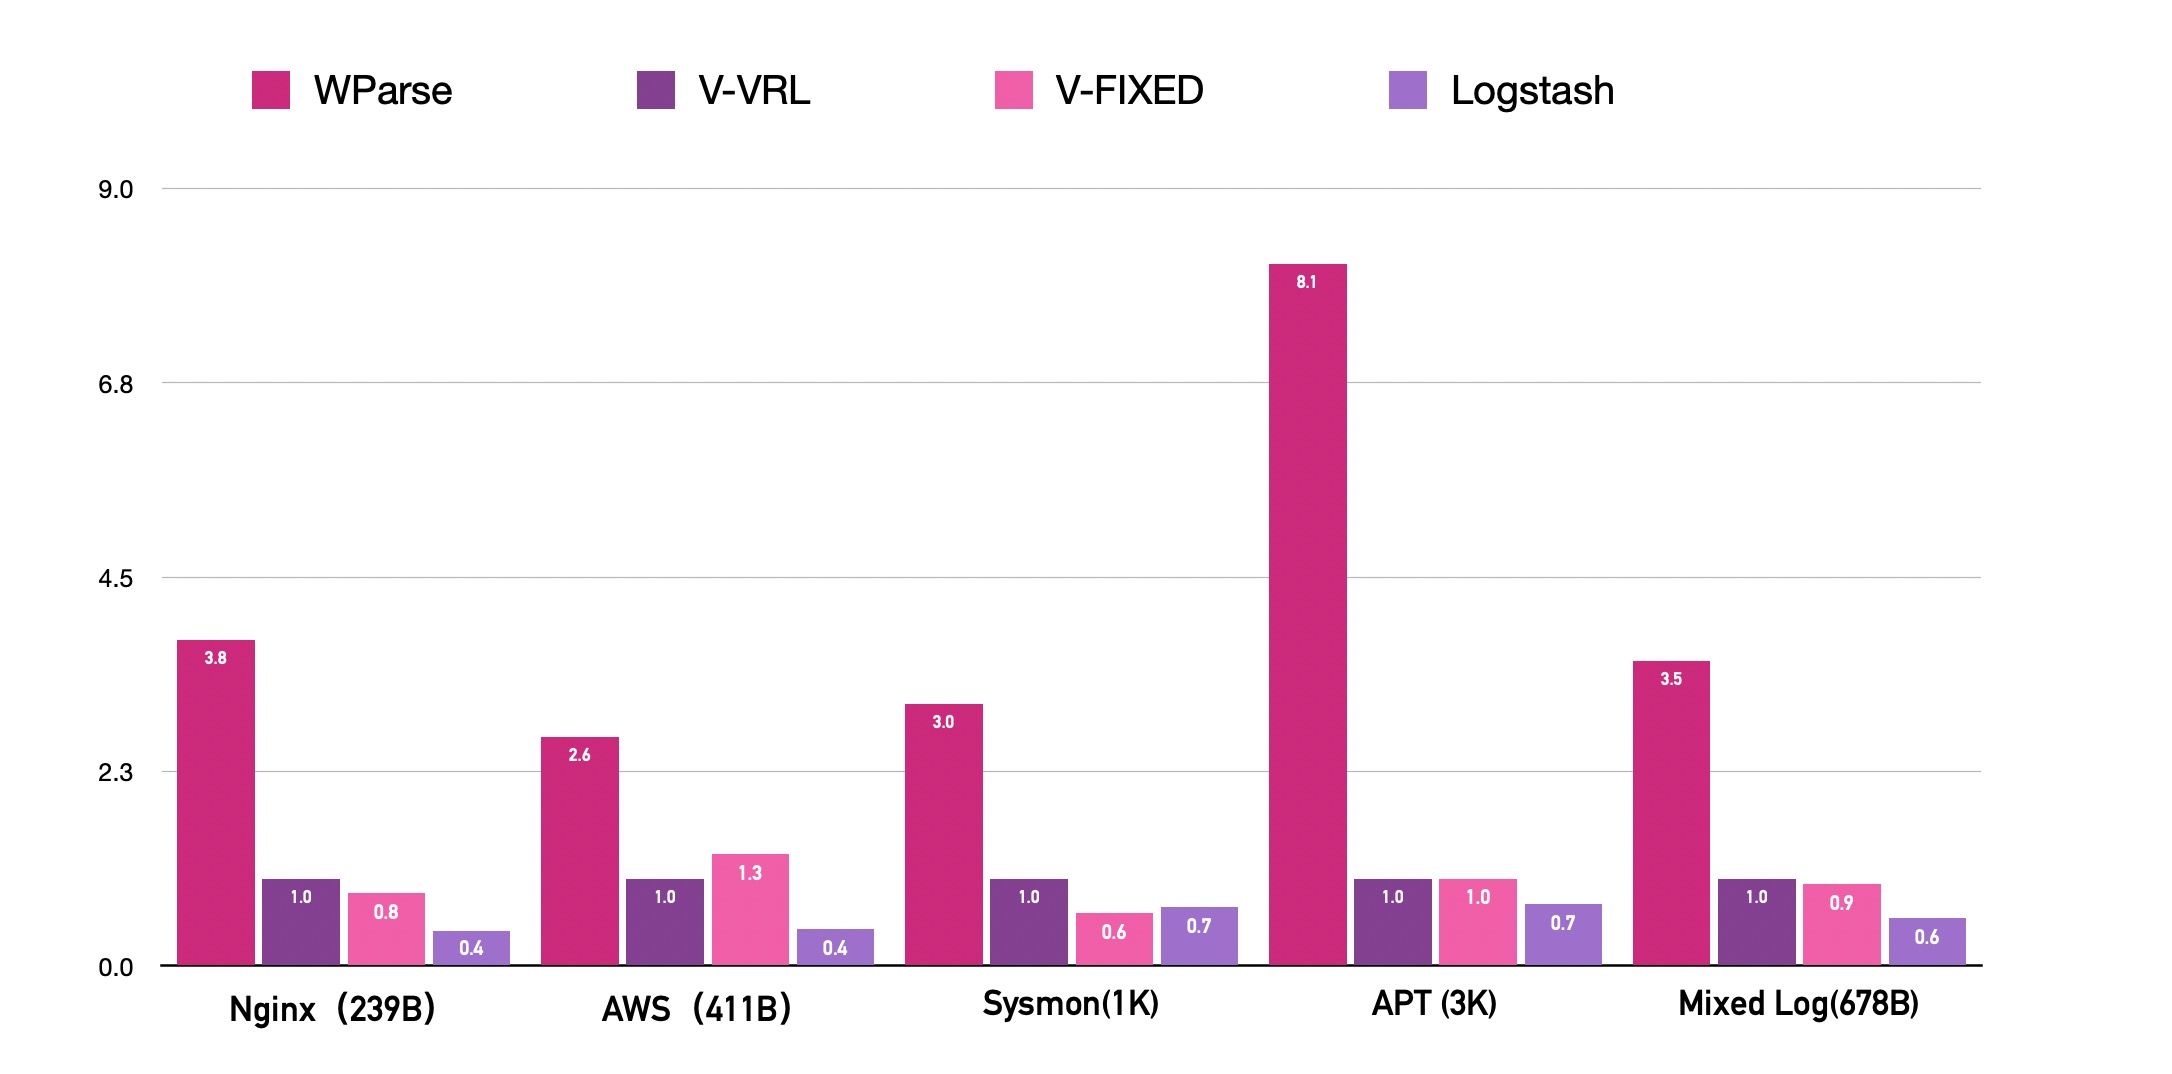
Fast and easy to use database for logs, which can efficiently handle terabytes of logs
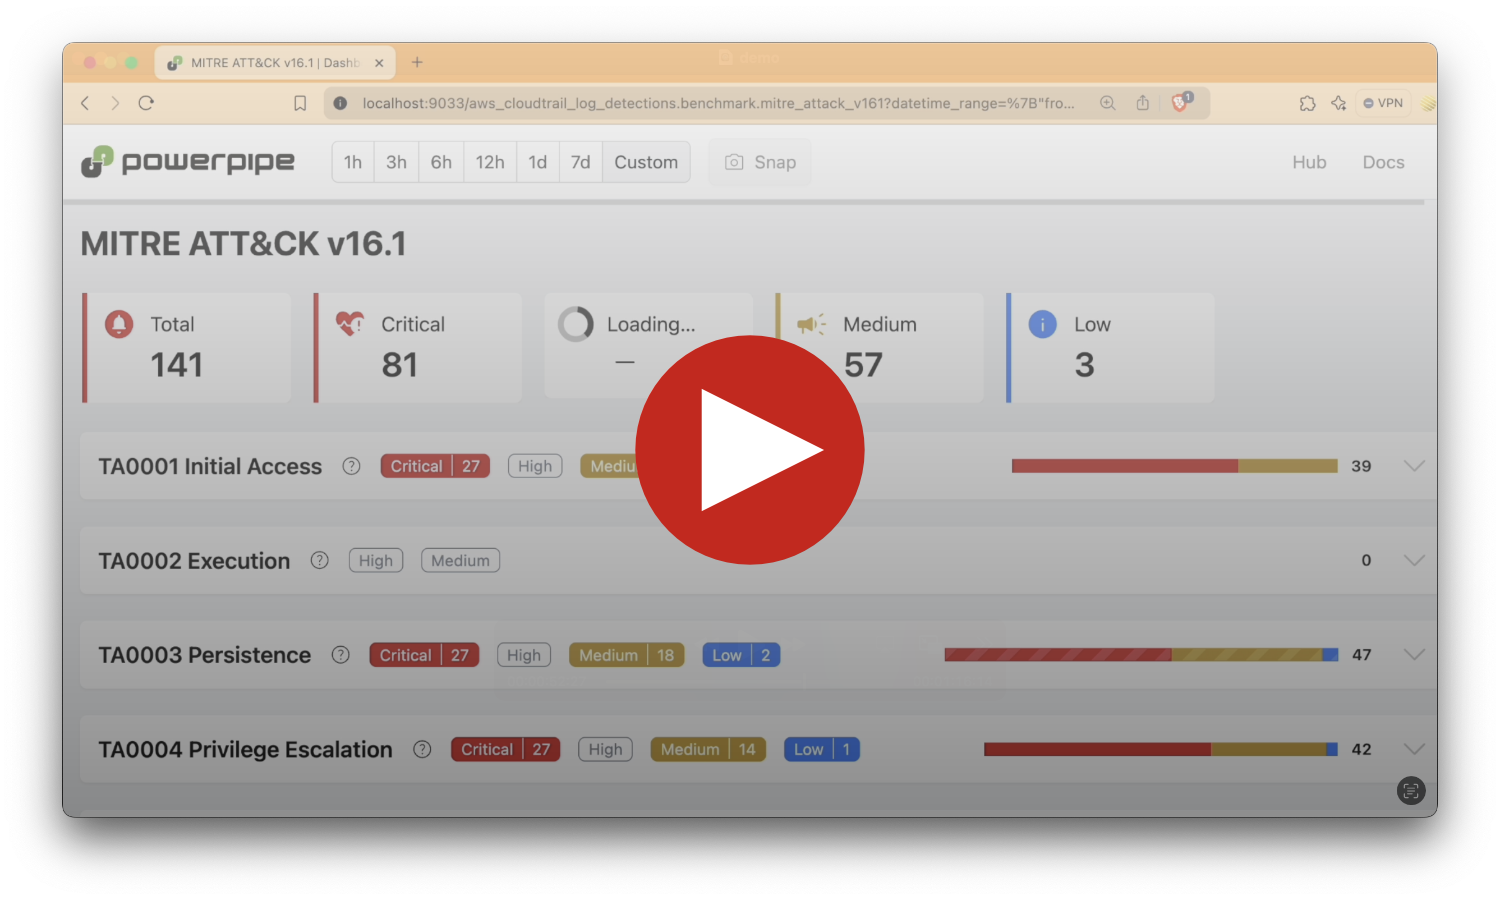
Tools to rapidly deploy a threat hunting capability on Azure Sentinel that leverages Sysmon and MITRE ATT&CK
Real-time network monitor + outbound firewall — see & block every connection. Privacy-first, local-first, Rust fleet agent, SIEM exports, 8 languages. / Moniteur réseau temps réel + pare-feu sortant, agent de flotte Rust, exports SIEM. 100 % local.
Awesome list of keywords and artifacts for Threat Hunting sessions
select * from logs; Tailpipe is an open source SIEM for instant log insights, powered by DuckDB. Analyze millions of events in seconds, right from your terminal.
Set of EVTX samples (>270) mapped to MITRE ATT&CK tactic and techniques to measure your SIEM coverage or developed new use cases.
Vigil SOC: The leading open source AI SOC. Apache 2.0. Runs against your own LLM, local or remote.
ARTEX 한국어판 ·AI 기반 침해사고 대응 기능 추가 (upstream: Autumn-27/ARTEX, AGPL-3.0)
Purpleteam scripts simulation & Detection - trigger events for SOC detections
Build AI-powered security tools. 50+ hands-on labs covering ML, LLMs, RAG, threat detection, DFIR, and red teaming. Includes Colab notebooks, Docker environment, and CTF challenges.
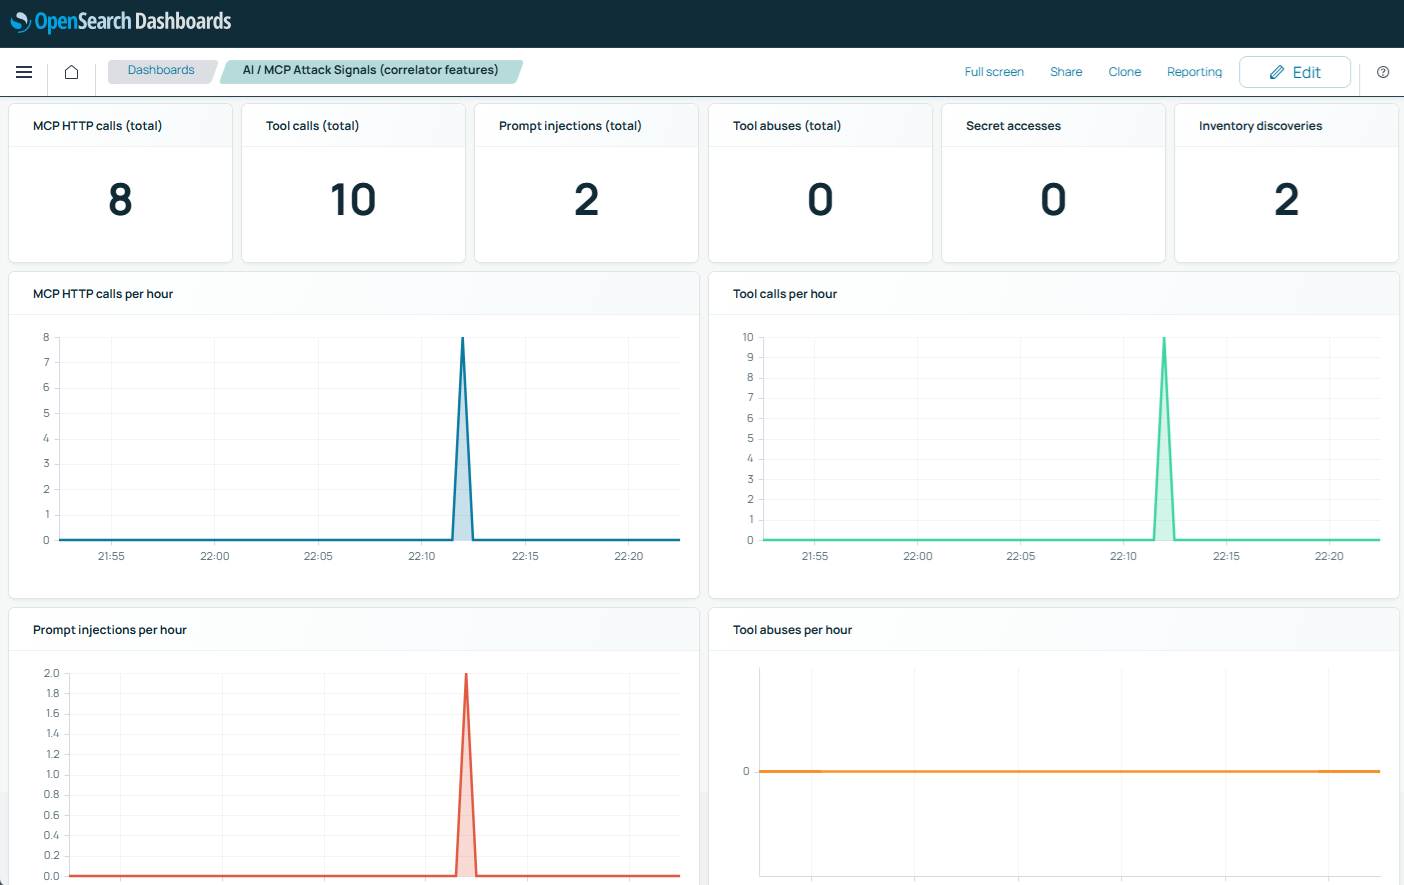
Collector/Correlator, Embedded log-based WAF, AI Patterns Classifier
Agentic SOC for Wazuh built on Strands Agents: a 13-agent swarm with 37 Wazuh-verified skills triages, investigates and plans response through the Wazuh MCP Server. Policy-gated autonomy, approvals, RBAC, audit, tracing and evals in one Docker stack. Bedrock, Anthropic, NVIDIA NIM, vLLM, LiteLLM or air-gapped Ollama.
Open-source security suite for OSINT, web scanning, API testing, SIEM integration, and AI-powered analysis
Hardware-accelerated, zero-copy systems file scanner for Node.js. Powered by AVX-512/AVX2/NEON SIMD, kernel mmap, and persistent thread pools for 50+ GB/s throughput with 0 MB V8 heap.
Sigma detection rules for hunting with the threathunting-keywords project
This tool will be invaluable for: SIEM Testing - Generate realistic multi-source logs Security Training - Reproducible scenarios for education Development - Consistent test data for log processing systems Research - Controlled log generation for cybersecurity studies
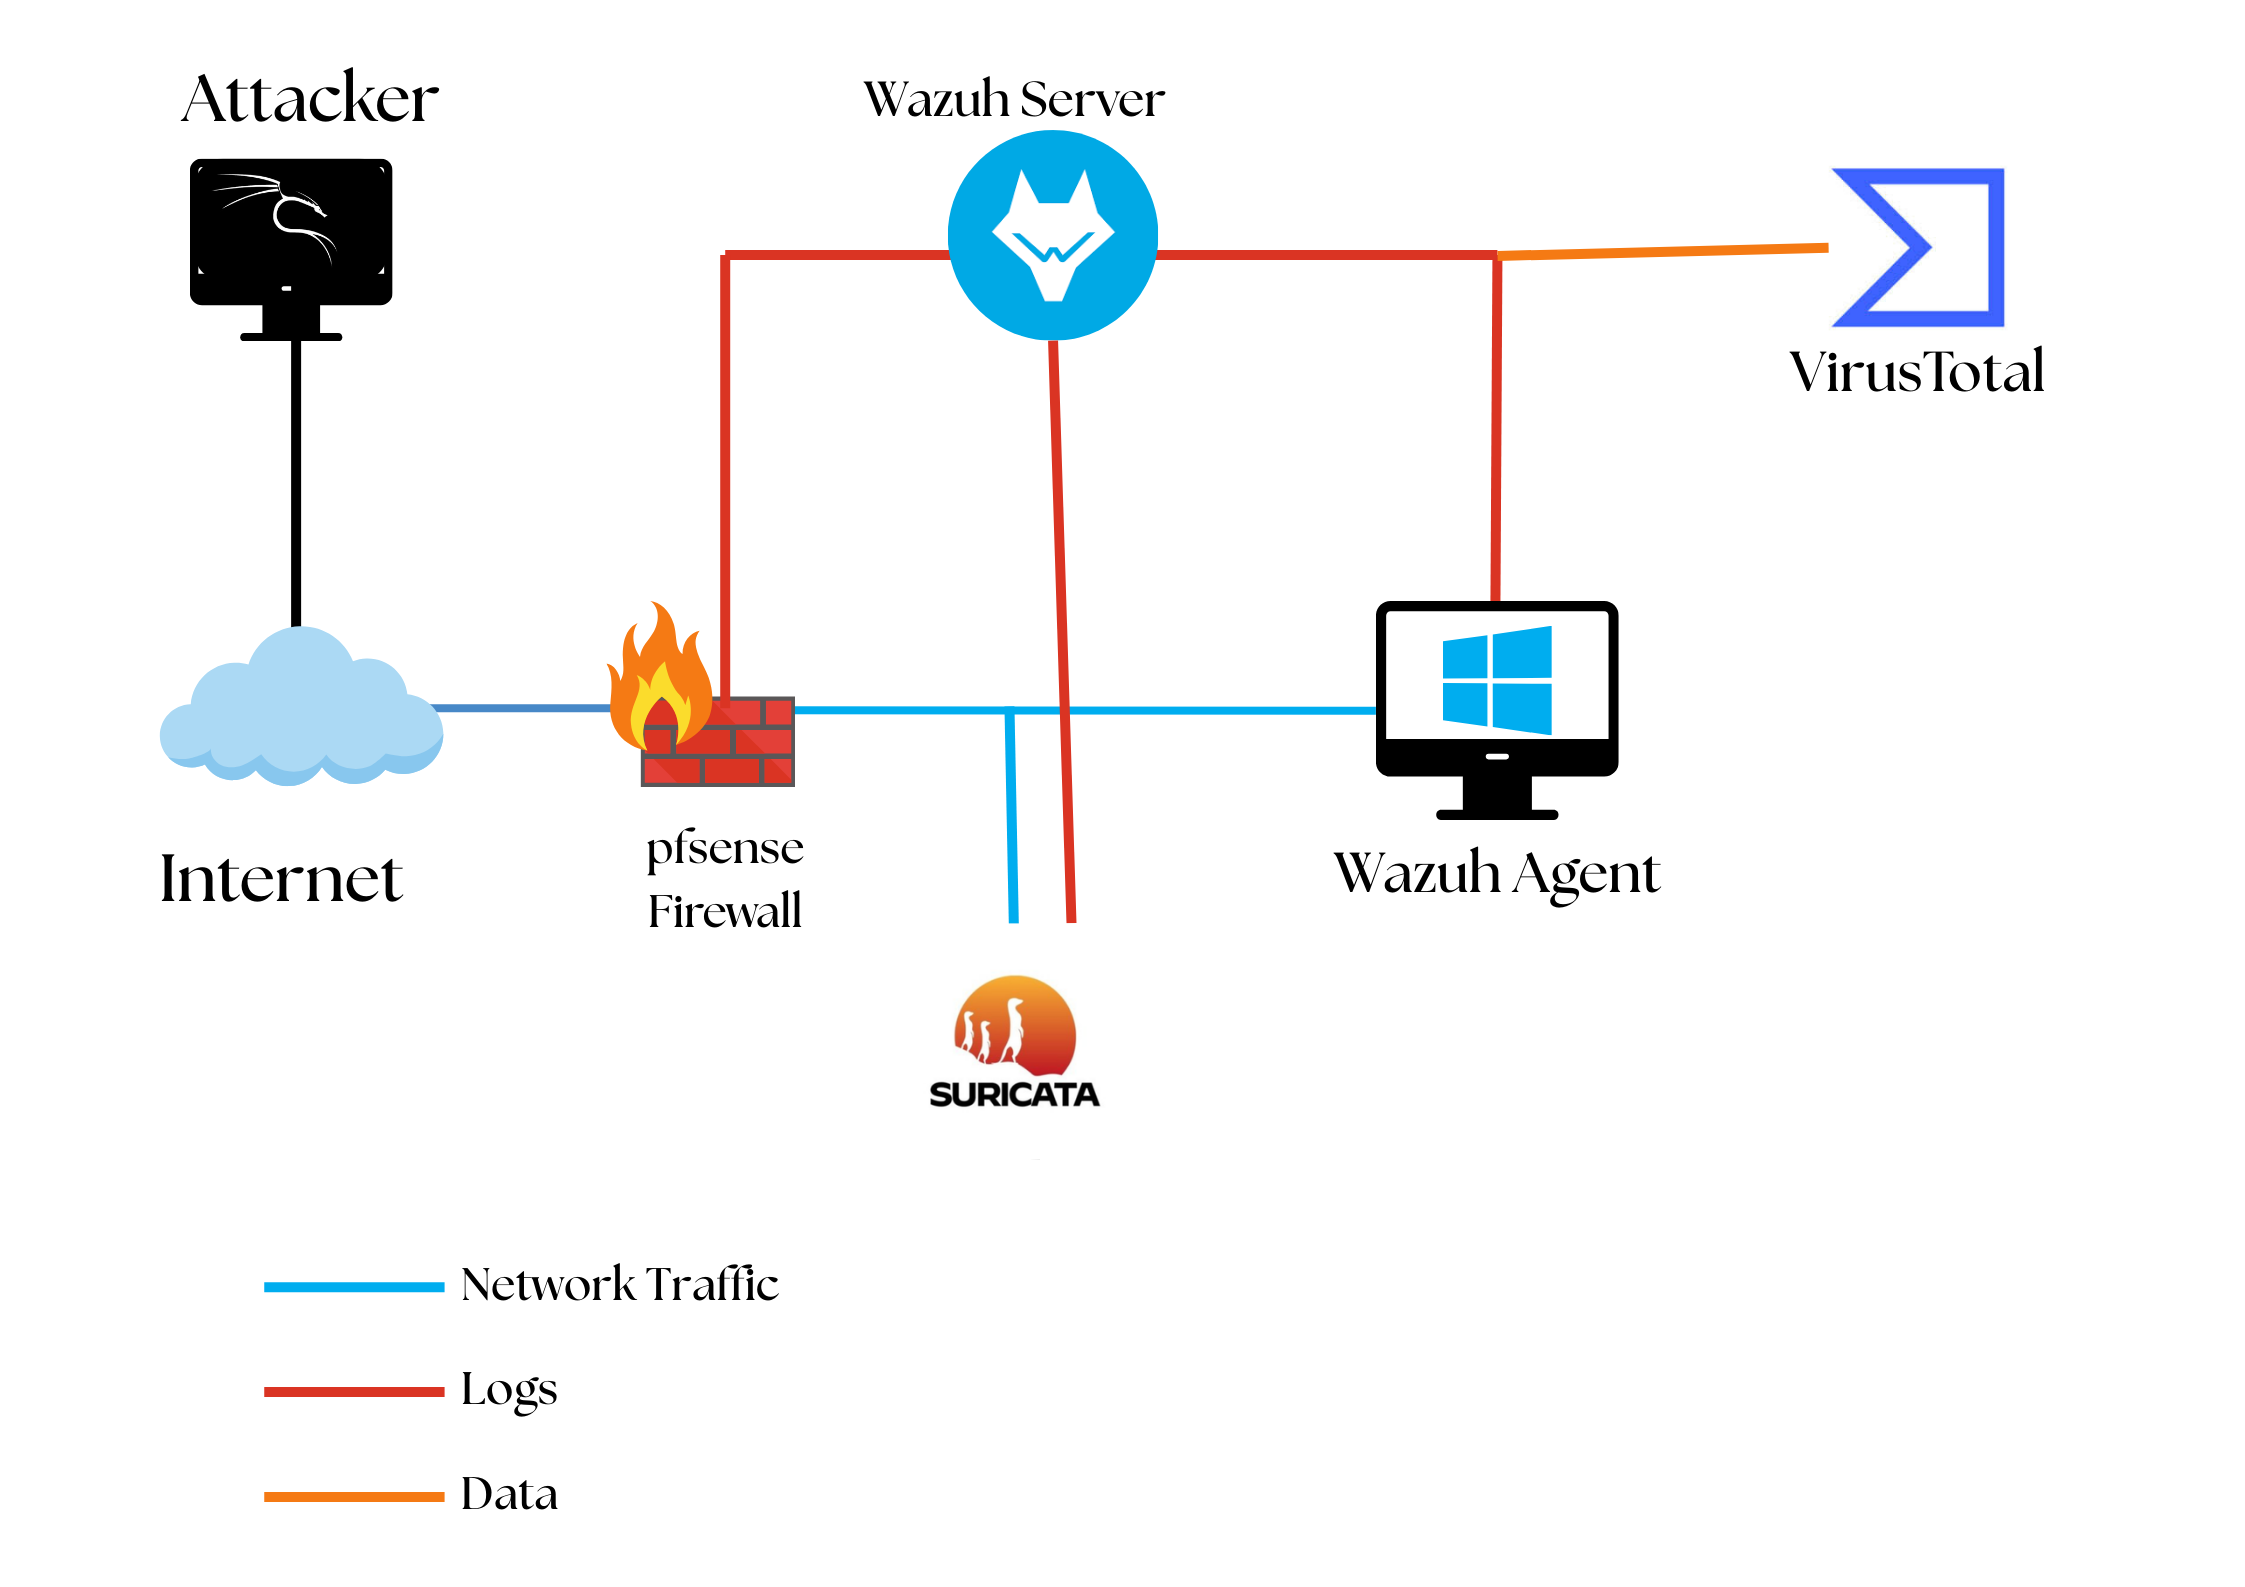
A SOC home lab built with Wazuh SIEM/XDR, pfSense, Suricata IDS/IPS, VirusTotal and Sysmon. Demonstrating log collection, threat detection, and attack simulation.
🛡️ Free AI that blocks hackers while you sleep. Runs on cheap hardware. When someone in Tokyo gets attacked, you're protected in 30 seconds. No fees. No experts needed. Just protection. One node's detection → everyone's protection.
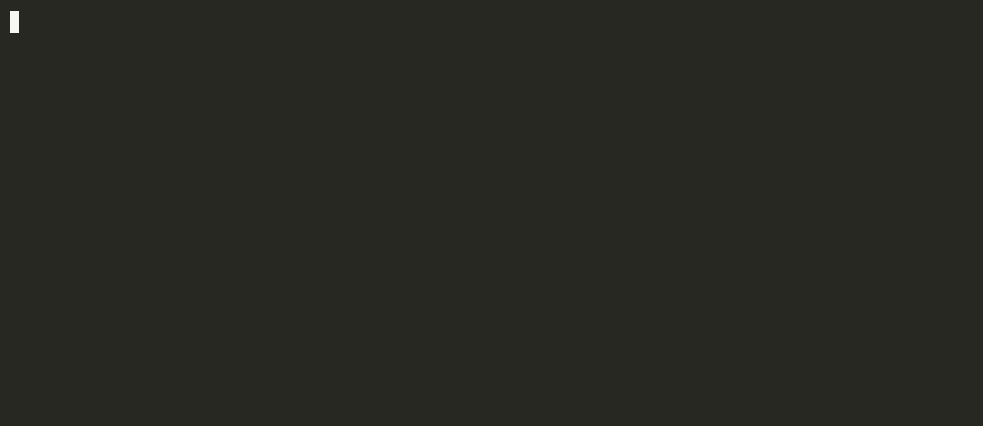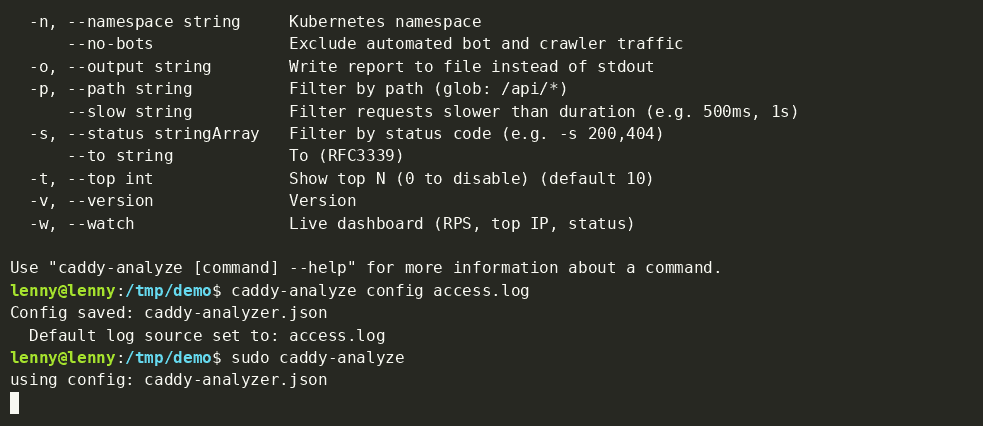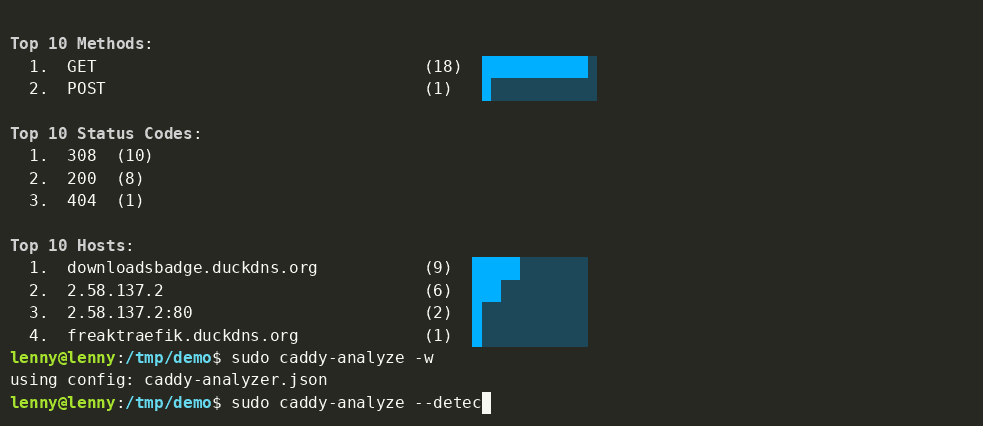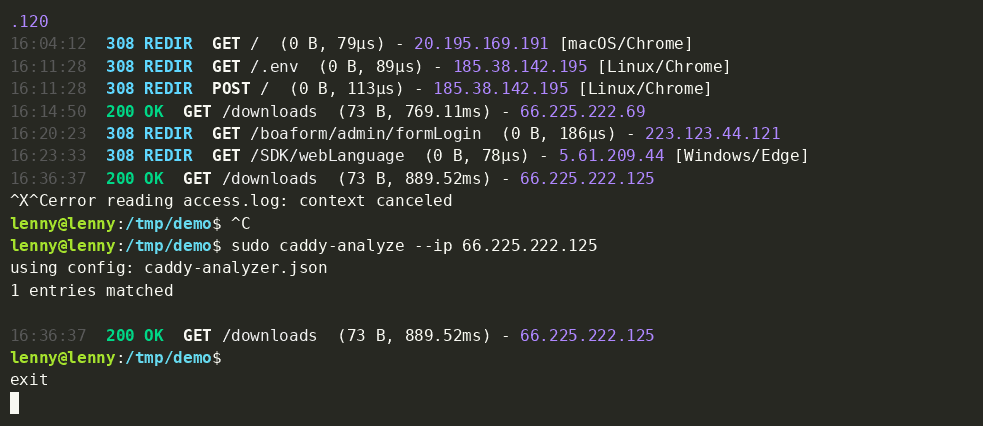
Fast, zero-dependency access log analyzer, security threat inspector, and TUI dashboard for Caddy v2
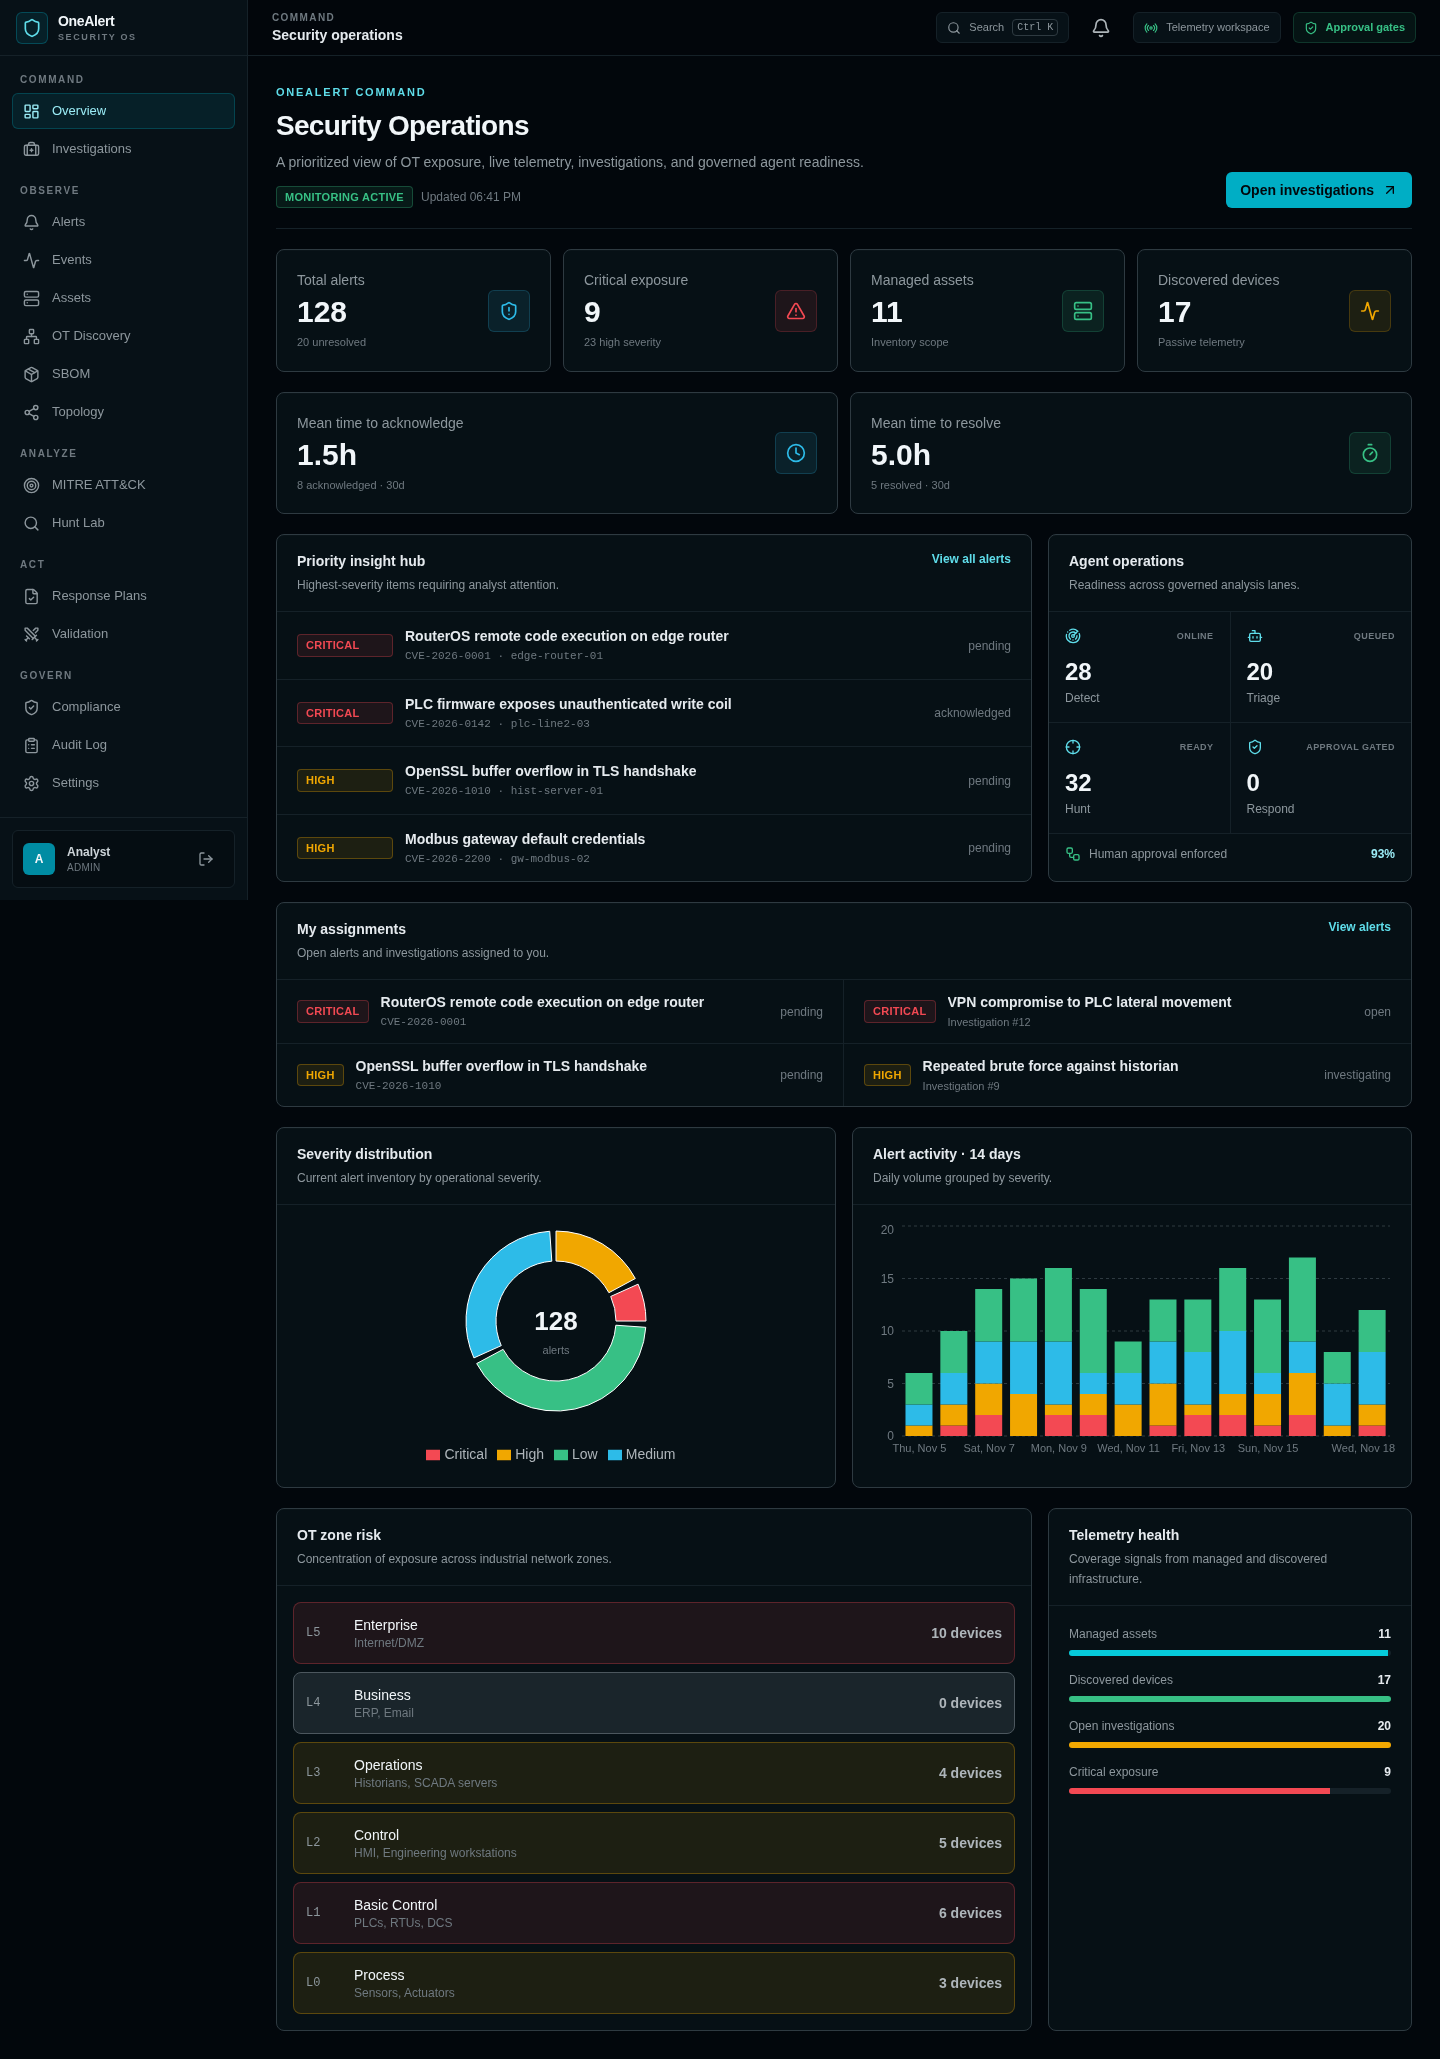
AI-powered SOC for OT/ICS networks — 6 autonomous agents, MITRE ATT&CK mapping, Suricata/Zeek ingestion, human-in-the-loop response, 330+ tests. Open-source alternative to Claroty/Dragos for SMBs.
Deploy custom SOC Agents to Gemini Enterprise Agent Platform
AgentForensics is an open-source security framework that monitors complete LLM agent sessions in real time, detecting prompt injection attacks across tool outputs, web pages, documents, and API responses. It uses heuristic rules, a DistilBERT ML classifier, instruction boundary detection, semantic drift, and sliding-window multi-turn detection.